セキュリティレポートへ移動
ドメインのセキュリティと脅威インテリジェンス
fernleighcounsel.com favicon

fernleighcounsel.com

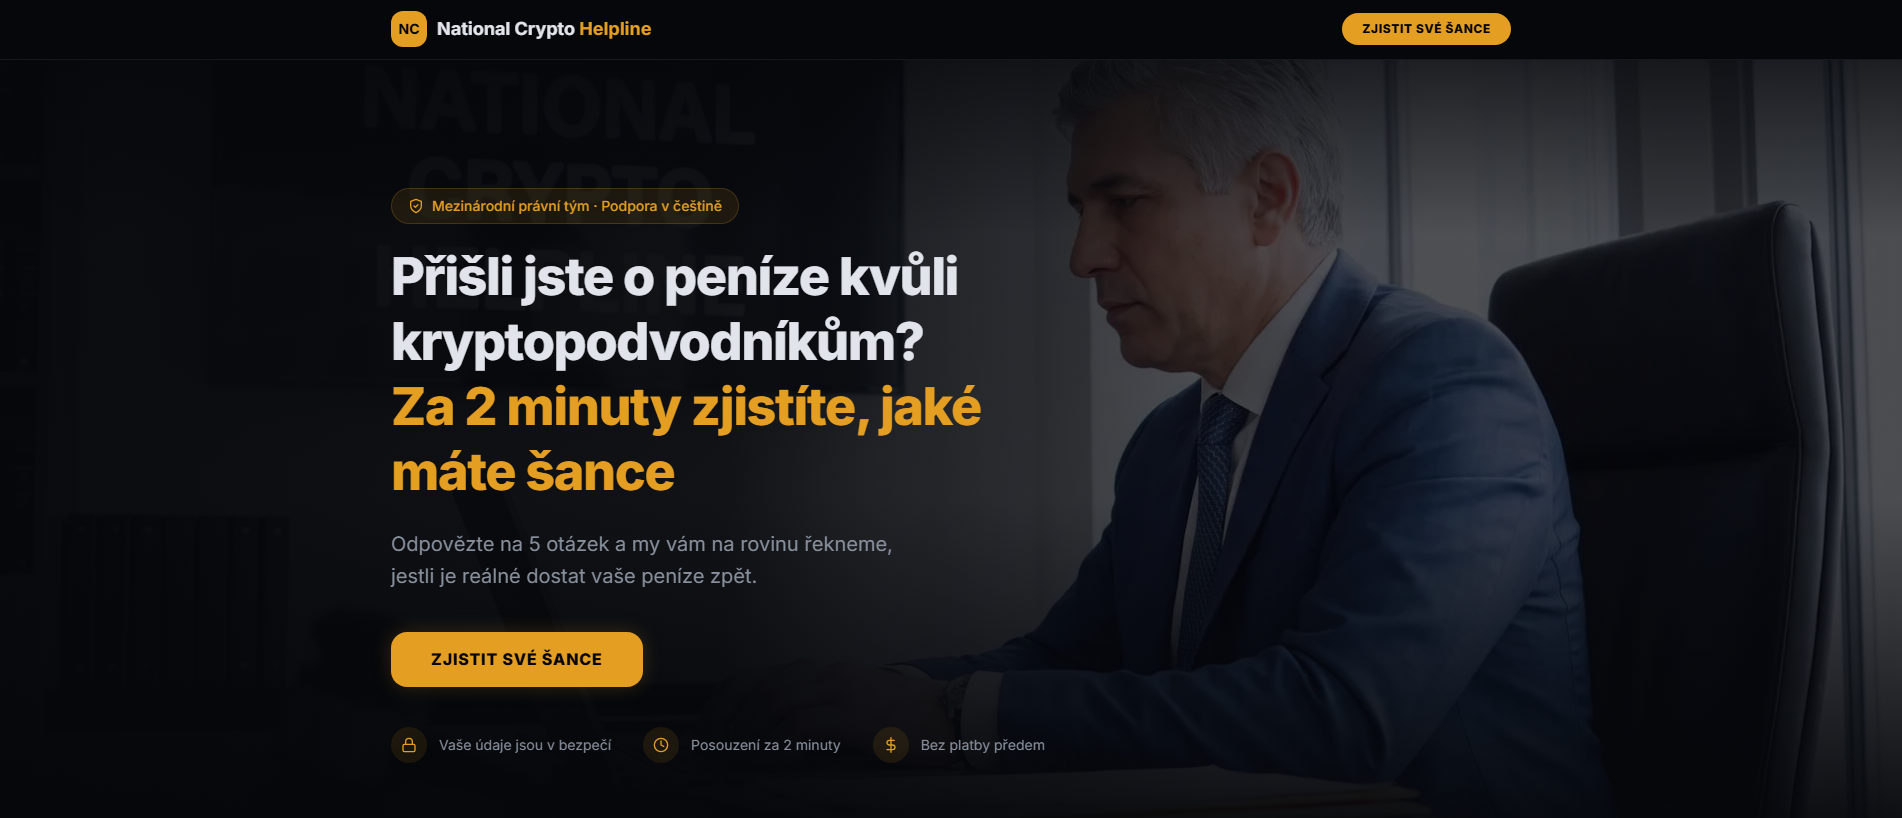
“National Crypto Helpline — Pomoc obětem kryptopodvodů”

レジストラ
Spaceship
Resolved IP
137.184.215.29
Registered
2026年9月10日
PhishDestroy assessment クリティカル
可用性 最後に確認されたアクティブな状態 最新の保存された到達可能性の観測 観測された · HTTP probe
VirusTotal 検出数: 7/91 保存されたブロックリストの一致: 2 詐欺タイプ: Impersonation
OTX: 4 refs 2026年9月17日 1 Report Sent
API
このドメインは悪意のあるものとして報告されています
検出を報告するセキュリティ エンジン: 7。 一致を報告する公開ブロックリスト: 2。 細心の注意を払ってください — 資格情報や個人情報を入力しないでください。
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@spaceship.com. The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
1 month
Reports sent
1
Latest case ID
PD-20260917-22D850
Current status
HTTP 200 at latest stored check
VirusTotal
engine detections
Google Safe Browsing
OTX
community references
Page captures
open gallery
Domain age
Reports sent
view timeline
レポート概要

フィッシング: fernleighcounsel.com — 最後に確認されたアクティブな状態 (HTTP 200). 証拠の概要: VirusTotal 7/91 (alphaMountain.ai, BitDefender, CRDF, Forcepoint ThreatSeeker, Gridinsoft)…

元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。

Source evidenceVirusTotal 7 / 91 · OTX 4 references 6 sources

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Analysis

クリティカル
VirusTotal
7 / 91
OTX
4 community refs
Page captures
3

PhishDestroy threat report

Overview

fernleighcounsel.com is an impersonation phishing page that presents itself as a "National Crypto Helpline" offering help to victims of crypto scams. The Czech-language page title, "Pomoc obětem kryptopodvodů" (help for victims of crypto fraud), shows it targets Czech-speaking people who have already lost money. PhishDestroy first flagged it on 2026-09-17. As of 2026-10-19 the site was still online and serving its content.

How the scam works

Sites like this run a recovery scam. They pose as an official-sounding helpline or legal counsel, and the domain name itself suggests a law firm. Victims who reach out are told their stolen crypto can be traced and returned. The operators then ask for upfront fees, identity documents, account logins, wallet seed phrases or remote access to the victim's computer. The person loses money a second time, and their personal and financial details can be reused against them.

Evidence

Seven of 91 VirusTotal engines classified the domain as malicious when it was scanned on 2026-09-29. The flagging vendors were alphaMountain.ai, BitDefender, CRDF, Forcepoint ThreatSeeker, Gridinsoft, Kaspersky and SOCRadar. That is a modest share, but it is consistent across several established security vendors. MetaMask and SEAL list the domain on their blocklists alongside PhishDestroy. It also appears in four AlienVault OTX threat pulses, which means other researchers have tracked it independently.

Infrastructure

The domain was registered through Spaceship, Inc. on 2026-09-10, only seven days before PhishDestroy detected it. That short gap is typical of throwaway domains built for a single campaign. The site is hosted on DigitalOcean, LLC servers in the United States. It uses a free Let's Encrypt certificate, so the browser padlock only means the connection is encrypted and says nothing about whether the helpline is real.

What to do

Do not pay any fee, tax or deposit this site requests, and stop all contact. If you shared a seed phrase, move your remaining funds to a new wallet right away. If you installed remote-access software, remove it and change the passwords and 2FA on your email, banking and exchange accounts from a clean device. If you sent ID documents, warn your bank. Report the contact to the Czech Police along with any payment details, since legitimate authorities never charge to recover stolen crypto. Defenders should block the domain and its hosting IP and watch for Czech-language recovery-service lures in inbound mail.

Blocklist matchesMetaMask · PhishDestroy · SEAL 3
MetaMask 掲載あり View source
PhishDestroy PhishDestroy list View source
SEAL 掲載あり View source

Last checked

保存済みキャプチャ · 3 captures

Domain details

ドメイン
URLScan verdict 分析完了 score 0 report ↗
IPレピュテーション abuse score 0/100 0 reports checked 2026年10月18日
OTX tags 2026-09activeall-domainsblocklistcontentcryptoドメインdrainerfraudlivemonthlyphishdestroyphishingscam
レジストラ Spaceship (Unknown)
登録情報作成日 2026年9月10日 (39d · New) — Expires 2027年9月10日
HTTPステータス200
技術詳細Provenance & timestamps
初確認2026年9月17日
DOM Analysisanalyzed 2026年9月18日score 95/100
Submitted URLhttp://fernleighcounsel.com/
Favicon Hash
ケース ID
Observed page title
National Crypto Helpline — Pomoc obětem kryptopodvodů
TLS証明書
発行者 Let's Encrypt / YR2 · stored validity ends in 50 days

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
137.184.215.29
Network ASN
AS14061
Organization
Digital Ocean
Observed location
North Bergen, US
Server header
nginx

ネームサーバー 2

  • launch1.spaceship.net
  • launch2.spaceship.net

Location describes the IP network.

TLS証明書

Issuer
Let's Encrypt / YR2
Valid from
2026-09-10 19:37:34
Valid until
2026-12-09 19:37:33
Validity
Within stored validity dates
Collection time
2026-10-11 04:02:09 UTC
Collection source
PhishDestroy collector
Certificate fingerprint34eae15cd43563fa71c30eb422eed9f28f3d5fbe88e68f9e392246fa5758d9f1

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Latest Classified Outcome 2026-10-19 22:29:18 UTC

Primary outcome コンテンツ公開中 reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation コンテンツ公開中 Ordinary HTTP content served 90% 2026-10-19 22:29:18 UTC
RDAP registration 不明
Observed timeline last reachable: 2026-10-19 22:35:32 UTC last content: 2026-10-19 22:29:18 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
使用技術 · 4 identified
Detected via Cloudflare Radar · Wappalyzer engine
このドメインを報告する 証拠を提出し、他の人を守る手助けをしましょう

VirusTotalによる分析

7 / 91 セキュリティ ベンダーがこのドメインにフラグを立てました
View on VT
Last analyzed First positive detection Previous stored snapshot: 7 detections
alphaMountain.ai
BitDefender
CRDF
Forcepoint ThreatSeeker
Gridinsoft
カスペルスキー
SOCRadar

アーカイブ済み証拠

Wayback Machine Snapshot
過去のスナップショットは証拠のレビューに利用可能です
View Archive
サイトパフォーマンス分析

Google PageSpeed Insights — mobile performance audit of fernleighcounsel.com · checked Sep 17, 2026

65
Needs Work
Performance
FCP
3.57s
First Contentful Paint
LCP
5.65s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
204ms
Total Blocking Time
SI
5.43s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Registration & observation details3

Availability observations

Last reachable observation
Last content observation
Estimate basis
Currently reachable

An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

fernleighcounsel.com
保存済みの結果
Cloaked / Filtered
Stored observation history22

Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.

  1. Availability monitor · Recorded state

    不明→live_content

    content_served

  2. Availability monitor · Recorded state

    不明→live_content

    content_served

  3. Availability monitor · Recorded state

    不明→live_content

    content_served

  4. Availability monitor · Recorded state

    利用不可→到達可能

  5. Availability monitor · Recorded state

    到達可能→利用不可

Earlier observations 17
  1. Availability monitor · Recorded state

    不明→live_content

    content_served

  2. Availability monitor · Recorded state

    不明→live_content

    content_served

  3. Availability monitor · Recorded state

    不明→live_content

    content_served

  4. Availability monitor · Recorded state

    不明→live_content

    content_served

  5. Availability monitor · Recorded state

    不明→live_content

    content_served

  6. Availability monitor · Recorded state

    不明→live_content

    content_served

  7. Availability monitor · Recorded state

    不明→live_content

    content_served

  8. Availability monitor · Recorded state

    不明→live_content

    content_served

  9. Availability monitor · Recorded state

    不明→live_content

    content_served

  10. Availability monitor · Recorded state

    不明→live_content

    content_served

  11. Availability monitor · Recorded state

    不明→live_content

    content_served

  12. Availability monitor · Recorded state

    不明→live_content

    content_served

  13. Availability monitor · Recorded state

    不明→live_content

    content_served

  14. Availability monitor · Recorded state

    不明→live_content

    content_served

  15. Availability monitor · Recorded state

    不明→live_content

    content_served

  16. VirusTotal · Detection count

    0→1

  17. Availability monitor · First collection record

    到達可能

Recorded activity

6 entries
  1. AlienVault OTX

    4 community references

    View source
  2. Google Safe Browsing

    No threat flag

    View source
  3. VirusTotal

    7/91 engine detections

    View source
  4. Abuse report sent

    PD-20260917-22D850

    abuse@spaceship.com
  5. Added to PhishDestroy

    fernleighcounsel.com

    View source
  6. URLScan

    Page captured

    View source

証拠および外部報告書

送信済み証拠のスナップショット
Sent: Ledger records: 1 Case ID: PD-20260917-22D850 Recipient: abuse@spaceship.com
PDF notice generated
詳細な分析
Help & reporting

このサイトによって何か影響を受けましたか?

6 evidence signal groups linked 1 stored notification records 最後に確認されたアクティブな状態
If credentials were compromised, report immediately. Do not engage with recovery scammers.

アカウント資格情報、個人情報、支払い情報を入力した場合、またはこのドメインからファイルをダウンロードした場合は、すぐに対処してください。インシデントを報告し、自分自身を守るのに役立つリソースを以下に示します。

Official reporting routes

復旧を装った詐欺に注意! 犯罪者は、捜査員、弁護士、または回収業者を装い、被害者に再び連絡を取る可能性があります。 前払い料金を支払ったり、資格情報を共有したりしないでください。 回復詐欺について詳しくはこちら →

お住まいの地域の当局へ報告してください

サイバー犯罪の公式連絡先 または 苦情草稿を作成する → を取得するには、国を選択してください。

97か国のディレクトリ

Template-based draft · optional AI wording assistance requires separate consent

AI 支援ドラフト — インシデントの詳細は AI プロバイダーによって処理されます · 自分で確認して送信する
After a phishing incident

被害者への推奨事項とアドバイス

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

今すぐ何をすべきでしょうか?

至急

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • すべてのパスワードを変更する — メール、Exchangeアカウントなど、同じパスワードを使用しているものすべて
  • 2段階認証を有効にする 認証アプリ(SMSではない)を使用する。SMSによる復旧機能を無効にする
  • カードの凍結 フィッシングサイトに銀行口座情報を入力してしまった場合

レポート作成のために、どのような情報を収集すべきでしょうか?

FBIのガイドライン

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • 正確な日時 — 各取引および詐欺師との最初の接触について
  • スクリーンショット — 詐欺サイト、チャットメッセージ、メール、ウォレットでの取引、ソーシャルメディア
  • すべてのURLおよびドメイン 詐欺師が使用した(以下を含む) fernleighcounsel.com)
  • コミュニケーション — 詐欺師が使用したメール、テキストメッセージ、電話番号、ユーザー名

たとえすべての詳細がわかっていなくても―― とにかく報告を提出する. 不完全な情報であっても、捜査には役立つ。

この詐欺はどこに通報すればいいですか?

  • FBI IC3 — インターネット犯罪通報センター(米国連邦政府の通報窓口)
  • ユーロポール — 欧州におけるサイバー犯罪の報告(EU)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • 地元の警察 — たとえ直ちに行動を起こせなくても、公式な記録が残される

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • 偽のウェブサイト — 正規サイトのドメインをわずかに変更した、ピクセル単位で完璧に再現されたクローンサイト
  • pig butchering — TelegramやWhatsApp、出会い系アプリを通じて数週間にわたって信頼関係を築き、その後、金銭をだまし取られる
  • 詐欺による金銭の返還を装った詐欺 — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • AIを利用した詐欺 — ディープフェイク、自動化されたフィッシング、AI生成サイトにより、詐欺の発見が難しくなっている

今後、どうすれば身を守ることができるでしょうか?

  • 公式サイトをブックマークする — メール、DM、広告に含まれるリンクは絶対にクリックしないでください
  • ドメインの確認 — 確認する PhishDestroy 操作を行う前に、HTTPS、スペル、ドメインの登録期間を確認してください。
  • 「良すぎて怪しい」=詐欺 — 確実なリターン、有名人の推薦、差し迫った締め切り

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

最新情報を入手し、安全を確保しましょう

リアルタイムの脅威を監視するか、誤検知だと思われる場合はこのリストに異議を申し立ててください

リアルタイム脅威情報フィード この掲載情報について異議を申し立てる
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

このレポートを埋め込む

この脅威情報を、ご自身のウェブサイトやブログで共有してください

embed.html
<iframe
  src="https://phishdestroy.io/ja/embed/domain/fernleighcounsel.com"
  title="PhishDestroy threat report for fernleighcounsel.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>