
追跡対象のドメインを検索し、保存されている証拠、検知結果、および最新の稼働状況を確認します。
保存済みレポートを検索します。この操作では脅威を報告しません。記録がないことは、ドメインが安全であることを意味しません。
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake ドメイン
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of フィッシング Pages
フィッシング pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of 悪意のある Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical 分析
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. インフラ-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea フィッシング Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App 詐欺 (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
リクエスト for private keys or seed phrases
Unexpected transaction requests
貧しい website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1 Always verify domain authenticity
2 Enable two-factor authentication
3 Use hardware wallets for transactions
4 Regularly update security software
5 Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 597 domains tracked for this threat type
WalletConnect Abuse 597 domains
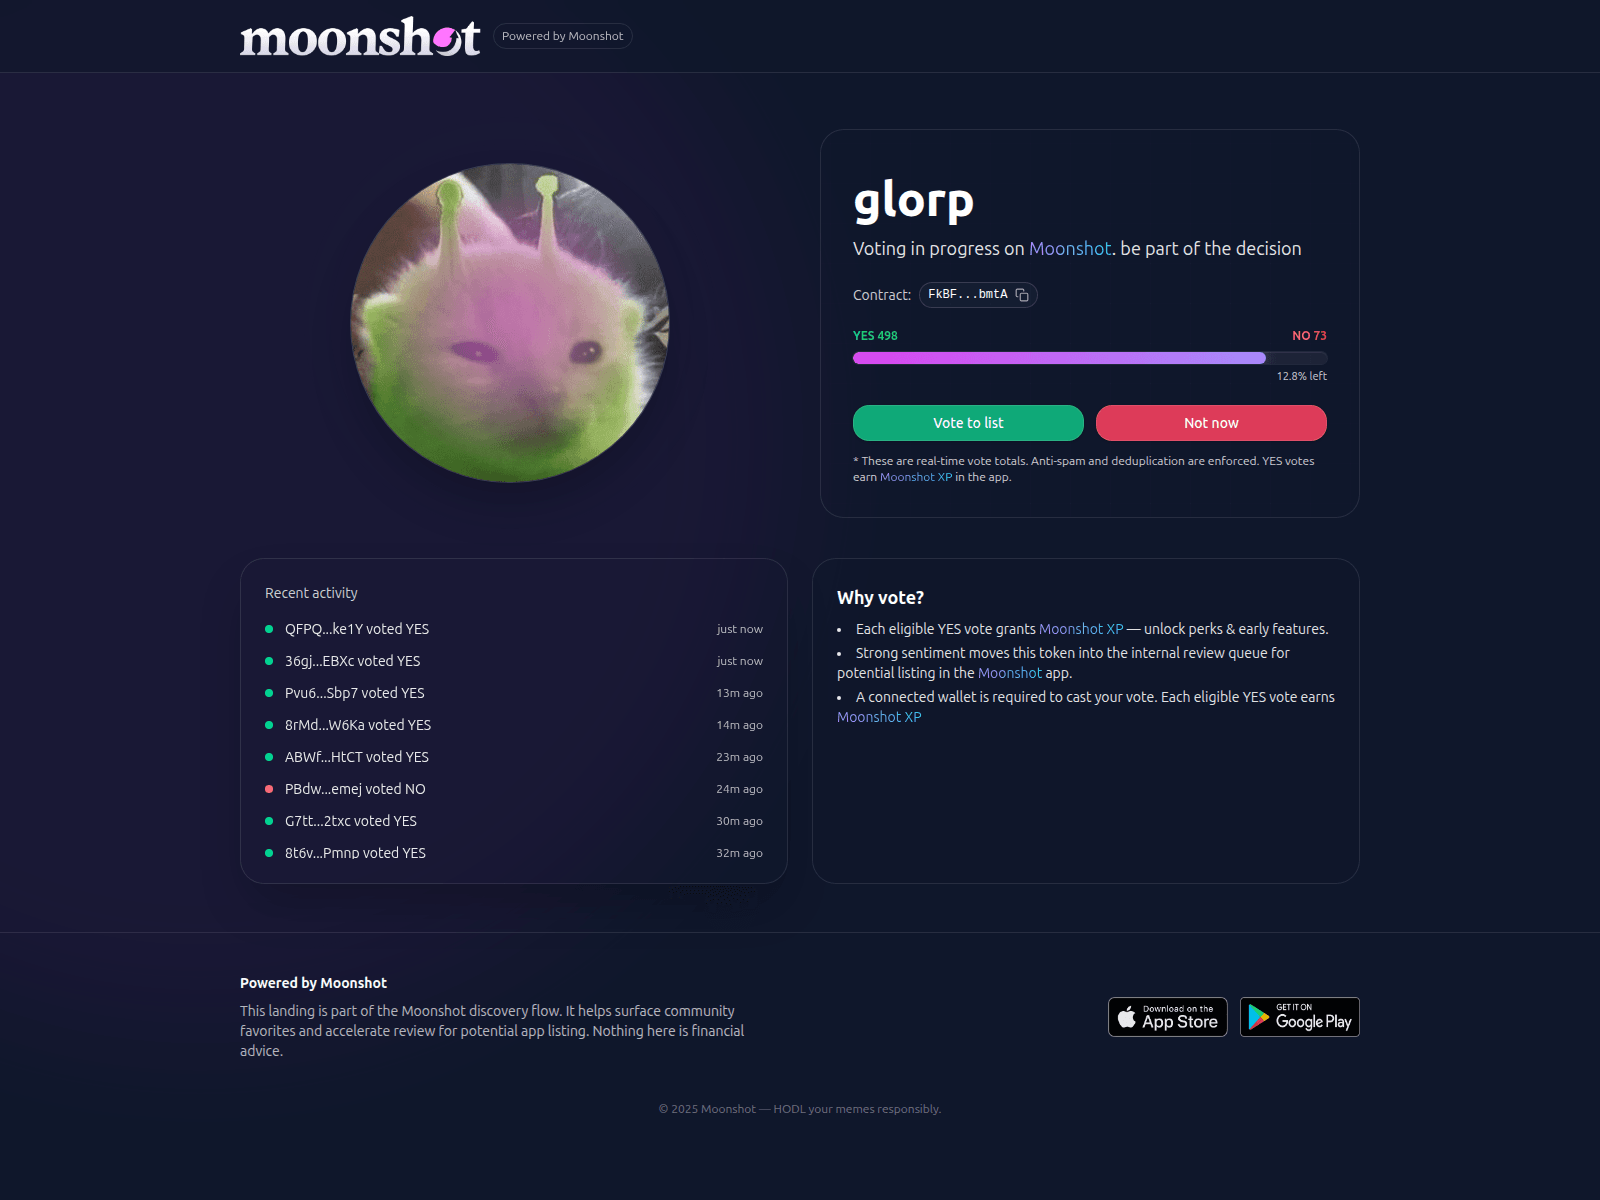

welovesolana.com
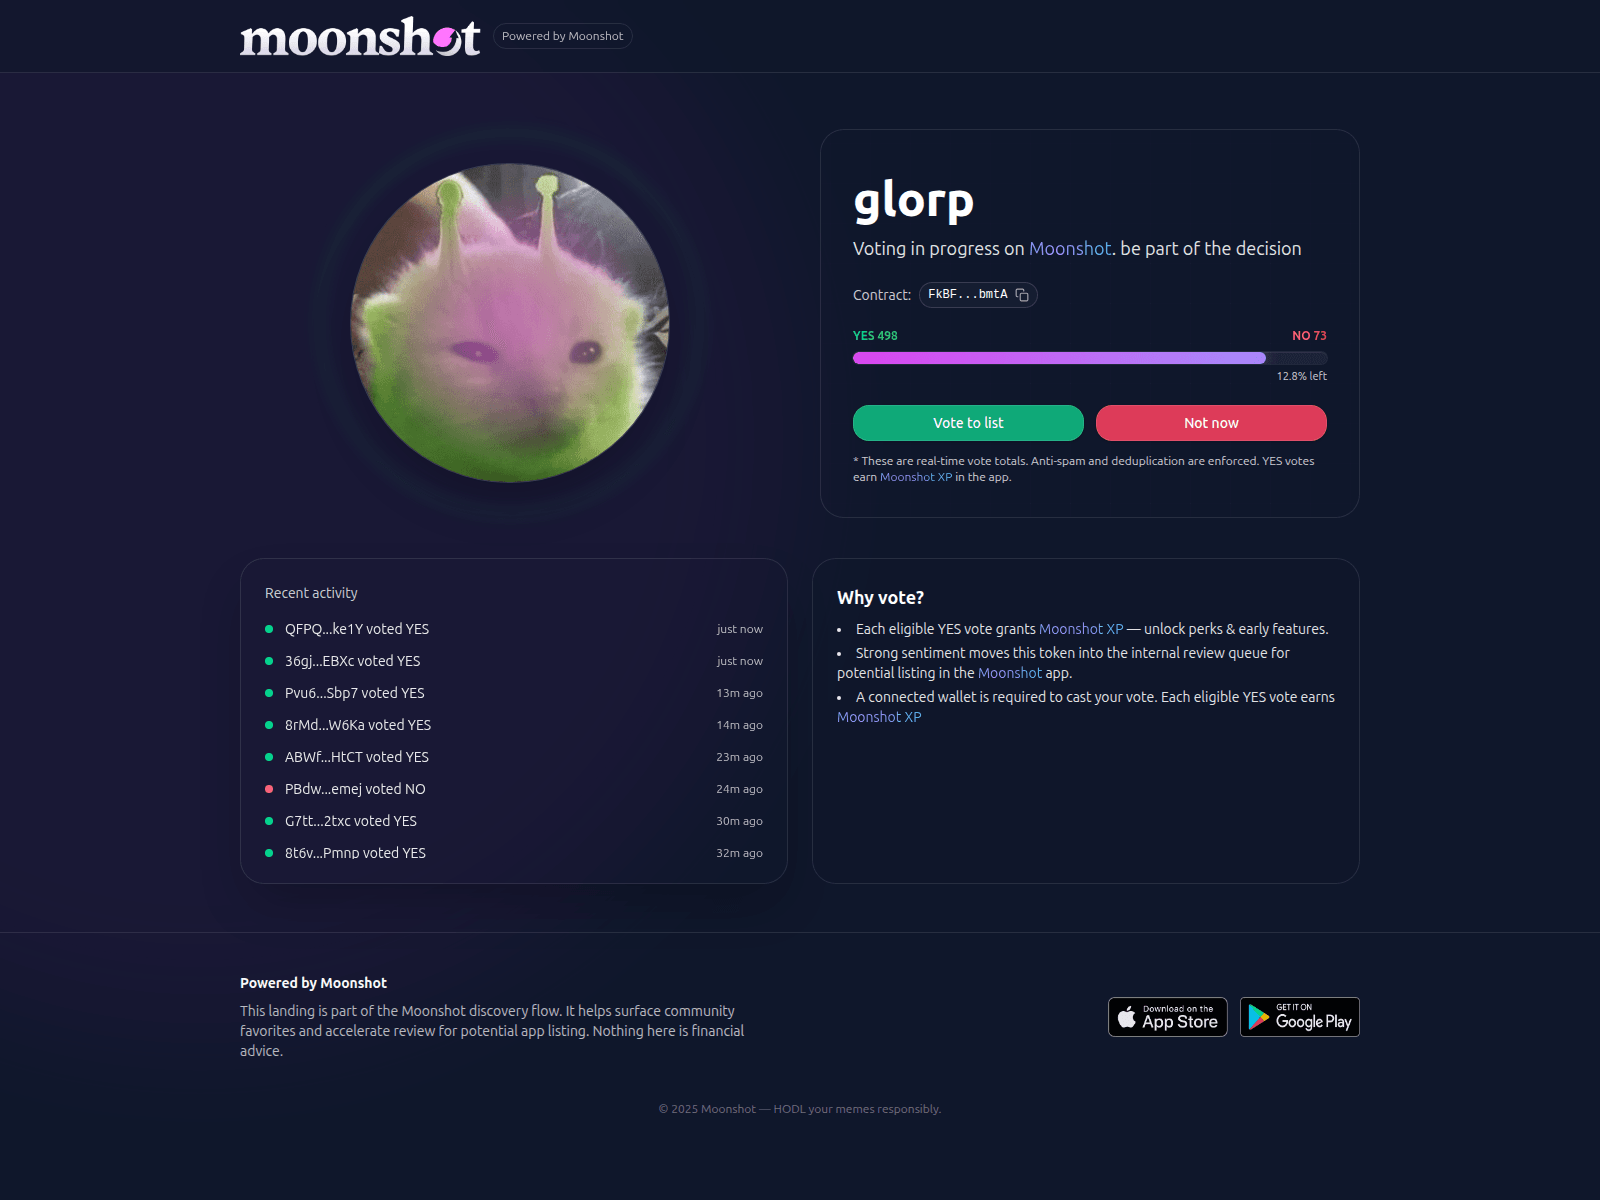
whatonsolana.com
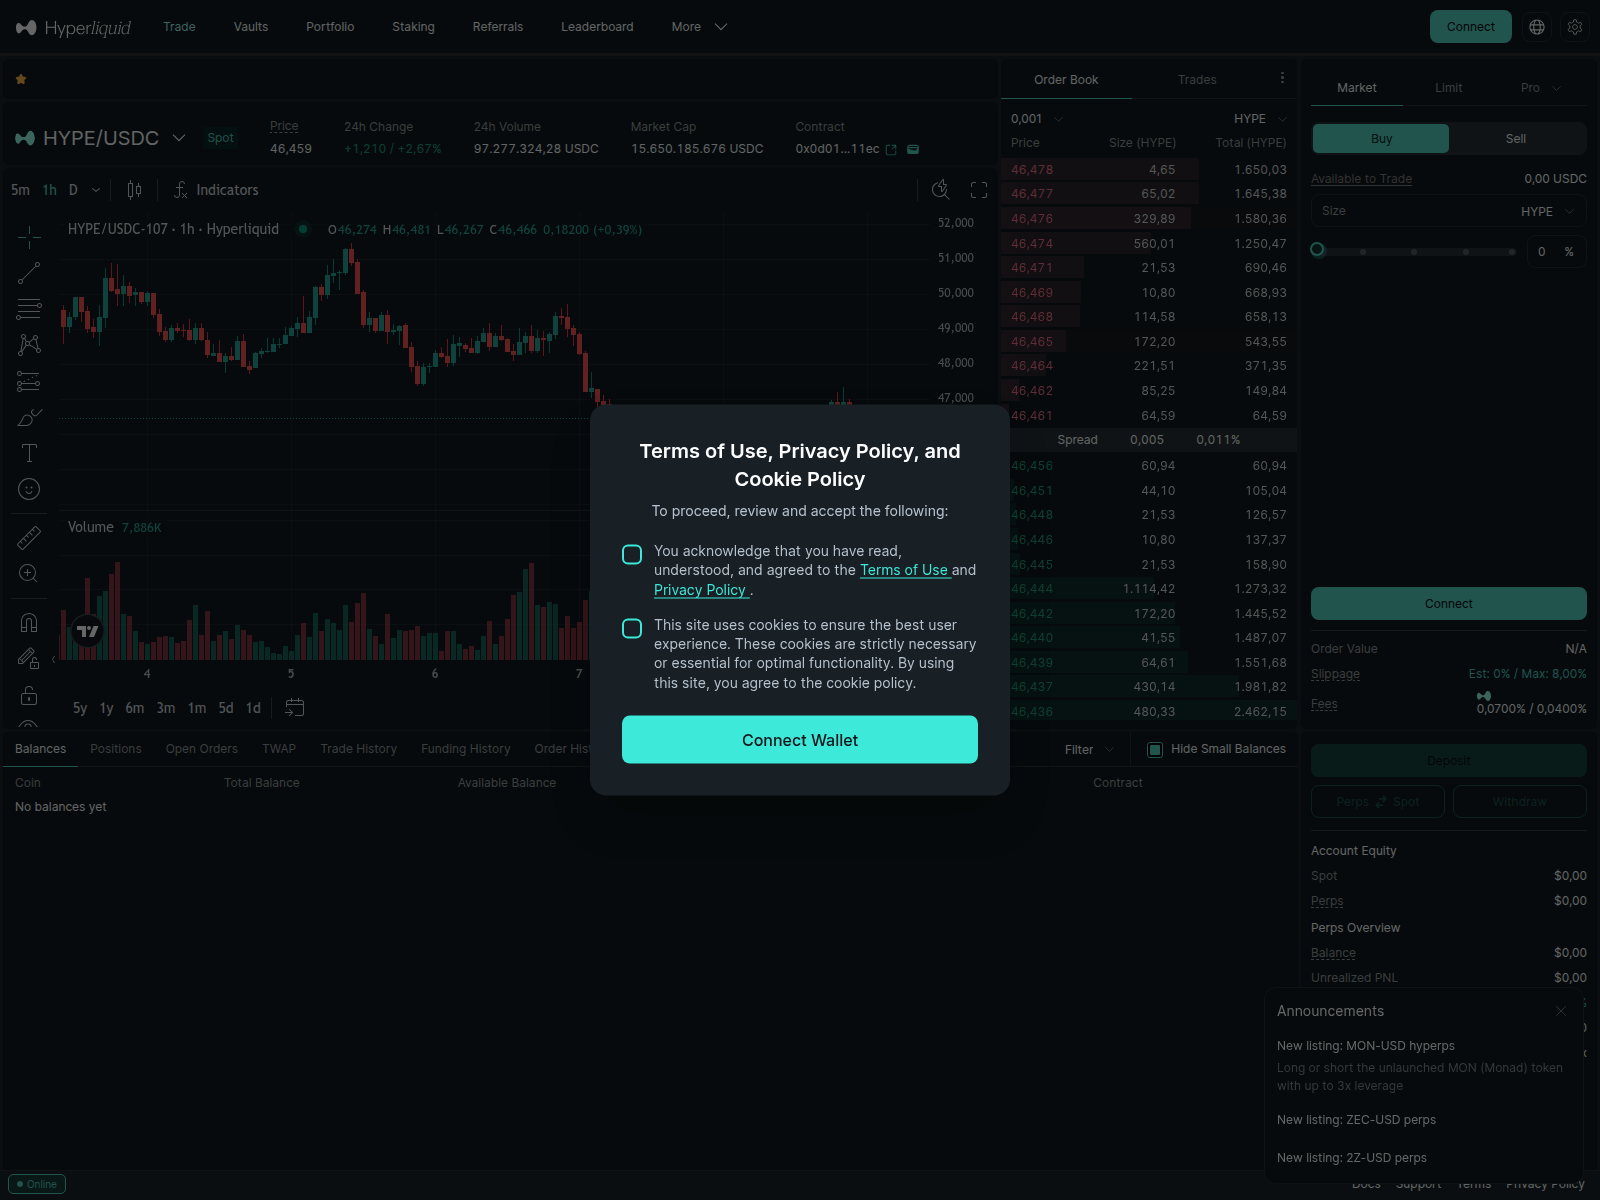
wwx-hyqerlipuid.com
xn--monshts-cx4ce.com

xn--moonshoo-eyb.net
xn--moonshot-03a.com
xn--moonshot-03a.net

xn--moonshot-o9c.net

xn--moonshts-03a.net

xn--moonshts-7d1d.com
xn--moonshts-j6c.net
3s3mtopgs-x.com

access-plasma.to
aio.sushi.us.com

allocation-hyperswap.com

aml-check.asia

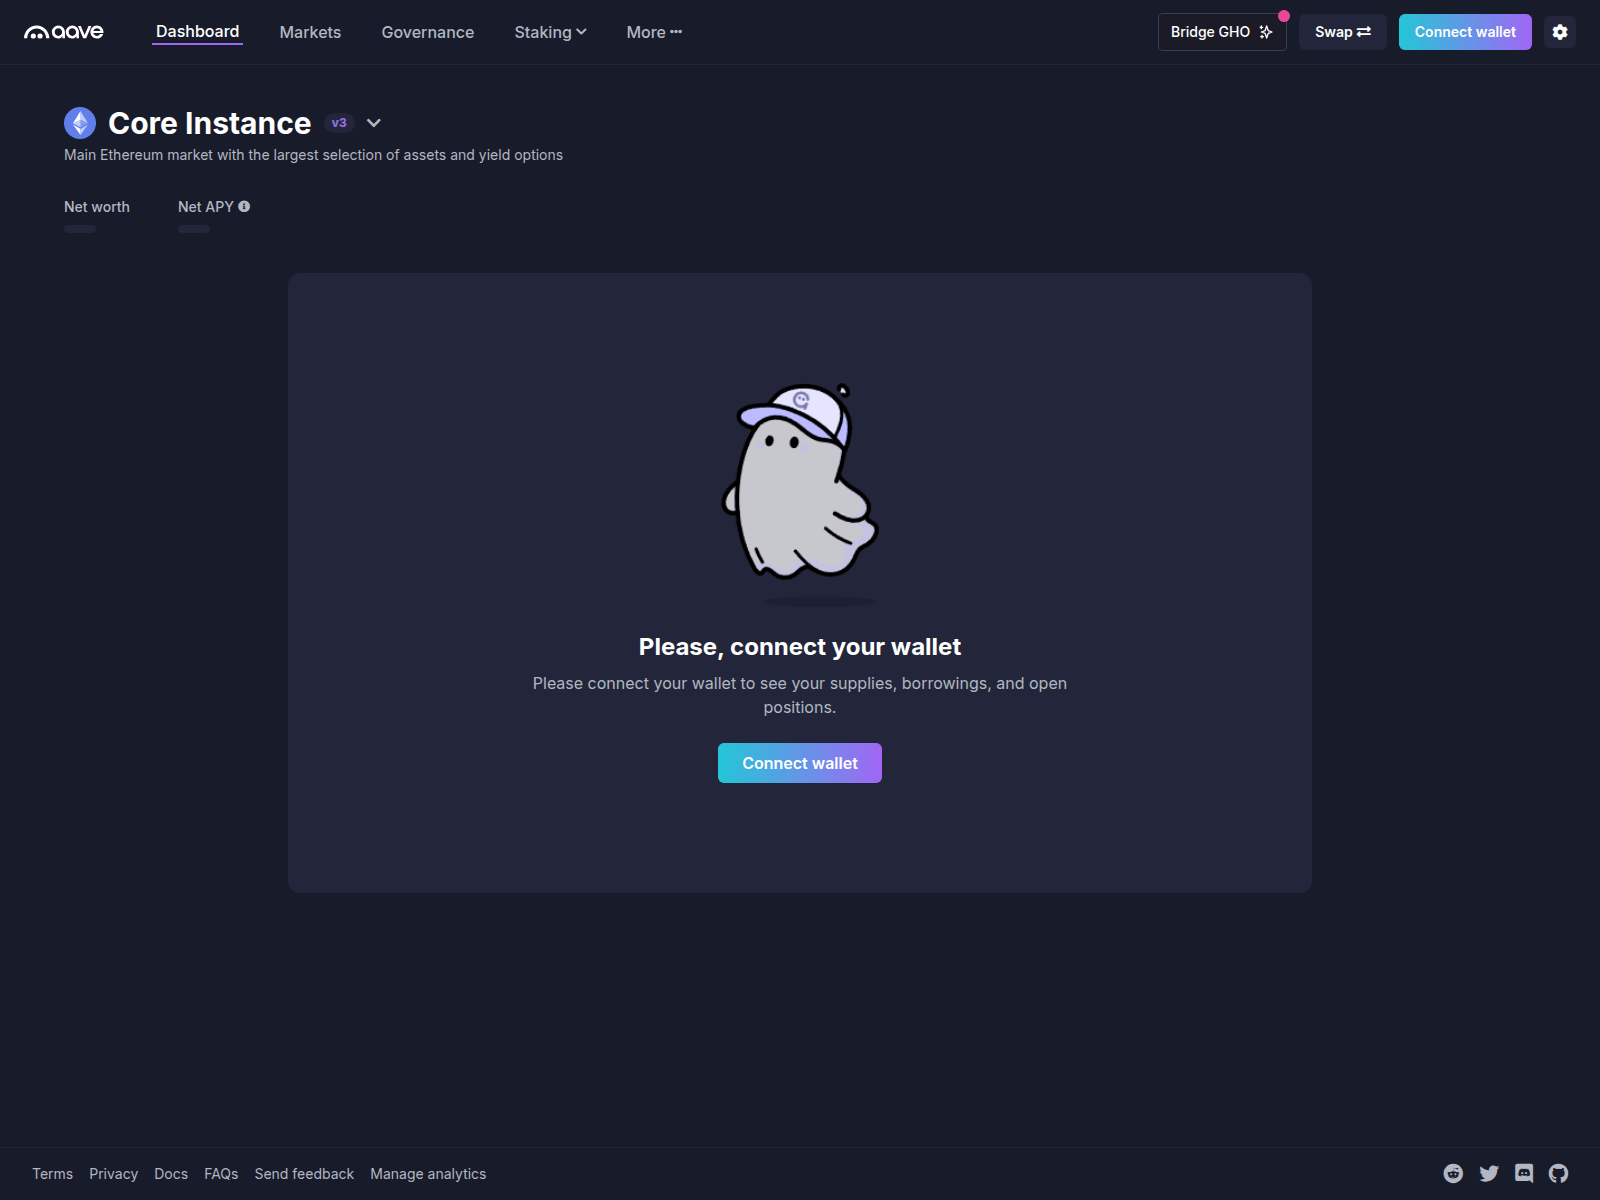
app-aave-launch-sv2.com
app-hyper-liquid.com

authappresolverr.xyz

aviir.space

bitenadogs.cc

blockdog.network

bonkfam.com

bonkfarm.com

bonksfarm.com

bounty-internal.xyz
claim-tokabu.com

claimblockdag.network
claims-bonk.com

cryptomus.forum

cryptospeed.network

cryptospeed.online
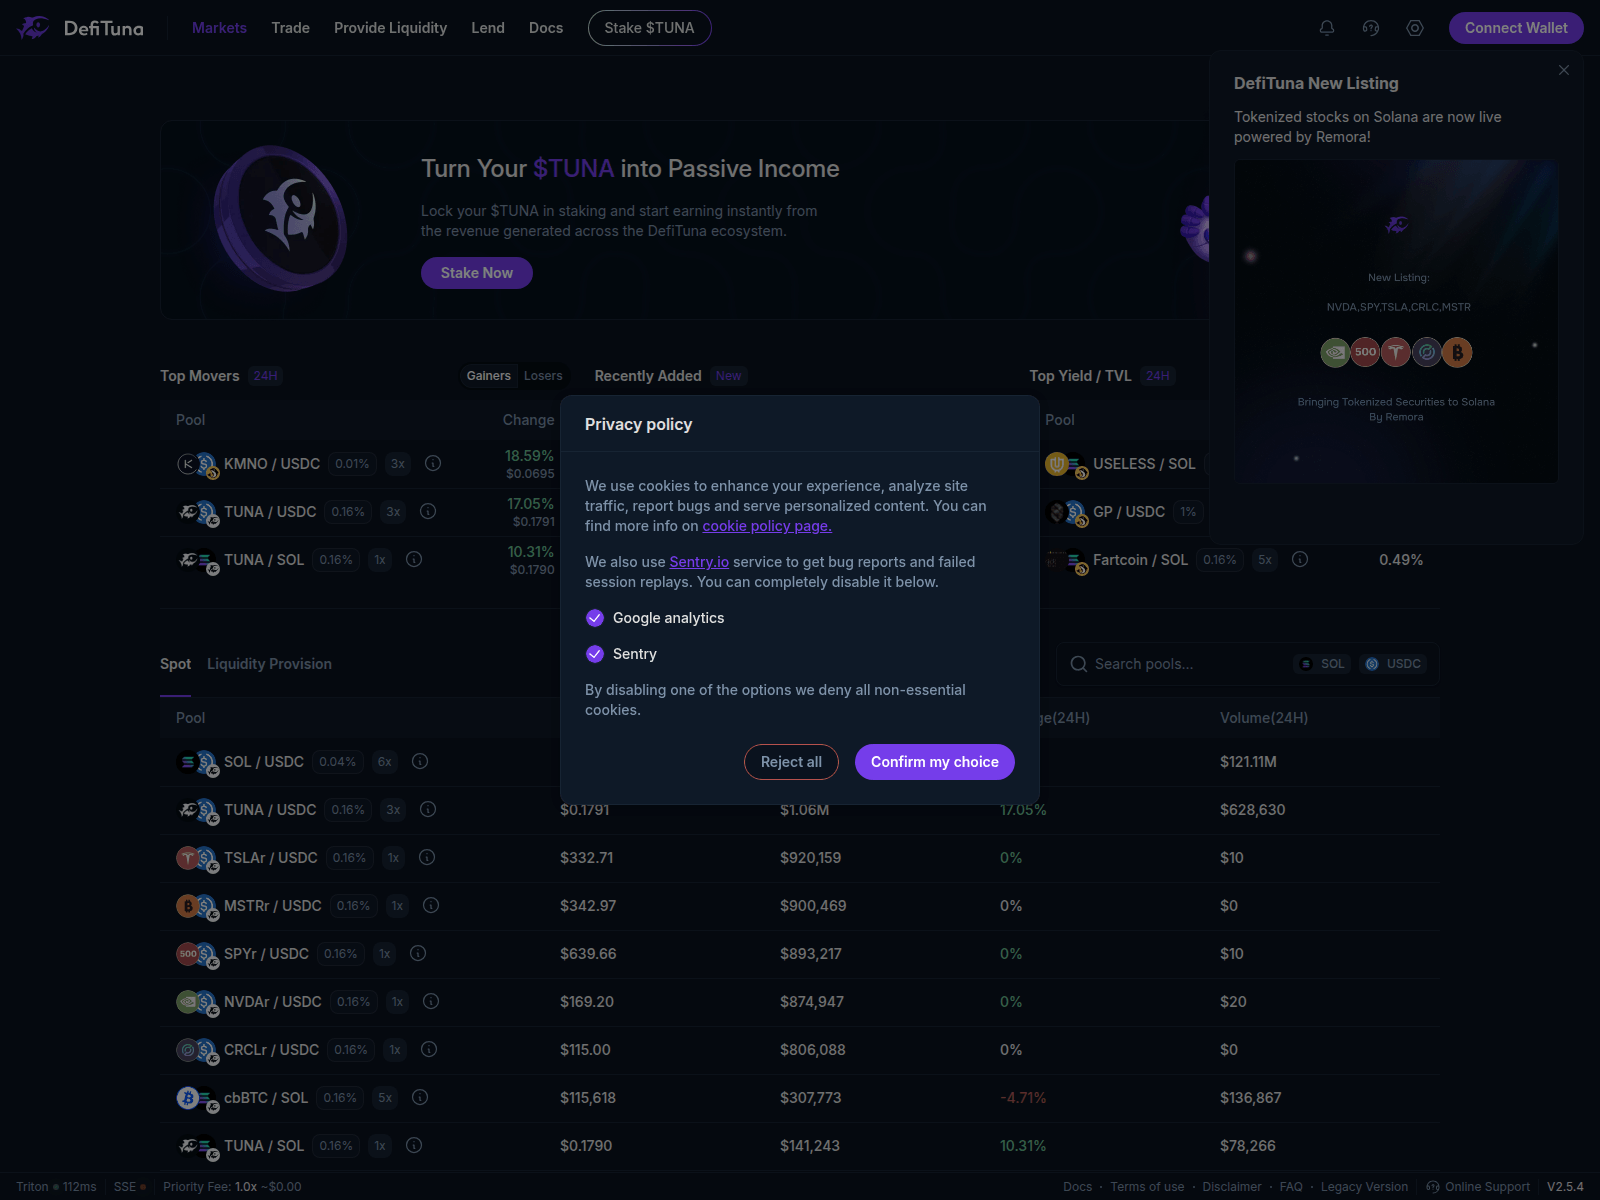
defituna.exchange

defituna.finance
diagnosticnode.co
e627.usdcbsc.cc

earn-pol.com

earnpol.org
easycenterr107.store
errorblockdag.network

ethincnerator.fun
ethincnerator.lol

gainpol.org

huuaq.com

hyperliquid.com-prod-online-cdn-portal.cloud

liquity-bounty.com
lsol.top

magiceden.net.offer-proposal.com

miner.blockdog.network

molangsolana.com

multiplier-benqi.com
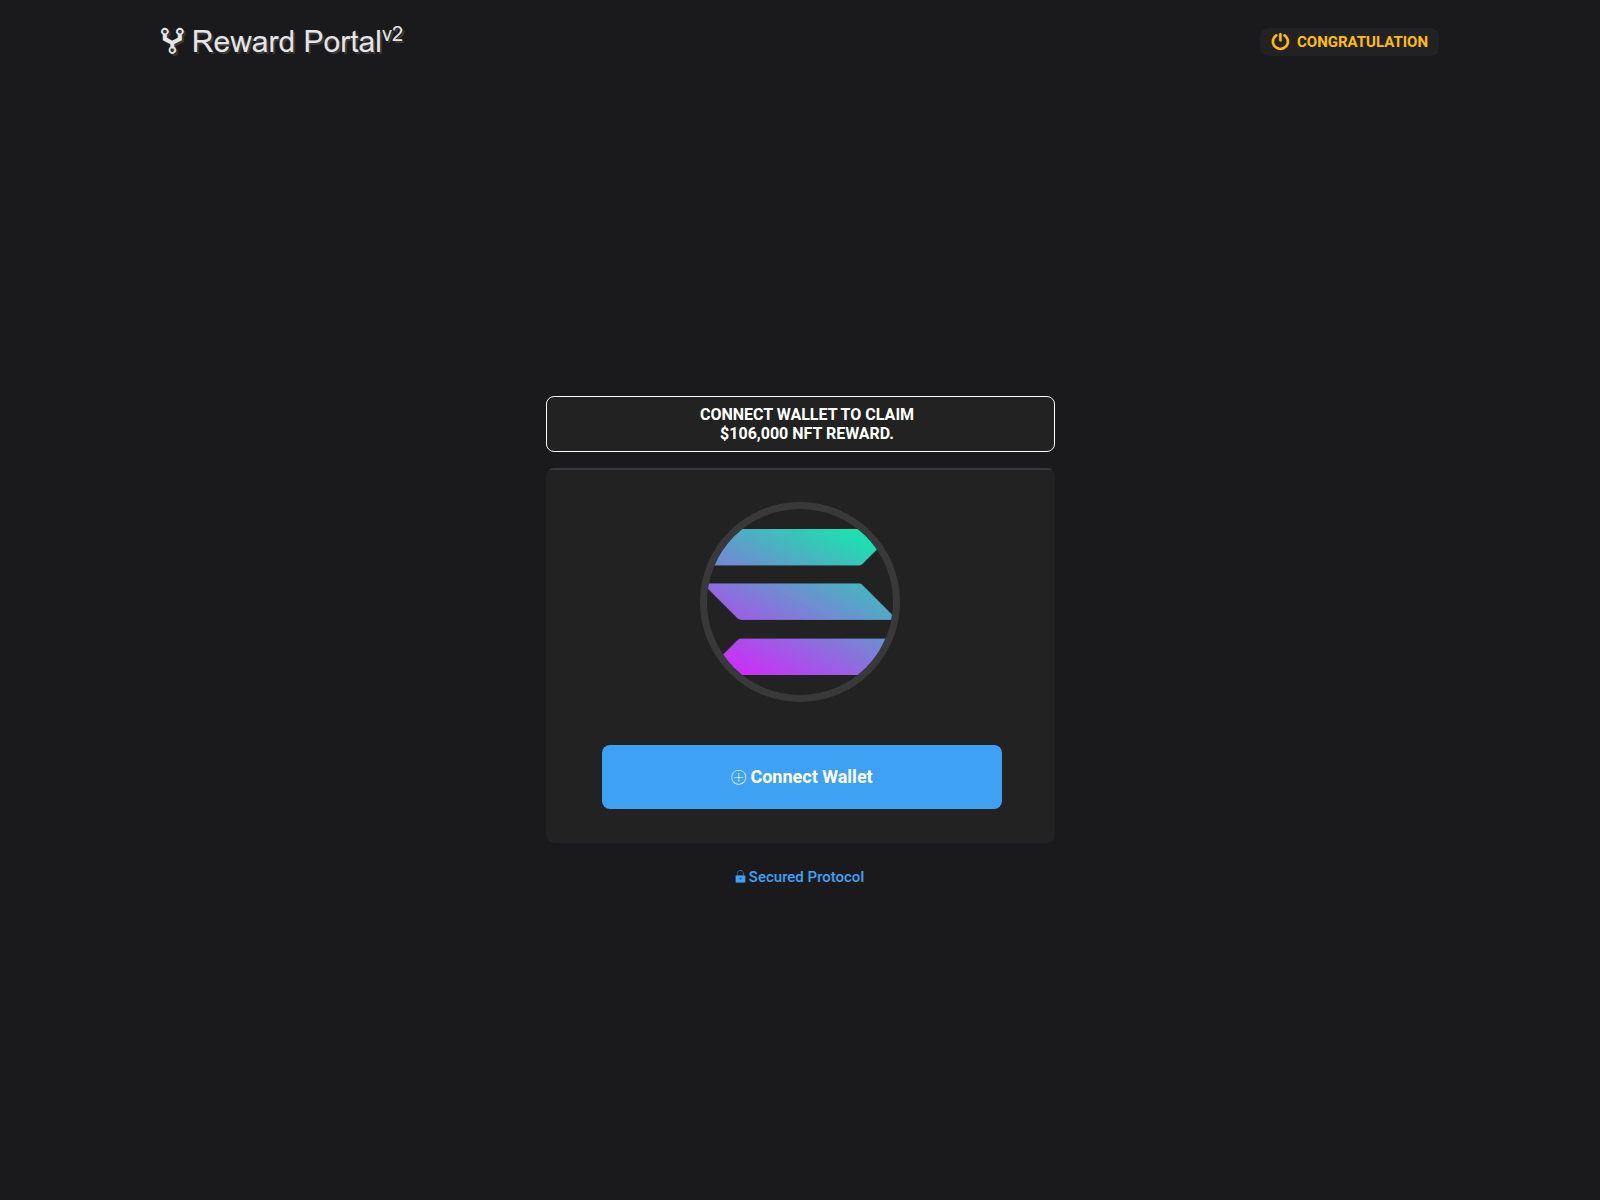
nsol.top
oavc.app

onchain-crypto-gc.cc
onchainscore.live

onchainscores.site

onefootballclub.website
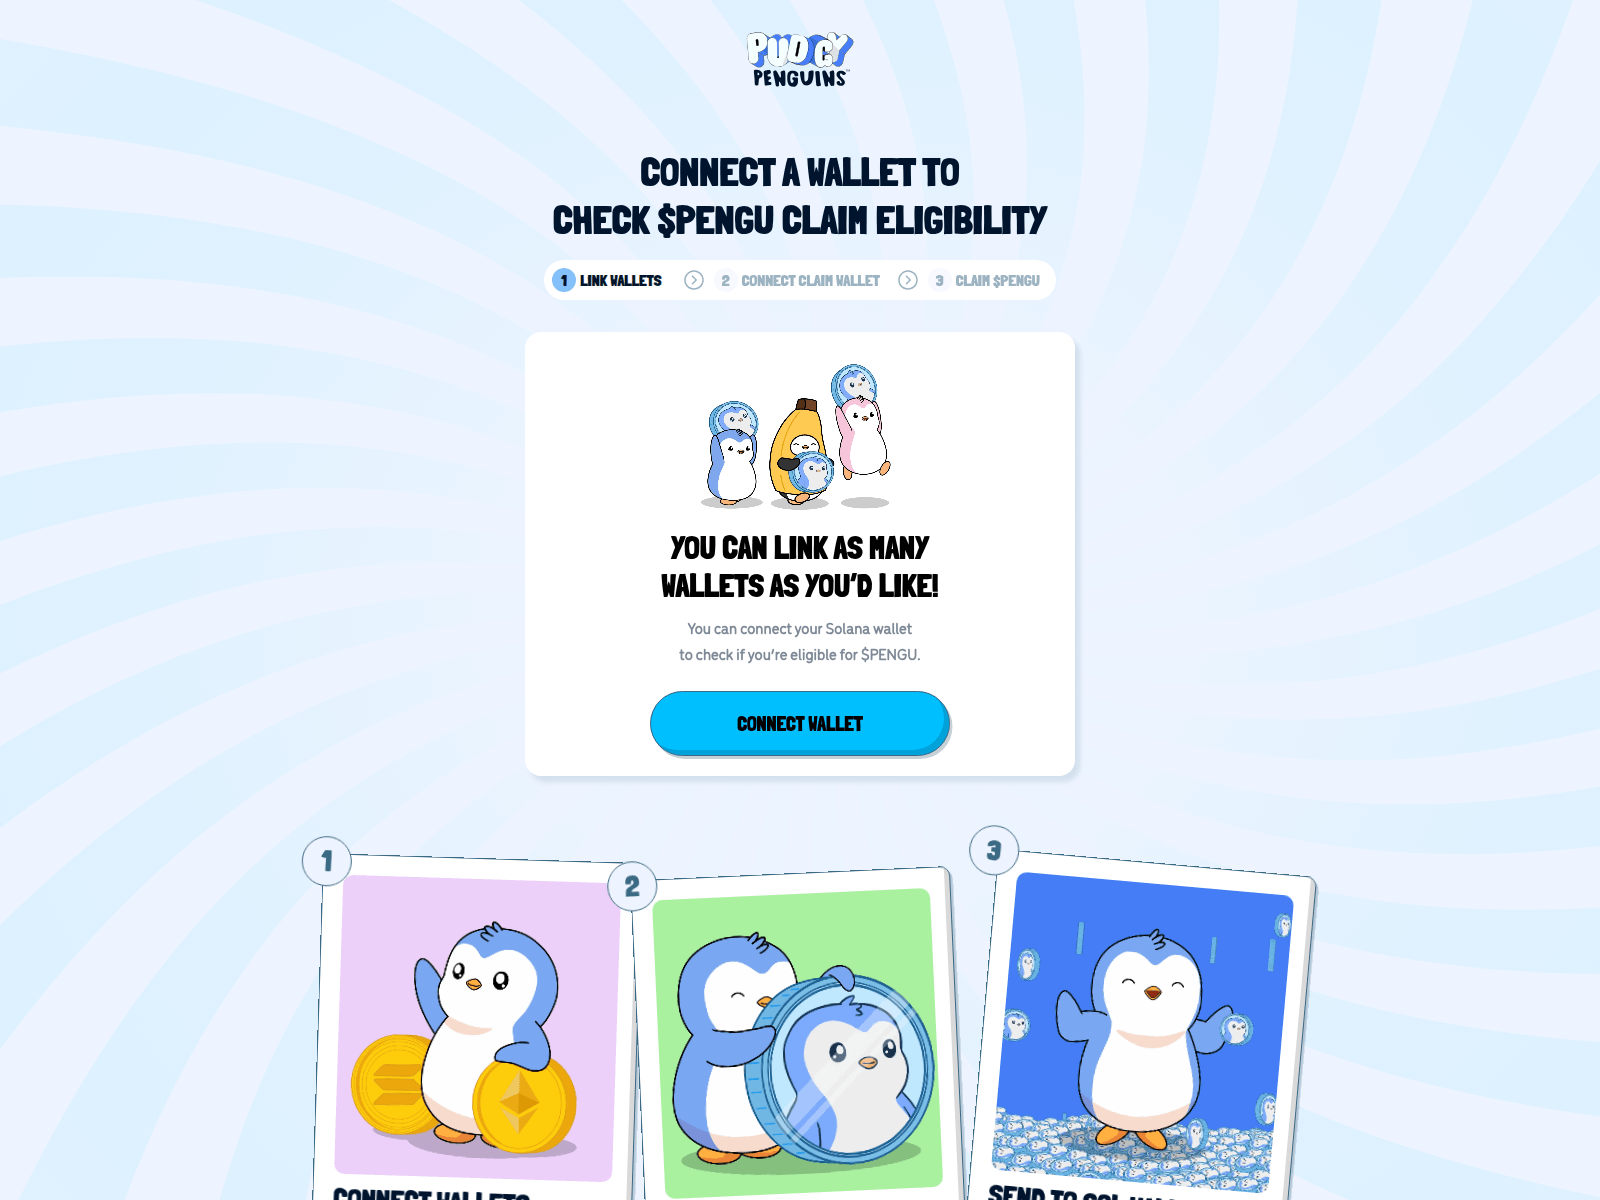
pengu.onsol.pro

pengusol-drop.fun

polymarket.validations.center
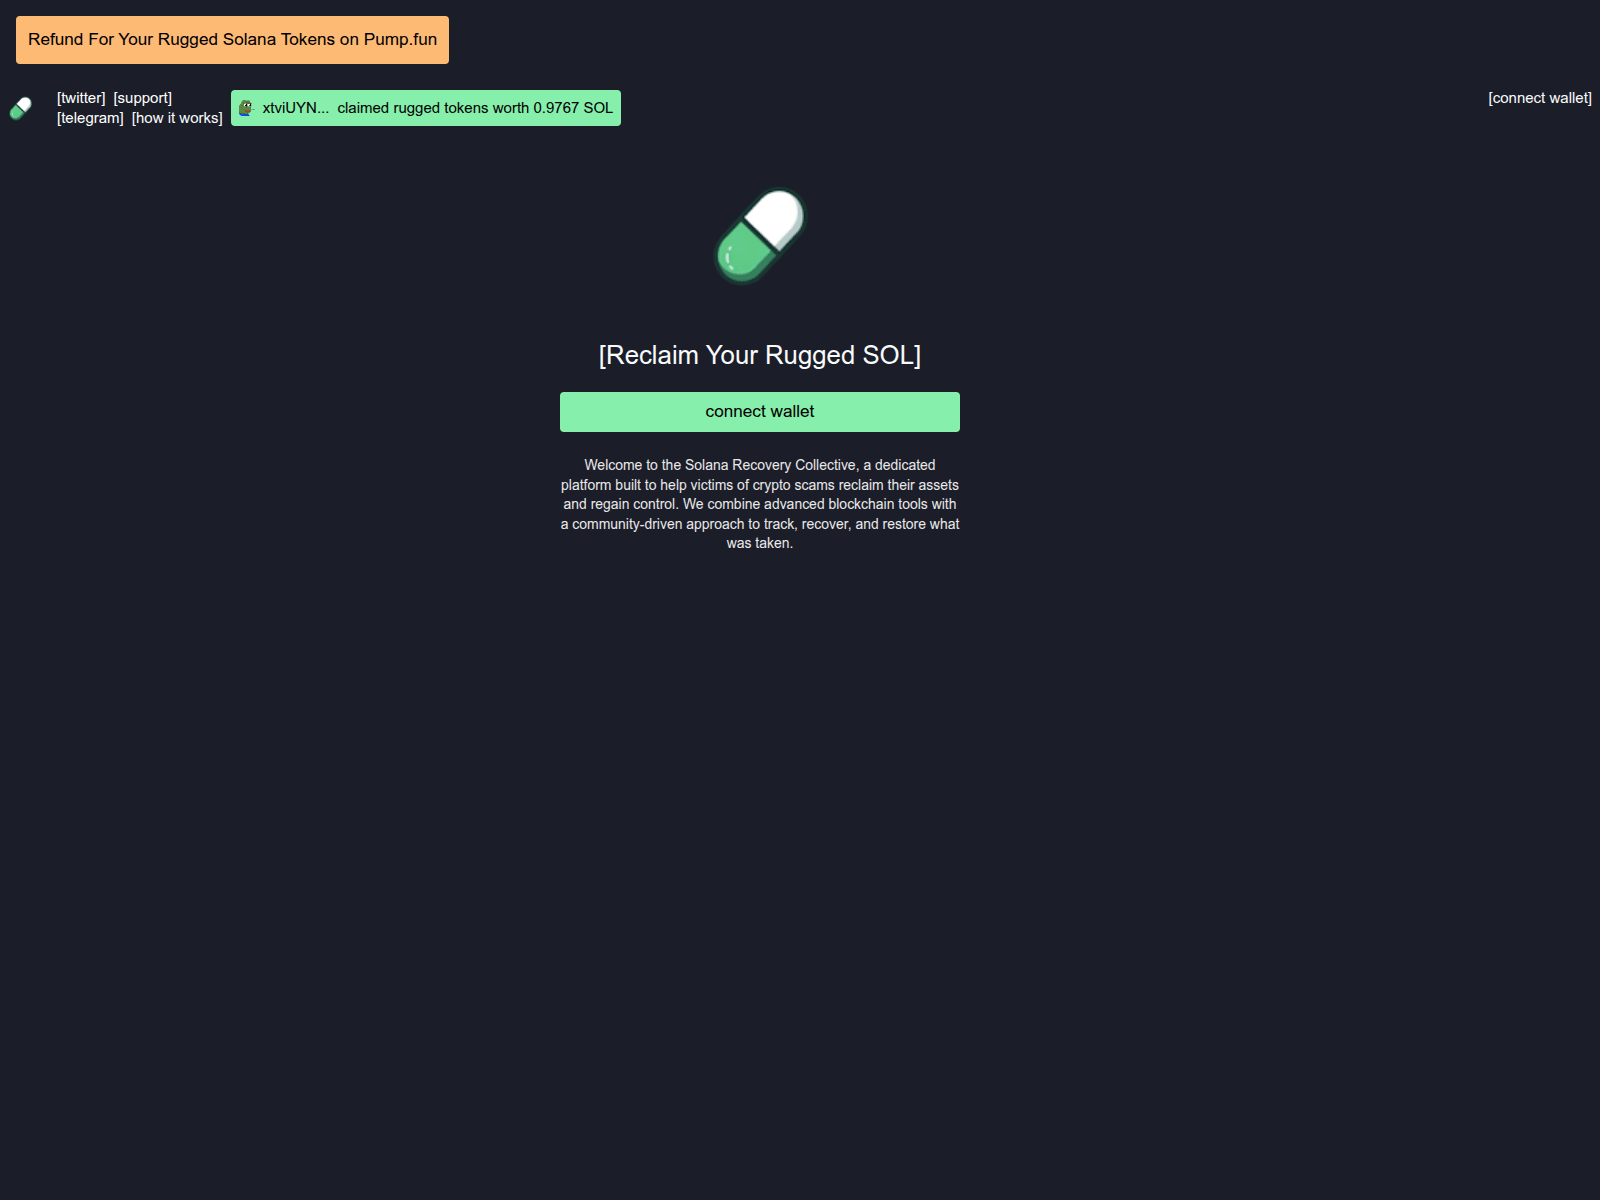
pumpfun-refundsol.web.app
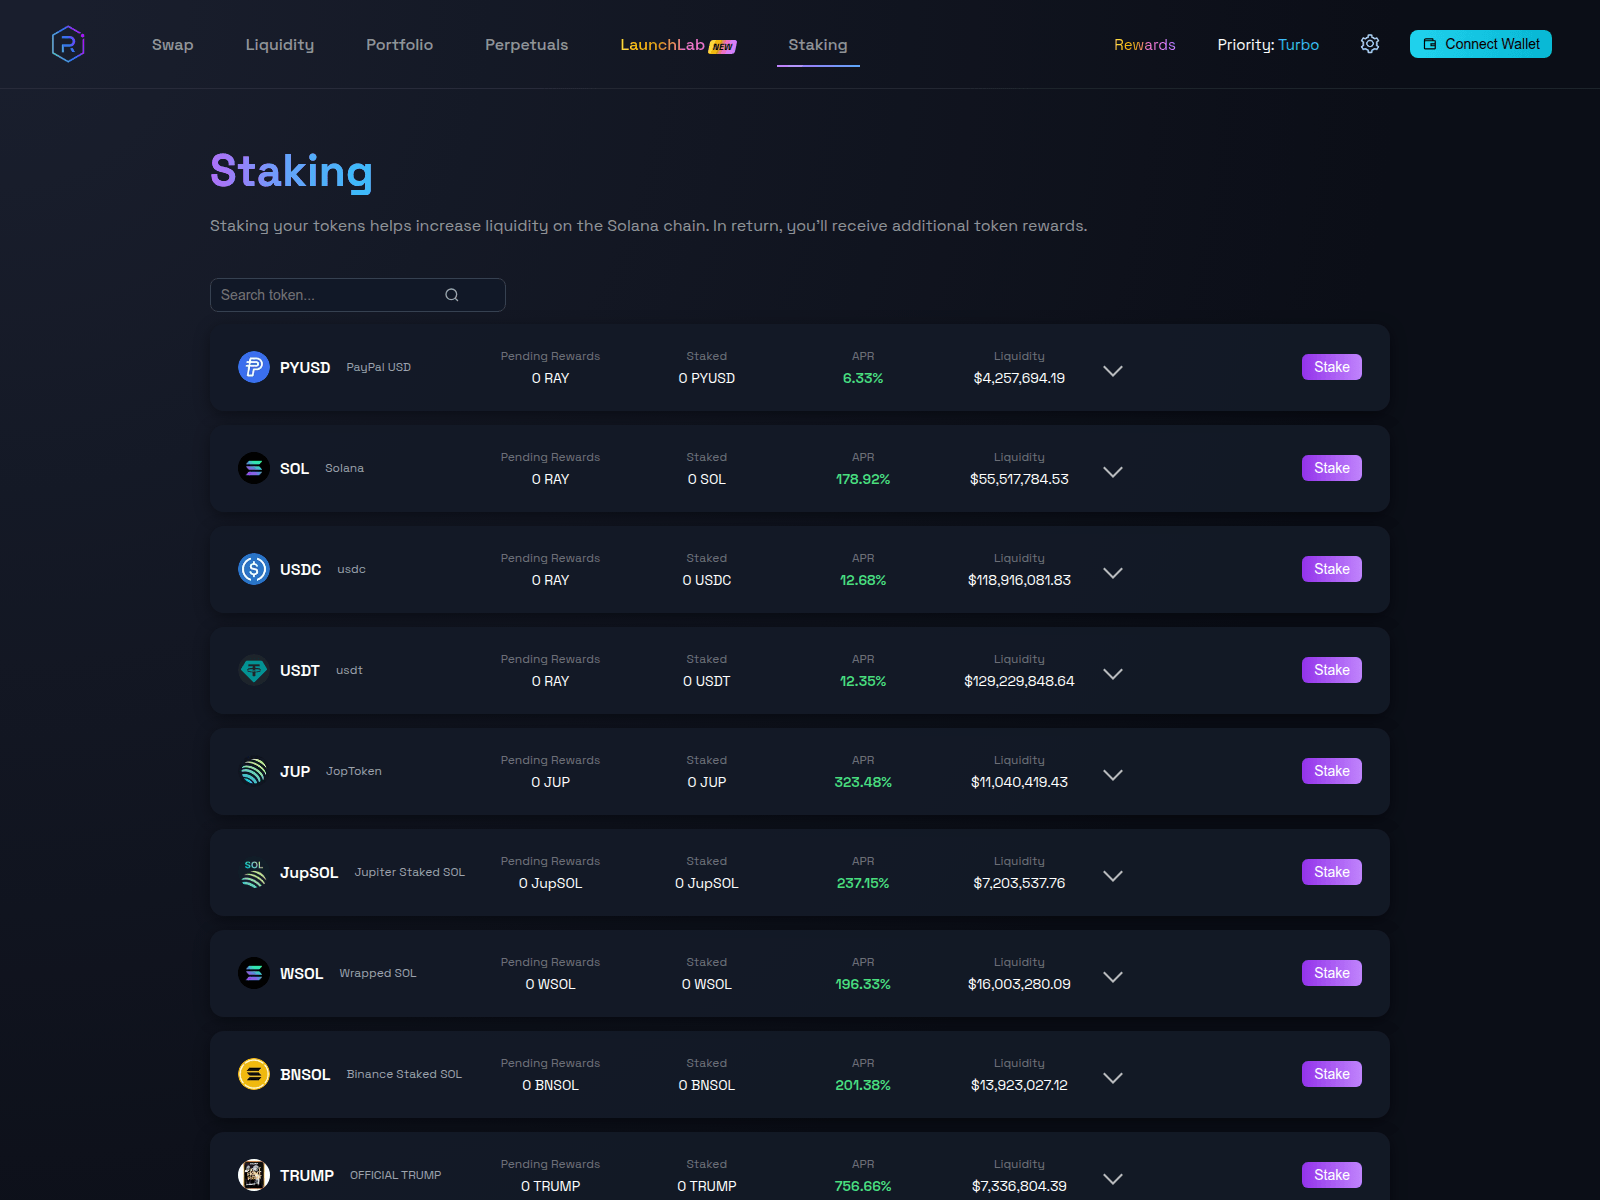
ray-dium.baby

receivepol.com

rpc.blockdog.network
rsxcf.com
rziuh.com

snekevent.site
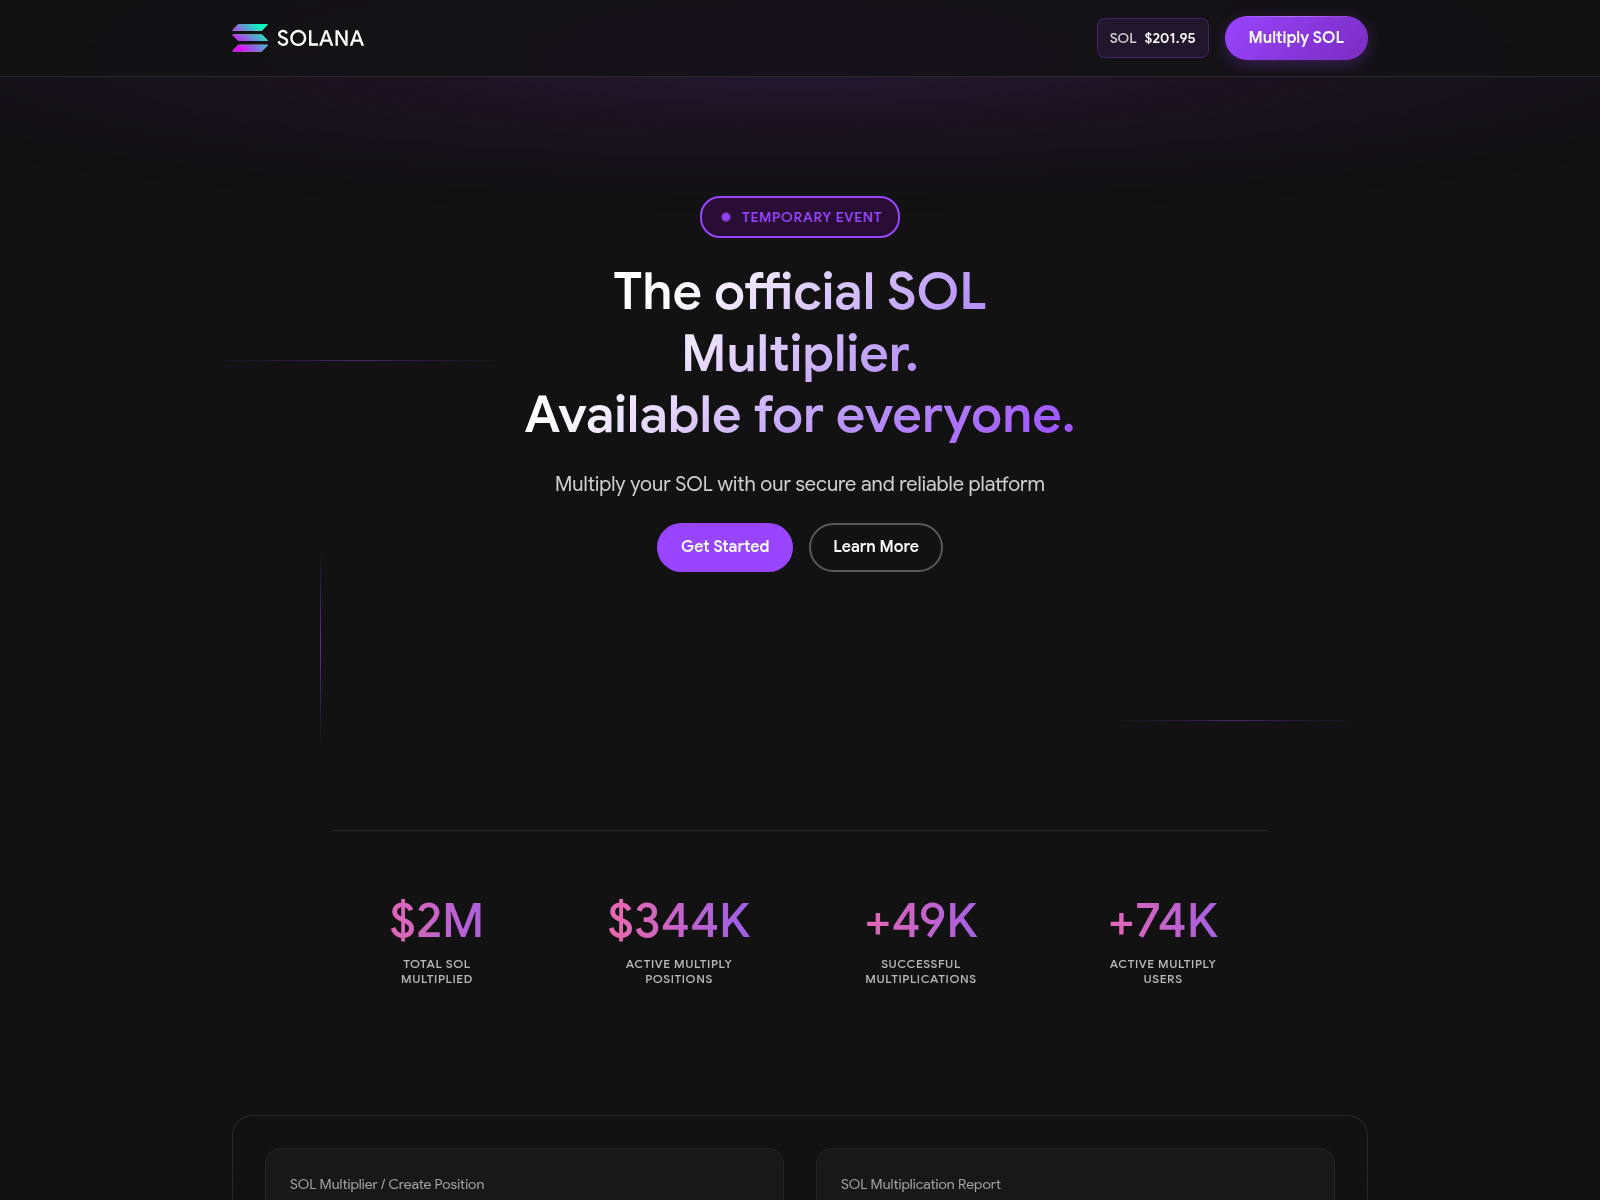
sol-activity.company

sol-claims.info

sol-meme.xyz

solana-paws.com

solanasewer.com

solbiscuits.vip

solland.icu
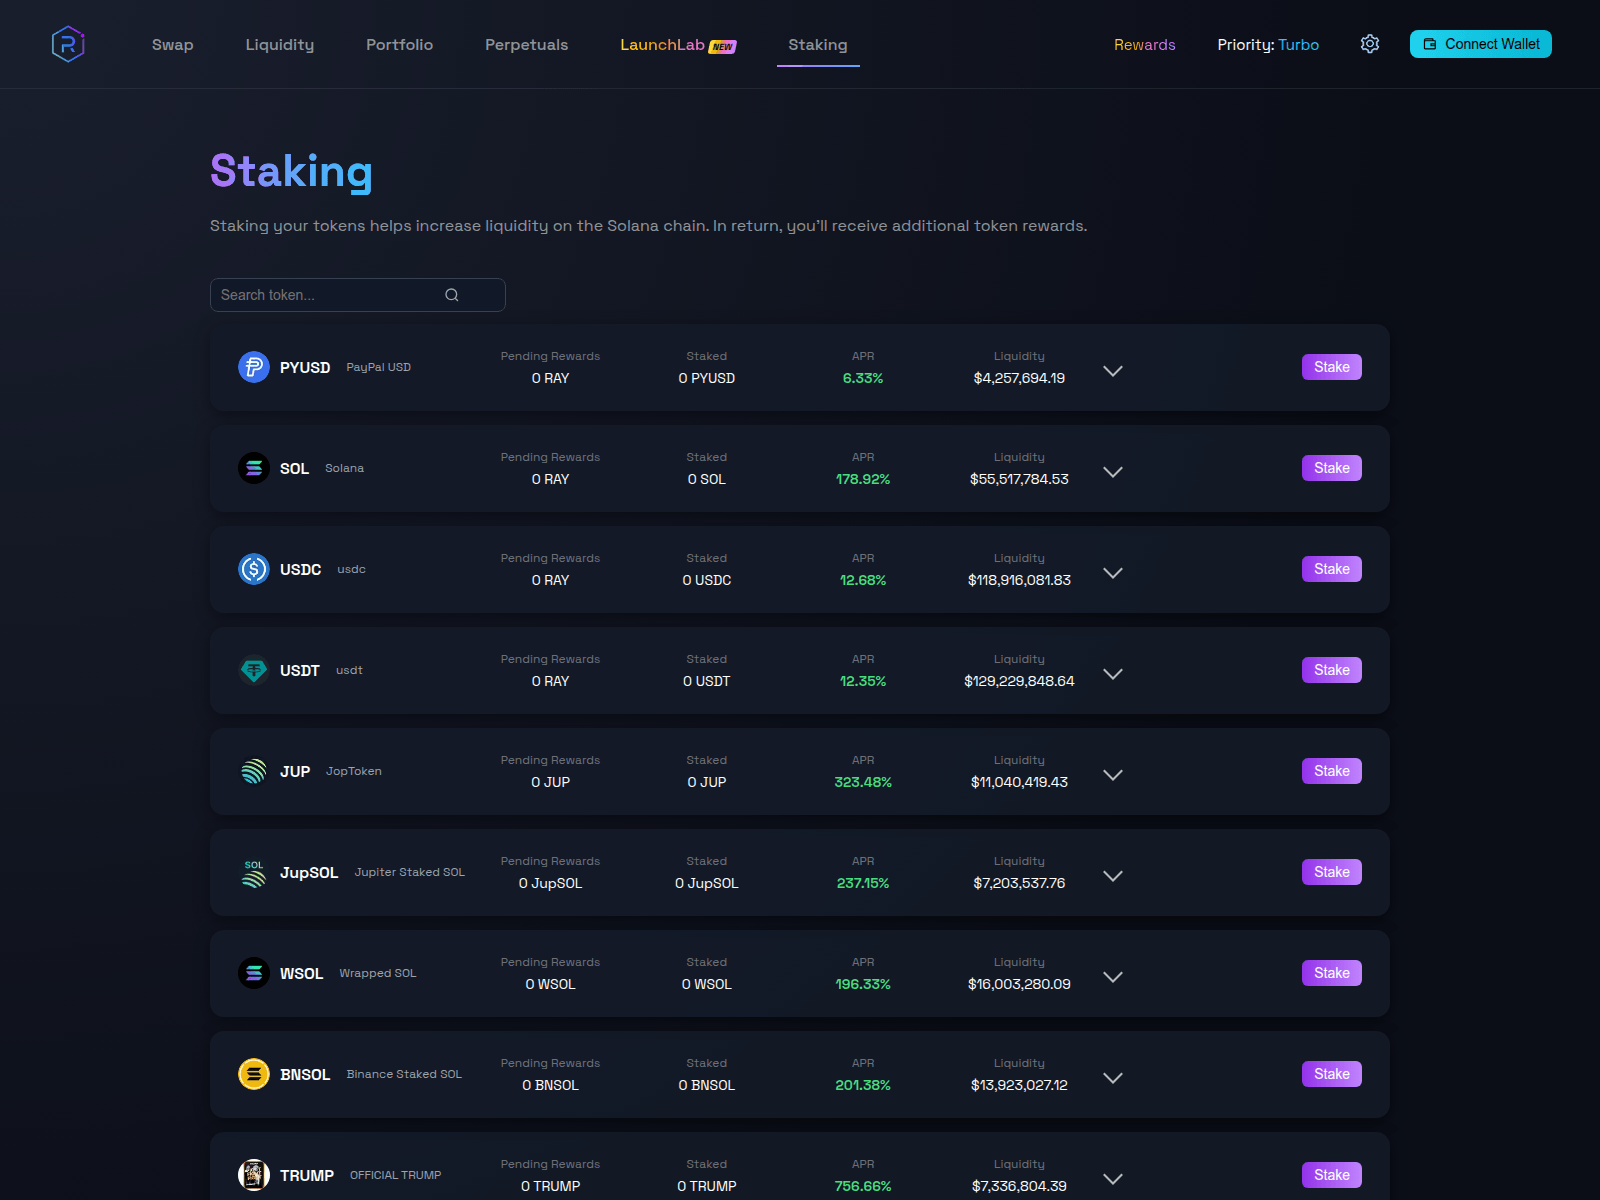
stake.raydium.cash

suchiswap.info

tokenversedogs.cc

uranuscoins.net

urbanshopp021.shop
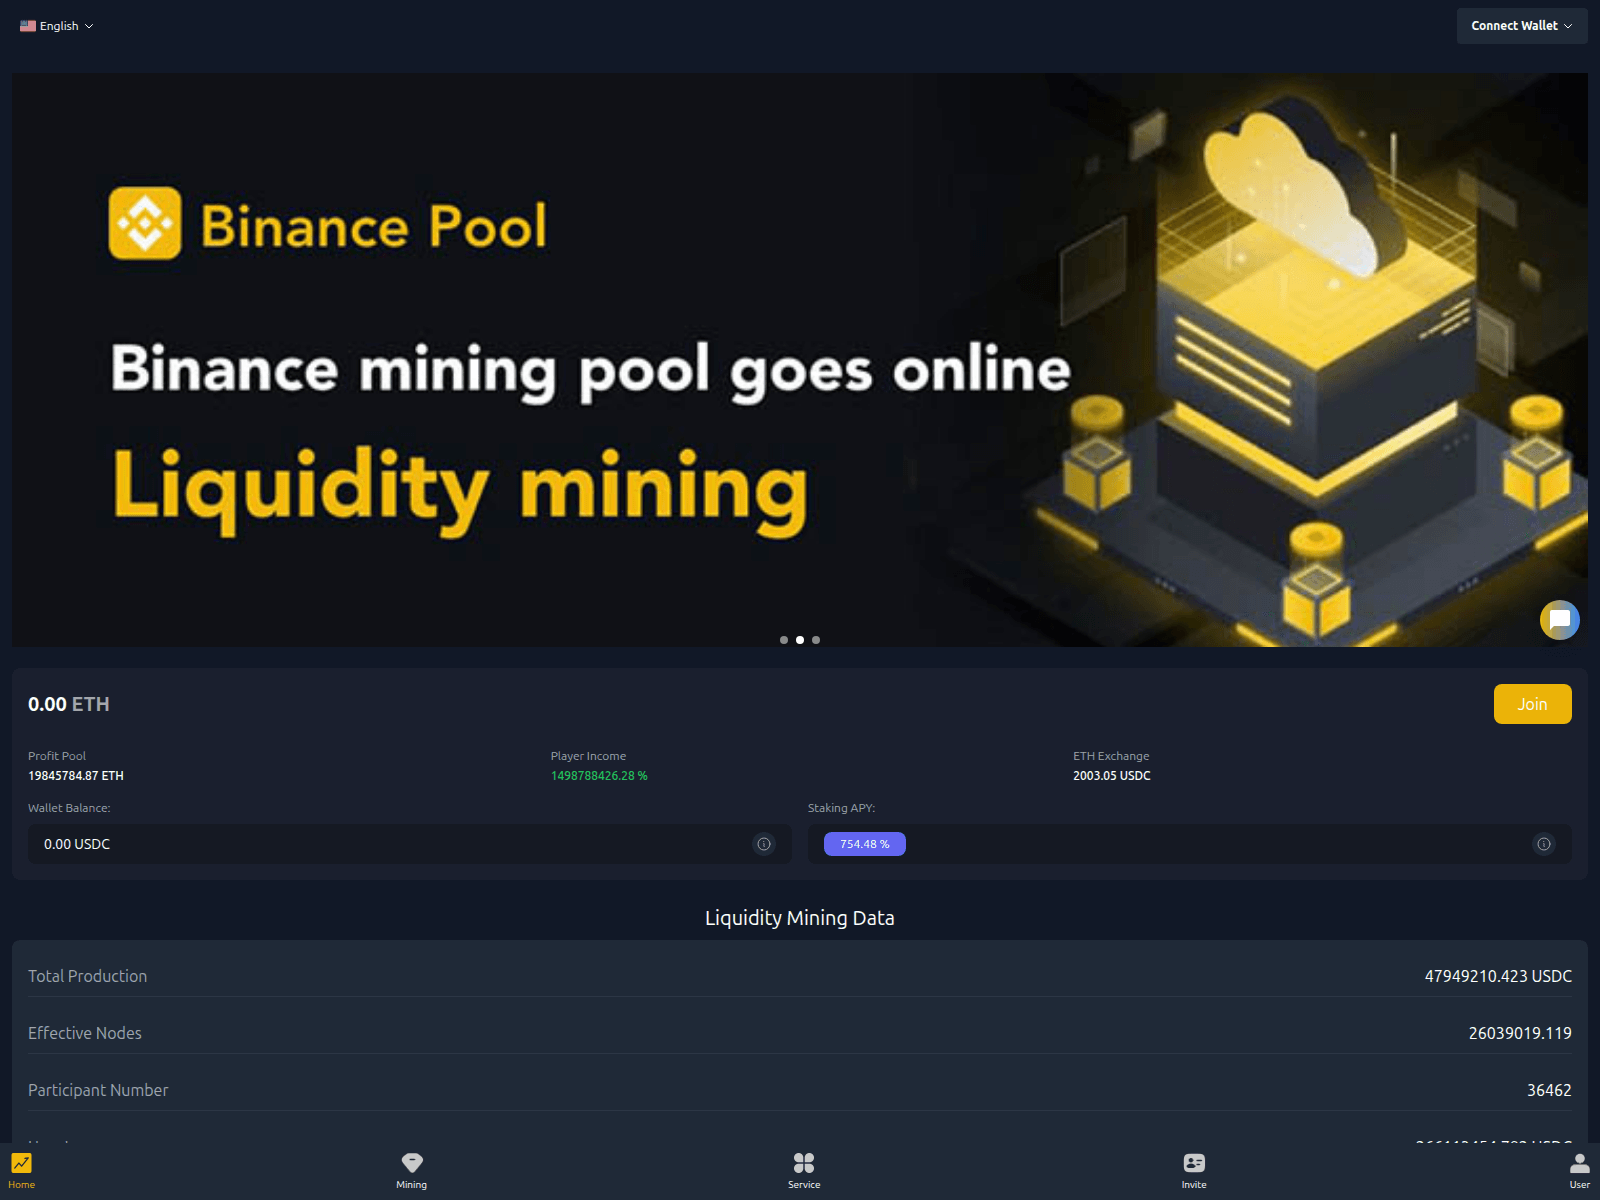
usdc.sundapp.vip

v1.token2049.cyou
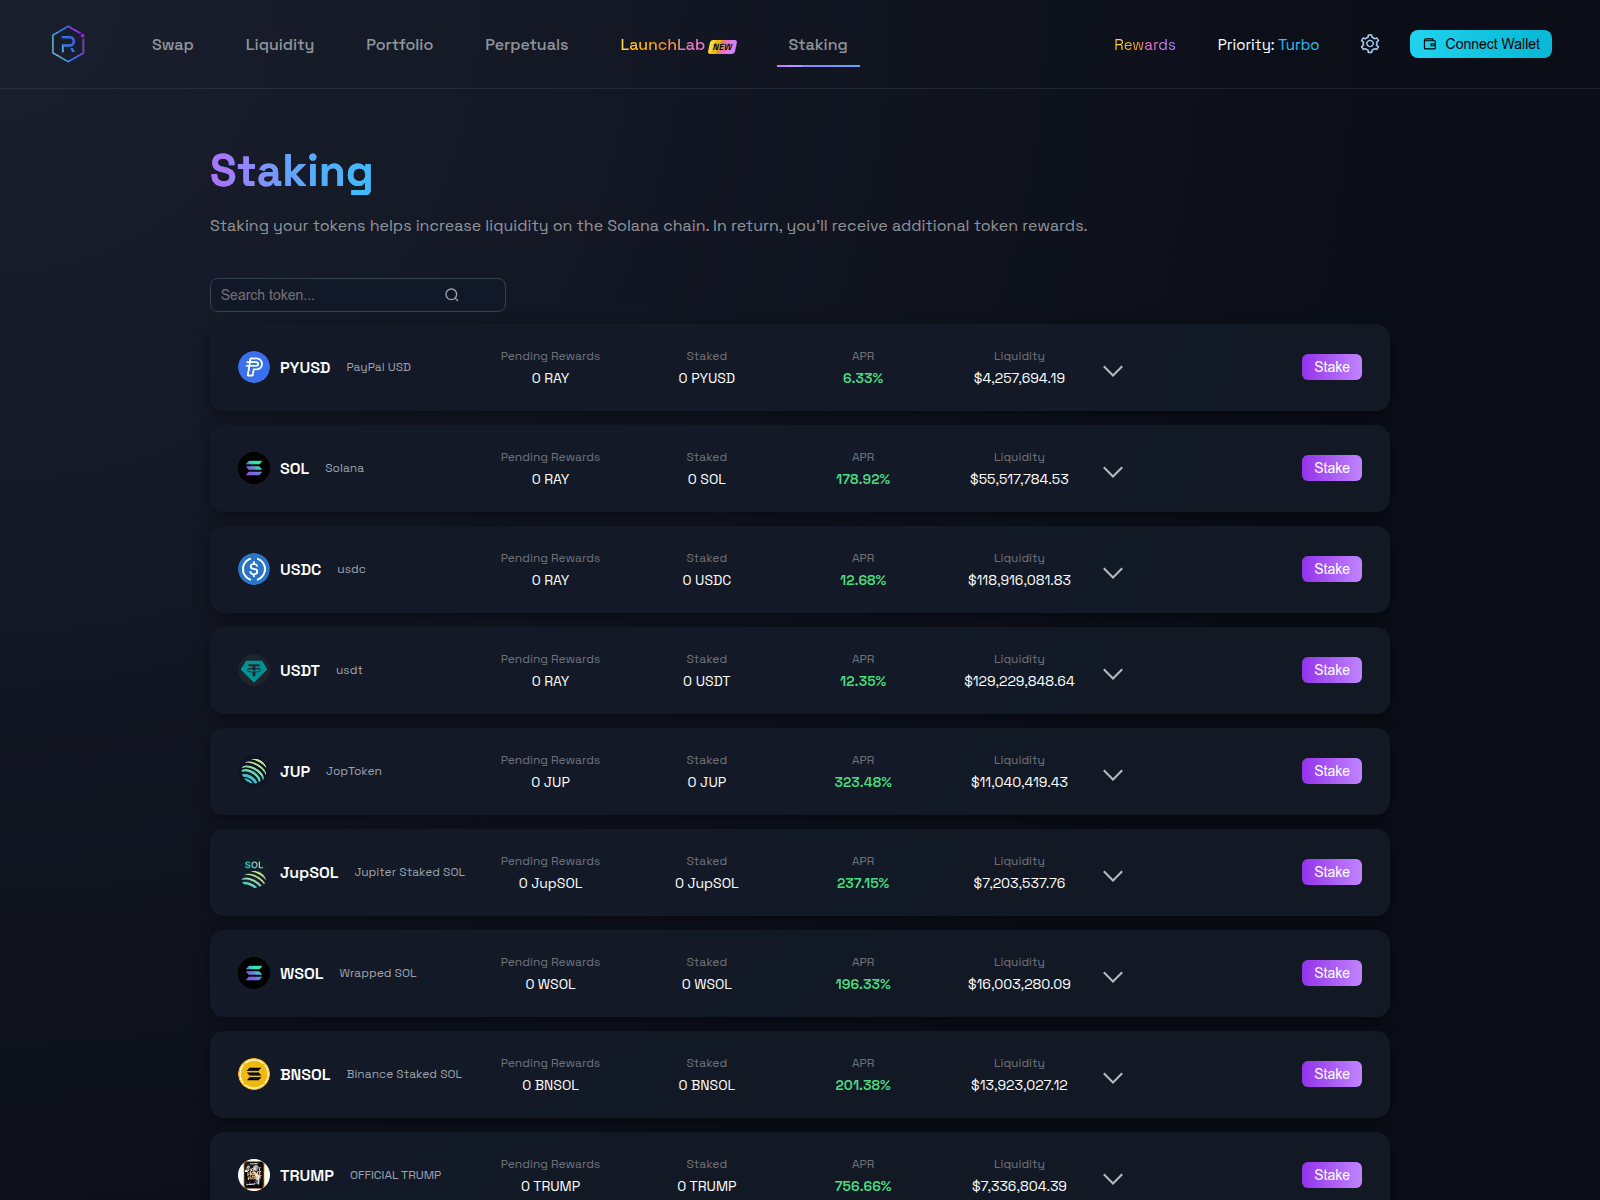
webdisk.raydium.mom

wr.jcy100.com
xn--monsho-8kb.com
xn--moonshot-dxb.com
yxraq.com
zestycenterr498.shop

aio.sushistakes.info

allocation-sperax.com

asdasdasd-cpy.pages.dev

bitgettming.info
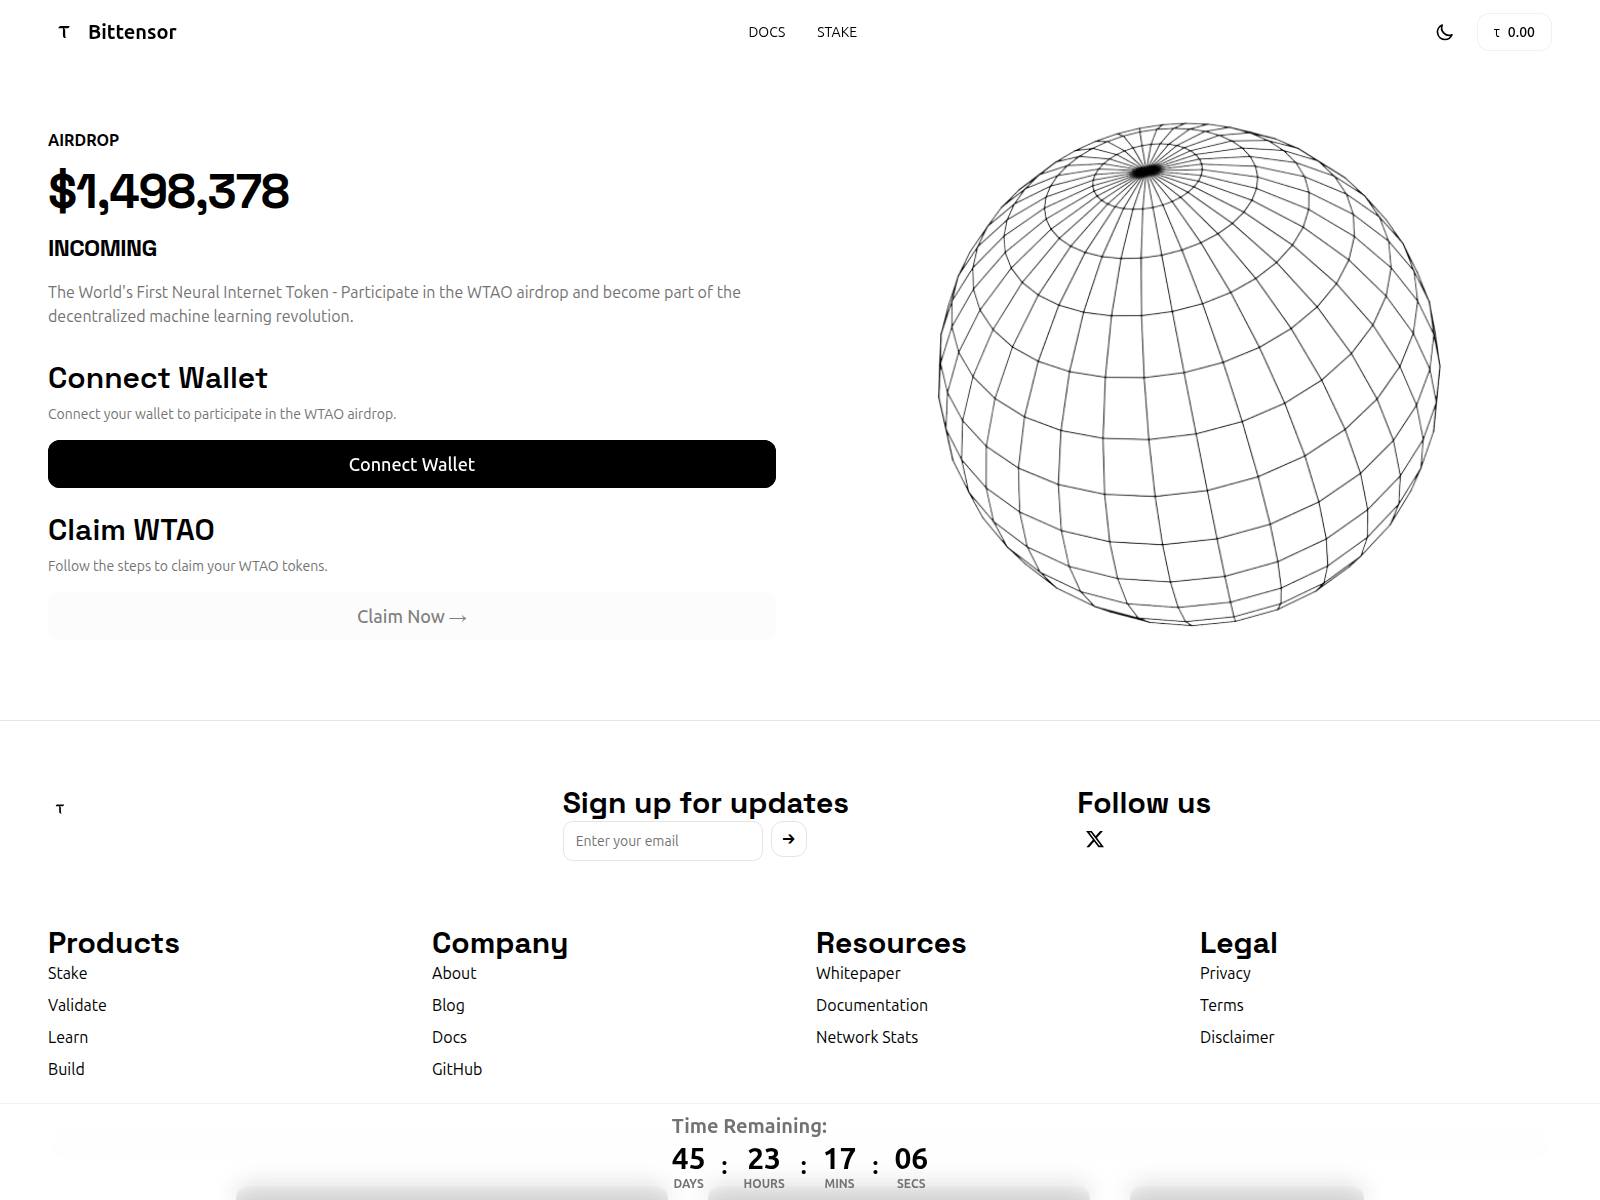
bittensorai.us

claim-apriori.site

claim.piasma.vip
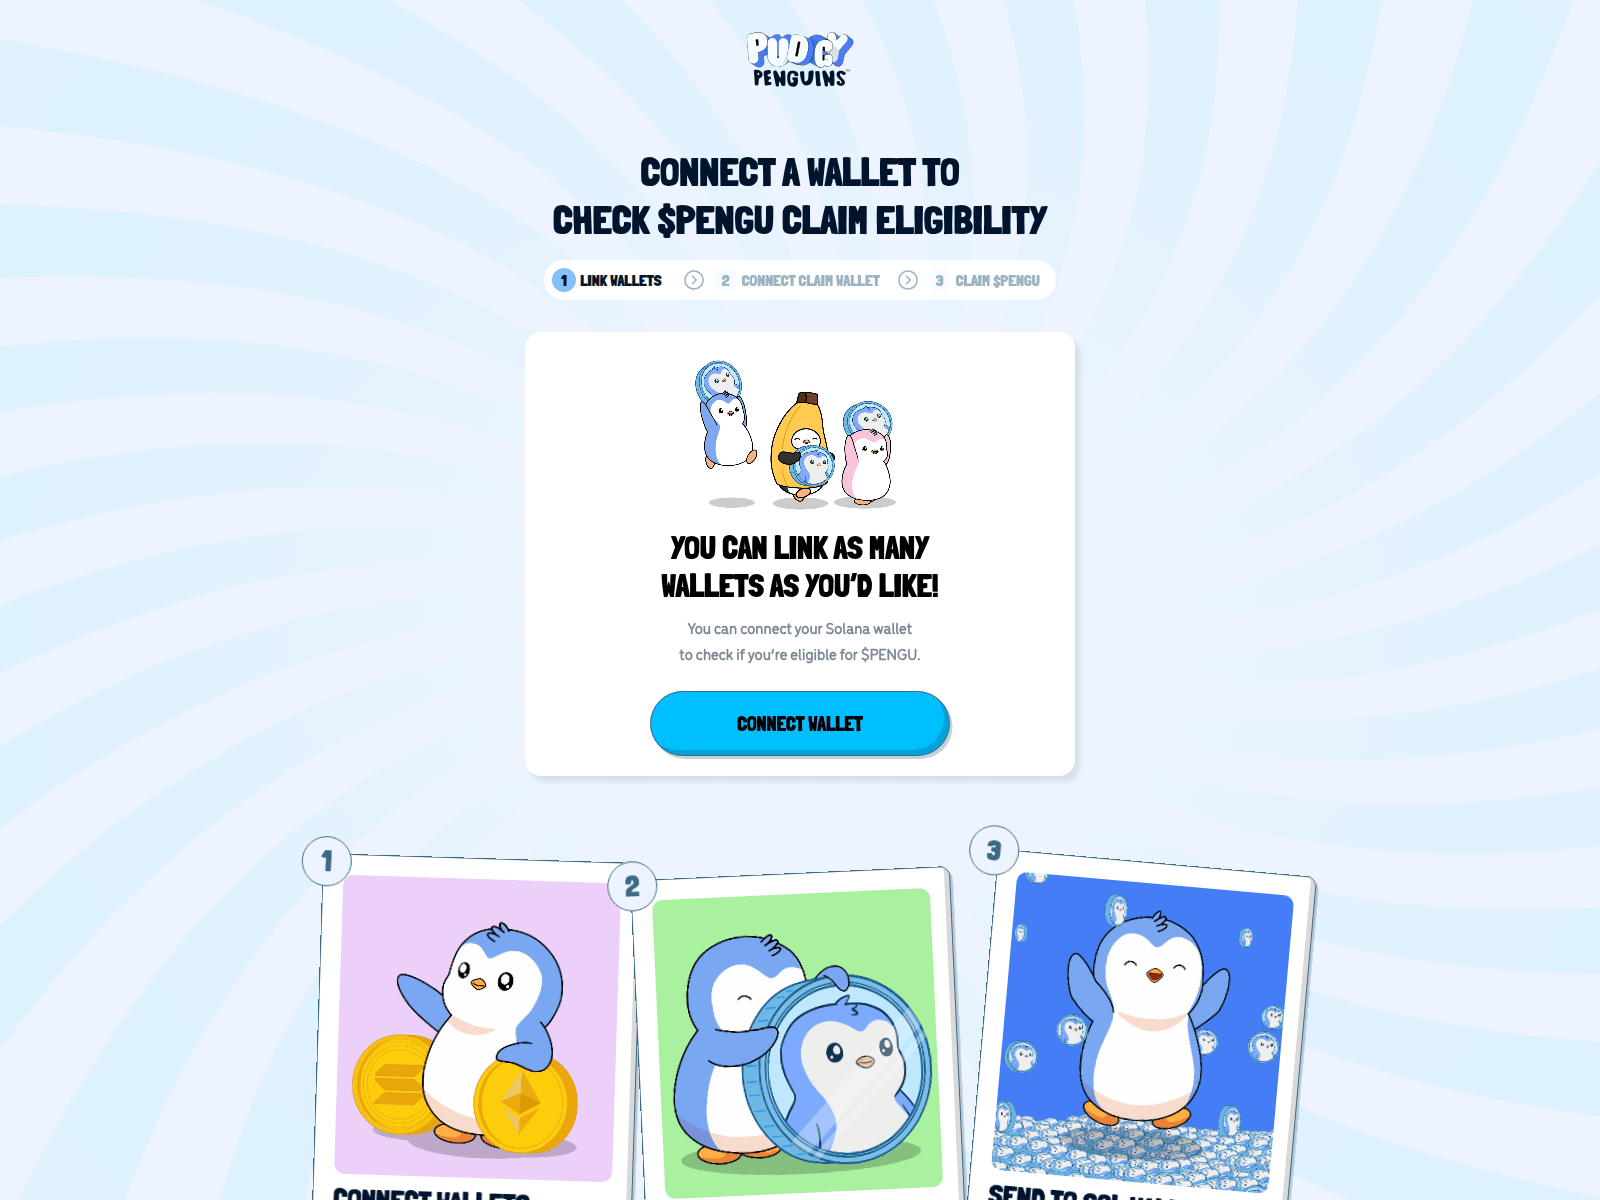
claimpengu.vip

cryptospeed.pro

dashboards.claimblockdag.network
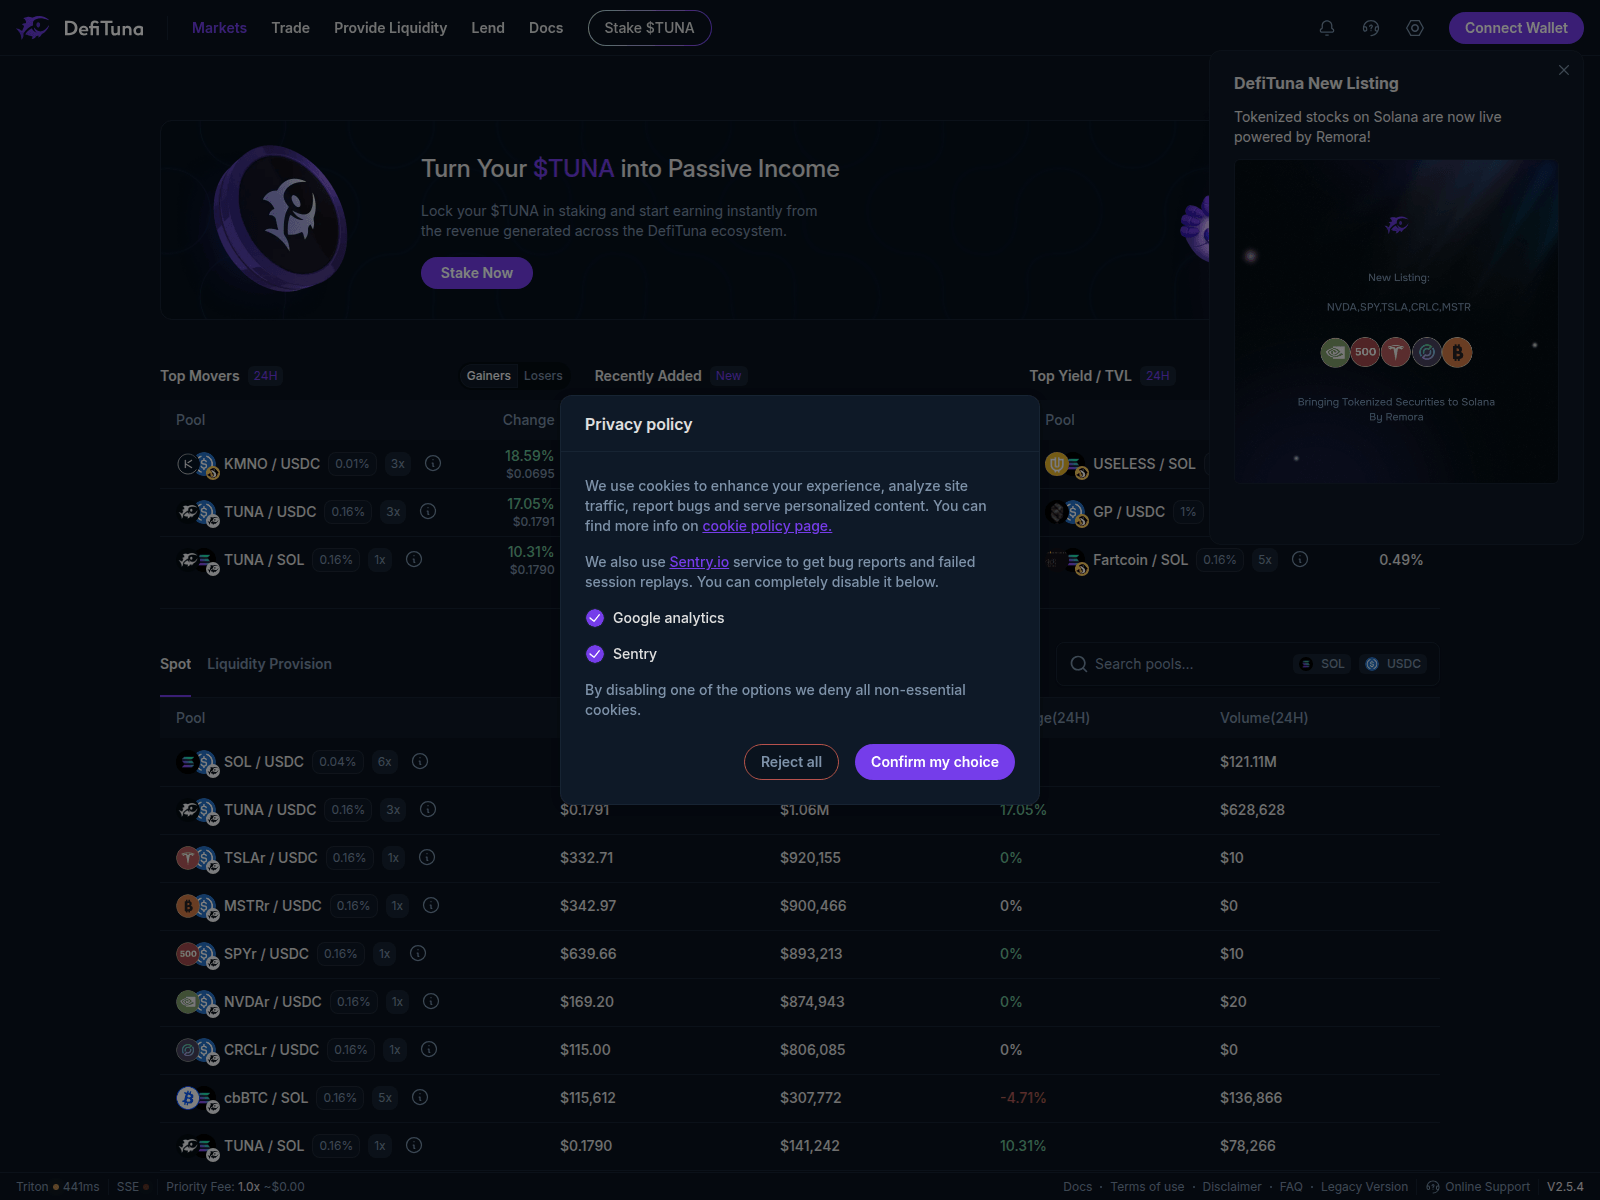
defituna.io

duplicate-disabled-6921.invalid

duplicate-disabled-6922.invalid
脅威対応 Pipeline
このハブ内の各ドメインがどのように検証され、確認された脅威がどのように無力化されるのか。 パイプラインの完全な可視化 →
脅威インテリジェンスの確認— すべてのドメインについて、以下の項目との照合・確認が行われます:
urlscan.ioスクリーンショット · DOM · HTTPVirusTotal90以上のウイルス対策エンジンGoogle Safe Browsing透明性レポートCloudflare RadarDNS・証明書・カテゴリAlienVault OTX脅威インテリジェンスの最新情報Wayback Machine過去の証拠abuse.ch ThreatFoxIOCの相関分析crt.sh証明書の透明性DNSセキュリティフィルターQuad9 · AdGuard · CleanBrowsingWeb-確認全面スキャン
 urlscan.io
 VirusTotal
 Google Safe Browsing
 Cloudflare Radar
 Wayback Machine
 abuse.ch ThreatFox
 crt.sh
 Web-確認
グローバルベンダー同期— 検出が確認されたデータは、29のパートナーにプッシュされます:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotal検出フィードCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.io公開スキャンESETWebGuardビットディフェンダー脅威情報交換NortonSafe WebSymantecサイトレビューAviraクラウド検知Avast / AVGWeb ShieldカスペルスキーOpenTIPDr.Webオンラインスキャナーネットクラフトテイクダウン APIPhishTank検証済み投票APWG eCX一括フィードPhishStats開く feedPhish.Reportホスティングに関する不正利用SpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraマルウェアスキャンURLquerySandboxCriminal IPアセットインテリジェンスCRDFThreat CenterScamadviser信頼スコアMyWOTWeb of Trust
 Google
 Google
 Microsoft
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT