
追跡対象のドメインを検索し、保存されている証拠、検知結果、および最新の稼働状況を確認します。
How This Attack Works
Solana Drainer threats exploit vulnerabilities in Solana's crypto ecosystem to steal funds. Understanding their operation is crucial for prevention.
STEP 1
Target Identification
Attackers identify potential victims through phishing emails and fake websites.
STEP 2
Phishing Execution
Victims are lured to malicious sites mimicking legitimate platforms, like phantomairdrop.com.
STEP 3
Credential Harvesting
Once on the fake site, victims input sensitive information, believing it to be secure.
STEP 4
Fund Drainage
Attackers utilize harvested credentials to access wallets and drain funds via illicit transactions.
Technical Analysis
Solana Drainer attacks leverage phishing techniques to exploit the Solana blockchain. Attackers often create copycat websites using top TLDs such as .com, .xyz, and .cc, with domains hosted by registrars like Cloudflare, Inc. and PDR Ltd. These sites employ deceptive JavaScript and HTML code to mimic legitimate interfaces, tricking users into entering their private keys or seed phrases. Once credentials are obtained, attackers interact with the Solana blockchain via RPC calls to execute unauthorized transactions. The usage of smart contract functions like `transfer` and `approve` allows attackers to swiftly move funds out of victims' accounts. The infrastructure often involves a network of proxy servers to obfuscate the origin of the attack and make tracing back to the perpetrators difficult.
Real Cases
Phantom Wallet Breach (2023)
$2 million stolen
Attackers created a fraudulent Phantom wallet site to harvest user credentials, resulting in a $2 million theft.
SolUnion Scam (2024)
$1.5 million stolen
Using the domain phantom.solunion.cc, scammers executed a sophisticated phishing attack, stealing $1.5 million in SOL.
VaultBenefits Exploit (2024)
$3 million stolen
A fake airdrop campaign via vaultbenefits.net led to credential compromise and a subsequent $3 million drain.
How to Detect
Unsolicited emails or messages offering free SOL or airdrops
Websites with slight misspellings of legitimate names
Requests for private keys or seed phrases
Suspicious URL structures or unfamiliar TLDs like .xyz or .cc
Lack of HTTPS security on sites claiming to be secure
How to Protect Yourself
1
Verify URLs carefully before interacting
2
Enable multi-factor authentication on your wallet
3
Never share your private key or seed phrase
4
Regularly check transaction histories for unauthorized activity
5
Use official wallet apps and browser extensions
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 2,758 domains tracked for this threat type
Solana Drainer 2,758 domains

ai-rug.xyz
air.sol-community.cc
alienjak.officialreward.live
allocation.digital
amaai.world
analyzer.lol
andrew-tate-2025.sol-app.live
app.meteorafi.com
app.turtlerdote.xyz
appledailypharma.com
arctoken.run
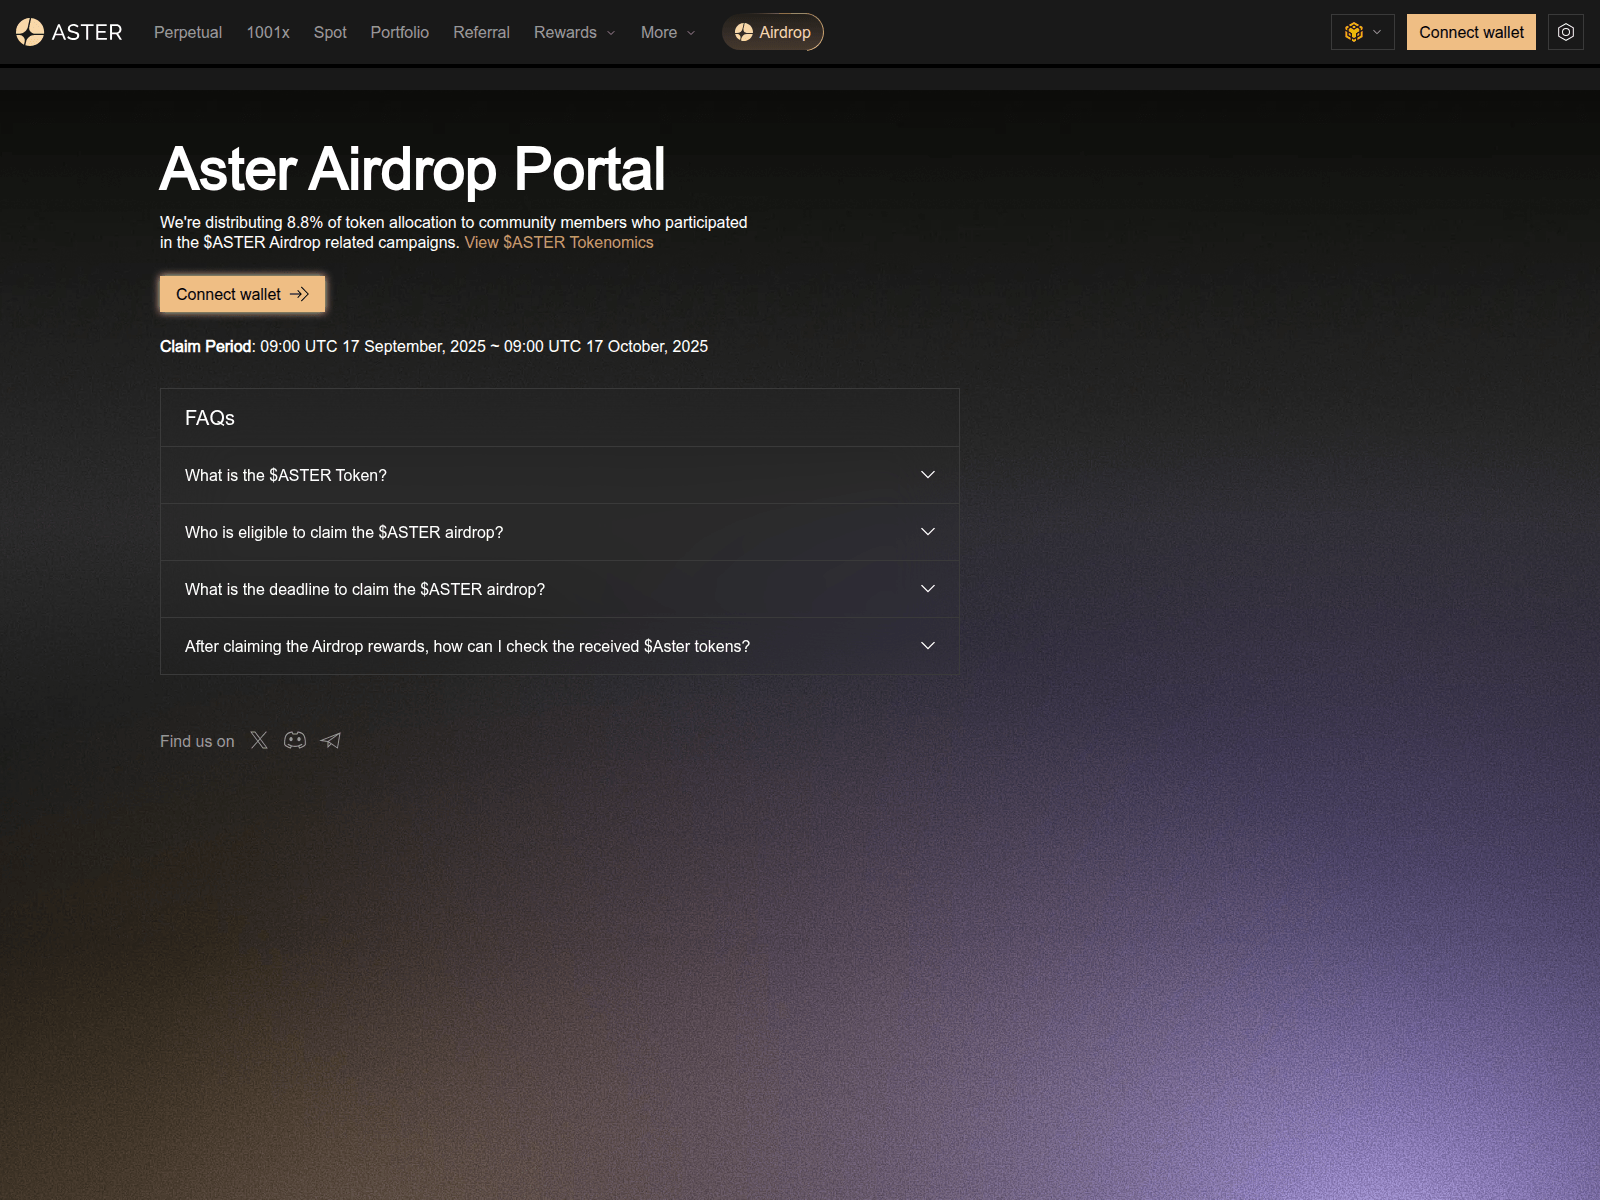
asterdefi.xyz
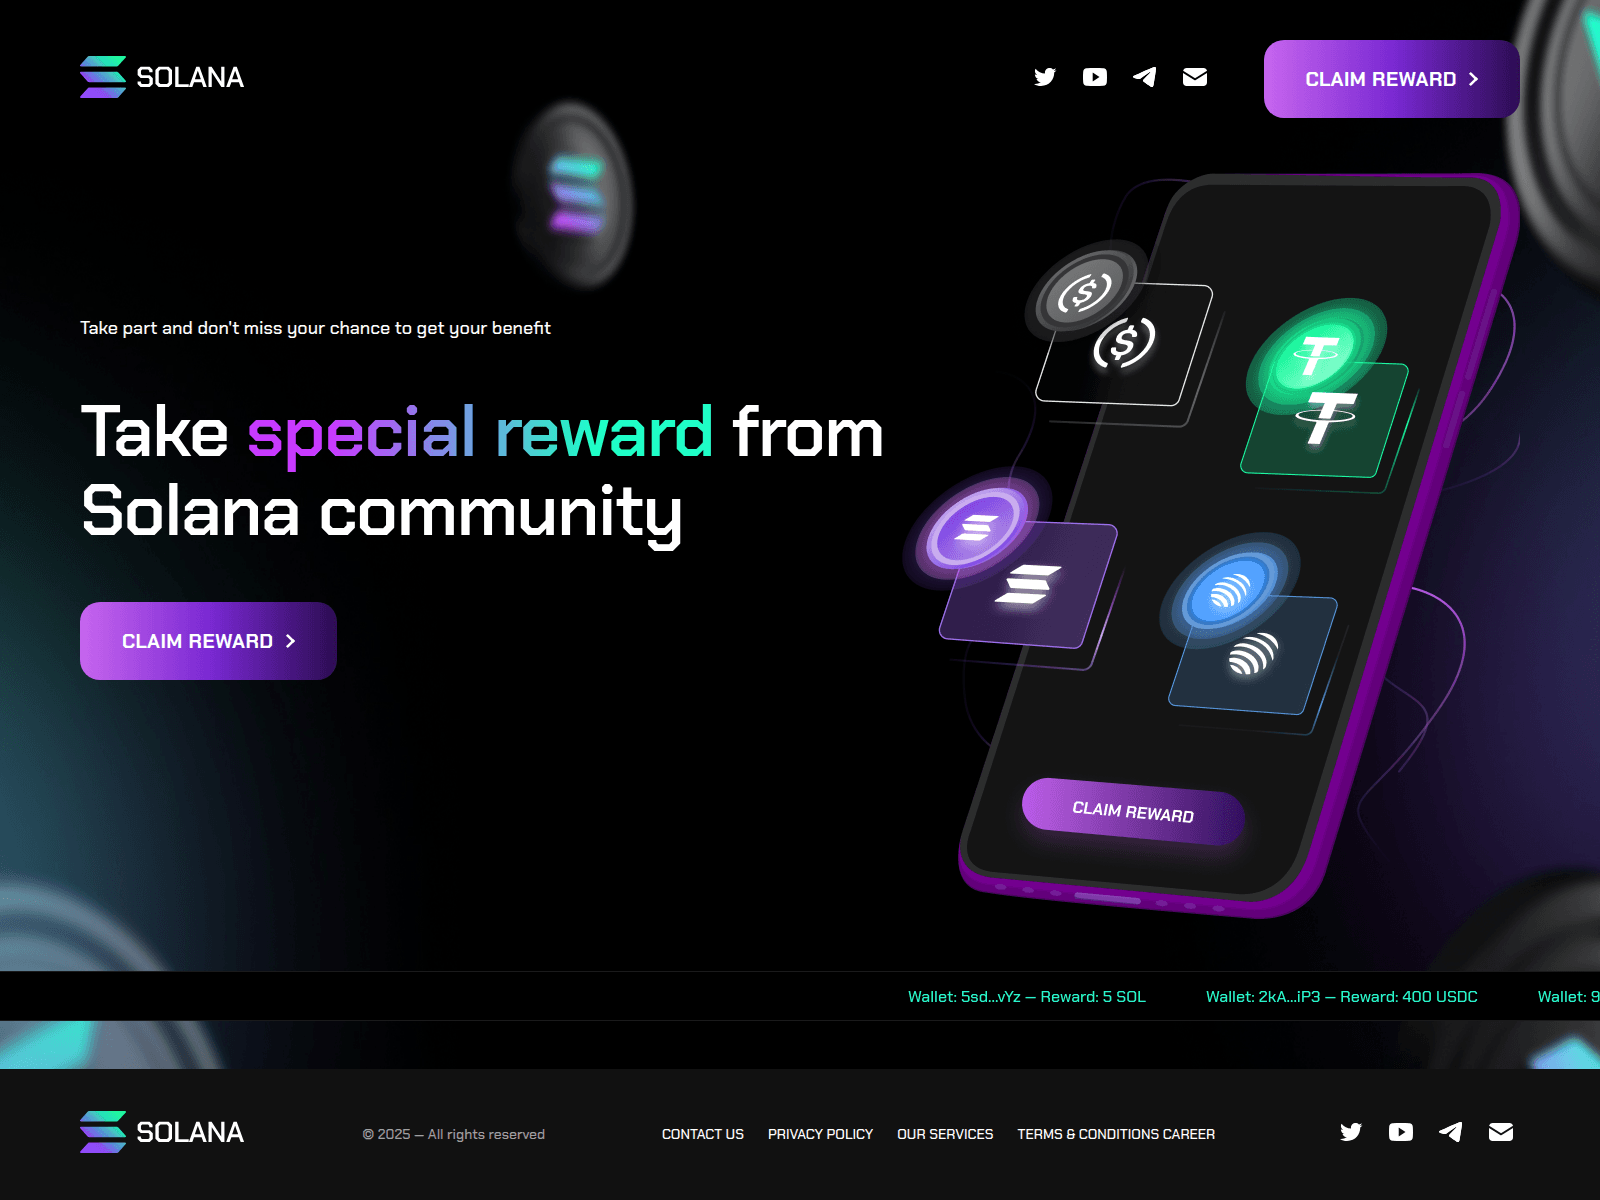
authappresolverr.xyz
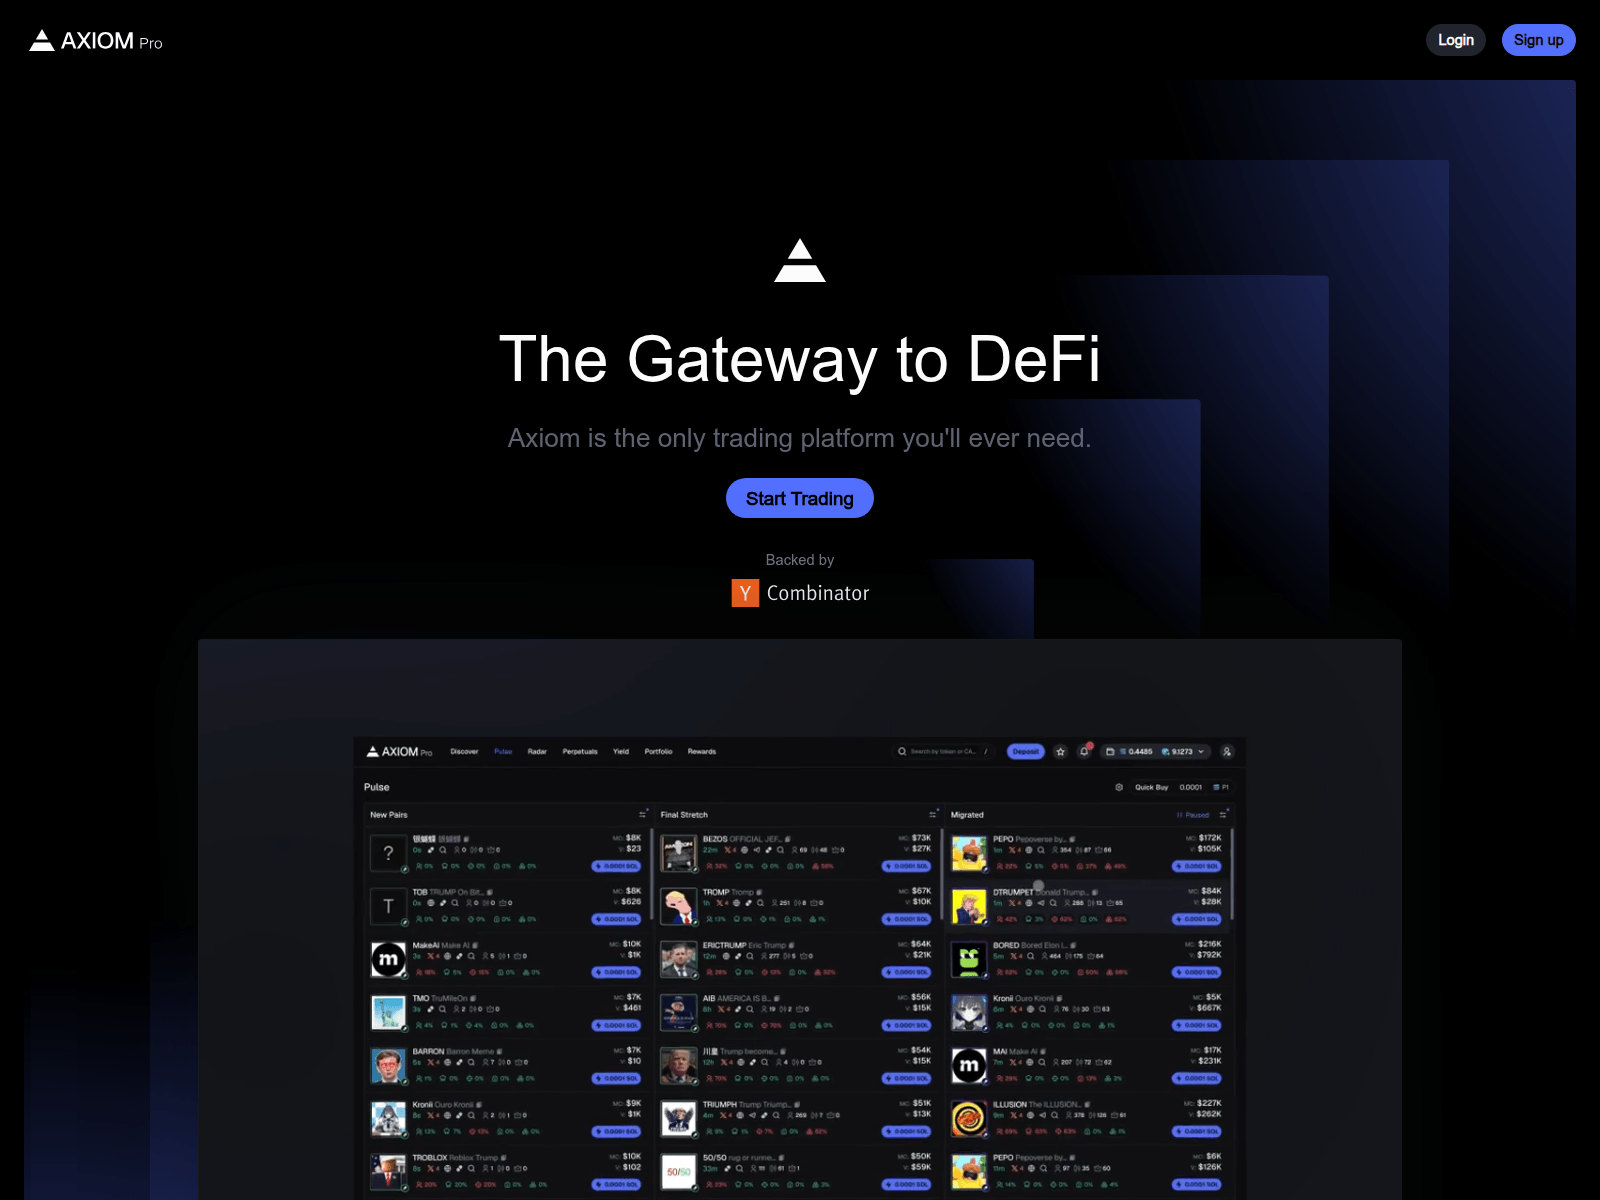
axiompro.top
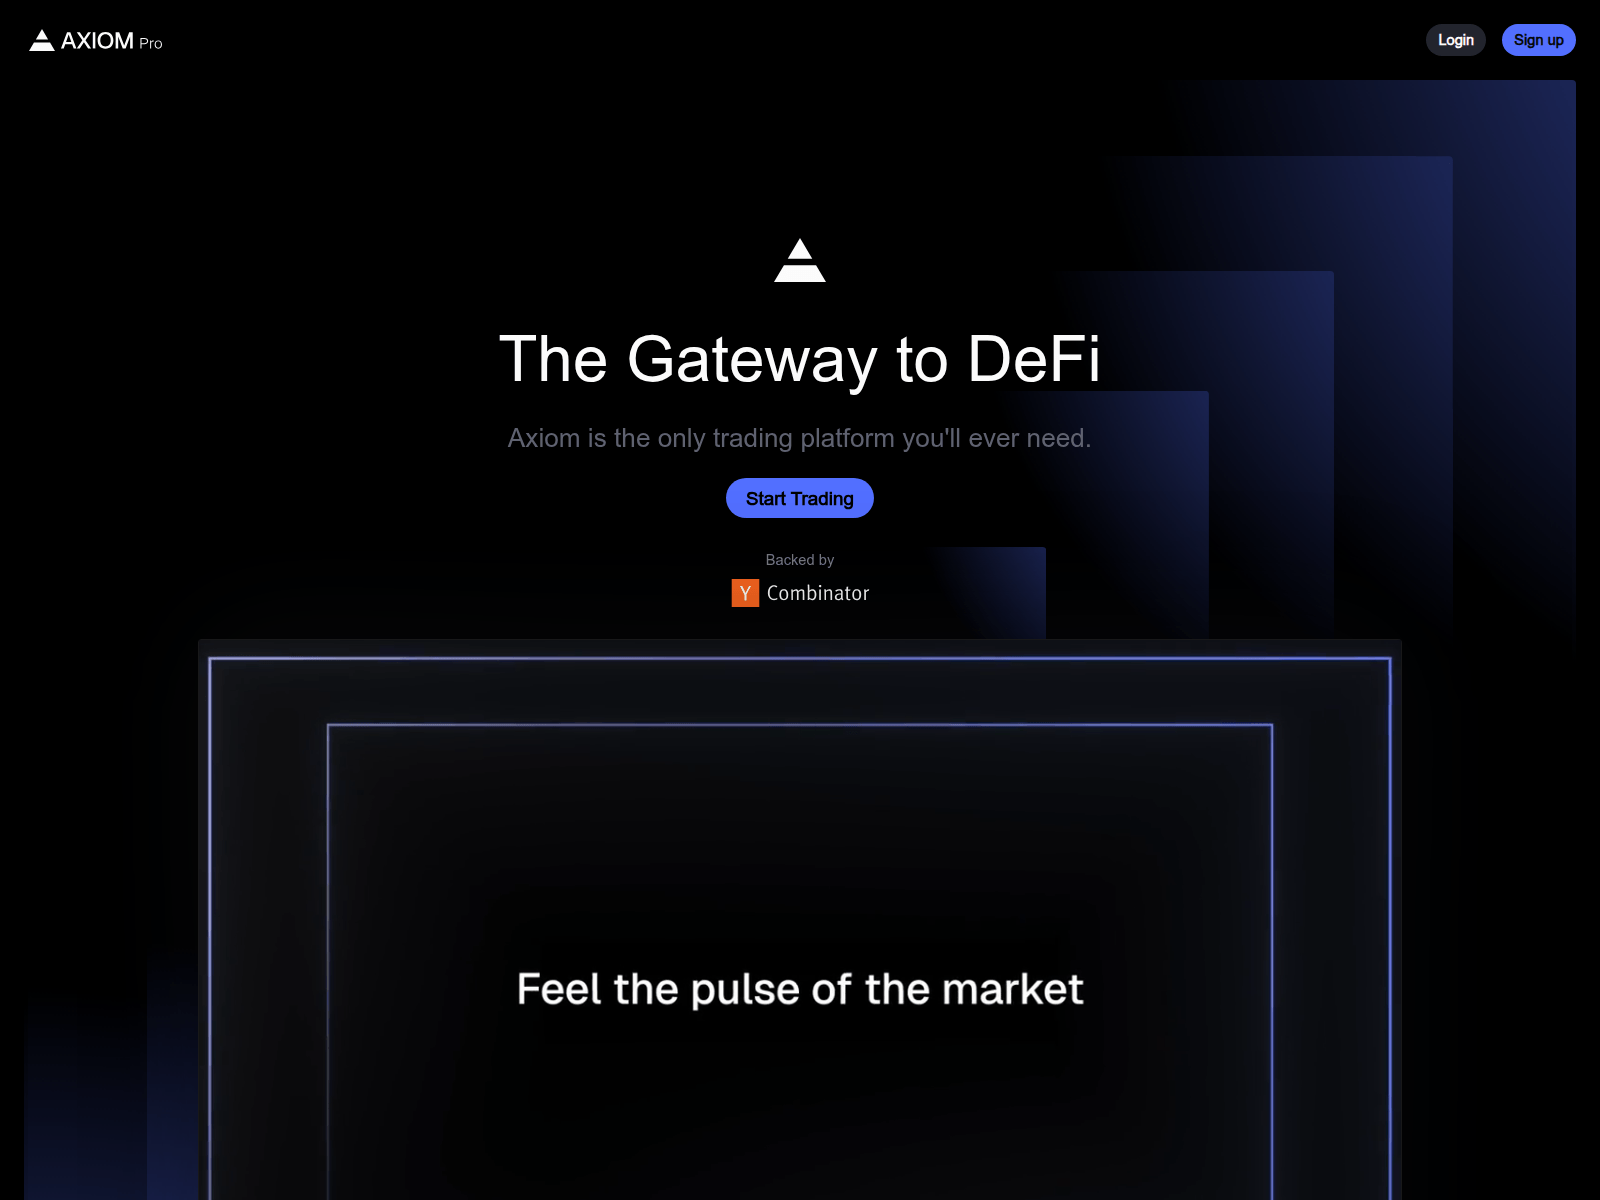
axiomx.trade
badgersolana.xyz
beta-diamondhands.com
birbtoken.run
bitgetxdrops.pro
bitpredict.app
blackbulldrop.top
blog-phantommoney-org.pages.dev
bongsolana-e7b.pages.dev
bonkair.live
bonkfam.com
bonkfarm.com
bonkfarm.org
bonkscapta.space
bonksfarm.com
botfathersolana-xyz.pages.dev
buiix.cfd
bullx-trade.site
buttfishsol.com
calvindrop.top
cards-phantom.icu
cashback.tradepadre.xyz
catownkimono.onsolx.io
chain-nodes.com
chaoonsolana-drainer.pages.dev
check.pumpfnd.com
chinasolx.com
claim.bonk-coin.pro
claim.fartless.click
claim.humidifi.cc
claim.jupiter.expert
claim.jupitercoin.org
claim.momad.life
claim.xn--jupter-yva.net
claim.xn--metora-dva.com
claimauthresolvr.xyz
claimsolana.co.in
claritysolana.best
coinfor.world
contractverified.online
cope.web3sol.xyz
corgisolana.xyz
cr7solana.pages.dev
crashoutsolana.fun
cs2solana.net
dappsolanaprotocol.com
diamondhandbeta.net
diamondhandsbeta.net
doogleonsolana-claim.pages.dev
doraemonsolana.org
drop-masterbot.fun
drop-pippin.top
dropsol-main.com

duplicate-disabled-10848.invalid
duplicate-disabled-185045.invalid
duplicate-disabled-46506.invalid
dyno-node.com
easysol-check.com
efficient-assetpool.site
elegible-pump.fun
en-orca-solana.pages.dev
eo-phantomwalat.pages.dev
event-afk.fun
event-artemis.fun
event-chudsome.fun
event-cpeng.fun
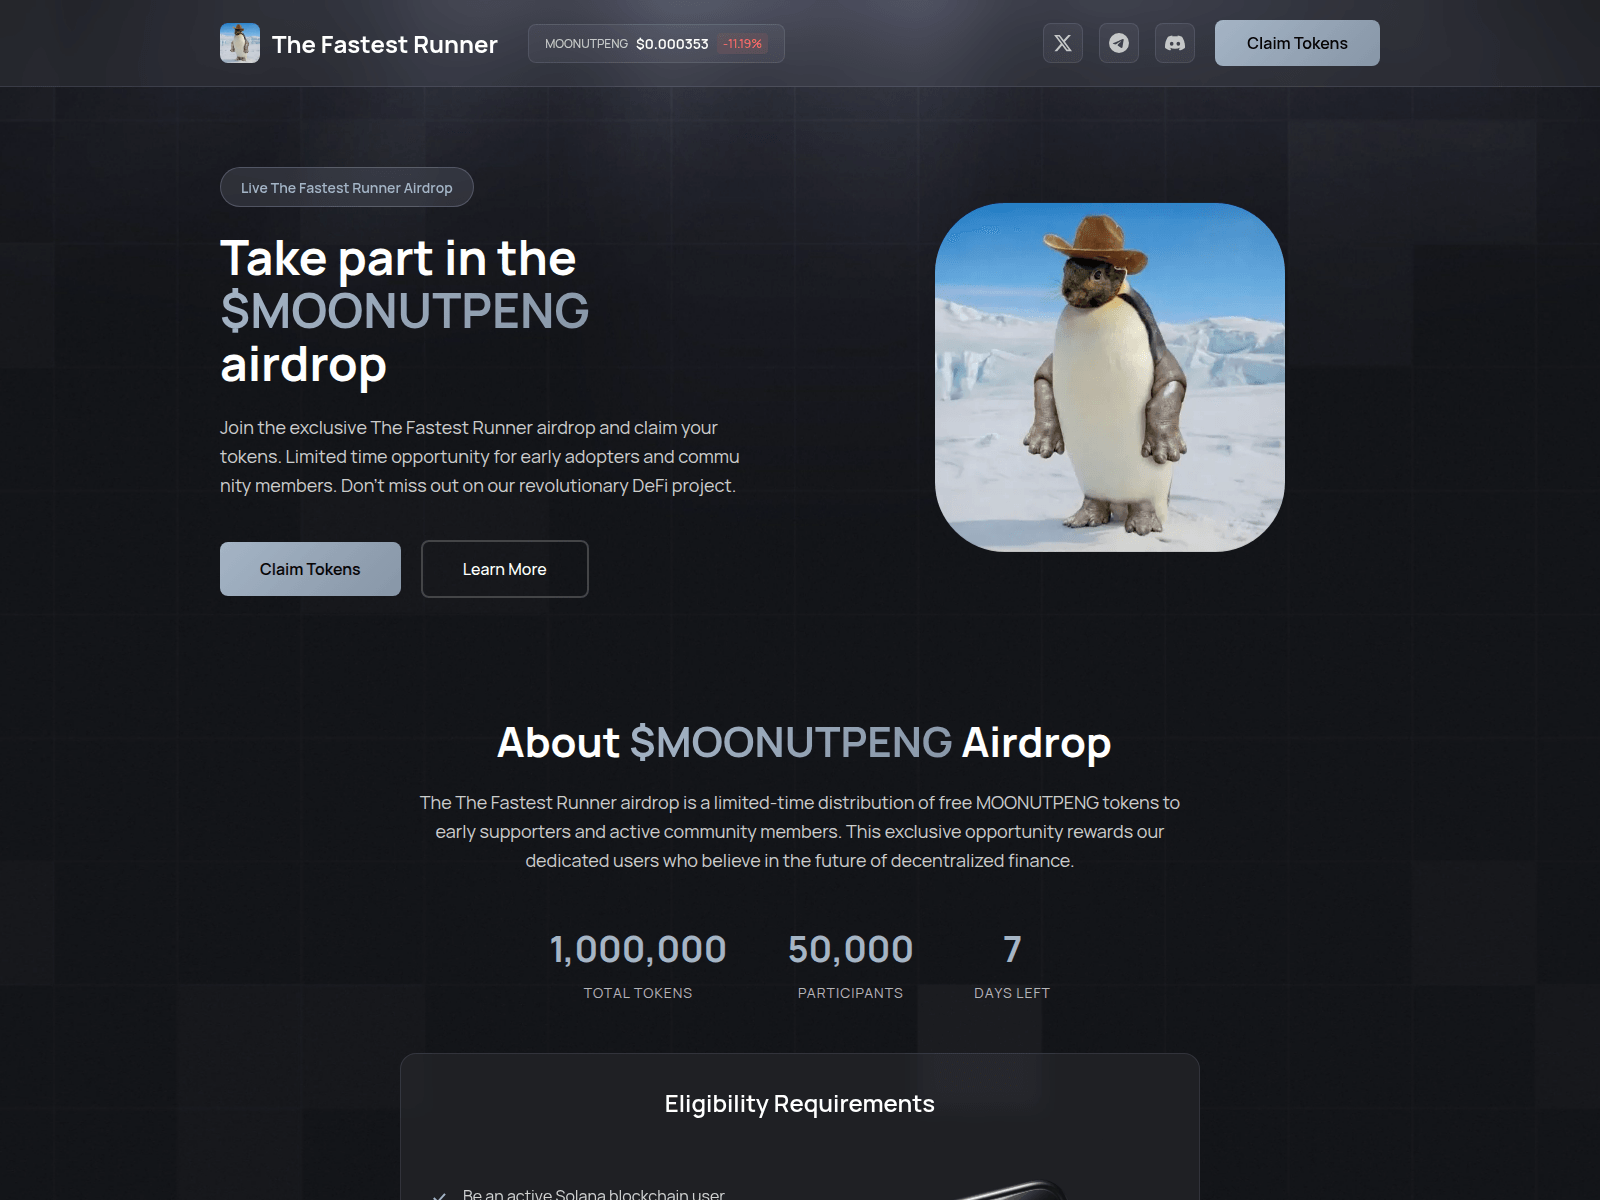
event-moonutpeng.fun
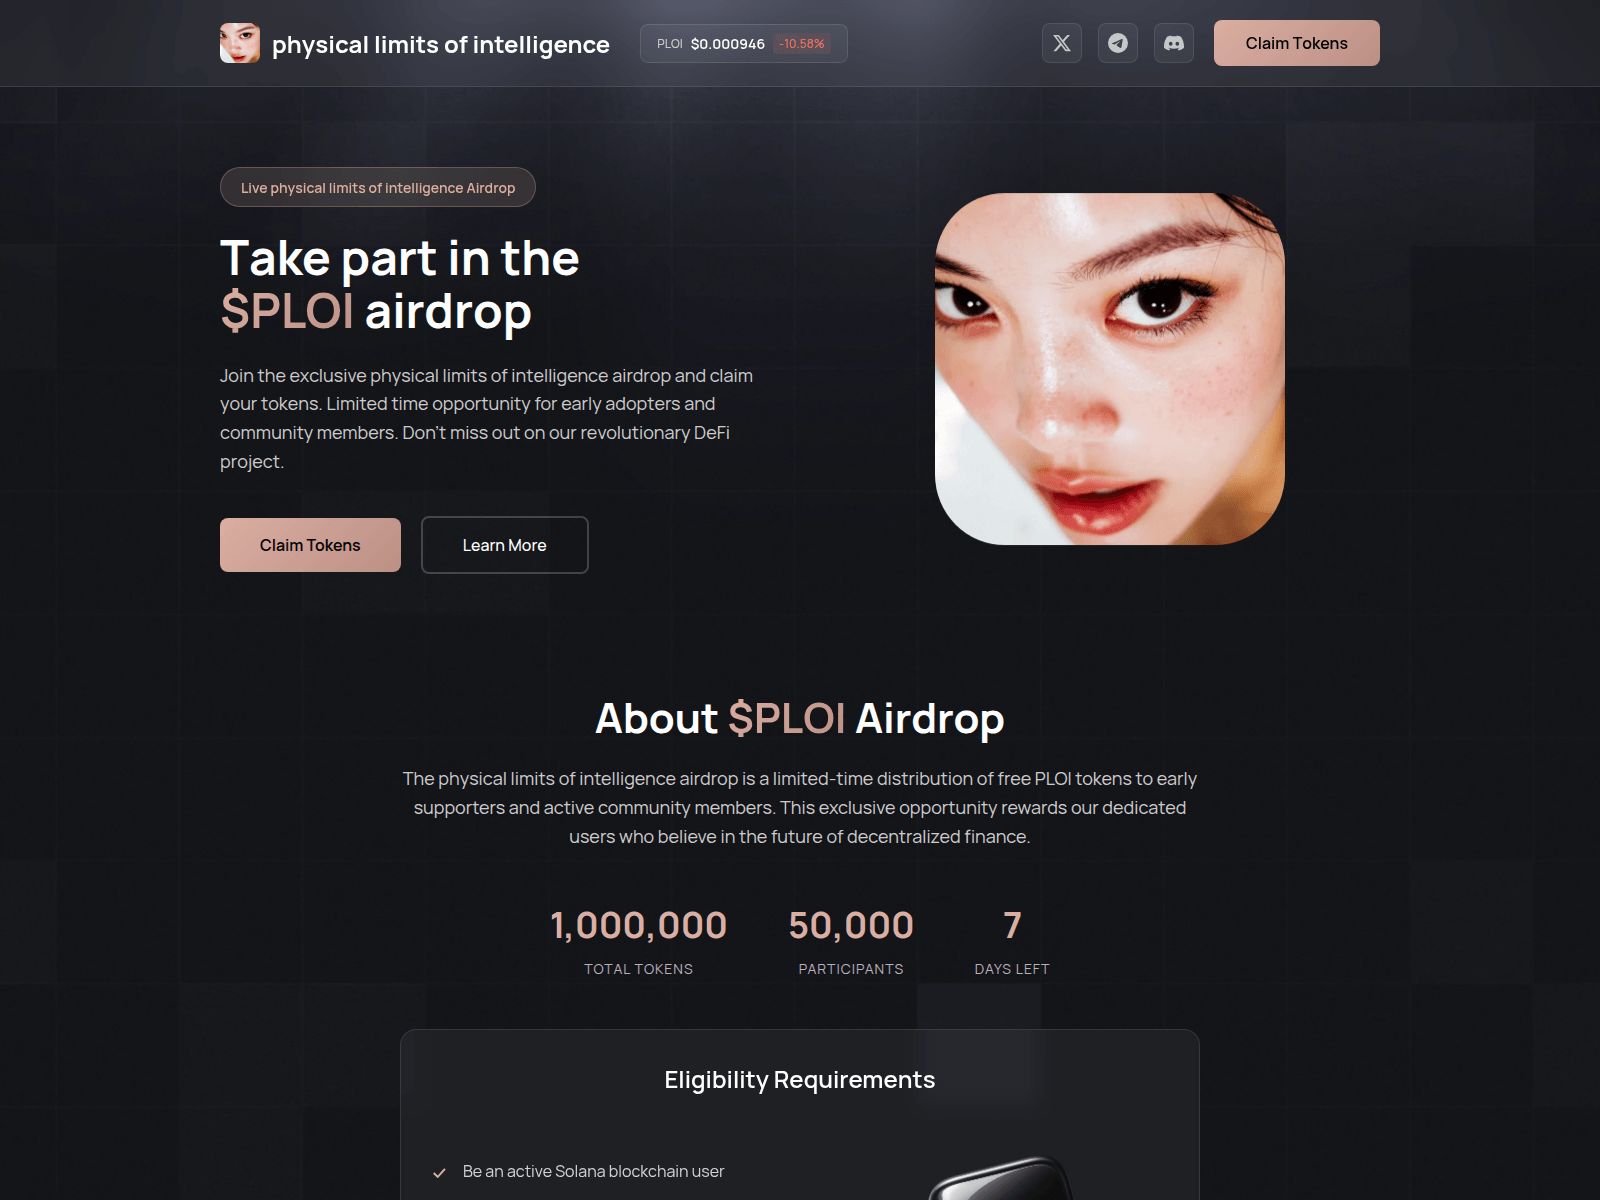
event-ploi.xyz
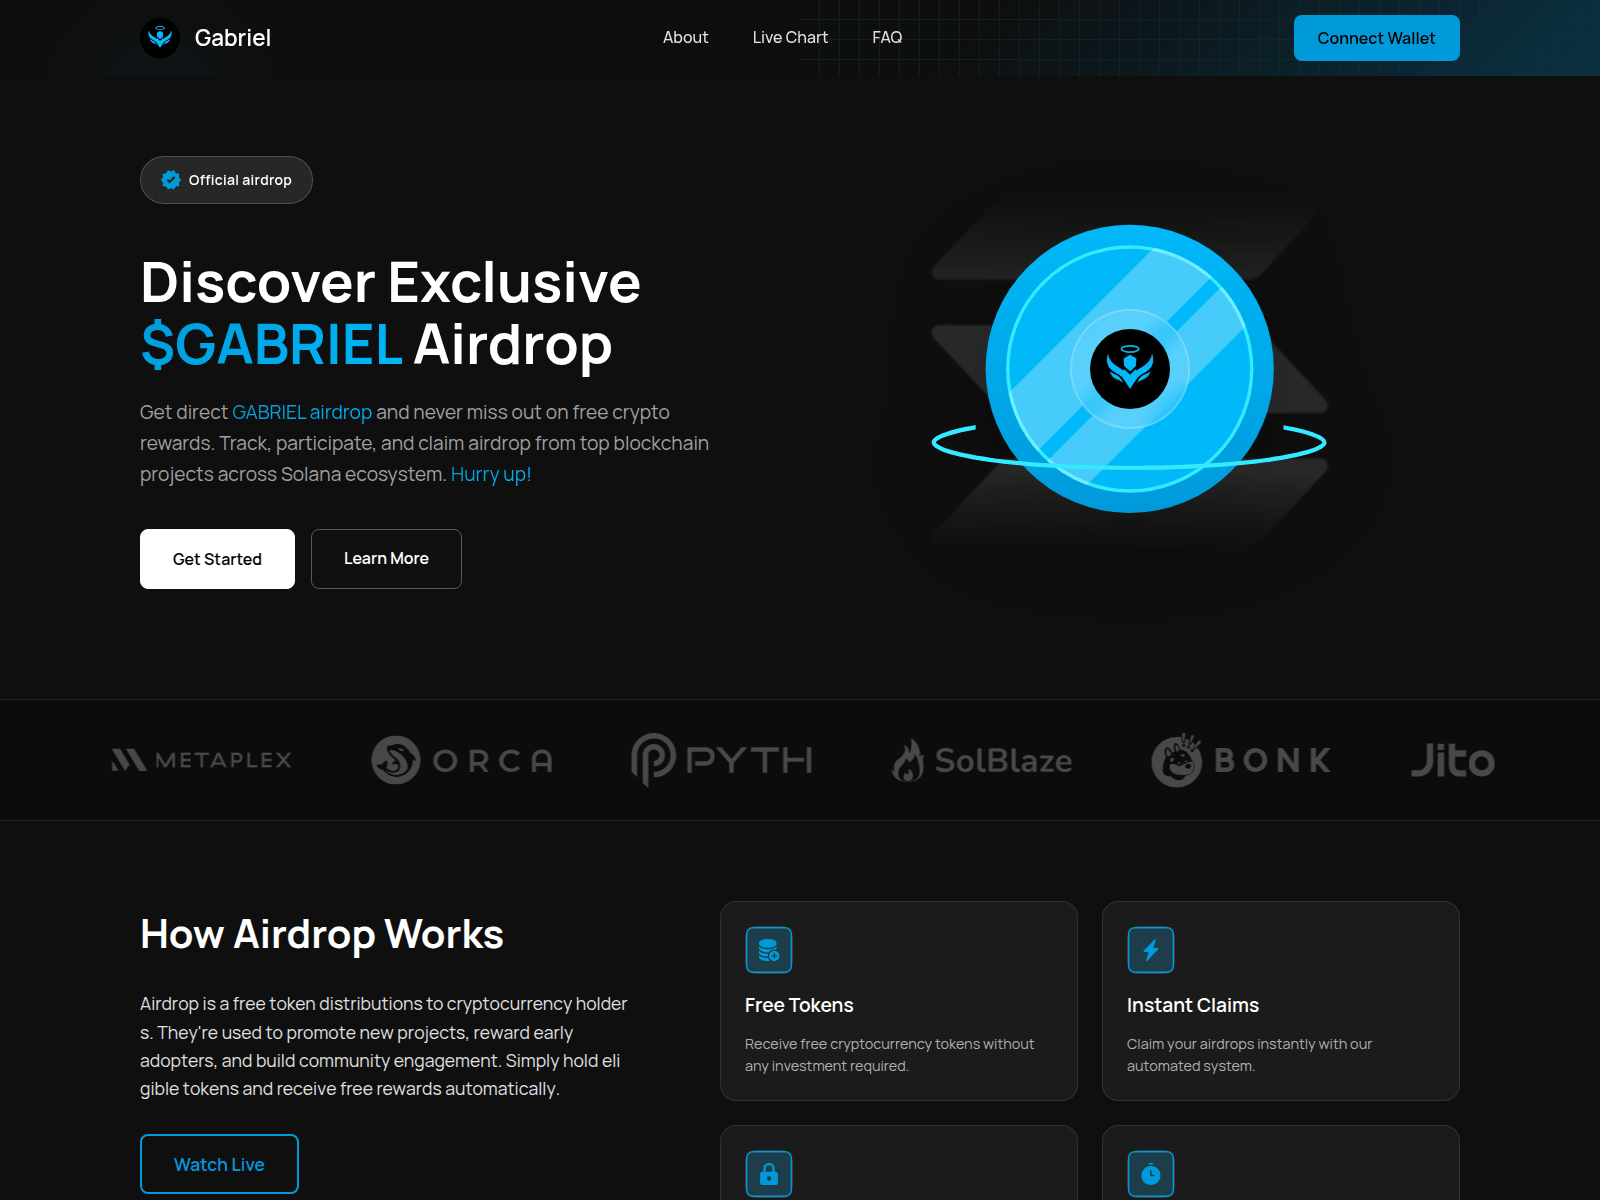
events-gabriel.xyz
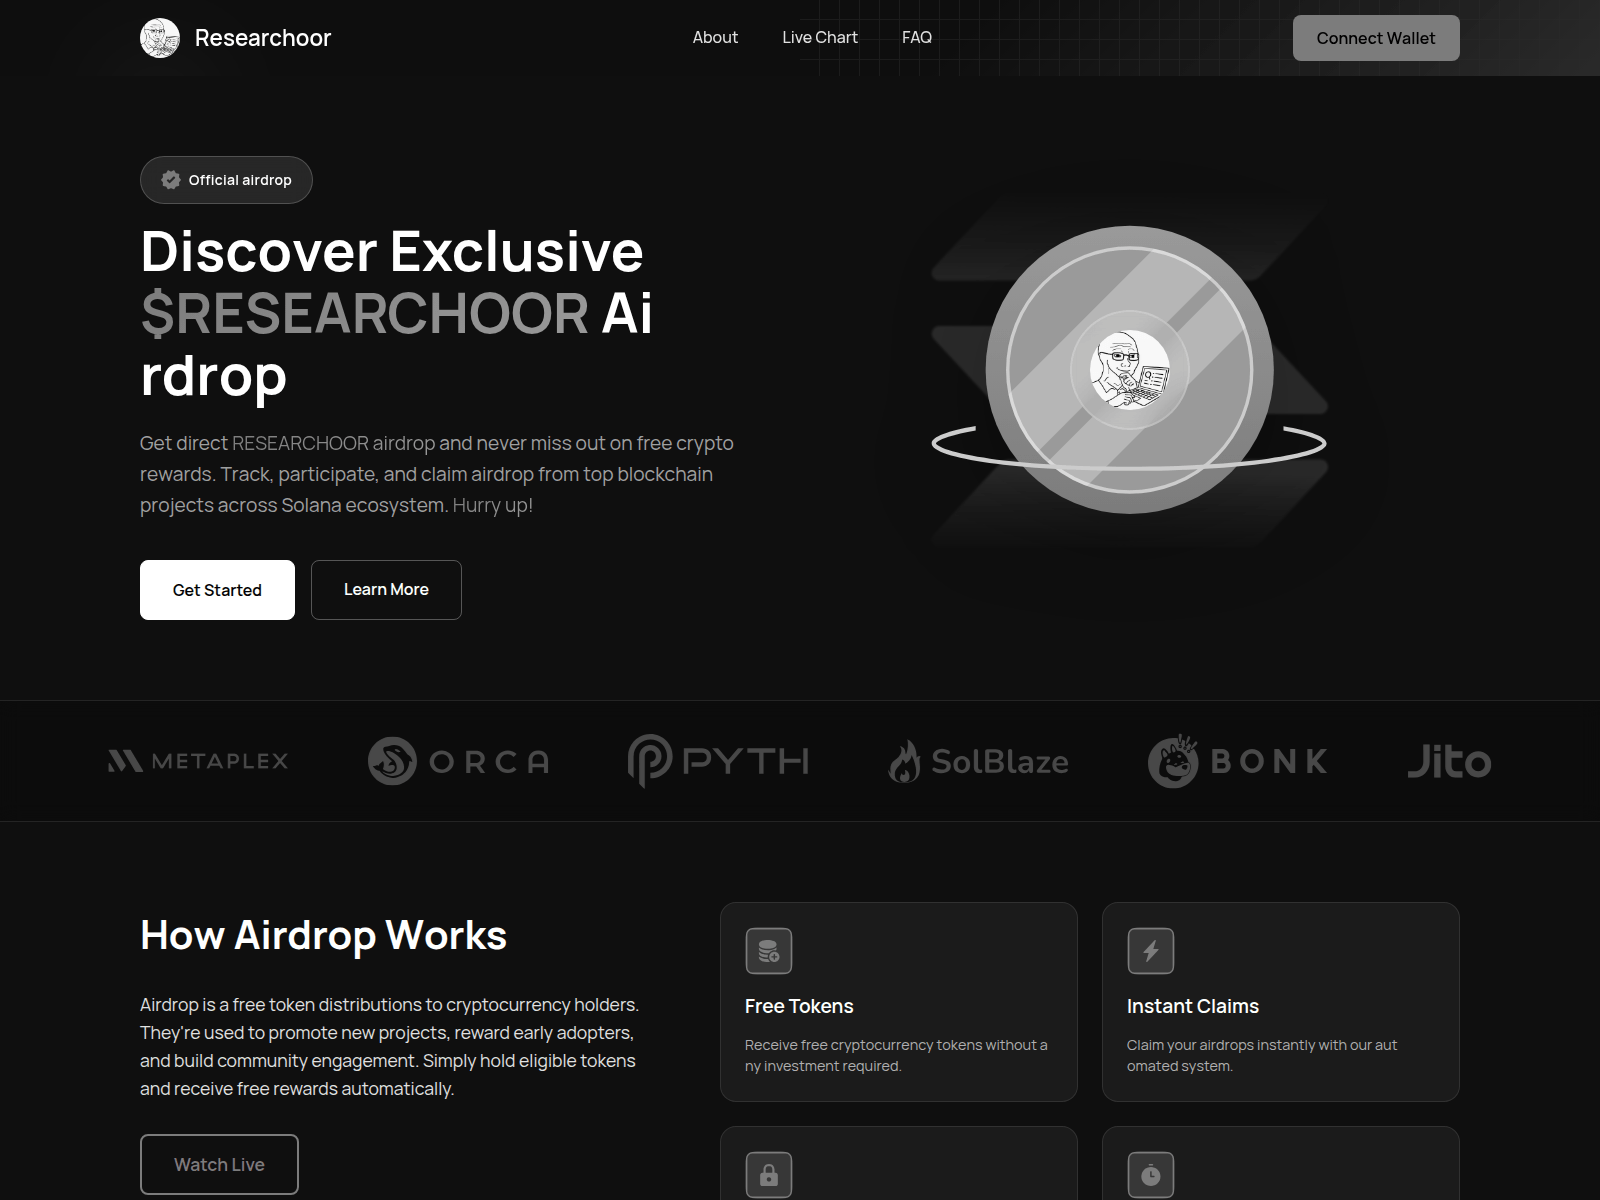
events-researchoor.xyz
evet-unlock.xyz
fakephantom.online
fassets-au.cc

fluffy-solana.xyz
four-memes.fun
franklin.solhub.trade
fraudonsolana.xyz
frogedrop.top
fullcoiresolver.xyz
gboy.top
getbonkmeme.fun
getjup.lol
getlicked.xyz
getvine.top
giftmesolana.com
giraffes.fonudation.info
脅威対応 Pipeline
このハブ内の各ドメインがどのように検証され、確認された脅威がどのように無力化されるのか。 パイプラインの完全な可視化 →
脅威インテリジェンスの確認— すべてのドメインについて、以下の項目との照合・確認が行われます:
urlscan.ioスクリーンショット · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency レポートCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesウェイバック・マシンHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS セキュリティ FiltersQuad9 · AdGuard · CleanBrowsingWeb-確認Full surface scan
 crt.sh
グローバルベンダー同期— 検出が確認されたデータは、29のパートナーにプッシュされます:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardビットディフェンダーThreat exchangeNortonSafe WebSymantecサイトレビューAviraCloud detectionAvast / AVGWeb ShieldカスペルスキーOpenTIPDr.WebOnline scannerネットクラフトテイクダウン APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.レポートHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust