
追跡対象のドメインを検索し、保存されている証拠、検知結果、および最新の稼働状況を確認します。
How This Attack Works
Solana Drainer threats exploit vulnerabilities in Solana's crypto ecosystem to steal funds. Understanding their operation is crucial for prevention.
STEP 1
Target Identification
Attackers identify potential victims through phishing emails and fake websites.
STEP 2
Phishing Execution
Victims are lured to malicious sites mimicking legitimate platforms, like phantomairdrop.com.
STEP 3
Credential Harvesting
Once on the fake site, victims input sensitive information, believing it to be secure.
STEP 4
Fund Drainage
Attackers utilize harvested credentials to access wallets and drain funds via illicit transactions.
Technical Analysis
Solana Drainer attacks leverage phishing techniques to exploit the Solana blockchain. Attackers often create copycat websites using top TLDs such as .com, .xyz, and .cc, with domains hosted by registrars like Cloudflare, Inc. and PDR Ltd. These sites employ deceptive JavaScript and HTML code to mimic legitimate interfaces, tricking users into entering their private keys or seed phrases. Once credentials are obtained, attackers interact with the Solana blockchain via RPC calls to execute unauthorized transactions. The usage of smart contract functions like `transfer` and `approve` allows attackers to swiftly move funds out of victims' accounts. The infrastructure often involves a network of proxy servers to obfuscate the origin of the attack and make tracing back to the perpetrators difficult.
Real Cases
Phantom Wallet Breach (2023)
$2 million stolen
Attackers created a fraudulent Phantom wallet site to harvest user credentials, resulting in a $2 million theft.
SolUnion Scam (2024)
$1.5 million stolen
Using the domain phantom.solunion.cc, scammers executed a sophisticated phishing attack, stealing $1.5 million in SOL.
VaultBenefits Exploit (2024)
$3 million stolen
A fake airdrop campaign via vaultbenefits.net led to credential compromise and a subsequent $3 million drain.
How to Detect
Unsolicited emails or messages offering free SOL or airdrops
Websites with slight misspellings of legitimate names
Requests for private keys or seed phrases
Suspicious URL structures or unfamiliar TLDs like .xyz or .cc
Lack of HTTPS security on sites claiming to be secure
How to Protect Yourself
1
Verify URLs carefully before interacting
2
Enable multi-factor authentication on your wallet
3
Never share your private key or seed phrase
4
Regularly check transaction histories for unauthorized activity
5
Use official wallet apps and browser extensions
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 2,758 domains tracked for this threat type
Solana Drainer 2,758 domains
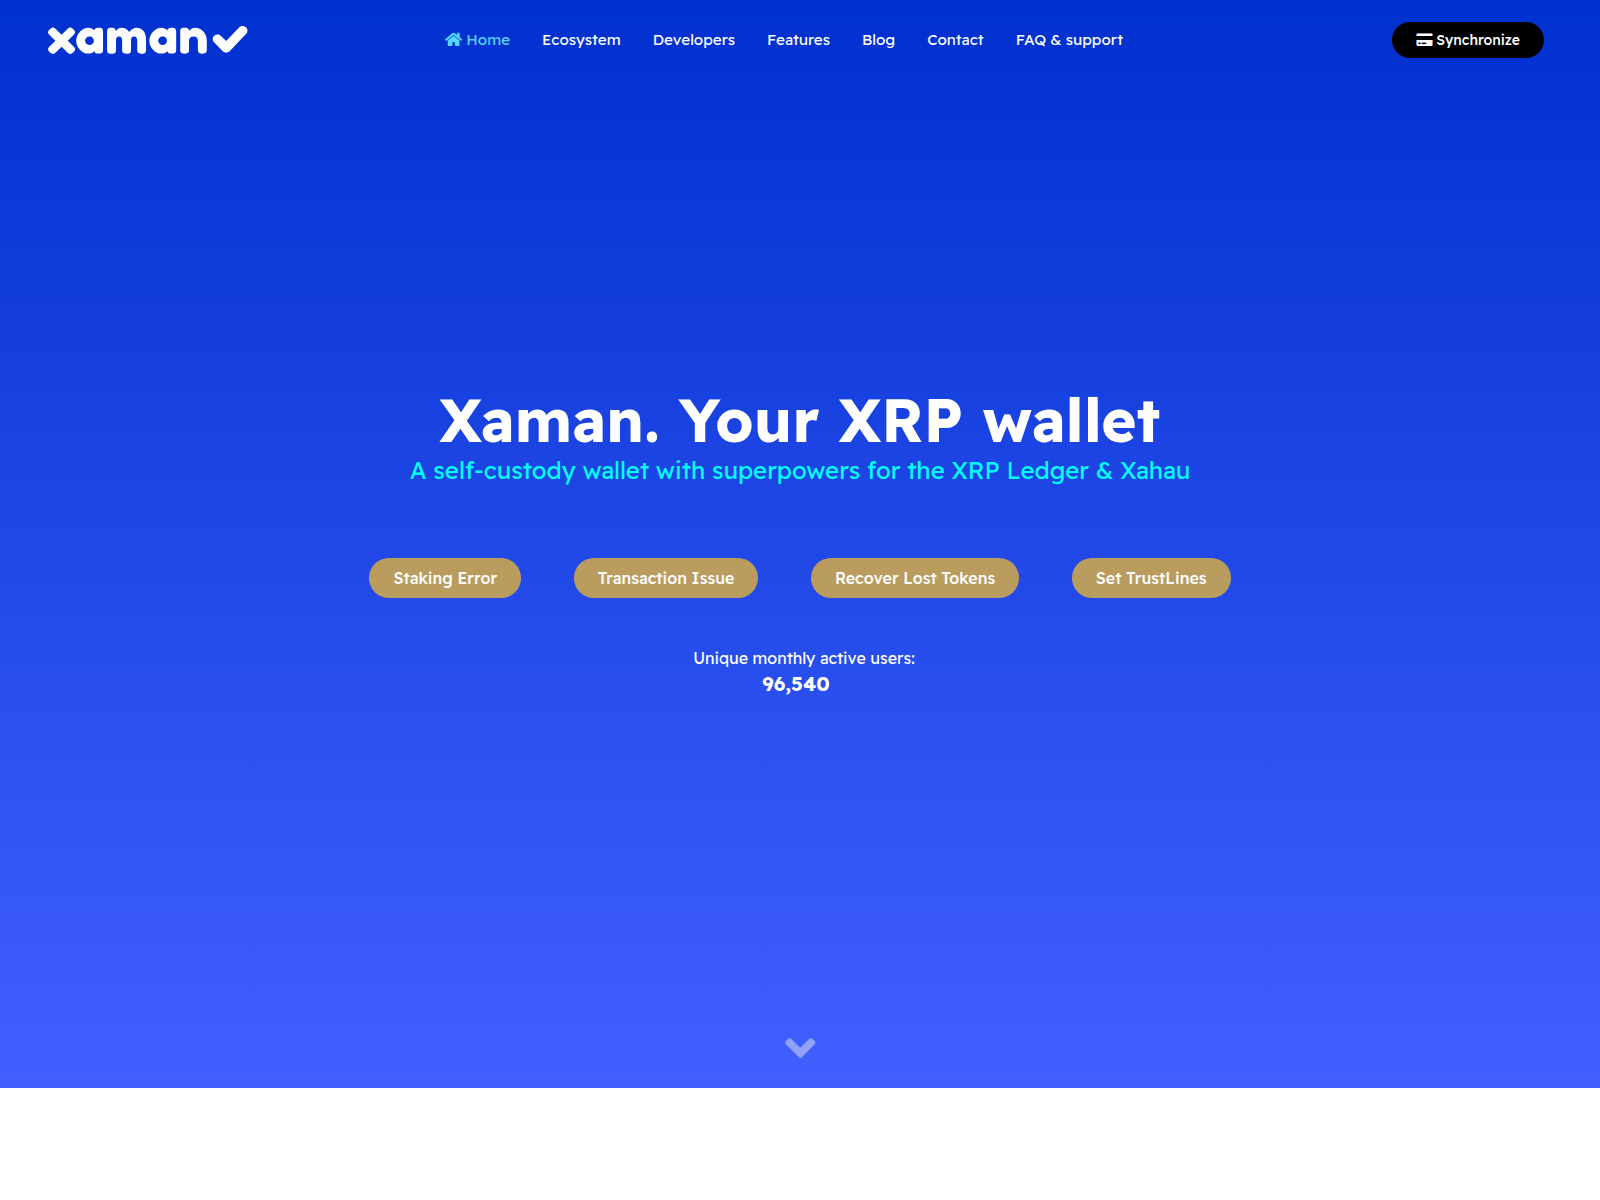
xamanappmodule.web.app
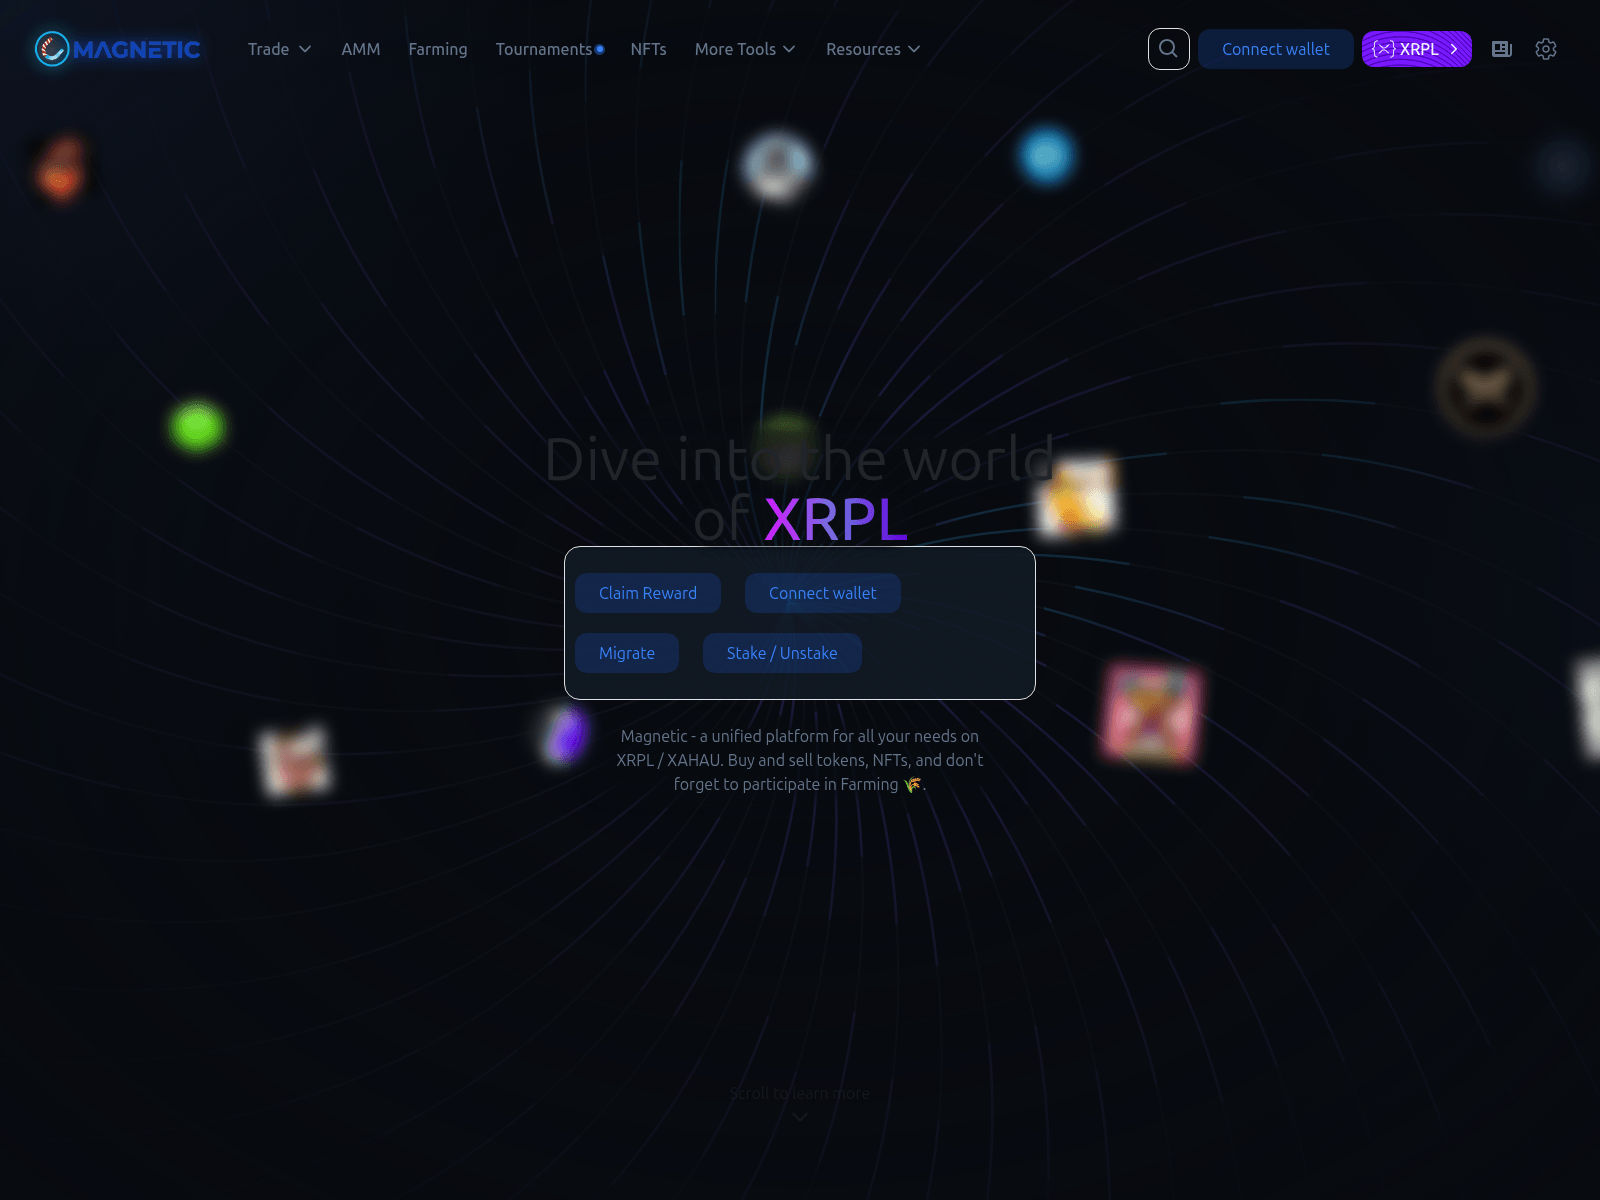
xmagneticdapp.web.app
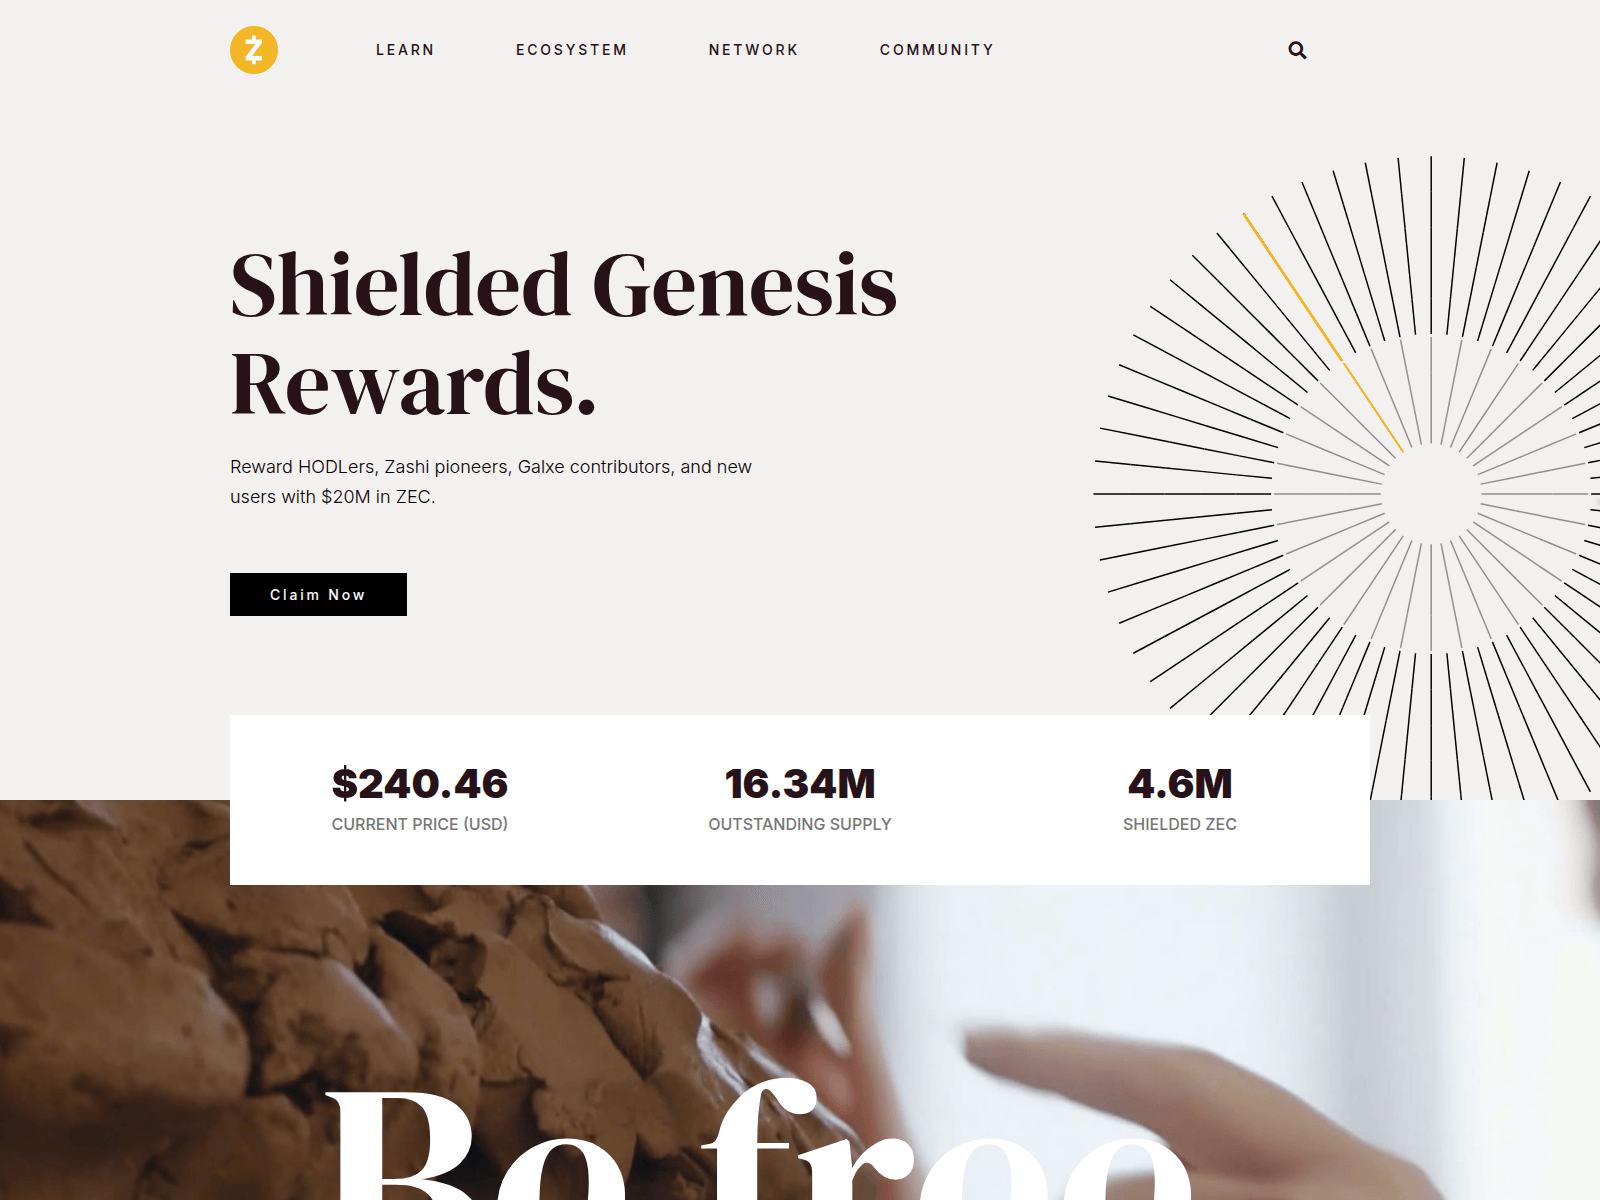
zcash-foundation.com
zunawallet.com
12515215.pages.dev
2025-event.xyz
62988.one
airdroop.world
airdrop-grass.io
airdrop-lmao.fun
aml-one.org
amlero.com
amlwix.com
apextradecapital.pro
app-axlom.cfd

avicichain.run
beetlesolana.xyz
bfs.solspace.io
binancealpha.fun
blipsmigrate.xyz
bonk-token.world
bonkfinance.top
brucewaynesolana.xyz
bull-x.online
capbetsolana.com
cashbackterminal.app
chainnodez.com
claim-fish.xyz
claim-sigmasolanacom.pages.dev
claim.ketsolana.app
claim.moonbirds.cc
defiland-migration.live
dexvotex.live
djcoin.onsol.pro
donald-coin-air.world
drop-coin.live
duplicate-disabled-3093.invalid
event-bpengu.fun
event-dhcoins.fun
event-memecoin.fun
event-nekomata.fun
event-png.fun
event-shellraiser.fun
event-skillstack.fun
event-zhc.fun
events-sachi.xyz
events-trollboy.xyz
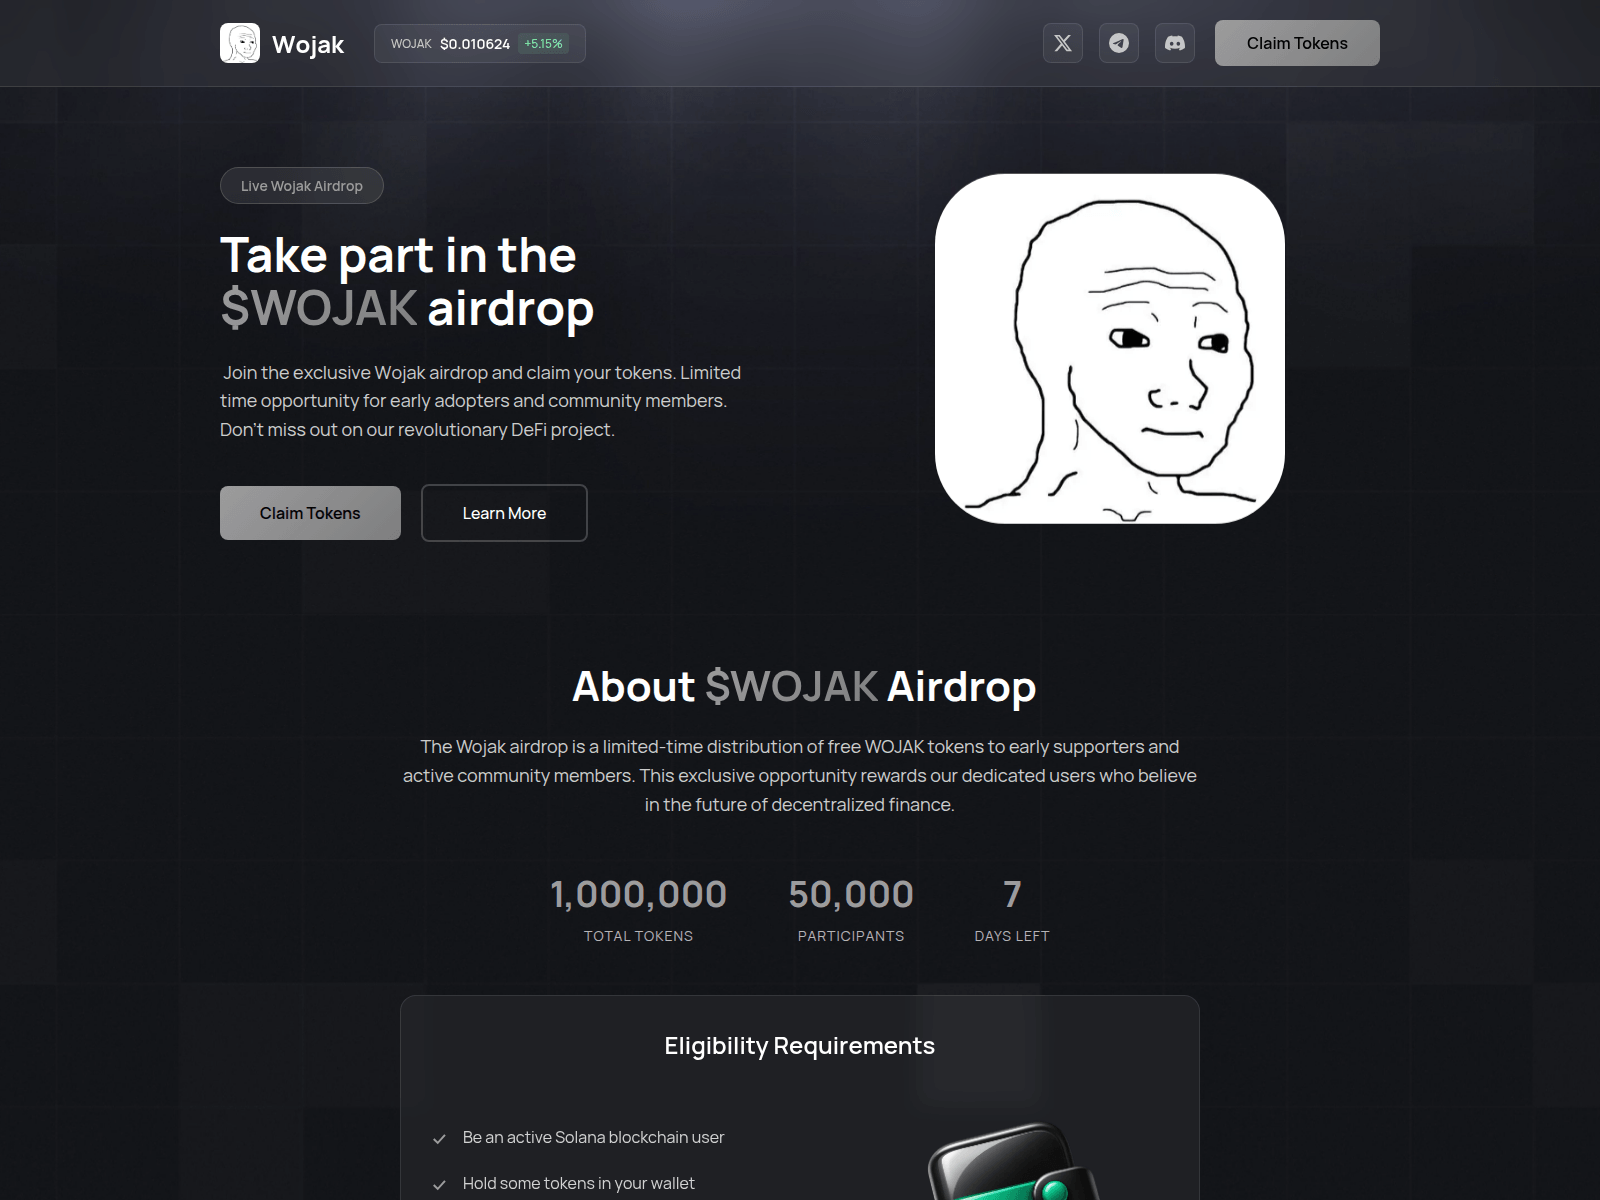
events-wojakmeme.xyz
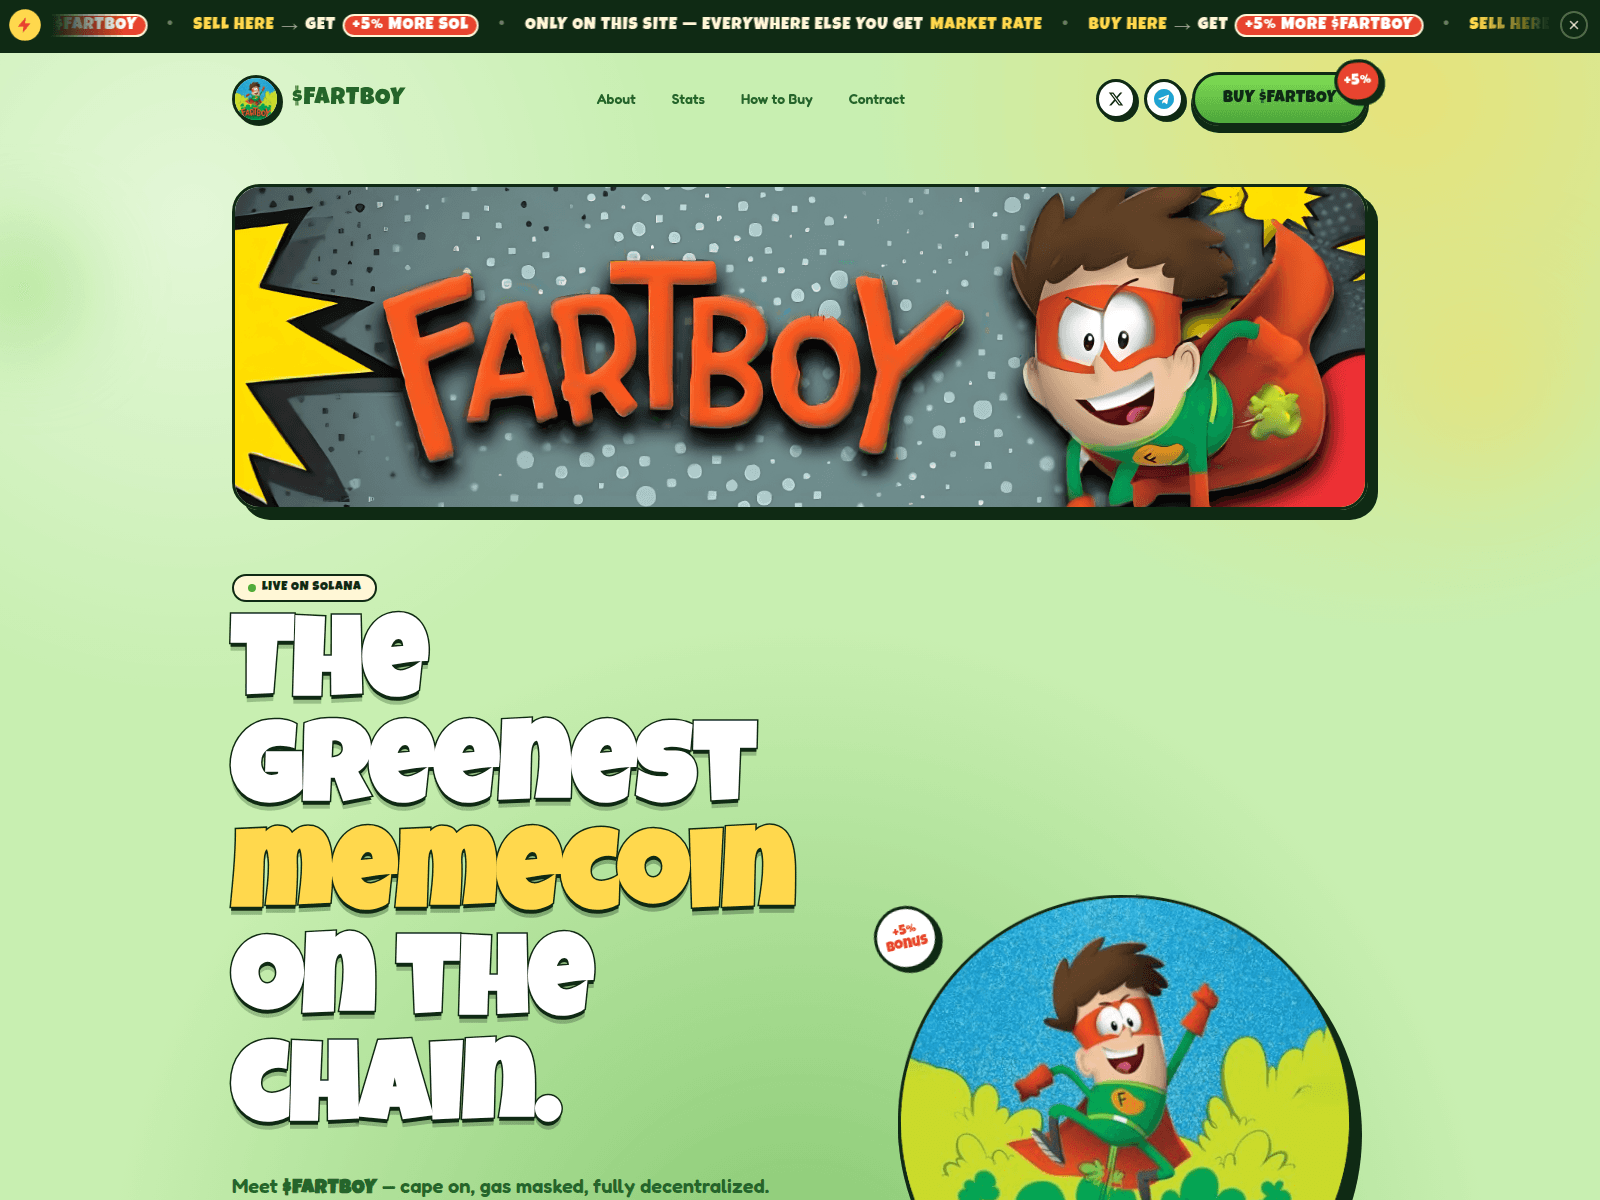
fartboysolana.com
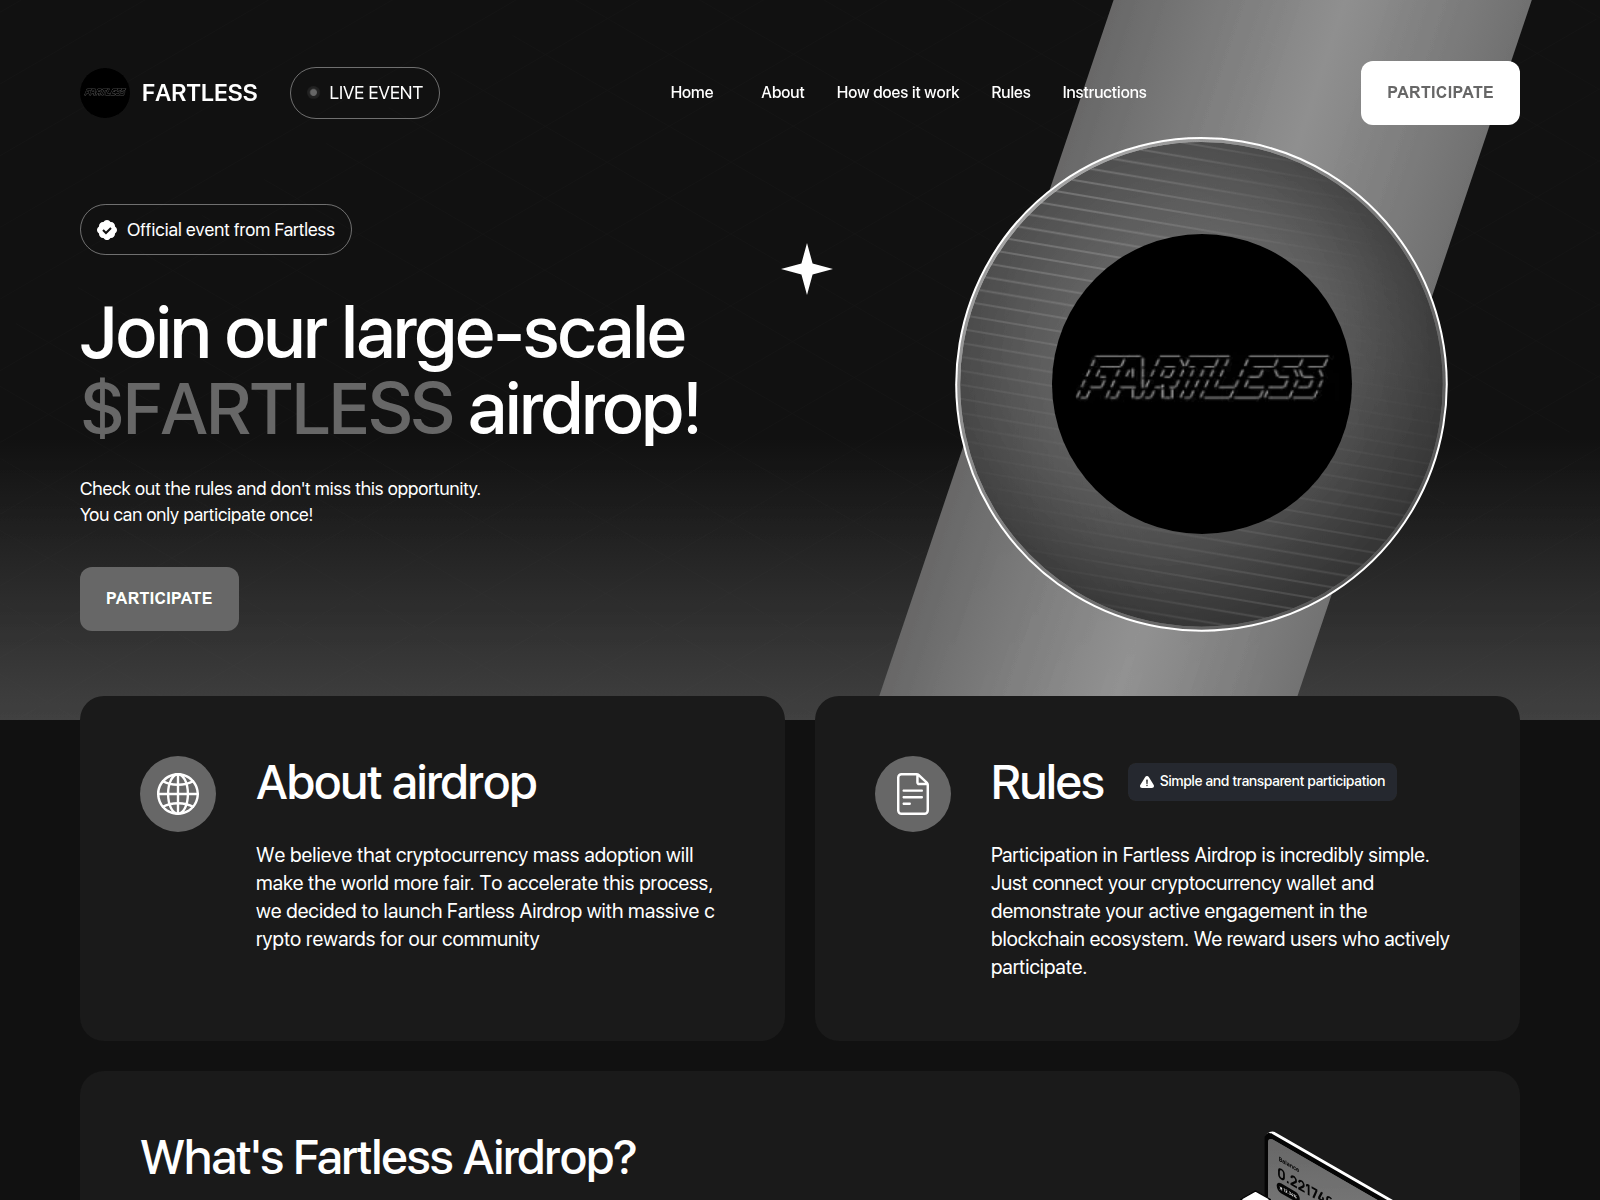
fartlessdrop.top
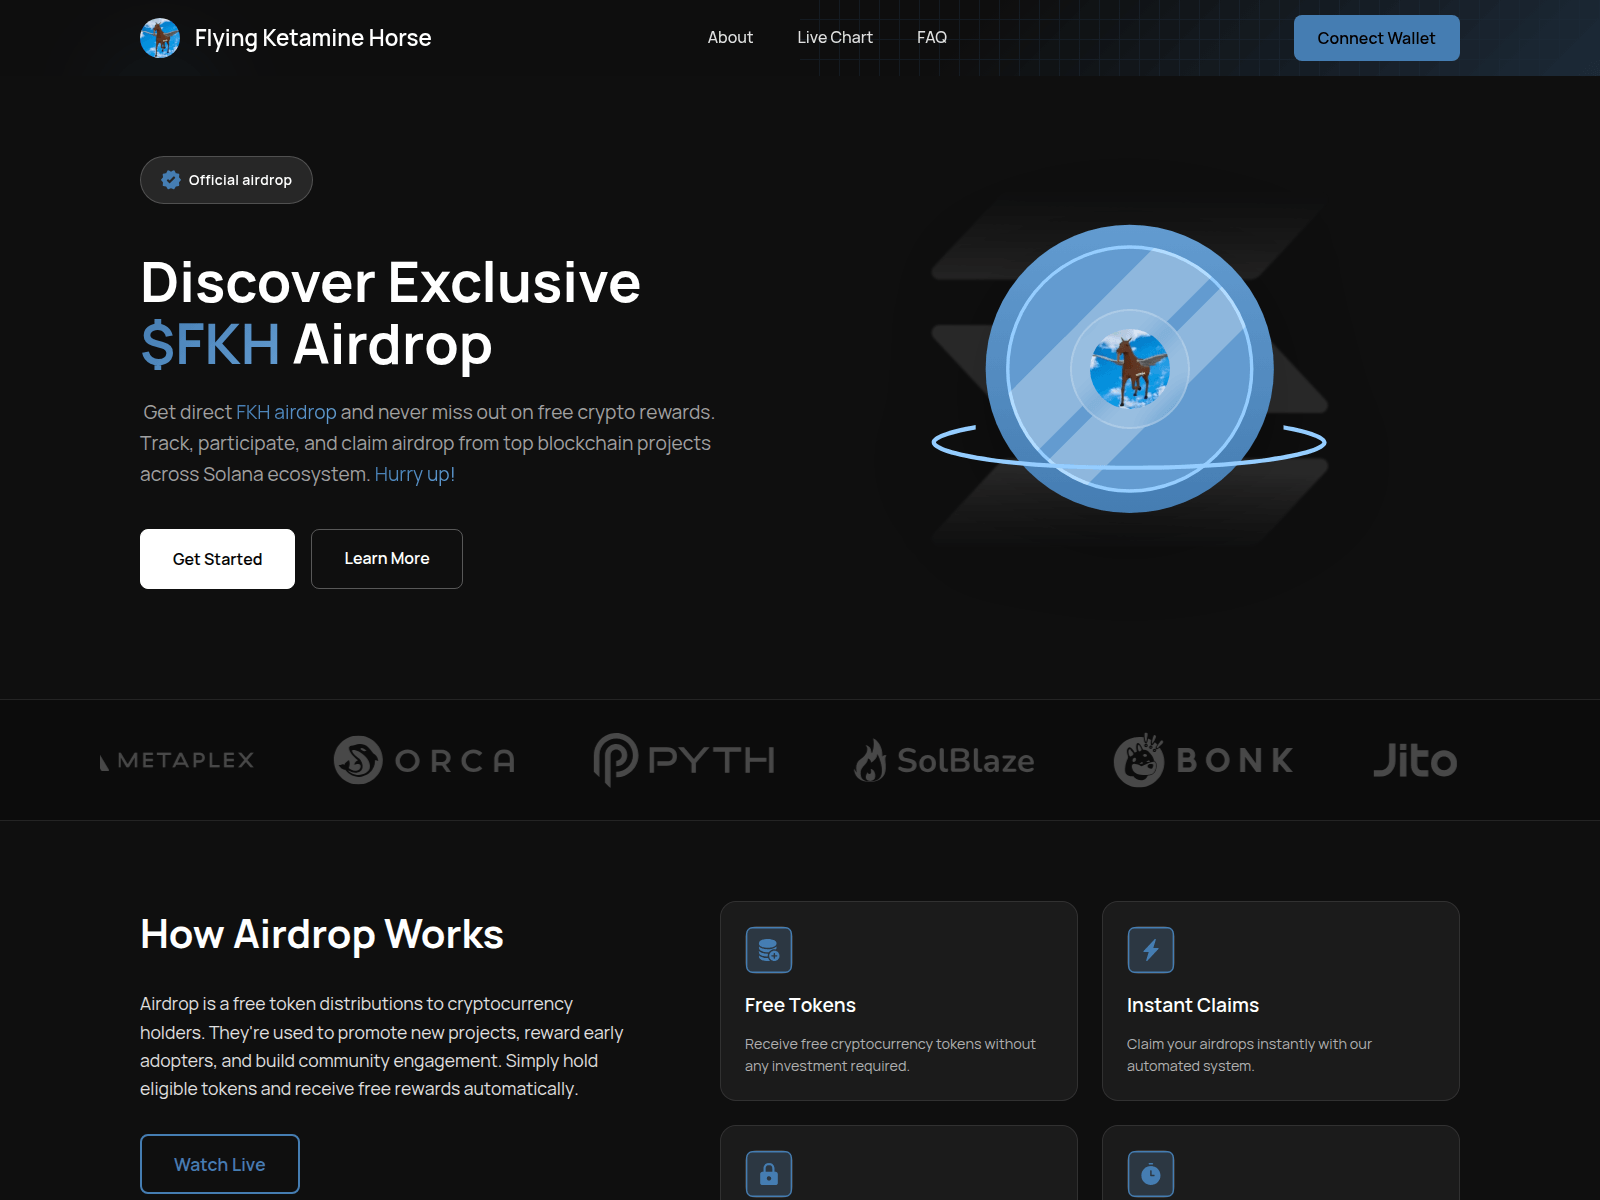
flyingketaminehorse.top
fomo.solcore.cc
fraudcoin.solfor.us
fumbledsol.xyz
fwogfam.top
glooponsolana.com
goopysolana.com
governance-solanamobile.icu
homeonmeme.world
hylo.network
ibizafinalboss.click
ieo-phantomwala.pages.dev
jarsairdrop.icu
jito.run
jitofi.xyz
join-babysol.xyz
join-peppen.xyz
join-qbscore.xyz
join-trollboys.xyz
jupboost.fun
jupiterswap.group
kimchiofficial.live
kmno-solana.airdrops-ak.lol
launchsol-sniper.com
learnsolana.app
lfinity.io
lootlanesol.click
masterbot-sol.fun
masterbotsolana.com
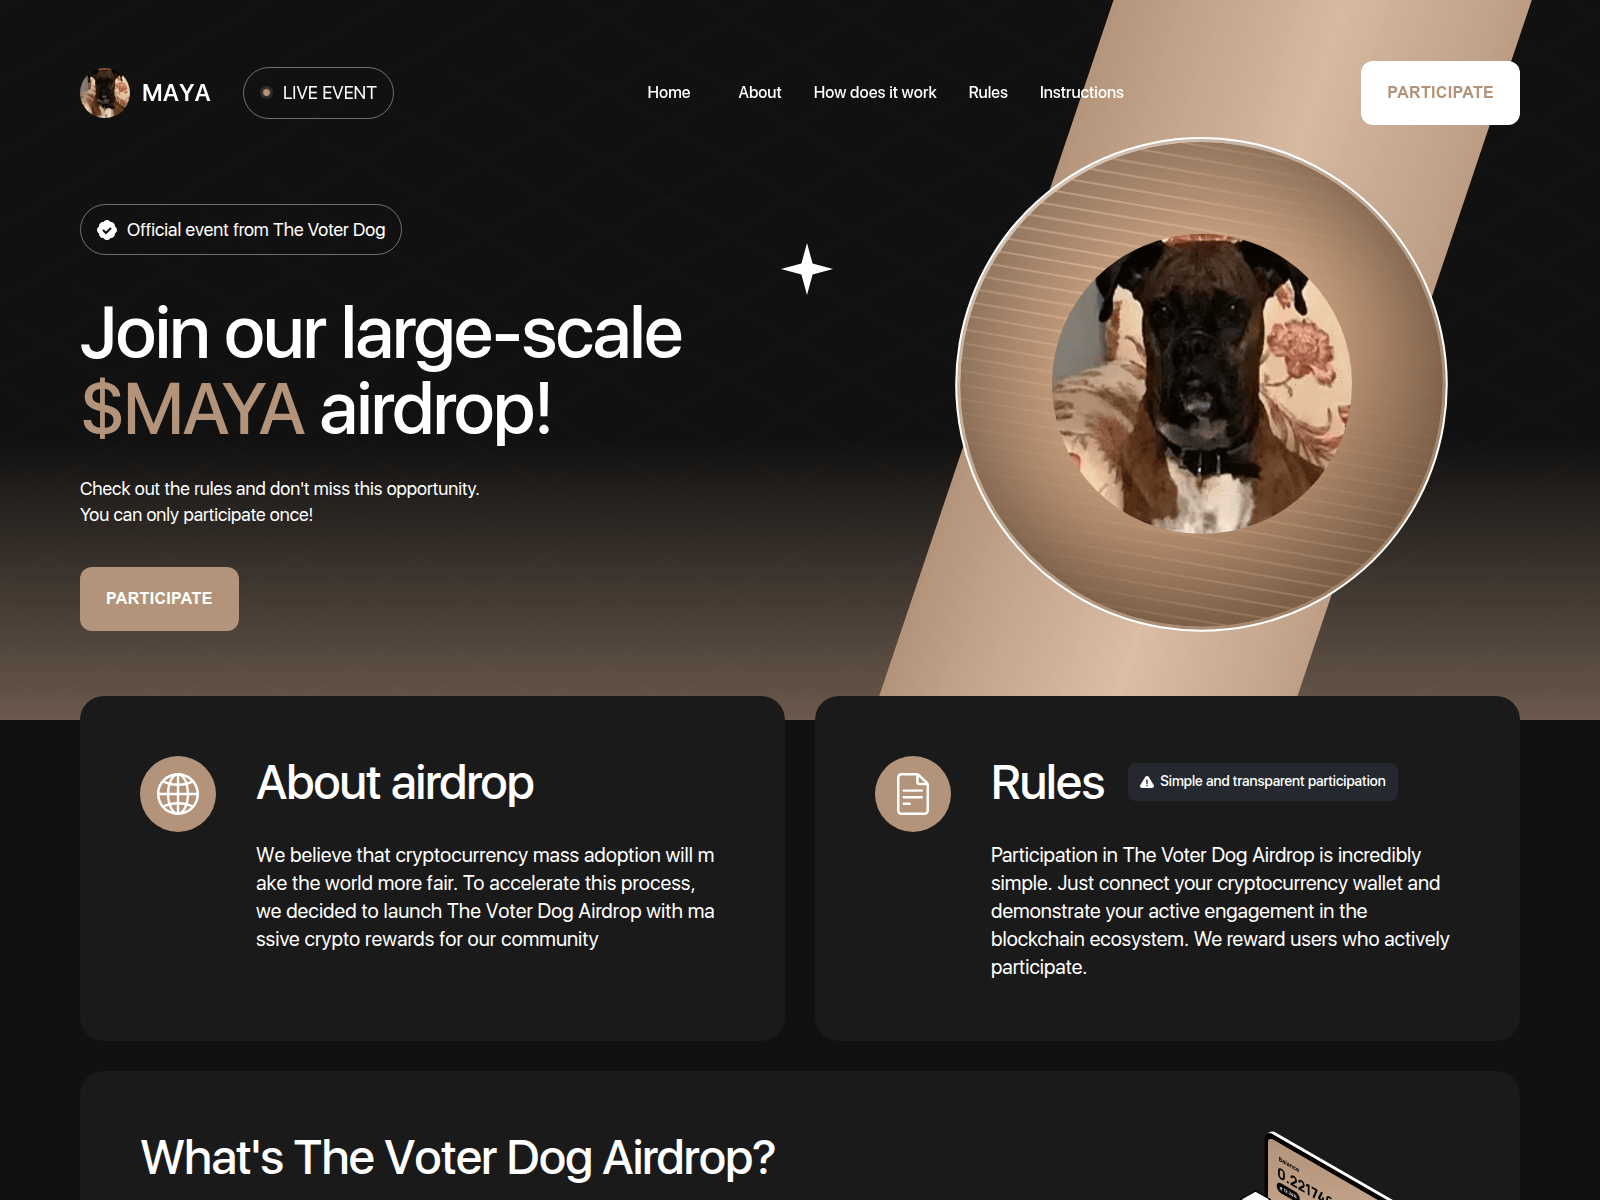
mayadog.bitpump.fun
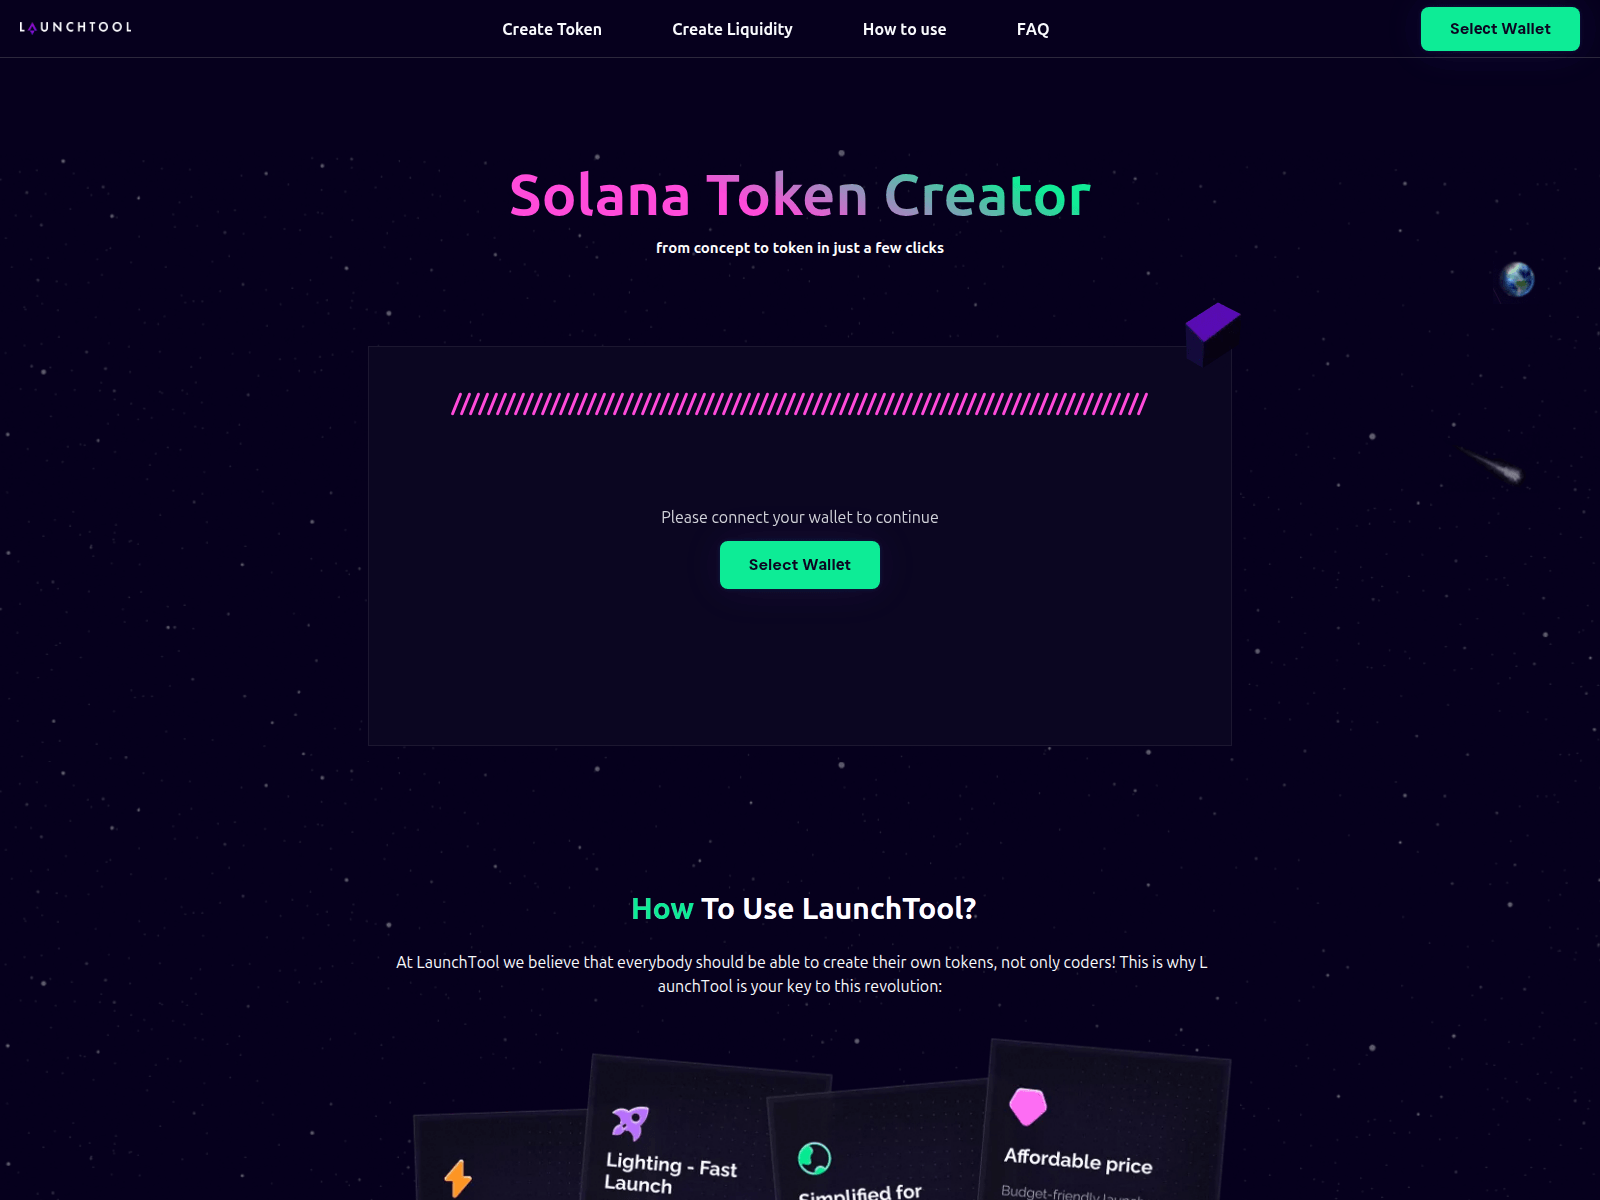
memedex.life
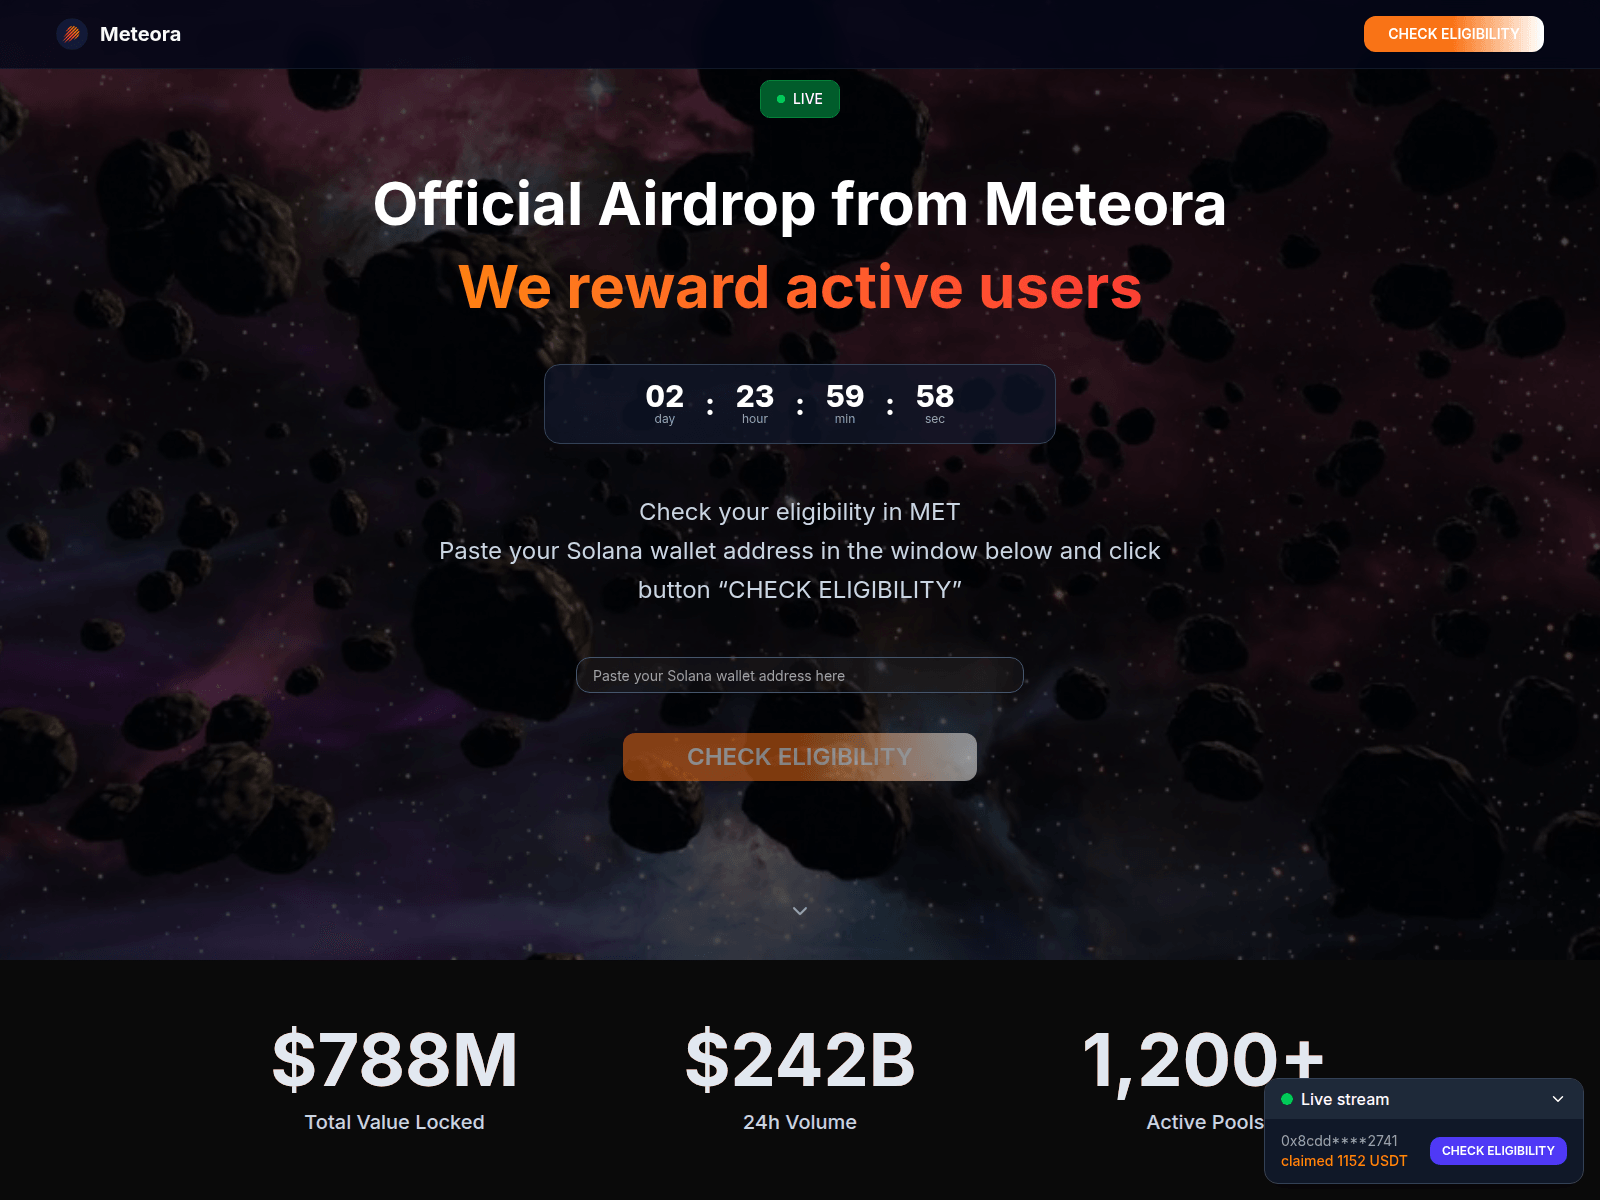
meteoracheck.live
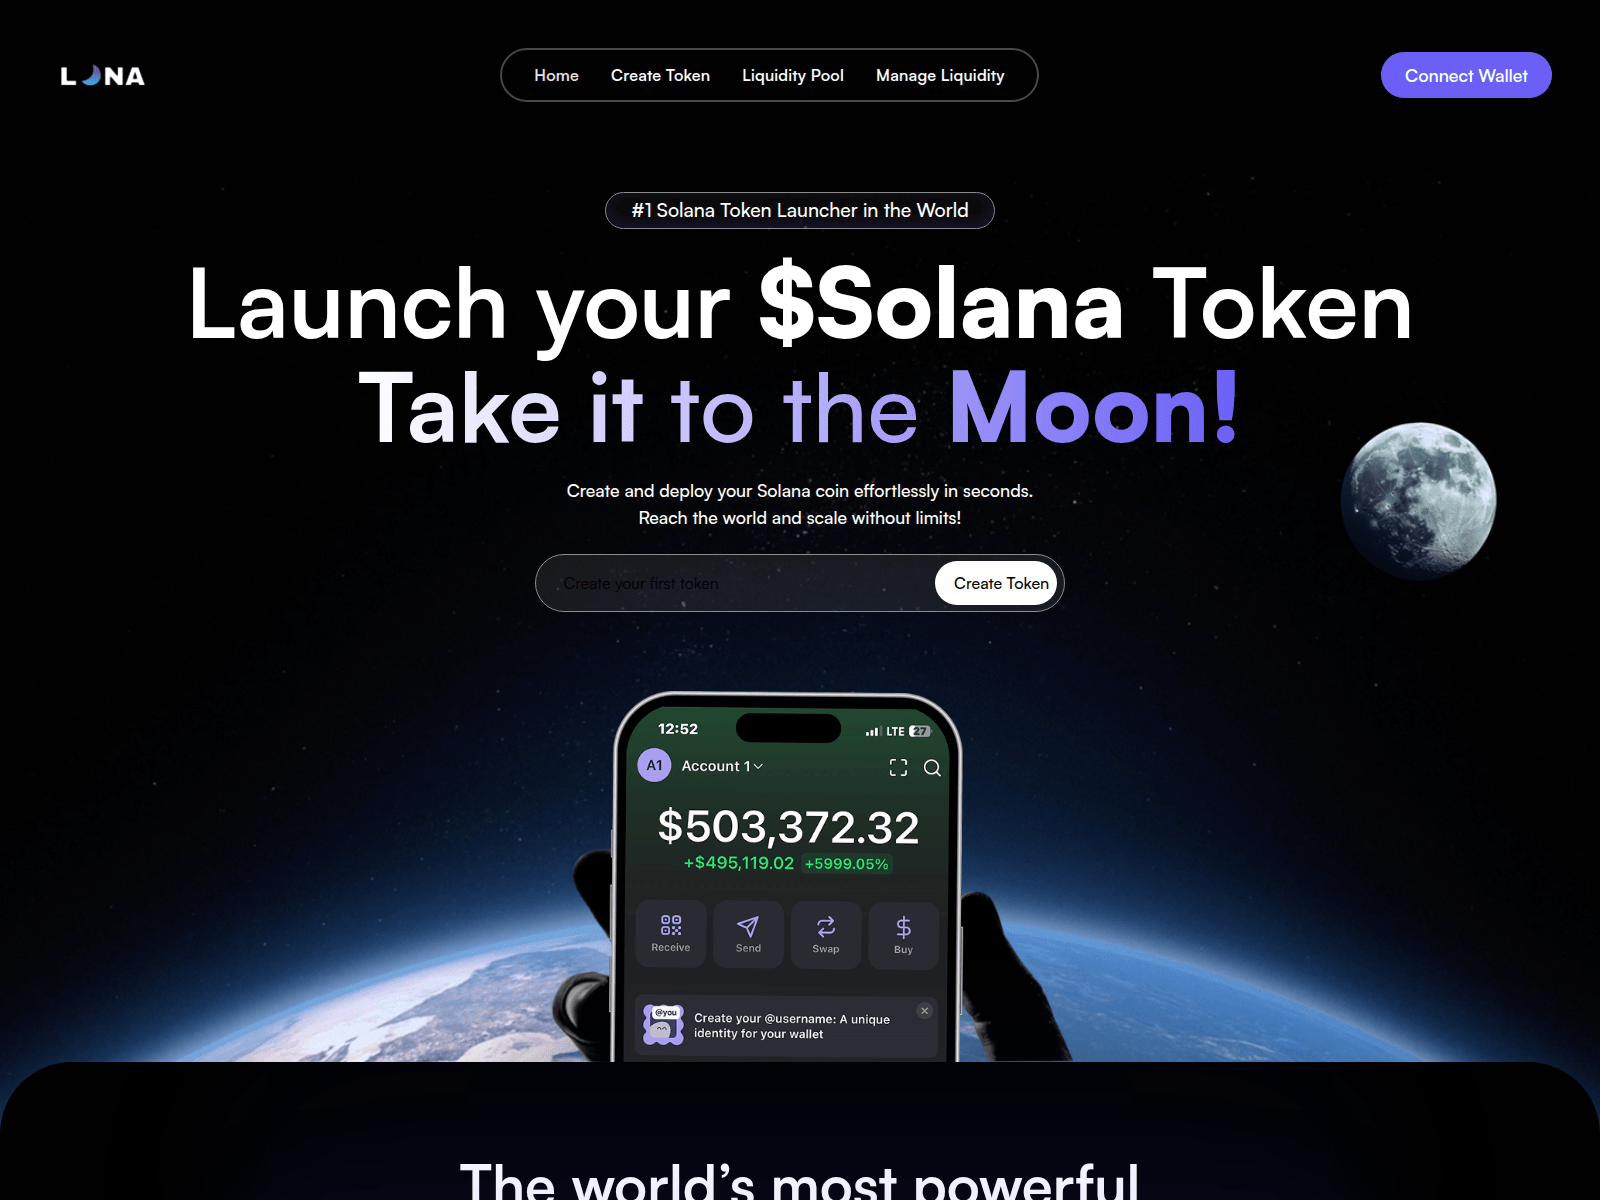
mintmemesol.company
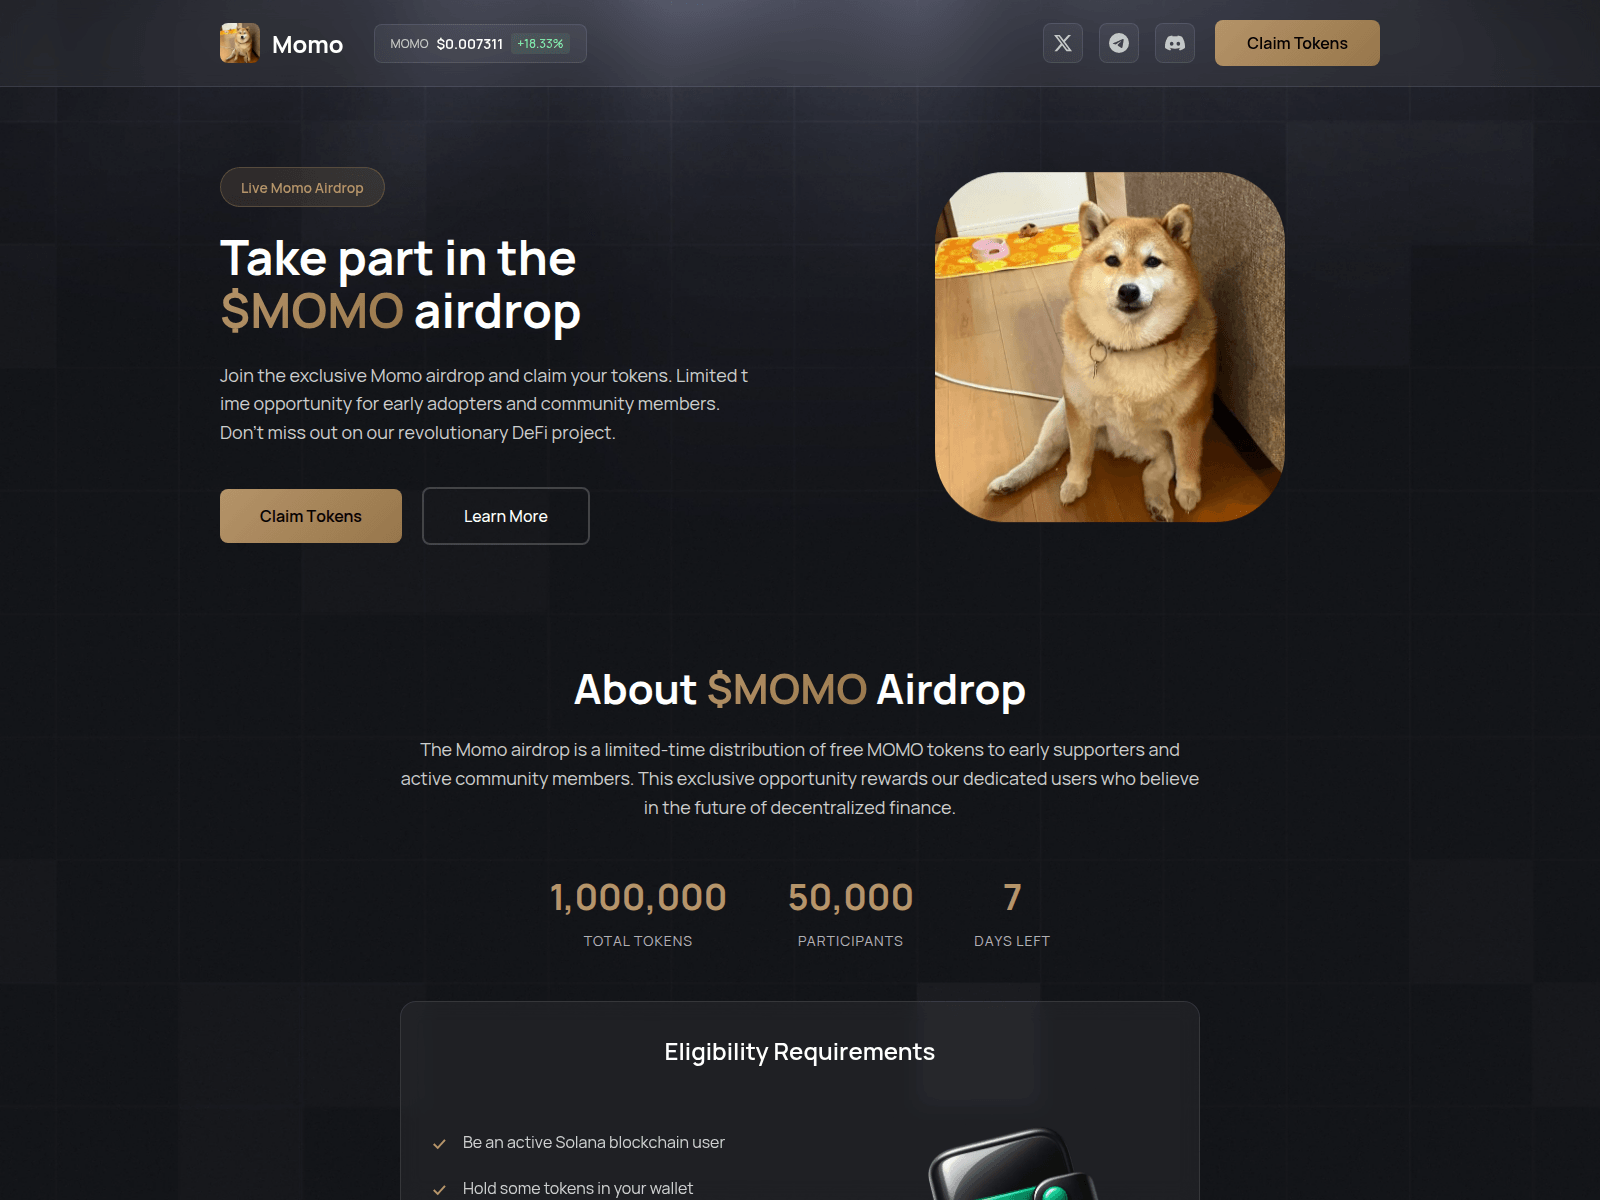
momo.onsol.pro
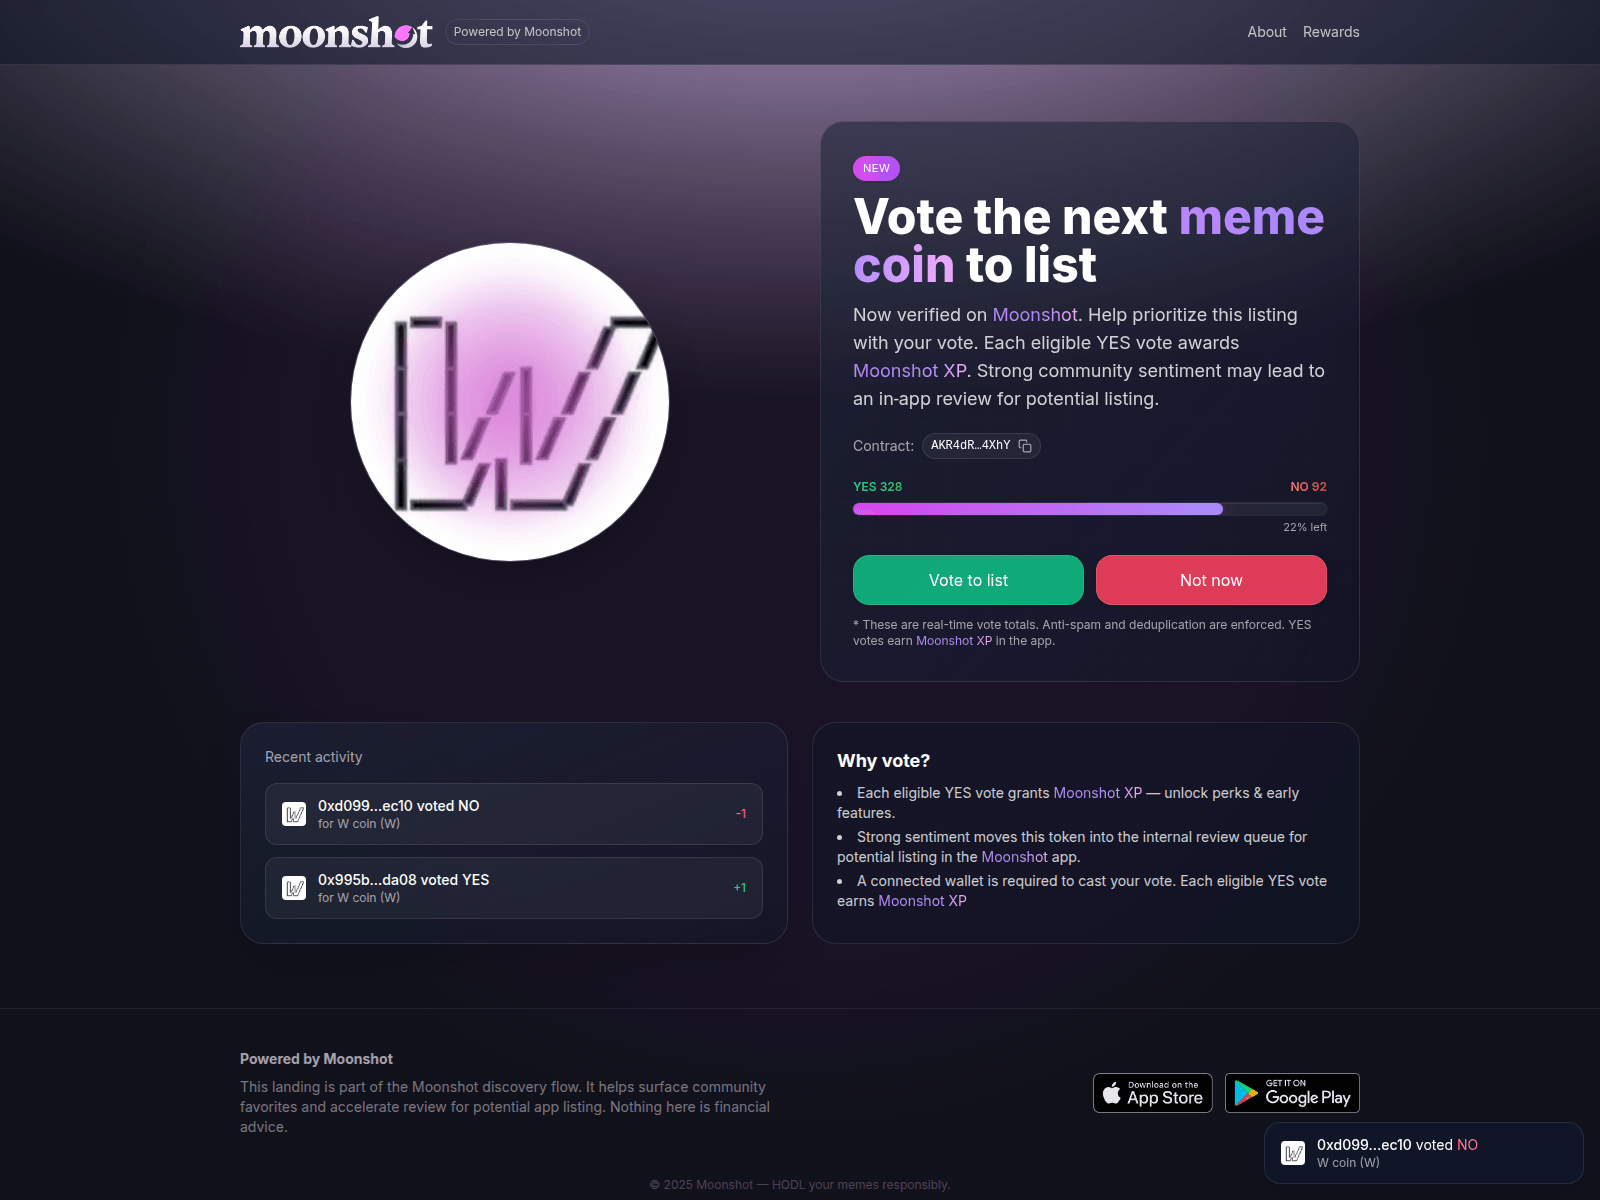
moonshotv.com
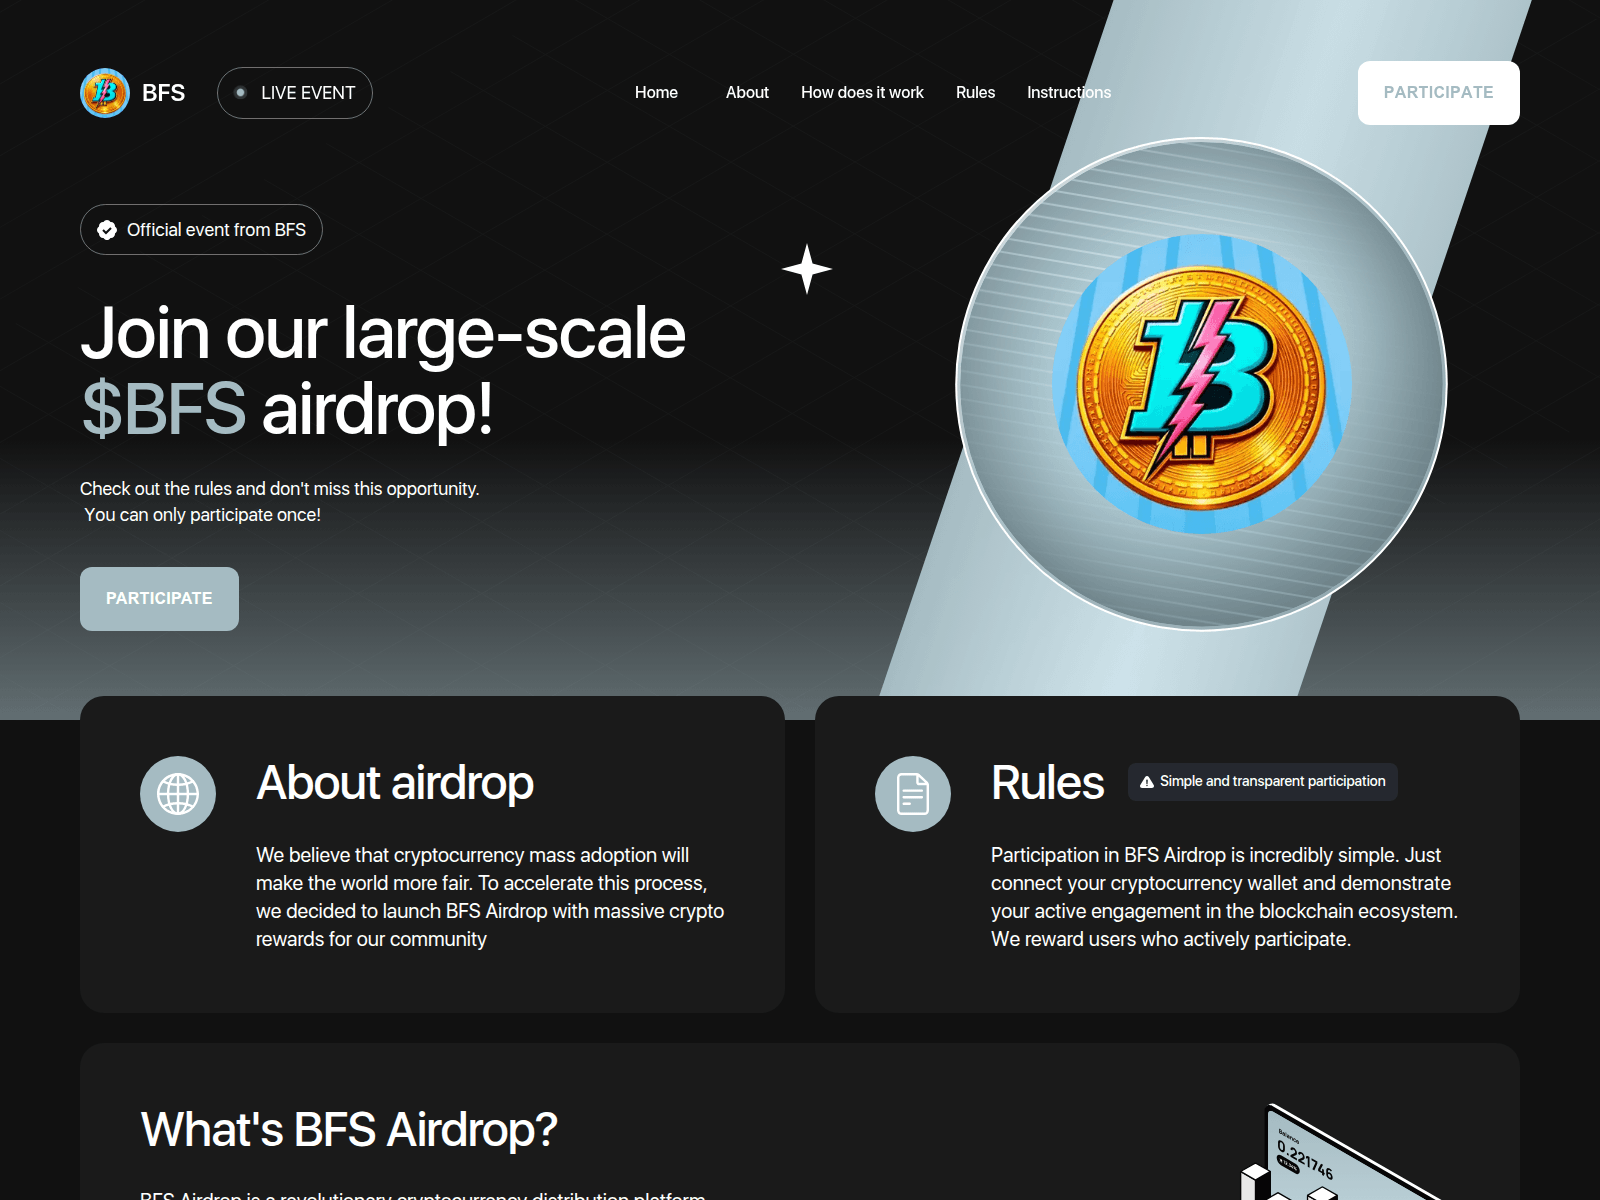
mrdropbfs.live
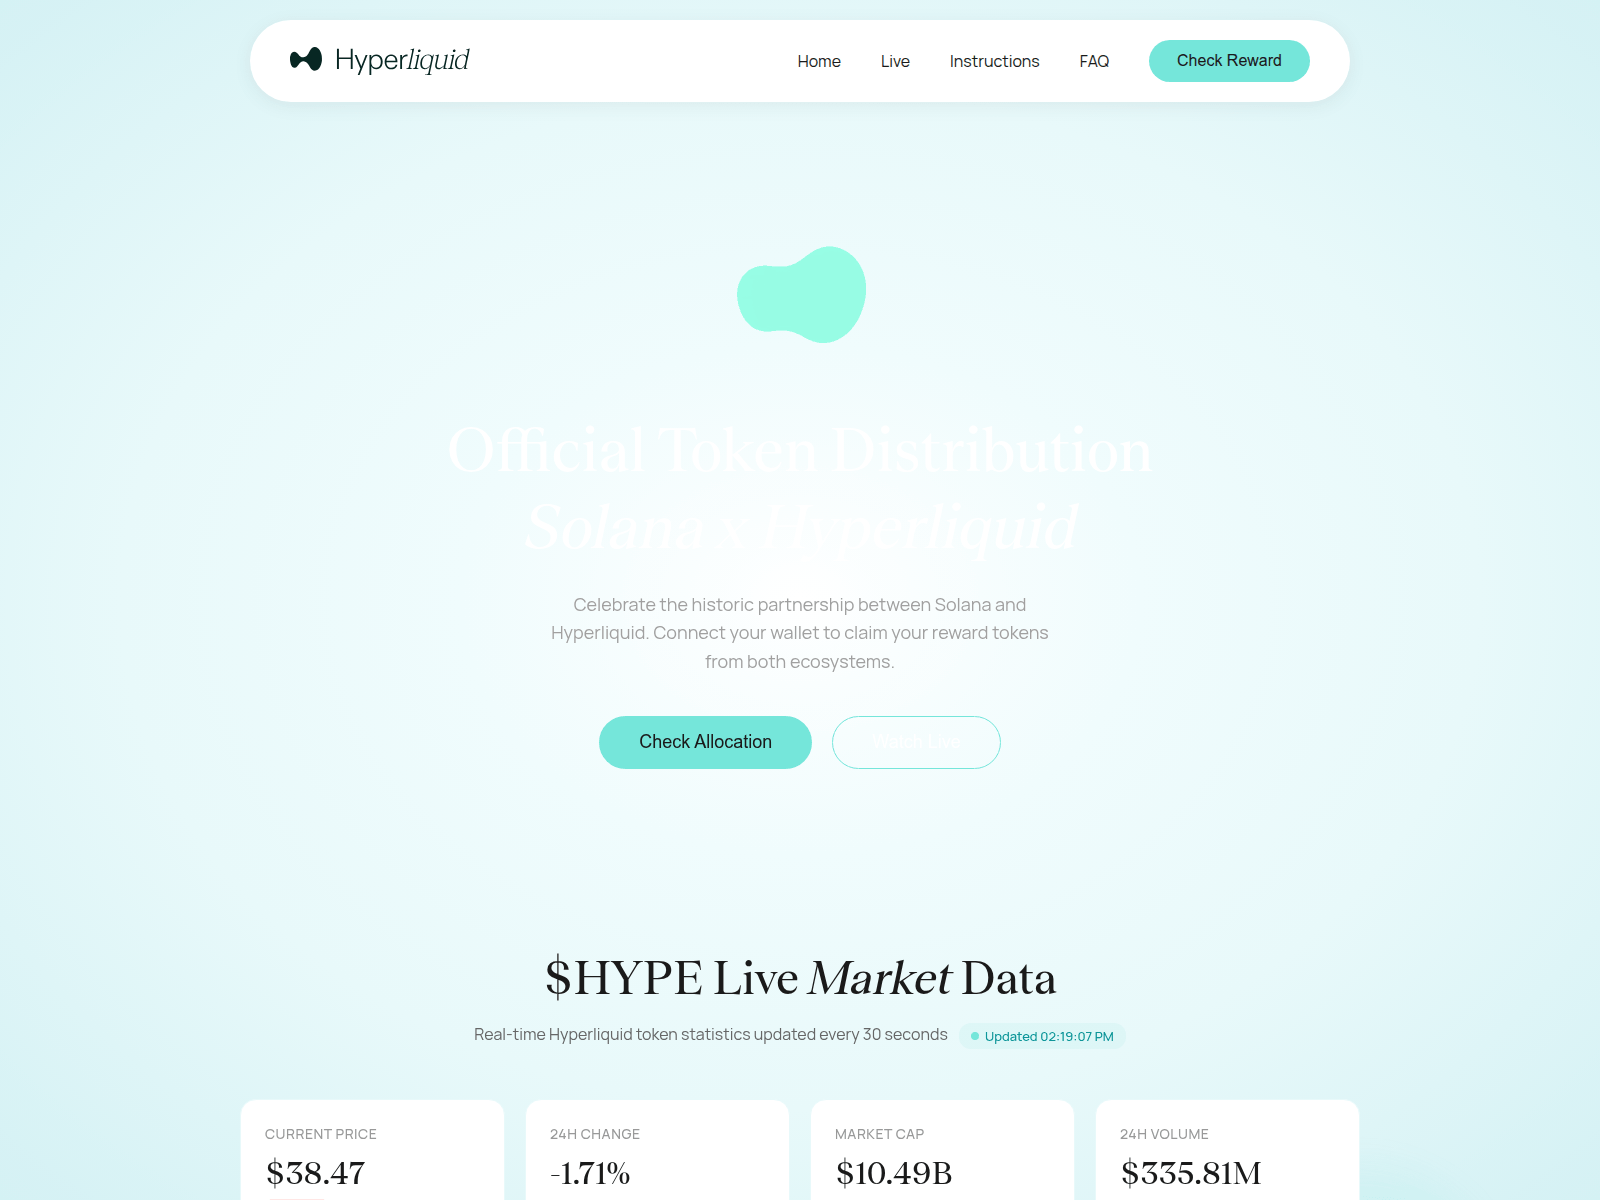
news-hypxerliq.xyz
opensupportteam.com
oreproject.top
pamtas.com
pandu.x-sol.us
pay-phantom.com
peacesolana.lat
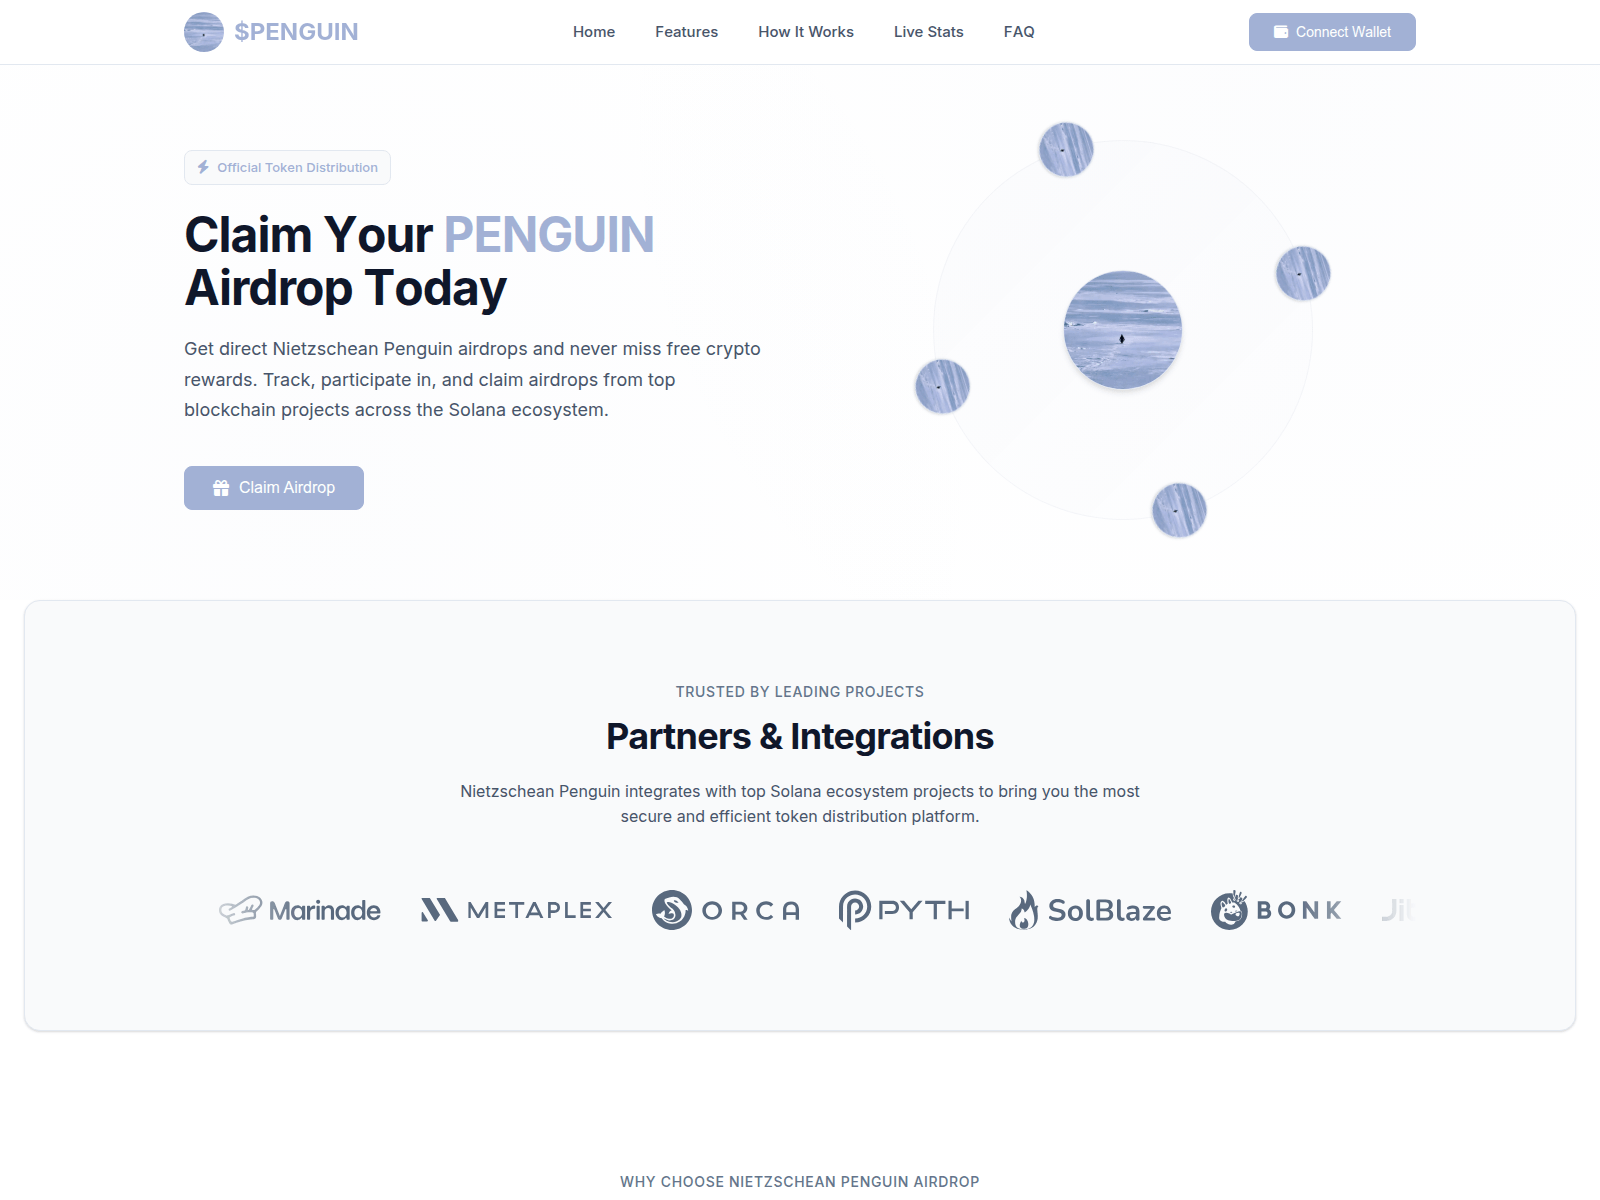
penguin.solchain.cc
penguinonsolana.xyz
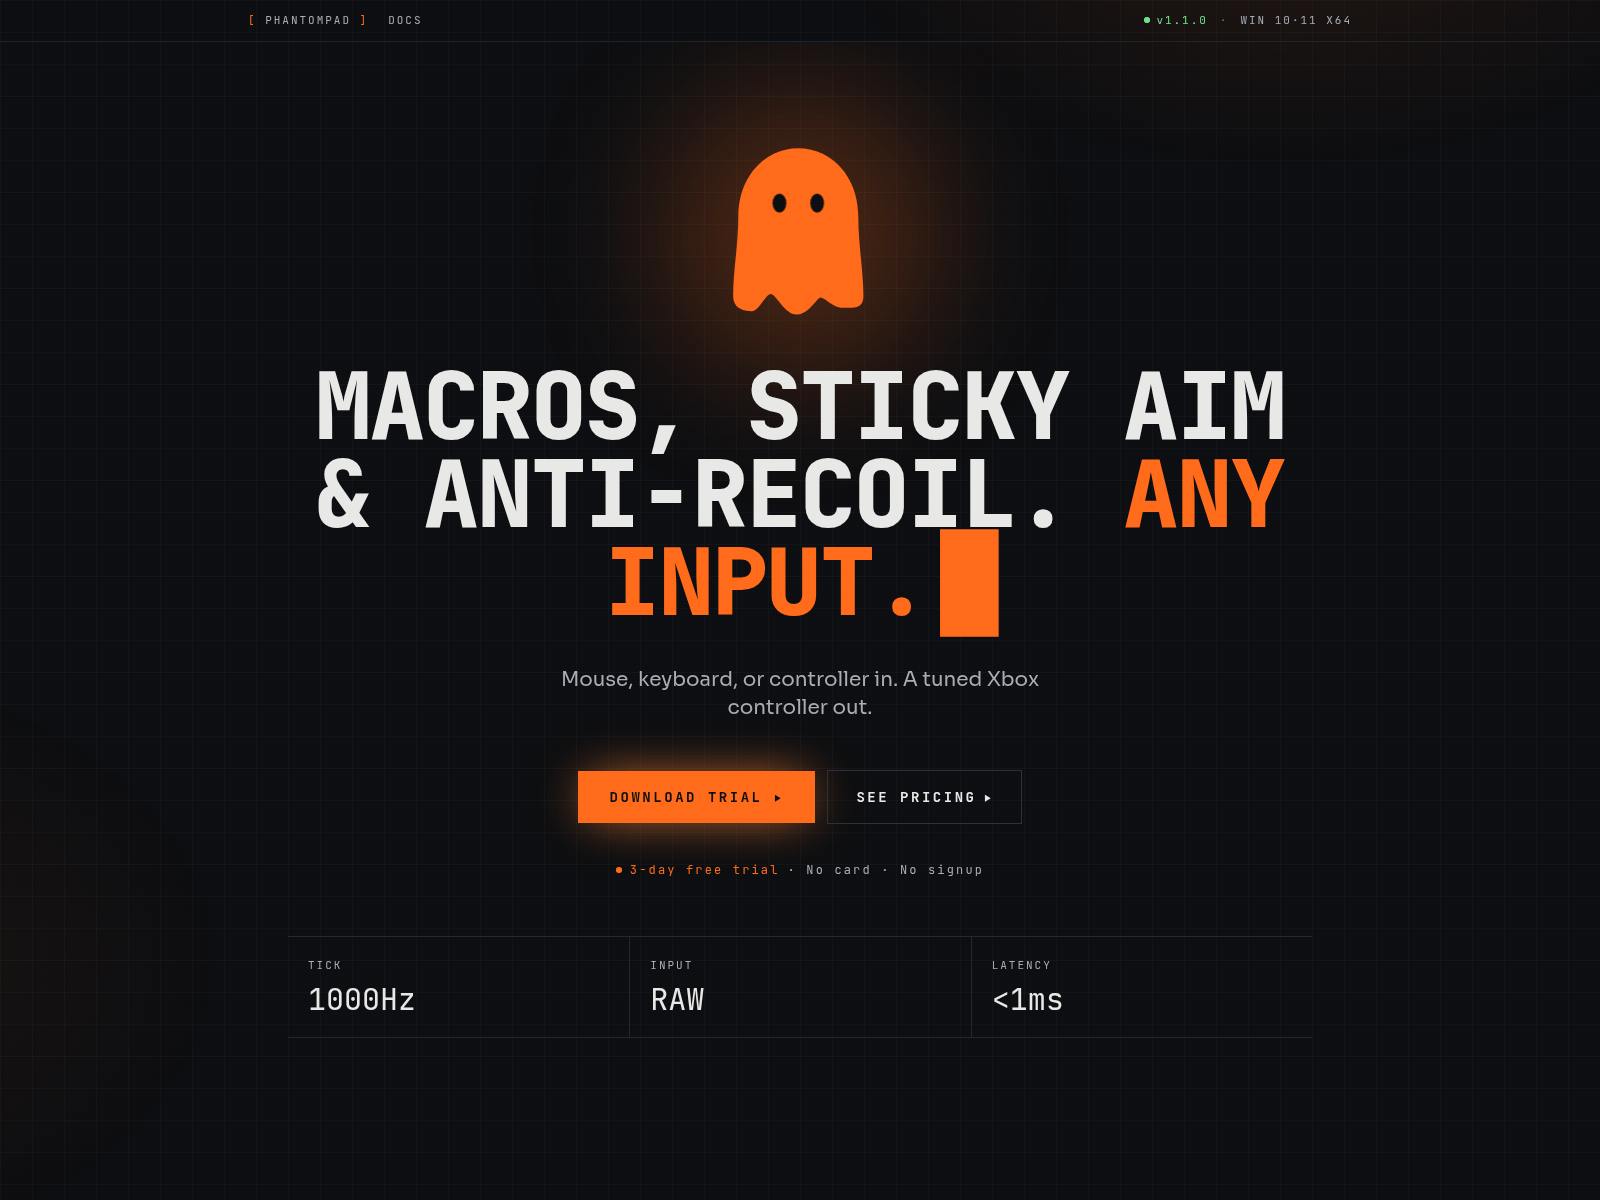
phantom-pad.com
phantom-sol-wiq.pages.dev
phantom-wallat-extantion-rho.vercel.app
脅威対応 Pipeline
このハブ内の各ドメインがどのように検証され、確認された脅威がどのように無力化されるのか。 パイプラインの完全な可視化 →
脅威インテリジェンスの確認— すべてのドメインについて、以下の項目との照合・確認が行われます:
urlscan.ioスクリーンショット · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency レポートCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesウェイバック・マシンHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS セキュリティ FiltersQuad9 · AdGuard · CleanBrowsingWeb-確認Full surface scan
 crt.sh
グローバルベンダー同期— 検出が確認されたデータは、29のパートナーにプッシュされます:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardビットディフェンダーThreat exchangeNortonSafe WebSymantecサイトレビューAviraCloud detectionAvast / AVGWeb ShieldカスペルスキーOpenTIPDr.WebOnline scannerネットクラフトテイクダウン APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.レポートHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust