VirusTotal
10 / 91 engine detections
Apri il rapporto

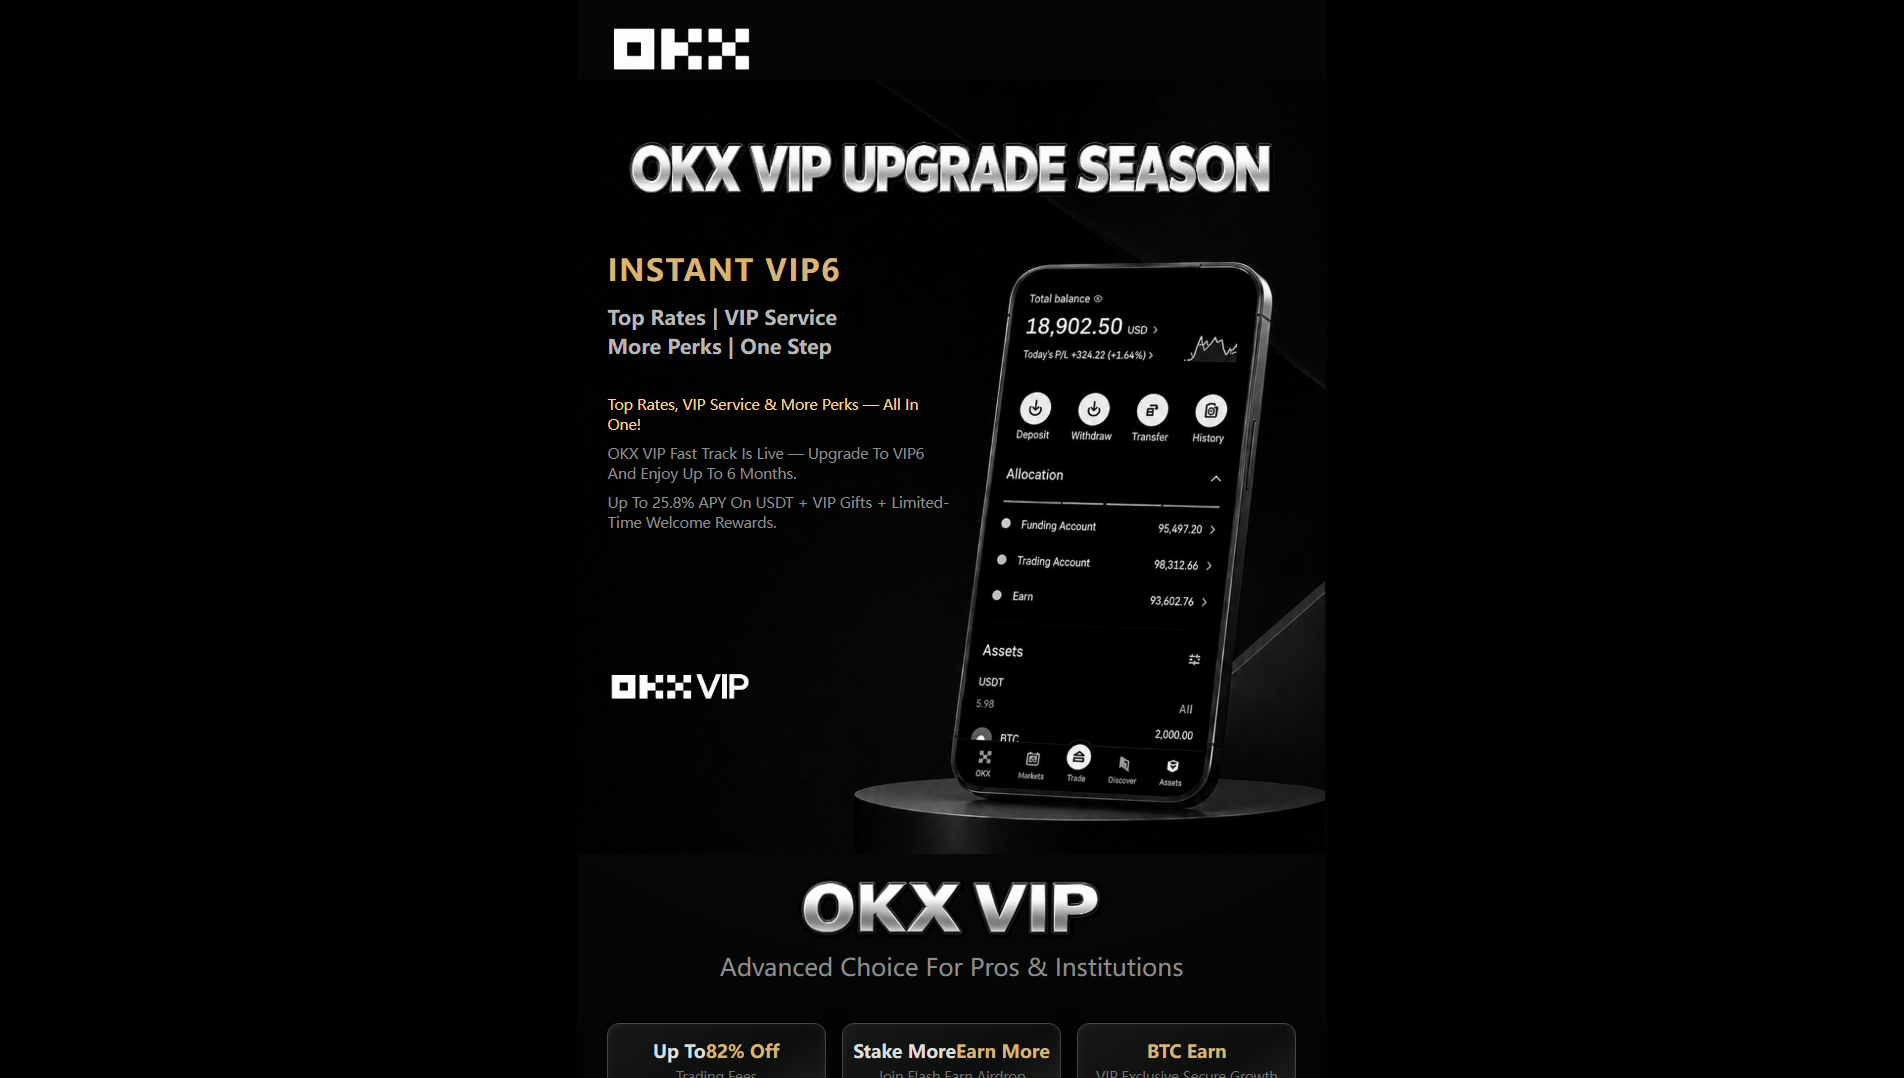
“OKX VIP Upgrade Season”
Imitazione di OKX: okx.boutique — Contenuto non disponibile. Riepilogo delle prove: VirusTotal 10/91 (alphaMountain.ai, CRDF, ESET, Emsisoft, Fortinet)…
L’analisi dettagliata di PhishDestroy AI resta in inglese per preservare il rapporto forense originale.
10 / 91 engine detections
Apri il rapporto2 threat-system alerts
Apri il rapportoMalevolo
Apri il rapportoMalevolo
Apri il rapportono community references
Apri il rapportoNo threat flag
Apri il rapportoResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| DNS4EU | www.jx9adrpc5z8094di7.net |
malicious | Sinkholed |
| Cloudflare DNS | okx.boutique |
malicious | Sinkholed |
PhishDestroy threat report
okx.boutique was a phishing site posing as the OKX crypto exchange under the banner "OKX VIP Upgrade Season". It targeted OKX customers who might believe they were being offered a higher account tier. PhishDestroy first flagged it on 2026-09-01. The site went offline on 2026-09-07, and its DNS was still inactive when last checked on 2026-10-19.
The "VIP Upgrade Season" theme plays on the real tier perks exchanges offer, such as lower fees and higher limits, so the visitor feels they are claiming a reward. Pages like this usually ask the user to sign in to "activate" the upgrade, which hands their OKX email, password and one-time 2FA codes to the operators. Some variants also ask the user to connect a wallet or send a qualifying deposit. Either way, the victim risks losing control of their exchange account and any funds in it.
Ten of 91 VirusTotal engines flagged the domain as of 2026-09-03, including ESET, Kaspersky, Fortinet, Netcraft, Emsisoft, Gridinsoft, CRDF and alphaMountain.ai. That is a modest count, but it comes from a broad mix of established vendors. urlscan.io rated the page malicious and recognised OKX branding on it. The domain is also on the MetaMask and SEAL blocklists alongside PhishDestroy, so wallet users were warned at the browser-extension level.
The domain was registered on 2026-08-30 through GNAME.COM PTE. LTD., just two days before PhishDestroy detected it. That short gap fits a throwaway domain bought for a single campaign. The .boutique extension lets the brand name sit alone as the second-level domain, which makes the address look plausible at a glance. The site was served through Cloudflare's network, with the address geolocated to Canada, which hides the real origin server.
If you signed in on this page, change your OKX password immediately. Then reset your 2FA and log out all other sessions. Check your account for new API keys, unfamiliar withdrawal addresses or changed security settings, and contact OKX support if anything looks wrong. If you connected a wallet, revoke any approvals you granted and move funds to a fresh wallet if you signed anything unusual. Defenders should block the domain and watch for new registrations pairing "okx" with novelty extensions, since this kind of campaign is often re-hosted quickly.
Last checked
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
La reputazione Edge-IP non è attribuita a questo dominio.
jo.ns.cloudflare.comrene.ns.cloudflare.comLocation describes the IP network.
Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of okx.boutique · checked Sep 1, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
okx.boutique
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Sconosciuto→dns_inactive
dns_nxdomain
Sconosciuto→dns_inactive
dns_nxdomain
Sconosciuto→dns_inactive
dns_nxdomain
Sconosciuto→dns_inactive
dns_nxdomain
Sconosciuto→dns_inactive
dns_nxdomain
Sconosciuto→dns_inactive
dns_nxdomain
Sconosciuto→dns_inactive
dns_nxdomain
Sconosciuto→dns_inactive
dns_nxdomain
Sconosciuto→dns_inactive
dns_nxdomain
dns_inactive
dns_nxdomain
Raggiungibile→Non disponibile
Raggiungibile
10/91 engine detections
View sourceNo threat flag
View sourcePD-20260901-70632E
okx.boutique
View sourcePage captured
View source89 domini simili memorizzati
Ogni riga rappresenta un motivo per cui un dominio è collegato a questo host. I nodi a dimensione intera indicano rilevamenti di VirusTotal, mentre quelli tratteggiati sono già offline. Di seguito è riportato l'elenco completo.
Stesso hash della favicon o stesso titolo della pagina di questo host.
Questi report si risolvono nello stesso IP edge condiviso. Aiutano con l'individuazione dei report ma non implicano la proprietà comune o un server di origine condiviso.
Reports with the same collector label. A shared label does not establish impersonation or common ownership. View matching reports →
Registrati tramite lo stesso registrar. Un registrar serve milioni di clienti non collegati tra loro, quindi questo dato indica semplicemente un raggruppamento piuttosto che dimostrare un nesso.
PD-20260901-70632E Recipient: complaint@gname.com Registrar: Gname.com Pte. Ltd. (Singapore) Policy Violations: Illegal Activities section forbids phishing, fraud, fake sites, malware distribution; registrar investigates and may suspend or delete domain Applicable Laws: Computer Misuse Act 1993 §§3+, Penal Code §§415–420 (cheating), Online Criminal Harms Act (OCHA)
Se hai inserito credenziali dell'account, informazioni personali o di pagamento oppure hai scaricato un file da questo dominio, agisci immediatamente. Di seguito sono riportate le risorse per aiutarti a segnalare l'incidente e proteggerti.


Seleziona il tuo Paese per ottenere contatti ufficiali del crimine informatico o creare una bozza di reclamo →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
okx.boutique)Anche se non conosci tutti i dettagli — sporgere comunque denuncia. Anche le informazioni parziali sono comunque utili alle indagini.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Analisi delle minacce utilizzando blocklist archiviate, WHOIS, DNS e prove di scansione pubblica
Scansiona oraSegnala i domini sospetti al nostro database delle minacce — proteggi la comunità
SegnalaSegnalazioni recenti di phishing e modifiche osservate della disponibilità
MonitoraControlla le minacce in tempo reale oppure contesta questa segnalazione se ritieni che si tratti di un falso positivo
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.