Lompat ke laporan keamanan
Keamanan domain dan intelijen ancaman
trustwalletpay.cloud favicon

trustwalletpay.cloud

“Wallet Payment · USDC Authorization”

Registrar
Hostinger
Resolved IP
173.208.142.58
Registered
09/10/2026
Putusan ancaman Tinggi
Spamhaus DBL: DBL_PHISH Daftar blokir yang disimpan cocok: 2 Peniruan identitas merek: Trust Wallet Domain muda: 1 berumur hari
OTX: 1 ref 11/10/2026 Trust Wallet
API
Domain ini telah ditandai sebagai berbahaya
Daftar blokir publik yang melaporkan kecocokan: 2. Berhati-hatilah — jangan memasukkan kredensial atau informasi pribadi.
Ringkasan laporan

trustwalletpay.cloud — Belum terverifikasi. Peniruan identitas merek: Trust Wallet; Jenis penipuan: Impersonation. Ringkasan bukti: URLScan capture; Spamhaus DBL_PHISH; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 66/100. Registrar: Hostinger.

Analisis terperinci PhishDestroy AI di bawah tetap berbahasa Inggris untuk menjaga catatan forensik asli.

Spamhaus DBL
DBL_PHISH

OTX references
URLScan
URLScan
Sertifikat TLS
Kedaluwarsa atau belum diverifikasi
Usia
1d Brand New!
PhishDestroy
Daftar Hapus
Terdaftar

Source evidence

5 sources

Spamhaus DBL

DBL_PHISH

URLQuery

Report stored; detailed verdict not recorded

Laporan

OTX

1 community reference

Laporan

URLScan capture

laporan yang disimpan

Stored URLScan capture preview
Laporan

Google Safe Browsing

Checked; no threat flag recorded

Laporan

Ringkasan bukti

Tinggi
OTX
1 community ref
URLScan
Stored capture

Assessment

TrustWalletPay.cloud was externally blocked by MetaMask and SEAL as of 2026-10-11, per dated observation. The domain was also listed internally by PhishDestroy, which is a distinct indicator from external blocklists.

Recorded Evidence

MetaMask and SEAL both recorded trustwalletpay.cloud on their external blocklists as of 2026-10-11. The domain was first observed on 2026-10-11 and internally listed by PhishDestroy on the same date. Its registration was recorded with HOSTINGER operations, UAB on 2026-10-09, and its SSL certificate was issued by Let's Encrypt / YR1.

Interpretation

PhishDestroy contains an internal listing for trustwalletpay.cloud, which is a measurement of its own internal assessment. External blocklists such as MetaMask and SEAL provide records of detection, each documenting their own criteria and scope. The timeline shows that these observations were made within a close range of dates, allowing for comparison of how quickly different sources recorded the domain.

Recommended Actions

For trustwalletpay.cloud, preserve the blocklist entries from MetaMask and SEAL as distinct records for ongoing reference. Compare the internal listing from PhishDestroy with external blocklist records to track any future changes or additional entries. Maintain a record of the registration and SSL certificate details for technical context in future assessments.

Analisis deteksi dan penghindaran

Pemeriksaan penyamaran dan distribusi lalu lintas

Belum dipindai Belum ada perbedaan yang tercatat antara crawler dan browser

Data pengamatan perbandingan crawler versus browser yang telah disimpan untuk host ini, ditambah pemeriksaan sidik jari secara real-time untuk sistem distribusi lalu lintas bergaya Keitaro.

Bendera penyamaran yang tersimpan
Belum dipindai
Pemindaian penyamaran terakhir

Catatan pemindai: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='trustwalletpay.cloud', port=80): Max retries exceeded with url: / (Caused by NewConnection

Pemeriksaan sidik jari secara langsung melalui TDS
Tujuh sidik jari Keitaro ditambah perbandingan antara crawler dan browser; jalankan dari pemindai PhishDestroy saat panel ini terbuka.
Menunggu

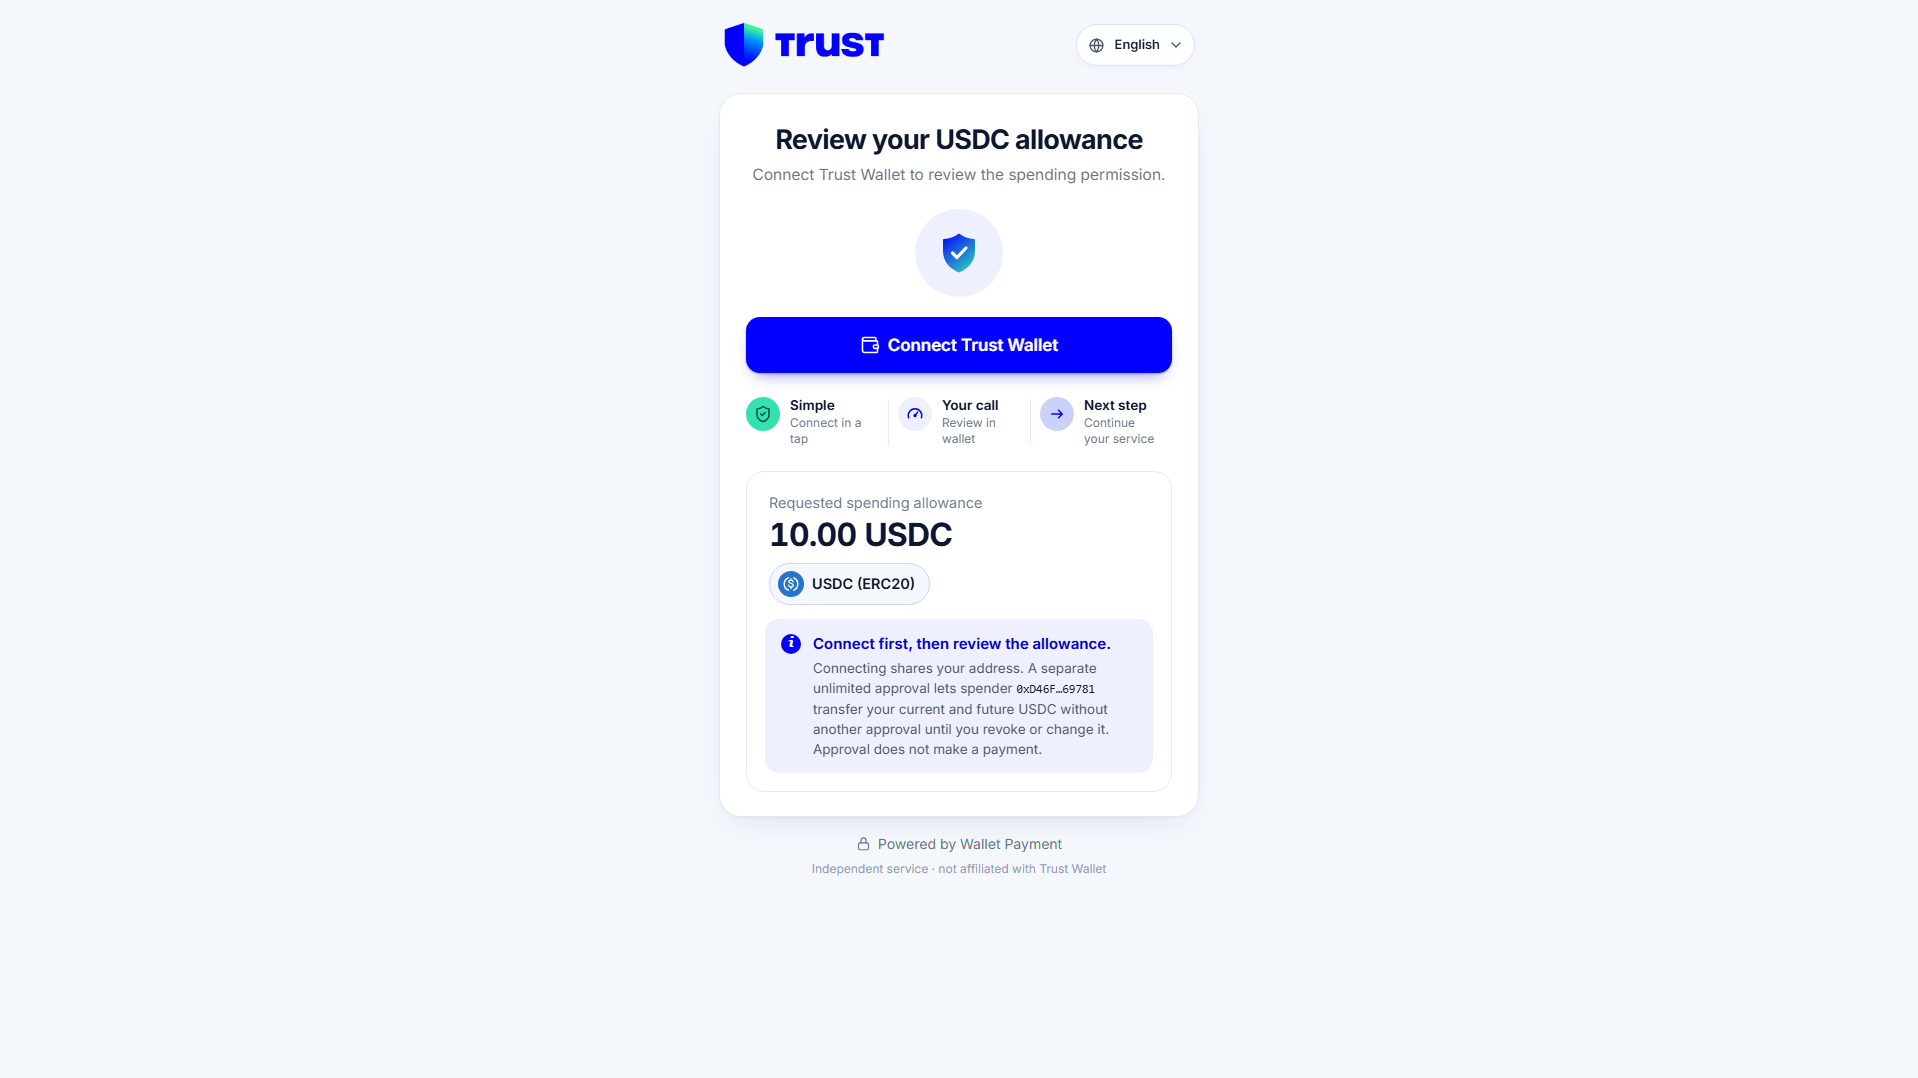
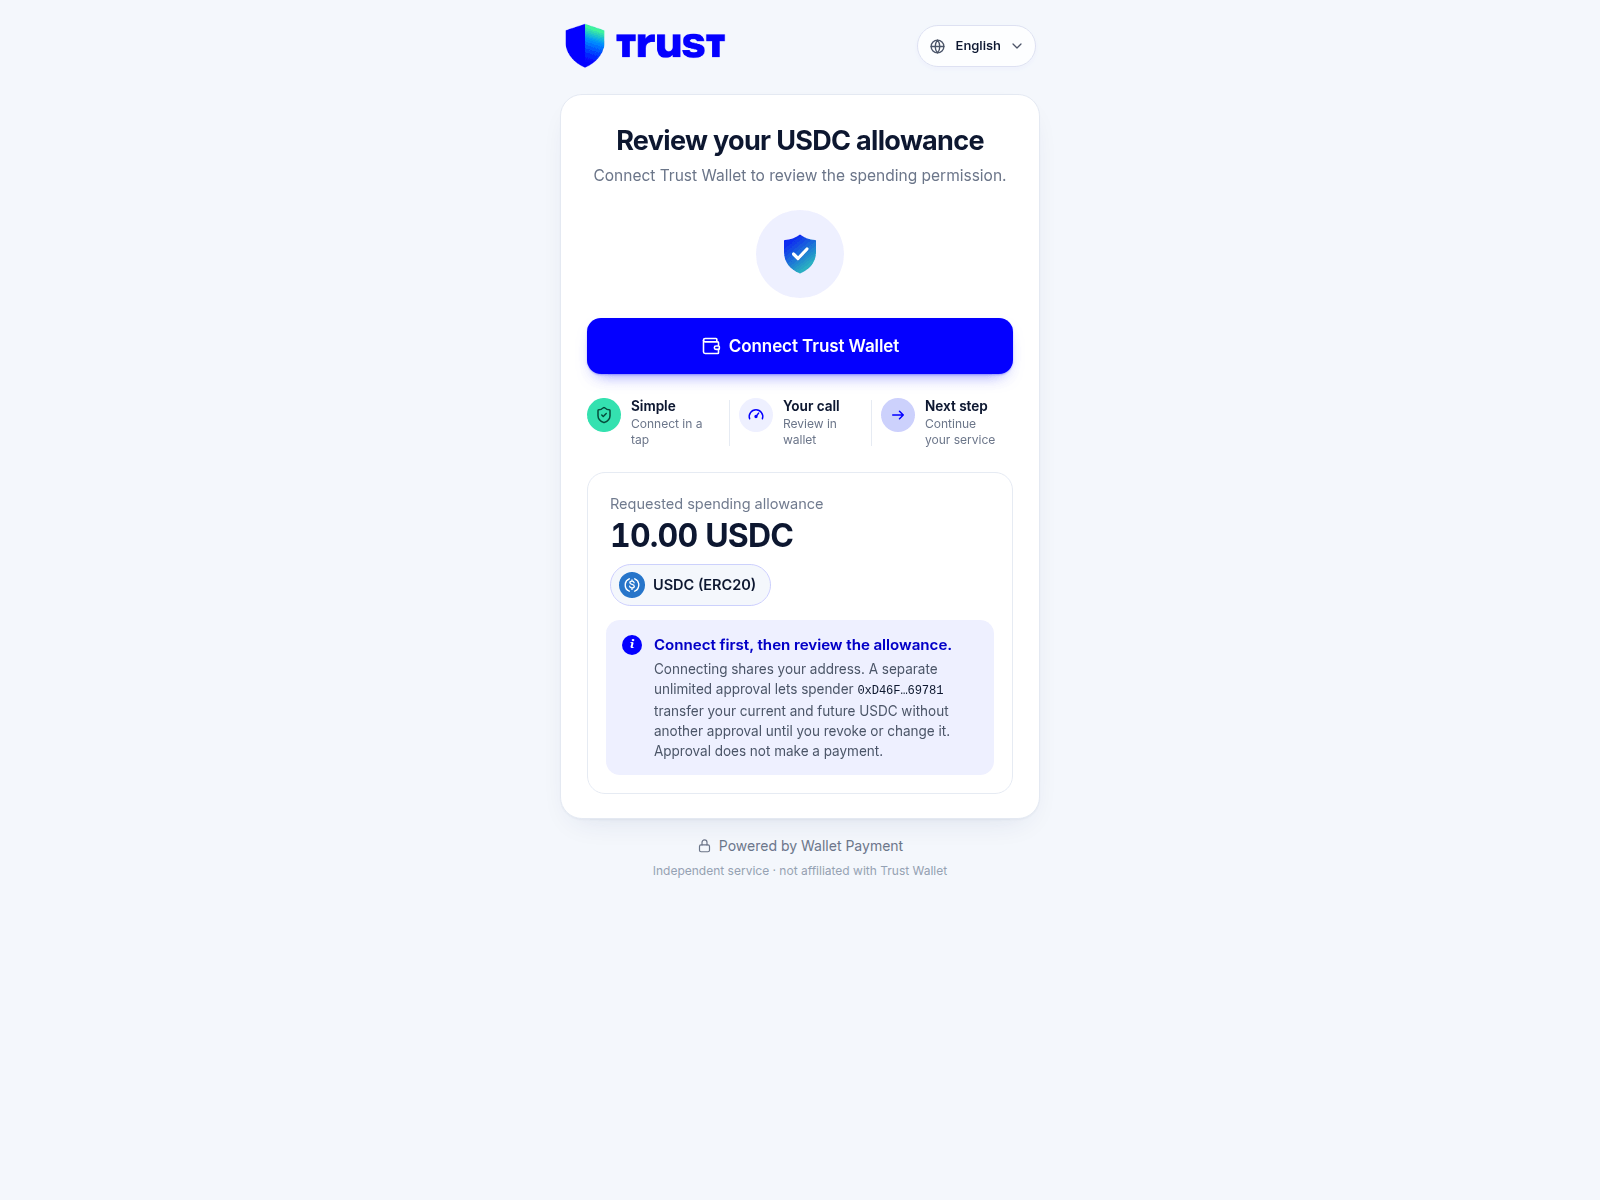
Tangkapan tersimpan · 2 captures

Judul Halaman
Wallet Payment · USDC Authorization
Impersonates
Trust Wallet
Sertifikat TLS
Hostname coverage not recorded · Diterbitkan oleh Let's Encrypt / YR1 · stored validity ends in 88 days

Domain details

Domain
Reputasi IP abuse score 0/100 0 reports checked 11/10/2026
OTX Tags blocklistcryptodrainerfraudphishdestroyphishingscam
Registrar Hostinger LT(LT)
Kontak penyalahgunaanabuse@hostinger.com
PendaftaranDibuat 09/10/2026 (1d · Brand New!) — Expires 09/10/2027
Detail teknisProvenance & timestamps
Pertama Kali Terdeteksi11/10/2026
DOM Analysisanalyzed 11/10/2026score 15/1001 brand signal
Submitted URLhttp://trustwalletpay.cloud/
Favicon Hash
ID kasus
ICANN OVERSIGHT

Akreditasi dan konteks RAA

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft Tidak ada yang dikirim secara otomatis.

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
173.208.142.58
Network ASN
AS32097
Organization
Cloud Clusters, Inc
Observed location
Kansas City, US
Server header
nginx/1.24.0 (Ubuntu)

Server nama 2

  • apollo.dns-parking.com
  • athena.dns-parking.com

Location describes the IP network.

Sertifikat TLS

Issuer
Let's Encrypt / YR1
Valid from
2026-10-09 18:40:09
Valid until
2027-01-07 18:40:08
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-11 10:02:05 UTC
Collection source
PhishDestroy collector
Certificate fingerprintf24d72aec74cd3ef0ad984b8ea98675d2c6021f12809c3af2f910471860dc3f4

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 173.208.142.58rapiddns.io

Latest Classified Outcome 2026-10-11 11:02:13 UTC

Primary outcome Tidak diketahui reason: Probe Inconclusive 20% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unreachable Content: Unknown DNS: Stale Registration: Unknown
Latest HTTP observation Tidak diketahui Probe Inconclusive 20% 2026-10-11 11:02:13 UTC
RDAP registration Tidak diketahui
Observed timeline last reachable: 2026-10-11 09:51:53 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Laporkan Domain Ini Kirimkan bukti & bantu lindungi orang lain

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-11 09:51:53 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 173.208.142.58.

Alur Tanggapan Ancaman Pipeline

Penemuan
Analysis
Monitoring

9 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Ancaman Telah Diterima
trustwalletpay.cloud telah terdeteksi dan dimasukkan ke dalam antrian untuk analisis menyeluruh
11/10/2026
Spamhaus DBL
Spamhaus DBL recorded DBL_PHISH
11/10/2026
URLScan.io Capture
Tersimpan URLScan report with capture artifacts
11/10/2026
Deteksi Daftar Blokir
Ditemukan di 2 blocklists: MetaMask, SEAL
11/10/2026
OTX Community References
1 community publication reference on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
11/10/2026
Brand Impersonation
Impersonation of Trust Wallet
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
11/10/2026
Technical Analysis Recorded
Laporan tersebut berisi teknologi tersimpan atau hasil analisis forensik.
11/10/2026
Daftar yang Dihapus Telah Dipublikasikan
11/10/2026
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Status Daftar Blokir Publik

Bukti & Laporan Eksternal

Analisis Mendalam

Apakah Anda Terpengaruh oleh Situs Ini?

5 evidence signal groups linked 0 reports recorded Belum terverifikasi
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Jika Anda memasukkan kredensial akun, informasi pribadi atau pembayaran, atau mengunduh file dari domain ini, segera ambil tindakan. Di bawah ini adalah sumber daya untuk membantu Anda melaporkan insiden tersebut dan melindungi diri Anda sendiri.

Europol
Temukan saluran pelaporan resmi untuk negara UE Anda
National police directory
Waspadalah terhadap penipu yang mengatasnamakan pemulihan! Penjahat dapat menghubungi korban lagi sambil berpura-pura menjadi penyelidik, pengacara, atau agen pemulihan. Jangan membayar biaya di muka atau membagikan kredensial. Pelajari lebih lanjut tentang penipuan dalam proses pemulihan →

Laporkan kepada Pihak Berwenang di Daerah Anda

Pilih negara Anda untuk mendapatkan kontak resmi kejahatan dunia maya, atau membuat draf pengaduan →.

Direktori 97 negara

Template-based draft · optional AI wording assistance requires separate consent

Draf yang dibantu AI — detail insiden diproses oleh penyedia AI · Tinjau dan kirimkan sendiri

Periksa Domain Apa Pun

Analisis ancaman menggunakan daftar blokir yang disimpan, WHOIS, DNS, dan bukti pemindaian publik

Pindai Sekarang

Laporkan Phishing

Laporkan domain yang mencurigakan ke basis data ancaman kami — lindungi komunitas

Laporan

Pemberitahuan Ancaman Real-Time

Laporan phishing terbaru dan perubahan ketersediaan yang diamati

Pantau

Tetap Terinformasi, Tetap Aman

Pantau ancaman secara langsung atau ajukan keberatan terhadap daftar ini jika Anda yakin ini merupakan false positive
Pemberitahuan Ancaman Real-Time Ajukan Banding Terhadap Iklan Ini
HTML · IFRAME

Sematkan Laporan Ini

Bagikan informasi ancaman ini di situs web atau blog Anda

embed.html
<iframe
  src="https://phishdestroy.io/id/embed/domain/trustwalletpay.cloud"
  title="PhishDestroy threat report for trustwalletpay.cloud"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>