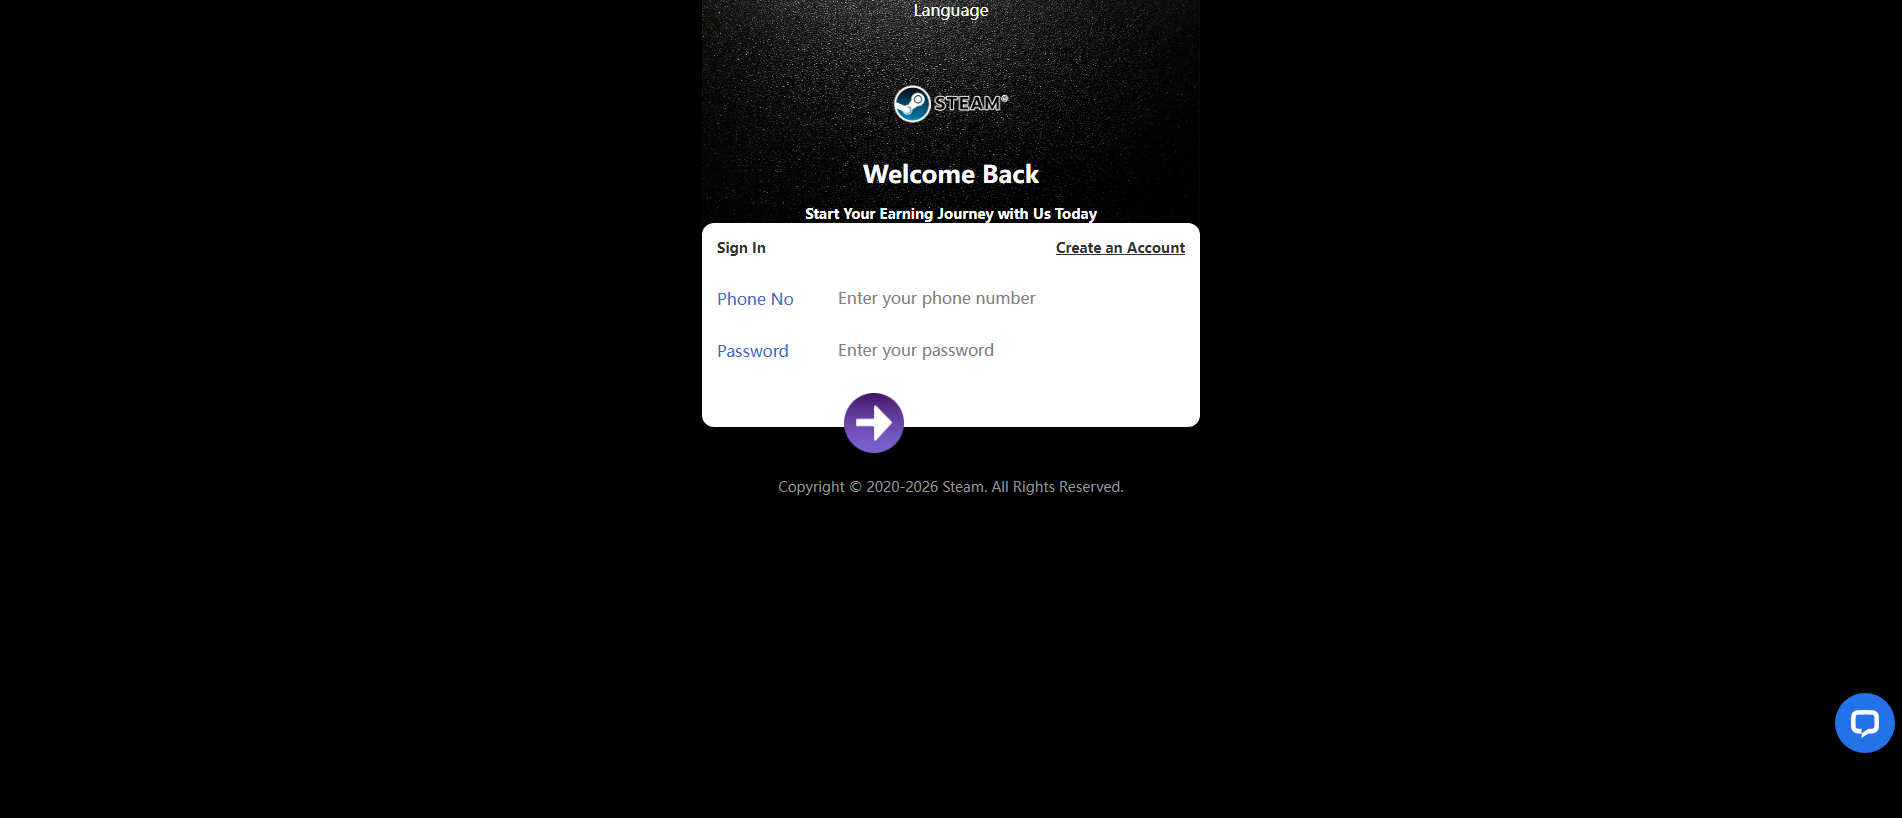
64.118.144.242
VirusTotal

11 / 92 deteksi mesin
Analisis:
Buka laporan VirusTotalCatatan asli sumberTeramati: 9 kolom
Teramati: · Diambil:
Jumlah hasil vendor
- Waktu habis
- 0
- Tidak berbahaya
- 46
- Berbahaya
- 11
- Mencurigakan
- 0
- Tidak terdeteksi
- 35
Label pemasok
- VIPRE
- phishing
- G-Data
- phishing
- Lionic
- phishing
- Sophos
- phishing
- Fortinet
- phishing
- Seclookup
- malicious
- BitDefender
- phishing
- Chong Lua Dao
- malicious
- alphaMountain.ai
- phishing
- Google Safe Browsing
- phishing
- Forcepoint ThreatSeeker
- phishing
Skor reputasi
0Kategori
- Sophos
- phishing and fraud
- alphaMountain.ai
- Phishing (alphaMountain.ai)
- Forcepoint ThreatSeeker
- phishing and other frauds
Pertama terlihat
Catatan DNS
- TTL, detik
- 21600
- Jenis
- NS
- Nilai
- b.share-dns.net
- TTL, detik
- 21600
- Jenis
- NS
- Nilai
- a.share-dns.com
- TTL, detik
- 600
- Jenis
- SOA
- Alamat penanggung jawab
- master.share-dns.com
- Nilai
- a.share-dns.com
- TTL, detik
- 600
- Jenis
- A
- Nilai
- 64.118.144.242
Waktu pengambilan catatan DNS
Sidik jari JARM
27d40d40d00040d00042d43d000000d2e61cae37a985f75ecafb81b33ca523Sertifikat
- Nama alternatif subjek (SAN)
- getstemgames.shop
- www.getstemgames.shop
- Penerbit
- Let's Encrypt / YE2
- Nomor seri
- 57f8c667b57ca7e24f2e4f2156e6d4043a4
- SHA-256
- 575444d983bc4e5a5caf7f394624715533a0b076eb4fa3194c56423431082e34
- Subjek
- getstemgames.shop
- Berlaku hingga
- Berlaku sejak
Kolom asli sumber · JSON
| Jumlah hasil vendor | {
"timeout": 0,
"harmless": 46,
"malicious": 11,
"suspicious": 0,
"undetected": 35
} |
|---|---|
| Label pemasok | {
"VIPRE": "phishing",
"G-Data": "phishing",
"Lionic": "phishing",
"Sophos": "phishing",
"Fortinet": "phishing",
"Seclookup": "malicious",
"BitDefender": "phishing",
"Chong Lua Dao": "malicious",
"alphaMountain.ai": "phishing",
"Google Safe Browsing": "phishing",
"Forcepoint ThreatSeeker": "phishing"
} |
| Reputasi | 0 |
| Kategori | {
"Sophos": "phishing and fraud",
"alphaMountain.ai": "Phishing (alphaMountain.ai)",
"Forcepoint ThreatSeeker": "phishing and other frauds"
} |
| Pertama terlihat | 2026-05-29T10:31:07Z |
| Catatan DNS | [
{
"ttl": 21600,
"type": "NS",
"value": "b.share-dns.net"
},
{
"ttl": 21600,
"type": "NS",
"value": "a.share-dns.com"
},
{
"ttl": 600,
"type": "SOA",
"rname": "master.share-dns.com",
"value": "a.share-dns.com"
},
{
"ttl": 600,
"type": "A",
"value": "64.118.144.242"
}
] |
| Dns at | 2026-06-01T03:54:43Z |
| Jarm | 27d40d40d00040d00042d43d000000d2e61cae37a985f75ecafb81b33ca523 |
| Sertifikat | {
"san": [
"getstemgames.shop",
"www.getstemgames.shop"
],
"issuer": "Let's Encrypt / YE2",
"serial": "57f8c667b57ca7e24f2e4f2156e6d4043a4",
"sha256": "575444d983bc4e5a5caf7f394624715533a0b076eb4fa3194c56423431082e34",
"subject": "getstemgames.shop",
"valid_to": "2026-08-27T09:08:58Z",
"valid_from": "2026-05-29T09:08:59Z"
} |
Separate collector summary
This is a separate stored result. Its counts, vendors and dates do not replace the provider observation above. A retrieval date is not an analysis date.
- source
- VirusTotal
- scope
- unknown
- result_state
- null
- numerator
- 20
- denominator
- 91
- malicious
- null
- suspicious
- null
- vendors
- ["ADMINUSLabs","alphaMountain.ai","BitDefender","CRDF","CyRadar","Ermes","ESET","Emsisoft","Fortinet","G-Data","Google Safebrowsing","Gridinsoft","Kaspersky","LevelBlue","Lionic","Netcraft","Seclookup","SOCRadar","Sophos","VIPRE"]
- observed_at
- null
- checked_at
- 2026-07-02 18:30:18
- fetched_at
- null
- time_basis
- as stored; legacy timezone not established





 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 Kaspersky
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT