FBI IC3
Laporkan kejahatan yang dimungkinkan oleh internet di Amerika Serikat
Federal tips line1-800-CALL-FBI

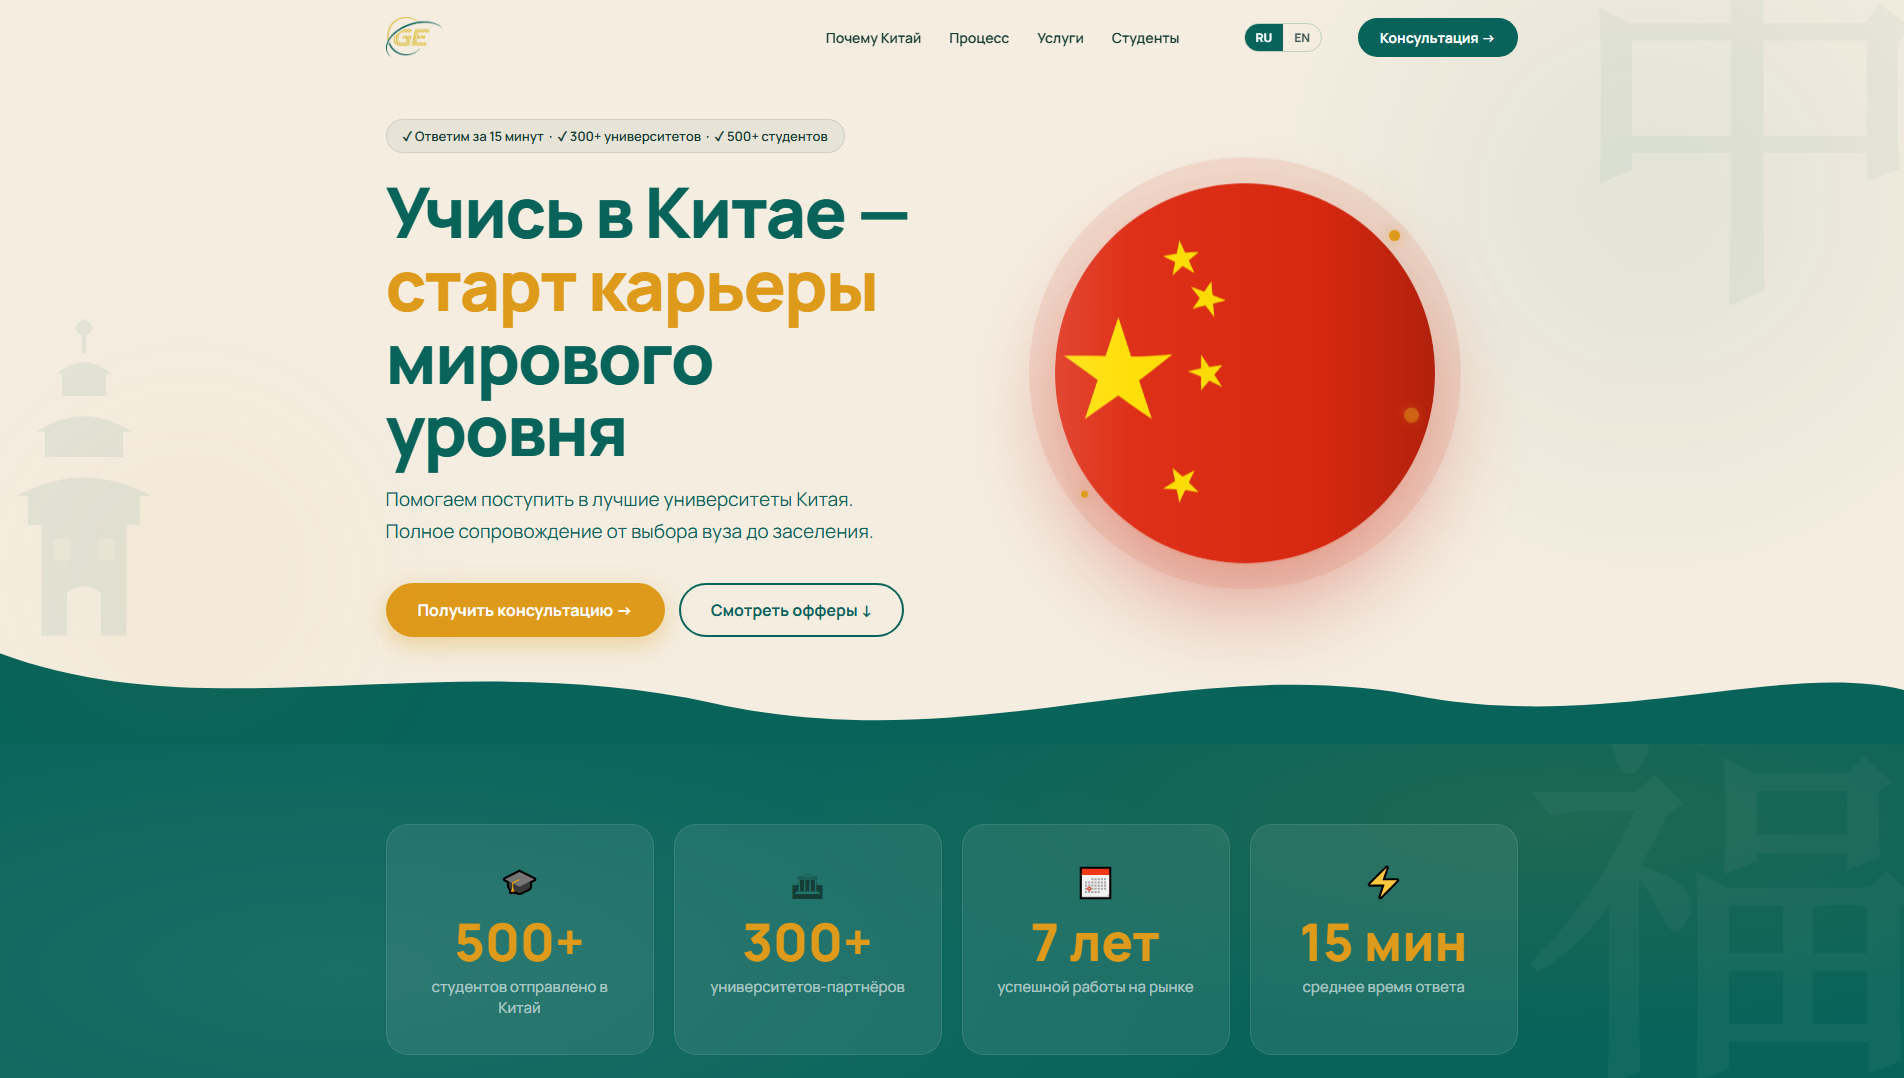
“GE Agency — Обучение в Китае | Поступление в университеты КНР”
The sent-report ledger records the first outgoing report at .
The recorded recipient is tld-abuse@nic.ru.
The latest stored availability evidence still shows the domain reachable; 3 months has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
ge.agency — Terakhir diketahui aktif (HTTP 200). Peniruan identitas merek: Unknown; Jenis penipuan: Generic Phishing. Ringkasan bukti: VirusTotal 5/89 (alphaMountain.ai, Chong Lua Dao, CRDF, Forcepoint ThreatSeeker, Gridinsoft); URLQuery 1 alert; PhishDestroy score 83/100. Registrar: Regional Network Infor….
Analisis terperinci PhishDestroy AI di bawah tetap berbahasa Inggris untuk menjaga catatan forensik asli.
PhishDestroy has identified the domain ge.agency as a generic phishing threat with an elevated risk level. This domain was registered on July 16, 2025, and its exact phishing purpose remains unspecified, but it is likely used for credential theft or malware distribution. No specific brand impersonation or drainer kit has been identified.
Technical analysis reveals that ge.agency resolves to IP address 89.104.79.186 and has been flagged by 2 out of 95 security vendors on VirusTotal. It appears on one security blocklist and is associated with one threat intelligence pulse on AlienVault OTX. The domain was registered through Regional Network Information Center, JSC dba RU-CENTER and uses an SSL certificate issued by ZeroSSL GmbH via ZeroSSL RSA DV SSL CA 2. Google Safe Browsing status is not reported, but the domain's presence on a blocklist indicates some level of malicious activity.
The domain is currently offline, and PhishDestroy recommends that users avoid any interaction if it becomes active again. The remaining risk is low due to its taken-down status, but users should remain vigilant and verify any unexpected links or communications purporting to be from ge.agency. Always confirm the legitimacy of domains through PhishDestroy's verification tools.

| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Hagezi Threat Feed | ge.agency |
malicious | Sinkholed |
Evasion analysis
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
openrestyScanner note: alive_content: raw=ok; http=200; via=https_proxy; server=openresty
 (VN)

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Dilaporkan oleh 1 anggota komunitas; pertama terlihat 15/06/2026
PD-20260617-FC5B75 Recipient: tld-abuse@nic.ru Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Jika Anda memasukkan kredensial akun, informasi pribadi atau pembayaran, atau mengunduh file dari domain ini, segera ambil tindakan. Di bawah ini adalah sumber daya untuk membantu Anda melaporkan insiden tersebut dan melindungi diri Anda sendiri.


Pilih negara Anda untuk mendapatkan kontak resmi kejahatan dunia maya, atau membuat draf pengaduan →.
Infrastructure map · ge.agency
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
These domains also target Tidak diketahui users. View all Unknown threats →
Part of the Tidak diketahui phishing campaign. View all campaign domains →
Laporan baru-baru ini ditambahkan dari database PhishDestroy. Tautan penemuan ini tidak berarti infrastruktur atau kepemilikan bersama.
Analisis ancaman menggunakan daftar blokir yang disimpan, WHOIS, DNS, dan bukti pemindaian publik
Pindai SekarangLaporkan domain yang mencurigakan ke basis data ancaman kami — lindungi komunitas
LaporanLaporan phishing terbaru dan perubahan ketersediaan yang diamati
PantauPantau ancaman secara langsung atau ajukan keberatan terhadap daftar ini jika Anda yakin ini merupakan false positive
 goldtscore.postkiller.com
 epic-checker.online
 ru-pills.com
 hamsterbit.pro
 moneyport.world
 rufus.im
 budowagips.com
 fsv-pl.com
 1kecv.com
 qua.vexotra.com
 efootball.hilesi.org