Lompat ke laporan keamanan
Keamanan domain dan intelijen ancaman
bezopasnet.space favicon

bezopasnet.space

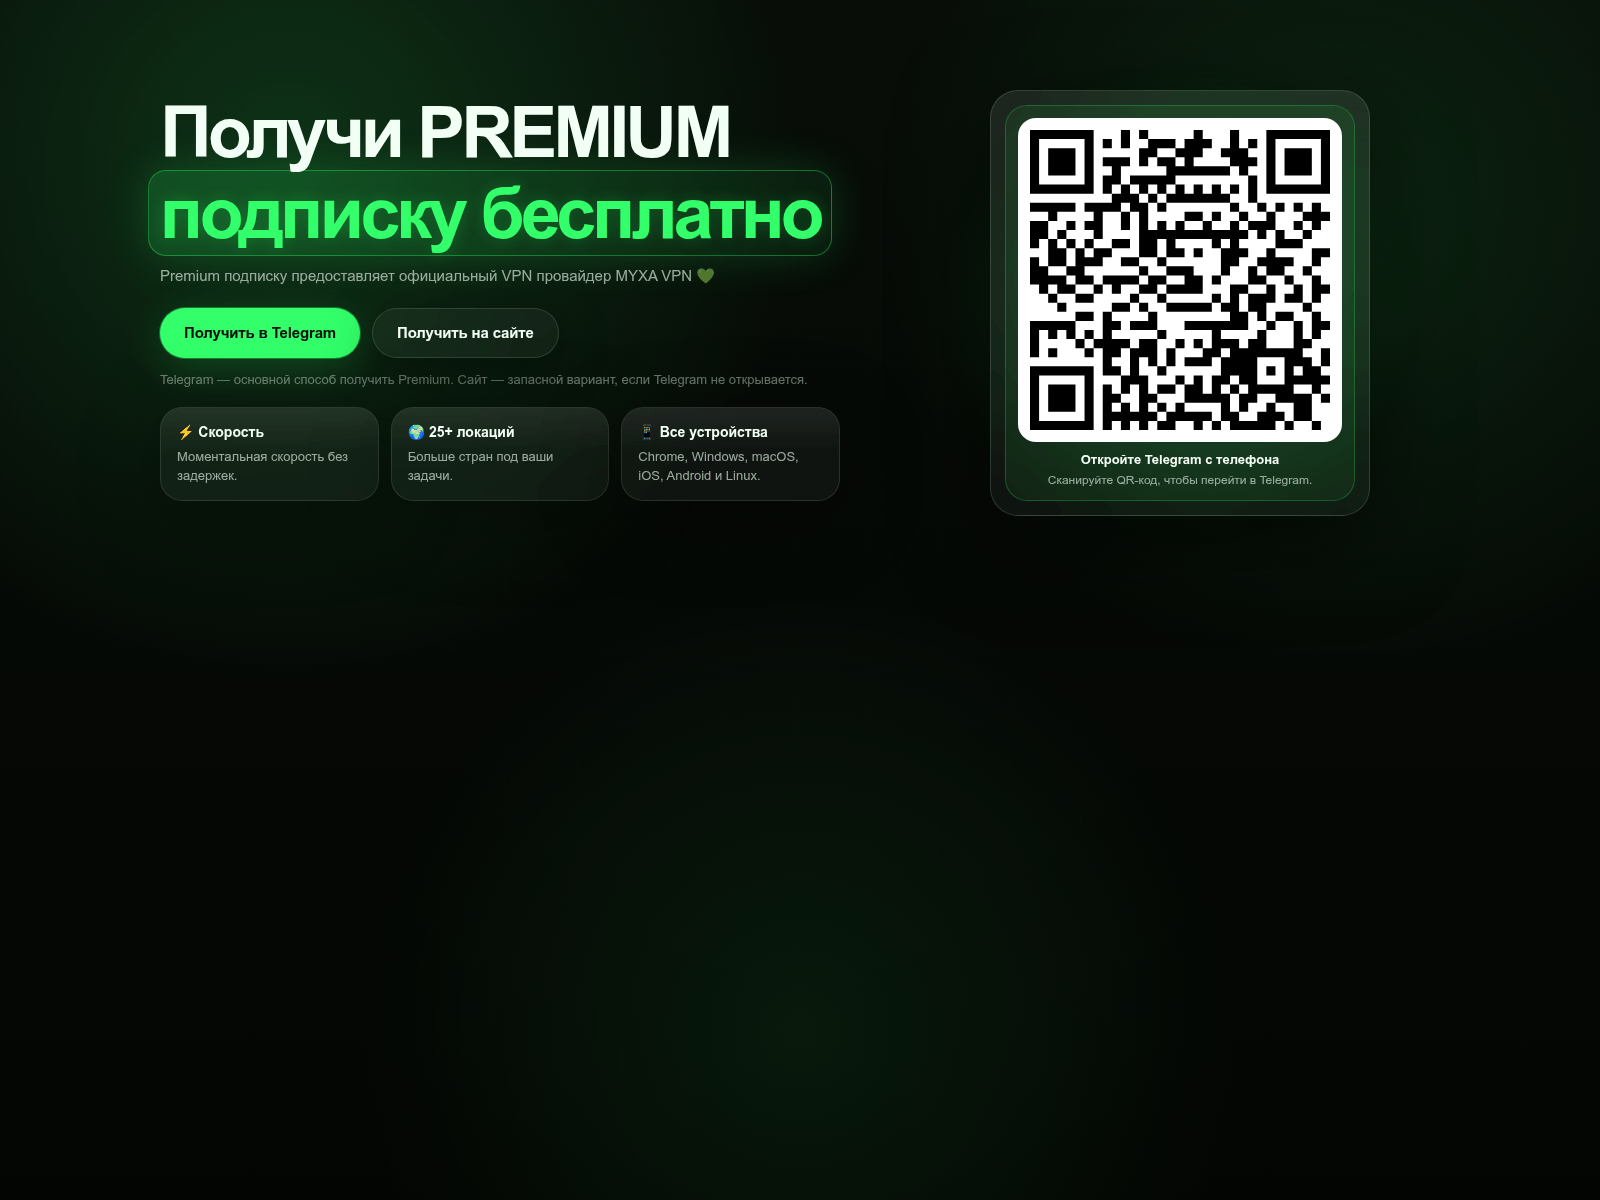
“MYXA VPN — Premium бесплатно”

Registrar
Registrar of Domain Na…
Resolved IP
212.192.14.75
Registered
20/05/2026
Putusan ancaman Kritis
Ketersediaan Terakhir diketahui aktif Pengamatan keterjangkauan tersimpan terbaru Teramati
Source: HTTP probe
Deteksi Total Virus: 18/92 Daftar blokir yang disimpan cocok: 1 Peniruan identitas merek: Telegram
OTX: 9 refs 13/10/2026 Telegram 1 Report Sent
API
Domain ini telah ditandai sebagai berbahaya
Mesin keamanan melaporkan deteksi: 18. Daftar blokir publik yang melaporkan kecocokan: 1. Berhati-hatilah — jangan memasukkan kredensial atau informasi pribadi.
Ringkasan laporan

bezopasnet.space — Terakhir diketahui aktif (HTTP 301). Peniruan identitas merek: Telegram; Jenis penipuan: Impersonation. Ringkasan bukti: VirusTotal 18/92 (alphaMountain.ai, BitDefender, Certego, Chong Lua Dao, CRDF); URLQuery 3 det.; 1 external blocklist match (CryptoFirewall); CF Radar malicious; PhishDestroy score 100/100. Registrar: Registrar of Domain Na….

Analisis terperinci PhishDestroy AI di bawah tetap berbahasa Inggris untuk menjaga catatan forensik asli.

VirusTotal
VirusTotal
18 det.
URLQuery
URLQuery
3 det.
OTX references
CF Radar
Berbahaya
URLScan
URLScan
Sertifikat TLS
Kedaluwarsa atau belum diverifikasi
Usia
5 mo
Status terpantau
Terakhir diketahui aktif 301
PhishDestroy
Daftar Hapus
Terdaftar
Reports Sent
1

Source evidence

7 sources

VirusTotal

18 / 92

Laporan

CF Radar

provider verdict: malicious

Laporan

OTX

9 community references

Laporan

URLScan capture

laporan yang disimpan

Stored URLScan capture preview
Laporan

URLScan verdict

Analisis selesai

Laporan

Google Safe Browsing

Checked; no threat flag recorded

Laporan
Intelijen Keamanan Jaringan
CF Cloudflare Radar Verdict Berbahaya
Malware Malware Security threats

Ringkasan bukti

Kritis
VirusTotal
18/92
OTX
9 community refs
URLScan
Stored capture

Assessment

bezopasnet.space was observed in a CryptoFirewall blocklist entry dated 2026-10-13, which records its inclusion on an external security list. The domain also received a high PageSpeed performance score, providing insight into its technical configuration.

Recorded Evidence

On 2026-10-13, bezopasnet.space was listed in the CryptoFirewall external blocklist. VirusTotal checked the domain on 2026-10-11 and documented 18 detections out of 92 total scanners. OTX pulses were recorded as 9 on 2026-10-13. The domain registration date is 2026-05-20, and it is registered with Registrar of Domain Names REG.RU LLC. The internal PhishDestroy listing was also active as of 2026-10-13.

Interpretation

PhishDestroy contains an internal listing for bezopasnet.space, which documents its presence in a monitored database. VirusTotal records the domain's detection count and scanner coverage, representing a technical assessment of its network presence. The evidence spans several sources and dates, offering a snapshot of external and internal security observations for comparison.

Recommended Actions

For bezopasnet.space, preserve the CryptoFirewall blocklist entry and VirusTotal detection records for ongoing reference. Compare OTX pulse counts and internal PhishDestroy listings to monitor changes in security intelligence. Retain source records to support future technical reviews and maintain a timeline of observed evidence for the domain.

Analisis deteksi dan penghindaran

Diduga terjadi cloaking: judul pada pemindai dan pengunjung berbeda

Belum dipindai Belum ada perbedaan yang tercatat antara crawler dan browser

Data pengamatan perbandingan crawler versus browser yang telah disimpan untuk host ini, ditambah pemeriksaan sidik jari secara real-time untuk sistem distribusi lalu lintas bergaya Keitaro.

Bendera penyamaran yang tersimpan
Belum dipindai
Pemindaian penyamaran terakhir
Header server yang terlihat oleh pemindai
nginx/1.24.0 (Ubuntu)

Catatan pemindai: redirect: raw=redirect_301; http=301; via=https_proxy; location=https://myxavpn.online/; server=nginx/1.24.0 (Ubuntu)

Judul yang ditampilkan pada pemindai keamanan301 Moved Permanently
Judul yang ditampilkan kepada pengunjung browserMYXA VPN — Premium бесплатно
Pemeriksaan sidik jari secara langsung melalui TDS
Tujuh sidik jari Keitaro ditambah perbandingan antara crawler dan browser; jalankan dari pemindai PhishDestroy saat panel ini terbuka.
Menunggu

Tangkapan tersimpan · 2 captures

Judul Halaman
MYXA VPN — Premium бесплатно
Impersonates
Telegram
Sertifikat TLS
Certificate hostname mismatch · Diterbitkan oleh Let's Encrypt / YE2 · stored validity ends in 31 days

Domain details

Domain
URLScan Verdict Analisis selesai score 0 report ↗
Reputasi IP abuse score 0/100 0 reports checked 13/10/2026
OTX Tags 2026-10all-domainsblocklistbrand impersonationbrowser hijackingbrowser traffic redirectionchrome extensionscryptodns-over-https evasiondomaindrainerfilehashmd5filehashsha1filehashsha256+6 more
Registrar Registrar of Domain Na… RU(RU)
Kontak penyalahgunaanabuse@reg.ru, abuse@gir.network
PendaftaranDibuat 20/05/2026 (146d) — Expires 20/05/2027
Status HTTP301 Moved Permanently
Detail teknisProvenance & timestamps
Pertama Kali Terdeteksi13/10/2026
DOM Analysisanalyzed 13/10/2026score 98/1001 brand signal
Submitted URLhttp://bezopasnet.space/
Favicon Hash
ID kasus
ICANN OVERSIGHT

Akreditasi dan konteks RAA

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft Tidak ada yang dikirim secara otomatis.

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
212.192.14.75
Network ASN
AS207713
Organization
GLOBAL INTERNET SOLUTIONS LLC
Observed location
Moscow, RU
Server header
nginx/1.24.0 (Ubuntu)

Server nama 2

  • ns1.reg.ru
  • ns2.reg.ru

Location describes the IP network.

Sertifikat TLS

Issuer
Let's Encrypt / YE2
Valid from
2026-08-15 17:59:11
Valid until
2026-11-13 17:59:10
Hostname coverage
Certificate hostname mismatch
Validity
Within stored validity dates
Collection time
2026-10-13 01:02:09 UTC
Collection source
PhishDestroy collector
Certificate fingerprintc68bd69a04a2bfbd8407f16c46d89856b0a0953d9fb667ca1af84ead841a35d1
Certificate names · 1 SANs
  • www.bezopasnet.space

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 212.192.14.75rapiddns.io

Latest Classified Outcome 2026-10-13 10:00:11 UTC

Primary outcome Redirecting reason: HTTP redirect observed 80% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Redirecting Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Redirecting HTTP redirect observed 80% 2026-10-13 10:00:11 UTC
RDAP registration Tidak diketahui
Observed timeline last reachable: 2026-10-13 10:00:11 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Teknologi · 3 identified
Detected via Cloudflare Radar · Wappalyzer engine
Laporkan Domain Ini Kirimkan bukti & bantu lindungi orang lain

Analisis VirusTotal

18 / Vendor keamanan 92 menandai domain ini
View on VT
Last analyzed First positive detection
alphaMountain.ai
BitDefender
Certego
Chong Lua Dao
CRDF
CyRadar
ESTsecurity
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
Lionic
Seclookup
SOCRadar
Sophos
VIPRE
Webroot
Analisis Performa Situs

Google PageSpeed Insights — mobile performance audit of bezopasnet.space · checked Oct 13, 2026

91
Good
Performance
FCP
1.56s
First Contentful Paint
LCP
3.41s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
10ms
Total Blocking Time
SI
1.56s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-13 00:04:50 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 212.192.14.75.

Alur Tanggapan Ancaman Pipeline

Penemuan
Analysis
Notifications
Monitoring

12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Ancaman Telah Diterima
bezopasnet.space telah terdeteksi dan dimasukkan ke dalam antrian untuk analisis menyeluruh
13/10/2026
URLScan.io Capture
Tersimpan URLScan report with capture artifacts
13/10/2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
18/92 recorded on VirusTotal
13/10/2026
Deteksi Daftar Blokir
Ditemukan di 1 blocklist: CryptoFirewall
13/10/2026
OTX Community References
9 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
13/10/2026
CF Radar: Malicious
Cloudflare Radar classified this domain as Malware, malware, Security threats
Brand Impersonation
Impersonation of Telegram
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
13/10/2026
Technical Analysis Recorded
Laporan tersebut berisi teknologi tersimpan atau hasil analisis forensik.
13/10/2026
Sent Report Recorded
Stored outgoing record associated with registrar Registrar of Domain Names REG.RU LLC, 2 abuse contacts
abuse@reg.ruabuse@gir.network
13/10/2026
Daftar yang Dihapus Telah Dipublikasikan
13/10/2026
Monitoring Continues
Domain tetap dapat dijangkau atau aksesnya dibatasi; pemeriksaan di masa depan dapat memperbarui pengamatan ini.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Status Daftar Blokir Publik

Bukti & Laporan Eksternal

Snapshot bukti yang dikirim
Sent: Ledger records: 1 Case ID: PD-20261013-54E31C Recipient: abuse@reg.ru
Page title stored with report: MYXA VPN — Premium бесплатно
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 235.1 KB
PDF notice generated Notice text archived (324 chars)
Abuse notice text as sent to the provider
Registrar: REG.RU (Russia)
Policy Violations: Abuse policy + ICANN contractual obligations; phishing classified as bad-faith use in UDRP; domains may be suspended/removed
Applicable Laws: Criminal Code RF Art.159 (fraud), Art.272 (illegal access), Art.273 (malware creation), Art.274.1 (critical infrastructure interference)
Analisis Mendalam

Apakah Anda Terpengaruh oleh Situs Ini?

6 evidence signal groups linked 1 reports recorded Terakhir diketahui aktif
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Jika Anda memasukkan kredensial akun, informasi pribadi atau pembayaran, atau mengunduh file dari domain ini, segera ambil tindakan. Di bawah ini adalah sumber daya untuk membantu Anda melaporkan insiden tersebut dan melindungi diri Anda sendiri.

Europol
Temukan saluran pelaporan resmi untuk negara UE Anda
National police directory
Waspadalah terhadap penipu yang mengatasnamakan pemulihan! Penjahat dapat menghubungi korban lagi sambil berpura-pura menjadi penyelidik, pengacara, atau agen pemulihan. Jangan membayar biaya di muka atau membagikan kredensial. Pelajari lebih lanjut tentang penipuan dalam proses pemulihan →

Laporkan kepada Pihak Berwenang di Daerah Anda

Pilih negara Anda untuk mendapatkan kontak resmi kejahatan dunia maya, atau membuat draf pengaduan →.

Direktori 97 negara

Template-based draft · optional AI wording assistance requires separate consent

Draf yang dibantu AI — detail insiden diproses oleh penyedia AI · Tinjau dan kirimkan sendiri

Periksa Domain Apa Pun

Analisis ancaman menggunakan daftar blokir yang disimpan, WHOIS, DNS, dan bukti pemindaian publik

Pindai Sekarang

Laporkan Phishing

Laporkan domain yang mencurigakan ke basis data ancaman kami — lindungi komunitas

Laporan

Pemberitahuan Ancaman Real-Time

Laporan phishing terbaru dan perubahan ketersediaan yang diamati

Pantau

Tetap Terinformasi, Tetap Aman

Pantau ancaman secara langsung atau ajukan keberatan terhadap daftar ini jika Anda yakin ini merupakan false positive
Pemberitahuan Ancaman Real-Time Ajukan Banding Terhadap Iklan Ini
HTML · IFRAME

Sematkan Laporan Ini

Bagikan informasi ancaman ini di situs web atau blog Anda

embed.html
<iframe
  src="https://phishdestroy.io/id/embed/domain/bezopasnet.space"
  title="PhishDestroy threat report for bezopasnet.space"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>

