VirusTotal
12 / 91
Laporan


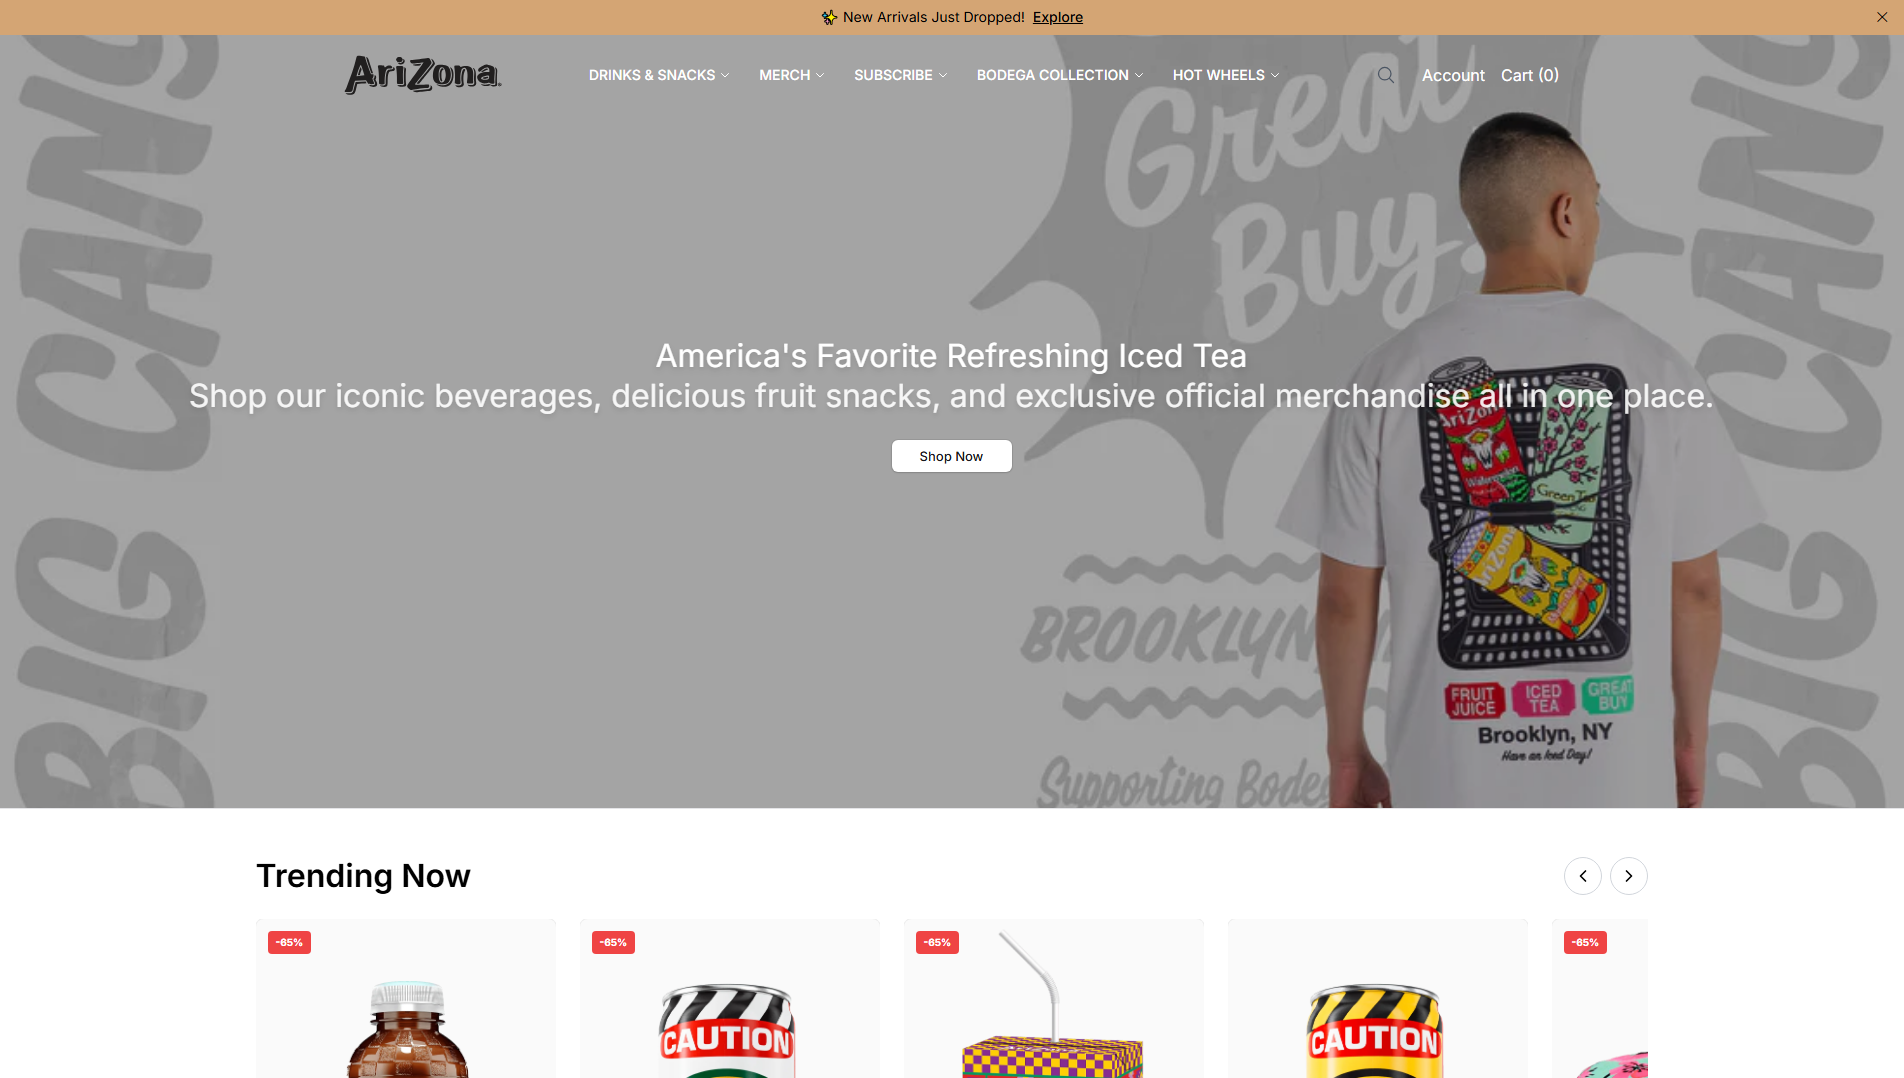
“Home | AriZona Beverages”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@rashost.com.
The latest stored availability evidence still shows the domain reachable; 7 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
arizonafoods.shop — Terakhir diketahui aktif (HTTP 200). Jenis penipuan: Impersonation. Ringkasan bukti: VirusTotal 12/91 (alphaMountain.ai, BitDefender, CRDF, ESET, Fortinet); URLQuery 2 det.; URLScan malicious verdict; Spamhaus DBL_SPAM; PhishDestroy score 100/100. Registrar: Dynadot.
Analisis terperinci PhishDestroy AI di bawah tetap berbahasa Inggris untuk menjaga catatan forensik asli.

12 / 91
2 det.
Laporanmalicious
LaporanDBL_SPAM
4 community references
Laporanlaporan yang disimpan
 Laporan
Report stored; verdict not recorded
LaporanChecked; no threat flag recorded
LaporanArizonafoods.shop was flagged for phishing risks on 2026-10-05, according to PhishDestroy's internal listing. The SSL certificate issued by Let's Encrypt / YE1 was scanned on the same date.
PhishDestroy internally listed arizonafoods.shop on 2026-10-05. The domain was first observed on 2026-10-04. The SSL certificate issued by Let's Encrypt / YE1 was scanned on 2026-10-04. The IP address 23.252.79.139 is associated with the domain, located in the US under AS199242 Malakmadze Web LLC.
The dated records show arizonafoods.shop was catalogued by PhishDestroy and scanned for its SSL certificate on 2026-10-04. These observations provide a snapshot of the domain's status at that time without implying ongoing activity or content.
Retain the PhishDestroy internal listing and the SSL certificate scan record for arizonafoods.shop. Compare these dated records with any future observations to identify changes in status or technical details.
Data pengamatan perbandingan crawler versus browser yang telah disimpan untuk host ini, ditambah pemeriksaan sidik jari secara real-time untuk sistem distribusi lalu lintas bergaya Keitaro.
Catatan pemindai: alive_content: raw=ok; http=200; via=https_proxy
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
brett.ns.cloudflare.compam.ns.cloudflare.comLocation describes the IP network.
4c06ac31c3dba20c53fb02cf5d9dca4849911d69767a7d95259ace1e81936376Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of arizonafoods.shop · checked Oct 5, 2026
23.252.79.139. 11 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20261004-916A6D Recipient: abuse@rashost.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Jika Anda memasukkan kredensial akun, informasi pribadi atau pembayaran, atau mengunduh file dari domain ini, segera ambil tindakan. Di bawah ini adalah sumber daya untuk membantu Anda melaporkan insiden tersebut dan melindungi diri Anda sendiri.


Pilih negara Anda untuk mendapatkan kontak resmi kejahatan dunia maya, atau membuat draf pengaduan →.
Template-based draft · optional AI wording assistance requires separate consent
Setiap jalur merupakan salah satu alasan mengapa sebuah domain terhubung ke host ini. Ukuran node menandai deteksi VirusTotal, sedangkan node bergaris putus-putus menunjukkan bahwa node tersebut sudah offline. Daftar lengkapnya tercantum di bawah ini.
Hash favicon yang sama atau judul halaman yang sama dengan host ini.
IP asal ini menghosting beberapa domain phishing — infrastruktur dapat digunakan bersama di seluruh kampanye.
Didaftarkan melalui penyedia layanan pendaftaran yang sama. Sebuah penyedia layanan pendaftaran melayani jutaan pelanggan yang tidak saling terkait, sehingga hal ini sekadar mengelompokkan laporan-laporan tersebut, bukan membuktikan adanya hubungan.
Laporan baru-baru ini ditambahkan dari database PhishDestroy. Tautan penemuan ini tidak berarti infrastruktur atau kepemilikan bersama.
Analisis ancaman menggunakan daftar blokir yang disimpan, WHOIS, DNS, dan bukti pemindaian publik
Pindai SekarangLaporkan domain yang mencurigakan ke basis data ancaman kami — lindungi komunitas
LaporanLaporan phishing terbaru dan perubahan ketersediaan yang diamati
PantauPantau ancaman secara langsung atau ajukan keberatan terhadap daftar ini jika Anda yakin ini merupakan false positive