
Cari domain yang dipantau dan tinjau bukti yang tersimpan, hasil deteksi, serta ketersediaan terbaru yang teramati.
221,203
Total yang Dilacak
215,390
VT Terdeteksi
85,968
Terakhir Terlihat Aktif
135,235
Tidak tersedia pada pemeriksaan terakhir
0
VT Sedang Diproses
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake Domain
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Phishing Pages
Phishing pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Malicious Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Analysis
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Infrastructure-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Phishing Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Scam (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Requests for private keys or seed phrases
Unexpected transaction requests
Poor website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1
Always verify domain authenticity
2
Enable two-factor authentication
3
Use hardware wallets for transactions
4
Regularly update security software
5
Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 1,678 domains tracked for this threat type
WalletConnect Abuse 1,678 domains


truemoney.finance
v0-walletconnect-v2-integration.vercel.app
voters-manyushib.info

votes-walletconnect.xyz

wallet-procedurasafezone.com

walletconnect-dapp-psi.vercel.app

walletconnect-example-front.vercel.app
walletconnectdev.burnghost.com
wallsec.app

wave-backly.site

wcp-wallet-verification-demo-git-svenvoska-a6979f-walletconnect.vercel.app
web-openbugsresolve.org
web3bay.io

wojakwhales.com
wormholesolana.web.app
zynft.xyz

0-cz.com

0rigindefi.org
2jglw-bqaaa-aaaap-qbl2q-cai.icp0.io

aavebank.net
acrosstozora.com
aetherclaim.xyz
aetherswift.com
agicoin.vip

airdrop.sentlient.xyz

amlchecksecurity.com

amlrated.net

amlrated.top

app-firelight.xyz

approveusdt.app
approveusdt.com

approvewalletcheck.com

aviciwhale.com

bakeryswa-p.web.app
bancusportal.io

beta.rabitiai.net

betonbase365.xyz
bitget.biz
blendprotocol.network
bnb-21.cc
bnb-22.cc

bob-mainnet-m6g11tm5n-distributed-crafts.vercel.app

bob-mainnet-qmtu140y8-distributed-crafts.vercel.app
bonuses-zkpass.com

bscscan.support

catchthepi.com

chainvaultdapp.org

check-usdt.org

check-wallet.org
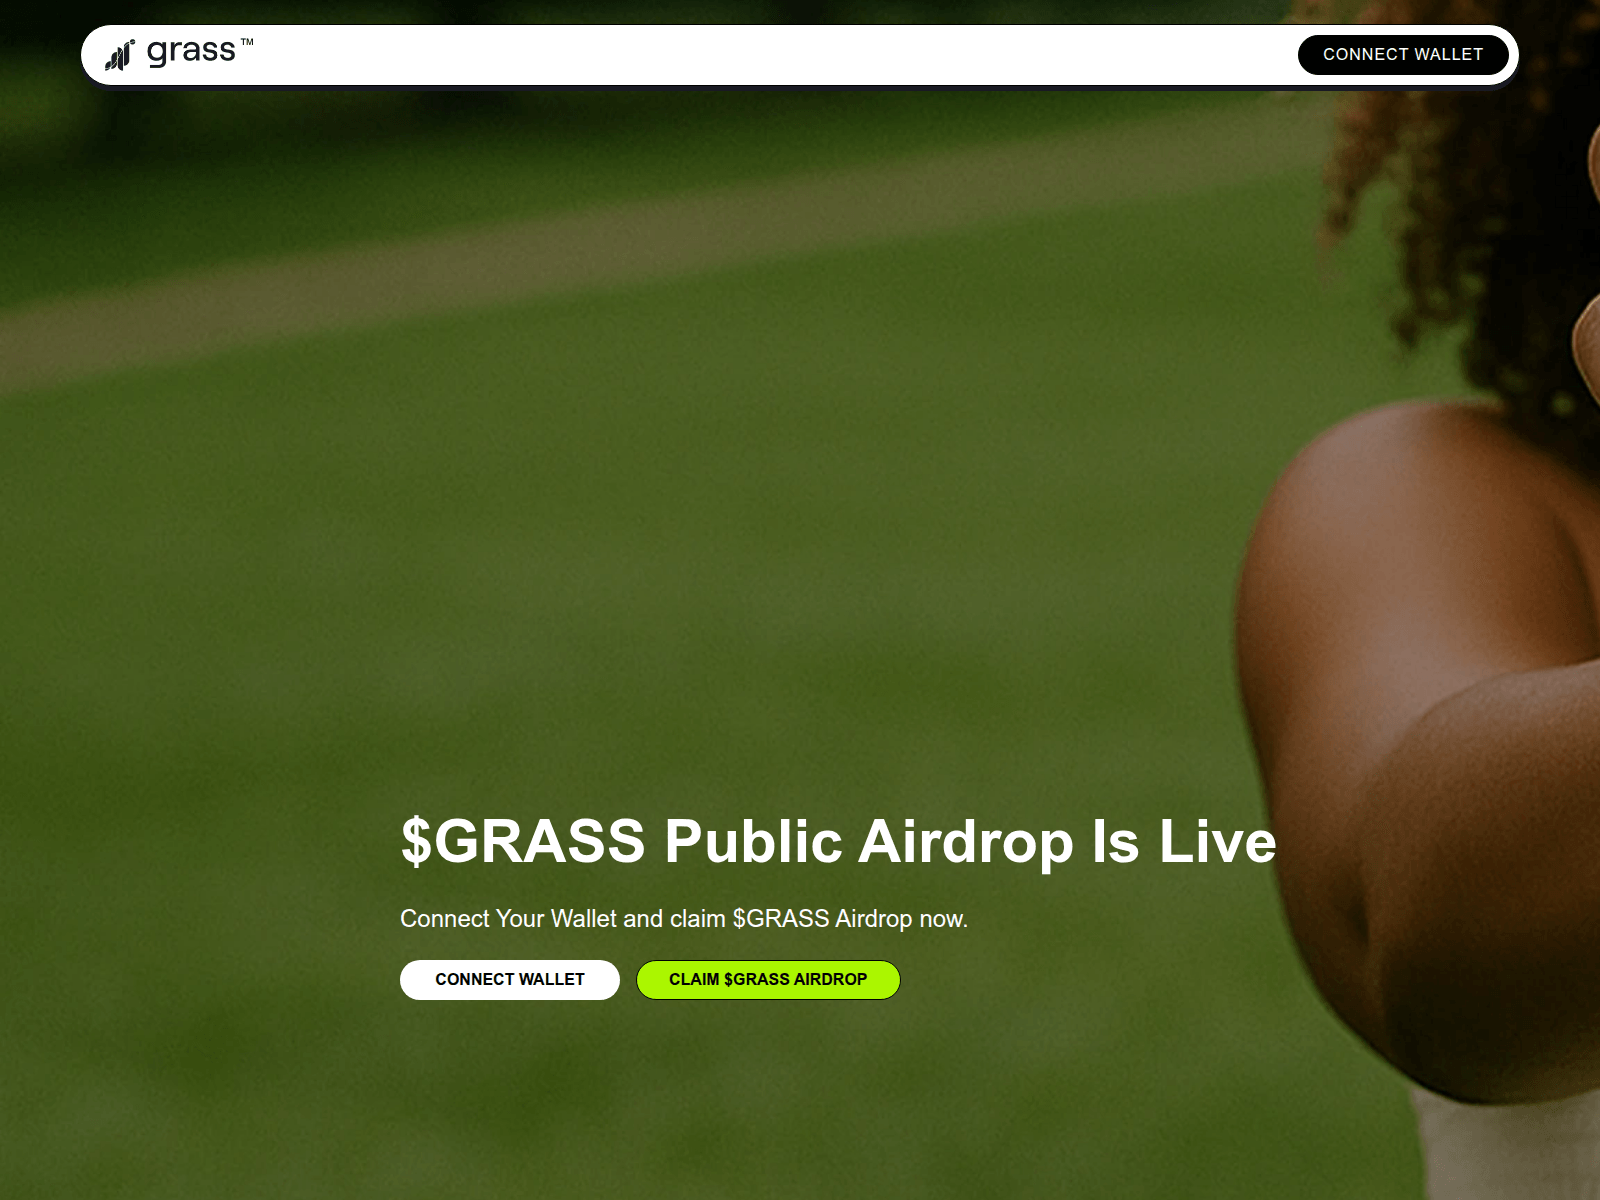
claim-grass.app
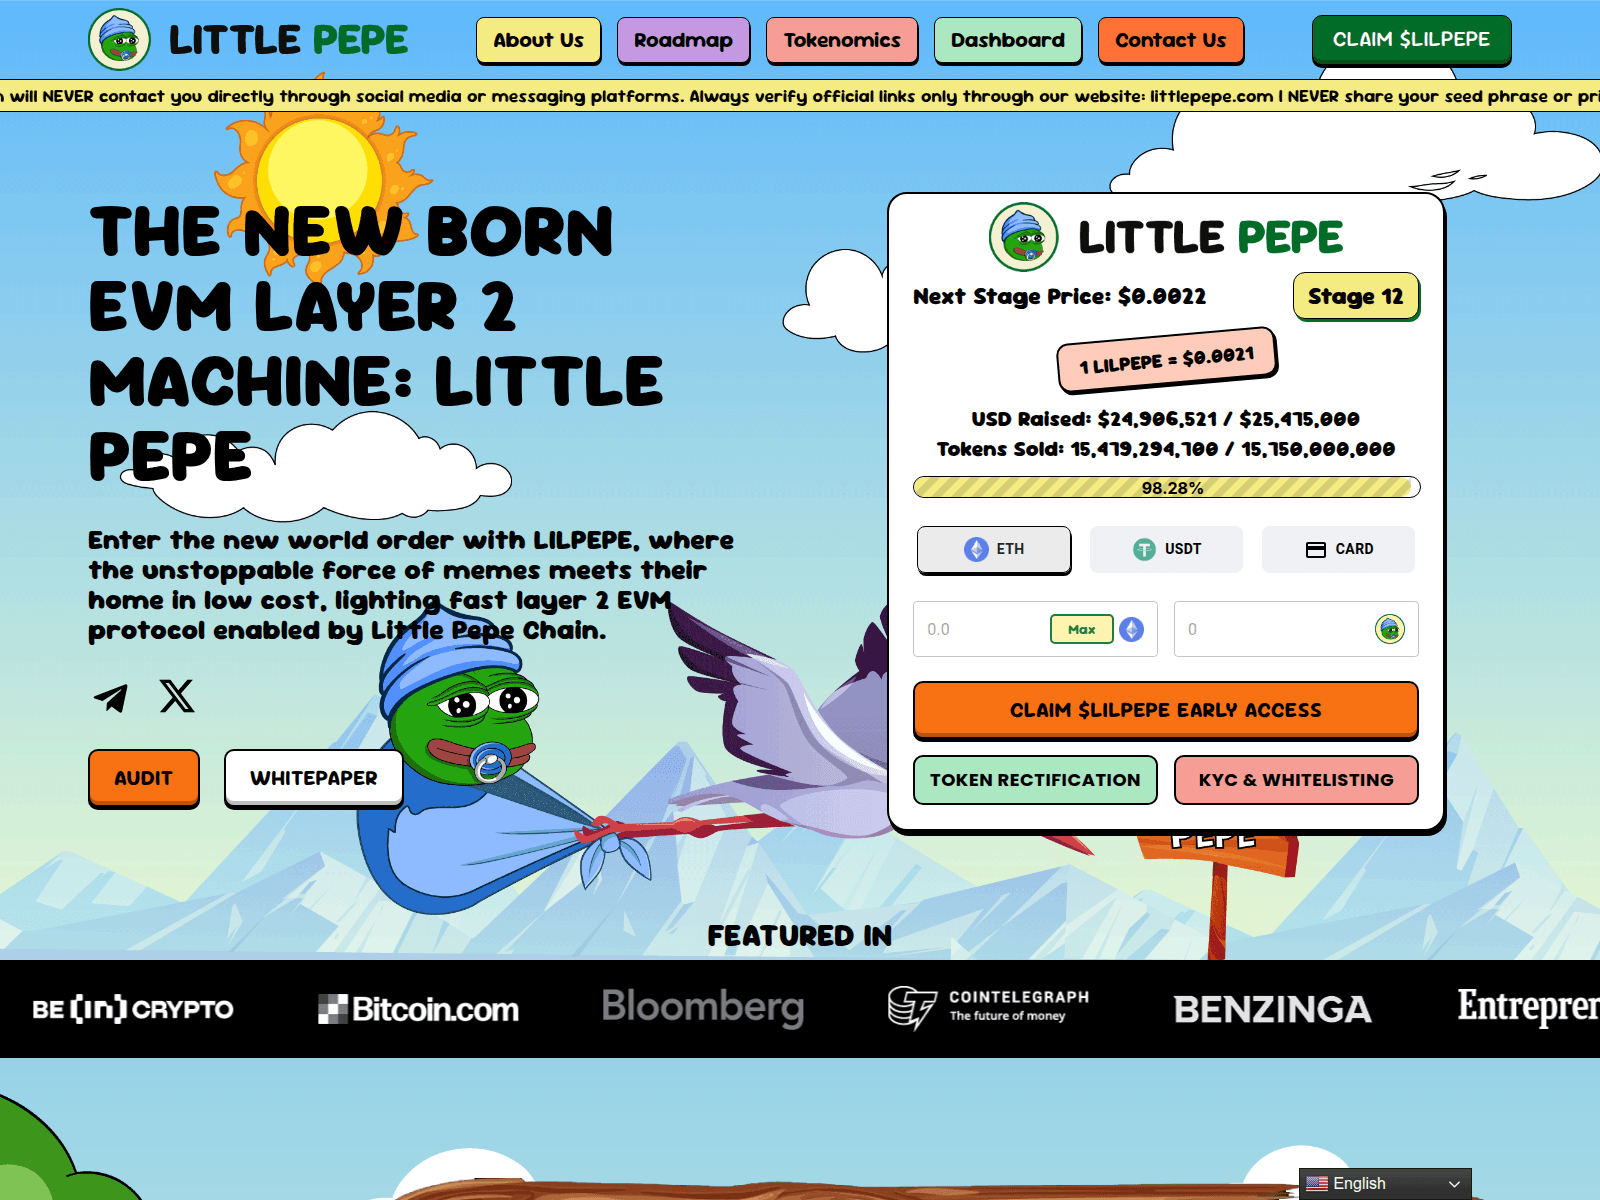
claim.lilpepetoken.dev

claims-talus.org

claimtaiko.loopring.io
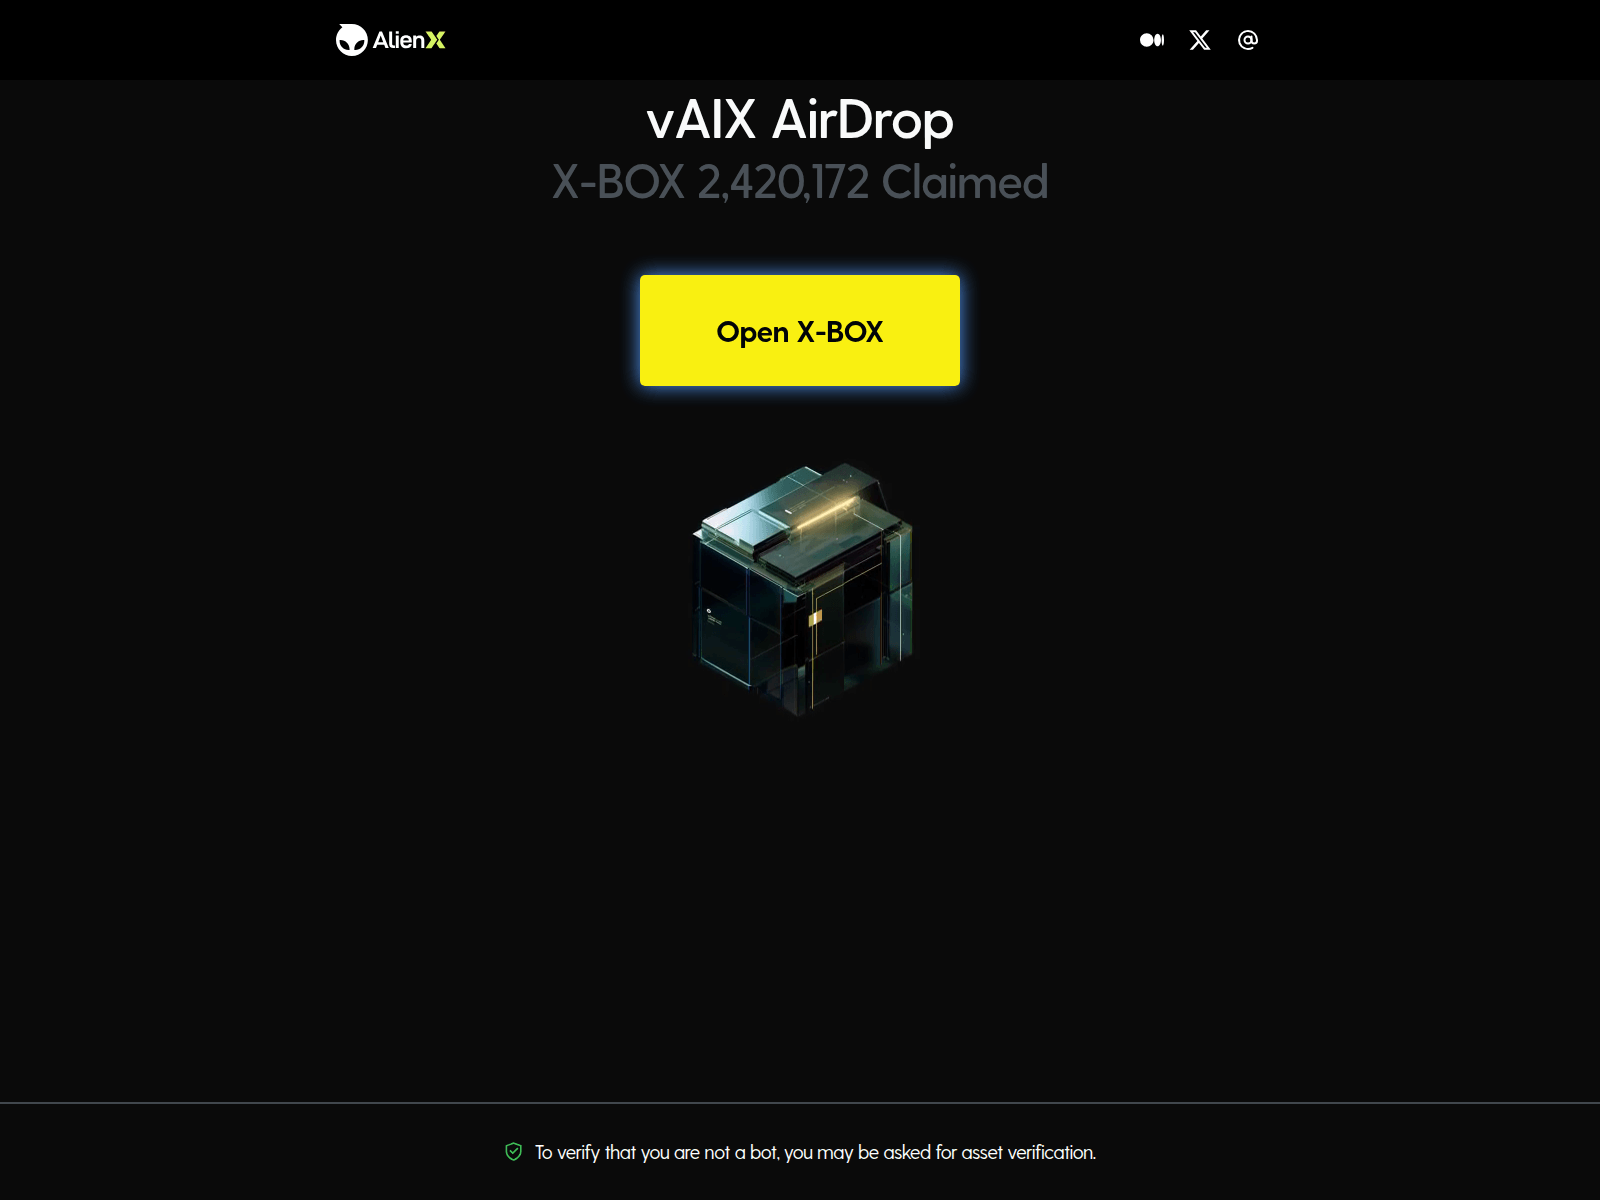
claimxbox.web.app

club-onefootball.site

connection-today.com
cryptoverif.com
dapp-radar.top

deathx.fun

defigap.app
digital-eth.net
eligibility-destranetwork.xyz

era-claim.icu
fqpsfr.cc

grokdextools.site
hoursglass-kyc.com

hyperliqdxyz.com
ib67n-yiaaa-aaaao-qjwca-cai.icp0.io
ifp-airdrop.com
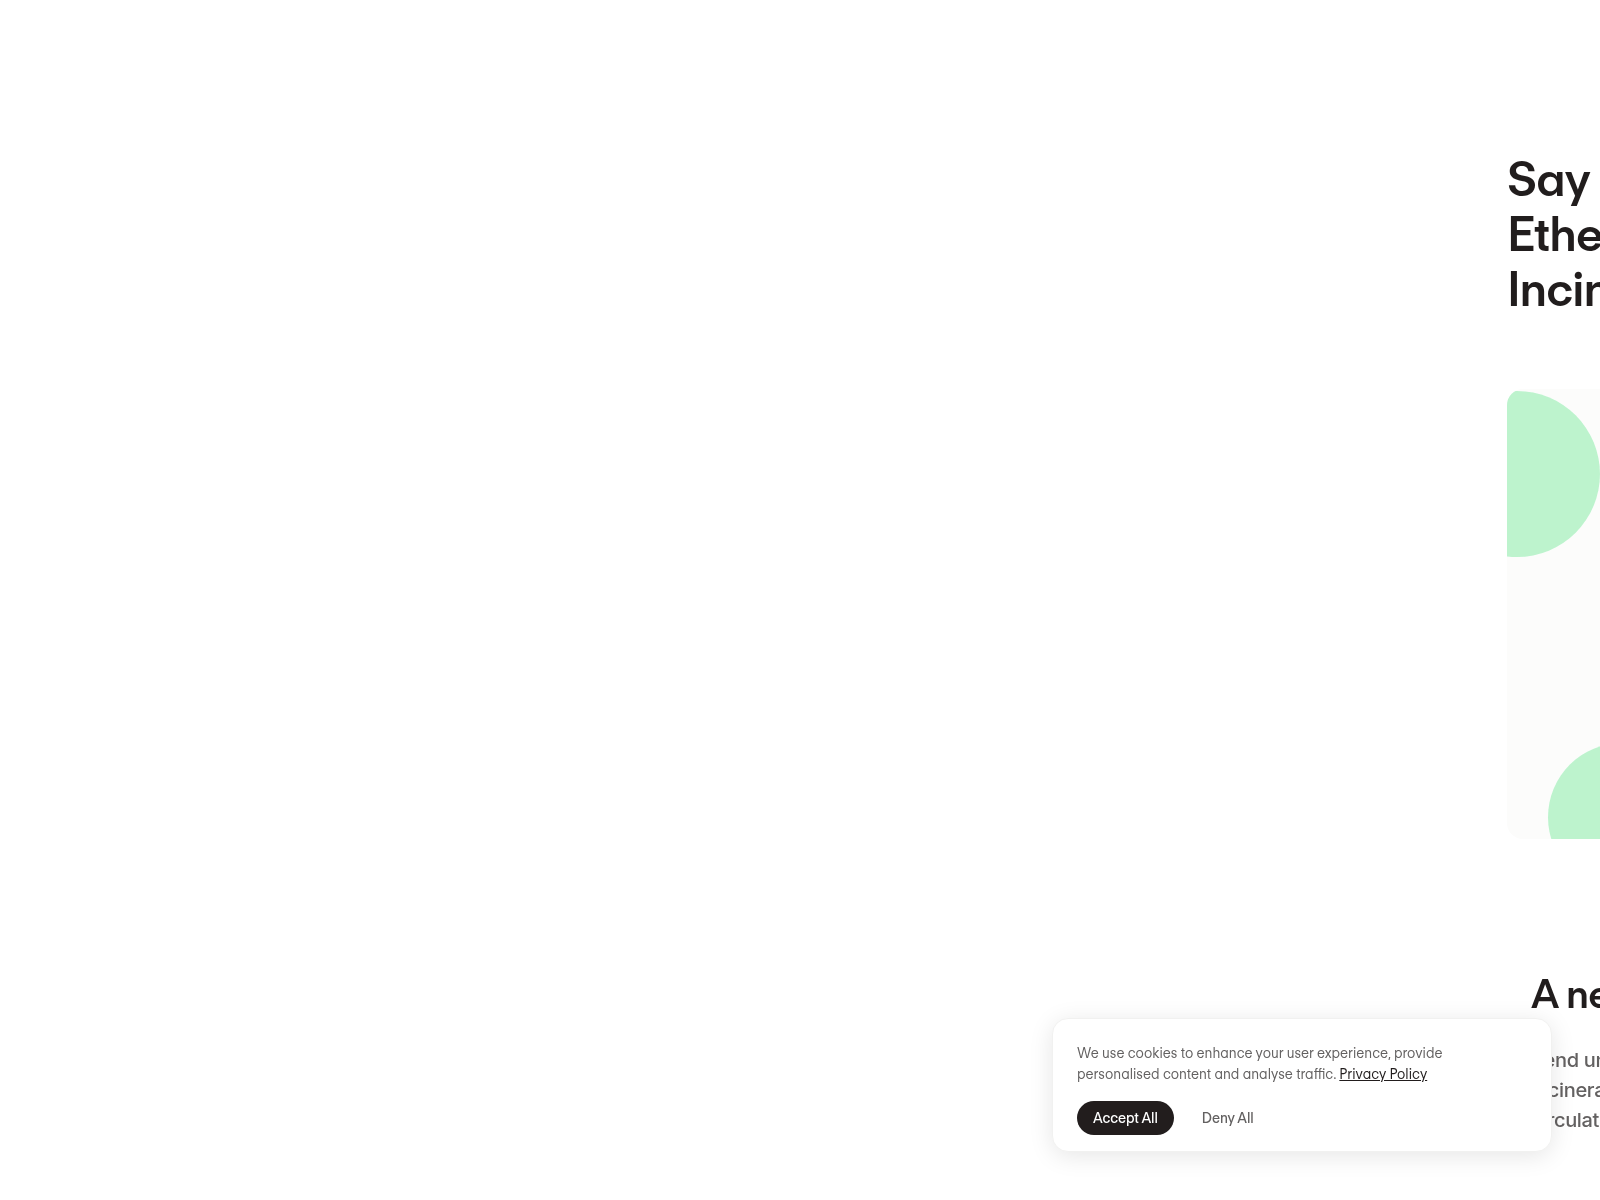
incinerate-ethereum.com
jameswynnr-allocations.xyz
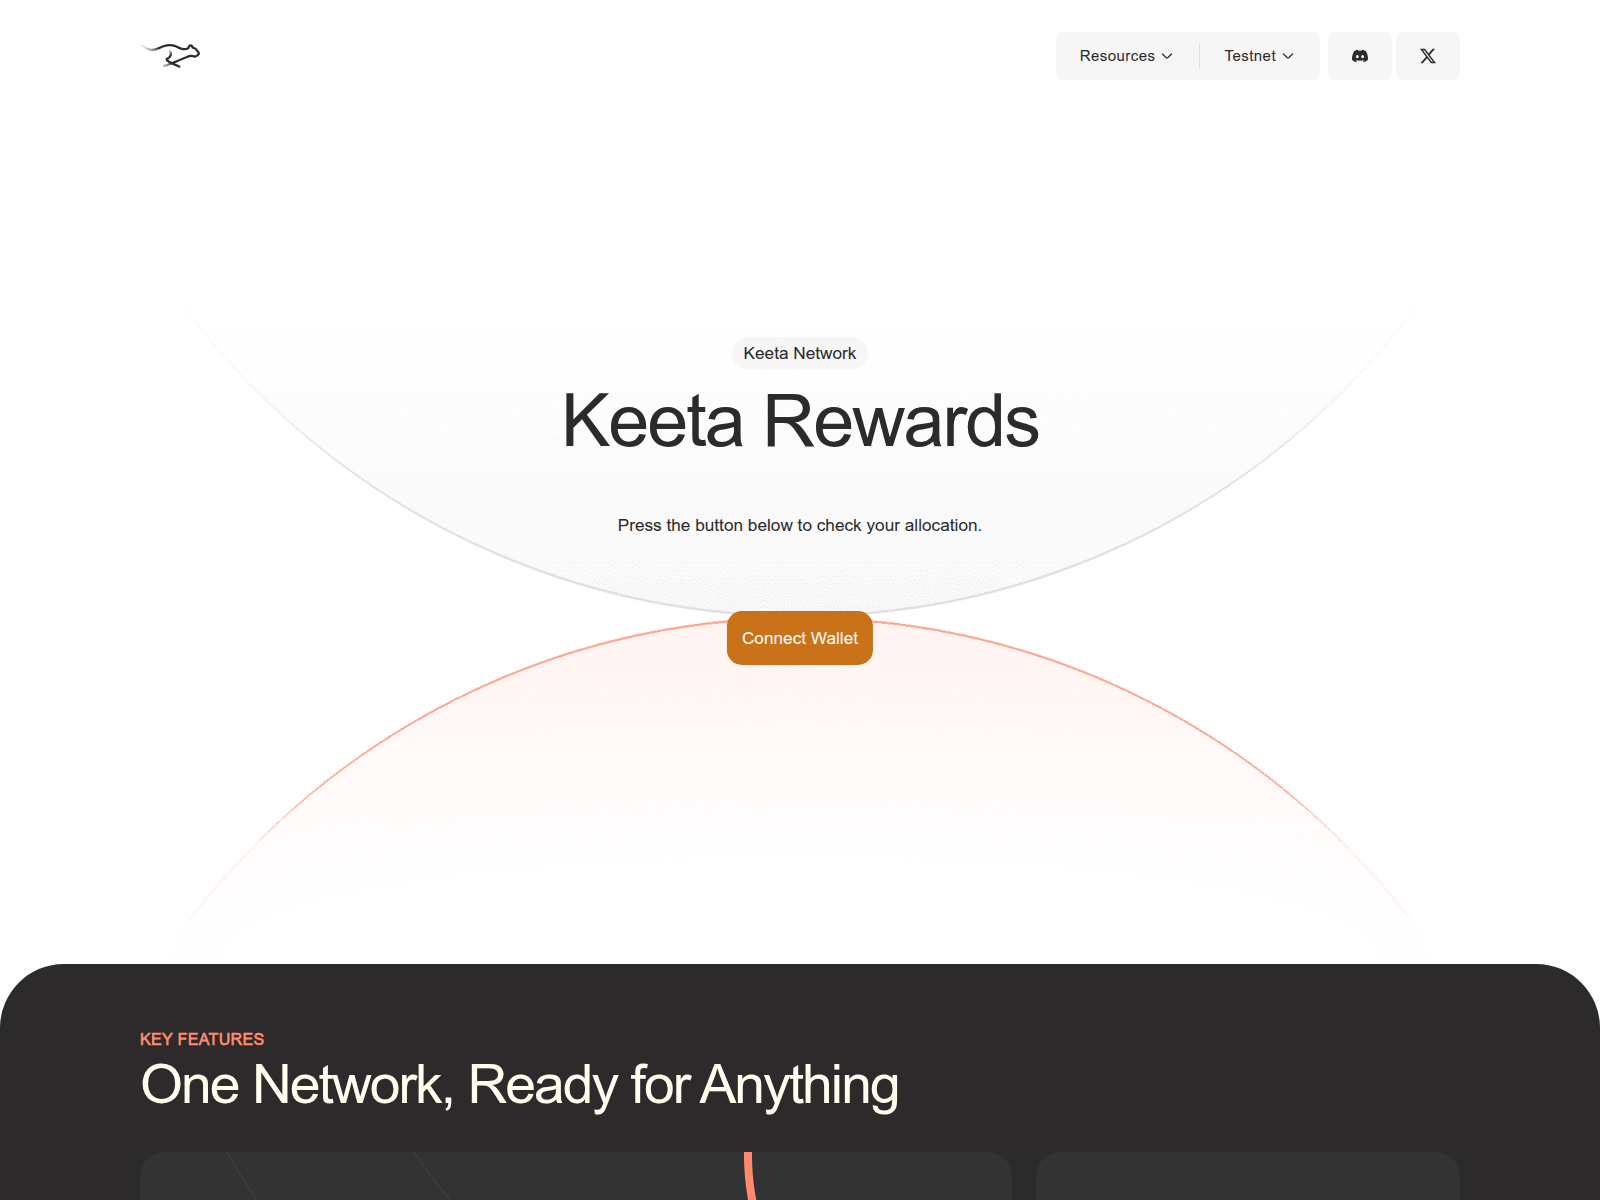
ketasclaimnow.xyz

kinetiql.xyz

kittenswap-finance.net

koinly.tax

layerswap-exchange.com

legendary-drops.app

limitless-exchange.website
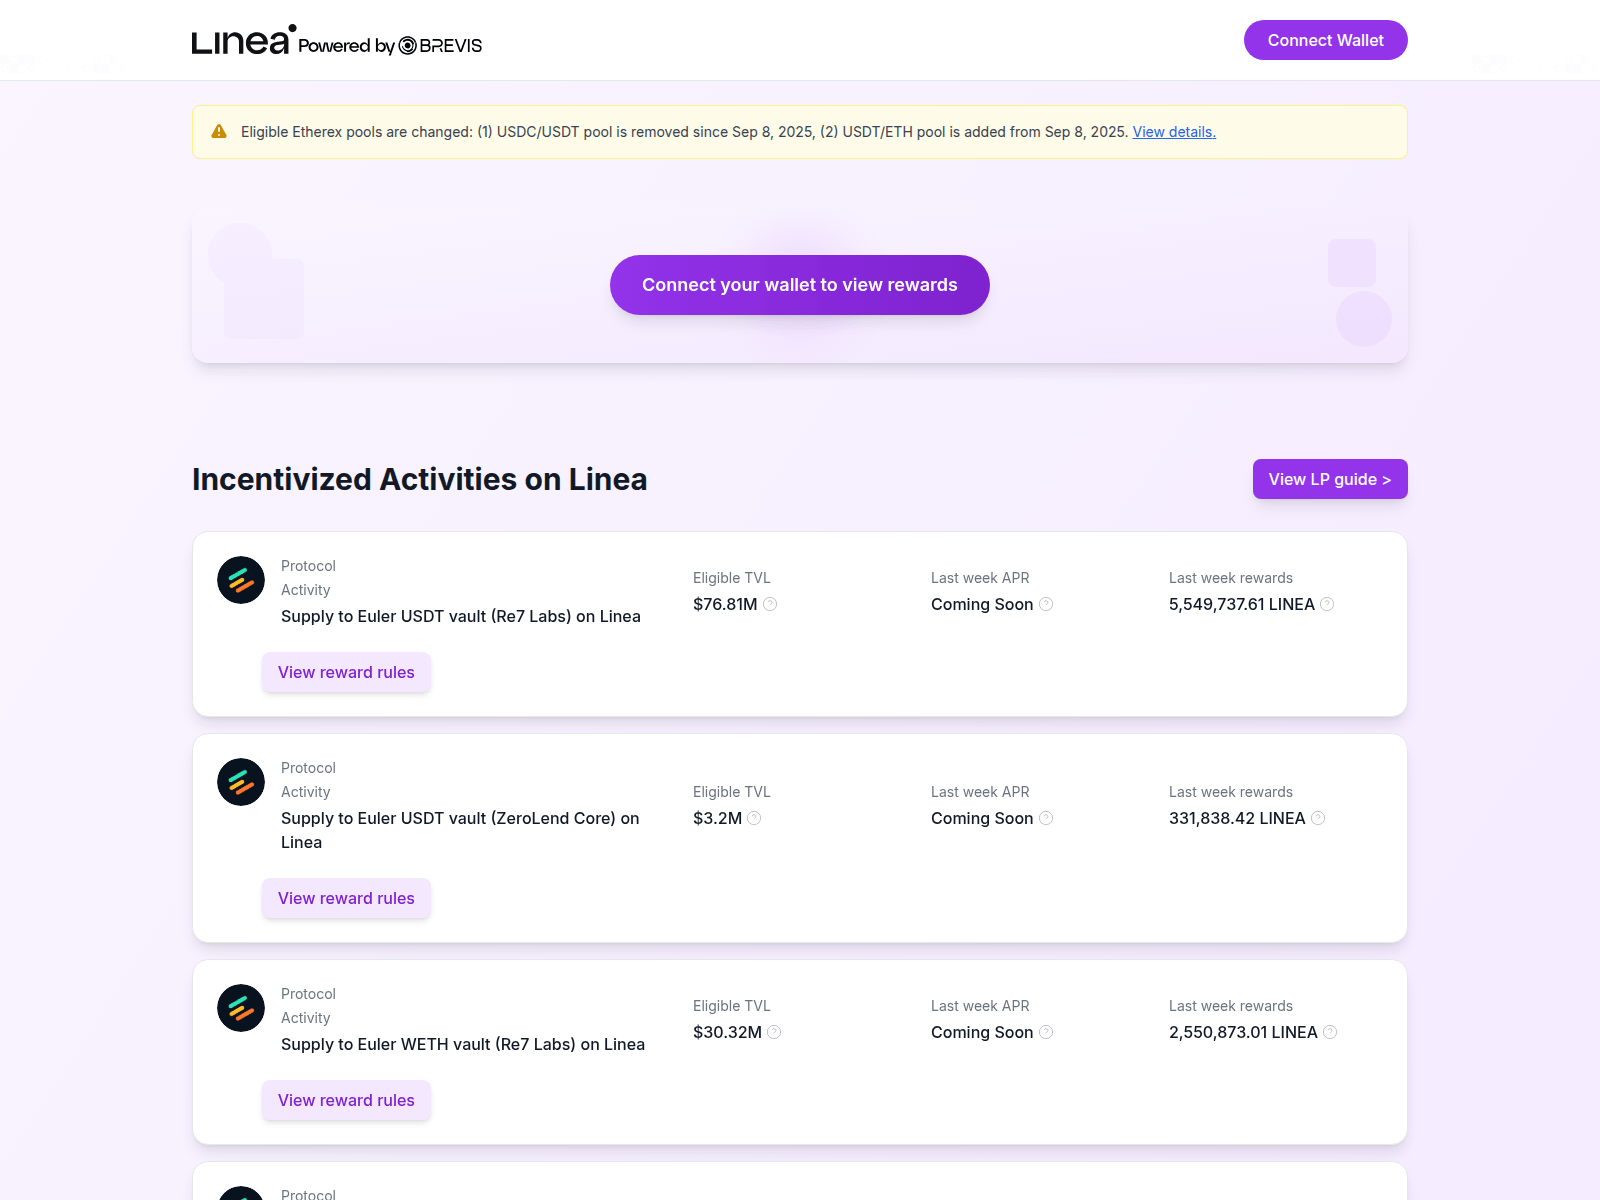
linea-claim.xyz

lineaslive.com

loopingcollective.xyz
lpbonds.com
lulofi.app
mascor.info

meta-rwrd.top
mh.hb027.net
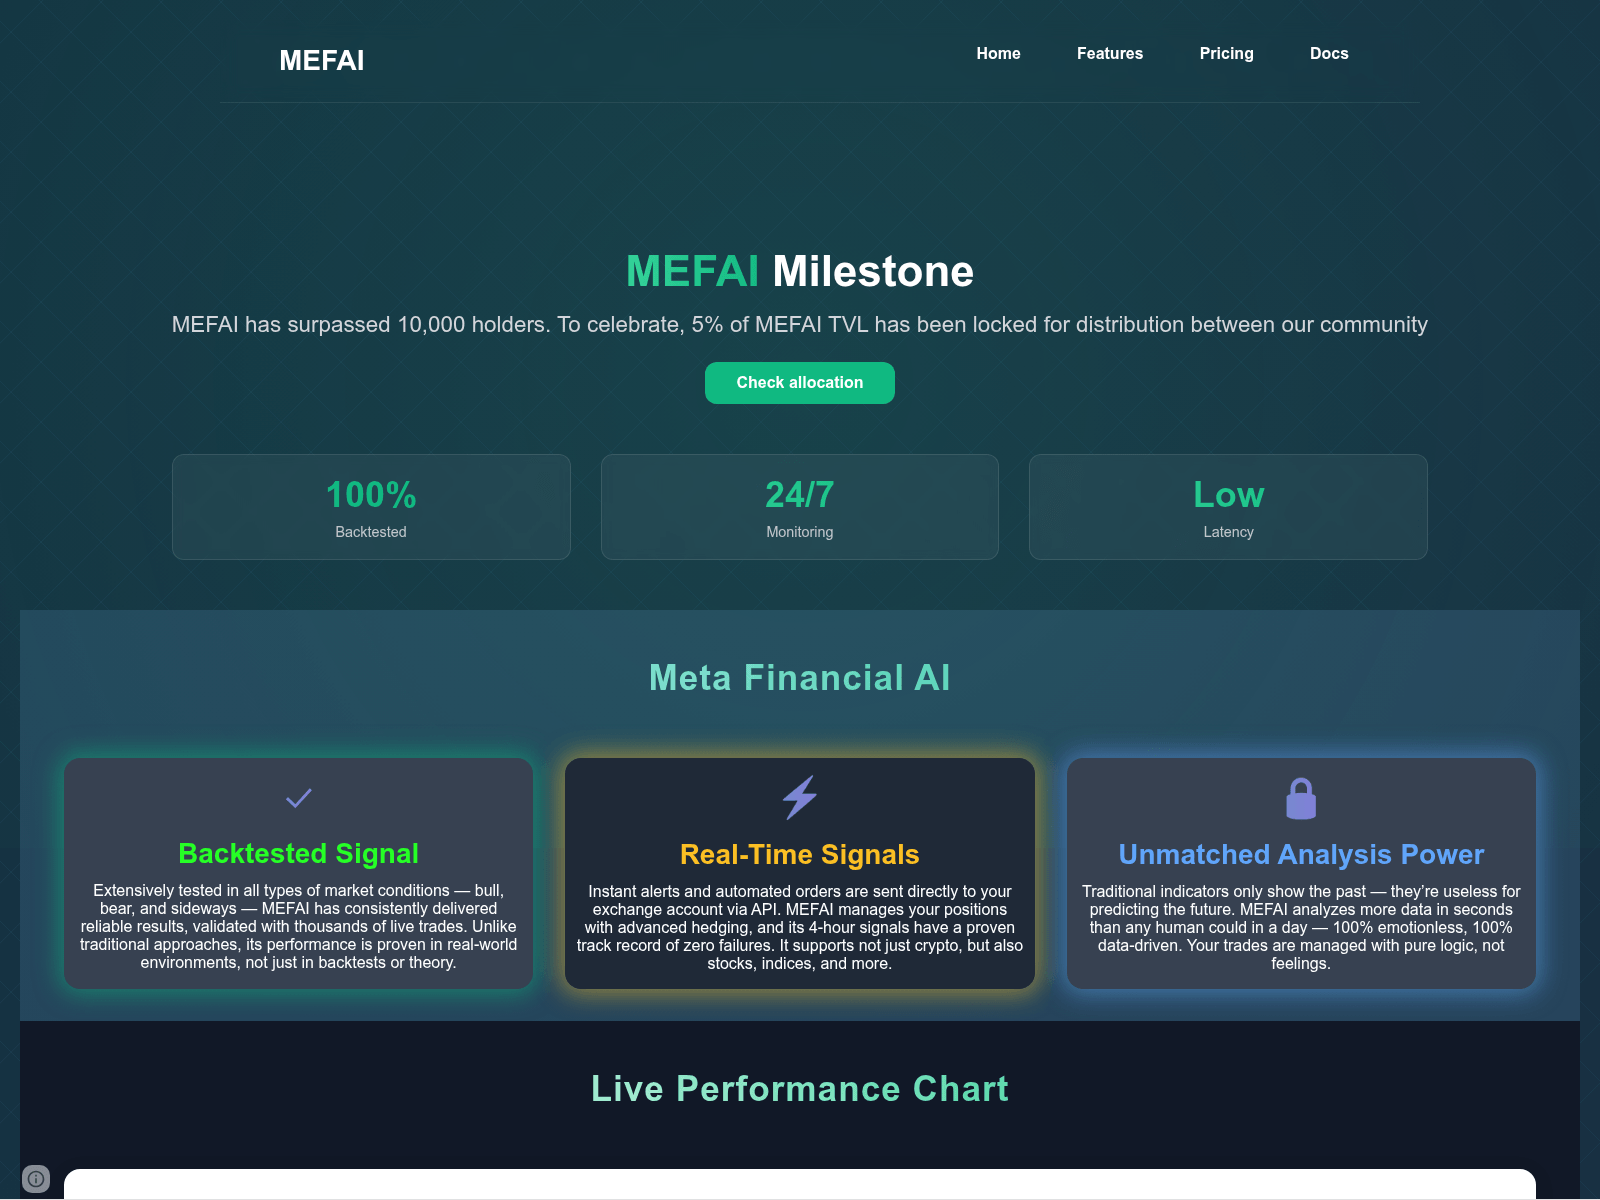
milestone-mefai.com
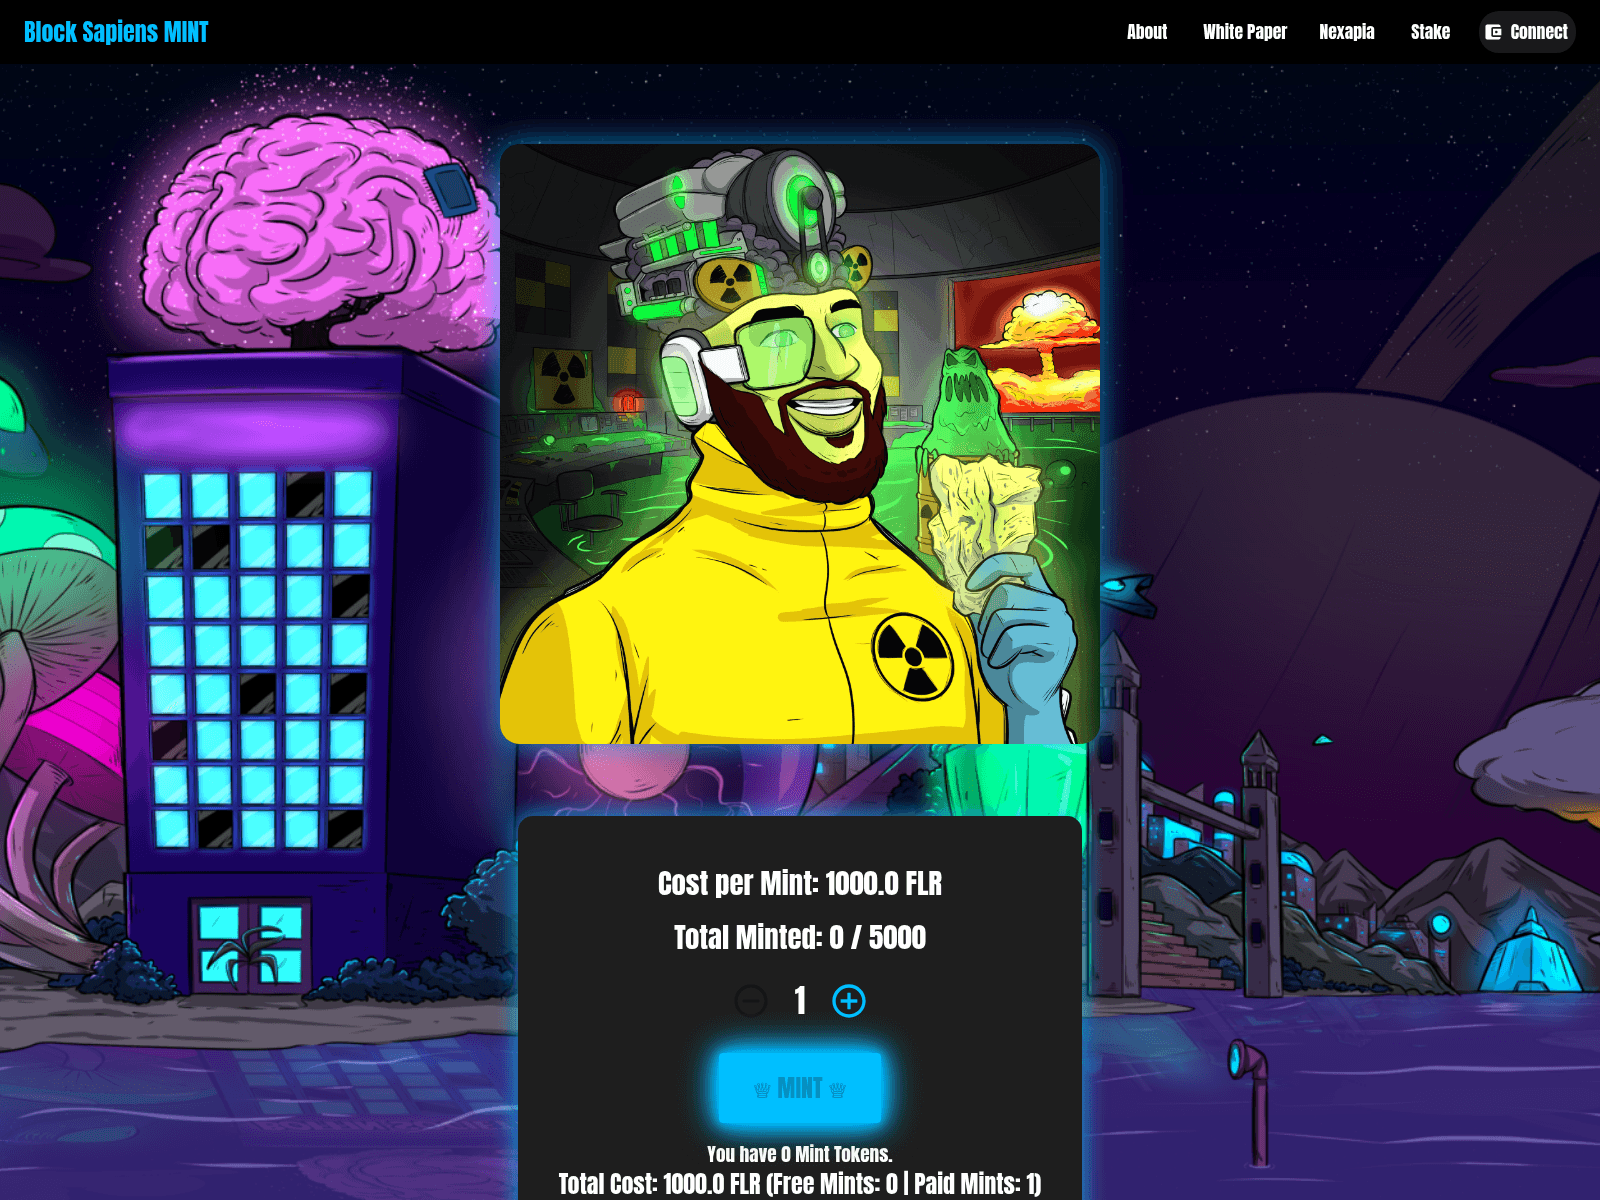
mint.nexapia.xyz

monade.foundation
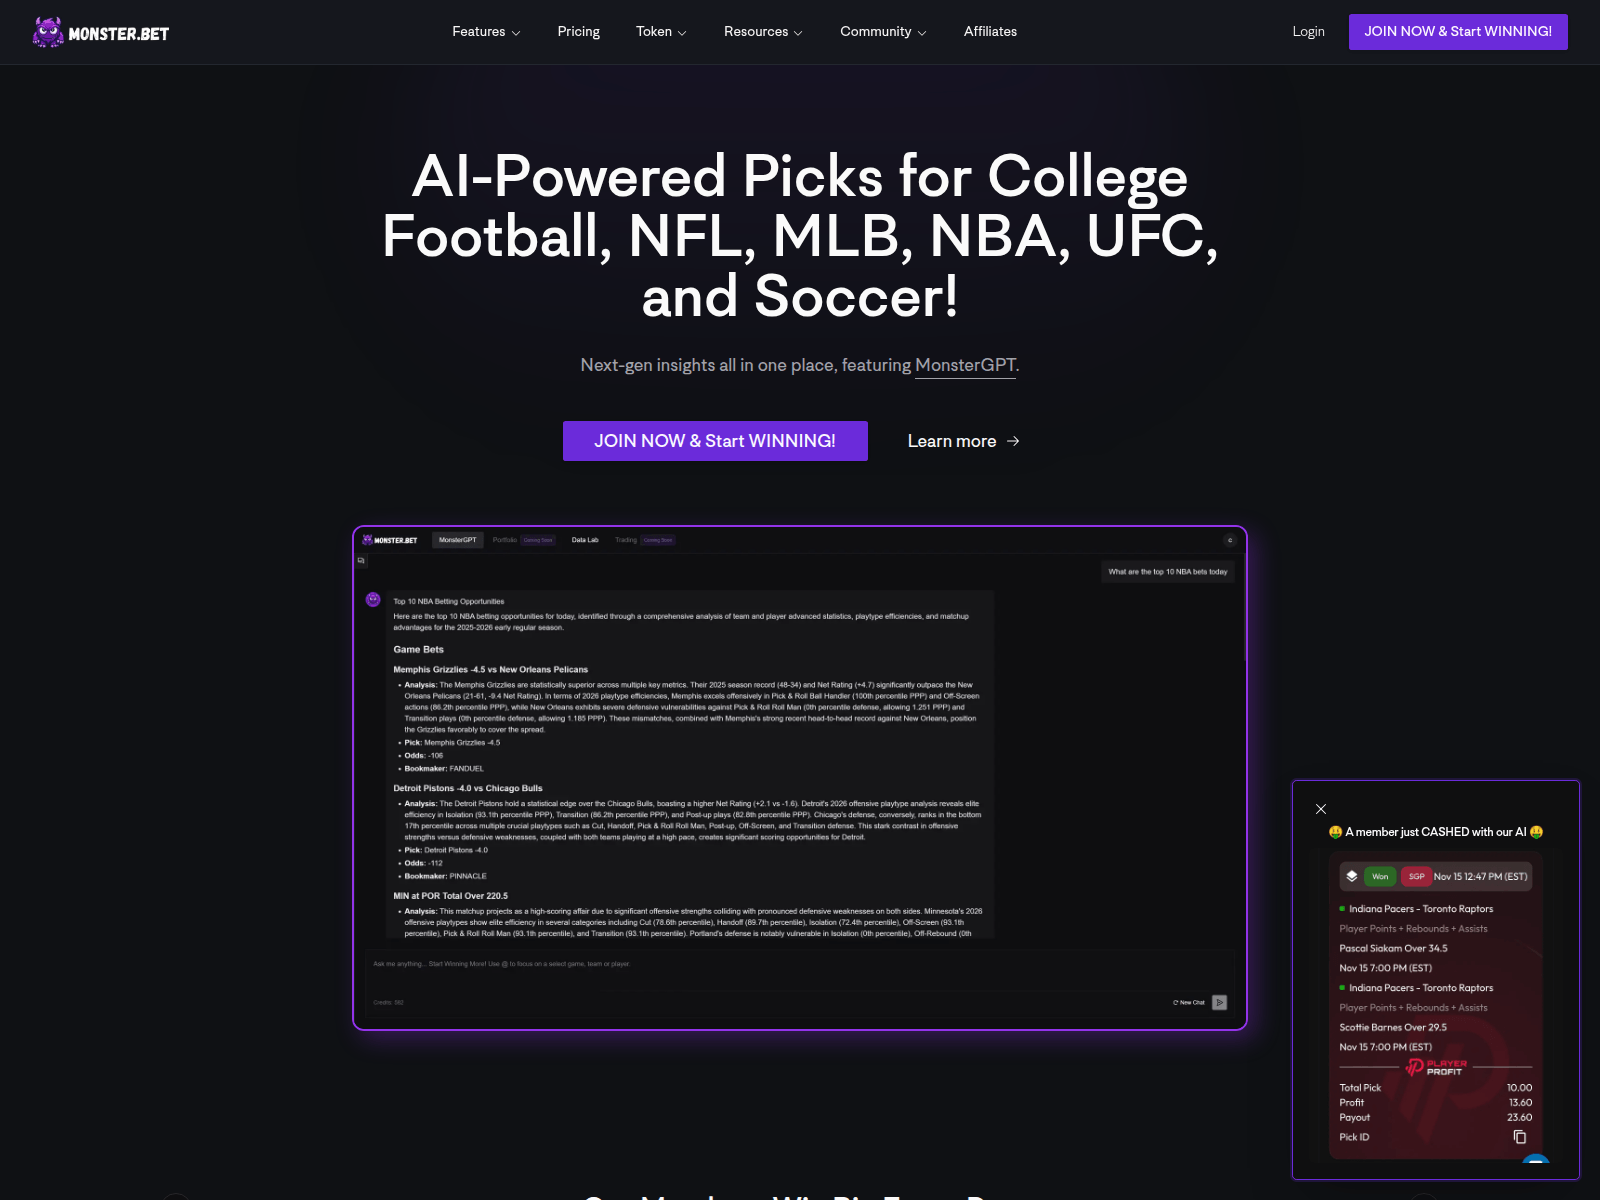
monster.bet

nowa.finance
oguser.pages.dev
opportunities.campaigns-merkl.xyz

papedrop.net

payusdc.app
pepeoftherings.io
polymarket-elon-tracker.com
portal-pepusunchained.com
register-pancakeswap.xyz

sea-app.co
Alur Tanggapan Ancaman Pipeline
Bagaimana setiap domain di hub ini diverifikasi dan bagaimana ancaman yang telah dikonfirmasi dinetralkan. Visualisasi alur kerja lengkap →
Pemeriksaan Intelijen Ancaman— setiap domain dipindai dan dicocokkan dengan:
urlscan.ioTangkapan layar · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency LaporanCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Keamanan FiltersQuad9 · AdGuard · CleanBrowsingWeb-PeriksaFull surface scan
 crt.sh
Sinkronisasi Pemasok Global— hasil deteksi yang telah dikonfirmasi dikirimkan ke 29 mitra:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecUlasan SitusAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftPenghapusan APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.LaporanHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust