एफबीआई आईसी3
संयुक्त राज्य अमेरिका में इंटरनेट-सक्षम अपराध की रिपोर्ट करें
Federal tips line1-800-CALL-FBI

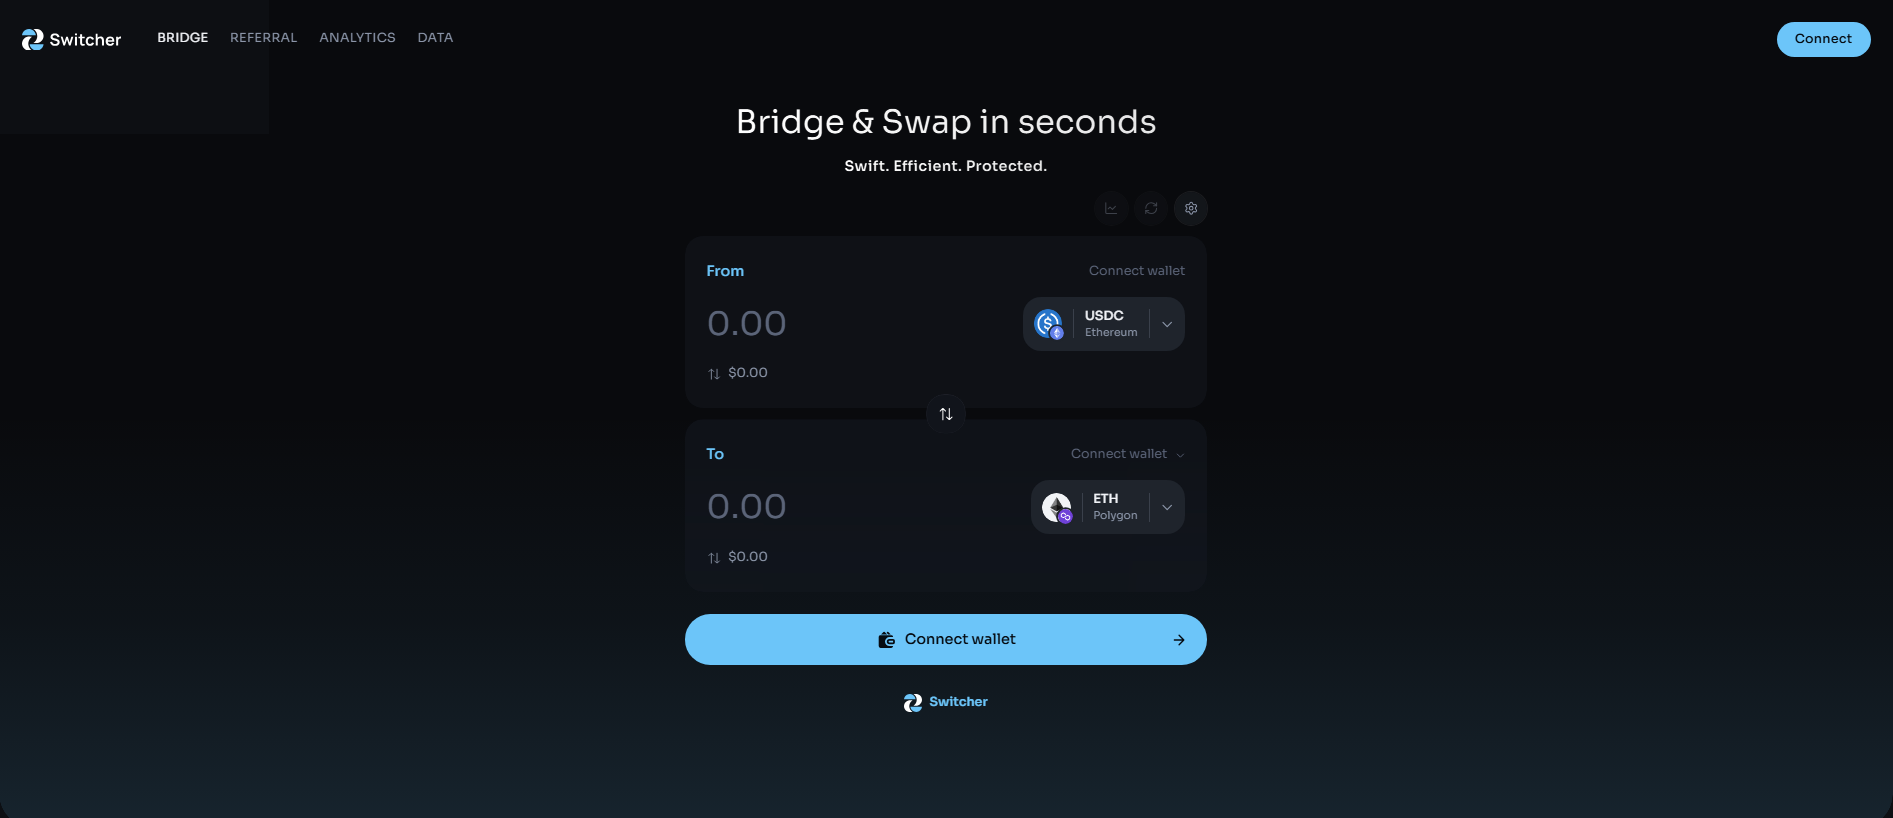
“Switcher | Bridge & Swap in Seconds”
switcher.finance identified as active cryptocurrency phishing site targeting DeFi bridge users. Domain created June 12, 2026, flagged by 2/95 security vendors.
मूल फॉरेंसिक रिकॉर्ड सुरक्षित रखने के लिए नीचे का विस्तृत PhishDestroy AI विश्लेषण अंग्रेज़ी में रखा गया है।
The domain switcher.finance has been identified as an active cryptocurrency phishing site specifically targeting users of decentralized finance (DeFi) bridge and swap services. Analysis confirms this infrastructure is designed to impersonate legitimate cross-chain transaction platforms, presenting itself as a fast bridge and swap service under the page title 'Switcher | Bridge & Swap in Seconds.' The site remains operational and continues to pose a high risk to users seeking to transfer assets between blockchains. Infrastructure analysis reveals the domain was registered on June 12, 2026, through NICENIC INTERNATIONAL GROUP CO., LIMITED, a registrar frequently associated with high-risk domains. It resolves to the IP address 188.114.96.3 and is secured with an SSL certificate issued by Google Trust Services, providing a false sense of legitimacy. As of the latest scan, only 2 of 95 security vendors on VirusTotal have flagged switcher.finance as malicious, indicating low initial detection coverage and suggesting the infrastructure may still evade many automated defenses. No legitimate association with known DeFi platforms or bridge services has been established, and the domain exhibits no historical record of valid financial operations. The site remains active and continues to serve fraudulent content. Users and organizations are strongly advised to block access to switcher.finance at the network level and update endpoint protection rules to include this domain and its associated IP. Security teams should monitor for credential harvesting attempts linked to this infrastructure and educate users on verifying domain authenticity before interacting with DeFi services. Given the low detection rate, manual review of related domains and IPs is recommended to identify potential secondary attack vectors.

Evasion analysis
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
cloudflareScanner note: alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare
 (RU)
PhishDestroy Investigation
 San Francisco, US
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
यदि आपने खाता क्रेडेंशियल, व्यक्तिगत या भुगतान जानकारी दर्ज की है, या इस डोमेन से कोई फ़ाइल डाउनलोड की है, तो तुरंत कार्रवाई करें। घटना की रिपोर्ट करने और अपनी सुरक्षा करने में आपकी सहायता के लिए नीचे संसाधन दिए गए हैं।


आधिकारिक साइबर अपराध संपर्क, या एक शिकायत ड्राफ्ट बनाएं → प्राप्त करने के लिए अपना देश चुनें।
Infrastructure map · switcher.finance
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
ये रिपोर्ट समान साझा एज आईपी का समाधान करती हैं। वे रिपोर्ट खोज में मदद करते हैं लेकिन सामान्य स्वामित्व या साझा मूल सर्वर का संकेत नहीं देते हैं।
These domains also target अज्ञात users. View all Unknown threats →
Part of the अज्ञात phishing campaign. View all campaign domains →
PhishDestroy डेटाबेस से हाल ही में रिपोर्टें जोड़ी गईं। ये खोज लिंक साझा बुनियादी ढांचे या स्वामित्व का संकेत नहीं देते हैं।
संग्रहीत ब्लॉकलिस्ट, WHOIS, DNS और सार्वजनिक स्कैन साक्ष्य का उपयोग करके खतरे का विश्लेषण
अभी स्कैन करेंसंदिग्ध डोमेन हमारे थ्रेट डेटाबेस में जमा करें — समुदाय की सुरक्षा करें
रिपोर्ट करेंहाल की फ़िशिंग रिपोर्टें और उपलब्धता में परिवर्तन देखे गए
निगरानी करेंलाइव खतरों की निगरानी करें या यदि आपको लगता है कि यह एक गलत सकारात्मक है तो इस लिस्टिंग को चुनौती दें।

 wrencapstead.digital
 zywa-capovin.pro
 xtradegrok36.com
 chat-trade-ai.live
 clawnchtoken.com
 1kecv.com
 qua.vexotra.com
 efootball.hilesi.org
 primarkpolska.pl