एफबीआई आईसी3
संयुक्त राज्य अमेरिका में इंटरनेट-सक्षम अपराध की रिपोर्ट करें
Federal tips line1-800-CALL-FBI

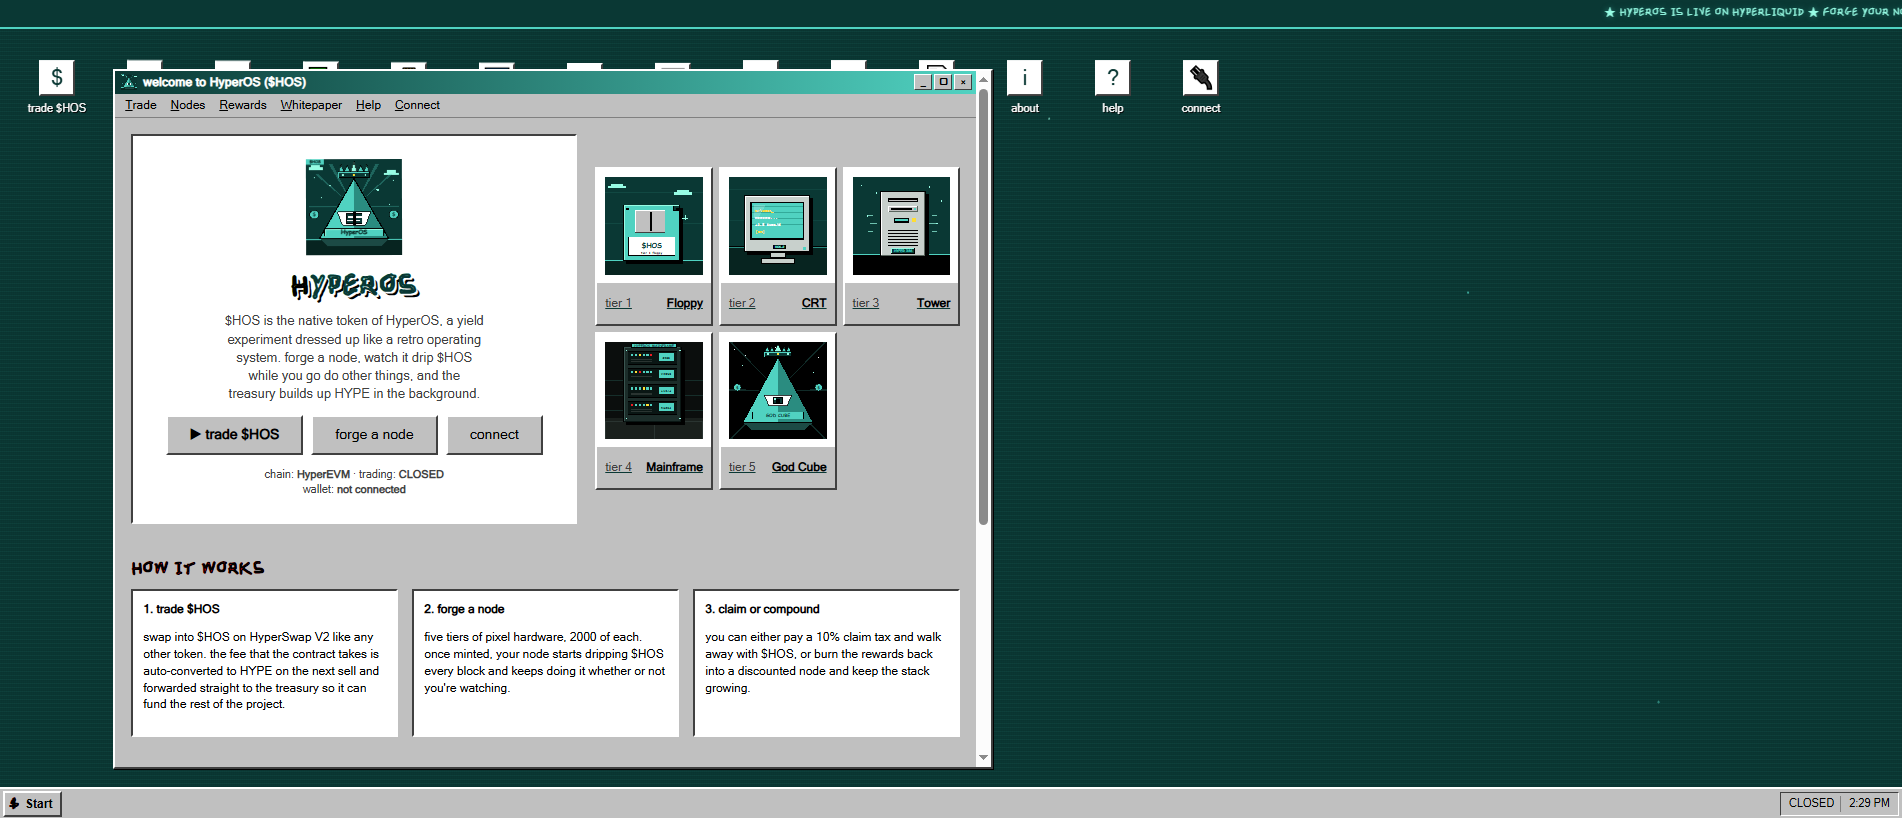
“HyperOS - $HOS”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@namecheap.com.
The latest stored availability evidence still shows the domain reachable; 3 months has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
hyper-os.finance — अंतिम ज्ञात सक्रिय (HTTP 200). ब्रांड प्रतिरूपण: Unknown; घोटाले का प्रकार: Generic Phishing. साक्ष्य सारांश: VirusTotal 9/89 (alphaMountain.ai, BitDefender, Chong Lua Dao, Forcepoint ThreatSeeker, Fortinet); 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 87/100. रजिस्ट्रार: NameCheap.
मूल फॉरेंसिक रिकॉर्ड सुरक्षित रखने के लिए नीचे का विस्तृत PhishDestroy AI विश्लेषण अंग्रेज़ी में रखा गया है।
The domain hyper-os.finance is identified as a phishing site, posing a high risk to users who may visit it. Phishing domains are designed to steal personal and financial information by mimicking legitimate websites and tricking users into providing sensitive data.
Analysis indicates that hyper-os.finance is flagged as a generic_phishing domain by 10 out of 95 security vendors on VirusTotal. The domain was created on May 27, 2026, and is registered through NameCheap, Inc. The site uses technologies such as LiteSpeed and jsDelivr, which are common in both legitimate and malicious web infrastructures. The SSL certificate is issued by Sectigo Limited, and the domain resolves to the IP address 67.223.118.135. Additionally, the domain appears on three security blocklists and has a Gridinsoft trust score of 0/100, indicating a significant lack of trustworthiness.
If a user has visited hyper-os.finance, it is recommended to immediately change any passwords that may have been entered on the site, especially for financial and cryptocurrency accounts. Users should also monitor their financial statements and credit reports for any unauthorized activity. Running a full system scan using reputable antivirus software is advised to ensure no malware was installed. Finally, users should be cautious of any emails or messages that appear to be related to this domain and report them to their respective security teams.

Evasion analysis
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
LiteSpeedScanner note: alive_content: raw=ok; http=200; via=https_proxy; server=LiteSpeed
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Google PageSpeed Insights — mobile performance audit of hyper-os.finance · checked Jun 26, 2026
1 समुदाय सदस्य ने रिपोर्ट किया; पहली बार 29/05/2026 को देखा गया
PD-20260529-FC3BC3 Recipient: abuse@namecheap.com Registrar: Namecheap Inc (United States) Policy Violations: Domain Registration Agreement prohibits hacking, misuse of domain to conduct attacks, scam and fraudulent activities; AUP allows immediate suspension Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
यदि आपने खाता क्रेडेंशियल, व्यक्तिगत या भुगतान जानकारी दर्ज की है, या इस डोमेन से कोई फ़ाइल डाउनलोड की है, तो तुरंत कार्रवाई करें। घटना की रिपोर्ट करने और अपनी सुरक्षा करने में आपकी सहायता के लिए नीचे संसाधन दिए गए हैं।


आधिकारिक साइबर अपराध संपर्क, या एक शिकायत ड्राफ्ट बनाएं → प्राप्त करने के लिए अपना देश चुनें।
Infrastructure map · hyper-os.finance
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
एक अन्य फ़िशिंग डोमेन इस मूल आईपी को साझा करता है - संभावित सह-स्थित बुनियादी ढाँचा।
These domains also target अज्ञात users. View all Unknown threats →
Part of the अज्ञात phishing campaign. View all campaign domains →
PhishDestroy डेटाबेस से हाल ही में रिपोर्टें जोड़ी गईं। ये खोज लिंक साझा बुनियादी ढांचे या स्वामित्व का संकेत नहीं देते हैं।
संग्रहीत ब्लॉकलिस्ट, WHOIS, DNS और सार्वजनिक स्कैन साक्ष्य का उपयोग करके खतरे का विश्लेषण
अभी स्कैन करेंसंदिग्ध डोमेन हमारे थ्रेट डेटाबेस में जमा करें — समुदाय की सुरक्षा करें
रिपोर्ट करेंहाल की फ़िशिंग रिपोर्टें और उपलब्धता में परिवर्तन देखे गए
निगरानी करेंलाइव खतरों की निगरानी करें या यदि आपको लगता है कि यह एक गलत सकारात्मक है तो इस लिस्टिंग को चुनौती दें।
 woqokn.com
 rufus.im
 budowagips.com
 fsv-pl.com
 1kecv.com
 qua.vexotra.com
 efootball.hilesi.org