VirusTotal
8 / 92 engine detections
Ouvrir le rapport

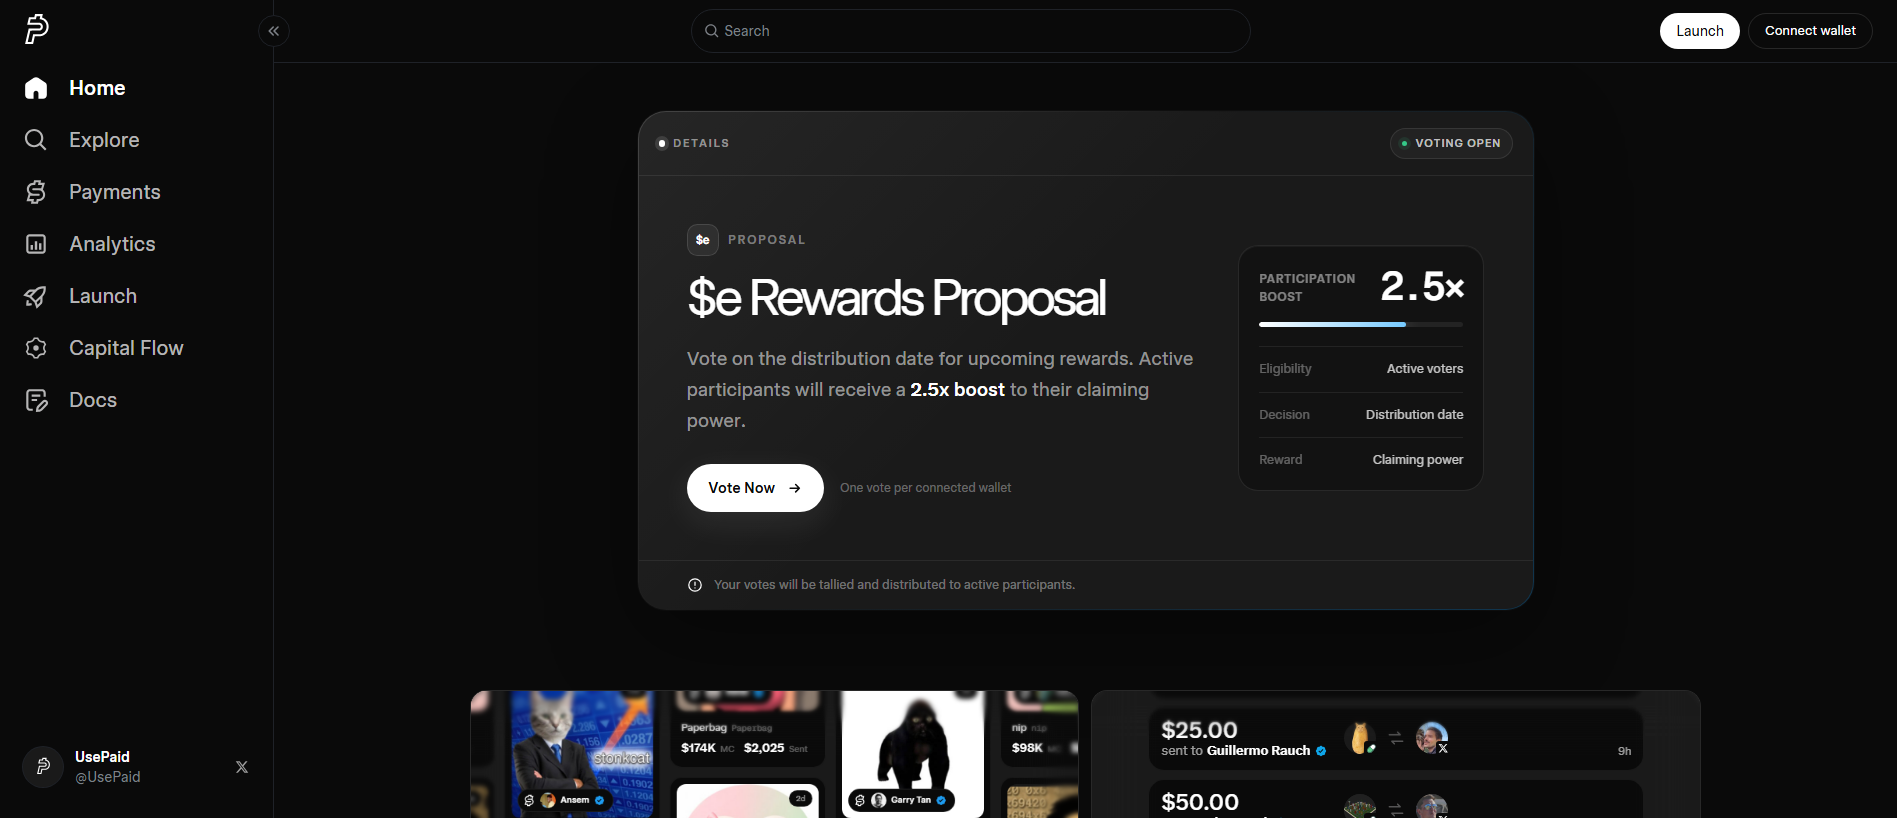
“UsePaid - Route token fees through X Money”
The sent-report ledger records the first outgoing report at .
The recorded recipient is registrar-abuse@google.com.
The latest stored availability evidence still shows the domain reachable; 23 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Usurpation de MetaMask: e-usepaid.app — Dernier actif connu (HTTP 200). Résumé des preuves: VirusTotal 8/92 (alphaMountain.ai, BitDefender, Forcepoint…
L’analyse détaillée de PhishDestroy AI reste en anglais afin de préserver le relevé forensique original.
8 / 92 engine detections
Ouvrir le rapport2 det.
Ouvrir le rapportSuspicious
Ouvrir le rapportDBL_SPAM
4 community references
Ouvrir le rapportNo threat flag
Ouvrir le rapportNo malicious flag
Ouvrir le rapportResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
e-usepaid.app is an impersonation phishing page that borrows the UsePaid name and presents itself as "UsePaid - Route token fees through X Money." It targets crypto users who might believe a payments service will handle their token transaction fees. PhishDestroy first flagged it on 2026-09-27. As of 2026-10-19 the site was still online and serving its content.
The page pitches a convenience feature: route your token fees through X Money and let UsePaid take care of the rest. Impersonation pages like this ask visitors to connect a wallet, sign a request or send funds to "activate" a service that does not exist. A signature or approval can let the operator move tokens out of the wallet. A direct transfer is simply lost. The familiar brand names and the narrow, technical-sounding offer are there to make that request feel routine.
Eight of 92 VirusTotal engines flagged the domain on 2026-10-07: alphaMountain.ai, BitDefender, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, Kaspersky and SOCRadar. That is a modest count, but it comes from a broad mix of independent vendors. Stronger backing comes from the crypto-specific blocklists. MetaMask, ScamSniffer and SEAL all list it alongside PhishDestroy, which means the major wallet-protection feeds treat it as a threat to users. Spamhaus also lists the domain in its DBL as spam, and it appears in four AlienVault OTX threat pulses.
The domain was registered on 2026-09-26 through NICENIC INTERNATIONAL GROUP CO., LIMITED and was caught one day later. That timing fits a short-lived campaign domain built for immediate use. Traffic passes through Cloudflare's network, geolocated to Canada. This means the visible address belongs to the proxy rather than the server actually hosting the page.
Do not connect a wallet or sign anything on e-usepaid.app. If you already connected and approved a request, revoke the approvals granted to unfamiliar spenders with a token-approval checker. Move any remaining assets to a fresh wallet if you signed something you did not understand. Any fee you sent to the site should be treated as gone, and you should ignore follow-up offers to recover it for a charge. Defenders should block the domain at DNS and proxy level and add it to wallet and browser blocklists. Watch for lookalike UsePaid or X Money fee-routing domains from the same registration pattern.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
0x09a61c9d23f30ffb70ef60faeac7894aad312f66Format validated · Domain analysis0x2483553d7721ab4fa9d2496cb325c7deb1ae8be4Format validated · Domain analysis0x276c33312c83d1f905d81658b67d2efc3b6f633dFormat validated · Domain analysis0x3e4439186ea40a01355329040d9aa047b8a2ee54Format validated · Domain analysis0x470d38b03554befc6f5c2eae62c2c48f4748fb7aFormat validated · Domain analysis0x52a6140e5109547e4c1ec86b4cda0cd0ddea29c8Format validated · Domain analysis0x58967fbf6c56b371521653f8888dded9e22f4ad2Format validated · Domain analysis0x633de59aba83b57ff9dc0330f2fc16187e04fa16Format validated · Domain analysis0x9ba8f776e7d4de314ab7611491a72ca1496d6378Format validated · Domain analysis0xebd79ceada7a7798ee75727671581dda5a9e88e4Format validated · Domain analysishttps://t.me/usepaidappStored page referenceIoC extraction recorded 2026-09-28 04:00:09 UTC
Last checked
 (RU)
PhishDestroy Investigation
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
La réputation Edge-IP n’est pas attribuée à ce domaine.
lady.ns.cloudflare.comrob.ns.cloudflare.comLocation describes the IP network.
c5f65879a8f07636200c9b47949dd4e3f31c0e13cec236c24f75cc1c3b2ffae6Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of e-usepaid.app · checked Sep 27, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Inconnu→live_content
content_served
Indisponible→Accessible
Accessible→Indisponible
Inconnu→live_content
content_served
Inconnu→live_content
content_served
Indisponible→Accessible
Accessible→Indisponible
Inconnu→live_content
content_served
Indisponible→Accessible
Accessible→Indisponible
Inconnu→live_content
content_served
Indisponible→Accessible
Accessible→Indisponible
Inconnu→live_content
content_served
Indisponible→Accessible
Accessible→Indisponible
Inconnu→live_content
content_served
Inconnu→live_content
content_served
Inconnu→live_content
content_served
Inconnu→live_content
content_served
Inconnu→live_content
content_served
Inconnu→live_content
content_served
Inconnu→live_content
content_served
Inconnu→live_content
content_served
Inconnu→live_content
content_served
0→2
Accessible
No threat flag
View source8/92 engine detections
View source4 community references
View sourcePD-20260927-5D42F8
e-usepaid.app
View sourcePage captured
View source79 domaines ressemblants enregistrés
Chaque ligne correspond à une raison pour laquelle un domaine est associé à cet hébergeur. La taille des nœuds indique les détections de VirusTotal et les nœuds en pointillés sont déjà hors ligne. Les listes complètes figurent ci-dessous.
Même hachage de favicon ou même titre de page que cet hébergeur.
Ces rapports renvoient à la même adresse IP périphérique partagée. Ils facilitent la découverte des rapports mais n'impliquent pas de propriété commune ni de serveur d'origine partagé.
Reports with the same collector label. A shared label does not establish impersonation or common ownership. View matching reports →
Enregistrés auprès du même bureau d'enregistrement. Un bureau d'enregistrement dessert des millions de clients sans lien entre eux ; ce regroupement constitue donc simplement un constat et ne prouve pas l'existence d'un lien.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
e-usepaid.app
PD-20260927-5D42F8 Recipient: registrar-abuse@google.com Si vous avez saisi des informations d'identification de compte, des informations personnelles ou de paiement, ou téléchargé un fichier à partir de ce domaine, agissez immédiatement. Vous trouverez ci-dessous des ressources pour vous aider à signaler l'incident et à vous protéger.


Sélectionnez votre pays pour obtenir contacts officiels en matière de cybercriminalité ou créer un projet de plainte →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
e-usepaid.app)Même si vous ne disposez pas de tous les détails — déposer quand même une plainte. Même des informations partielles peuvent aider les enquêtes.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Analyse des menaces à l'aide de listes de blocage stockées, de WHOIS, de DNS et de preuves d'analyse publique
Scanner maintenantSignalez les domaines suspects à notre base de données des menaces — protégez la communauté
SignalerRapports de phishing récents et changements de disponibilité observés
SurveillerSurveillez les menaces en temps réel ou signalez cette alerte si vous pensez qu'il s'agit d'un faux positif
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.