IC3 del FBI
Denunciar delitos cometidos a través de Internet en los Estados Unidos
Federal tips line1-800-CALL-FBI

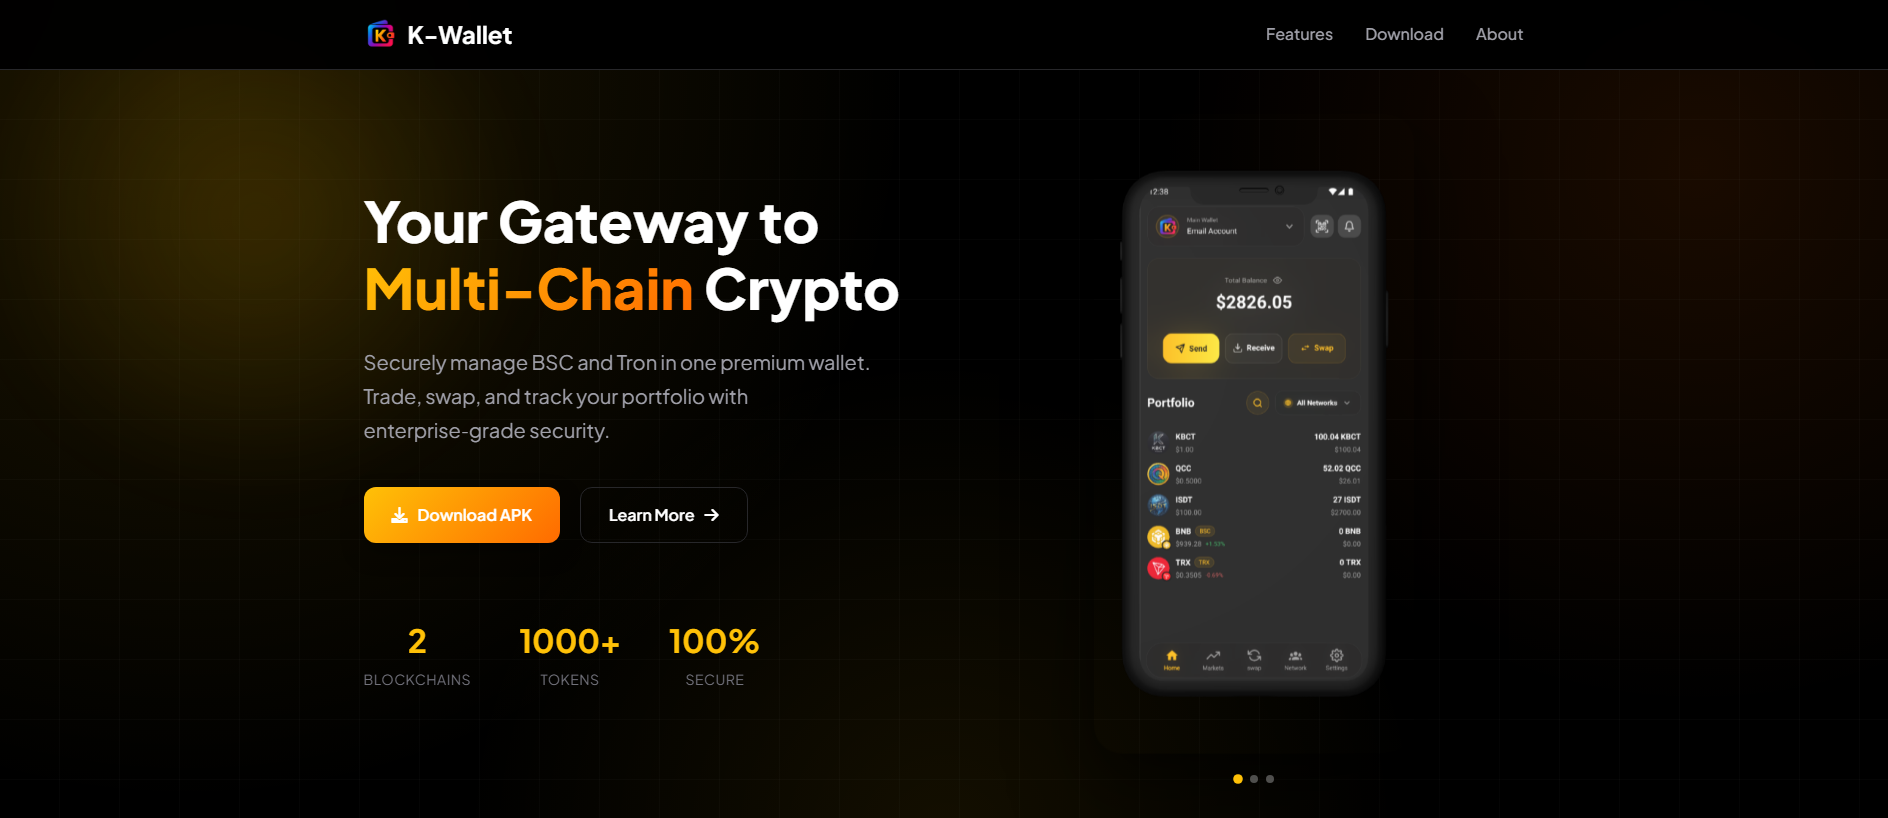
“K-Wallet - BSC & Tron Crypto Wallet”
www.kwallet.trade is an active crypto drainer phishing domain impersonating a BSC & Tron wallet. Resolves to 82.112.226.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.
This domain, www.kwallet.trade, is flagged as an active crypto drainer phishing site designed to target users of Binance Smart Chain (BSC) and Tron cryptocurrency wallets. The site masquerades as a legitimate wallet service under the name 'K-Wallet,' luring victims into connecting their wallets to malicious smart contracts that siphon funds without authorization. Analysis indicates the use of a drainer kit, likely deployed to automate the theft of digital assets upon wallet connection, a common tactic in recent cryptocurrency phishing campaigns. Infrastructure analysis reveals the following technical indicators: the domain resolves to IP address 82.112.226.231 and was registered on September 11, 2025, through GoDaddy.com, LLC. The SSL certificate is issued by Let's Encrypt, a detail often exploited by threat actors to lend a false sense of legitimacy. As of the latest scan, VirusTotal reports 2 out of 95 security vendors flagging the domain, while it appears on two independent security blocklists, including PhishDestroy and OISD. The domain's recent creation date and immediate malicious activity suggest a short-lived, high-impact campaign typical of crypto drainer operations. The site remains active and poses an elevated risk to users who may unknowingly connect their wallets. Immediate response actions include blocking the domain at the DNS level, revoking wallet access to any connected smart contracts, and monitoring for unauthorized transactions. Despite its presence on blocklists, the domain may still evade detection in some environments due to its recent registration and low initial detection rate. Users are advised to verify wallet addresses, avoid interacting with unsolicited wallet prompts, and cross-reference domain details with official sources before engaging with any cryptocurrency service.

Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.
Nota del escáner: alive_content: raw=ok; http=200; via=https_proxy
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Google PageSpeed Insights — mobile performance audit of kwallet.trade · checked Jun 26, 2026
Reportado por 1 miembro de la comunidad; visto por primera vez el 30/05/2026
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Cada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
El mismo hash del favicon o el mismo título de página que este servidor.
Forma parte de la campaña de phishing «Unknown». Ver todos los dominios de la campaña →
Otro dominio de phishing comparte esta IP de origen: posible infraestructura compartida.
Estos dominios también se dirigen a los usuarios de Unknown. Ver todas las amenazas de «Unknown» →
Registrados a través del mismo proveedor de registro. Un proveedor de registro presta servicio a millones de clientes que no tienen relación entre sí, por lo que este dato solo agrupa los registros, en lugar de demostrar que exista un vínculo.
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.