IC3 del FBI
Denunciar delitos cometidos a través de Internet en los Estados Unidos
Federal tips line1-800-CALL-FBI

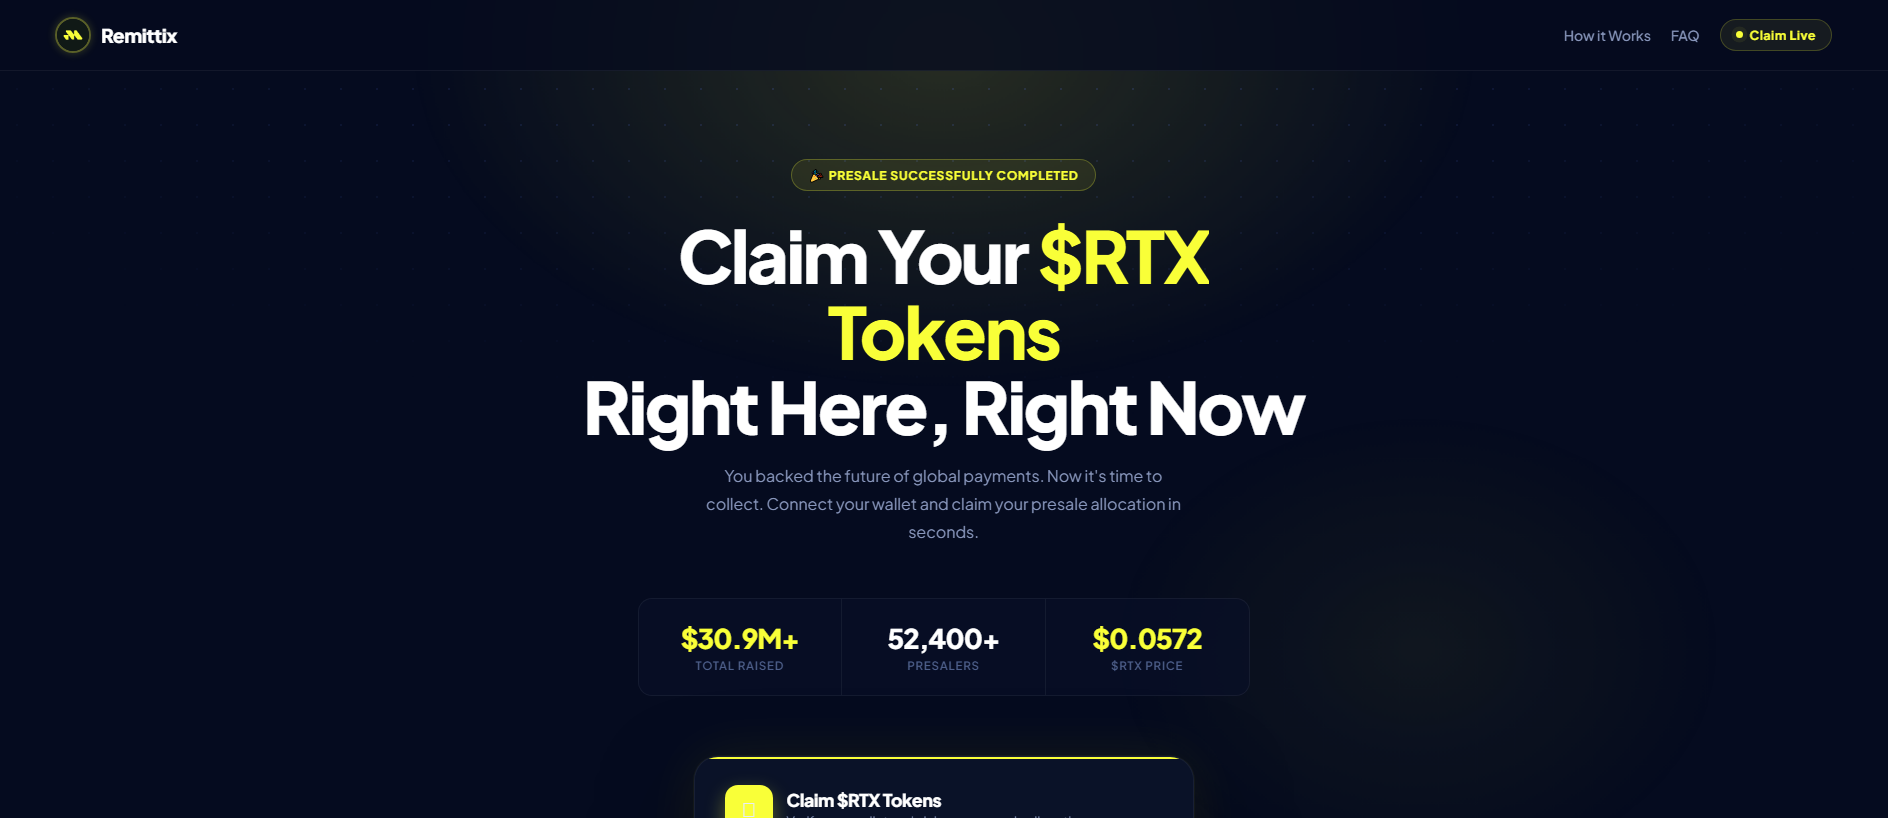
“Remittix — Claim Your $RTX Tokens”
Analysis of www.claimremittixtoken.live indicates that the site was operated as a fake airdrop crypto drainer.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.
Analysis of www.claimremittixtoken.live indicates that the site was operated as a fake airdrop crypto drainer. The page title “Remittix — Claim Your $RTX Tokens” was observed, matching the declared scam type of a fake airdrop. The domain resolves to the IP address 64.29.17.65, which belongs to Amazon.com, Inc. (AS16509) and is geolocated in the United States. DNS resolution uses Cloudflare nameservers seth.ns.cloudflare.com and mckenzie.ns.cloudflare.com. The site presented a valid TLS certificate issued by Let’s Encrypt (R12), confirming encrypted HTTPS availability at the time of capture.
HTTP response code 451 was recorded, indicating that the content was unavailable for legal reasons, and the current status is reported as taken offline. Registration data shows the domain was registered through NICENIC INTERNATIONAL GROUP CO., LIMITED. The domain appears on one security blocklist and is specifically blocked by PhishDestroy. VirusTotal analysis returned five detections out of ninety‑one scanners, confirming that multiple security vendors flagged the domain as malicious.
No additional intelligence such as Safe Browsing or OTX references were provided. The evidence confirms that the domain was used to lure victims into submitting cryptocurrency wallet credentials under the pretense of receiving RTX tokens. Defenders should continue to block the domain at perimeter and DNS layers, monitor for any resurgence of the same IP or Cloudflare nameserver configuration, and incorporate the observed indicators—IP address, TLS certificate issuer, page title, and VirusTotal detection count—into threat‑intel feeds. Ongoing observation is advised to detect possible re‑registration or copycat campaigns employing similar branding or infrastructure.

Evasion evidence
The page served one response to a browser-like visitor and another to a crawler or security scanner. Cloaking exists only to keep reviewers away from the real landing page.
status_splitVercelScanner note: dead_http: raw=http_451; http=451; via=https_proxy; server=Vercel; provider_error=DEPLOYMENT_DISABLED
Provider response during scan: DEPLOYMENT_DISABLED
 (RU)
PhishDestroy Investigation
 Walnut, US
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Infrastructure map · claimremittixtoken.live
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Estos informes se resuelven en la misma IP perimetral compartida. Ayudan a descubrir informes, pero no implican una propiedad común ni un servidor de origen compartido.
These domains also target Desconocido users. View all Unknown threats →
Part of the Desconocido phishing campaign. View all campaign domains →
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.
 seguralzgestion.com
 usualmoneys.com
 pumplivesol.top
 parik-24.hu