VirusTotal
5 / 91 engine detections
Abrir informe
“USDT0”
Phishing: duplicate-disabled-462728.invalid — Contenido no disponible. Resumen de las pruebas: VirusTotal 5/91 (alphaMountain.ai, Forcepoint ThreatSeeker…
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.
5 / 91 engine detections
Abrir informeDBL_PHISH
checked — no detections recorded
Abrir informe2 community references
Abrir informeprovider verdict: clean
Abrir informeNo threat flag
Abrir informeNo malicious flag
Abrir informeResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
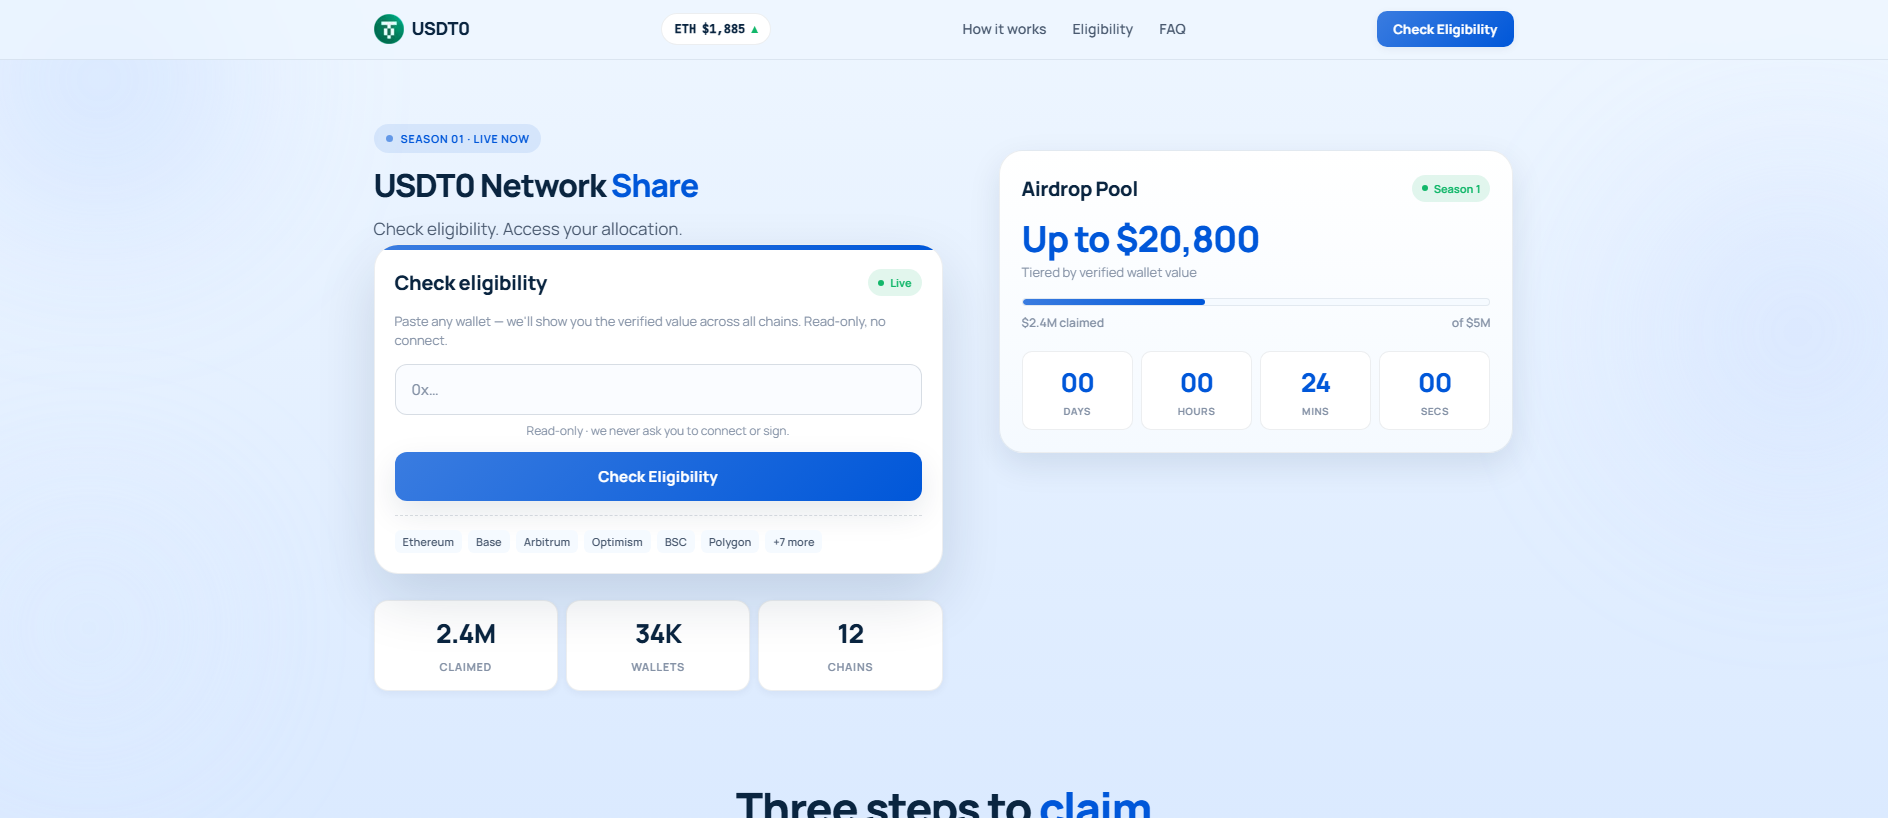
duplicate-disabled-462728.invalid presented itself under the page title "USDT0", impersonating the USDT0 stablecoin brand to catch people who hold or move that token. PhishDestroy first flagged it on 2026-08-14 and classifies it as impersonation phishing. The site has been offline since 2026-09-25 and was still unreachable when last checked on 2026-10-19.
Sites like this copy the look and name of a legitimate crypto project so a visitor believes they are on the official portal. The visitor is then pushed toward an action the real brand would never require on an unfamiliar domain. That might be connecting a wallet and signing a transaction or token approval. It might also be typing in a recovery phrase or private key to "verify" or "claim" something. Any of these can let the operators move the victim's USDT0 and other assets, and on-chain transfers cannot be reversed.
On 2026-08-26, VirusTotal showed 5 of 91 engines flagging the domain: alphaMountain.ai, Forcepoint ThreatSeeker, Fortinet, SOCRadar and VIPRE. That count is modest, which is common for short-lived crypto phishing that has not yet spread widely. The domain also has independent confirmation outside VirusTotal. Spamhaus lists it in its DBL under the phishing category, and it appears in 2 AlienVault OTX threat pulses alongside the PhishDestroy blocklist entry.
The domain was registered through TUCOWS.COM, CO. on 2026-07-04, roughly six weeks before PhishDestroy detected it. That gap suggests the operators prepared the infrastructure in advance rather than launching on the day of registration. It was served from Cloudflare's network, with the address geolocated to Canada, so the true origin server sat behind a reverse proxy. Its TLS certificate came from Google Trust Services, which means the browser padlock offered no signal about whether the site was legitimate.
If you connected a wallet to this site and approved or signed anything, open a token-approval checker for that wallet and revoke any permissions you do not recognize. Then move your remaining funds to a fresh wallet. If you entered a seed phrase or private key, treat that wallet as fully compromised and transfer everything out immediately to a new wallet created from a new phrase. Reach USDT0 only through links published on its official channels. Defenders should block the domain at DNS and proxy layers and hunt logs for past connections to it. They should also watch for lookalike USDT0 domains registered by the same operators.
 (KN)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
La reputación de Edge-IP no se atribuye a este dominio.
barbara.ns.cloudflare.comnikon.ns.cloudflare.comLocation describes the IP network.
6823bc01a6550669706f8ecfd1fd9e54a8f6fea8133761d65a30e39e76dee11cevmentry.comSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of duplicate-disabled-462728.invalid · checked Aug 14, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Accesible→No disponible
5/91 engine detections
View source2 community references
View sourceNo threat flag
View sourceduplicate-disabled-462728.invalid
View sourcePage captured
View sourceCada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
El mismo hash del favicon o el mismo título de página que este servidor.
Registrados a través del mismo proveedor de registro. Un proveedor de registro presta servicio a millones de clientes que no tienen relación entre sí, por lo que este dato solo agrupa los registros, en lugar de demostrar que exista un vínculo.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
duplicate-disabled-462728.invalid
Listed domains receive at least one abuse report; this entry has no retained notification history.
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
duplicate-disabled-462728.invalid)Aunque no tengas todos los detalles — presenta la denuncia de todos modos. Incluso la información parcial sigue siendo útil para las investigaciones.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.