Spamhaus DBL
DBL_SPAM


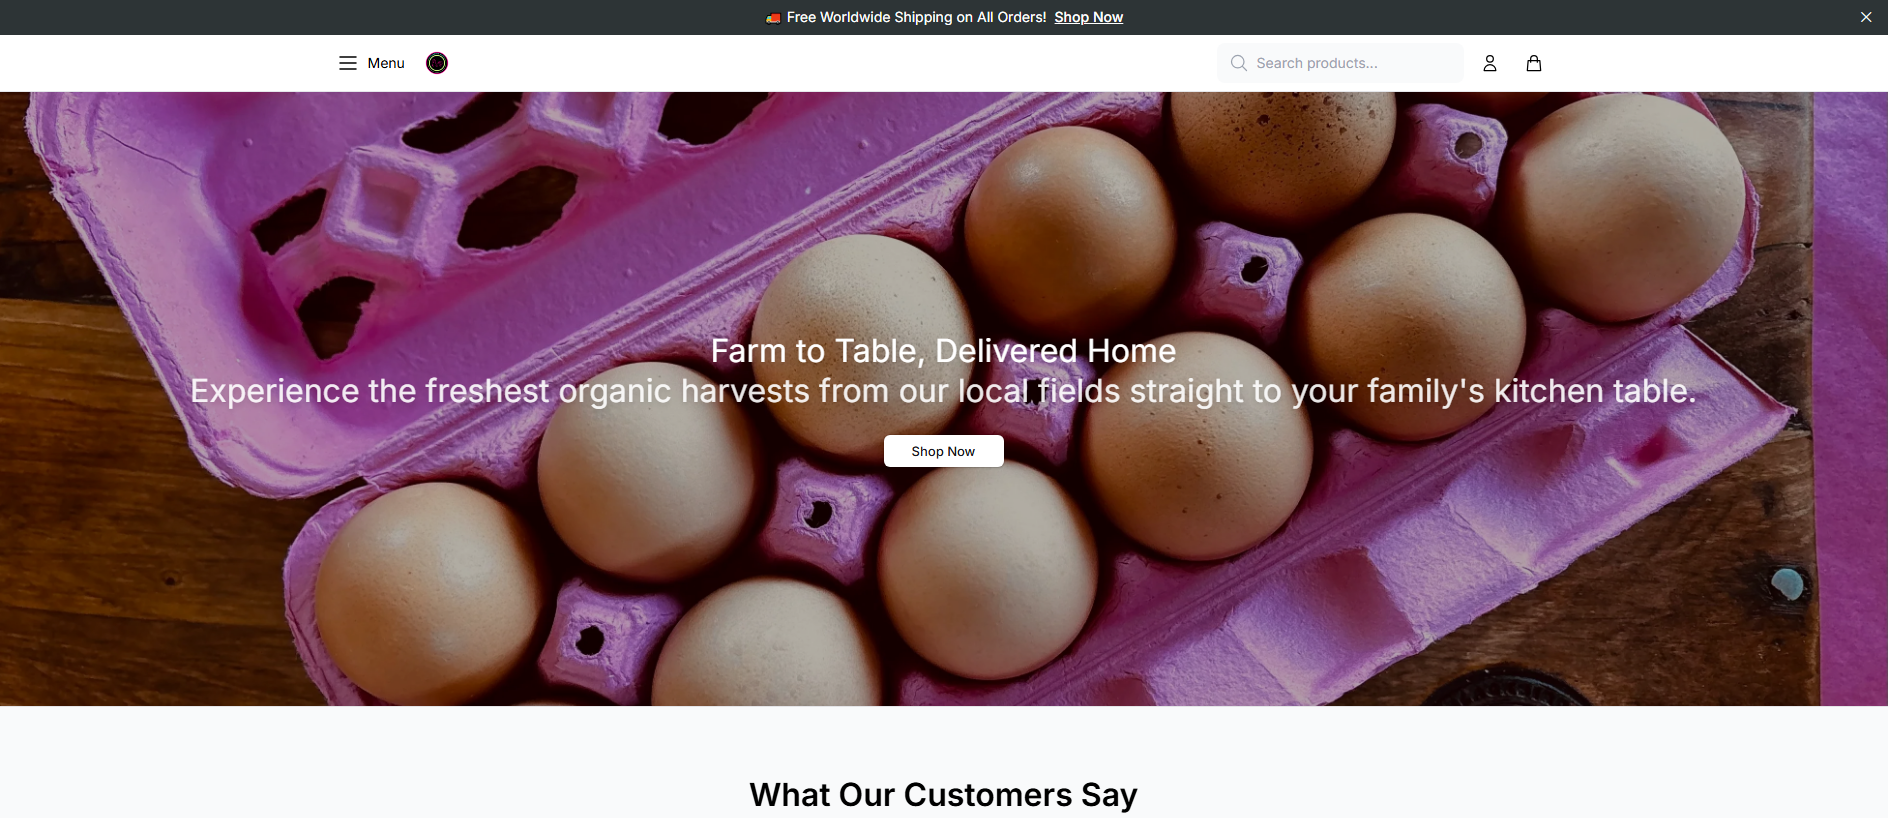
“Home | Blackbird Farms”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@rashost.com.
The latest stored availability evidence still shows the domain reachable; 3 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Phishing: blackbirdcoopshop.shop — Último activo conocido (HTTP 200). Resumen de las pruebas: VirusTotal 0/92; URLScan malicious verdict; Spamhaus DBL_SPAM…
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.
DBL_SPAM
Malicioso
Abrir informe0 / 92 engine detections
Abrir informeScan report
Abrir informe4 community references
Abrir informeprovider verdict: clean
Abrir informeNo threat flag
Abrir informeResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
blackbirdcoopshop.shop is a fake online shop that presents itself as "Blackbird Farms", a homely farm-and-coop storefront aimed at ordinary online shoppers rather than crypto users. PhishDestroy first flagged it on 2026-10-16. The site was still online with its shop content live when last checked on 2026-10-19, so it can still take orders.
The page, titled "Home | Blackbird Farms", borrows the trust that small family farms enjoy and wraps it in a standard webshop layout with product listings, a cart and a checkout. Fake shops like this usually lure buyers with prices noticeably below normal, then collect payment and card or personal details at checkout. Orders either never arrive or are replaced with worthless items. Follow-up messages to the seller go unanswered. Victims lose the purchase amount, and any card data and address they entered can be reused or sold.
urlscan.io rated the site malicious and specifically identified it as a fake shop. Spamhaus lists the domain in its DBL as spam, and it appears in four AlienVault OTX threat pulses, so other researchers have tracked it independently. VirusTotal tells a different story: 0 of 92 engines flagged it on 2026-10-16. That clean result reflects how slowly antivirus vendors pick up fraudulent storefronts, and it should not be read as a sign the shop is safe.
The domain was registered through Dynadot Inc. on 2026-05-20, about five months before PhishDestroy caught it. That gap gave the shop time to look established and collect orders unnoticed. It is hosted on the Malakmadze Web LLC network in Georgia, an unusual location for a business presenting itself as a local farm store. The Let's Encrypt certificate only means the connection is encrypted. It says nothing about who runs the shop.
If you paid on this site, contact your bank or card issuer right away, report the charge as fraud and ask for a chargeback. Cancel the card if you entered its details. Keep your order confirmation and any emails as evidence, and treat follow-up messages claiming to be about delivery or refunds as likely phishing. If you created an account, change that password anywhere you reused it. Defenders should block the domain, add it to web and mail filters, and watch for lookalike Blackbird Farms storefronts on other new domains.
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
ashton.ns.cloudflare.comlina.ns.cloudflare.comLocation describes the IP network.
100c5b2944cff618290529d4cb56e861958b9af58e51f1cfc3ab57c966a2f22aSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of blackbirdcoopshop.shop · checked Oct 16, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
http://blackbirdcoopshop.shop/https://blackbirdcoopshop.shop/Cache-Control: private, no-cache, no-store, max-age=0, must-revalidateContent-Encoding: gzipContent-Type: text/html; charset=utf-8summary_large_imageh3=":443"; ma=2592000private, no-cache, no-store, max-age=0, must-revalidategziptext/html; charset=utf-8Fri, 16 Oct 2026 19:47:39 GMT; rel=preload; as="style"strict-origin-when-cross-originchunkedRSC, Next-Router-State-Tree, Next-Router-Prefetch, Next-Router-Segment-Prefetch, Accept-Encoding1.1 CaddynosniffSAMEORIGIN1; mode=blockValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Accesible→No disponible
Desconocido→live_content
content_served
No disponible→Accesible
Accesible→No disponible
Desconocido→live_content
content_served
Desconocido→live_content
content_served
No disponible→Accesible
Accesible→No disponible
Accesible
No threat flag
View source4 community references
View source0/92 engine detections
View sourcePD-20261016-EFB557
blackbirdcoopshop.shop
View sourcePage captured
View sourceCada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
El mismo hash del favicon o el mismo título de página que este servidor.
Esta IP de origen aloja múltiples dominios de phishing; la infraestructura puede compartirse entre campañas.
Registrados a través del mismo proveedor de registro. Un proveedor de registro presta servicio a millones de clientes que no tienen relación entre sí, por lo que este dato solo agrupa los registros, en lugar de demostrar que exista un vínculo.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
blackbirdcoopshop.shop
PD-20261016-EFB557 Recipient: abuse@rashost.com Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
blackbirdcoopshop.shop)Aunque no tengas todos los detalles — presenta la denuncia de todos modos. Incluso la información parcial sigue siendo útil para las investigaciones.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.