VirusTotal
1 / 92
DenunciarInterpretation & limits
Engine detections from this stored analysis. Vendors and collection times may differ from other sources.


“BIRD EYE Sportswear | BIRD EYE”
Assessment based on the stored source evidence below. Review sources →
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@rashost.com.
The latest stored availability evidence still shows the domain reachable; 2 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
beifashion.shop — Último activo conocido (HTTP 200). Suplantación de marca: Apple; Tipo de estafa: Impersonation. Resumen de las pruebas: VirusTotal 1/92 (Gridinsoft); URLScan malicious verdict; PhishDestroy score 81/100. Registrador: Dynadot.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

These are dated observations, not a live safety check. No flag, a stored capture, or a completed analysis does not establish that a site is safe.
1 / 92
DenunciarEngine detections from this stored analysis. Vendors and collection times may differ from other sources.
malicious
DenunciarThis is the recorded automated analysis. Completion alone is not a safety verdict.
Report stored; detailed verdict not recorded
Alerts refer to the preserved scan. They do not describe the current state of the site.
4 community references
DenunciarCommunity publication references, not a vendor verdict or evidence of a common operator.
provider verdict: clean
A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
informe almacenado
 Denunciar
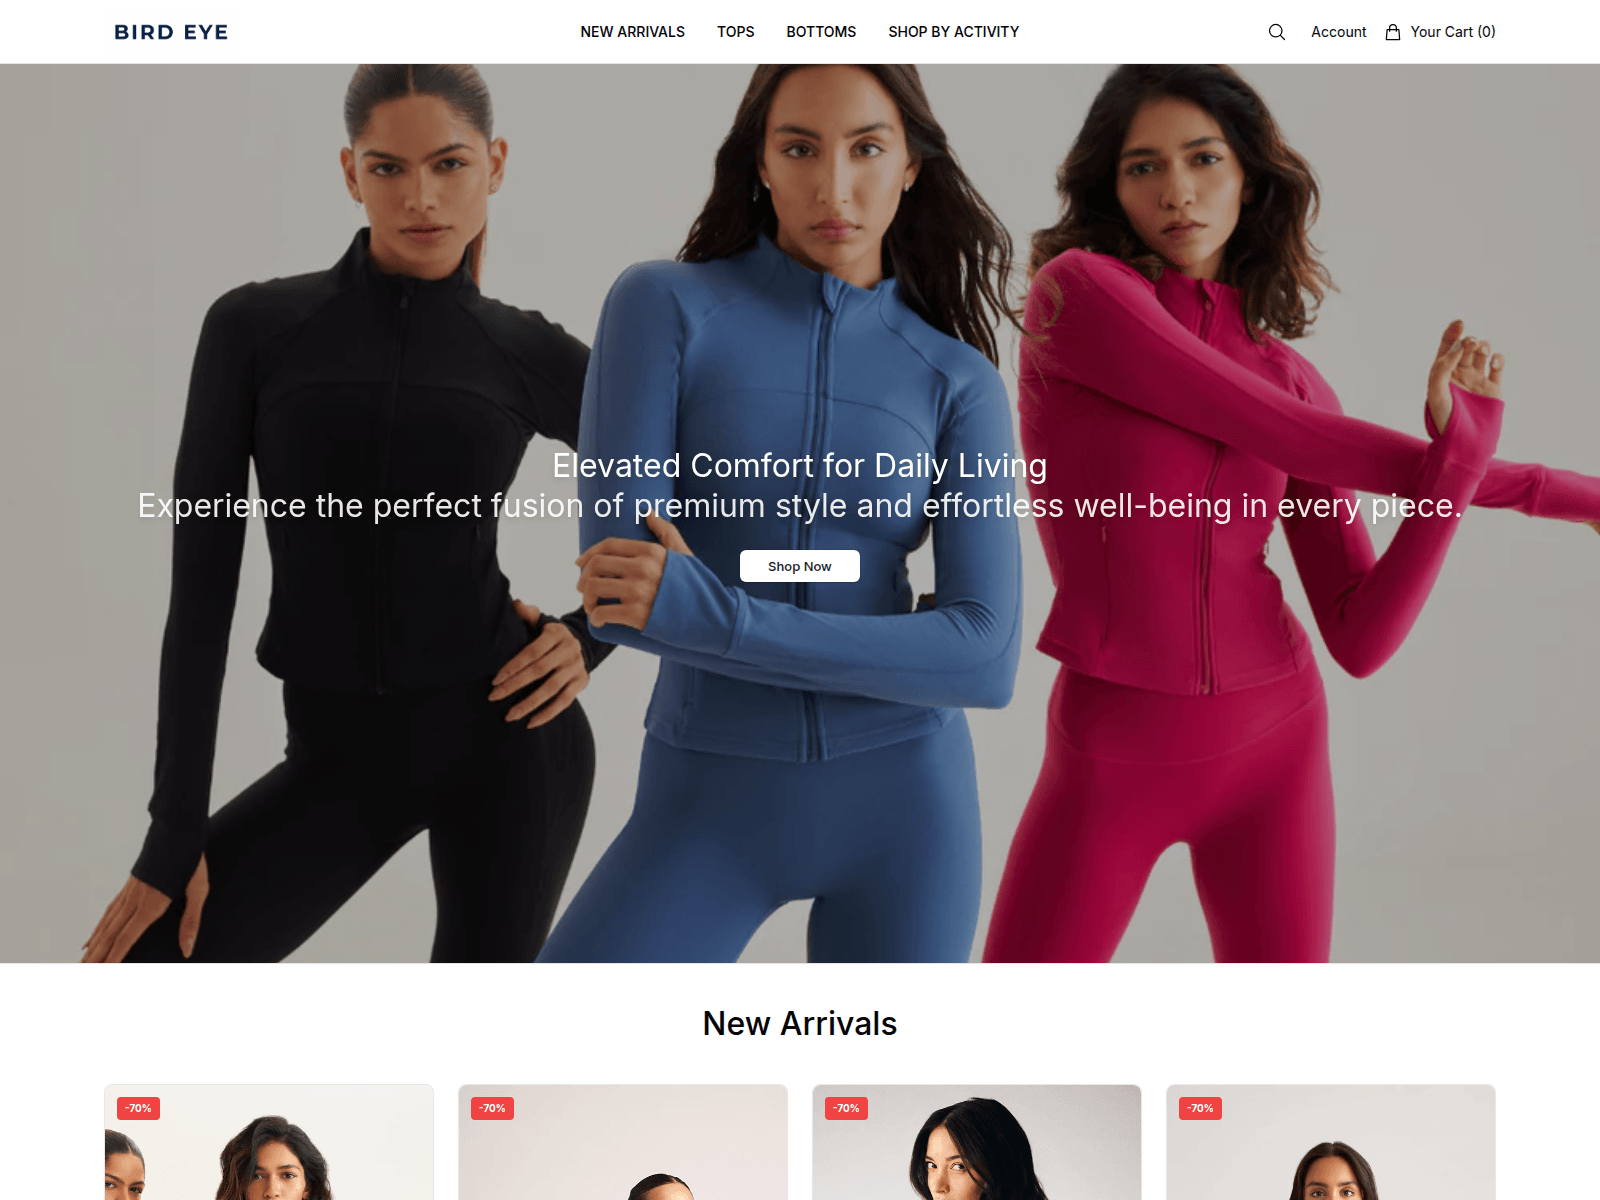
A preserved page image documents what the collector received; a capture is not a safety verdict.
Checked; no threat flag recorded
DenunciarA result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
Stored narrative · generated . Provider checks below retain their own observation dates.
beifashion.shop was recorded in the PhishDestroy internal listing on 2026-10-13, providing a dated security intelligence entry for the domain. Additional technical data includes a PageSpeed performance score of 70 on the same date.
PhishDestroy internally listed beifashion.shop as of 2026-10-13. PageSpeed measured the domain's performance with a score of 70 on 2026-10-13. VirusTotal checked beifashion.shop on 2026-10-11, documenting 1 detection out of 92 scanners. OTX referenced the domain in four pulses as of 2026-10-13.
PhishDestroy contains a dated listing for beifashion.shop, which serves as a recorded catalogue entry for security review. VirusTotal provides a scan-based measurement, documenting how many external scanners flagged the domain. OTX records the domain’s appearance in several pulses, reflecting its mention within security community activity. These sources together offer a technical snapshot of beifashion.shop across different intelligence and detection platforms.
For beifashion.shop, retain the PhishDestroy, VirusTotal, OTX, and PageSpeed records for ongoing reference. Compare future VirusTotal and OTX results to these existing records to track any changes in detections or community reporting. Preserve the PhishDestroy listing and PageSpeed performance score for comprehensive historical context.
Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.
Nota del escáner: alive_content: raw=ok; http=200; via=https_proxy
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
arely.ns.cloudflare.comjoel.ns.cloudflare.comLocation describes the IP network.
d4456334eaa33ad8344845caf851089a760a8cf54140728008944d2fc3cf9ae7Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of beifashion.shop · checked Oct 13, 2026
193.162.133.218.15 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20261013-FDB0B5 Recipient: abuse@rashost.com AUP & Terms of Service Violations: Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices. Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension. Applicable Legal Framework (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Template-based draft · optional AI wording assistance requires separate consent
Cada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
Esta IP de origen aloja múltiples dominios de phishing; la infraestructura puede compartirse entre campañas.
Estos dominios también se dirigen a los usuarios de Apple. Ver todas las amenazas de «Apple» →
Registrados a través del mismo proveedor de registro. Un proveedor de registro presta servicio a millones de clientes que no tienen relación entre sí, por lo que este dato solo agrupa los registros, en lugar de demostrar que exista un vínculo.
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.