Skip to security report
Domain security and threat intelligence
zestprotocol.forum favicon

zestprotocol.forum

“Zest Protocol | The Bitcoin liquidity protocol”

Registrar
Spaceship
Resolved IP
188.114.96.3
Registered
Oct 6, 2026
Threat verdict Critical
Availability Unverified Current reachability is unverified Observed
Source: HTTP probe
VirusTotal detections: 9/92 Stored blocklist matches: 2 Brand impersonation: Sei Young domain: 5 days old
OTX: 3 refs Oct 7, 2026 Sei 1 Report Sent CDN
API
This domain has been flagged as malicious
Security engines reporting a detection: 9. Public blocklists reporting a match: 2. Exercise extreme caution — do not enter credentials or personal information.
ABUSE NOTICE · 72H+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@spaceship.com. The latest stored availability evidence still shows the domain reachable; 4 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
4 days
Reports sent
1
Latest case ID
PD-20261007-29B0CD
Current status
Observed active at latest stored check
VirusTotal
VirusTotal
9 det.
URLQuery
URLQuery
4 det.
OTX references
URLScan
URLScan
TLS Certificate
Expired or unverified
Age
5d Brand New!
PhishDestroy
DestroyList
Listed
Reports Sent
1

Source evidence

7 sources

VirusTotal

9 / 92

Report

OTX

3 community references

Report

CF Radar

provider verdict: suspicious

Report

URLScan capture

stored report

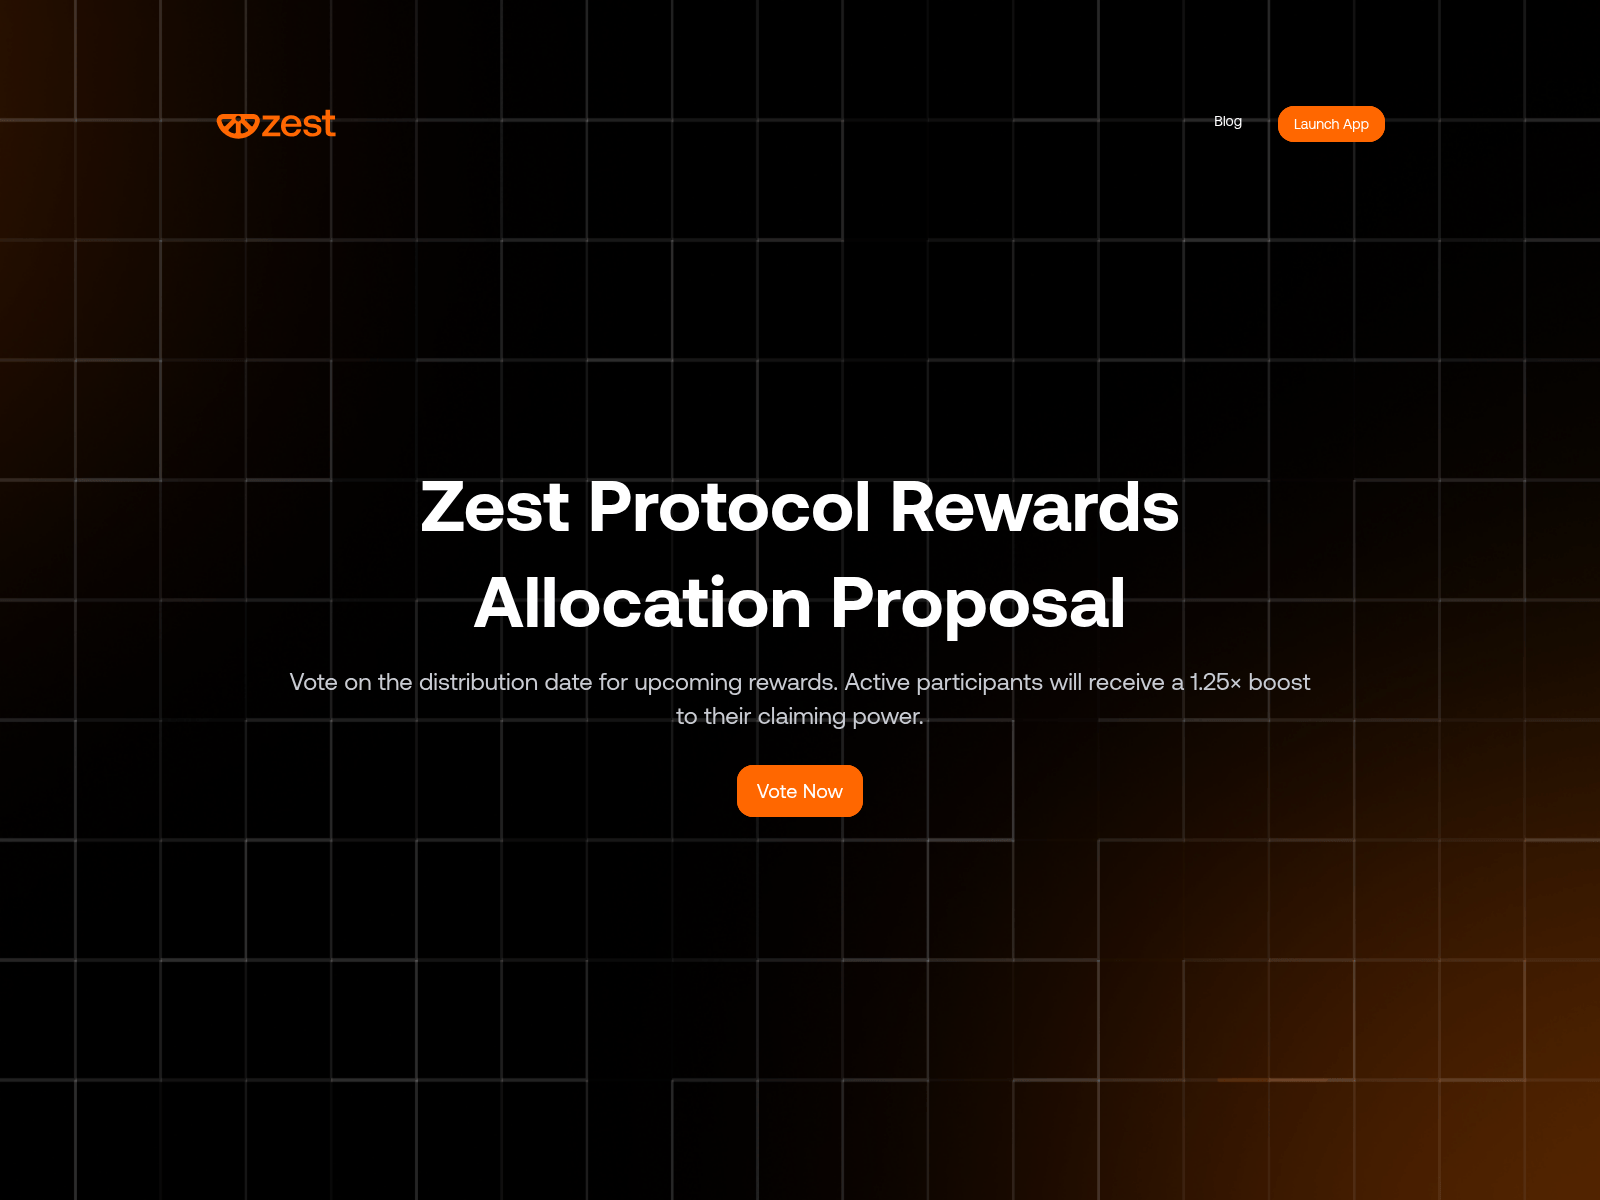
Stored URLScan capture preview
Report

URLScan verdict

Analysis completed

Report

Google Safe Browsing

Checked; no threat flag recorded

Report

Evidence Summary

Critical
VirusTotal
9/92
OTX
3 community refs
URLScan
Stored capture

Assessment

zestprotocol.forum was recorded on 2026-10-07 with inclusion on both the MetaMask and SEAL blocklists, reflecting external attention from these sources. The domain was registered shortly before this observation, on 2026-10-06.

Recorded Evidence

MetaMask and SEAL each listed zestprotocol.forum on their blocklists as of 2026-10-07. Phishdestroy recorded an internal listing for zestprotocol.forum on the same date. The domain registration was completed through Spaceship, Inc. on 2026-10-06.

Interpretation

The blocklist entries from MetaMask and SEAL provide documentation from two external sources regarding zestprotocol.forum. The internal listing by Phishdestroy adds another perspective from a separate system. These records allow comparison of external and internal observations made soon after the domain’s registration.

Recommended Actions

For zestprotocol.forum, review and retain the blocklist records from MetaMask and SEAL as well as the internal listing from Phishdestroy. Compare these source records in future assessments to track any changes or additional observations. Use the documented registration information as a reference for the domain’s timeline in ongoing monitoring efforts.

Detection-evasion analysis

Cloaking and traffic-distribution check

Not yet scanned No crawler-versus-browser difference has been recorded yet

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Last cloaking scan

Scanner note: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='zestprotocol.forum', port=80): Max retries exceeded with url: / (Caused by NewConnectionEr

Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this panel is open.
Waiting

Stored Capture · 3 captures

Page Title
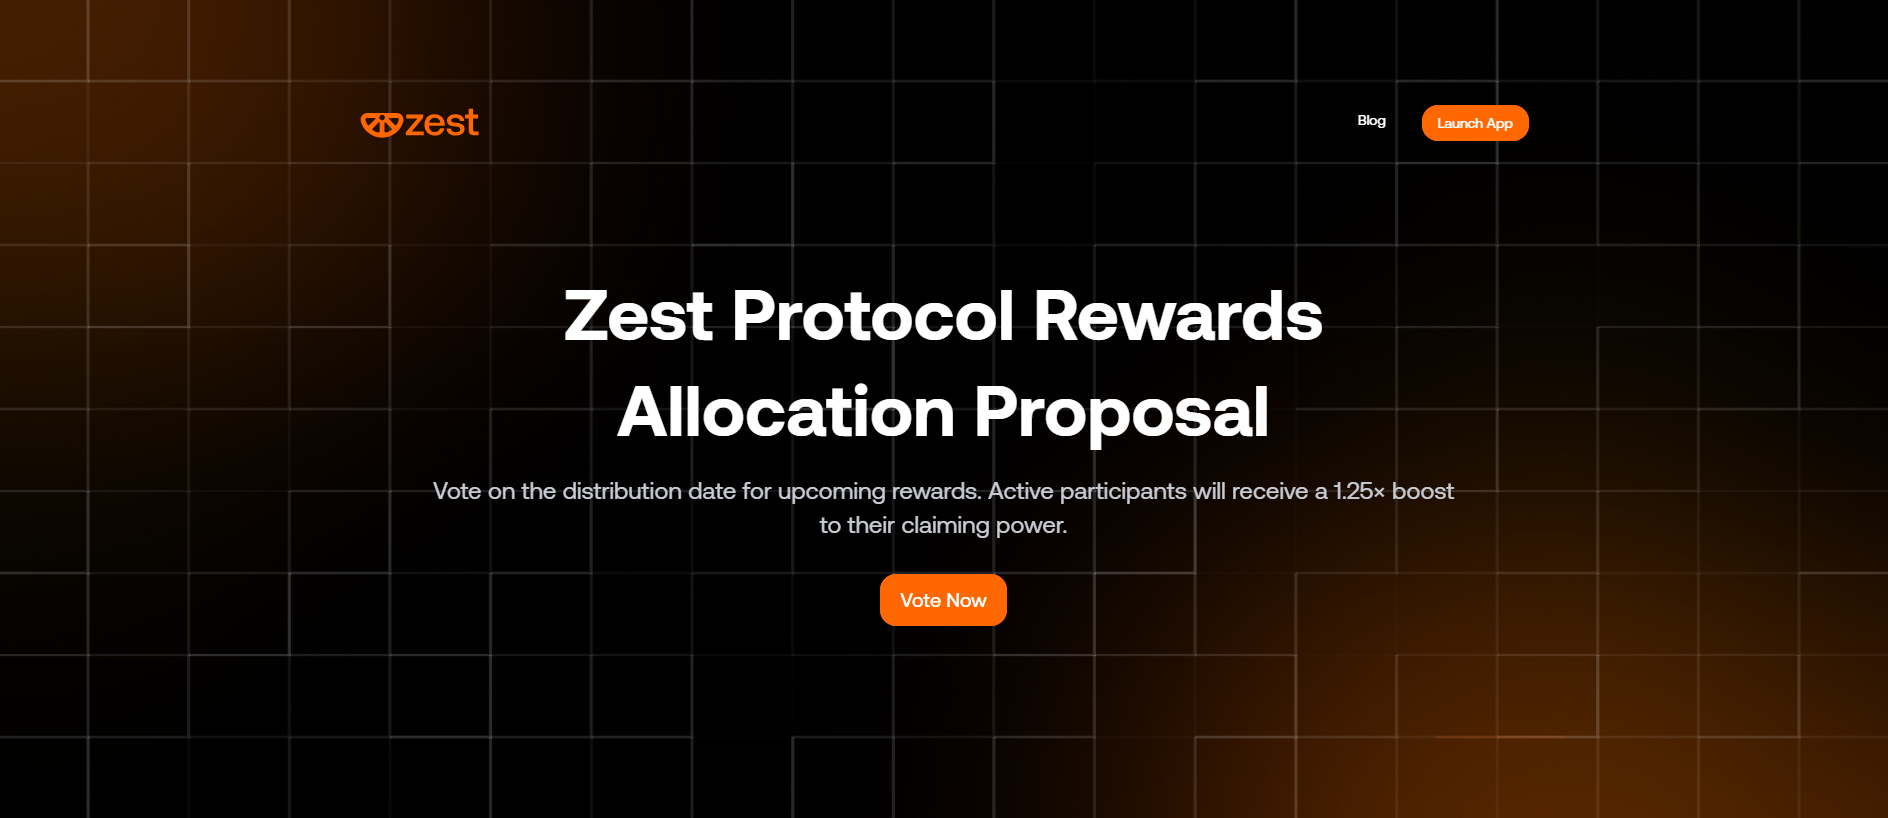
Zest Protocol | The Bitcoin liquidity protocol
Impersonates
Discord
TLS Certificate
Hostname coverage not recorded · Issued by Let's Encrypt / YE1 · stored validity ends in 84 days

Domain details

Domain
URLScan Verdict Analysis completed score 0 report ↗
IP Context Cloudflare shared edge origin IP hidden Edge-IP reputation is not attributed to this domain.
OTX Tags 2026-10all-domainsblocklistcryptodomainsdrainerfraudlivemonthlyphishdestroyphishingscam
Registrar Spaceship US(US)
RegistrationCreated Oct 6, 2026 (5d · Brand New!) — Expires Oct 6, 2027
Technical detailsProvenance & timestamps
First DetectedOct 7, 2026
DOM Analysisanalyzed Oct 9, 2026score 98/1001 brand signal
Submitted URLhttp://zestprotocol.forum/
Favicon Hash
Case ID
ICANN OVERSIGHT

Accreditation and RAA context

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft Nothing is sent automatically.

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
188.114.96.3
Network ASN
AS13335
Organization
Cloudflare, Inc.
Observed location
San Francisco, US
Server header
cloudflare

Edge-IP reputation is not attributed to this domain.

Nameservers 2

  • ashley.ns.cloudflare.com
  • evan.ns.cloudflare.com

Location describes the IP network.

TLS certificate

Issuer
Let's Encrypt / YE1
Valid from
2026-10-06 12:24:21
Valid until
2027-01-04 12:24:20
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-11 16:03:25 UTC
Collection source
PhishDestroy collector
Certificate fingerprint986353248d791766a7e175bb4b2112fcc92ed78e3fee0e1f61d1255d8f83bb0e

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 188.114.96.3rapiddns.io

Latest Classified Outcome 2026-10-10 20:20:48 UTC

Primary outcome DNS inactive reason: DNS NXDOMAIN 80% confidence
Attribution source: Dns Cache
Evidence layers Availability: DNS inactive Content: Unreachable DNS: NXDOMAIN Registration: Unknown
Latest HTTP observation Unknown Probe Inconclusive 20% 2026-10-11 10:29:20 UTC
RDAP registration Unknown
Observed timeline last reachable: 2026-10-09 22:30:50 UTC last content: 2026-10-09 22:30:50 UTC current episode first observed: 2026-10-10 20:20:48 UTC observed RIP window: 2026-10-09 22:30:50 UTC → 2026-10-10 20:20:48 UTC · 21.83h midpoint estimate ≈ 2026-10-10 09:25:49 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Technologies · 4 identified
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain Submit evidence & help protect others

VirusTotal Analysis

9 / 92 security vendors flagged this domain
View on VT
Last analyzed First positive detection Previous stored snapshot: 3 detections
alphaMountain.ai
BitDefender
CRDF
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
SOCRadar
Site Performance Analysis

Google PageSpeed Insights — mobile performance audit of zestprotocol.forum · checked Oct 7, 2026

73
Needs Work
Performance
FCP
1.95s
First Contentful Paint
LCP
9.03s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
2.63s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-07 10:49:51 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 188.114.96.3.

Threat Response Pipeline

Discovery
Analysis
Notifications
Monitoring

11 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Threat Ingested
zestprotocol.forum detected and queued for full analysis
Oct 7, 2026
URLScan.io Capture
Stored URLScan report with capture artifacts
Oct 7, 2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
9/92 recorded on VirusTotal
Oct 11, 2026
Blocklist Detection
Found in 2 blocklists: MetaMask, SEAL
Oct 11, 2026
OTX Community References
3 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
Oct 7, 2026
Brand Impersonation
Impersonation of Sei
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
Oct 7, 2026
Technical Analysis Recorded
The report contains stored technology or forensic-analysis results.
Oct 11, 2026
Sent Report Recorded
Stored outgoing record associated with registrar Spaceship, Inc., 1 abuse contact
abuse@spaceship.com
Oct 7, 2026
DestroyList Published
Oct 7, 2026
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Public Blocklist Status

Evidence & External Reports

Submitted Evidence Snapshot
Sent: Ledger records: 1 Case ID: PD-20261007-29B0CD Recipient: abuse@spaceship.com
Page title stored with report: Zest Protocol | The Bitcoin liquidity protocol
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 443.9 KB
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Deep Analysis

Were You Affected by This Site?

6 evidence signal groups linked 1 reports recorded Unverified
If credentials were compromised, report immediately. Do not engage with recovery scammers.

If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Europol
Find the official reporting channel for your EU country
National police directory
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

97-country directory

Template-based draft · optional AI wording assistance requires separate consent

Template-based draft • optional AI wording assistance requires separate consent · Review and submit it yourself

Check Any Domain

Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence

Scan Now

Report Phishing

Submit suspicious domains to our threat database — protect the community

Report

Live Threat Feed

Recent phishing reports and observed availability changes

Monitor

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive
Live Threat Feed Appeal This Listing
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/zestprotocol.forum"
  title="PhishDestroy threat report for zestprotocol.forum"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>