



Domain security and threat intelligence

www-kapiital.click
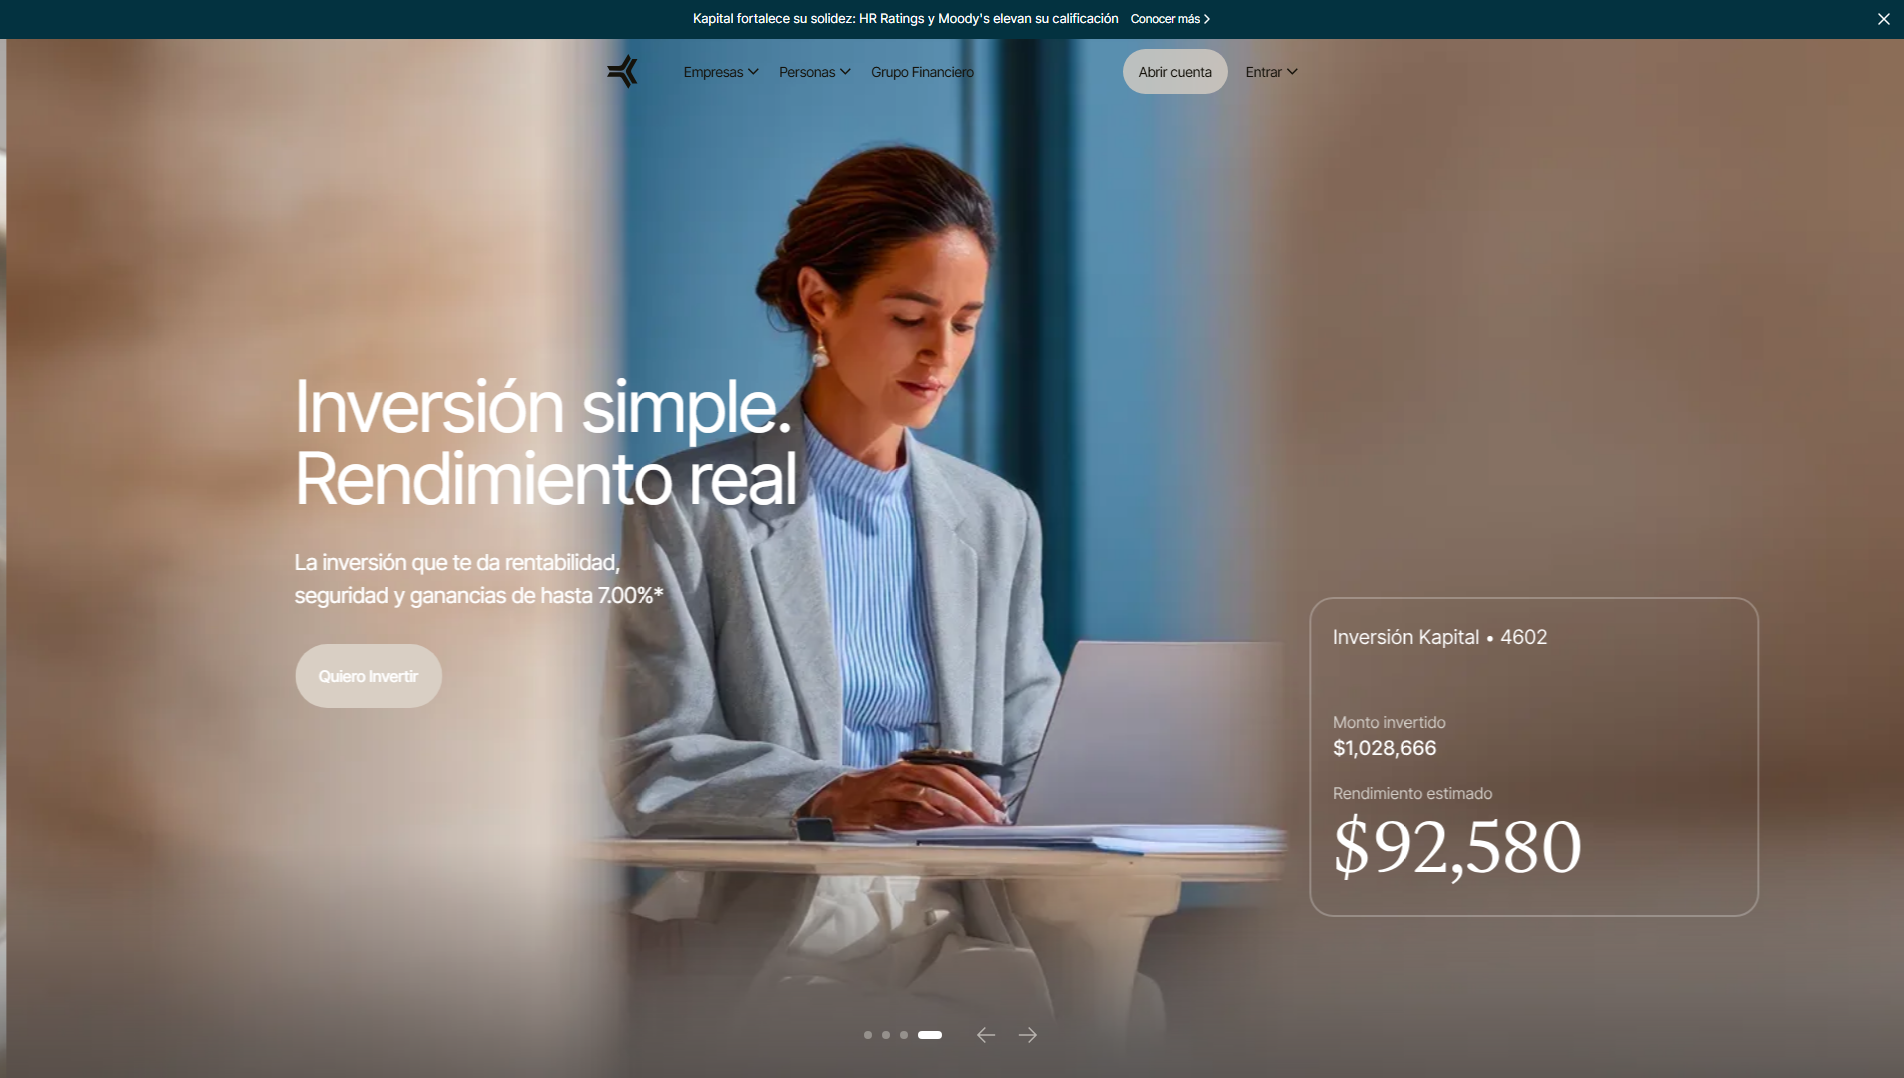
“Kapital: Soluciones financieras para empresas y personas | México”
Threat verdict
Critical
73/100 evidence score
Availability
Content unavailable
Content was unavailable in the latest observation
Risk signals
VirusTotal detections: 6/91
Spamhaus DBL: DBL_PHISH
Brand impersonation: Unknown
Actions
API
Evidence Summary
CRITICAL
PhishDestroy first observed www-kapiital.click on Aug 25, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “Kapital: Soluciones financieras para empresas y personas | México”. Stored page analysis classifies the content as impersonation. Current evidence score: 73/100 (critical).
Positive findings are stored from 2 sources: VirusTotal and Spamhaus DBL. VirusTotal recorded 6 detections among 91 engines: alphaMountain.ai, ESET, Forcepoint ThreatSeeker, Gridinsoft, LevelBlue, SOCRadar on Aug 31, 2026 at 02:07 UTC. Spamhaus DBL: DBL_PHISH on Aug 25, 2026 at 18:30 UTC. Non-positive and contextual checks: On Aug 30, 2026 at 01:47 UTC, AlienVault OTX listed 4 community pulse references (not vendor detections); Google Safe Browsing returned no flag. The separate external-blocklist snapshot contained no matches on Sep 29, 2026 at 10:20 UTC. URLQuery recorded no positive detection on Aug 25, 2026 at 18:19 UTC. URLScan completed without a malicious verdict (score 0) on Aug 25, 2026 at 23:08 UTC.
No conclusive timestamped HTTP response is stored. Registration records for the domain list Atak Domain Bilgi Teknolojileri AS as the registrar and Jul 15, 2026 as the creation date. At collection time, the hostname resolved to 85.121.177.90 on AS200019 (ALEXHOST SRL). The recorded endpoint location is Frankfurt am Main, DE. The stored server header is Apache/2.4.58 (Ubuntu). The evidence archive retains 3 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists Let's Encrypt / YE1 as the certificate issuer with validity through Nov 22, 2026; checked Aug 25, 2026 at 19:02 UTC.
The content indicators and 2 positive source findings support the current Unknown-themed impersonation classification.
VirusTotal
6 det.
OTX references
URLScan
TLS Certificate
Expired or unverified
Age
3 mo New
Observed status
Content unavailable
DestroyList
Listed
Reports Sent
1
Data coverage
VirusTotal
6 / 91
URLQuery
checked — no detections recorded
OTX
4 community references
CF Radar
scan completed
URLScan capture
stored report
URLScan verdict
Analysis completed
TLS
Expired or unverified
WHOIS
3 mo old
Screenshot
3 captures · 3 sources
Network Security Intelligence
SSL Certificate
Invalid
SSL certificate is invalid or expired. Issuer:
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Domain Status Transition Sep 10, 2026 · 12:00 UTCDomain state transitioned from alive to dead.
-
VirusTotal Detections Update Aug 27, 2026 · 00:15 UTCVirusTotal scanner detections updated from 1 to 3. Added scanner alerts: Gridinsoft, alphaMountain.ai.
-
VirusTotal Detections Update Aug 26, 2026 · 00:17 UTCVirusTotal scanner detections updated from 0 to 1. Added scanner alerts: SOCRadar.
-
Threat First Observed Aug 25, 2026 · 20:14 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
85.121.177.90.
Threat Response Pipeline
Discovery
Checks
Reports
Availability
17/17
Sent Report Recorded
Stored sent-report record for registrar Atak Domain Bilgi Teknolojileri AS, hosting provider, 2 abuse contacts
byazici@atakteknoloji.comabuse-alexhost@rnc.ro
Public Blocklist Status
Detection-evasion analysis
Cloaking and traffic-distribution check
Not yet scanned
No crawler-versus-browser difference has been recorded yet
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
- Last cloaking scan
Scanner note: dns_error: raw=dns_error; via=local_dns_prefilter
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this panel is open.
Waiting
Stored Capture · 3 sources
Domain Intelligence
Domain
URLScan Verdict
Analysis completed
score 0 report ↗
Server / ASN
Apache/2.4.58 (Ubuntu) · AS200019 ALEXHOST SRL
IP Reputation
abuse score 0/100 0 reports checked Aug 25, 2026
OTX Tags
2026-08activeall-domainsblocklistcontentcryptodomainsdrainerfraudlivemonthlyphishdestroyphishingscam
Registrar
Atak Domain Bilgi Tekn…
 (TR)
(TR)
RegistrationCreated Jul 15, 2026 (75d · New) — Expires Jul 15, 2027
Technical detailsDNS, SSL SANs, timestamps
First DetectedAug 25, 2026
IoC Extraction
Submitted URLhttps://www-kapiital.click/BN/
Nameserverseu.atakdomain.comtr.atakdomain.com
TLS Fingerprint
TLS Observation
Case ID
ICANN OVERSIGHT
Accreditation and RAA context
Accreditation and RAA context
Registrar accreditation and DNS abuse obligations
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Accreditation is a contract, not a safety seal.
Verify ICANN fees
Read RAA §3.18
PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
Technologies · 2 identified
Ubuntu
Operating systems
Apache HTTP Server
Web servers
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain
Submit evidence & help protect others
VirusTotal Analysis
6 / 91 security vendors flagged this domain
View on VT
Last analyzed First positive detection Previous stored snapshot: 3 detections
alphaMountain.ai
ESET
Forcepoint ThreatSeeker
Gridinsoft
LevelBlue
SOCRadar
Site Performance Analysis
Google PageSpeed Insights — mobile performance audit of www-kapiital.click · checked Aug 25, 2026
100
Good
Performance
FCP
0.78s
First Contentful Paint
LCP
0.78s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
1.62s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Evidence & External Reports
Security Analysis
Submitted Evidence Snapshot
Sent: Ledger records: 1
Case ID:
PD-20260825-3203A2 Recipient: byazici@atakteknoloji.com
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
OSINT & Intelligence
DNS & Network
SEO & Domain
Were You Affected by This Site?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Action Fraud
Report fraud and cybercrime in England, Wales and Northern Ireland
Contact centre0300 123 2040
PhishDestroy listing review Not a law-enforcement report
Domain Appeal
Request a review if you own this domain and believe the listing is incorrect
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
Report to Your Local Authorities
Select your country to get official cybercrime contacts, or create a complaint draft →.
97-country directory
Template-based draft • optional AI wording assistance requires separate consent
Review and submit it yourself
Related Infrastructure & Reports
- Direct link Shares a registration or an identical phishing kit.
- Supporting signal Shares infrastructure or a target brand; not proof of one operator.
- Discovery only Listed for navigation; no shared attribute with this host.
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Unknown impersonation 8
These domains also target Unknown users. View all Unknown threats →
Same registrar: Atak Domain Bilgi Tekn… 6
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.

Recent threat reports 6
Recently added threat reports.
Check Any Domain
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowReport Phishing
Submit suspicious domains to our threat database — protect the community
ReportLive Threat Feed
Recent phishing reports and observed availability changes
MonitorStay Informed, Stay Safe
Monitor live threats or contest this listing if you believe it's a false positive