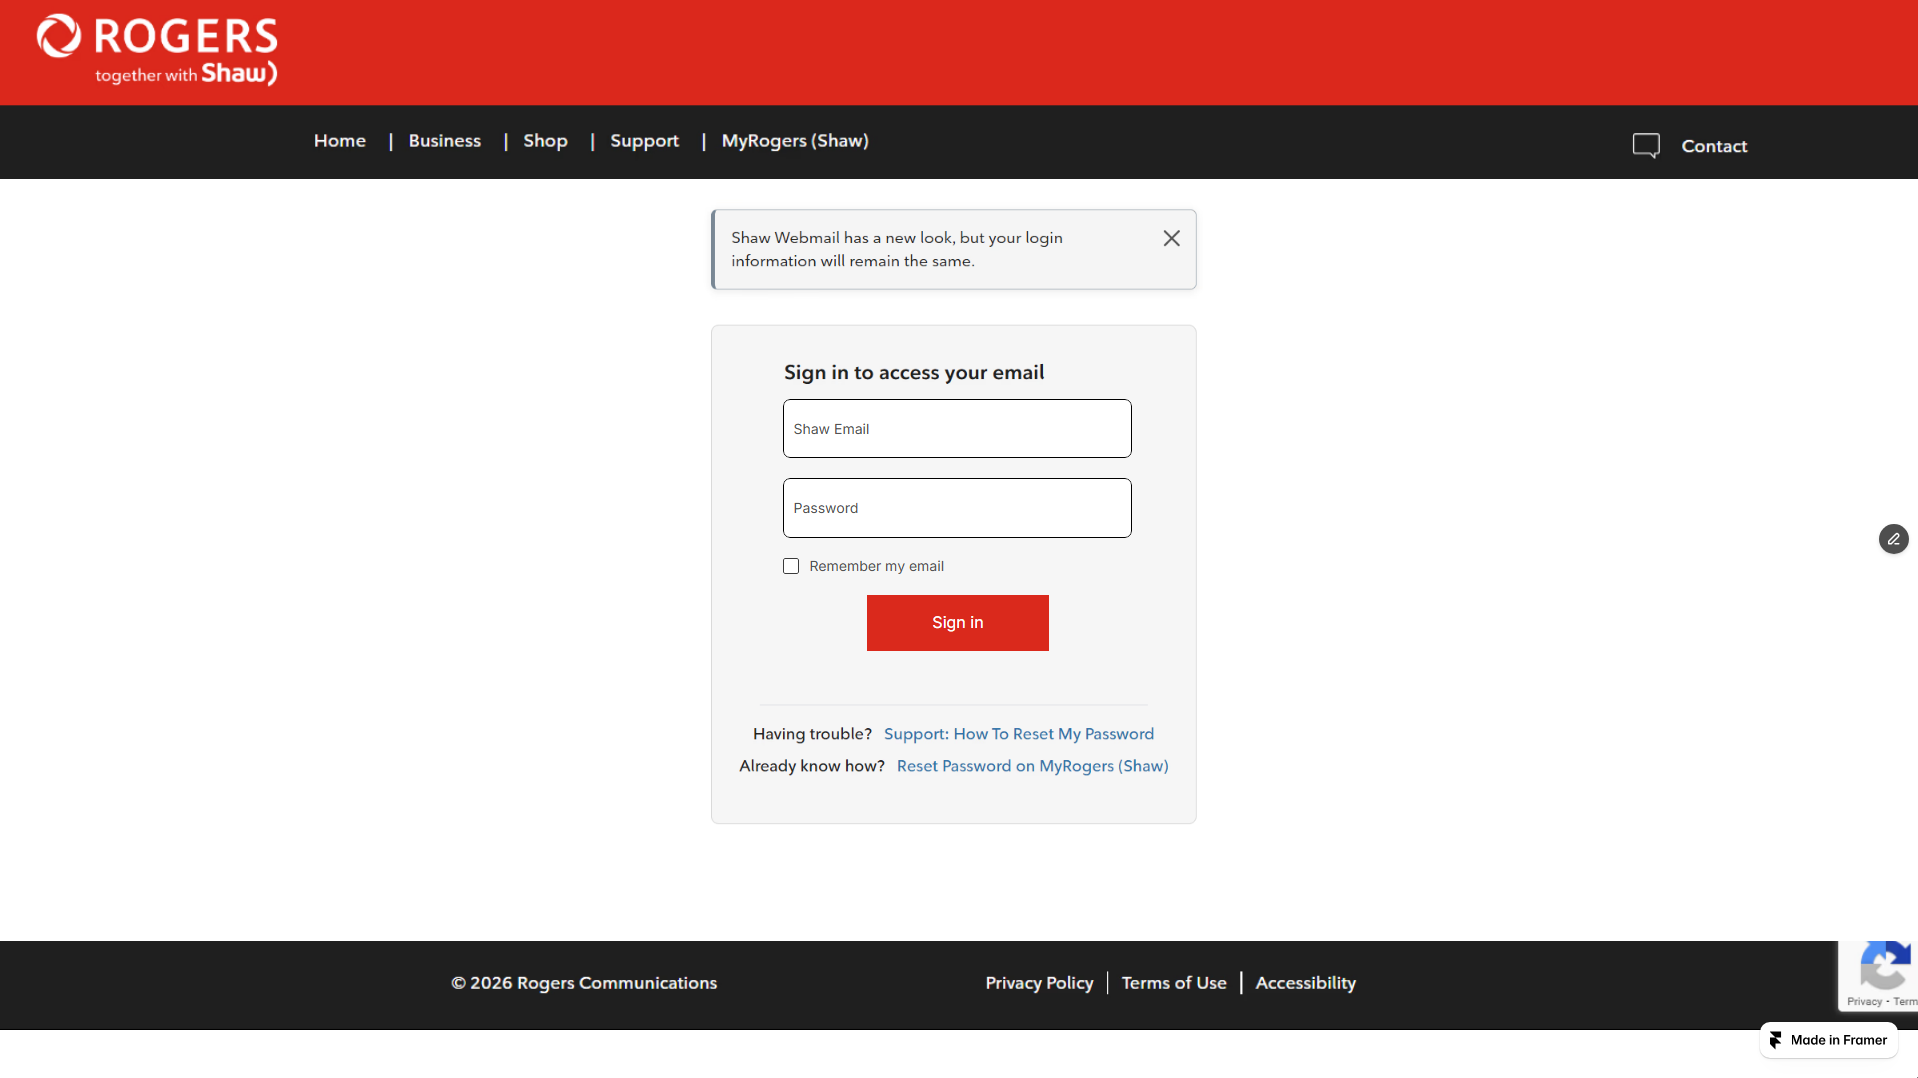
http://winj.life/HTTP 200
1.3 KB
638 B
0 internal · 0 external
Content-Type: text/html; charset=utf-8Server: CaddyAll stored response-header names (8)
Accept-RangesContent-LengthContent-TypeEtagLast-ModifiedServerVaryDate“Sign in . Rogers together with Shaw”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse-trusted.savcom@in.wixanswers.com.
The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
The domain winj.life was registered through Sav.com, LLC on 2026-01-06 and is currently resolving to the IPv4 address 102.220.160.203.
The detailed PhishDestroy AI analysis below remains in English to preserve the original forensic record.
The domain winj.life was registered through Sav.com, LLC on 2026-01-06 and is currently resolving to the IPv4 address 102.220.160.203. DNS resolution is serviced by Cloudflare nameservers cris.ns.cloudflare.com and rayne.ns.cloudflare.com, indicating the use of Cloudflare’s DNS and potentially its CDN or WAF services. The domain remains active as of the report date (2026-07-29) and has been flagged by multiple security services. VirusTotal records show that 6 of 91 scanning engines have generated a malicious classification for winj.life, reflecting a modest but non‑trivial detection rate.
The domain also appears on a single external security blocklist and is listed as blocked by the PhishDestroy mitigation platform, further corroborating its abusive nature. No public evidence has been released regarding the site’s SSL certificate, HTTP response codes, page title, or the specific brand or service being impersonated; those elements remain unverified. The limited detection footprint suggests the site may be newly deployed or employing evasive techniques to avoid broader detection. Nonetheless, the combination of an active Cloudflare‑backed infrastructure, a recent registration date, and multiple independent detections meets the criteria for a high‑risk phishing indicator.
Defenders should add winj.life to local blocklists, enforce DNS sinkholing where possible, and monitor outbound traffic for connections to 102.220.160.203. Continuous re‑scanning on VirusTotal or similar platforms is advised to capture any changes in detection ratios. Organizations using threat‑intelligence feeds that incorporate PhishDestroy or Cloudflare‑based blocklists will already receive alerts for this indicator. Given the current evidence, the domain should be treated as a confirmed phishing infrastructure and mitigated accordingly.
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| DigiCert UltraDNS | winj.life |
malicious | Sinkholed |
| Cloudflare DNS | winj.life |
malicious | Sinkholed |
| OpenDNS | winj.life |
phishing | Phishing Block |
| Cloudflare DNS | shaggy-tenets-541262.framer.app |
malicious | Sinkholed |
| OpenDNS | shaggy-tenets-541262.framer.app |
phishing | Phishing Block |
102.220.160.203.
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Framer is a no-code web design platform for designing and publishing responsive websites.
www.framer.com 100% confidenceReact is an open-source JavaScript library for building user interfaces or UI components.
reactjs.org 100% confidenceHTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
www.rfc-editor.org 100% confidenceHTTP/3 is the third major version of the Hypertext Transfer Protocol used to exchange information on the World Wide Web.
httpwg.org 100% confidenceGoogle PageSpeed Insights — mobile performance audit of winj.life · checked Jul 29, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
http://winj.life/Content-Type: text/html; charset=utf-8Server: CaddyAccept-RangesContent-LengthContent-TypeEtagLast-ModifiedServerVaryDatePD-20260729-877FA3 Recipient: abuse-trusted.savcom@in.wixanswers.com If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.
Select your country to get official cybercrime contacts, or create a complaint draft →.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive