URLQuery
2 det.
Report
“App”
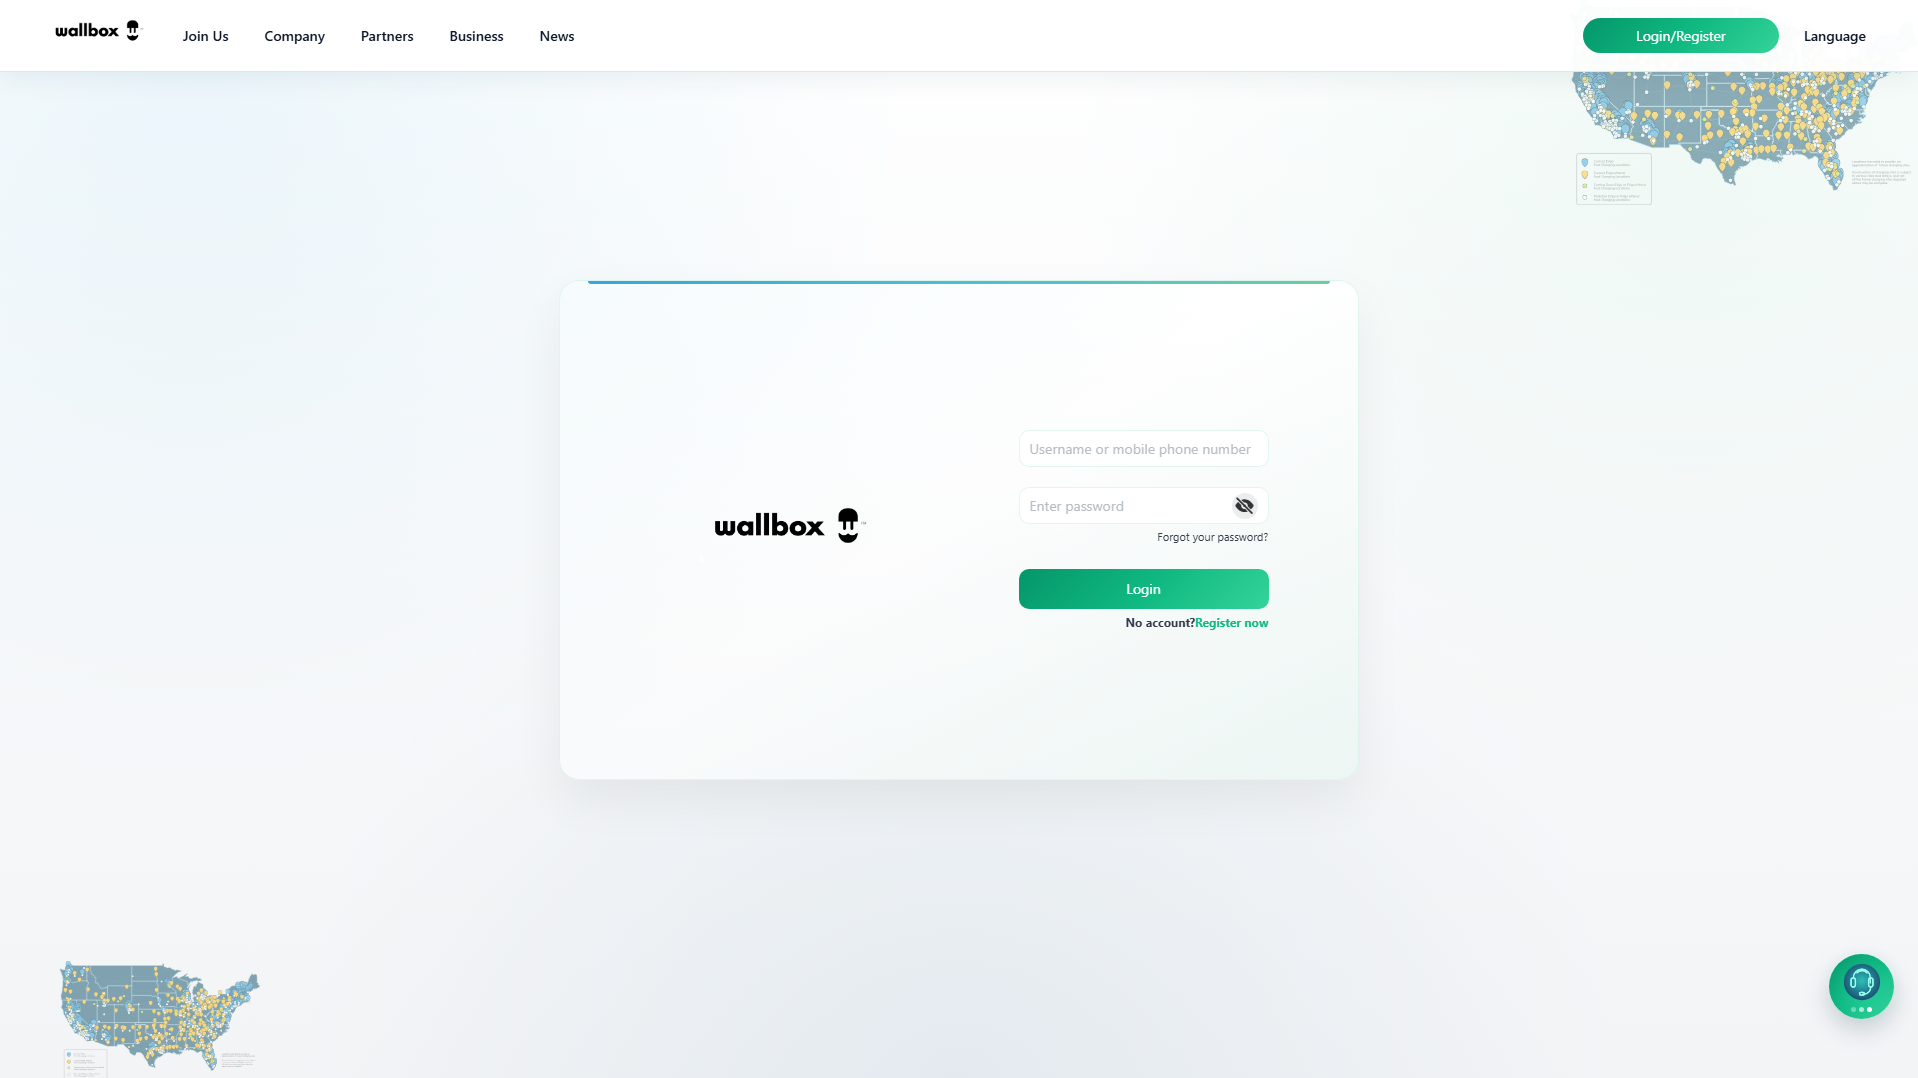
PhishDestroy first observed wallbox-charging.top on Oct 4, 2026. The captured page title is “App”. Current evidence score: 66/100 (high).
Positive findings are stored from 3 sources: MetaMask, SEAL, and URLQuery. MetaMask and SEAL listed the hostname in the separate external-blocklist snapshot on Oct 4, 2026 at 06:20 UTC. URLQuery recorded 2 detections; no observation timestamp was retained. Additional recorded evidence: URLScan captured the page on Oct 4, 2026 at 05:37 UTC.
The collector marked the hostname reachable on Oct 4, 2026 at 05:37 UTC, but did not retain the HTTP response code. Latest classified outcome: unknown; cause probe inconclusive on Oct 4, 2026 at 03:37 UTC. Registration records for the domain list NameMart Pte. Ltd. as the registrar and Sep 23, 2026 as the creation date. Registration preceded first observation by 10 days. At collection time, the hostname resolved to 104.21.9.27. The IP and ASN identify shared Cloudflare edge infrastructure; the origin server is not established by this address. The evidence archive retains 2 visual captures from PhishDestroy and URLScan. TLS metadata lists Let's Encrypt / YE1 as the certificate issuer with validity through Dec 22, 2026; checked Oct 4, 2026 at 07:02 UTC.
The content indicators and 3 positive source findings support the current phishing classification.
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
 (SE)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Edge-IP reputation is not attributed to this domain.
eloise.ns.cloudflare.comsid.ns.cloudflare.comLocation describes the IP network.
ec7e659579b9c78ca7958c5929807e0f3ab95a886f5215c82ade542c4cdcb6deSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
104.21.9.27. 7 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
PD-20261004-972AD4 Recipient: abuse@namemart.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Shared edge IP; unrelated tenants may be present.
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive