



Domain security and threat intelligence

trezor-help.support
“Trezor Wallet Recovery”
Threat verdict
Critical
100/100 evidence score
Availability
Content unavailable
Content was unavailable in the latest observation
Risk signals
VirusTotal detections: 21/91
Stored blocklist matches: 2
URLQuery threat systems: 6 alerts
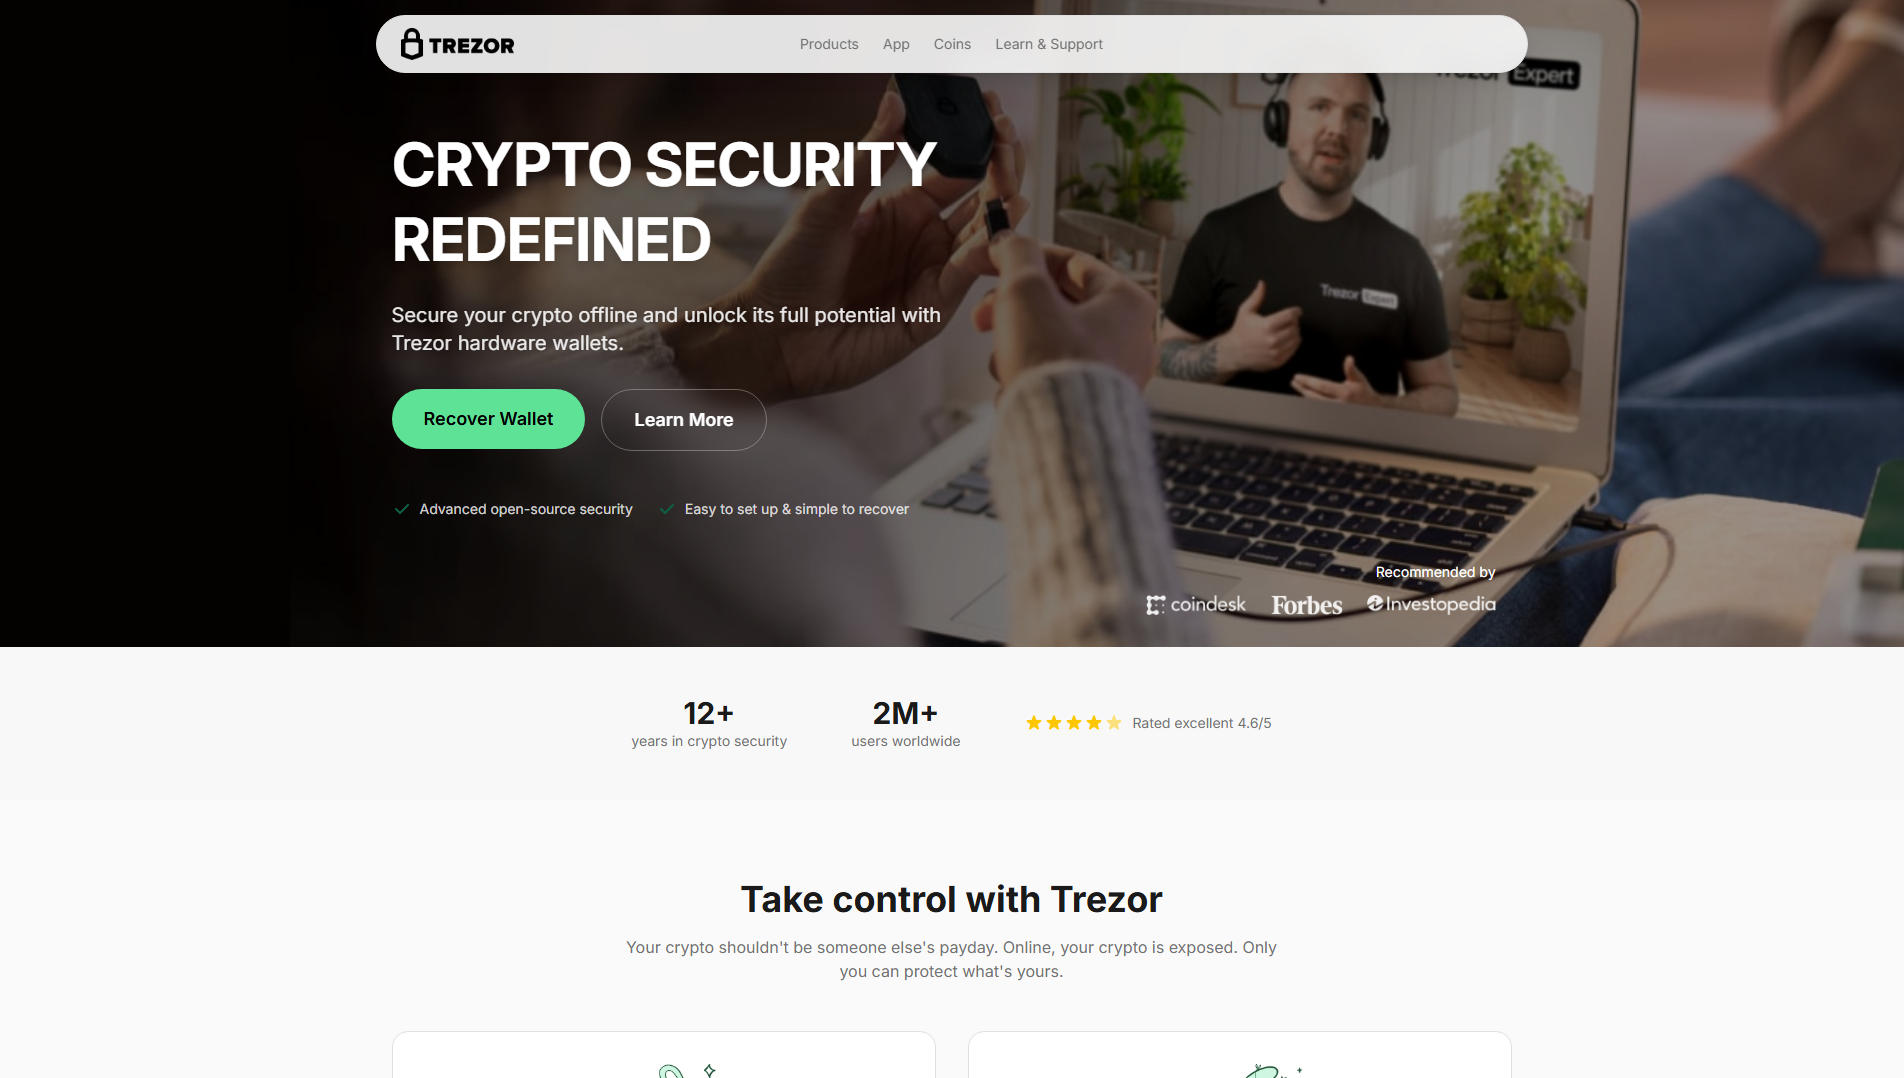
Brand impersonation: Trezor
Actions
API
Report overview
trezor-help.support is an active brand impersonation scam targeting Trezor users. Flagged by 22/95 VirusTotal vendors as a crypto drainer threat, this domain.
The detailed PhishDestroy AI analysis below remains in English to preserve the original forensic record.
Evidence Summary
CRITICAL
The domain trezor-help.support is currently active and operates as a brand impersonation scam specifically targeting Trezor, a well-known cryptocurrency hardware wallet provider. Analysis confirms this domain is designed to deceive users into entering sensitive wallet recovery information, likely functioning as a crypto drainer to siphon digital assets from victims. The site remains operational despite multiple security detections, posing a high-risk threat to unsuspecting users seeking wallet recovery services. Infrastructure analysis reveals the domain was registered on June 15, 2026, through Name.com, Inc., an uncommon future registration date that may indicate an attempt to evade immediate detection. The domain resolves to IP address 34.111.179.208 and uses an SSL certificate issued by Let's Encrypt (identifier E7), providing a false sense of security. Security vendors have flagged this domain in 22 of 95 VirusTotal scans, with active blocks implemented by PhishDestroy, MetaMask, and SEAL. The domain appears on three distinct security blocklists, and its page title, 'Trezor Wallet Recovery,' directly mimics official Trezor support pages to enhance credibility. Current threat status remains active, with no indications of takedown or mitigation. Users are strongly advised to avoid interacting with this domain and any associated pages. Trezor wallet holders should exclusively use the official support channels verified through the legitimate Trezor website. Security teams are recommended to update blocklists with the domain and IP address, monitor for similar impersonation attempts, and educate users on verifying domain authenticity before entering sensitive wallet information. The combination of brand impersonation, active security flags, and direct targeting of cryptocurrency recovery processes underscores the critical need for heightened vigilance in this threat landscape.
VirusTotal
21 det.
URLQuery
6 threat alerts
OTX references
CF Radar
Malicious
URLScan
TLS Certificate
Expired or unverified -51d
Age
3 mo
Observed status
Content unavailable 404
DestroyList
Listed
Reports Sent
1
Data coverage
VirusTotal
21 / 91
URLQuery
6 threat-system alerts
OTX
2 community references
CF Radar
provider verdict: malicious
URLScan capture
stored report
URLScan verdict
malicious
TLS
Expired or unverified
WHOIS
3 mo old
Screenshot
3 captures · 3 sources
Network Security Intelligence
Threat Detection Systems
6 alerts
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | trezor-help.support |
malicious | Sinkholed |
| OpenDNS | trezor-help.support |
phishing | Phishing Block |
| DigiCert UltraDNS | trezor-help.support |
malicious | Sinkholed |
| Hagezi Threat Feed | trezor-help.support |
malicious | Sinkholed |
| DNS4EU | trezor-help.support |
malicious | Sinkholed |
| Quad9 DNS | trezor-help.support |
malicious | Sinkholed |
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Cloudflare Radar Scan Jun 26, 2026 · 05:35 UTCCloudflare Radar scan registered: View Radar report.
Threat Response Pipeline
Discovery
Checks
Reports
Availability
17/17
Sent Report Recorded
Stored sent-report record for registrar Name.com, Inc., hosting provider, 1 abuse contact
abuse@name.com
Public Blocklist Status
Detection-evasion analysis
Cloaking suspected: scanner and visitor titles differ
Not observed
No cloaking was observed in the stored scan
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not observed
- Cloaking score
- 0/6
- Last cloaking scan
Scanner note: dead_http: raw=http_404; http=404; via=https_proxy
Title shown to the security scannerThis app isn't live yet
Title shown to a browser visitorTrezor Wallet Recovery
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this panel is open.
Waiting
Stored Capture · 3 sources
Domain Intelligence
Domain
URLScan Verdict
Malicious
score 100 Phishing brand: Trezor report ↗
Server / ASN
Google Frontend · AS396982 Google LLC
IP Reputation
abuse score 36/100 73 reports Fraud OrdersDDoS AttackPhishingOpen ProxyEmail SpamPort ScanBad Web Bot checked Aug 26, 2026
OTX Tags
2026-06all-domainscryptodomainslivemonthlyphishdestroyphishingscam
Registrar
Name.com
 (SE)
(SE)
IP Address
34.111.179.208

RegistrationCreated Jun 15, 2026 (104d) — Expires Feb 24, 2027
HTTP Status404 Not Found
Technical detailsDNS, SSL SANs, timestamps
First DetectedJun 15, 2026
IoC Extraction
Submitted URLhttp://trezor-help.support/
Nameserversns1cny.name.com
TLS Fingerprint
TLS Observation
Favicon Hash
Case ID
ICANN OVERSIGHT
Accreditation and RAA context
Accreditation and RAA context
Registrar accreditation and DNS abuse obligations
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Accreditation is a contract, not a safety seal.
Verify ICANN fees
Read RAA §3.18
PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
Technologies · 7 identified
Node.js
Programming languages
Google Cloud
IaaS
Express
Web frameworks
Web servers
HSTS
Security
Google Cloud Trace
Performance
Google Cloud CDN
CDN
HTTP/3
Miscellaneous
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain
Submit evidence & help protect others
VirusTotal Analysis
21 / 91 security vendors flagged this domain
View on VT
Last analyzed Previous stored snapshot: 22 detections
ADMINUSLabs
ChainPatrol
Criminal IP
alphaMountain.ai
BitDefender
Chong Lua Dao
Cluster25
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
LevelBlue
Lionic
Seclookup
SOCRadar
Sophos
VIPRE
Webroot
Lookalike domains
74 stored lookalike domains
treaor.io
replacement Internal report
treozr.io
transposition Internal report
trzezor.io
insertion Internal report
trzor.io
omission Internal report
rtrezor.io
insertion Internal report
terezor.io
insertion Internal report
trazor.io
bitsquatting Internal report
trexzor.io
insertion Internal report
trezort.io
addition Internal report
5rezor.io
replacement
6rezor.io
replacement
frezor.io
replacement
Show all (62)
grezor.io
replacement
rezor.io
omission
rrezor.io
replacement
rtezor.io
transposition
tdezor.io
replacement
teezor.io
replacement
terzor.io
transposition
tezor.io
omission
tfezor.io
replacement
tr.ezor.io
subdomain
tr3zor.io
replacement
treeor.io
replacement
treezor.io
insertion
treor.io
omission
treqor.io
replacement
tresor.io
replacement
trezeor.io
insertion
trezer.io
vowel-swap
trezior.io
insertion
trezir.io
replacement
trezkor.io
insertion
trezlor.io
insertion
trezo.io
omission
trezoe.io
replacement
trezoir.io
insertion
trezopr.io
insertion
trezor-io.com
various
trezorio.com
various
trezot.io
replacement
trezpor.io
insertion
trezpr.io
replacement
trezr.io
omission
trezro.io
transposition
trezxor.io
insertion
trezzor.io
insertion
trizor.io
vowel-swap
trozor.io
vowel-swap
trrzor.io
replacement
trtezor.io
insertion
trwezor.io
insertion
trwzor.io
replacement
trzeor.io
transposition
trzzor.io
replacement
ttezor.io
replacement
ttrezor.io
insertion
tyrezor.io
insertion
yrezor.io
replacement
ytrezor.io
insertion
prezor.io
bitsquatting
treazor.io
insertion
trerzor.io
insertion
trewzor.io
insertion
trexor.io
bitsquatting
trez0r.io
homoglyph
trezaor.io
insertion
trezora.io
addition
trezore.io
addition
trezoro.io
addition
trezorr.io
addition
trezors.io
addition
xn--tezor-5bb.io
homoglyph
xn--trezo-9bb.io
homoglyph
Community intelligence
1 community report
CategoryIMPERSONATION
The domain is a live, recently registered site that presents itself as Trezor and uses wallet-recovery language aimed at crypto users. The page includes calls to recover a wallet using a recovery phrase, which is consistent with seed-phrase harvesting and phishing behavior rather
Community reports
Reported by 1 community member, first seen Jun 15, 2026
- Stored reports
- 1
- Unique reported URLs
- 1
Accepted1
Evidence & External Reports
Security Analysis
Community Scam Report — ChainAbuse
1 report filed for trezor-help.support (1 written by a person) · category: Impersonation · source checked
“The domain is a live, recently registered site that presents itself as Trezor and uses wallet-recovery language aimed at crypto users. The page includes calls to recover a wallet using a recovery phrase, which is consistent with seed-phrase harvesting and phishing behavior rather than legitimate support content. The domain is independently registered and hosted, so removal of the hosted content plus registrar suspension is warranted; internal blocklisting is also appropriate to reduce exposure w”
— reported by Anonymous Trusted reporter on May 12, 2026 · Source: ChainAbuse (TRM Labs) — full report and evidence there.
Submitted Evidence Snapshot
Sent: Ledger records: 1
Case ID:
PD-20260617-C4F1EA Recipient: abuse@name.com Page title stored with report: Problem loading page
Blocklist hits included with submission: MetaMask, SEAL
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
OSINT & Intelligence
DNS & Network
SEO & Domain
Were You Affected by This Site?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Action Fraud
Report fraud and cybercrime in England, Wales and Northern Ireland
Contact centre0300 123 2040
PhishDestroy listing review Not a law-enforcement report
Domain Appeal
Request a review if you own this domain and believe the listing is incorrect
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
Report to Your Local Authorities
Select your country to get official cybercrime contacts, or create a complaint draft →.
97-country directory
Template-based draft • optional AI wording assistance requires separate consent
Review and submit it yourself
Related Infrastructure & Reports
- Direct link Shares a registration or an identical phishing kit.
- Supporting signal Shares infrastructure or a target brand; not proof of one operator.
- Discovery only Listed for navigation; no shared attribute with this host.
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Recovery Scam kit 8
Part of the Recovery Scam phishing campaign. View all campaign domains →

Shared IP 34.111.179.208 6
Multiple reports share this IP.


Trezor impersonation 8
These domains also target Trezor users. View all Trezor threats →


Same registrar: Name.com 6
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.


Recent threat reports 6
Recently added threat reports.


Check Any Domain
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowReport Phishing
Submit suspicious domains to our threat database — protect the community
ReportLive Threat Feed
Recent phishing reports and observed availability changes
MonitorStay Informed, Stay Safe
Monitor live threats or contest this listing if you believe it's a false positive