




Domain security and threat intelligence

start-live-io.created.app
“Ledger Live App® | #1 Official Ledger Mobile & Desktop”
Threat verdict
Critical
100/100 evidence score
Availability
Last known active
Latest stored reachability observation
Risk signals
VirusTotal detections: 15/89
Stored blocklist matches: 2
Brand impersonation: Ledger
Last known active
Actions
API
Evidence Summary
CRITICAL
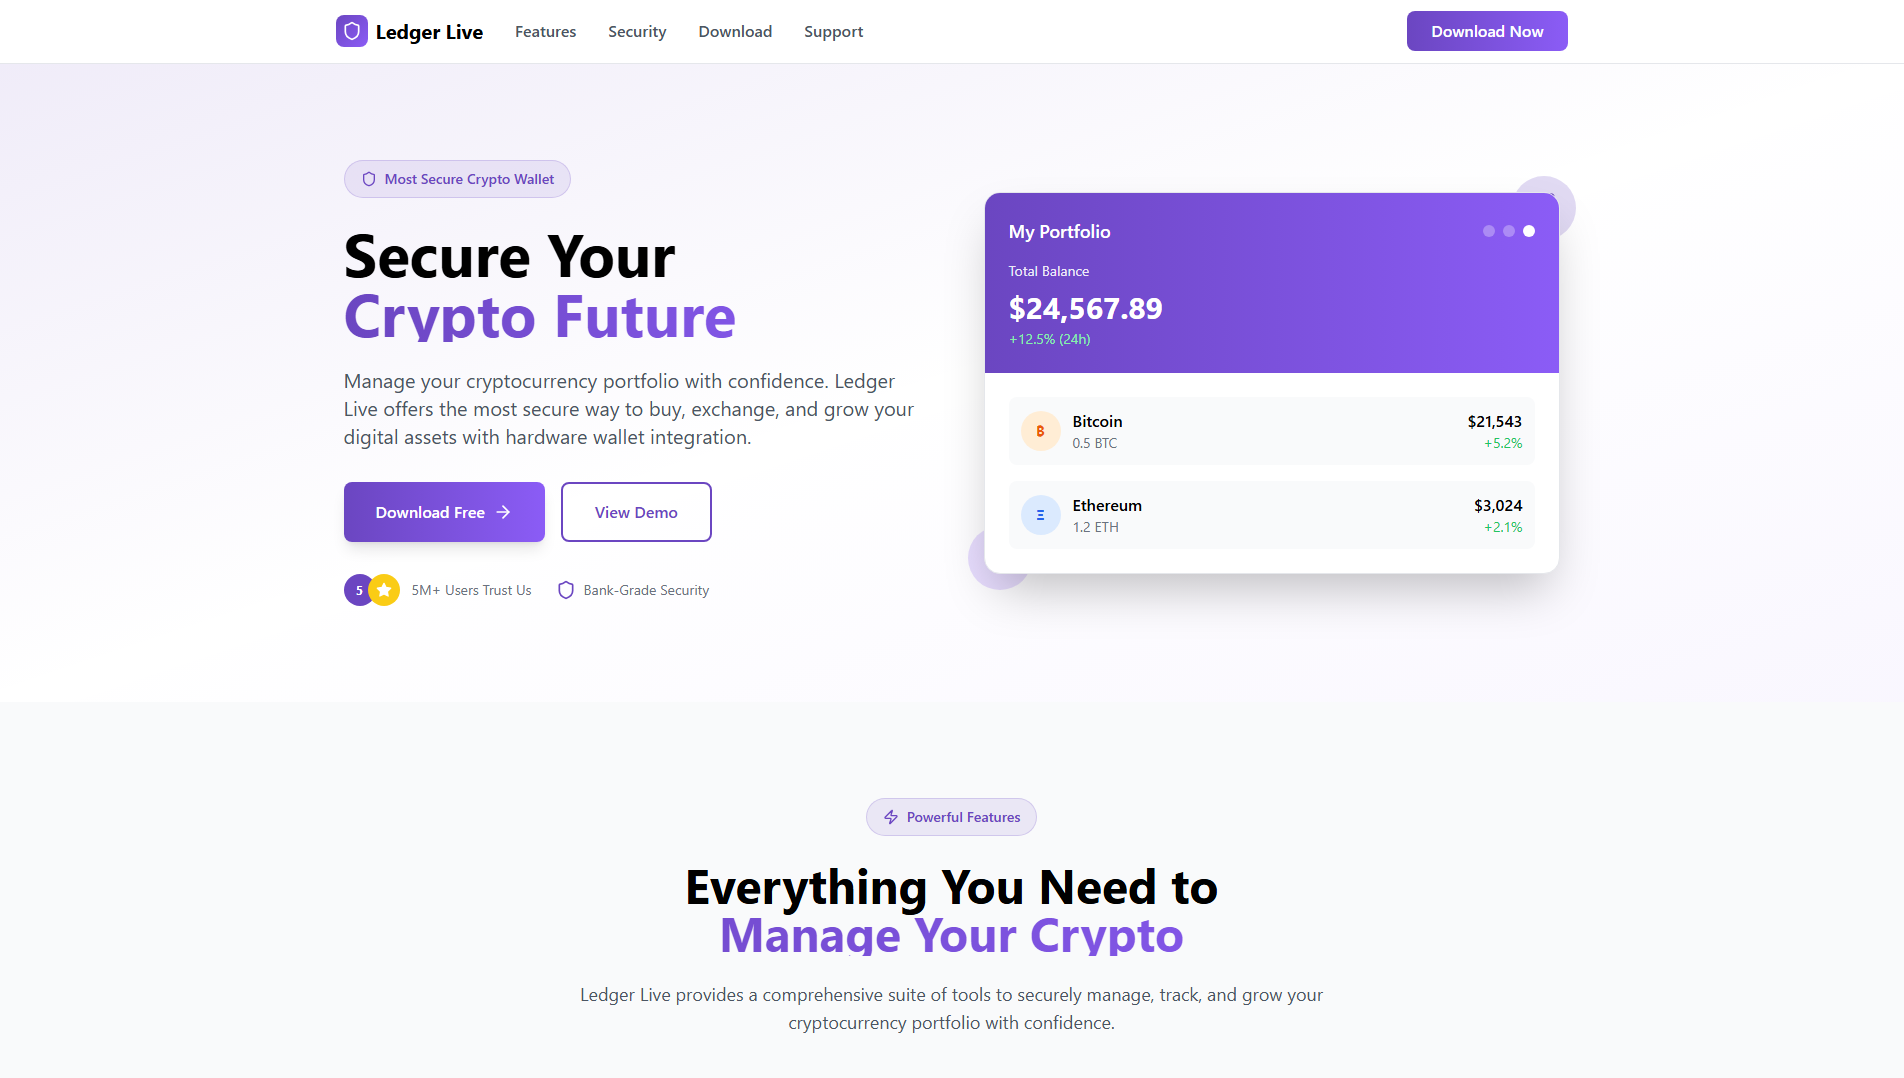
start-live-io.created.app is a subdomain of created.app. PhishDestroy first observed the hostname on Aug 29, 2026. Stored content metadata identifies Ledger as the apparent target. The captured page title is “Ledger Live App® | #1 Official Ledger Mobile & Desktop”. Stored page analysis classifies the content as impersonation. Current evidence score: 100/100 (critical).
Positive findings are stored from 4 sources: VirusTotal, MetaMask, SEAL, and URLScan. VirusTotal recorded 15 detections among 89 engines: alphaMountain.ai, CyRadar, Ermes, ESET, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, Kaspersky, LevelBlue, Lionic, SOCRadar, Sophos, VIPRE, Webroot on Sep 12, 2026 at 02:16 UTC. MetaMask and SEAL listed the hostname in the separate external-blocklist snapshot on Sep 21, 2026 at 14:20 UTC. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Ledger and assigned phishing as its category on Aug 29, 2026 at 17:08 UTC. Non-positive and contextual checks: Google Safe Browsing returned no flag on Sep 12, 2026 at 04:00 UTC.
HTTP 200 was recorded on Sep 21, 2026 at 10:06 UTC. Registration records for the registrable domain created.app list Created App as the registrar. At collection time, the hostname resolved to 216.150.16.129. The IP and ASN identify shared Vercel edge infrastructure; the origin server is not established by this address. The evidence archive retains 2 visual captures from PhishDestroy and URLScan. TLS metadata lists Let's Encrypt as the certificate issuer.
The content indicators and 4 positive source findings support the current Ledger-themed impersonation classification.
VirusTotal
15 det.
URLScan
Scamadviser
80/100Likely Safe
TLS Certificate
Let's Encrypt
Observed status
Last known active 200

DestroyList
Listed
Data coverage
VirusTotal
15 / 89
OTX
no community references
CF Radar
scan completed
URLScan capture
stored report
URLScan verdict
malicious
TLS
valid certificate, 87d
WHOIS
not parsed
Screenshot
2 captures · 2 sources
Scamadviser
80/100
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
VirusTotal Detections Update Aug 31, 2026 · 00:04 UTCVirusTotal scanner detections updated from 15 to 15. Added scanner alerts: SOCRadar. Resolved alerts: Phishtank.
-
VirusTotal Detections Update Aug 30, 2026 · 07:28 UTCVirusTotal scanner detections updated from 14 to 15. Added scanner alerts: Ermes.
-
VirusTotal Detections Update Aug 30, 2026 · 02:41 UTCVirusTotal scanner detections updated from 13 to 14. Added scanner alerts: Cluster25.
-
VirusTotal Detections Update Aug 30, 2026 · 00:07 UTCVirusTotal scanner detections updated from 1 to 13. Added scanner alerts: CyRadar, ESET, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, Kaspersky, Lionic, Phishtank, Sophos, VIPRE, alphaMountain.ai.
-
Threat First Observed Aug 29, 2026 · 18:02 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
216.150.16.129.
Threat Response Pipeline
Discovery
Checks
Reports
Availability
15/17
Public Blocklist Status
Evasion analysis
Cloaking & traffic-distribution check
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
- Last cloaking scan
- Server header seen by scanner
Vercel
Scanner note: alive_content: raw=ok; http=200; via=https_proxy; server=Vercel
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
Stored Capture · 2 sources
Domain Intelligence
Domain
URLScan Verdict
Malicious
score 100 Phishing brand: Ledger report ↗
Server / ASN
Vercel
IP Context
Vercel shared edge
origin IP hidden
Edge-IP reputation is not attributed to this domain.
Registrar (base domain)
Created App
IP Address
216.150.16.129
CDN
Geo US
USThe origin IP is hidden behind a CDN proxy. Reverse-IP results for the edge address contain unrelated tenants; finding the origin requires passive DNS or certificate-transparency data.
HTTP Status200
Technical detailsDNS, SSL SANs, timestamps
First DetectedAug 29, 2026
IoC Extraction
Submitted URLhttps://start-live-io.created.app/
Favicon Hash
ICANN OVERSIGHT
Registration: created.app
Accreditation and RAA context
Accreditation and RAA context
Registrar accreditation and DNS abuse obligations
For the registrable domain created.app behind this subdomain, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Accreditation is a contract, not a safety seal.
Verify ICANN fees
Read RAA §3.18
PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
Technologies · 9 identified
Node.js
Programming languages
React
JavaScript frameworks
Google Cloud
IaaS
Vercel
PaaS
Next.js
JavaScript frameworks
Web frameworks
LaunchDarkly
Feature management
HSTS
Security
Google Cloud CDN
CDN
Webpack
Miscellaneous
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain
Submit evidence & help protect others
VirusTotal Analysis
15 / 89 security vendors flagged this domain
View on VT
Last analyzed First positive detection Previous stored snapshot: 15 detections
alphaMountain.ai
CyRadar
Ermes
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
LevelBlue
Lionic
SOCRadar
Sophos
VIPRE
Webroot
Archived Evidence
Wayback Machine Snapshot
A historical snapshot is available for evidence review
Site Performance Analysis
Google PageSpeed Insights — mobile performance audit of start-live-io.created.app · checked Aug 29, 2026
72
Needs Work
Performance
FCP
2.55s
First Contentful Paint
LCP
6.05s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
137ms
Total Blocking Time
SI
3.28s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Lookalike domains
151 stored lookalike domains
ledfger.com
insertion Internal report
ledgfer.com
insertion Internal report
ledgher.com
insertion Internal report
ledgrr.com
replacement Internal report
lefdger.com
insertion Internal report
lesdger.com
insertion Internal report
lkedger.com
insertion Internal report
lredger.com
insertion Internal report
lwedger.com
insertion Internal report
xn--ledgr-9za.com
homoglyph Internal report
ledgerk.com
addition Internal report
edger.com
omission
Show all (88)
eldger.com
transposition
kedger.com
replacement
kledger.com
insertion
l3dger.com
replacement
ldeger.com
transposition
ldger.com
omission
le.dger.com
subdomain
lecger.com
replacement
ledber.com
replacement
ledegr.com
transposition
leder.com
omission
ledg3r.com
replacement
ledge.com
omission
ledged.com
replacement
ledgedr.com
insertion
ledgee.com
replacement
ledgeer.com
repetition
ledgercom.com
various
ledget.com
replacement
ledgewr.com
insertion
ledgger.com
repetition
ledgir.com
vowel-swap
ledgor.com
vowel-swap
ledgr.com
omission
ledgre.com
transposition
ledgrer.com
insertion
ledgsr.com
replacement
ledgwer.com
insertion
ledgwr.com
replacement
ledher.com
replacement
ledhger.com
insertion
ledsger.com
insertion
ledtger.com
insertion
ledyer.com
replacement
ledzer.com
replacement
leedger.com
insertion
legder.com
transposition
leger.com
omission
lerdger.com
insertion
lerger.com
replacement
lesger.com
replacement
lewdger.com
insertion
lidger.com
vowel-swap
lledger.com
repetition
lodger.com
vowel-swap
lrdger.com
replacement
lsdger.com
replacement
oedger.com
replacement
pedger.com
replacement
pledger.com
insertion
dedger.com
bitsquatting
hedger.com
bitsquatting
iedger.com
homoglyph
l-edger.com
hyphenation
ladger.com
bitsquatting
lcdlger.com
homoglyph
lddger.com
bitsquatting
lebger.com
homoglyph
leclger.com
homoglyph
ledcer.com
bitsquatting
leddger.com
insertion
ledeer.com
bitsquatting
ledeger.com
insertion
ledfer.com
bitsquatting
ledg-er.com
hyphenation
ledgar.com
bitsquatting
ledger0.com
addition
ledger1.com
addition
ledger4.com
addition
ledger5.com
addition
ledger6.com
addition
ledgerb.com
addition
ledgerc.com
addition
ledgerf.com
addition
ledgeri.com
addition
ledgern.com
addition
ledgerq.com
addition
ledgerx.com
addition
ledges.com
bitsquatting
ledgez.com
bitsquatting
ledgur.com
bitsquatting
lediger.com
homoglyph
ledqer.com
homoglyph
leeger.com
bitsquatting
leelger.com
homoglyph
lefger.com
bitsquatting
letger.com
bitsquatting
ludger.com
bitsquatting
Showing 100 of 151
Evidence & External Reports
Security Analysis
OSINT & Intelligence
DNS & Network
SEO & Domain
Were You Affected by This Site?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Action Fraud
Report fraud and cybercrime in England, Wales and Northern Ireland
Contact centre0300 123 2040
PhishDestroy listing review Not a law-enforcement report
Domain Appeal
Request a review if you own this domain and believe the listing is incorrect
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
Report to Your Local Authorities
Select your country to get official cybercrime contacts, or create a complaint draft →.
97-country directory
Template-based draft • optional AI wording assistance requires separate consent
Review and submit it yourself
Related Infrastructure & Reports
Infrastructure map · start-live-io.created.app
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Content matches 8


Other reports on shared Vercel edge 6
Shared edge IP; unrelated tenants may be present.
 robinhood-me.app
 portal-idos.network
Same registrar: Created App 6
Ledger impersonation 8
These domains also target Ledger users. View all Ledger threats →
Check Any Domain
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowReport Phishing
Submit suspicious domains to our threat database — protect the community
ReportLive Threat Feed
Recent phishing reports and observed availability changes
MonitorStay Informed, Stay Safe
Monitor live threats or contest this listing if you believe it's a false positive