Skip to security report
Domain security and threat intelligence
mail.goldserving-incorporation.us favicon

mail.goldserving-incorporation.us

Registrar
Cloudflare
Resolved IP
109.238.86.88
Registered
Jul 15, 2026
PhishDestroy assessment Critical
First observed Oct 20, 2026 13:20 UTC · PhishDestroy
VirusTotal detections: 10/92 Spamhaus DBL: DBL_SPAM Stored blocklist matches: 1 Automated brand label: Binance
Oct 20, 2026
API
This domain has been flagged as malicious
Security engines reporting a detection: 10. Public blocklists reporting a match: 1. Exercise extreme caution — do not enter credentials or personal information.
VirusTotal
engine detections
Google Safe Browsing
URLQuery
detections
Page captures
open gallery
Domain age
Source evidenceVirusTotal 10 / 92 7 sources

VirusTotal

10 / 92 engine detections

Open report

Spamhaus DBL

DBL_SPAM

OTX

no community references

Open report

Google Safe Browsing

No threat flag

Open report

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Analysis

Critical
VirusTotal
10 / 92
Page captures
3

PhishDestroy threat report

Overview

PhishDestroy has listed mail.goldserving-incorporation.us as a suspicious domain. The domain was first observed by PhishDestroy on 2026-10-20. No page title was recorded at the time of observation.

How the scam works

The listing indicates the domain may be used in typical online fraud or phishing campaigns, but no specific malicious behavior was observed on the page. Because the page title is unknown, we cannot identify a particular impersonated brand or scheme.

Evidence

VirusTotal scanned the domain on 2026-10-20 and reported 10 detections out of 92 engines, with vendors such as alphaMountain.ai, CRDF, Emsisoft, Fortinet, Kaspersky, LevelBlue, Netcraft and OpenPhish flagging it. Google Safe Browsing checked on 2026-10-20 reported the domain as not flagged. PhishDestroy’s internal blocklist includes the domain, while external blocklists checked on the same date returned zero matches. OTX had no pulses referencing the domain as of 2026-10-20.

Infrastructure

The recorded IP address for mail.goldserving-incorporation.us is 109.238.86.88. No registration, CDN or certificate details are available in the current evidence.

What to do

If you visited the site, monitor your accounts for unexpected activity and consider scanning your device with up‑to‑date security software. Change any passwords that may have been entered on the site. Security teams should block the exact domain and add it to monitoring rules, and review logs for any connections to 109.238.86.88.

Blocklist matchesOpenPhish · PhishDestroy 2
OpenPhish Listed View source
PhishDestroy PhishDestroy list View source

Last checked

Stored Capture · 3 captures

Domain details

Domain
IP Reputation abuse score 0/100 0 reports checked Oct 20, 2026
Registrar (base domain) Cloudflare US(US)
Registration (base domain)goldserving-incorporation.us · Created Jul 15, 2026 (96d) — Expires Jul 15, 2027
Technical detailsProvenance & timestamps
First DetectedOct 20, 2026
DOM Analysisanalyzed Oct 20, 2026score 25/1004 brand signals
Submitted URLhttp://mail.goldserving-incorporation.us/
Favicon Hash
Case ID
Automated brand references
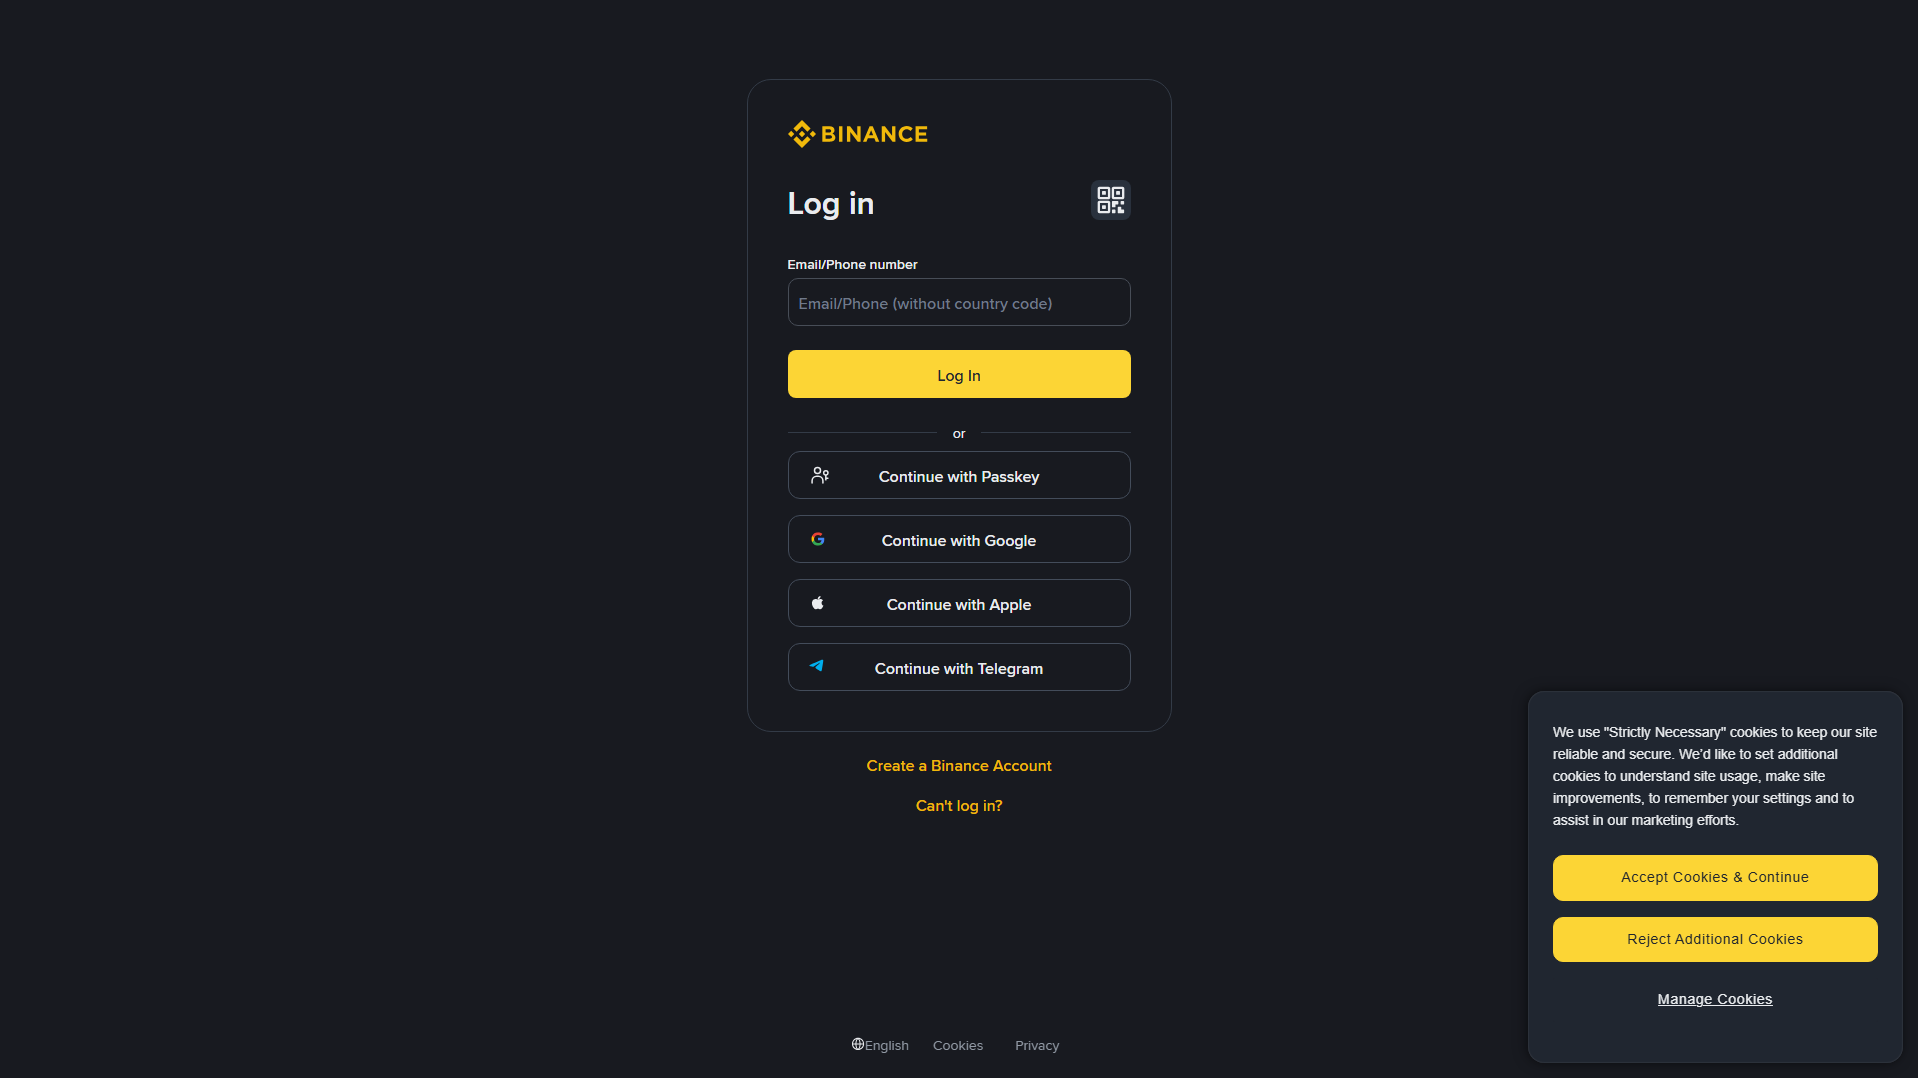
Apple Binance Google Telegram

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
109.238.86.88
Network ASN
AS201738
Organization
UFO TECHNOLOGIES LIMITED
Observed location
Erith, GB

Nameservers 2

  • augustus.ns.cloudflare.com
  • rachel.ns.cloudflare.com

Location describes the IP network.

Report This Domain Submit evidence & help protect others

VirusTotal Analysis

10 / 92 security vendors flagged this domain
View on VT
Last analyzed
alphaMountain.ai
CRDF
Emsisoft
Fortinet
Kaspersky
LevelBlue
Netcraft
OpenPhish
SOCRadar
Webroot
Stored Capture Evidence 1 snapshot

Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.

Archived HTTP response HTTP 200
Requested URL: http://mail.goldserving-incorporation.us/
Final URL: https://kidsgreenay.com/en/login
Log In | Binance
login-description
Response
HTTP 200
HTML body
175.9 KB
Compressed
32.8 KB
Links
0 internal · 2 external
Detected technologies
nginx
Selected response headers
Server: nginx/1.24.0 (Ubuntu)
Content-Type: text/html
Content-Encoding: gzip
HSTS: not observed DNSSEC: not observed WAF / firewall: not observed Cloaking flag: not observed
Open Graph title: Bitcoin Exchange | Cryptocurrency Exchange | Binance
Open Graph description: Binance cryptocurrency exchange - We operate the worlds biggest bitcoin exchange and altcoin crypto exchange in the world by volume
Saved response-header values · 7
Connection
keep-alive
Content-Encoding
gzip
Content-Type
text/html
Date
Tue, 20 Oct 2026 13:25:39 GMT
Last-Modified
Fri, 09 Oct 2026 19:27:18 GMT
Server
nginx/1.24.0 (Ubuntu)
Transfer-Encoding
chunked

Values retained by the collector; long values may be shortened during collection.

Recorded activity

4 entries
  1. URLScan

    Page captured

    View source
  2. Google Safe Browsing

    No threat flag

    View source
  3. VirusTotal

    10/92 engine detections

    View source
  4. Added to PhishDestroy

    mail.goldserving-incorporation.us

    View source

Lookalike domains

187 stored lookalike domains

Show all (88)
binabce.com replacement binacne.com transposition binan.ce.com subdomain binancecom.com various binanci.com vowel-swap binanco.com vowel-swap binancr.com replacement binancs.com replacement binancw.com replacement binande.com replacement binanfe.com replacement binanve.com replacement binanxe.com replacement binnace.com transposition binonce.com vowel-swap binsnce.com replacement binunce.com vowel-swap binynce.com replacement binznce.com replacement bniance.com transposition bunance.com replacement ibnance.com transposition ninance.com replacement b-inance.com hyphenation b8inance.com insertion b8nance.com replacement b9nance.com replacement bbinance.com repetition bhinance.com insertion bi-nance.com hyphenation biance.com omission bibance.com replacement bibnance.com insertion bihance.com replacement bihnance.com insertion biinance.com repetition bijnance.com insertion biknance.com insertion bimance.com homoglyph bimnance.com insertion bin-ance.com hyphenation binaance.com repetition binabnce.com insertion binace.com omission binahce.com replacement binamnce.com insertion binan-ce.com hyphenation binanbce.com insertion binanc-e.com hyphenation binanc.com omission binanc3.com replacement binancce.com repetition binancve.com insertion binancxe.com insertion binancz.com replacement binandce.com insertion binane.com omission binanec.com homoglyph binanhce.com insertion binanmce.com insertion binannce.com homoglyph binanvce.com insertion binanxce.com insertion binarnce.com homoglyph binasnce.com insertion binawnce.com insertion binbance.com insertion binhance.com insertion binmance.com insertion binnance.com homoglyph binnce.com omission binqance.com insertion binsance.com insertion binwnce.com replacement binyance.com insertion bionance.com insertion birnance.com homoglyph biunance.com insertion bjnance.com replacement bnance.com omission bninance.com insertion boinance.com insertion bonance.com replacement buinance.com insertion bvinance.com insertion clinance.com homoglyph dinarce.com homoglyph ginance.com replacement

Showing 100 of 187

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

mail.goldserving-incorporation.us

Evidence & External Reports

Deep Analysis
Help & reporting

Were You Affected by This Site?

4 evidence signal groups linked 0 stored notification records Unverified

Listed domains receive at least one abuse report; this entry has no retained notification history.

If credentials were compromised, report immediately. Do not engage with recovery scammers.

If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Official reporting routes

Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

97-country directory

Template-based draft · optional AI wording assistance requires separate consent

Template-based draft • optional AI wording assistance requires separate consent · Review and submit it yourself
After a phishing incident

Recommendations & Advice for Victims

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

What should I do immediately?

Urgent

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • Change all passwords — email, exchange accounts, anything that shares the same password
  • Enable 2FA using an authenticator app (not SMS). Disable SMS-based recovery
  • Freeze cards if you entered banking details on the phishing site

What information should I collect for my report?

FBI guidelines

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • Exact dates & times — of each transaction and first contact with scammer
  • Screenshots — scam website, chat messages, emails, wallet transactions, social media
  • All URLs & domains used by the scammer (including mail.goldserving-incorporation.us)
  • Communications — emails, texts, phone numbers, usernames the scammer used

Even if you don't have all details — file a report anyway. Partial information still helps investigations.

Where should I report the scam?

  • FBI IC3 — Internet Crime Complaint Center (US federal reporting)
  • Europol — European cybercrime reporting (EU)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • Local police — creates an official record, even if they can't act immediately

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • Fake websites — pixel-perfect clones of legitimate sites with slightly altered domains
  • Pig butchering — trust built over weeks via Telegram/WhatsApp/dating apps, then money stolen
  • Recovery scams — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • AI-powered scams — deepfakes, automated phishing, and AI-generated sites making fraud harder to detect

How can I protect myself in the future?

  • Bookmark official sites — never click links from emails, DMs, or ads
  • Verify domains — check on PhishDestroy before interacting. Check HTTPS, spelling, domain age
  • "Too good to be true" = scam — guaranteed returns, celebrity endorsements, urgent deadlines

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive

Live Threat Feed Appeal This Listing
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.


Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/mail.goldserving-incorporation.us"
  title="PhishDestroy threat report for mail.goldserving-incorporation.us"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>