




Domain security and threat intelligence

get-tron.org
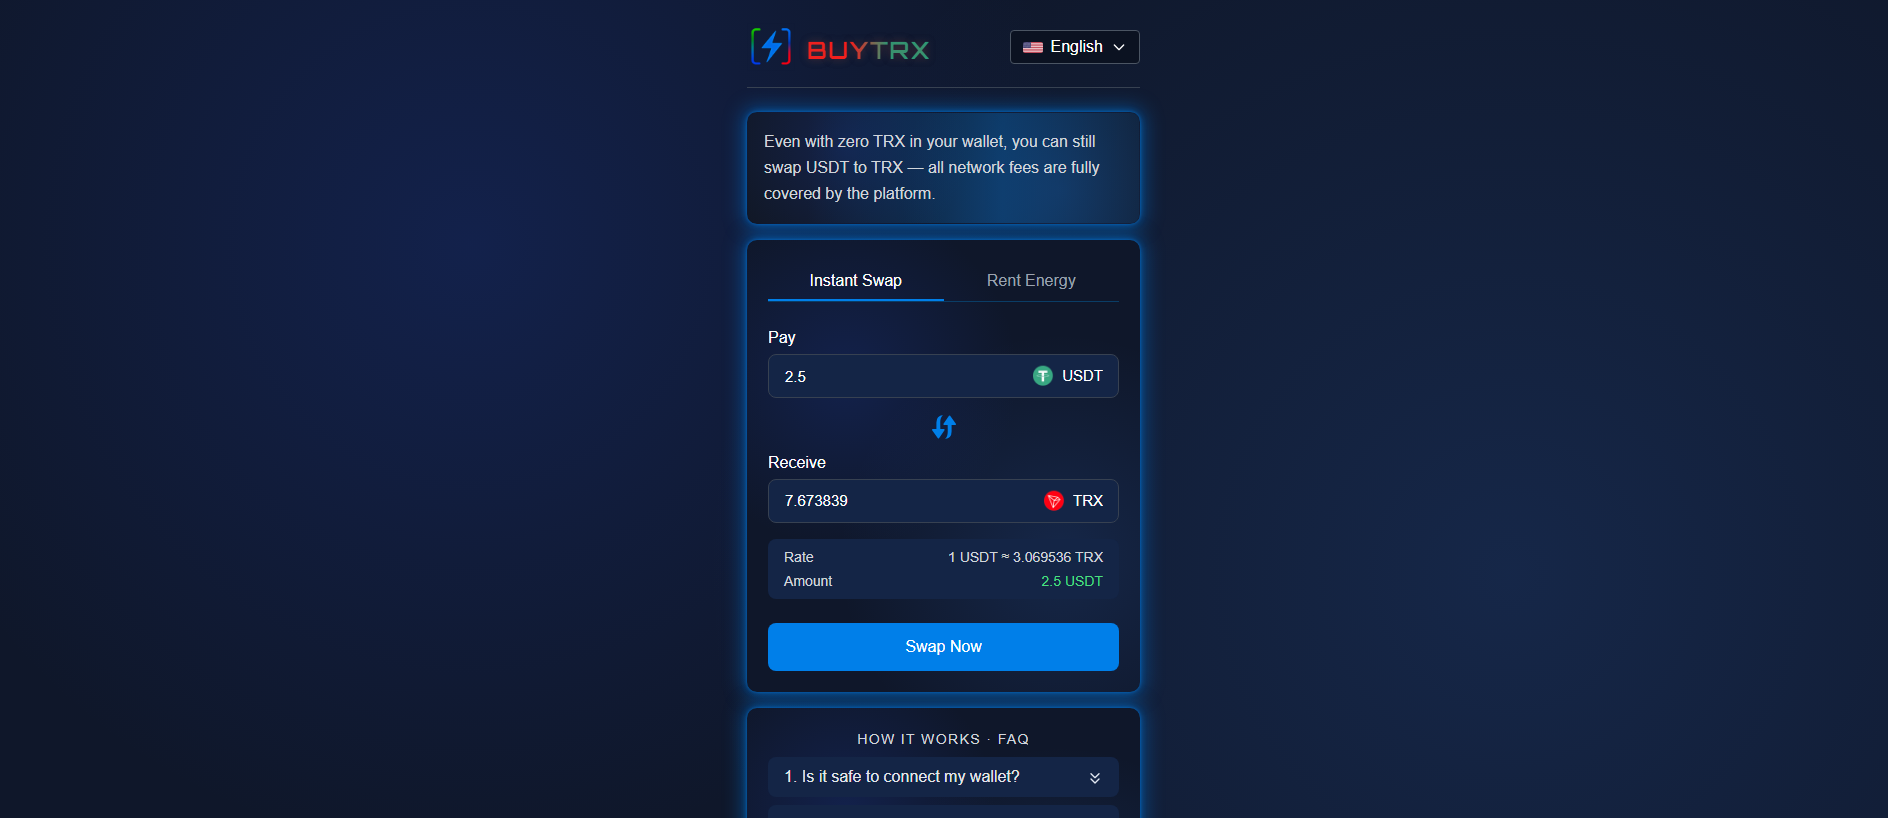
“Buy TRX with USDT & TRON Energy Purchase | Fast, Secure, Reliable”
Threat verdict
Critical
80/100 evidence score
Availability
Last known active
Latest stored reachability observation
Risk signals
VirusTotal detections: 5/89
Last known active
Actions
API
ABUSE NOTICE · 7D+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is registry@key-systems.net.
The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
1 month
Reports sent
1
Latest case ID
PD-20260803-CB4BB6
Current status
HTTP 301 at latest stored check
Evidence Summary
CRITICAL
The domain get-tron.org was observed in a phishing infrastructure campaign and is currently listed as active. Automated analysis shows that the site is blocked by the PhishDestroy filtering service and that it appears on a single public security blocklist. A full scan on VirusTotal was performed, involving 91 independent antivirus and URL‑reputation engines; at the time of analysis none of the engines reported a detection for the domain.
No additional information on registrar, registration date, hosting IP, ASN, or TLS certificate has been published in open sources, and attempts to retrieve HTTP response headers returned no definitive status codes. The page title and any branding displayed by the site have not been captured, leaving the specific lure or targeted brand undefined. Consequently, while the domain is confirmed to be part of a generic phishing operation, the exact payload, credential‑stealing mechanisms, and victim profile remain uncertain.
Risk level is under investigation, reflecting the limited publicly available evidence, and the status remains active, indicating the infrastructure may still be used to host credential‑harvesting pages. Defenders should continue to block get-tron.org at network perimeters, incorporate the domain into URL filtering and threat‑intel feeds, and monitor for any changes in its hosting characteristics or detection status. Ongoing re‑scans of VirusTotal and periodic checks against broader blocklists are recommended to capture any future malicious activity that may emerge.
VirusTotal
5 det.
URLScan
TLS Certificate
Google Trust Services
Age
3 mo New
Observed status
Last known active 301

DestroyList
Listed
Reports Sent
1
Data coverage
VirusTotal
5 / 89
URLQuery
checked — no detections recorded
OTX
no community references
CF Radar
scan completed
URLScan capture
stored report
URLScan verdict
Analysis completed
TLS
valid certificate, 55d
WHOIS
3 mo old
Screenshot
5 captures · 4 sources
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Threat First Observed Aug 3, 2026 · 21:34 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
188.114.96.3.
Threat Response Pipeline
Discovery
Checks
Reports
Availability
11/12
Sent Report Recorded
Stored sent-report record for registrar Internet Domain Service BS Corp, hosting provider, 1 abuse contact
registry@key-systems.net
Public Blocklist Status
Stored observation
Observed title contrast
Scanner-facing title301 Moved Permanently
Visitor-facing titleBuy TRX with USDT & TRON Energy Purchase | Fast, Secure, Reliable
Stored Capture · 5 sources
Domain Intelligence
Domain
URLScan Verdict
Analysis completed
score 0 report ↗
Telegram IoCs
1 extracted
https://t.me/buytrx9
Server / ASN
cloudflare · AS13335 Cloudflare, Inc.
IP Context
Cloudflare shared edge
origin IP hidden
Edge-IP reputation is not attributed to this domain.
Registrar
Internet Domain Servic…
IP Address
188.114.96.3
CDN
Geo Toronto, CA
NetworkAS13335 · CloudFlare, Inc.
The origin IP is hidden behind a CDN proxy. Reverse-IP results for the edge address contain unrelated tenants; finding the origin requires passive DNS or certificate-transparency data.
RegistrationCreated Jun 30, 2026 (78d · New) — Expires Jun 30, 2027
HTTP Status301 Moved Permanently
Technical detailsDNS, SSL SANs, timestamps
First DetectedAug 3, 2026
IoC Extraction
Submitted URLhttps://get-tron.org/
Nameserversmaleah.ns.cloudflare.commiles.ns.cloudflare.com
TLS Fingerprint
TLS Observation
Favicon Hash
Case ID
Technologies · 3 identified
Cloudflare Browser Insights
Analytics
RUM
Cloudflare
CDN
HTTP/3
Miscellaneous
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain
Submit evidence & help protect others
VirusTotal Analysis
5 / 89 security vendors flagged this domain
View on VT
Last analyzed First positive detection Previous stored snapshot: 7 detections
alphaMountain.ai
CRDF
Forcepoint ThreatSeeker
Gridinsoft
SOCRadar
Archived Evidence
Wayback Machine Snapshot
A historical snapshot is available for evidence review
Site Performance Analysis
Google PageSpeed Insights — mobile performance audit of get-tron.org · checked Aug 3, 2026
83
Needs Work
Performance
FCP
2.31s
First Contentful Paint
LCP
4.02s
Largest Contentful Paint
CLS
0.045
Cumulative Layout Shift
TBT
53ms
Total Blocking Time
SI
3.69s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Evidence & External Reports
Security Analysis
Submitted Evidence Snapshot
Sent: Ledger records: 1
Case ID:
PD-20260803-CB4BB6 Recipient: registry@key-systems.net OSINT & Intelligence
DNS & Network
SEO & Domain
Were You Affected by This Site?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Action Fraud
Report fraud and cybercrime in England, Wales and Northern Ireland
Contact centre0300 123 2040
PhishDestroy listing review Not a law-enforcement report
Domain Appeal
Request a review if you own this domain and believe the listing is incorrect
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
Report to Your Local Authorities
Select your country to get official cybercrime contacts, or create a complaint draft →.
97-country directory
Template-based draft • optional AI wording assistance requires separate consent
Review and submit it yourself
Related Infrastructure & Reports
Infrastructure map · get-tron.org
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Content matches 7

Other reports on shared Cloudflare edge 6
Shared edge IP; unrelated tenants may be present.
Same registrar: Internet Domain Servic… 6
 qprofitsystem.org
 quantumhancock.org
 ethereumproair.org
 immediateprofit.org
 bitcoin-maker.org
Check Any Domain
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowReport Phishing
Submit suspicious domains to our threat database — protect the community
ReportLive Threat Feed
Recent phishing reports and observed availability changes
MonitorStay Informed, Stay Safe
Monitor live threats or contest this listing if you believe it's a false positive