




Domain security and threat intelligence

flowers.somewaresinmaine.com
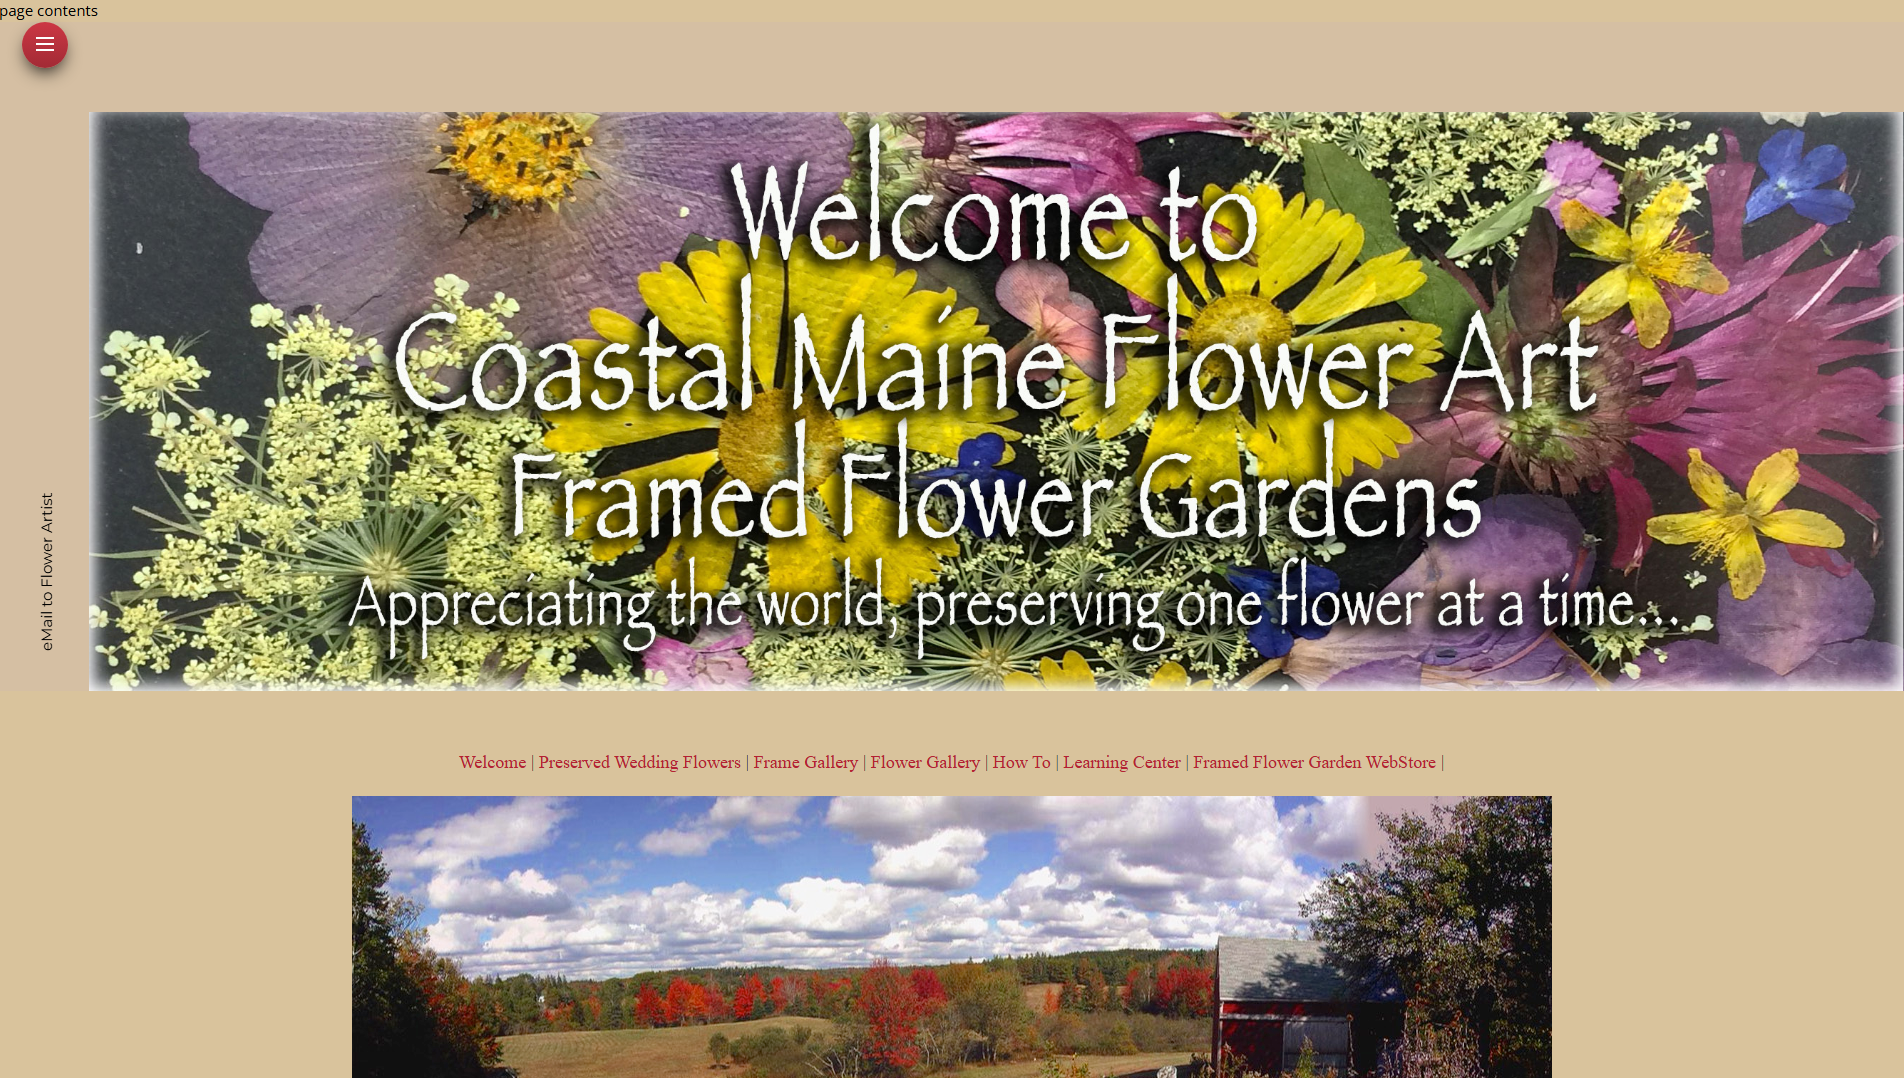
“Welcome to Coastal Maine Flower Art”
Threat verdict
Critical
88/100 evidence score
Availability
Unverified
Current reachability is unverified
Risk signals
VirusTotal detections: 12/91
Brand impersonation: Unknown
Actions
API
Evidence Summary
CRITICAL
flowers.somewaresinmaine.com is a subdomain of somewaresinmaine.com. PhishDestroy first observed the hostname on Sep 27, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “Welcome to Coastal Maine Flower Art”. Page analysis recorded additional brand references to Gmail and Rainbow. Current evidence score: 88/100 (critical).
Positive findings are stored from 2 sources: VirusTotal and Cloudflare Radar. VirusTotal recorded 12 detections among 91 engines: alphaMountain.ai, BitDefender, Chong Lua Dao, CRDF, Fortinet, G-Data, Gridinsoft, Kaspersky, Lionic, Sophos, VIPRE, Webroot on Sep 27, 2026 at 22:29 UTC. Cloudflare Radar classified the hostname as malicious and assigned the categories malware and security threats; its verdict timestamp was not retained. Non-positive and contextual checks: The separate external-blocklist snapshot contained no matches on Sep 27, 2026 at 22:20 UTC. Google Safe Browsing returned no flag on Sep 27, 2026 at 22:29 UTC. URLScan captured the page on Sep 27, 2026 at 21:27 UTC.
The collector marked the hostname reachable on Sep 27, 2026 at 21:27 UTC, but did not retain the HTTP response code. Registration records for the registrable domain somewaresinmaine.com list DREAMHOST as the registrar and Jun 17, 2012 as the creation date. At collection time, the hostname resolved to 66.33.195.169 on AS26347 (New Dream Network, LLC). The recorded endpoint location is Hillsboro, US. DOM analysis on Sep 27, 2026 at 22:20 UTC returned 88/100. The evidence archive retains 3 visual captures from PhishDestroy and URLScan. TLS metadata lists Let's Encrypt / YR2 as the certificate issuer with validity through Dec 12, 2026; checked Sep 27, 2026 at 22:02 UTC.
The content indicators and 2 positive source findings support the current Unknown impersonation and phishing classification. The target field identifies Unknown, but the record does not establish whether the page requested credentials, a seed phrase, or a wallet connection.
VirusTotal
12 det.
CF Radar
Malicious
URLScan
TLS Certificate
Let's Encrypt / YR2
Age
14.3 yr
Observed status
Unverified

DestroyList
Listed
Data coverage
VirusTotal
12 / 91
OTX
no community references
CF Radar
provider verdict: malicious
URLScan capture
stored report
TLS
valid certificate, 75d
WHOIS
174 mo old
Screenshot
3 captures · 2 sources
Network Security Intelligence
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Threat First Observed Sep 27, 2026 · 23:27 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
66.33.195.169.
Threat Response Pipeline
Discovery
Checks
Reports
Availability
10/12
Public Blocklist Status
Detection-evasion analysis
Cloaking and traffic-distribution check
Not yet scanned
No crawler-versus-browser difference has been recorded yet
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this panel is open.
Waiting
Stored Capture · 3 sources
Domain Intelligence
Domain
Server / ASN
AS26347 New Dream Network, LLC
IP Reputation
abuse score 0/100 0 reports checked Sep 28, 2026
Registrar (base domain)
DREAMHOST
IP Address
66.33.195.169

Registration (base domain)somewaresinmaine.com · Created Jun 17, 2012 — Expires Jun 17, 2027
Technical detailsDNS, SSL SANs, timestamps
First DetectedSep 27, 2026
DOM Analysis
Submitted URLhttp://www.flowers.somewaresinmaine.com/
Nameserversns1.dreamhost.comns2.dreamhost.comns3.dreamhost.com
MX Records0 mx1.dreamhost.com 0 mx2.dreamhost.com
TLS Fingerprint
TLS Observation
TLS SAN Domainswww.flowers.somewaresinmaine.com
Favicon Hash
Technologies · 3 identified
Apache HTTP Server
Web servers
jQuery
JavaScript libraries
Google Analytics
Analytics
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain
Submit evidence & help protect others
VirusTotal Analysis
12 / 91 security vendors flagged this domain
View on VT
Last analyzed First positive detection Previous stored snapshot: 12 detections
alphaMountain.ai
BitDefender
Chong Lua Dao
CRDF
Fortinet
G-Data
Gridinsoft
Kaspersky
Lionic
Sophos
VIPRE
Webroot
Site Performance Analysis
Google PageSpeed Insights — mobile performance audit of flowers.somewaresinmaine.com · checked Sep 27, 2026
61
Needs Work
Performance
FCP
3.49s
First Contentful Paint
LCP
13.91s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
42ms
Total Blocking Time
SI
8s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Evidence & External Reports
Security Analysis
OSINT & Intelligence
DNS & Network
SEO & Domain
Were You Affected by This Site?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Action Fraud
Report fraud and cybercrime in England, Wales and Northern Ireland
Contact centre0300 123 2040
PhishDestroy listing review Not a law-enforcement report
Domain Appeal
Request a review if you own this domain and believe the listing is incorrect
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
Report to Your Local Authorities
Select your country to get official cybercrime contacts, or create a complaint draft →.
97-country directory
Template-based draft • optional AI wording assistance requires separate consent
Review and submit it yourself
Related Infrastructure & Reports
- Direct link Shares a registration or an identical phishing kit.
- Supporting signal Shares infrastructure or a target brand; not proof of one operator.
- Discovery only Listed for navigation; no shared attribute with this host.
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Same registrar: DREAMHOST 6
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.


Recent threat reports 6
Recently added threat reports.


Check Any Domain
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowReport Phishing
Submit suspicious domains to our threat database — protect the community
ReportLive Threat Feed
Recent phishing reports and observed availability changes
MonitorStay Informed, Stay Safe
Monitor live threats or contest this listing if you believe it's a false positive