VirusTotal
11 / 89 engine detections
Open report

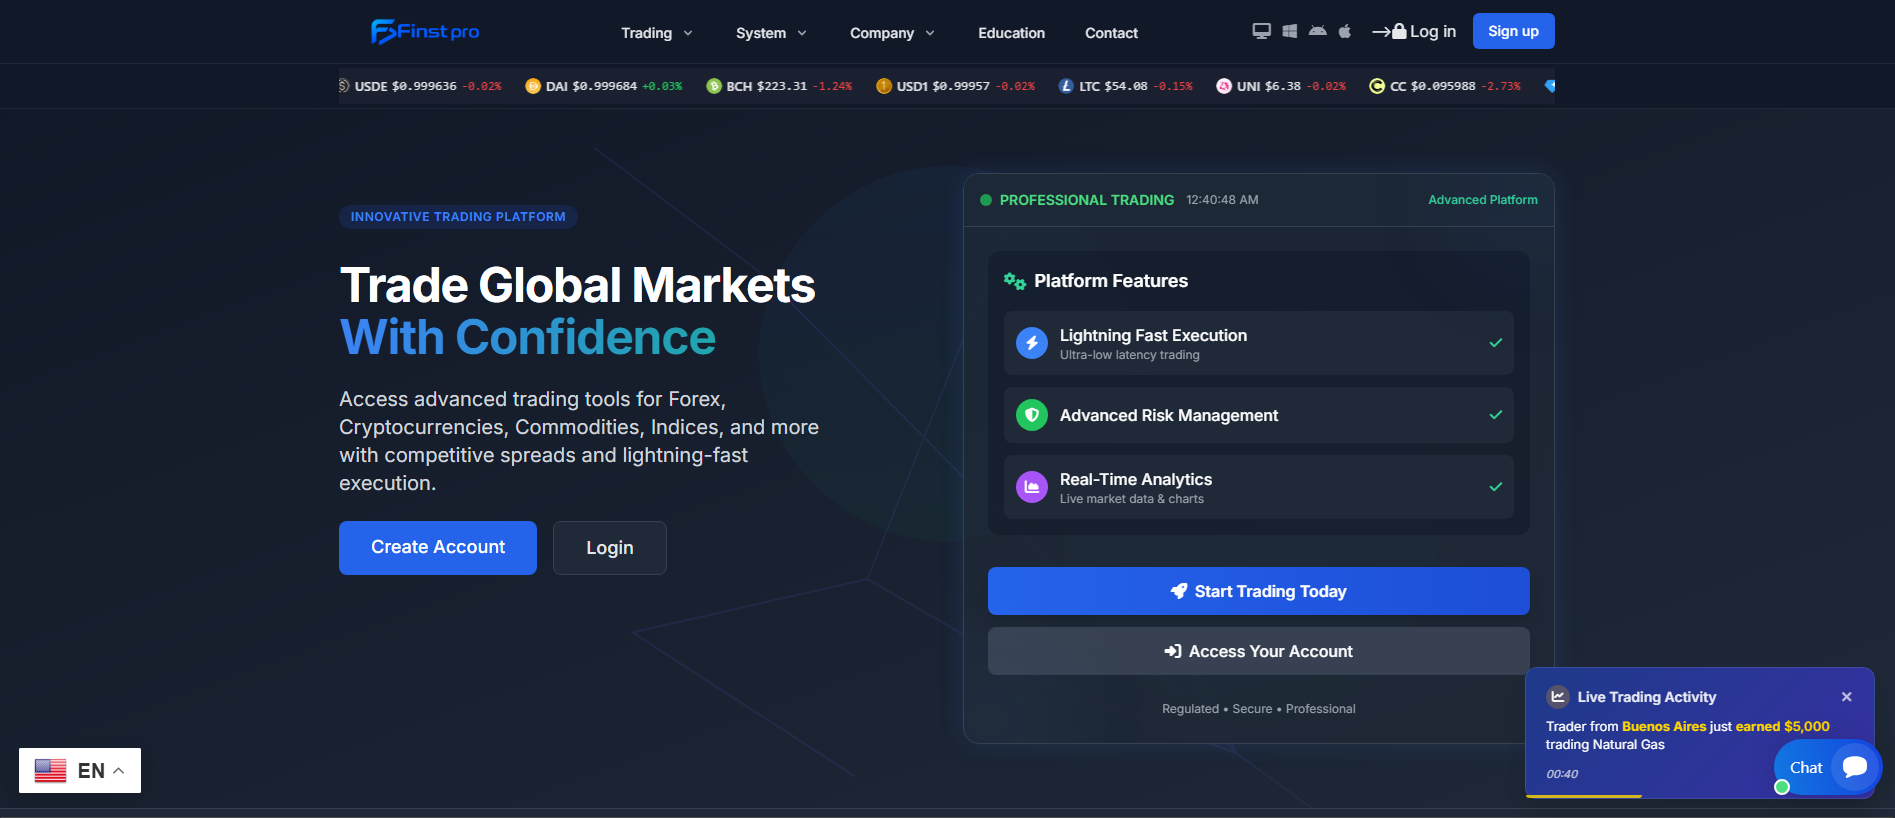
“Finstpro | CFD Trading — Trading on Stocks, Gold, Oil, Indices”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@aquiryn.com.
The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
11 / 89 engine detections
Open reportMalicious
Open reportchecked — no detections recorded
Open reportno community references
Open reportprovider verdict: clean
Open report80/100
Open reportNo threat flag
Open reportResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
AI-assisted evidence review
The domain finstpro.online.fortsill-staff.directory returned HTTP status 200 on 2026-10-01, according to the recorded HTTP check. The domain was observed operating from IP address 23.153.104.17 in the US, with Aquiryn LLC listed as the IP organization.
A VirusTotal scan on 2026-09-24 reported 11 detections out of 89 scanners for finstpro.online.fortsill-staff.directory. The SSL certificate was issued by Let's Encrypt / YR1, as recorded on 2026-09-15. The domain is internally listed in the PhishDestroy catalogue, and a PageSpeed performance score of 64 was documented on 2026-09-14.
The evidence from VirusTotal, SSL scan, HTTP check, and PhishDestroy listing each reflects a specific observation date, which means their findings should be compared in the context of when they were recorded. The IP address, country, and organization provide additional context for the domain's infrastructure, but do not establish any direct relationship or ownership.
For finstpro.online.fortsill-staff.directory, retain all dated evidence from VirusTotal, SSL, PageSpeed, HTTP, and PhishDestroy for future comparison. When reviewing subsequent observations, reference the exact dates to track any changes over time. Avoid submitting sensitive information during review, as the evidence does not describe how the domain manages such data.
For the registrable domain fortsill-staff.directory behind this subdomain, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Location describes the IP network.
13d92c5b884b432bc98cb8e2d74e96a7bb149790ce3ba3a152b1085439d42471finstpro.onlinewww.finstpro.online.fortsill-staff.directorySaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Hostnames retained in the domain record or Certificate Transparency cache. A hostname alone does not establish current availability or malicious activity.
www.finstpro.online.fortsill-staff.directoryDomain recordThe original observation time is not recorded for these hostnames.
Google PageSpeed Insights — mobile performance audit of finstpro.online.fortsill-staff.directory · checked Sep 14, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
finstpro.online.fortsill-staff.directory
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Unknown→live_content
content_served
Unknown→protected
captcha · challenge
Unknown→protected
captcha · challenge
protected→live_content
content_served
Unknown→protected
captcha · challenge
protected→live_content
content_served
Unknown→protected
captcha · challenge
Unknown→protected
captcha · challenge
Unknown→protected
captcha · challenge
Unknown→protected
captcha · challenge
Unknown→protected
captcha · challenge
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Reachable
No threat flag
View source11/89 engine detections
View sourcePD-20260914-804653
finstpro.online.fortsill-staff.directory
View sourcePage captured
View sourceEach lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Same favicon hash or the same page title as this host.
Multiple reports share this IP.
Reports with the same collector label. A shared label does not establish impersonation or common ownership. View matching reports →
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
PD-20260914-804653 Recipient: abuse@aquiryn.com If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
finstpro.online.fortsill-staff.directory)Even if you don't have all details — file a report anyway. Partial information still helps investigations.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.