Skip to security report
This domain has been flagged as malicious
Security engines reporting a detection: 14. Exercise extreme caution — do not enter credentials or personal information.
Domain security and threat intelligence
eobuwie.tiendasmgises.com favicon

eobuwie.tiendasmgises.com

In short

eobuwie.tiendasmgises.com is a phishing page detected by PhishDestroy on 2026-10-25.

“500 Internal Server Error”

Registrar
Cloudflare
Resolved IP
188.114.96.3
Registered
Aug 28, 2026
PhishDestroy assessment Critical
Availability Last known active Latest stored reachability observation Observed HTTP probe
VirusTotal detections: 14/92 Spamhaus DBL: phishing domain
VirusTotal
engine detections ·
OTX
community references
Cloudflare Radar
Page captures
open gallery
Domain age
Reports sent
No sent record
Oct 25, 2026 CDN
X Telegram API

Analysis

Domain summary

eobuwie.tiendasmgises.com is a phishing page detected by PhishDestroy on 2026-10-25. Risk: critical (100/100). Registrar: Cloudflare. Status: Last known active. Hosting: CloudFLARENET-EU. VirusTotal: 14/92 engines flag it. Listed on Spamhaus DBL. Do not enter credentials or connect a wallet.

Critical
VirusTotal
14 / 92
Page captures
5

PhishDestroy threat report

Overview

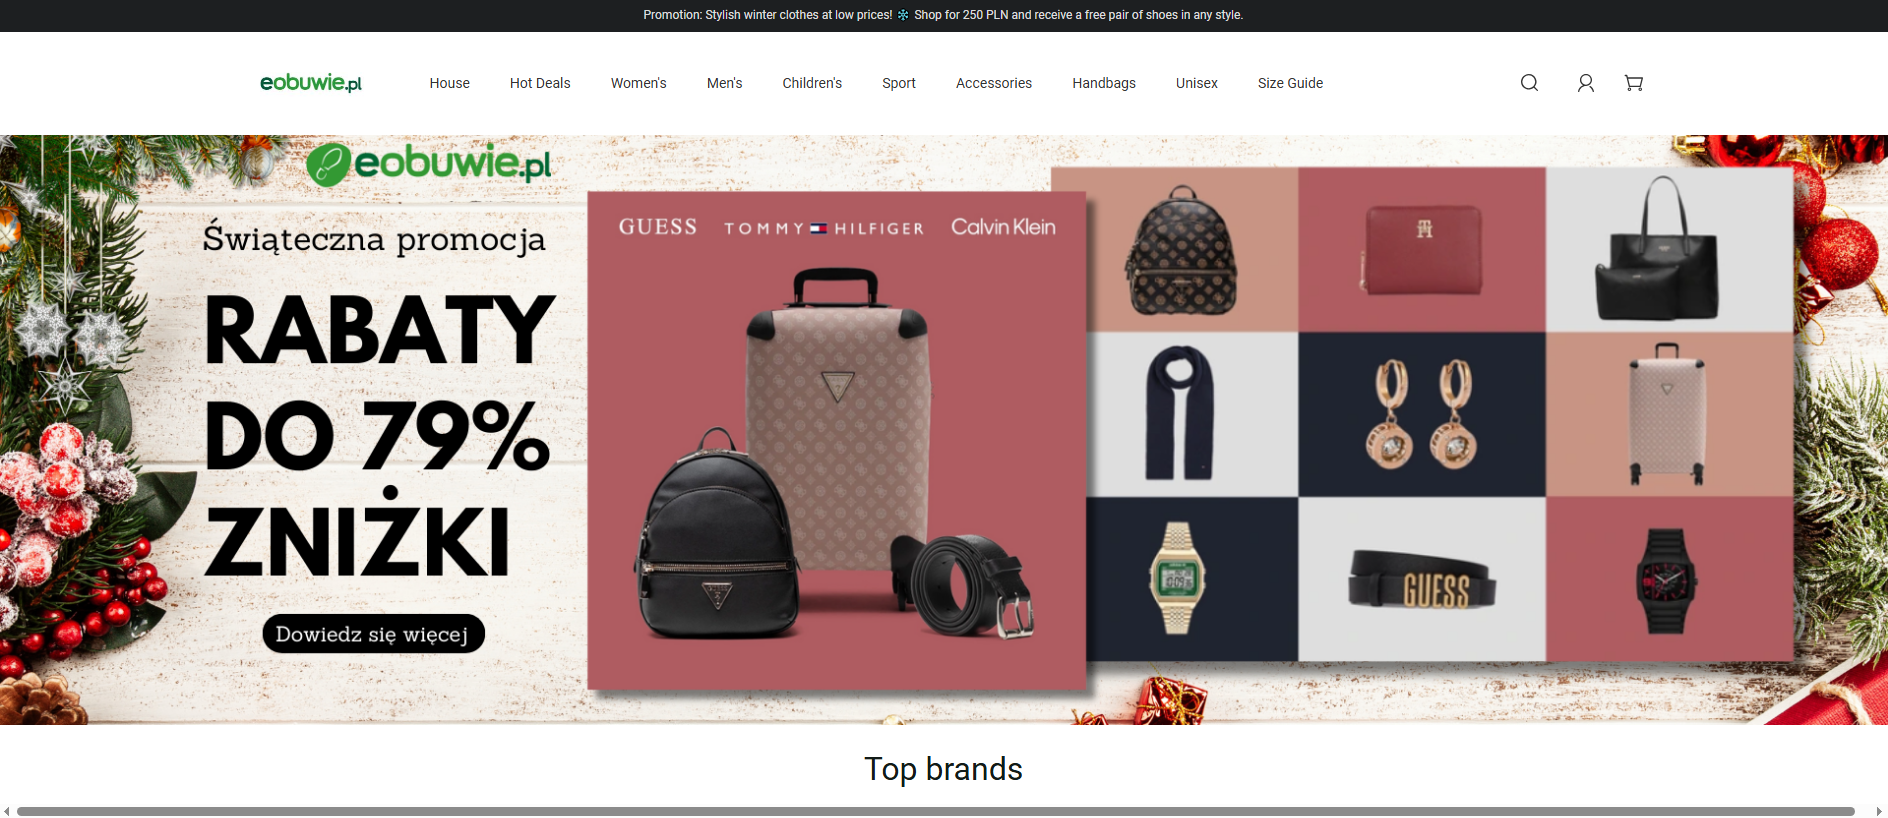
PhishDestroy added eobuwie.tiendasmgises.com to its internal blocklist on 2026-10-25. The intake system recorded a 403 HTTP response and a Cloudflare challenge, which prevented direct content analysis. A later fetch recorded the page title “500 Internal Server Error”, but the title date is not known. Subsequent scans captured a page with metadata referencing a Polish shoe retailer, creating a mismatch between the observed title and the later page content.

How the scam works

The domain is flagged as suspicious because multiple security engines have identified characteristics commonly associated with phishing or malware distribution, but no specific malicious payload, credential‑harvesting form, or wallet‑draining behavior was observed on the page. In general, such domains may be used to lure users into entering personal data, downloading unwanted files, or interacting with deceptive advertisements that mimic legitimate brands.

Evidence

VirusTotal reported 14 detections from 92 engines on 2026-10-22, including 11 malicious and 3 suspicious labels from vendors such as BitDefender, ESET, Fortinet and others. Google Safe Browsing checked the URL on 2026-10-25 and did not flag it. Cloudflare Radar scanned the site on 2026-10-25 and classified it as malicious with phishing and malware tags. URLScan captured a snapshot on 2026-09-22; its machine‑learning engine gave a malicious score of 66, while the overall verdict was clean. OTX listed zero pulses on 2026-10-25. PhishDestroy’s internal blocklist marks the domain as blocked, and external blocklists returned no hits on the same day.

Infrastructure

The recorded DNS data showed Cloudflare‑provided IP addresses 188.114.96.1, 188.114.97.3, 104.21.41.77 and 172.67.162.15, and the network was identified as CloudFLARENET‑EU in Great Britain. The TLS certificate, issued by Google Trust Services, was valid from 2026-09-21 to 2026-12-20. The domain’s apex age was 25 days and DNSSEC was not enabled. Nameservers were brad.ns.cloudflare.com and meilani.ns.cloudflare.com.

What to do

Do not enter credentials, payment details or personal information on this site. If you have already submitted data, change any associated passwords and monitor accounts for unusual activity. Network defenders should block eobuwie.tiendasmgises.com at firewalls or proxies and log any access attempts. Report any further observations to PhishDestroy for continued monitoring.

Source evidenceVirusTotal 14 / 92 8 sources

VirusTotal

14 / 92 engine detections · stored summary

Open report
VirusTotalOriginal source recordObserved: 13 fields

Observed: · Retrieved:

Vendor result counts

Timeout
0
Harmless
45
Malicious
11
Suspicious
3
Undetected
33

Vendor labels

CRDF
malicious
ESET
suspicious
VIPRE
phishing
G-Data
phishing
Lionic
phishing
Sophos
malware
Fortinet
phishing
Netcraft
malicious
SOCRadar
phishing
Kaspersky
phishing
Gridinsoft
suspicious
BitDefender
phishing
alphaMountain.ai
suspicious
Forcepoint ThreatSeeker
phishing

Reputation score

0

Registrar

Cloudflare, Inc.

Created

Expires

Updated

First seen

DNS records

  • TTL, seconds
    300
    Type
    A
    Value
    172.67.162.15
  • TTL, seconds
    300
    Type
    A
    Value
    104.21.41.77
  • TTL, seconds
    300
    Type
    AAAA
    Value
    2606:4700:3036::ac43:a20f
  • TTL, seconds
    300
    Type
    AAAA
    Value
    2606:4700:3032::6815:294d

DNS records observed

JARM fingerprint

27d40d40d00040d00042d43d00041df04c41293ba84f6efe3a613b22f983e6

Certificate

Subject alternative names
  • eobuwie.tiendasmgises.com
Issuer
Google Trust Services / WE1
Serial
c3f3ed7c7e085b360e7bbdf031dffb25
SHA-256
a347c192fabba5e114e61356ca85a82d3cf7e1d81f17e5022dc0a66411a1af43
Subject
eobuwie.tiendasmgises.com
Valid until
Valid from

Registration record

Registrar
Cloudflare, Inc.
Registrar IANA ID
1910
Registrar URL
http://www.cloudflare.com
Registered
Updated
Expires
Status
  • clientTransferProhibited
  • clienttransferprohibited
Nameservers
  • brad.ns.cloudflare.com
  • meilani.ns.cloudflare.com
DNSSEC
unsigned
Original source fields · JSON
Vendor result counts
{
    "timeout": 0,
    "harmless": 45,
    "malicious": 11,
    "suspicious": 3,
    "undetected": 33
}
Vendor labels
{
    "CRDF": "malicious",
    "ESET": "suspicious",
    "VIPRE": "phishing",
    "G-Data": "phishing",
    "Lionic": "phishing",
    "Sophos": "malware",
    "Fortinet": "phishing",
    "Netcraft": "malicious",
    "SOCRadar": "phishing",
    "Kaspersky": "phishing",
    "Gridinsoft": "suspicious",
    "BitDefender": "phishing",
    "alphaMountain.ai": "suspicious",
    "Forcepoint ThreatSeeker": "phishing"
}
Reputation
0
Registrar
Cloudflare, Inc.
Created
2026-08-28T06:24:19Z
Expires
2027-08-28T06:24:19Z
Updated
2026-09-04T08:34:57Z
First seen
2026-09-21T10:09:28Z
DNS records
[
    {
        "ttl": 300,
        "type": "A",
        "value": "172.67.162.15"
    },
    {
        "ttl": 300,
        "type": "A",
        "value": "104.21.41.77"
    },
    {
        "ttl": 300,
        "type": "AAAA",
        "value": "2606:4700:3036::ac43:a20f"
    },
    {
        "ttl": 300,
        "type": "AAAA",
        "value": "2606:4700:3032::6815:294d"
    }
]
Dns at
2026-10-22T06:12:24Z
Jarm
27d40d40d00040d00042d43d00041df04c41293ba84f6efe3a613b22f983e6
Certificate
{
    "san": [
        "eobuwie.tiendasmgises.com"
    ],
    "issuer": "Google Trust Services / WE1",
    "serial": "c3f3ed7c7e085b360e7bbdf031dffb25",
    "sha256": "a347c192fabba5e114e61356ca85a82d3cf7e1d81f17e5022dc0a66411a1af43",
    "subject": "eobuwie.tiendasmgises.com",
    "valid_to": "2026-12-20T09:50:06Z",
    "valid_from": "2026-09-21T08:50:10Z"
}
Registration record
{
    "registrar": "Cloudflare, Inc.",
    "registrar_iana_id": "1910",
    "registrar_url": "http://www.cloudflare.com",
    "created": "2026-08-28T06:24:19Z",
    "updated": "2026-08-28T06:24:19Z",
    "expires": "2027-08-28T06:24:19Z",
    "status": [
        "clientTransferProhibited",
        "clienttransferprohibited"
    ],
    "nameservers": [
        "brad.ns.cloudflare.com",
        "meilani.ns.cloudflare.com"
    ],
    "dnssec": "unsigned"
}
Separate source record · 11 malicious + 3 suspicious / 92 · 2026-10-22 06:07:02 UTC

The summary above and this provider record were collected at different times. Both remain available; malicious and suspicious classifications are shown separately.

record_source
collected_observations.vt
analysis_at
2026-10-22T06:07:02Z
fetched_at
2026-10-25T19:05:29Z
stats
{"timeout":0,"harmless":45,"malicious":11,"suspicious":3,"undetected":33}

Cloudflare Radar

Phishing

Open report
Cloudflare RadarOriginal source recordObserved: 14 fields

Observed: · Retrieved:

Report ID

bce63fca-f99f-4975-bd82-33222105df2c

Final URL

https://eobuwie.tiendasmgises.com/

HTTP response

200

Navigation history

  • URL
    https://eobuwie.tiendasmgises.com/
    Status
    200

DOM structure hash

b2d055e26983bd530aae4b55a2ba97c39045afd4c4b58a75aded9f638bd83b14

Document hash

e9a6b69eb79239c87ce4f7bc199cd7f945d0760a88ad8161f45799f58ec91432

Phishing classifier result

  • phishing

Domain risk categories

  • Malware
  • Security threats
  • CIPA Filter
  • CIPA

Cloudflare Radar rank

Rank range
>200000

DNS records

  • Name
    eobuwie.tiendasmgises.com
    Type
    A
    Value
    104.21.41.77
  • Name
    eobuwie.tiendasmgises.com
    Type
    A
    Value
    172.67.162.15
  • Name
    eobuwie.tiendasmgises.com
    Type
    AAAA
    Value
    2606:4700:3032::6815:294d
  • Name
    eobuwie.tiendasmgises.com
    Type
    AAAA
    Value
    2606:4700:3036::ac43:a20f

DNSSEC valid

No

IP address

104.21.41.77

Verdict

Tags
  • malware
Malicious
Yes
Categories
  • malware

Registration record

Registrar
Cloudflare, Inc.
Registered
Updated
Expires
Nameservers
  • brad.ns.cloudflare.com
  • meilani.ns.cloudflare.com
Original source fields · JSON
Uuid
bce63fca-f99f-4975-bd82-33222105df2c
Final url
https://eobuwie.tiendasmgises.com/
Status
200
History
[
    {
        "url": "https://eobuwie.tiendasmgises.com/",
        "status": 200
    }
]
DOM structure hash
b2d055e26983bd530aae4b55a2ba97c39045afd4c4b58a75aded9f638bd83b14
Document hash
e9a6b69eb79239c87ce4f7bc199cd7f945d0760a88ad8161f45799f58ec91432
Phishing v2
[
    "phishing"
]
Domain risks
[
    "Malware",
    "Security threats",
    "CIPA Filter",
    "CIPA"
]
Radar rank
{
    "bucket": ">200000"
}
DNS records
[
    {
        "name": "eobuwie.tiendasmgises.com",
        "type": "A",
        "value": "104.21.41.77"
    },
    {
        "name": "eobuwie.tiendasmgises.com",
        "type": "A",
        "value": "172.67.162.15"
    },
    {
        "name": "eobuwie.tiendasmgises.com",
        "type": "AAAA",
        "value": "2606:4700:3032::6815:294d"
    },
    {
        "name": "eobuwie.tiendasmgises.com",
        "type": "AAAA",
        "value": "2606:4700:3036::ac43:a20f"
    }
]
Dnssec valid
false
Ip
104.21.41.77
Verdict
{
    "tags": [
        "malware"
    ],
    "malicious": true,
    "categories": [
        "malware"
    ]
}
Registration record
{
    "registrar": "Cloudflare, Inc.",
    "created": "2026-08-28T06:24:19Z",
    "updated": "2026-08-28T06:24:19Z",
    "expires": "2027-08-28T06:24:19Z",
    "nameservers": [
        "brad.ns.cloudflare.com",
        "meilani.ns.cloudflare.com"
    ]
}
Separate stored summary: Not recorded · observation date not recorded

This summary differs from the dated scan above. It is retained for provenance and does not override the selected source observation.

verdict
null
categories
[]
observed_at
null
source_path
phishdestroy.technologies.cf_radar
scope
Separate stored summary; an absent observation date is not evidence of a clean scan.

Spamhaus DBL

phishing domain

URLScan

Malicious · engine verdict · score 81

Open report
URLScanOriginal source recordObserved: 18 fields

Observed: · Retrieved:

Report ID

01a17477-e2a2-705b-9401-5364dfc37d3a

Final URL

https://eobuwie.tiendasmgises.com/

HTTP response

200

Redirect type

https-only

Redirects

  • To
    https://eobuwie.tiendasmgises.com/
    From
    http://eobuwie.tiendasmgises.com/
    Status
    307

IP address

2a06:98c1:3121::3

Contacted IP addresses

  • 2a06:98c1:3121::3

Autonomous systems (ASN)

  • 13335

Document hash

6c5d74593398868b7285edba64f53c5db909a6fd2cf4052b5a617609d3b62b5d

Cookies

  • __cf_bm

TLS session and certificate

Subject alternative names
  • eobuwie.tiendasmgises.com
Cipher
AES_128_GCM
Issuer
WE1
Subject
eobuwie.tiendasmgises.com
Protocol
TLS 1.3
Valid until
Valid from

Domain age, days

34

Registered domain age, days

58

Certificate age, days

34

Certificate validity, days

90

Page requests

2

Provider verdicts

Engine verdict
Tags
  • urlscan-ml
  • urlscan-ml-60c5e22
Score
81
Malicious
Yes
Overall verdict
Score
0
Malicious
No

HTTP headers

Server
cloudflare
Content-type
text/html; charset=utf-8
Original source fields · JSON
Uuid
01a17477-e2a2-705b-9401-5364dfc37d3a
Final url
https://eobuwie.tiendasmgises.com/
Status
200
Redirected
https-only
Redirects
[
    {
        "to": "https://eobuwie.tiendasmgises.com/",
        "from": "http://eobuwie.tiendasmgises.com/",
        "status": 307
    }
]
Ip
2a06:98c1:3121::3
Contacted IP addresses
[
    "2a06:98c1:3121::3"
]
Asns
[
    "13335"
]
Document hash
6c5d74593398868b7285edba64f53c5db909a6fd2cf4052b5a617609d3b62b5d
Cookies
[
    "__cf_bm"
]
Tls
{
    "san": [
        "eobuwie.tiendasmgises.com"
    ],
    "cipher": "AES_128_GCM",
    "issuer": "WE1",
    "subject": "eobuwie.tiendasmgises.com",
    "protocol": "TLS 1.3",
    "valid_to": "2026-12-20T09:50:06Z",
    "valid_from": "2026-09-21T08:50:10Z"
}
Domain age days
34
Apex age days
58
Tls age days
34
Tls valid days
90
Requests
2
Provider verdicts
{
    "engines": {
        "tags": [
            "urlscan-ml",
            "urlscan-ml-60c5e22"
        ],
        "score": 81,
        "malicious": true
    },
    "overall": {
        "score": 0,
        "malicious": false
    }
}
HTTP headers
{
    "server": "cloudflare",
    "content-type": "text/html; charset=utf-8"
}

OTX

no community references

Open report

Google Safe Browsing

No threat flag

Open report

PhishDestroy DOM

0 / 100 · heuristic score · 0 brand references · 0 classifications

Open report

PhishDestroy narrative

Narrative generation metadata

Open report
Title, description and generation record

The narrative generation date is separate from observation dates. These are the retained publication fields, not an additional independent detection.

ai_title
eobuwie.tiendasmgises.com — Suspicious Domain
ai_description
PhishDestroy flags eobuwie.tiendasmgises.com as a suspicious domain after multiple security detections and a Cloudflare challenge prevented content review.
ai_generated_at
2026-10-25T19:08:17Z
ai_generated_by
threat-v3-groq
interpretation
Narrative generation metadata, separate from provider observation dates.

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Collected source details

Stored page, network and scanner observations, grouped by source and observation time.

Every stored field, with its source and date
Website checksOriginal source recordRetrieved: 25 fields

CAA records

Domain
eobuwie.tiendasmgises.com

Protective DNS results

Resolvers checked
12
Blocked by
  • CloudFlare Family
Blocking resolvers
1

Web archive observations

Last observation
First observation
Recorded changes
0
Archived days
1
Average page size, bytes
143181

Crawler rules

User agents
  • *
Present
Yes

Page title and metadata

Open Graph URL
https://eobuwie.tiendasmgises.com
Page title
Sklep internetowy eobuwie.pl • Modne buty, akcesoria i ...
Open Graph type
website
Open Graph title
Sklep internetowy eobuwie.pl • Modne buty, akcesoria i ...
Keywords
Sklep internetowy eobuwie.pl • Modne buty,akcesoria i ...
Open Graph site name
eobuwie-PL
Description
Sklep internetowy eobuwie.pl • Modne buty, akcesoria i ...
Twitter card
summary_large_image
Twitter account
https://eobuwie.tiendasmgises.com
Canonical URL
https://eobuwie.tiendasmgises.com
Open Graph description
Sklep internetowy eobuwie.pl • Modne buty, akcesoria i ...

Trackers

Requests
99
Observed services
  • Name
    Facebook
    Company
    Meta
    Country
    US
    Category
    Advertising
    Requests
    13
  • Name
    Google Translate
    Company
    Google
    Country
    US
    Category
    Customer Interaction
    Requests
    1
  • Name
    Google APIs
    Company
    Google
    Country
    US
    Category
    Hosting
    Requests
    1
  • Name
    Google Static
    Company
    Google
    Country
    US
    Category
    Hosting
    Requests
    4
  • Name
    Facebook Connect
    Company
    Meta
    Country
    US
    Category
    Site Analytics
    Requests
    13
  • Name
    TikTok Analytics
    Company
    ByteDance Inc
    Country
    KY
    Category
    Site Analytics
    Requests
    46

Forms and mixed content

Third-party scripts
0

HTTP response

Reachable
Yes
HTTP status
200
Request timings, ms
DNS
6
TLS
32
Waiting
387
Connection
8
Download
443
Response time, ms
876

TLS connection

ALPN
h2
Cipher
TLS_AES_256_GCM_SHA384
Protocol
TLSv1.3
Supported versions
  • TLSv1.2
  • TLSv1.3
Certificate authorized
Yes
Forward secrecy
Yes

Ports

Open ports
  • 80
  • 443
  • 8080

Carbon estimate

Bytes
918638
CO₂, grams
0.0336
Cleaner than, %
1

DNS servers

Nameservers
  • IP address
    108.162.194.196
    Host
    meilani.ns.cloudflare.com
  • IP address
    172.64.33.105
    Host
    brad.ns.cloudflare.com
DNS zone
tiendasmgises.com

Cookies

Cookies
  • Name
    _fbp
  • Name
    _abeiia_vid
  • Name
    _abeiia_cvid
  • Name
    _abeiia_vs
  • Name
    utm_source
  • Name
    utm_medium
  • Name
    order_utm_history
  • Name
    landing_page
  • Name
    _abeiia_ka
  • Name
    first_http_referer
  • Name
    first_visit_time
  • Name
    currency_code
    Session cookie
    Yes
  • Name
    PHPSESSID
    Session cookie
    Yes
  • Name
    __cf_bm
    Secure
    Yes
    HTTP-only
    Yes
    SameSite
    None
  • Name
    _EBFCI_ua
    Secure
    Yes
    SameSite
    None
  • Name
    _EBFCI_pu
    Secure
    Yes
    SameSite
    None
  • Name
    _EBFCI_tz
    Secure
    Yes
    SameSite
    None
  • Name
    _EBFCI_ss
    Secure
    Yes
    SameSite
    None
  • Name
    _EBFCI_lang
    Secure
    Yes
    SameSite
    None
  • Name
    _EBFCI_vs
    Secure
    Yes
    SameSite
    None

Location

IP address
2a06:98c1:3120::3
ASN
13335
Organization
CloudFLARENET-EU
City
London
Country
GB

TLS certificate

Issuer
Google Trust Services / WE1
Subject
eobuwie.tiendasmgises.com

DNS records

A
  • 188.114.97.3
  • 188.114.96.3
AAAA
  • 2a06:98c1:3121::3
  • 2a06:98c1:3120::3

DNSSEC

DS record
No
RRSIG
No
DNSKEY
No

HSTS

Observation
Site does not serve any HSTS headers.

HTTP security policies

X-Frame-Options
No
Referrer-Policy
No
X-XSS-Protection
No
Permissions-Policy
No
X-Content-Type-Options
No
Content-Security-Policy
No
Strict-Transport-Security
No
Cross-Origin-Opener-Policy
No
Cross-Origin-Embedder-Policy
No
Cross-Origin-Resource-Policy
No

Web application firewall

WAF product
Cloudflare
WAF detected
Yes

IP lookup

IP address
2a06:98c1:3120::3
IP version
6

Redirects

Redirect chain
  • https://eobuwie.tiendasmgises.com

Page links

External link addresses
  • https://www.facebook.com/
  • https://www.twitter.com/
  • https://www.pinterest.com/
External links
3
Internal links
281

Registration record

Registrar
Cloudflare, Inc.
Registered
Updated
Expires
Status
  • clientTransferProhibited https://icann.org/epp
Nameservers
  • brad.ns.cloudflare.com
  • meilani.ns.cloudflare.com

HTTP headers

Response headers
Server
cloudflare
Content-type
text/html; charset=utf-8
Original source fields · JSON
Caa records
{
    "domain": "eobuwie.tiendasmgises.com"
}
Protective DNS results
{
    "resolvers": 12,
    "blocked_by": [
        "CloudFlare Family"
    ],
    "blocked_count": 1
}
Web archive observations
{
    "last": "2026-10-25T19:05:27Z",
    "first": "2026-10-25T19:05:27Z",
    "changes": 0,
    "days_archived": 1,
    "avg_page_bytes": 143181
}
Crawler rules
{
    "agents": [
        "*"
    ],
    "present": true
}
Page title and metadata
{
    "ogUrl": "https://eobuwie.tiendasmgises.com",
    "title": "Sklep internetowy eobuwie.pl • Modne buty, akcesoria i ...",
    "ogType": "website",
    "ogTitle": "Sklep internetowy eobuwie.pl • Modne buty, akcesoria i ...",
    "keywords": "Sklep internetowy eobuwie.pl • Modne buty,akcesoria i ...",
    "ogSiteName": "eobuwie-PL",
    "description": "Sklep internetowy eobuwie.pl • Modne buty, akcesoria i ...",
    "twitterCard": "summary_large_image",
    "twitterSite": "https://eobuwie.tiendasmgises.com",
    "canonicalUrl": "https://eobuwie.tiendasmgises.com",
    "ogDescription": "Sklep internetowy eobuwie.pl • Modne buty, akcesoria i ..."
}
Trackers
{
    "requests": 99,
    "trackers": [
        {
            "name": "Facebook",
            "company": "Meta",
            "country": "US",
            "category": "Advertising",
            "requests": 13
        },
        {
            "name": "Google Translate",
            "company": "Google",
            "country": "US",
            "category": "Customer Interaction",
            "requests": 1
        },
        {
            "name": "Google APIs",
            "company": "Google",
            "country": "US",
            "category": "Hosting",
            "requests": 1
        },
        {
            "name": "Google Static",
            "company": "Google",
            "country": "US",
            "category": "Hosting",
            "requests": 4
        },
        {
            "name": "Facebook Connect",
            "company": "Meta",
            "country": "US",
            "category": "Site Analytics",
            "requests": 13
        },
        {
            "name": "TikTok Analytics",
            "company": "ByteDance Inc",
            "country": "KY",
            "category": "Site Analytics",
            "requests": 46
        }
    ]
}
Forms and mixed content
{
    "third_party_scripts": 0
}
Status
{
    "up": true,
    "code": 200,
    "timings": {
        "dns": 6,
        "tls": 32,
        "wait": 387,
        "connect": 8,
        "download": 443
    },
    "response_ms": 876
}
TLS connection
{
    "alpn": "h2",
    "cipher": "TLS_AES_256_GCM_SHA384",
    "protocol": "TLSv1.3",
    "versions": [
        "TLSv1.2",
        "TLSv1.3"
    ],
    "authorized": true,
    "forward_secrecy": true
}
Ports
{
    "open": [
        80,
        443,
        8080
    ]
}
Carbon
{
    "bytes": 918638,
    "co2_grams": 0.0336,
    "cleaner_than": 1
}
Dns server
{
    "ns": [
        {
            "ip": "108.162.194.196",
            "host": "meilani.ns.cloudflare.com"
        },
        {
            "ip": "172.64.33.105",
            "host": "brad.ns.cloudflare.com"
        }
    ],
    "zone": "tiendasmgises.com"
}
Cookies
{
    "cookies": [
        {
            "name": "_fbp"
        },
        {
            "name": "_abeiia_vid"
        },
        {
            "name": "_abeiia_cvid"
        },
        {
            "name": "_abeiia_vs"
        },
        {
            "name": "utm_source"
        },
        {
            "name": "utm_medium"
        },
        {
            "name": "order_utm_history"
        },
        {
            "name": "landing_page"
        },
        {
            "name": "_abeiia_ka"
        },
        {
            "name": "first_http_referer"
        },
        {
            "name": "first_visit_time"
        },
        {
            "name": "currency_code",
            "session": true
        },
        {
            "name": "PHPSESSID",
            "session": true
        },
        {
            "name": "__cf_bm",
            "secure": true,
            "http_only": true,
            "same_site": "None"
        },
        {
            "name": "_EBFCI_ua",
            "secure": true,
            "same_site": "None"
        },
        {
            "name": "_EBFCI_pu",
            "secure": true,
            "same_site": "None"
        },
        {
            "name": "_EBFCI_tz",
            "secure": true,
            "same_site": "None"
        },
        {
            "name": "_EBFCI_ss",
            "secure": true,
            "same_site": "None"
        },
        {
            "name": "_EBFCI_lang",
            "secure": true,
            "same_site": "None"
        },
        {
            "name": "_EBFCI_vs",
            "secure": true,
            "same_site": "None"
        }
    ]
}
Location
{
    "ip": "2a06:98c1:3120::3",
    "asn": "13335",
    "org": "CloudFLARENET-EU",
    "city": "London",
    "country": "GB"
}
Ssl
{
    "issuer": "Google Trust Services / WE1",
    "subject": "eobuwie.tiendasmgises.com"
}
DNS records
{
    "A": [
        "188.114.97.3",
        "188.114.96.3"
    ],
    "AAAA": [
        "2a06:98c1:3121::3",
        "2a06:98c1:3120::3"
    ]
}
Dnssec
{
    "ds": false,
    "rrsig": false,
    "dnskey": false
}
Hsts
{
    "message": "Site does not serve any HSTS headers."
}
HTTP security policies
{
    "xFrameOptions": false,
    "referrerPolicy": false,
    "xXSSProtection": false,
    "permissionsPolicy": false,
    "xContentTypeOptions": false,
    "contentSecurityPolicy": false,
    "strictTransportPolicy": false,
    "crossOriginOpenerPolicy": false,
    "crossOriginEmbedderPolicy": false,
    "crossOriginResourcePolicy": false
}
Firewall
{
    "waf": "Cloudflare",
    "has_waf": true
}
Get ip
{
    "ip": "2a06:98c1:3120::3",
    "family": 6
}
Redirects
{
    "chain": [
        "https://eobuwie.tiendasmgises.com"
    ]
}
Page links
{
    "external": [
        "https://www.facebook.com/",
        "https://www.twitter.com/",
        "https://www.pinterest.com/"
    ],
    "external_count": 3,
    "internal_count": 281
}
Registration record
{
    "registrar": "Cloudflare, Inc.",
    "created": "2026-08-28T06:24:19Z",
    "updated": "2026-08-28T06:24:19Z",
    "expires": "2027-08-28T06:24:19Z",
    "status": [
        "clientTransferProhibited https://icann.org/epp"
    ],
    "nameservers": [
        "brad.ns.cloudflare.com",
        "meilani.ns.cloudflare.com"
    ]
}
HTTP headers
{
    "headers": {
        "server": "cloudflare",
        "content-type": "text/html; charset=utf-8"
    }
}

Questions about eobuwie.tiendasmgises.com

Is eobuwie.tiendasmgises.com legit?

No. PhishDestroy classifies eobuwie.tiendasmgises.com as a phishing page (risk: critical, 100/100); it was first detected on 2026-10-25. VirusTotal: 14/92 engines flag it. Listed on Spamhaus DBL. Treat the site as unsafe.

Is eobuwie.tiendasmgises.com safe to connect a wallet?

No. Do not connect a wallet, sign messages or approve tokens on eobuwie.tiendasmgises.com. Phishing sites ask for approvals (approve, setApprovalForAll, Permit2) that let the operator move your assets, and a confirmed transaction cannot be reversed.

What should I do if I used eobuwie.tiendasmgises.com?

Change every password you entered there and turn on two-factor authentication. If you connected a wallet or signed something, revoke the approvals and move the remaining funds to a new wallet; never share your seed phrase. Step-by-step help: emergency guide.

Explore

Blocklist matchesPhishDestroy 1
PhishDestroy PhishDestroy list View source

Stored Capture · 5 captures

All capture links and hashes (5)

Domain details

Domain
IP Context Cloudflare shared edge origin IP hidden Edge-IP reputation is not attributed to this domain.
Registrar (base domain) Cloudflare US(US)
Registration (base domain)tiendasmgises.com · Created Aug 28, 2026 (58d · New) — Expires Aug 28, 2027
HTTP Status200
Technical detailsProvenance & timestamps
First DetectedOct 25, 2026
DOM Analysisanalyzed Oct 25, 2026score 0/100
Submitted URLhttp://eobuwie.tiendasmgises.com/
Favicon Hash
Observed page title
500 Internal Server Error
TLS Certificate
Issued by Google Trust Services / WE1 · stored validity ends in 55 days

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
188.114.96.3
Network ASN
AS13335
Organization
CloudFLARENET-EU
Observed location
London, GB
Server header
cloudflare

Edge-IP reputation is not attributed to this domain.

Nameservers 2

  • brad.ns.cloudflare.com
  • meilani.ns.cloudflare.com

Location describes the IP network.

TLS certificate

Issuer
Google Trust Services / WE1
Valid from
2026-09-21 08:50:10
Valid until
2026-12-20 09:50:06
Hostname coverage
Stored certificate dates valid
Validity
Within stored validity dates
Collection source
PhishDestroy collector
Certificate fingerprinta347c192fabba5e114e61356ca85a82d3cf7e1d81f17e5022dc0a66411a1af43
Certificate names · 1 SAN
  • eobuwie.tiendasmgises.com

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Report This Domain Submit evidence & help protect others

VirusTotal Analysis

14 / 92 security vendors flagged this domain
View on VT
Last analyzed
alphaMountain.ai
BitDefender
CRDF
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
Lionic
Netcraft
SOCRadar
Sophos
VIPRE

Archived Evidence

Wayback Machine Snapshot
View Archive
Site Performance Analysis

Google PageSpeed Insights — mobile performance audit of eobuwie.tiendasmgises.com · checked Oct 25, 2026

100
Good
Performance
FCP
0.76 s
First Contentful Paint
LCP
0.76 s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0 ms
Total Blocking Time
SI
0.76 s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Stored Capture Evidence 1 snapshot

Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.

Archived HTTP response HTTP 403
Requested URL: http://eobuwie.tiendasmgises.com/
Just a moment...
Response
HTTP 403
HTML body
5.6 KB
Compressed
3.3 KB
Links
0 internal · 0 external
Detected technologies
cloudflare
Selected response headers
Content-Type: text/html; charset=UTF-8
CF-Mitigated: challenge
Server: cloudflare
Content-Encoding: gzip
Security headers present
Content-Security-PolicyX-Frame-OptionsX-Content-Type-OptionsReferrer-PolicyPermissions-PolicyCross-Origin-Opener-PolicyCross-Origin-Resource-Policy
HSTS: not observed DNSSEC: not observed WAF / firewall: observed Cloaking flag: not observed
Saved response-header values · 20
Accept-Ch
Sec-CH-UA-Bitness, Sec-CH-UA-Arch, Sec-CH-UA-Full-Version, Sec-CH-UA-Mobile, Sec-CH-UA-Model, Sec-CH-UA-Platform-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Platform, Sec-CH-UA, UA-Bitness, UA-Arch, UA-Full-Version, UA-Mobile, UA-Model,
Cf-Mitigated
challenge
CF-RAY
a5037ead0dc5e5b3-YYZ
Connection
close
Content-Encoding
gzip
Content-Security-Policy
default-src 'none'; script-src 'nonce-ylnq1BigYa5sQQRKeVW0CG' 'unsafe-eval' https://challenges.cloudflare.com; script-src-attr 'none'; style-src 'unsafe-inline'; img-src 'self' https://challenges.cloudflare.com; connect-src 'self' https://challenges.cloudflare.com; frame-src 'self' https://challenges.cloudflare.com blo
Content-Type
text/html; charset=UTF-8
Critical-Ch
Sec-CH-UA-Bitness, Sec-CH-UA-Arch, Sec-CH-UA-Full-Version, Sec-CH-UA-Mobile, Sec-CH-UA-Model, Sec-CH-UA-Platform-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Platform, Sec-CH-UA, UA-Bitness, UA-Arch, UA-Full-Version, UA-Mobile, UA-Model,
Cross-Origin-Embedder-Policy
require-corp
Cross-Origin-Opener-Policy
same-origin
Cross-Origin-Resource-Policy
same-origin
Date
Sun, 25 Oct 2026 19:05:48 GMT
Origin-Agent-Cluster
?1
Permissions-Policy
accelerometer=(),camera=(),clipboard-read=(),clipboard-write=(),geolocation=(),gyroscope=(),hid=(),magnetometer=(),microphone=(),payment=(),publickey-credentials-get=(),screen-wake-lock=(),serial=(),sync-xhr=(),usb=(),xr-spatial-tracking=*
Referrer-Policy
same-origin
Server
cloudflare
Server-Timing
chlray;desc="a5037ead0dc5e5b3"
Transfer-Encoding
chunked
X-Content-Type-Options
nosniff
X-Frame-Options
SAMEORIGIN

Values retained by the collector; long values may be shortened during collection.

All retained availability observations3

Source: availability monitor. Every retained observation remains separate, including records with the same date or evidence hash but different sources or DNS states. An unknown state is not proof that the site is offline.

  1. current_state_backfillunknown
    Observation source
    current_state_backfill
    Cause
    http_2xx_unclassified
    Availability state
    unknown
    Content state
    unknown
    DNS state
    stale
    Recorded HTTP status
    200
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    40
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    Original source timestamp
    2026-10-25 20:11:29.000000
    Evidence SHA-256
    cd5d3c5f65e3aaa7d01aa37ca99845c94e20548063c297c82af6231381544446
    HTTP probe value as recorded
    200
    Evidence timestamp as recorded
    2026-10-25 20:11:29
    Evidence reason
  2. http_observationunknown
    Observation source
    http_observation
    Cause
    http_2xx_unclassified
    Availability state
    unknown
    Content state
    unknown
    DNS state
    unknown
    Recorded HTTP status
    200
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    40
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    Original source timestamp
    2026-10-25 20:11:29.000000
    Evidence SHA-256
    cd5d3c5f65e3aaa7d01aa37ca99845c94e20548063c297c82af6231381544446
    HTTP probe value as recorded
    200
    Evidence timestamp as recorded
    2026-10-25 20:11:29
    Evidence reason
  3. current_state_backfillunknown
    Observation source
    current_state_backfill
    Cause
    stale_current_evidence
    Availability state
    unknown
    Content state
    unknown
    DNS state
    stale
    Recorded HTTP status
    200
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    0
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    Original source timestamp
    2026-10-25 20:09:00.170073
    Evidence SHA-256
    f3049ef8aa957a0c75d1f37b703ae6008630522768f5aca88bbd9915c9e1400b
    DNS evidence marked stale
    true
    HTTP evidence marked stale
    true

Recorded activity

5 entries
  1. URLScan

    Page captured

    View source
  2. Cloudflare Radar

    Phishing

    View source
  3. VirusTotal

    14/92 engine detections

    View source
  4. Wayback Machine

    Page archived

    View source
  5. Added to PhishDestroy

    eobuwie.tiendasmgises.com

    View source
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

eobuwie.tiendasmgises.com

Evidence & External Reports

Deep Analysis
Help & reporting

Were You Affected by This Site?

3 evidence signal groups linked Last known active
You are not alone and there is nothing to be ashamed of. Scammers are sophisticated criminals who exploit trust. Reporting your experience is the most powerful weapon against fraud — your report can prevent others from becoming victims and help law enforcement take action. Silence is the scammer’s greatest advantage. Break it.
If credentials were compromised, report immediately. Do not engage with recovery scammers.

If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Official reporting routes

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

97-country directory

Template-based draft • optional AI wording assistance requires separate consent

Review and submit it yourself
After a phishing incident

Recommendations & Advice for Victims

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

What should I do immediately?

Urgent

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • Change all passwords — email, exchange accounts, anything that shares the same password
  • Enable 2FA using an authenticator app (not SMS). Disable SMS-based recovery
  • Freeze cards if you entered banking details on the phishing site

What information should I collect for my report?

FBI guidelines

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • Exact dates & times — of each transaction and first contact with scammer
  • Screenshots — scam website, chat messages, emails, wallet transactions, social media
  • All URLs & domains used by the scammer (including eobuwie.tiendasmgises.com)
  • Communications — emails, texts, phone numbers, usernames the scammer used

Even if you don't have all details — file a report anyway. Partial information still helps investigations.

Where should I report the scam?

  • FBI IC3 — Internet Crime Complaint Center (US federal reporting)
  • Europol — European cybercrime reporting (EU)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • Local police — creates an official record, even if they can't act immediately

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • Fake websites — pixel-perfect clones of legitimate sites with slightly altered domains
  • Pig butchering — trust built over weeks via Telegram/WhatsApp/dating apps, then money stolen
  • Recovery scams — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • AI-powered scams — deepfakes, automated phishing, and AI-generated sites making fraud harder to detect

How can I protect myself in the future?

  • Bookmark official sites — never click links from emails, DMs, or ads
  • Verify domains — check on PhishDestroy before interacting. Check HTTPS, spelling, domain age
  • "Too good to be true" = scam — guaranteed returns, celebrity endorsements, urgent deadlines

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive

Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/eobuwie.tiendasmgises.com"
  title="PhishDestroy threat report for eobuwie.tiendasmgises.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>