VirusTotal
6 / 92 engine detections
Open report

bombstore.shop is a phishing page detected by PhishDestroy on 2026-10-22. Risk: critical (88/100). Registrar: Dynadot. Status: Last known active. Hosting: Malakmadze Web LLC. PhishDestroy sent 1 abuse report. VirusTotal: 6/92 engines flag it. Do not enter credentials or connect a wallet.
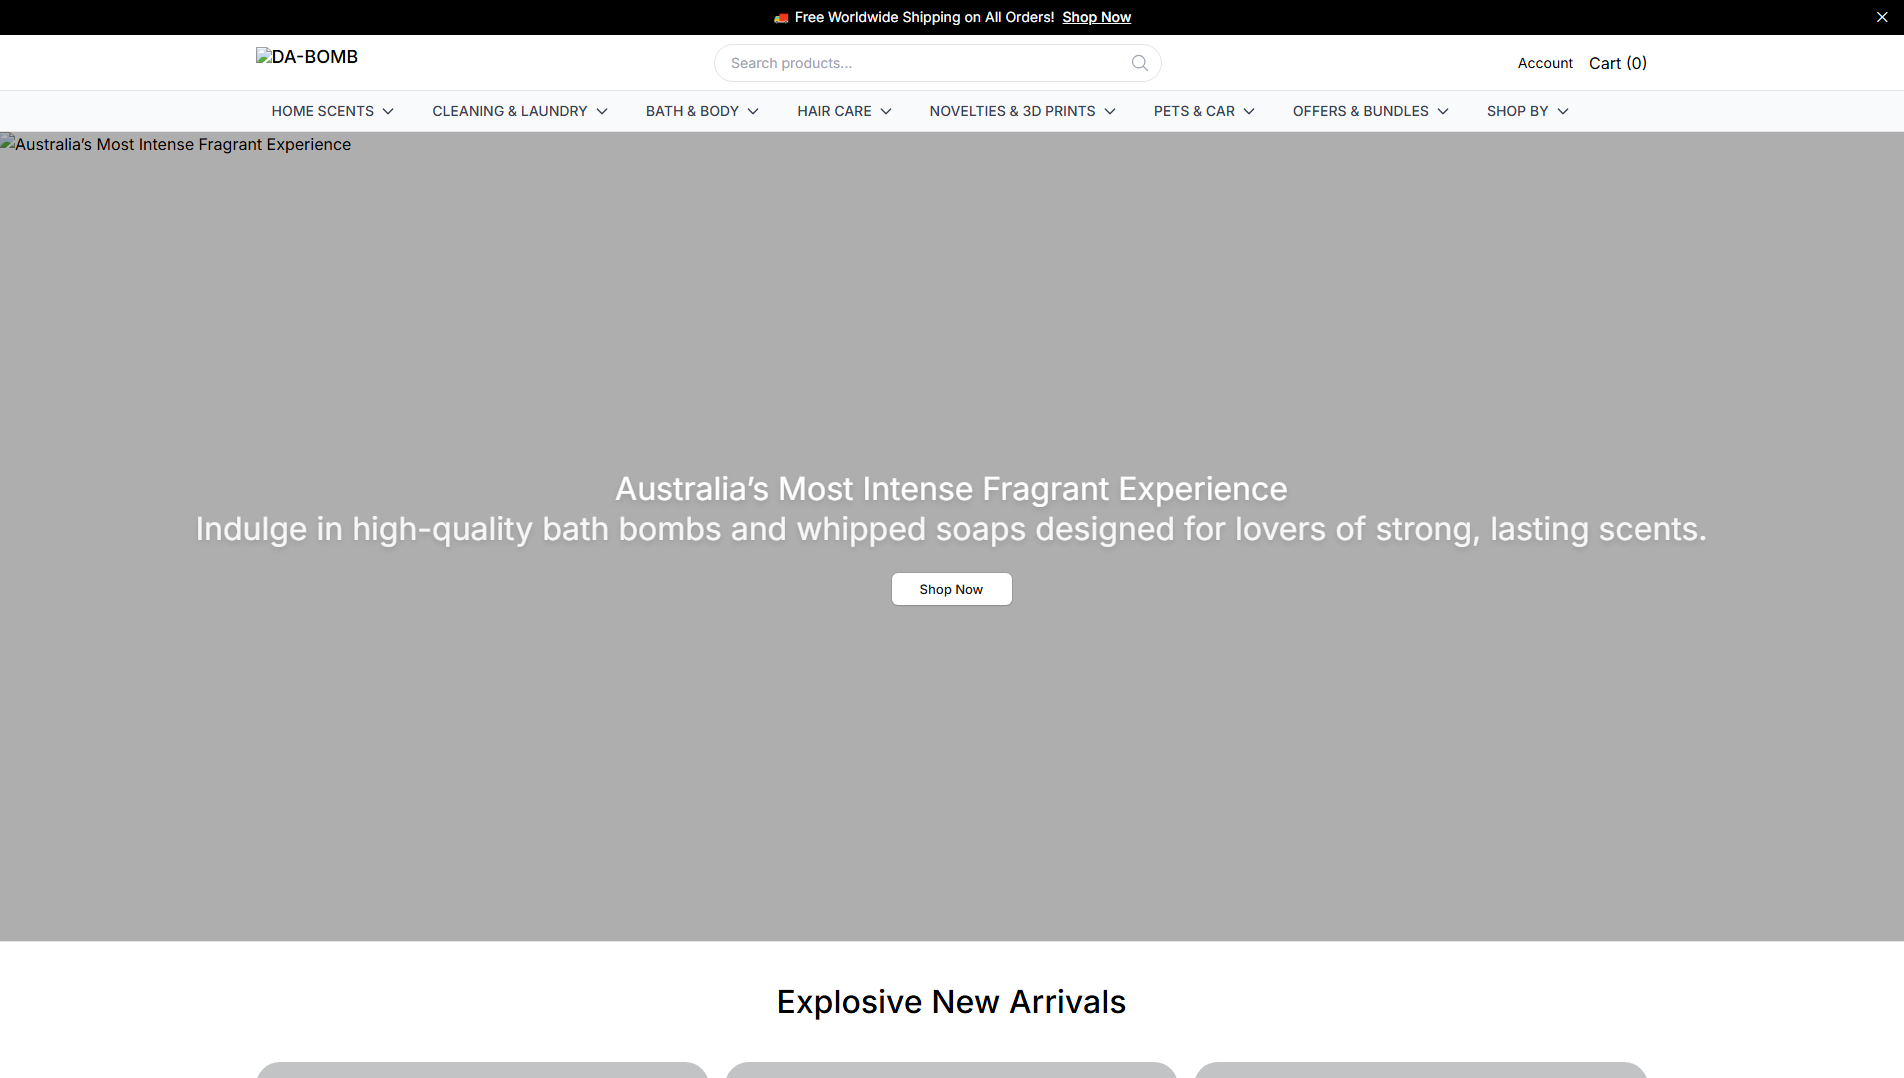
“DA-BOMB | Specialists in Bath Bombs & Whipped Soap | DA-BOMB”
6 / 92 engine detections
Open reportMalicious
Open reportScan report
Open report4 community references
Open reportprovider verdict: clean
Open reportNo threat flag
Open reportResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
PhishDestroy added bombstore.shop to its internal blocklist after the domain was first observed on 2026-10-22. The recorded page title reads “DA‑BOMB | Specialists in Bath Bombs & Whipped Soap | DA‑BOMB”. An HTTP 307 redirect forces HTTPS, and the final response returned a 200 status code on the same day.
The detections label the site as a phishing or fake‑shop page that could attempt to lure visitors into providing personal or payment details. No specific credential‑stealing form or malicious payload was captured in the snapshot, so the exact technique remains unconfirmed beyond the generic phishing risk.
VirusTotal (2026-10-22) reported 6 detections: 4 malicious (CRDF, G‑Data, Netcraft, LevelBlue) and 2 suspicious (Gridinsoft, alphaMountain.ai) out of 92 engines. Google Safe Browsing (2026-10-22) did not flag the domain. urlscan.io (2026-10-22) gave a malicious verdict with a score of 100, categorising it as phishing and labeling it a fake shop. OTX listed 4 pulses referencing the domain. No external blocklists reported the domain, but PhishDestroy’s internal list marks it as blocked.
The domain was registered with Dynadot Inc. on 2026-04-17. The recorded IP was 162.222.90.62 and the hosting organization was listed as Malakmadze Web LLC in Georgia. DNS is served by Cloudflare (lana.ns.cloudflare.com, bradley.ns.cloudflare.com). TLS uses a Let’s Encrypt certificate issued on 2026-10-13, valid until 2027-01-11. Open ports observed include 22, 80, 443 and 8000.
Visitors should avoid entering any personal, login or payment information on the site and, if they have already done so, change passwords on affected accounts and monitor for unauthorized activity. Defenders should block bombstore.shop at the network perimeter, log any connections to 162.222.90.62, and add the domain to local blocklists to prevent future access.
Stored page, network and scanner observations, grouped by source and observation time.
Observed: · Retrieved:
| Uuid | 01a16145-6401-72fa-b0f1-cf24044deaa6 |
|---|---|
| Final url | https://bombstore.shop/ |
| Status | 200 |
| Redirected | https-only |
| Redirects | [
{
"to": "https://bombstore.shop/",
"from": "http://bombstore.shop/",
"status": 307
}
] |
| Ip | 162.222.90.62 |
| Contacted domains | [
"placehold.co",
"fonts.gstatic.com",
"fonts.googleapis.com"
] |
| Contacted IP addresses | [
"188.114.96.3",
"142.251.20.94",
"2a00:1450:4001:c15::5f",
"162.222.90.62"
] |
| Asns | [
"13335",
"15169",
"199242"
] |
| Countries | [
"US",
"DE",
"GE"
] |
| Document hash | 041e20fdce259285336666e514630f8ace2dfa76d23324f8d4eb6cef6e84f242 |
| Script hashes | [
"dbaf5f84a9a85c20a55c7bdcc2f36019b3e083d6ec67029cde72be85375ce13a",
"da1c9803523e7a18f5f93419f7dbf9cab702b5a78564eb9dc0e18c32e492ae4f",
"56bef185cd5d43be7d55db75e9756858e8a4093525595194b8d3202210013efe",
"2d9ed79eb6d7a824a49129543fe8712e46fdc8f048e145692492d81f589f33b5",
"5790cd3ddf6d13150fad9403a3be5269f8bb5c8905966746bca6929477b611e0",
"9de785ee19ccdf688f837e8bf8d2bbdb4c1dabc04b8ee7166bc1f4057226e49d",
"91eb4c6e12d5d0f37080b53c6a8b513c579db4854839928eb478164ef6dc1d65",
"acfed8ce931532ba4fbcdbc534468ab16b1e4ab08c8f8b9859558b9fbfc86d3e",
"54674023c15e7c7d2c117eacd9399f7e7ff4a224093be6fbd07fba4480b882ba",
"ef598e4df04d2d336c9267057130a0ab7a499d928810f0bceb6393f28a5fcb03"
] |
| Globals | [
"__next_f",
"webpackChunk_N_E",
"next",
"_N_E_STYLE_LOAD",
"Prism"
] |
| Cookies | [
"_pkh_cid",
"_pkh_rg",
"_pkh_rid",
"_site_domain"
] |
| Storage keys | [
"analytics_session_id",
"analytics_session_id_ts",
"__analytics_utm__",
"analytics_visitor_id"
] |
| Tls | {
"san": [
"bombstore.shop"
],
"cipher": "AES_128_GCM",
"issuer": "YE2",
"subject": "bombstore.shop",
"protocol": "TLS 1.3",
"valid_to": "2027-01-11T08:44:09Z",
"valid_from": "2026-10-13T08:44:10Z"
} |
| Domain age days | 1121 |
| Apex age days | 1121 |
| Tls age days | 8 |
| Tls valid days | 89 |
| Requests | 53 |
| Provider verdicts | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-60c5e22"
],
"score": 86,
"malicious": true
},
"overall": {
"tags": [
"phishing"
],
"score": 100,
"brands": [
"fakeshop"
],
"malicious": true,
"categories": [
"phishing"
]
},
"urlscan": {
"tags": [
"phishing"
],
"score": 100,
"brands": [
"Fake Shop"
],
"malicious": true,
"categories": [
"phishing"
]
}
} |
| HTTP headers | {
"content-type": "text/html; charset=utf-8",
"x-frame-options": "SAMEORIGIN",
"x-content-type-options": "nosniff",
"referrer-policy": "strict-origin-when-cross-origin"
} |
Observed: · Retrieved:
| Uuid | bf4bec43-f3f2-403b-b24a-bb97ed84fe3e |
|---|---|
| Final url | https://bombstore.shop/ |
| Status | 200 |
| History | [
{
"url": "https://bombstore.shop/",
"status": 200
}
] |
| DOM structure hash | 77cb9ef359b7af7e047e83b6ed6b0f64213c14990dc330de62f0218e95a28e62 |
| Document hash | 5a42699568b4f8c81a98996bed73fa1ef99e56bfc74c1ad1a4a1143b37f28612 |
| Radar rank | {
"bucket": ">200000"
} |
| DNS records | [
{
"name": "bombstore.shop",
"type": "A",
"value": "162.222.90.62"
}
] |
| Dnssec valid | false |
| Ip | 162.222.90.62 |
Observed: · Retrieved:
| Vendor result counts | {
"timeout": 0,
"harmless": 52,
"malicious": 4,
"suspicious": 2,
"undetected": 34
} |
|---|---|
| Vendor labels | {
"CRDF": "malicious",
"G-Data": "malware",
"Netcraft": "malicious",
"LevelBlue": "phishing",
"Gridinsoft": "suspicious",
"alphaMountain.ai": "suspicious"
} |
| Reputation | 0 |
| Created | 2026-04-17T00:00:00Z |
| Updated | 2026-04-17T00:00:00Z |
| First seen | 2024-03-05T06:36:43Z |
| DNS records | [
{
"ttl": 21600,
"type": "NS",
"value": "lana.ns.cloudflare.com"
},
{
"ttl": 300,
"type": "A",
"value": "162.222.90.62"
},
{
"ttl": 21600,
"type": "NS",
"value": "bradley.ns.cloudflare.com"
},
{
"ttl": 1800,
"type": "SOA",
"rname": "dns.cloudflare.com",
"value": "bradley.ns.cloudflare.com"
}
] |
| Dns at | 2026-10-22T02:23:55Z |
| Jarm | 40d40d40d00000000043d43d00043d6aff5ab0f4fc31897186312c9e639319 |
| Certificate | {
"san": [
"bombstore.shop"
],
"issuer": "Let's Encrypt / YE2",
"serial": "5a3952b33b92a02011e994c77e69e70fec5",
"sha256": "39e1347043f526c56ae52561dbb9c789b7e9d7adc2ae62c7be1809598c3f1d4b",
"subject": "bombstore.shop",
"valid_to": "2027-01-11T08:44:09Z",
"valid_from": "2026-10-13T08:44:10Z"
} |
| Mail configuration | {
"spf_lookups": 0
} |
|---|---|
| Caa records | {
"domain": "bombstore.shop"
} |
| Protective DNS results | {
"resolvers": 12,
"blocked_count": 0
} |
| Web archive observations | {
"last": "2024-10-03T18:51:20Z",
"first": "2024-05-15T11:45:56Z",
"changes": 1,
"days_archived": 3,
"scans_per_day": 0.01,
"avg_page_bytes": 2533
} |
| TLS connection | {
"alpn": "h2",
"cipher": "TLS_AES_128_GCM_SHA256",
"protocol": "TLSv1.3",
"versions": [
"TLSv1.2",
"TLSv1.3"
],
"authorized": true,
"forward_secrecy": true
} |
| Ports | {
"open": [
22,
80,
443,
8000
]
} |
| Dns server | {
"ns": [
{
"ip": "172.64.35.35",
"host": "bradley.ns.cloudflare.com"
},
{
"ip": "172.64.32.182",
"host": "lana.ns.cloudflare.com"
}
],
"zone": "bombstore.shop"
} |
| Location | {
"ip": "162.222.90.62",
"asn": "199242",
"org": "Malakmadze Web LLC",
"country": "GE"
} |
| Ssl | {
"issuer": "Let's Encrypt / YE2",
"subject": "bombstore.shop"
} |
| DNS records | {
"A": [
"162.222.90.62"
],
"NS": [
"lana.ns.cloudflare.com",
"bradley.ns.cloudflare.com"
],
"SOA": "{\"nsname\": \"bradley.ns.cloudflare.com\", \"hostmaster\": \"dns.cloudflare.com\", \"serial\": 2417214953, \"refresh\": 10000, \"retry\": 2400, \"expire\": 604800, \"minttl\": 1800}"
} |
| Dnssec | {
"ds": false,
"rrsig": false,
"dnskey": false
} |
| Get ip | {
"ip": "162.222.90.62",
"family": 4
} |
No. PhishDestroy classifies bombstore.shop as a phishing page (risk: critical, 88/100); it was first detected on 2026-10-22. VirusTotal: 6/92 engines flag it. Treat the site as unsafe.
No. Do not connect a wallet, sign messages or approve tokens on bombstore.shop. Phishing sites ask for approvals (approve, setApprovalForAll, Permit2) that let the operator move your assets, and a confirmed transaction cannot be reversed.
Change every password you entered there and turn on two-factor authentication. If you connected a wallet or signed something, revoke the approvals and move the remaining funds to a new wallet; never share your seed phrase. Step-by-step help: emergency guide.
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
bradley.ns.cloudflare.comlana.ns.cloudflare.comLocation describes the IP network.
39e1347043f526c56ae52561dbb9c789b7e9d7adc2ae62c7be1809598c3f1d4bbombstore.shopSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Hostnames retained in the domain record or Certificate Transparency cache. A hostname alone does not establish current availability or malicious activity.
img.bombstore.shopDomain recordwww.bombstore.shopDomain recordThe original observation time is not recorded for these hostnames.
Google PageSpeed Insights — mobile performance audit of bombstore.shop · checked Oct 22, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
http://bombstore.shop/https://bombstore.shop/Cache-Control: private, no-cache, no-store, max-age=0, must-revalidateContent-Encoding: gzipContent-Type: text/html; charset=utf-8summary_large_imageh3=":443"; ma=2592000private, no-cache, no-store, max-age=0, must-revalidategziptext/html; charset=utf-8Thu, 22 Oct 2026 01:43:39 GMT; rel=preload; as="style"strict-origin-when-cross-originchunkedRSC, Next-Router-State-Tree, Next-Router-Prefetch, Next-Router-Segment-Prefetch, Accept-Encoding1.1 CaddynosniffSAMEORIGIN1; mode=blockValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Reachable
4 community references
View sourceNo threat flag
View source6/92 engine detections
View sourcePD-20261022-FDB704
bombstore.shop
View sourcePage captured
View sourceEach lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Multiple reports share this IP.
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
bombstore.shop
PD-20261022-FDB704 Recipient: abuse@rashost.com If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
bombstore.shop)Even if you don't have all details — file a report anyway. Partial information still helps investigations.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.