Spamhaus DBL
DBL_SPAM

“Blast Exit”
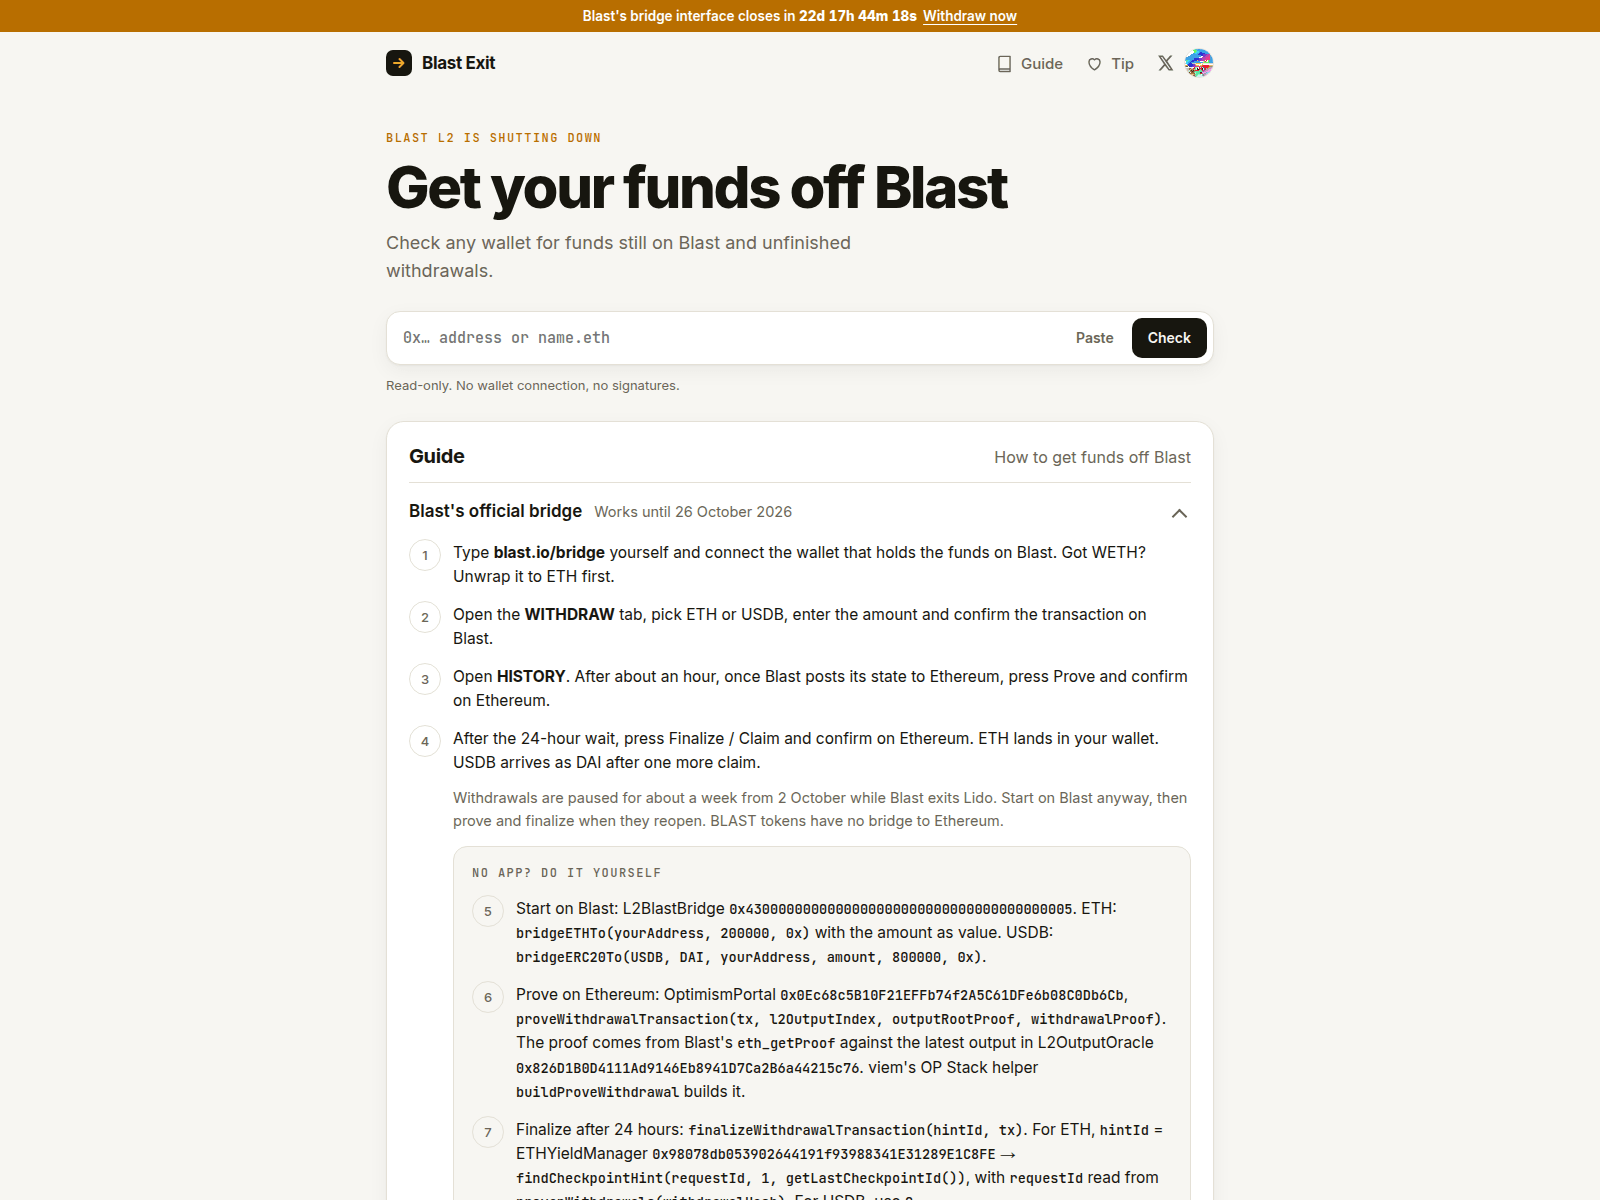
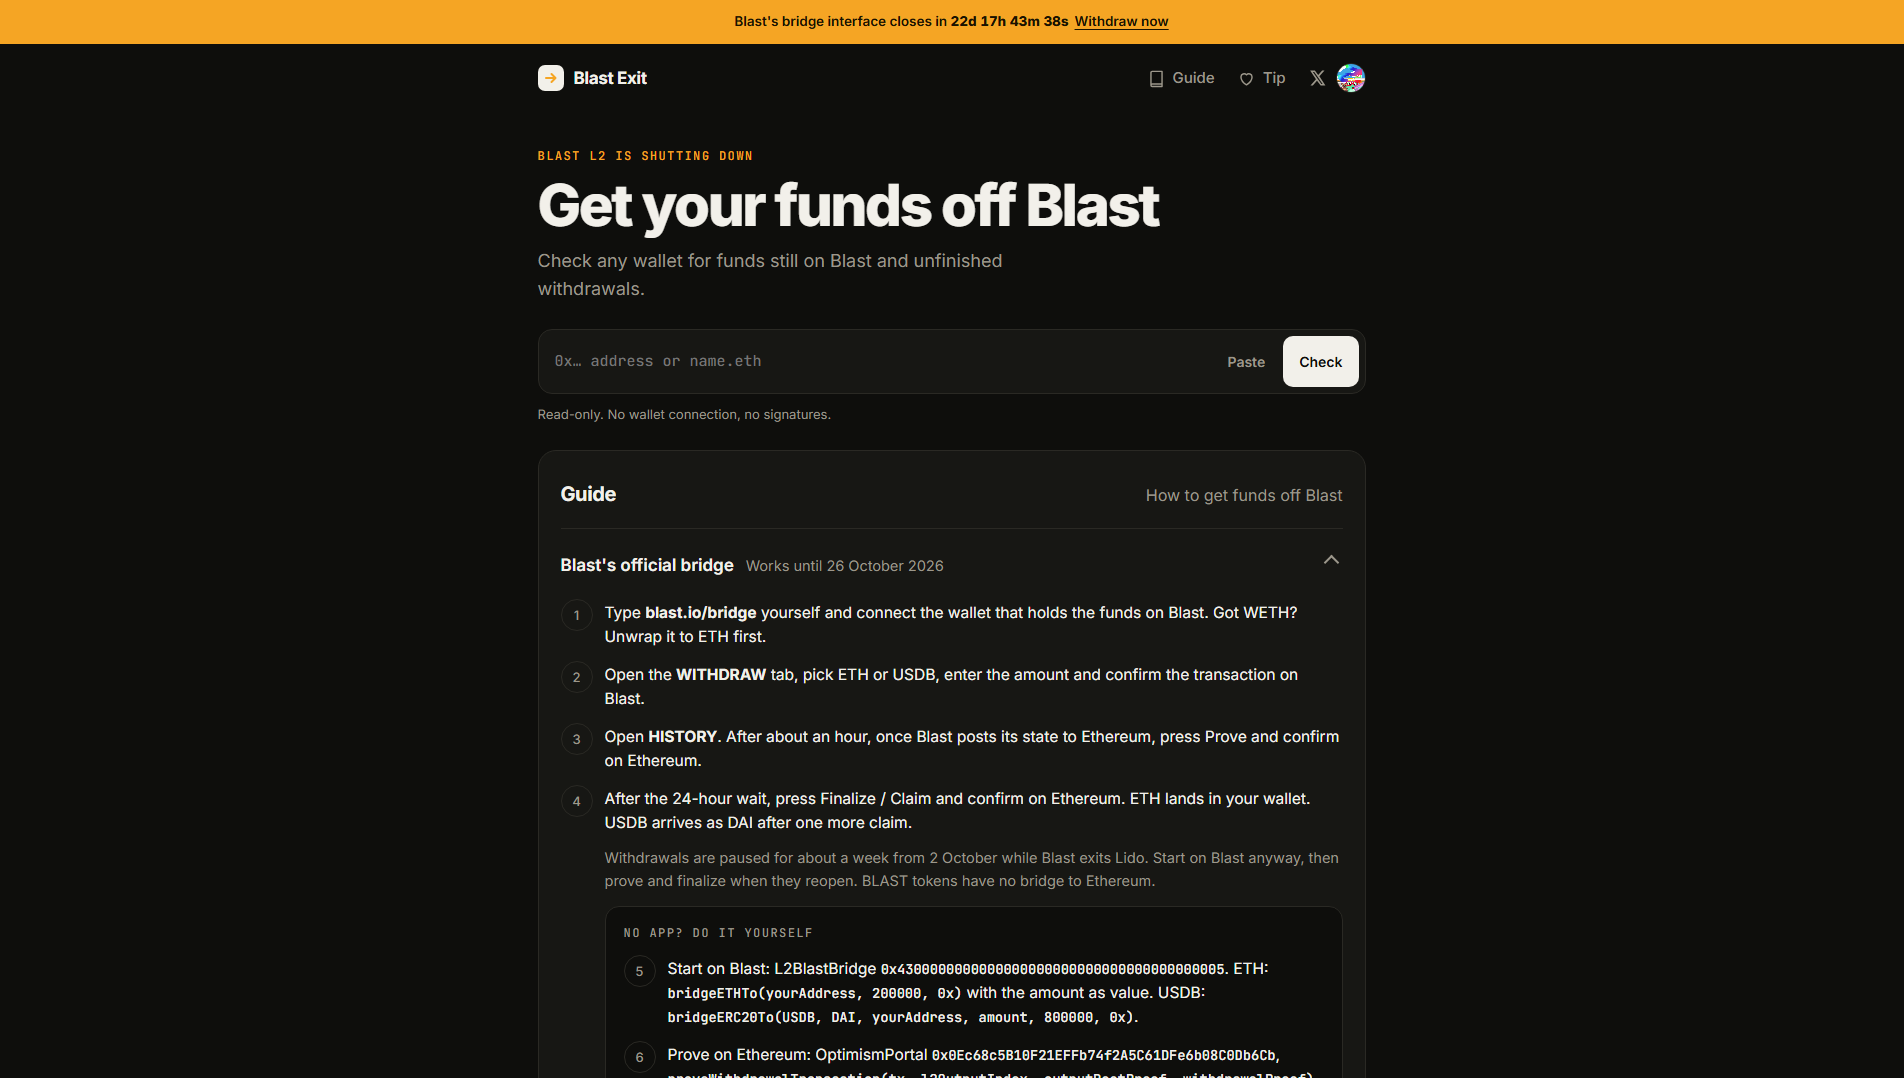
PhishDestroy first observed blastexit.com on Oct 4, 2026. The hostname explicitly references Blast; stored content metadata identifies the same apparent target. The captured page title is “Blast Exit”. Stored page analysis classifies the content as impersonation. Current evidence score: 78/100 (critical).
One source contains a positive finding: Spamhaus DBL. Spamhaus DBL: DBL_SPAM on Oct 4, 2026 at 22:30 UTC. Additional recorded evidence: URLScan captured the page on Oct 4, 2026 at 06:16 UTC.
The collector marked the hostname reachable on Oct 4, 2026 at 06:16 UTC, but did not retain the HTTP response code. Latest classified outcome: unknown; cause probe inconclusive on Oct 4, 2026 at 04:16 UTC. Registration records for the domain list NICENIC INTERNATIONAL GROUP CO., LIMITED as the registrar and Oct 3, 2026 as the creation date. Registration preceded first observation by 1 day. At collection time, the hostname resolved to 64.177.119.86 (AS20473 The Constant Company, LLC). The recorded endpoint location is Elk Grove Village, US. The evidence archive retains 3 visual captures from PhishDestroy and URLScan. TLS metadata lists Let's Encrypt / YE2 as the certificate issuer with validity through Jan 1, 2027; checked Oct 4, 2026 at 07:02 UTC.
Stored content provides classification context alongside the positive source finding.
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
 (RU)
PhishDestroy Investigation
ns3.my-ndns.comns4.my-ndns.comLocation describes the IP network.
a94c28cf0d208c8bce279c125d52f5901d3a9eac339b72d96c04393b42861156Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
64.177.119.86. 8 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
These domains also target Blast users. View all Blast threats →
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive