VirusTotal
7 / 92 engine detections
Open report

“Skate, Snow”
7 / 92 engine detections
Open reportMalicious
Open report4 community references
Open reportprovider verdict: clean
Open reportNo threat flag
Open reportResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
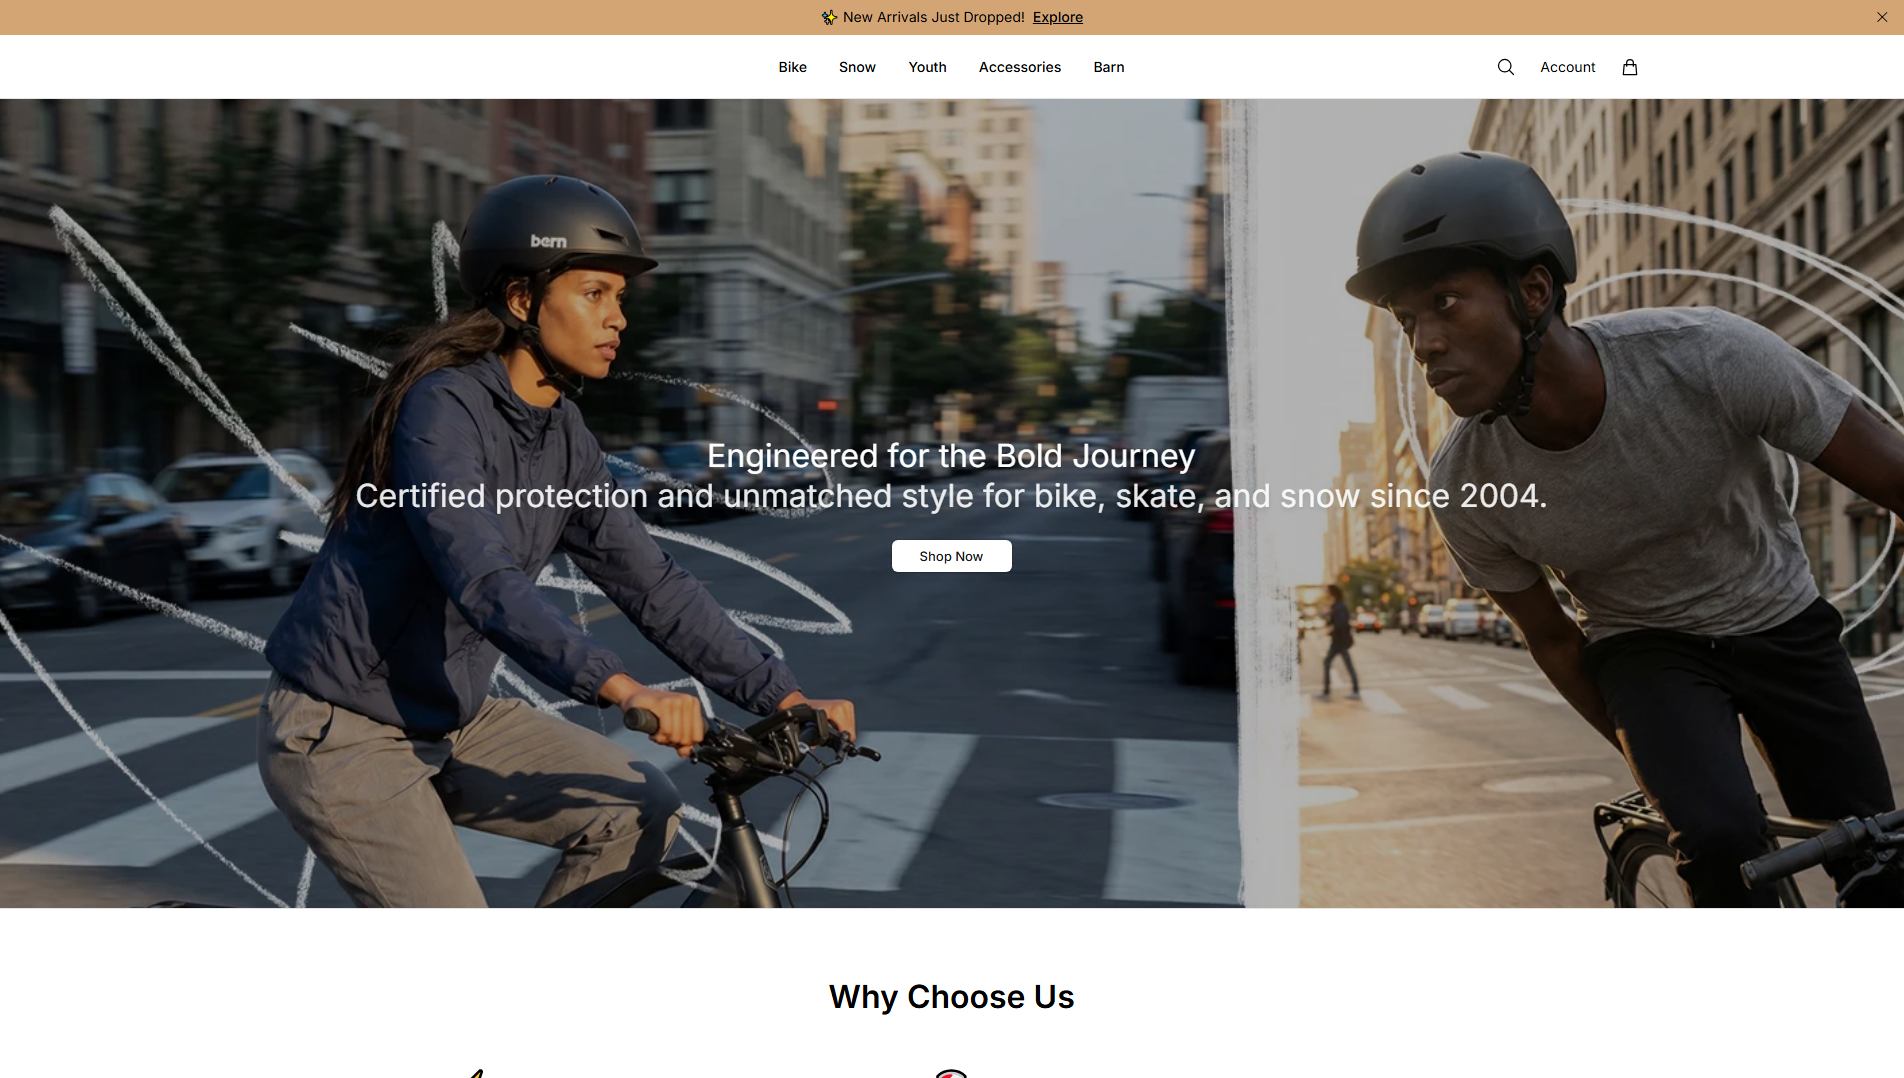
bhgear.shop presents itself as a sports retailer under the page title "Skate, Snow". It targets people shopping for skateboards, snowboards and related gear. PhishDestroy classifies it as an e-commerce scam and first flagged it on 2026-10-16. As of 2026-10-19 the site was still online and serving its storefront.
Fake shops like this copy the look of a real board-sports store and fill it with product photos and prices well below normal retail. They count on buyers who are chasing a seasonal deal and check out quickly. Victims pay by card or another method and then receive nothing, a cheap item unrelated to the order, or a tracking number that never updates. Each checkout also gives the operators the buyer's name, address, email, phone number and often card details, which can be reused for fraud or targeted phishing.
Seven of 92 VirusTotal engines flagged the domain on 2026-10-19: alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Fortinet, Gridinsoft, Netcraft and SOCRadar. That is a minority of engines, but several of these vendors specialize in fraud and phishing detection. urlscan.io rated the site malicious and tagged it specifically as a fake shop, which matches our classification. The domain appears in four AlienVault OTX threat pulses and is listed on the PhishDestroy blocklist.
The domain was registered through Dynadot Inc. on 2026-06-10, about four months before PhishDestroy detected it. A gap like that lets a storefront build up some history before it starts drawing complaints. The site is hosted in the US on the Malakmadze Web LLC network at 195.96.130.212.
If you ordered from bhgear.shop, contact your bank or card issuer now, report the charge as fraud and request a chargeback. Ask them to reissue the card if you typed its number on the site. If you created an account, change that password anywhere else you have used it. Expect phishing emails, texts or fake delivery notices that use the name and address you gave, and do not click links in them. Defenders and retailers should block the domain and its hosting IP, and report it to payment processors so they can cut off its ability to take payments.
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
amit.ns.cloudflare.comdeb.ns.cloudflare.comLocation describes the IP network.
ad05d887079f4d76bebefca697e8daf29a79d1c03785bf6d434621d73dc176acSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of bhgear.shop · checked Oct 16, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
http://bhgear.shop/https://bhgear.shop/Cache-Control: private, no-cache, no-store, max-age=0, must-revalidateContent-Encoding: gzipContent-Type: text/html; charset=utf-8summary_large_imageh3=":443"; ma=2592000private, no-cache, no-store, max-age=0, must-revalidategziptext/html; charset=utf-8Fri, 16 Oct 2026 00:11:19 GMT; rel=preload; as="style"strict-origin-when-cross-originchunkedRSC, Next-Router-State-Tree, Next-Router-Prefetch, Next-Router-Segment-Prefetch, Accept-Encoding1.1 CaddynosniffSAMEORIGIN1; mode=blockValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
alive_content: raw=ok; http=200; via=https_proxy
bhgear.shop
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Unknown→live_content
content_served
Unavailable→Reachable
Reachable→Unavailable
Unknown→live_content
content_served
Unknown→live_content
content_served
Unavailable→Reachable
Reachable→Unavailable
Unknown→live_content
content_served
Reachable
No threat flag
View source7/92 engine detections
View source4 community references
View sourcebhgear.shop
View sourcePage captured
View sourceEach lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Same favicon hash or the same page title as this host.
Multiple reports share this IP.
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Listed domains receive at least one abuse report; this entry has no retained notification history.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
bhgear.shop)Even if you don't have all details — file a report anyway. Partial information still helps investigations.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.