Skip to security report
Domain security and threat intelligence
bestchange.com.co favicon

bestchange.com.co

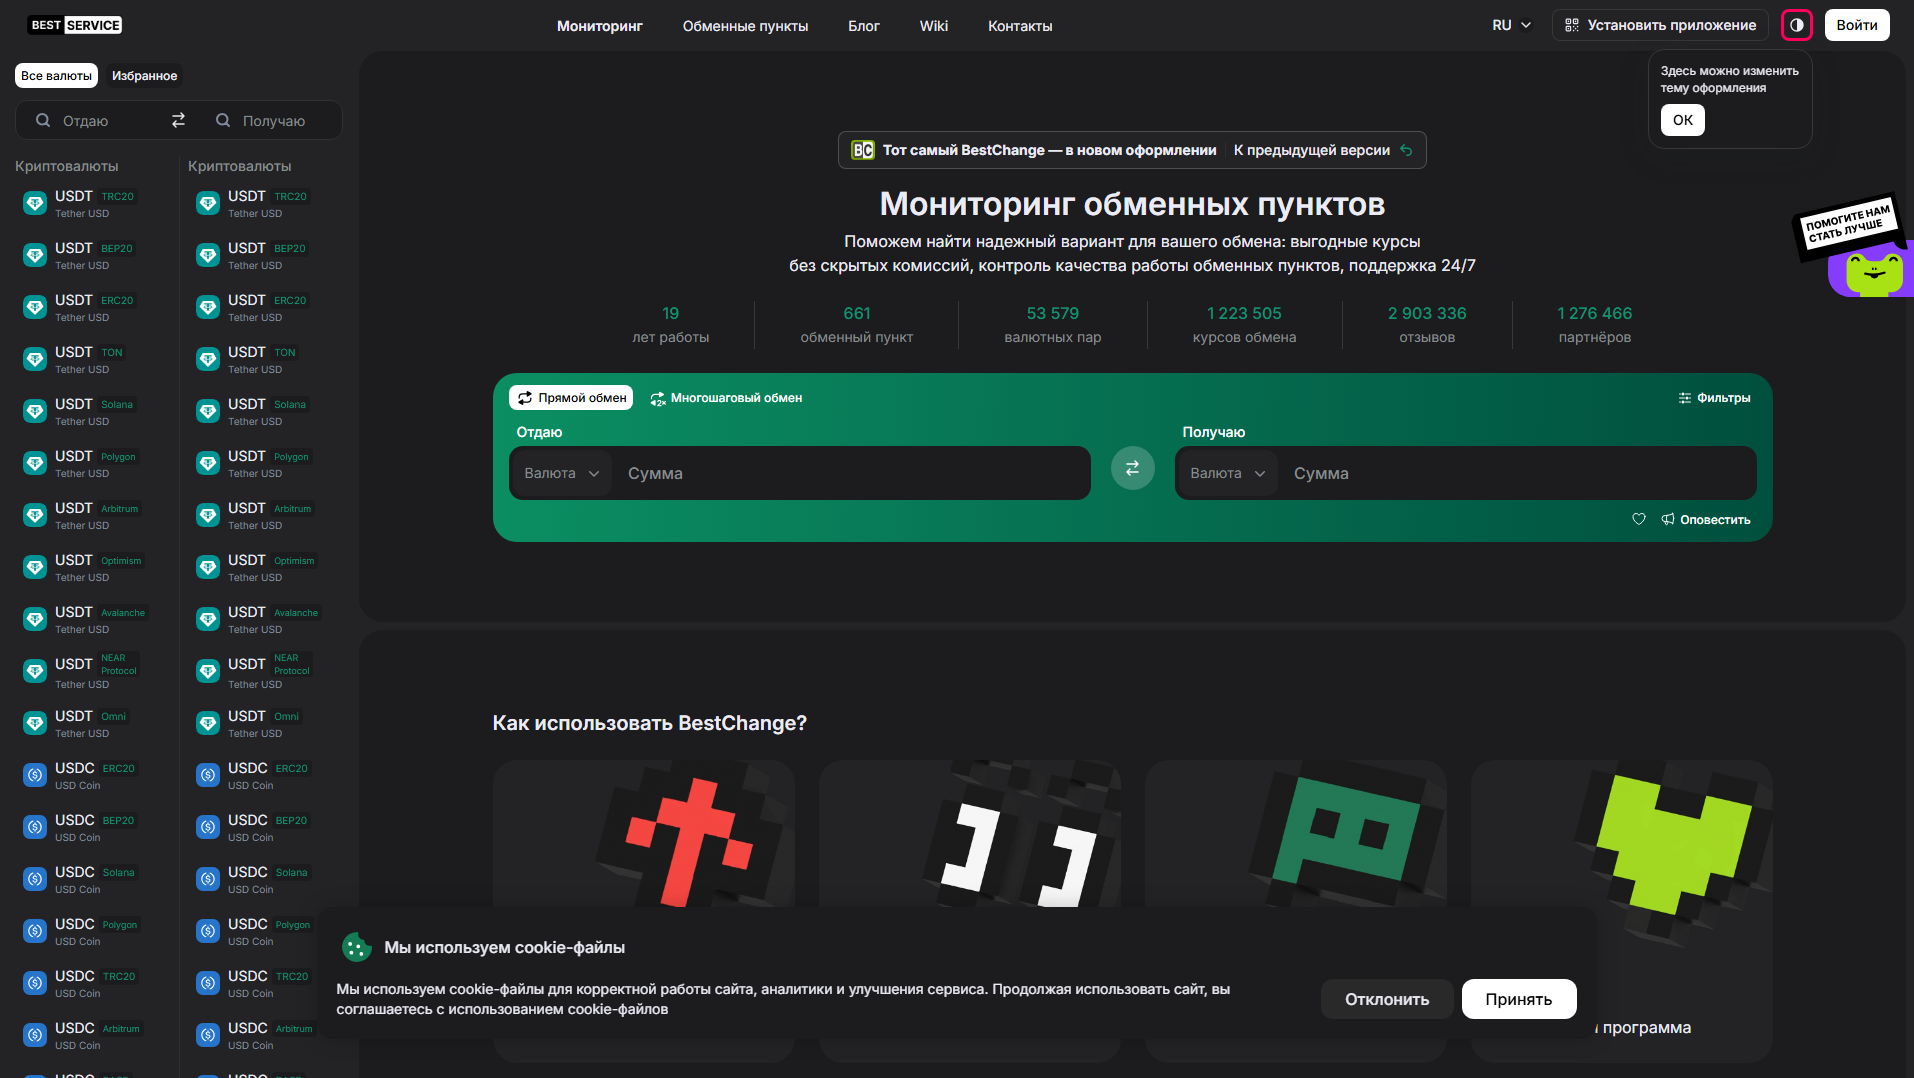
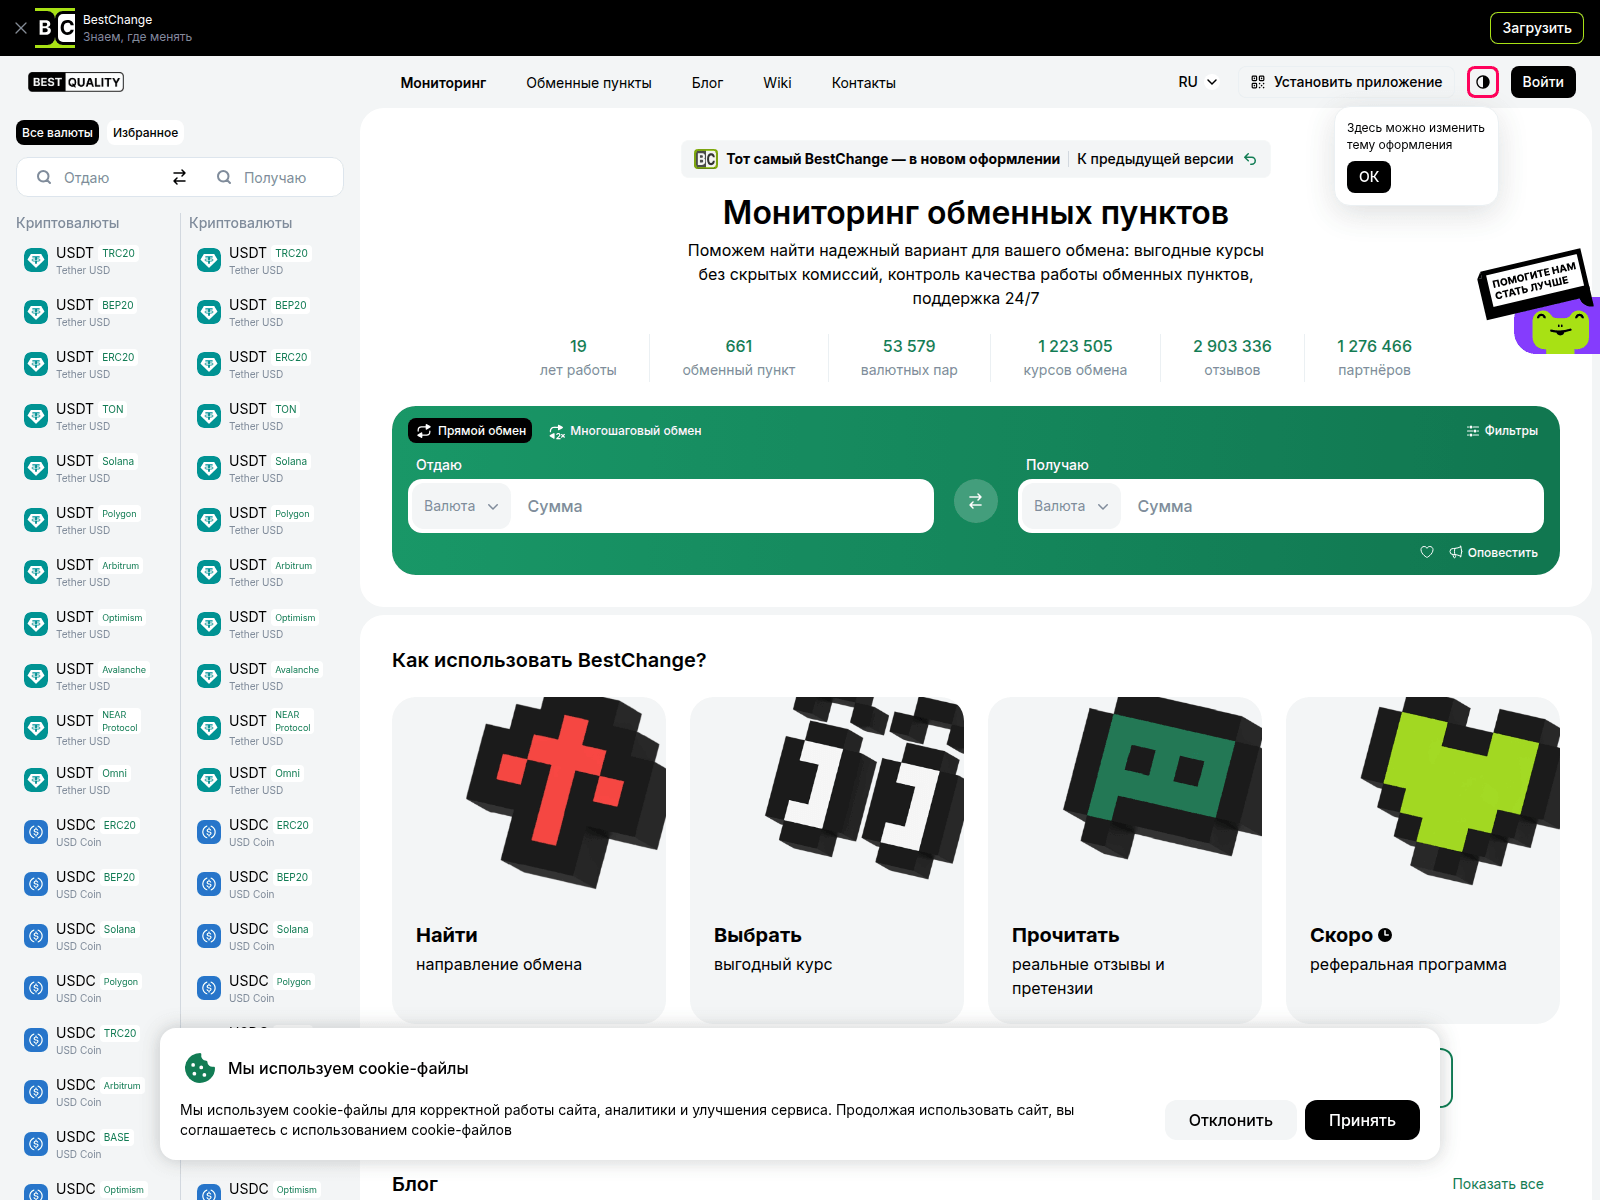
“BestChange — мониторинг обменников и выгодные курсы”

Registrar
Hosting Concepts
Resolved IP
172.67.181.146
Registered
Sep 21, 2026
Threat verdict Critical
Availability Last known active Latest stored reachability observation
VirusTotal detections: 3/91 Brand impersonation: Bestchange Young domain: 11 days old
OTX: 3 refs Sep 27, 2026 Bestchange 1 Report Sent CDN
API
This domain has been flagged as malicious
Security engines reporting a detection: 3. Exercise extreme caution — do not enter credentials or personal information.
ABUSE NOTICE · 72H+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@registrar.eu. The latest stored availability evidence still shows the domain reachable; 4 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
4 days
Reports sent
1
Latest case ID
PD-20260927-CF06C1
Current status
HTTP 200 at latest stored check
VirusTotal
VirusTotal
3 det.
OTX references
URLScan
URLScan
TLS Certificate
Expired or unverified
Age
11d Very New!
Observed status
Last known active 200
PhishDestroy
DestroyList
Listed
Reports Sent
1

Source evidence

7 sources

VirusTotal

3 / 91

Report

URLScan verdict

malicious

Report

URLQuery

Report stored; detailed verdict not recorded

Report

OTX

3 community references

Report

CF Radar

provider verdict: clean

Report

URLScan capture

stored report

Stored URLScan capture preview
Report

Google Safe Browsing

Checked; no threat flag recorded

Report

Evidence Summary

Critical
VirusTotal
3/91
OTX
3 community refs
URLScan
Stored capture

Assessment

bestchange.com.co was observed responding with HTTP status 200 on 2026-10-01, as recorded by a direct HTTP check. VirusTotal also provided a scan result for the domain, offering additional insight into its detection profile.

Recorded Evidence

The HTTP source recorded a status 200 response from bestchange.com.co on 2026-10-01. VirusTotal reported 3 detections out of 91 scanners in its scan dated 2026-09-29. OTX listed 3 pulses for the domain on 2026-10-01. The publisher-owned PhishDestroy catalogue included an internal listing for bestchange.com.co. The domain was first observed on 2026-09-27.

Interpretation

These records from HTTP, VirusTotal, OTX, and PhishDestroy reflect distinct types of monitoring and cataloguing for bestchange.com.co. Each source provides a dated observation, documenting the domain's presence and how it was recorded by various security and monitoring platforms. The information allows for a comparison of how the domain appeared to different sources within a short period.

Recommended Actions

For bestchange.com.co, preserve the HTTP status record, VirusTotal scan details, OTX pulse count, and PhishDestroy listing as separate reference points. When evaluating future activity or changes, compare new findings to these existing records to track any developments or new observations.

Extracted from stored page analysis

Observed indicators

0 wallet · 2 Telegram

Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.

Telegram
https://t.me/bestchange_botStored page reference
Telegram
https://t.me/bestchangerusStored page reference

IoC extraction recorded 2026-09-28 04:00:08 UTC

Detection-evasion analysis

Cloaking and traffic-distribution check

Not yet scanned No crawler-versus-browser difference has been recorded yet

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Last cloaking scan
Server header seen by scanner
cloudflare

Scanner note: alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare

Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this panel is open.
Waiting

Stored Capture · 2 captures

Domain details

Domain
URLScan Verdict Malicious score 100 Phishing brand: Bestchange report ↗
IP Context Cloudflare shared edge origin IP hidden Edge-IP reputation is not attributed to this domain.
OTX Tags 2026-09activeall-domainsblocklistcontentcryptodomainsdrainerfraudmonthlyphishdestroyphishingscam
Registrar Hosting Concepts NL(NL)
RegistrationCreated Sep 21, 2026 (11d · Very New!) — Expires Sep 21, 2027
HTTP Status200
Technical detailsProvenance & timestamps
First DetectedSep 27, 2026
DOM Analysisanalyzed Sep 28, 2026score 86/10012 brand signals
IoC Extractionscanned Sep 28, 20260 wallet · 2 Telegram IoCs
Submitted URLhttp://bestchange.com.co/
Favicon Hash
Case ID
Page Title
BestChange — мониторинг обменников и выгодные курсы
Impersonates
Arbitrum Avalanche Base Binance Ethereum Near Optimism PayPal +4
TLS Certificate
Hostname coverage not recorded · Issued by Let's Encrypt / YE1 · stored validity ends in 79 days

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
172.67.181.146
Network ASN
AS13335
Organization
Cloudflare, Inc.
Observed location
Toronto, CA
Server header
cloudflare

Edge-IP reputation is not attributed to this domain.

Nameservers 2

  • cesar.ns.cloudflare.com
  • maxine.ns.cloudflare.com

Location describes the IP network.

TLS certificate

Issuer
Let's Encrypt / YE1
Valid from
2026-09-22 12:14:30
Valid until
2026-12-21 12:14:29
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-09-27 22:02:03 UTC
Collection source
PhishDestroy collector
Certificate fingerprint21a9885234a5726968dcb18251bf4ef616d38fc37af98656031e582b96879b23

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 172.67.181.146rapiddns.io

Latest Classified Outcome 2026-10-02 10:09:29 UTC

Primary outcome Live content reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation Live content Ordinary HTTP content served 90% 2026-10-02 10:09:29 UTC
RDAP registration Unknown
Observed timeline last reachable: 2026-10-02 10:09:29 UTC last content: 2026-10-02 10:09:29 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Technologies · 3 identified
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain Submit evidence & help protect others

VirusTotal Analysis

3 / 91 security vendors flagged this domain
View on VT
Last analyzed First positive detection Previous stored snapshot: 3 detections
alphaMountain.ai
Forcepoint ThreatSeeker
SOCRadar

Archived Evidence

Wayback Machine Snapshot
A historical snapshot is available for evidence review
View Archive

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update 2026-09-29 17:50:23 UTC
    VirusTotal scanner detections updated from 0 to 3. Added scanner alerts: Forcepoint ThreatSeeker, SOCRadar, alphaMountain.ai.
  2. VirusTotal Detections Update 2026-09-29 16:16:33 UTC
    VirusTotal scanner detections updated from 2 to 0. Resolved alerts: Forcepoint ThreatSeeker, alphaMountain.ai.
  3. VirusTotal Detections Update 2026-09-28 15:42:42 UTC
    VirusTotal scanner detections updated from 3 to 2. Resolved alerts: SOCRadar.
  4. VirusTotal Detections Update 2026-09-28 11:37:58 UTC
    VirusTotal scanner detections updated from 2 to 3. Added scanner alerts: alphaMountain.ai.
  5. VirusTotal Detections Update 2026-09-28 06:29:04 UTC
    VirusTotal scanner detections updated from 1 to 2. Added scanner alerts: SOCRadar.
  6. Threat First Observed 2026-09-27 19:09:18 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 172.67.181.146.

Threat Response Pipeline

Discovery
Analysis
Notifications
Monitoring

17 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Sent Report Recorded
Stored outgoing record associated with registrar Hosting Concepts B.V. d/b/a Registrar.eu, 1 abuse contact
abuse@registrar.eu
Sep 27, 2026

Evidence & External Reports

Submitted Evidence Snapshot
Sent: Ledger records: 1 Case ID: PD-20260927-CF06C1 Recipient: abuse@registrar.eu
Page title stored with report: BestChange — мониторинг обменников и выгодные курсы
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 327.1 KB
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Deep Analysis

Were You Affected by This Site?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Europol
Find the official reporting channel for your EU country
National police directory
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

97-country directory

Template-based draft · optional AI wording assistance requires separate consent

Template-based draft • optional AI wording assistance requires separate consent · Review and submit it yourself

Check Any Domain

Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence

Scan Now

Report Phishing

Submit suspicious domains to our threat database — protect the community

Report

Live Threat Feed

Recent phishing reports and observed availability changes

Monitor

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive
Live Threat Feed Appeal This Listing
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/bestchange.com.co"
  title="PhishDestroy threat report for bestchange.com.co"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>