VirusTotal
4 / 92
Report


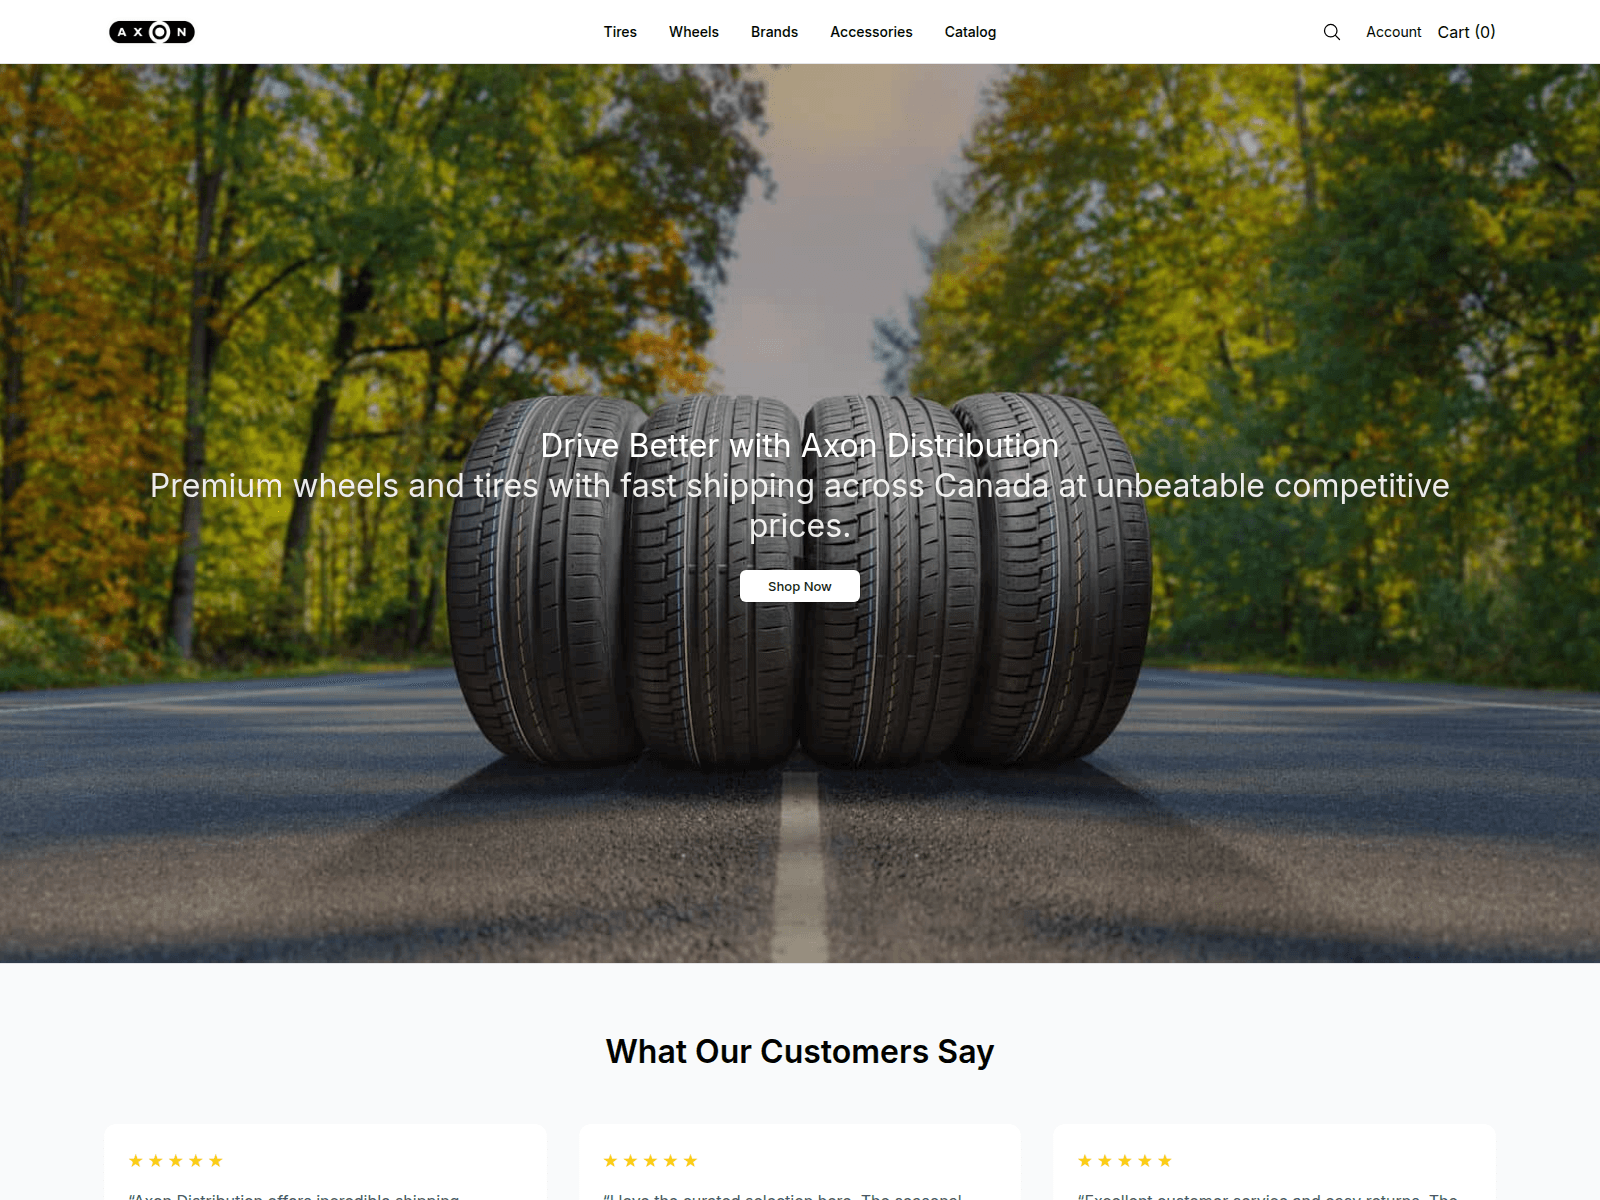
“Canada's Wheels, TPMS & Wheel Accessories | Axon Distribution”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@rashost.com.
The latest stored availability evidence still shows the domain reachable; 2 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

axonstore.shop returned an HTTP 200 status on 2026-10-09, confirming a live web server response on that date. The PageSpeed performance score for the domain was 75 as recorded on the same day.
OTX recorded three pulse entries for axonstore.shop on 2026-10-09. VirusTotal reported 4 detections out of 92 scanners on 2026-10-02. The domain is listed in the PhishDestroy internal catalogue as of 2026-10-09. The SSL certificate was issued by Let's Encrypt / YE2 on 2026-10-09.
The collected evidence provides a multi-source snapshot of axonstore.shop’s technical and security profile. OTX pulse entries, VirusTotal detections, and the PhishDestroy internal listing indicate that multiple security intelligence sources have recorded data on this domain within a short timeframe.
Review the OTX pulse records and VirusTotal scan results for axonstore.shop to identify any changes or additional context. Preserve the PhishDestroy internal listing and compare it with future security intelligence updates. Use the HTTP response and PageSpeed data as technical references for monitoring changes in the domain’s web behavior over time.
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
Scanner note: alive_content: raw=ok; http=200; via=https_proxy
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
ns1.dyna-ns.netns2.dyna-ns.netLocation describes the IP network.
1532e4c990bdf4576548092173c27d63bd698bcf23c41ede079e913708b1d917Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of axonstore.shop · checked Oct 9, 2026
176.126.101.21. 11 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20261009-22D624 Recipient: abuse@rashost.com AUP & Terms of Service Violations: Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices. Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension. Applicable Legal Framework (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Same favicon hash or the same page title as this host.
These domains also target Fakeshop users. View all Fakeshop threats →
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive