Skip to security report
Domain security and threat intelligence
arataofficial.shop favicon

arataofficial.shop

Resolved IP
80.71.144.122
Threat verdict Critical
VirusTotal detections: 4/91
Oct 3, 2026
API
This domain has been flagged as malicious
Security engines reporting a detection: 4. Exercise extreme caution — do not enter credentials or personal information.
VirusTotal
VirusTotal
4 det.
URLQuery
URLQuery
2 det.
URLScan
URLScan
PhishDestroy
DestroyList
Listed

Source evidence

6 sources

VirusTotal

4 / 91

Report

OTX

no community references

Report

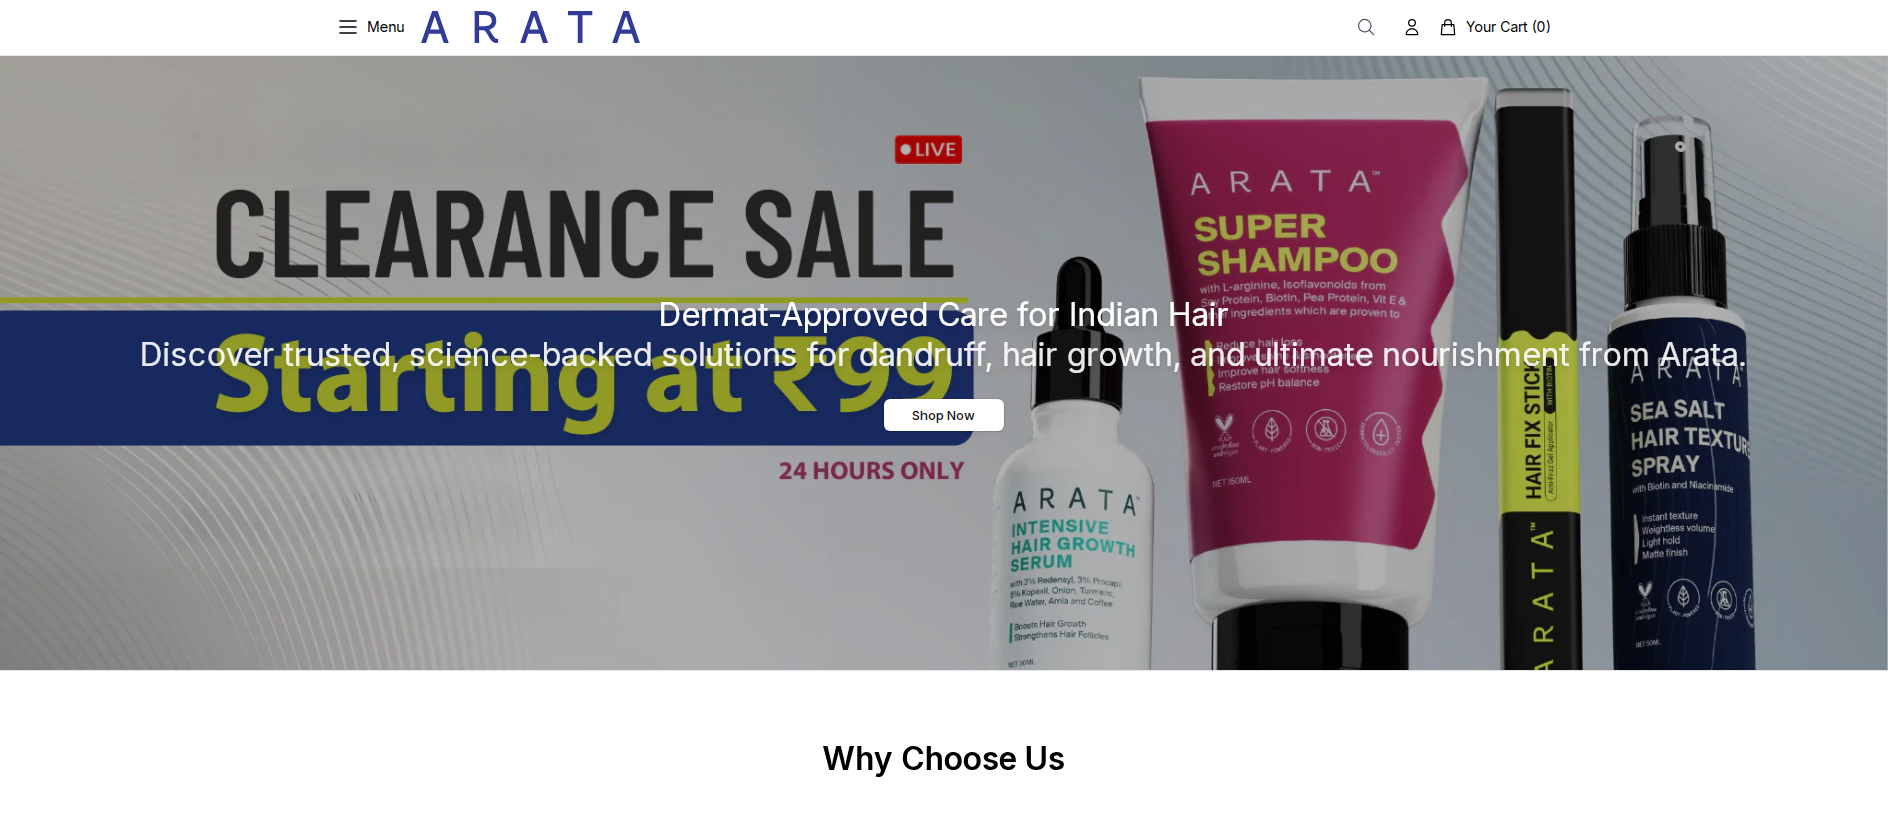
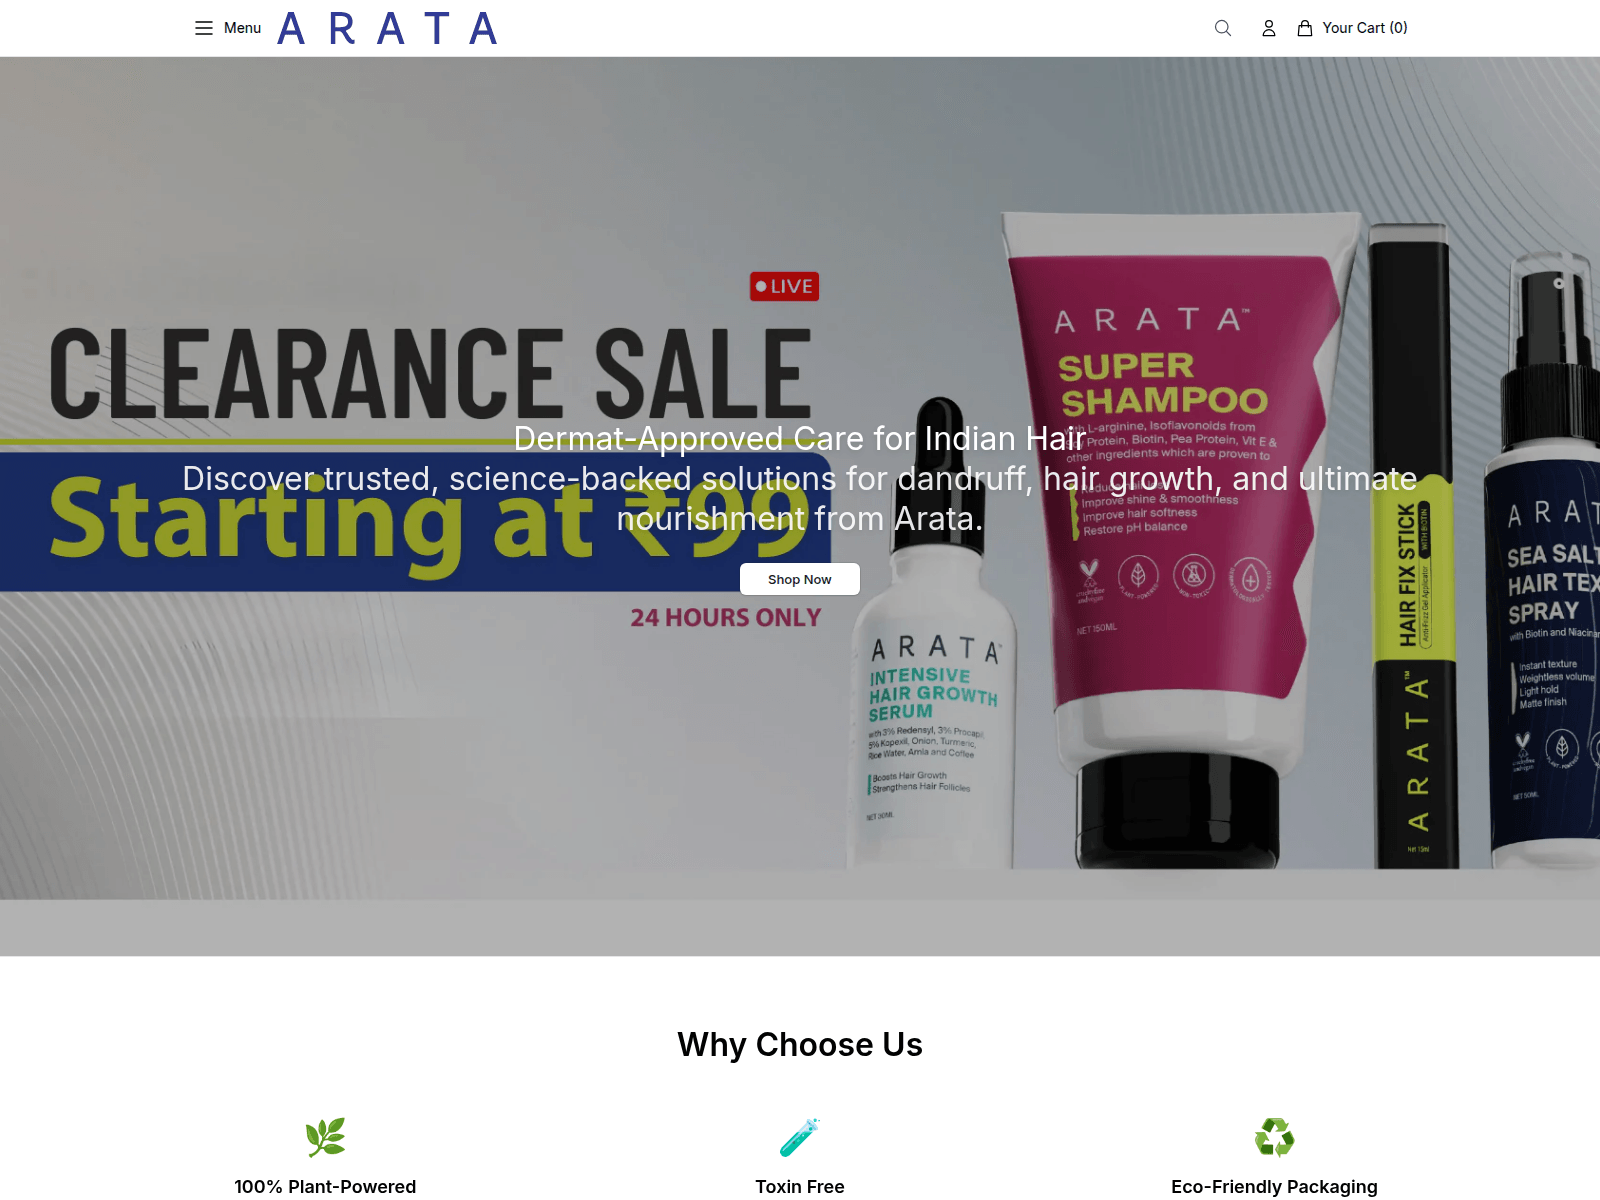
URLScan capture

stored report

Stored URLScan capture preview
Report

CF Radar

Report stored; verdict not recorded

Report

Google Safe Browsing

Checked; no threat flag recorded

Report

Evidence Summary

Critical
VirusTotal
4/91
URLScan
Stored capture

Assessment

arataofficial.shop was recorded in a VirusTotal scan on 2026-09-11, which found detections from several security vendors. On 2026-10-03, the domain was also listed in the PhishDestroy internal catalogue.

Recorded Evidence

VirusTotal reported 4 detections out of 91 scanners for arataofficial.shop on 2026-09-11. The domain was included in the PhishDestroy internal listing as of 2026-10-03. A PageSpeed performance scan on 2026-10-03 recorded a score of 66 for the domain.

Interpretation

These records show that arataofficial.shop was observed by multiple independent sources, each providing a different type of information. The VirusTotal scan and PhishDestroy listing reflect security-related observations, while the PageSpeed score offers a technical performance measure from the same period.

Recommended Actions

It is important to retain the VirusTotal detection record and PhishDestroy internal listing for arataofficial.shop when reviewing its history. The PageSpeed performance result should also be preserved for future technical comparisons. Each source record contributes to a broader understanding of the domain's profile.

Detection-evasion analysis

Cloaking and traffic-distribution check

Not yet scanned No crawler-versus-browser difference has been recorded yet

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this panel is open.
Waiting

Stored Capture · 2 captures

Domain details

Domain
Registrar Unknown
Abuse contactabuse@rashost.com
Technical detailsProvenance & timestamps
First DetectedOct 3, 2026
Submitted URLhttp://arataofficial.shop/
Case ID

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
80.71.144.122

Nameservers 2

  • bob.ns.cloudflare.com
  • marge.ns.cloudflare.com

Location describes the IP network.

viewdns.info · 80.71.144.122rapiddns.io

Latest Classified Outcome 2026-10-03 10:31:23 UTC

Primary outcome Unknown reason: Probe Inconclusive 20% confidence
Attribution source: Current State Backfill
Evidence layers Availability: Unreachable Content: Unknown DNS: Stale Registration: Unknown
Latest HTTP observation Unknown Probe Inconclusive 20% 2026-10-03 10:31:23 UTC
RDAP registration Unknown
Observed timeline last reachable: 2026-10-03 10:31:23 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Report This Domain Submit evidence & help protect others

VirusTotal Analysis

4 / 91 security vendors flagged this domain
View on VT
Last analyzed
alphaMountain.ai
CRDF
Gridinsoft
LevelBlue
Site Performance Analysis

Google PageSpeed Insights — mobile performance audit of arataofficial.shop · checked Oct 3, 2026

66
Needs Work
Performance
FCP
2.86s
First Contentful Paint
LCP
7.36s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
136ms
Total Blocking Time
SI
5.16s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-03 10:31:23 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 80.71.144.122.

Threat Response Pipeline

Discovery
Analysis
Monitoring

6 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Evidence & External Reports

Deep Analysis

Were You Affected by This Site?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Europol
Find the official reporting channel for your EU country
National police directory
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

97-country directory

Template-based draft · optional AI wording assistance requires separate consent

Template-based draft • optional AI wording assistance requires separate consent · Review and submit it yourself

Check Any Domain

Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence

Scan Now

Report Phishing

Submit suspicious domains to our threat database — protect the community

Report

Live Threat Feed

Recent phishing reports and observed availability changes

Monitor

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive
Live Threat Feed Appeal This Listing
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/arataofficial.shop"
  title="PhishDestroy threat report for arataofficial.shop"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>