VirusTotal
4 / 91
Report

PhishDestroy first observed aquasureusahome.shop on Oct 3, 2026. Current evidence score: 81/100 (critical).
Positive findings are stored from 2 sources: VirusTotal and URLQuery. VirusTotal recorded 4 detections among 91 engines: alphaMountain.ai, Fortinet, LevelBlue, Netcraft on Oct 3, 2026 at 10:06 UTC. URLQuery recorded 2 detections; no observation timestamp was retained. Additional recorded evidence: AlienVault OTX listed 4 community pulse references (not vendor detections) on Oct 3, 2026 at 10:06 UTC. URLScan captured the page on Oct 3, 2026 at 09:34 UTC.
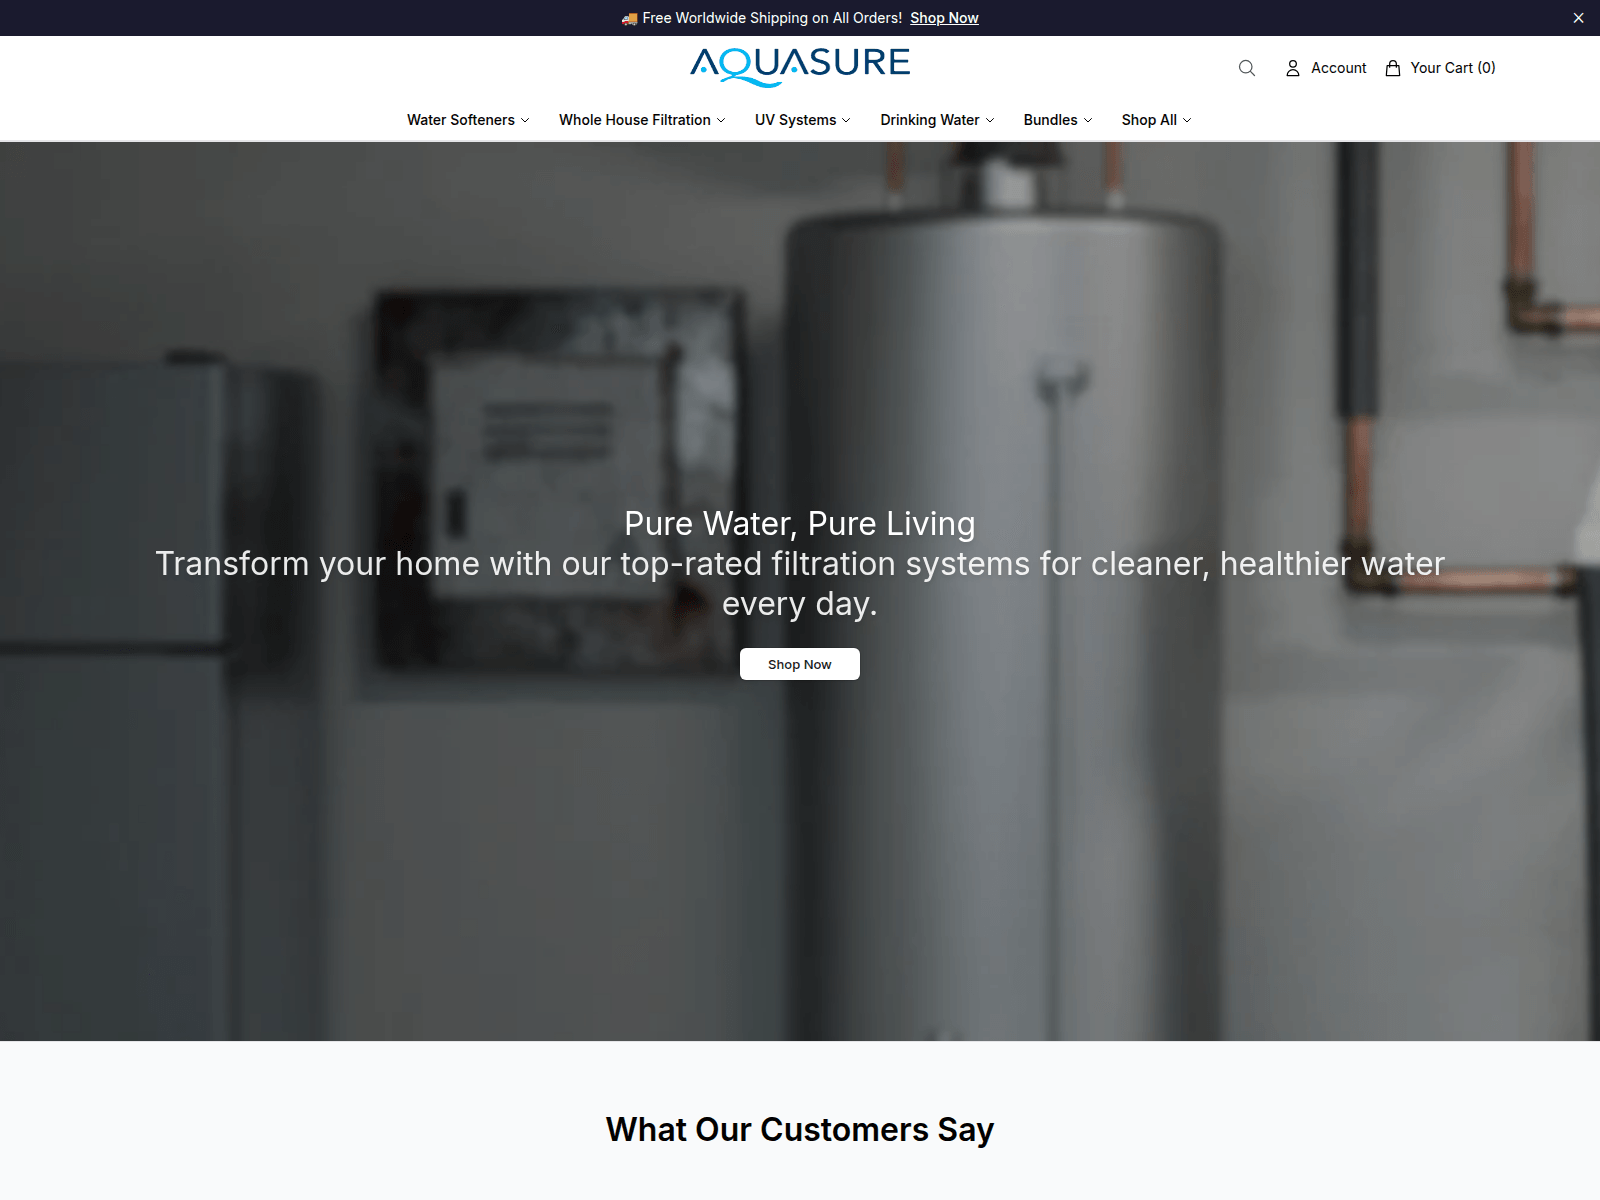
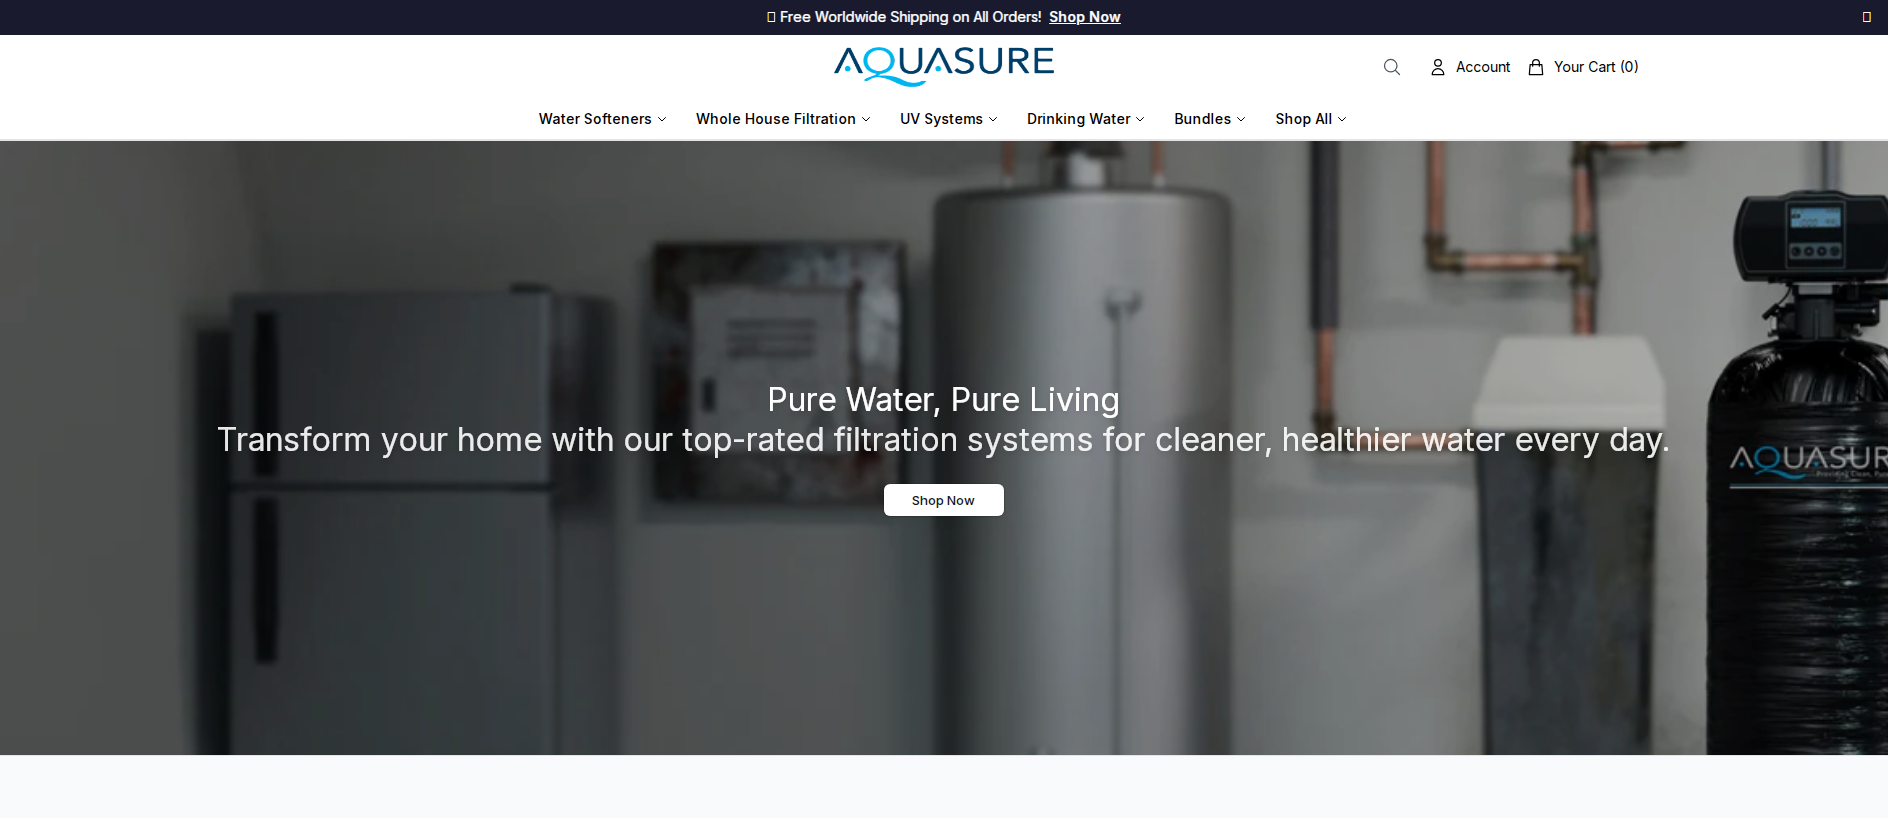
The collector marked the hostname reachable on Oct 3, 2026 at 09:34 UTC, but did not retain the HTTP response code. Latest classified outcome: unknown; cause probe inconclusive on Oct 3, 2026 at 07:34 UTC. At collection time, the hostname resolved to 162.222.90.246 (AS199242 Malakmadze Web LLC). The recorded endpoint location is Los Angeles, US. DOM analysis on Oct 3, 2026 at 10:20 UTC returned 81/100. The evidence archive retains 2 visual captures from PhishDestroy and URLScan; the captures preserve the landing-page appearance. TLS metadata lists Let's Encrypt / YE1 as the certificate issuer with validity through Dec 12, 2026; checked Oct 3, 2026 at 10:02 UTC.
The record contains 2 positive source findings supporting the current phishing classification.
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
frida.ns.cloudflare.comsimon.ns.cloudflare.comLocation describes the IP network.
c40d164b27dd0d6ccc9674084fdf5191f441700e84caf192af56ab89db5c0d1cSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of aquasureusahome.shop · checked Oct 3, 2026
162.222.90.246. 8 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive