Skip to security report
Domain security and threat intelligence
angelesway.shop favicon

angelesway.shop

Resolved IP
23.252.79.89
Threat verdict Critical
VirusTotal detections: 7 (vendor total unavailable)
Oct 4, 2026 1 Report Sent
API
This domain has been flagged as malicious
Security engines reporting a detection: 7. Exercise extreme caution — do not enter credentials or personal information.
VirusTotal
VirusTotal
7 det.
URLQuery
URLQuery
2 det.
URLScan
URLScan
TLS Certificate
Expired or unverified
PhishDestroy
DestroyList
Listed
Reports Sent
1

Source evidence

4 sources

VirusTotal

7 detections · vendor total unavailable

Report
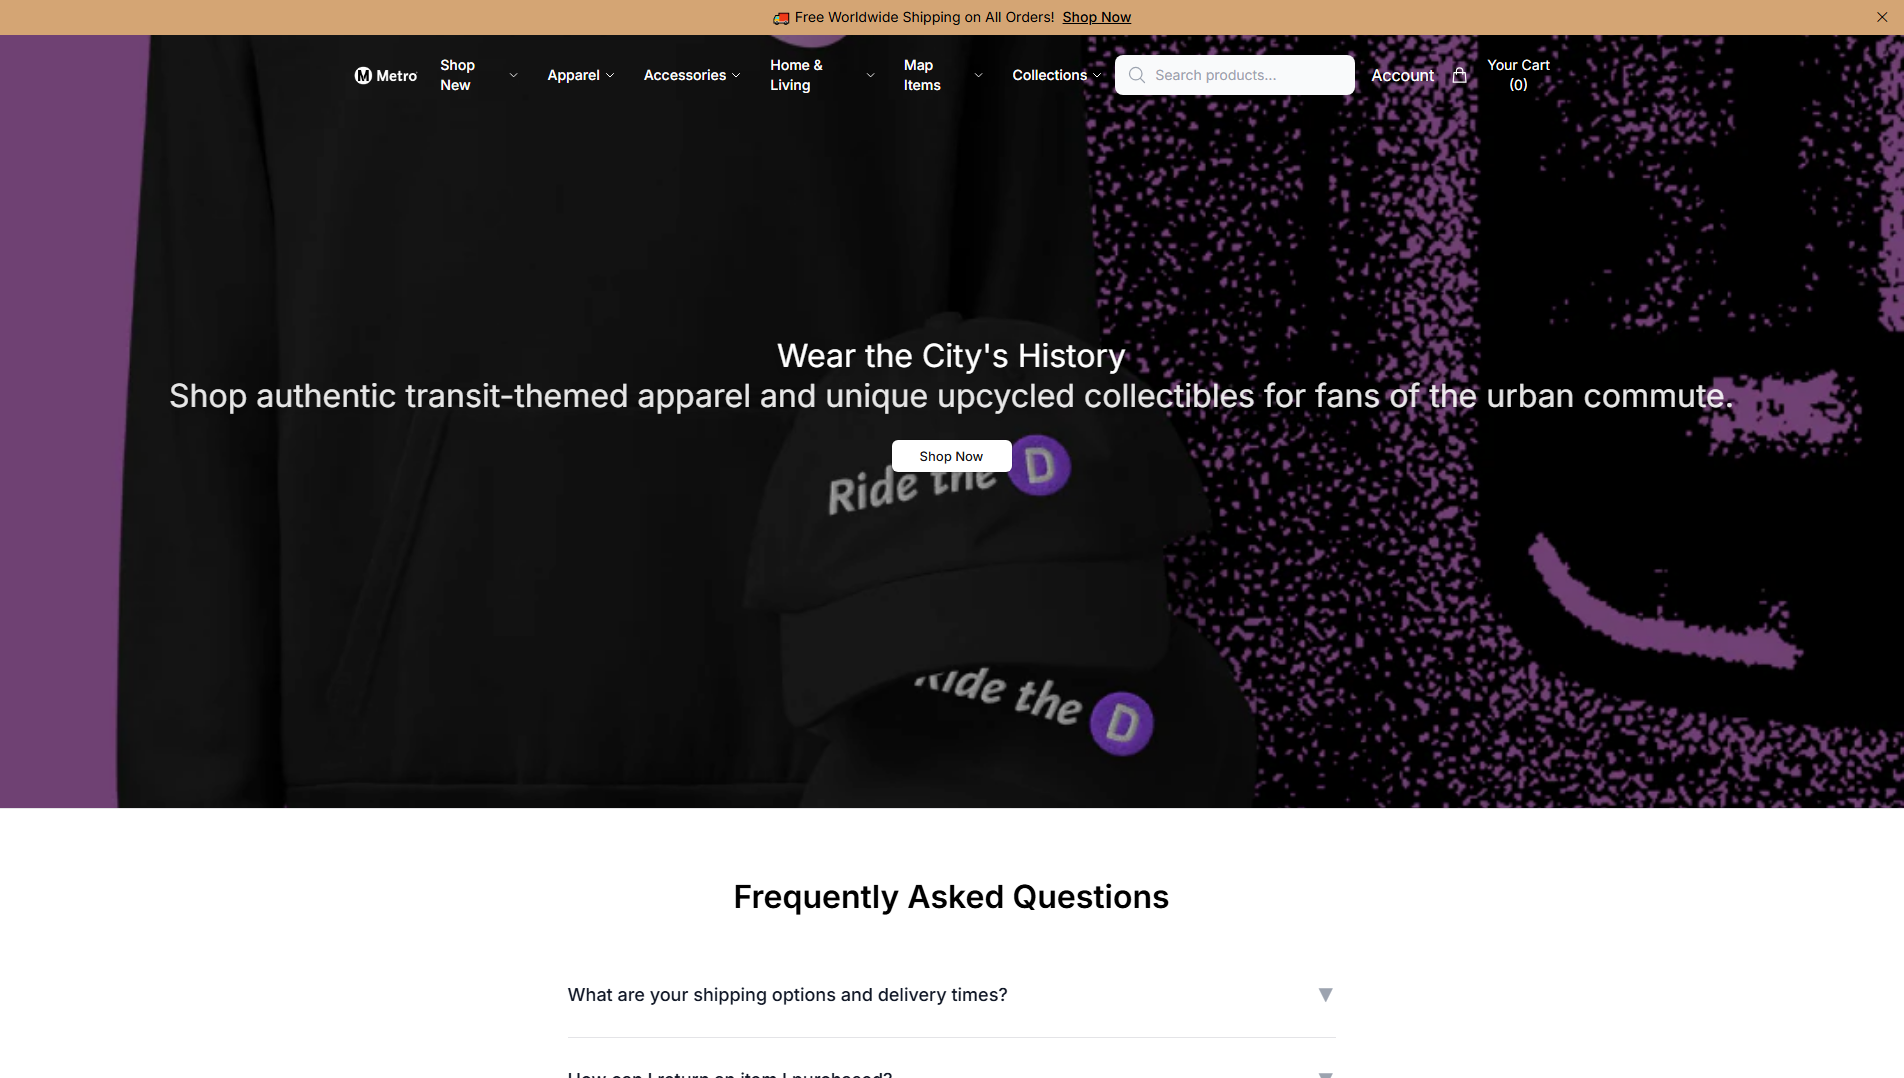
URLScan capture

stored report

Stored URLScan capture preview
Report

CF Radar

Report stored; verdict not recorded

Report

Evidence Summary

Critical
VirusTotal
7 detections
URLScan
Stored capture

PhishDestroy first observed angelesway.shop on Oct 4, 2026. Drainer analysis recorded Angel Drainer. Current evidence score: 100/100 (critical).

Positive findings are stored from 2 sources: VirusTotal and URLQuery. VirusTotal stored 7 positive engine results: CRDF, CyRadar, Forcepoint ThreatSeeker, Fortinet, G-Data, LevelBlue, Netcraft. URLQuery recorded 2 detections; no observation timestamp was retained. Additional recorded evidence: URLScan captured the page on Oct 4, 2026 at 00:04 UTC.

The collector marked the hostname reachable on Oct 4, 2026 at 00:04 UTC, but did not retain the HTTP response code. Latest classified outcome: unknown; cause probe inconclusive on Oct 3, 2026 at 22:04 UTC. At collection time, the hostname resolved to 23.252.79.89. The evidence archive retains 2 visual captures from PhishDestroy and URLScan; the captures preserve the landing-page appearance. TLS metadata lists Let's Encrypt / YE1 as the certificate issuer with validity through Nov 9, 2026; checked Oct 4, 2026 at 01:02 UTC.

The content indicators and 2 positive source findings support the current angel drainer classification.

Detection-evasion analysis

Cloaking and traffic-distribution check

Not yet scanned No crawler-versus-browser difference has been recorded yet

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this panel is open.
Waiting

Stored Capture · 2 captures

Domain details

Domain
Registrar Unknown
Abuse contactabuse@rashost.com
Technical detailsProvenance & timestamps
First DetectedOct 4, 2026
Submitted URLhttp://angelesway.shop/
Case ID
TLS Certificate
Hostname coverage not recorded · Issued by Let's Encrypt / YE1 · stored validity ends in 36 days

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
23.252.79.89

Nameservers 2

  • aisha.ns.cloudflare.com
  • max.ns.cloudflare.com

Location describes the IP network.

TLS certificate

Issuer
Let's Encrypt / YE1
Valid from
2026-08-11 06:53:15
Valid until
2026-11-09 06:53:14
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-04 01:02:04 UTC
Collection source
PhishDestroy collector
Certificate fingerprint72c94bfb6abbfeb1c9fac7fe884f1cc31a42c041394d2b31e0581375f8b8e582

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 23.252.79.89rapiddns.io

Latest Classified Outcome 2026-10-04 00:04:29 UTC

Primary outcome Unknown reason: Probe Inconclusive 20% confidence
Attribution source: Current State Backfill
Evidence layers Availability: Unreachable Content: Unknown DNS: Stale Registration: Unknown
Latest HTTP observation Unknown Probe Inconclusive 20% 2026-10-04 00:04:29 UTC
RDAP registration Unknown
Observed timeline last reachable: 2026-10-04 00:04:29 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Report This Domain Submit evidence & help protect others

VirusTotal Analysis

7 detections recorded · vendor total unavailable
View on VT
CRDF
CyRadar
Forcepoint ThreatSeeker
Fortinet
G-Data
LevelBlue
Netcraft

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-04 00:04:29 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 23.252.79.89.

Threat Response Pipeline

Discovery
Analysis
Notifications
Monitoring

7 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Sent Report Recorded
Stored outgoing record associated with domain registrar, 1 abuse contact
abuse@rashost.com
Oct 4, 2026

Evidence & External Reports

Submitted Evidence Snapshot
Sent: Ledger records: 1 Case ID: PD-20261004-BC73D7 Recipient: abuse@rashost.com
Page title stored with report: T-shirts, Toys, Posters, Mugs | Metro
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 716.9 KB
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Deep Analysis

Were You Affected by This Site?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

If a wallet, seed phrase, or account was exposed, report the incident immediately. Revoke approvals and move remaining assets to a new wallet created on a trusted device.

Europol
Find the official reporting channel for your EU country
National police directory
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Guaranteed crypto recovery is a fraud indicator. Learn more about recovery fraud →

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

97-country directory

Template-based draft · optional AI wording assistance requires separate consent

Template-based draft • optional AI wording assistance requires separate consent · Review and submit it yourself

Check Any Domain

Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence

Scan Now

Report Phishing

Submit suspicious domains to our threat database — protect the community

Report

Live Threat Feed

Recent phishing reports and observed availability changes

Monitor

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive

Live Threat Feed Appeal This Listing

Recommendations & Advice for Victims

An estimated $51 billion flowed to illicit crypto wallets in 2024 (source). If you interacted with angelesway.shop — act now.

What should I do immediately?
Urgent
  • Revoke token approvals — use revoke.cash to remove access granted to malicious smart contracts
  • Move remaining funds to a brand-new wallet. The compromised wallet is no longer safe
  • Change all passwords — email, exchange accounts, anything that shares the same password
  • Enable 2FA using an authenticator app (not SMS). Disable SMS-based recovery
  • Freeze cards if you entered banking details on the phishing site
What information should I collect for my report?
FBI guidelines

According to the FBI, the most important details are transaction data:

  • Cryptocurrency addresses — scammer's wallet (e.g., 0x5856...35985)
  • Amount & crypto type — exact amount (e.g., 1.02345 ETH, 0.5 BTC, 500 USDT)
  • Transaction ID (hash) — the unique blockchain transaction identifier
  • Exact dates & times — of each transaction and first contact with scammer
  • Screenshots — scam website, chat messages, emails, wallet transactions, social media
  • All URLs & domains used by the scammer (including angelesway.shop)
  • Communications — emails, texts, phone numbers, usernames the scammer used

Even if you don't have all details — file a report anyway. Partial information still helps investigations.

Where should I report the scam?
  • FBI IC3 — Internet Crime Complaint Center (US federal reporting)
  • Europol — European cybercrime reporting (EU)
  • Chainabuse — flag scam wallets across exchanges & platforms
  • Your crypto exchange — notify its fraud team immediately; it may be able to preserve records or restrict funds held on its platform
  • Local police — creates an official record, even if they can't act immediately

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do crypto scams typically work?
  • Fake websites — pixel-perfect clones of legitimate sites with slightly altered domains
  • Malicious approvals — "connect wallet" prompts that grant unlimited token spending to attackers
  • Pig butchering — trust built over weeks via Telegram/WhatsApp/dating apps, then money stolen
  • Recovery scams — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • Fake ads & airdrops — Google/social media ads and "free token" offers leading to wallet drainers
  • AI-powered scams — deepfakes, automated phishing, and AI-generated sites making fraud harder to detect
How can I protect myself in the future?
  • Use a hardware wallet (Ledger, Trezor). Never store large amounts in browser wallets
  • Bookmark official sites — never click links from emails, DMs, or ads
  • Read every approval — verify permissions before signing. Reject unlimited approvals
  • Verify domains — check on PhishDestroy before interacting. Check HTTPS, spelling, domain age
  • "Too good to be true" = scam — guaranteed returns, celebrity endorsements, urgent deadlines
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/angelesway.shop"
  title="PhishDestroy threat report for angelesway.shop"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>