Skip to security report
Domain security and threat intelligence
amivogue.shop favicon

amivogue.shop

“Boutique Officielle en Ligne | AMI”

Resolved IP
23.252.79.208
Threat verdict Critical
VirusTotal detections: 6/91 Spamhaus DBL: DBL_SPAM Brand impersonation: Fakeshop
OTX: 2 refs Oct 1, 2026 Fakeshop 1 Report Sent
API
This domain has been flagged as malicious
Security engines reporting a detection: 6. Exercise extreme caution — do not enter credentials or personal information.

Evidence Summary

Critical
VirusTotal
6/91
OTX
2 community refs
URLScan
Stored capture

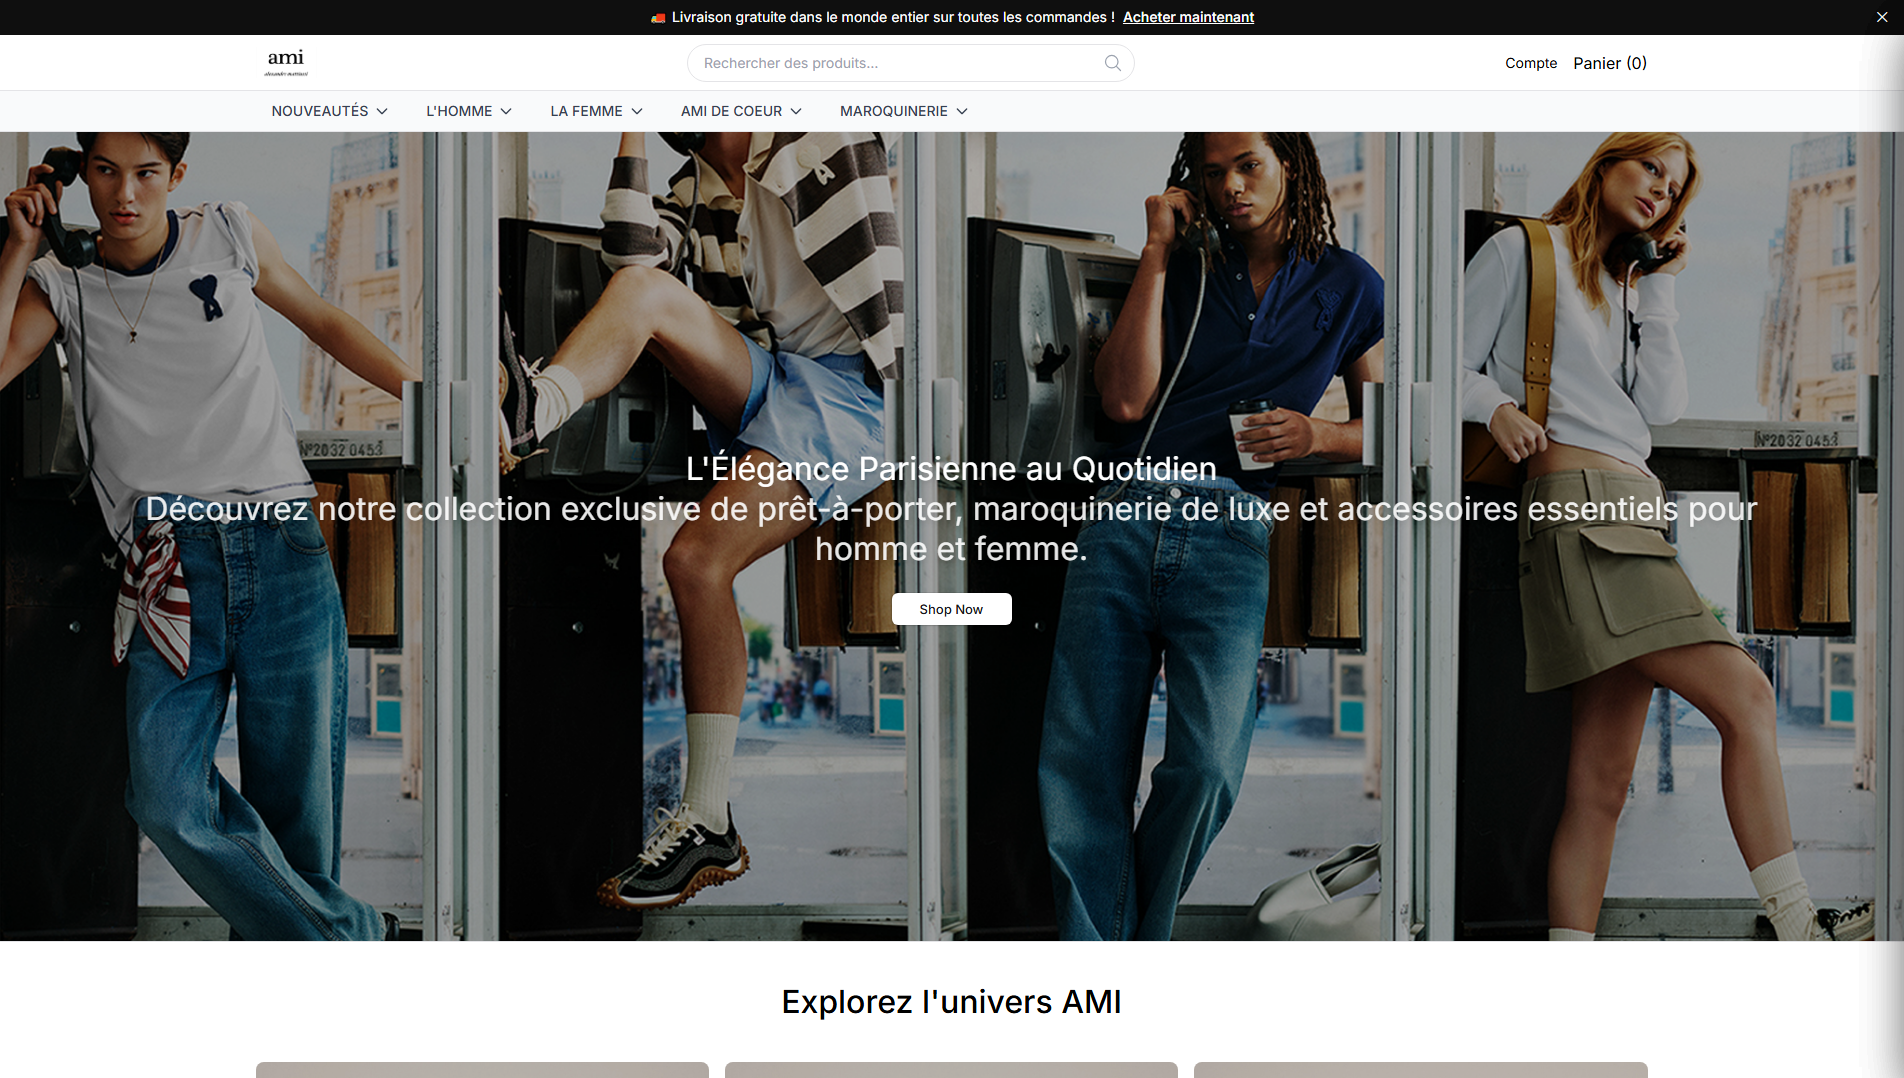
PhishDestroy first observed amivogue.shop on Oct 1, 2026. Stored content metadata identifies Fakeshop as the apparent target. The captured page title is “Boutique Officielle en Ligne | AMI”. Page analysis recorded additional brand references to Argent and Ton. Stored page analysis classifies the content as impersonation. Current evidence score: 100/100 (critical).

Positive findings are stored from 4 sources: VirusTotal, Spamhaus DBL, URLQuery, and URLScan. VirusTotal recorded 6 detections among 91 engines: alphaMountain.ai, CRDF, Fortinet, Gridinsoft, LevelBlue, Webroot on Oct 1, 2026 at 06:29 UTC. Spamhaus DBL: DBL_SPAM on Oct 1, 2026 at 06:30 UTC. URLQuery recorded 2 detections; no observation timestamp was retained. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Fakeshop and assigned phishing as its category on Oct 1, 2026 at 03:30 UTC. Additional recorded evidence: AlienVault OTX listed 2 community pulse references (not vendor detections) on Oct 1, 2026 at 06:31 UTC.

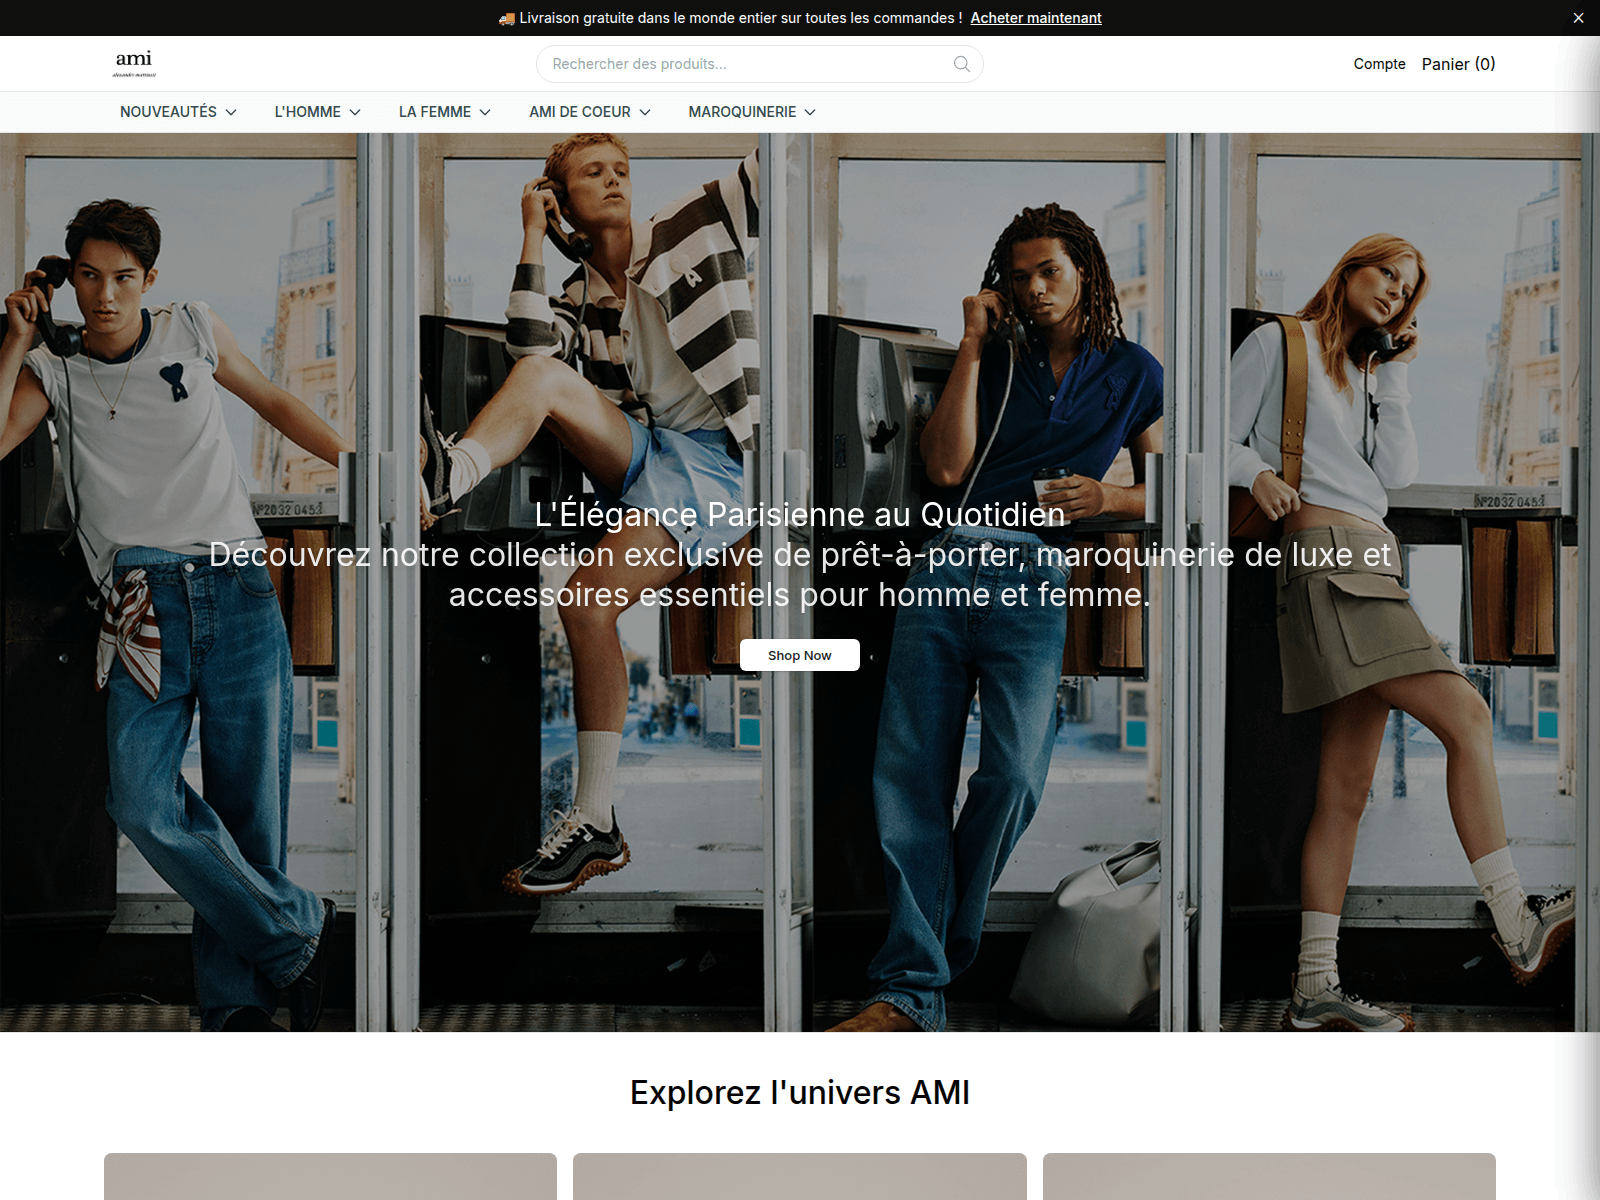
The collector marked the hostname reachable on Oct 1, 2026 at 03:01 UTC, but did not retain the HTTP response code. At collection time, the hostname resolved to 23.252.79.208. The recorded endpoint location is GE. DOM analysis on Oct 1, 2026 at 06:20 UTC returned 83/100. The evidence archive retains 2 visual captures from PhishDestroy and URLScan. TLS metadata lists YE2 as the certificate issuer.

The content indicators and 4 positive source findings support the current Fakeshop-themed impersonation classification.

Spamhaus DBL
DBL_SPAM
VirusTotal
VirusTotal
6 det.
URLQuery
URLQuery
2 det.
OTX references
URLScan
URLScan
TLS Certificate
Expired or unverified
PhishDestroy
DestroyList
Listed
Reports Sent
1

Source evidence

8 sources

VirusTotal

6 / 91

Report

URLScan verdict

malicious

Spamhaus DBL

DBL_SPAM

OTX

2 community references

Report

CF Radar

scan completed

Report

URLScan capture

stored report

Stored URLScan capture preview
Report

Google Safe Browsing

Checked; no threat flag recorded

Stored Capture · 2 captures

Domain details

Domain
URLScan Verdict Malicious score 100 Phishing brand: Fakeshop report ↗
IP Reputation abuse score 0/100 0 reports checked Oct 1, 2026
OTX Tags activeblocklistcontentcryptodrainerfraudphishdestroyphishingscam
Registrar Unknown
Abuse contactabuse@rashost.com
Technical detailsProvenance & timestamps
First DetectedOct 1, 2026
DOM Analysisanalyzed Oct 1, 2026score 83/1002 brand signals
Submitted URLhttp://amivogue.shop/
Favicon Hash
Page Title
Boutique Officielle en Ligne | AMI
Impersonates
Argent Ton
TLS Certificate
Hostname coverage not recorded · Issued by YE2

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
23.252.79.208
Observed location
GE

Nameservers 2

  • miles.ns.cloudflare.com
  • priscilla.ns.cloudflare.com

Location describes the IP network.

TLS certificate

Issuer
YE2
Hostname coverage
Hostname coverage not recorded
Collection source
PhishDestroy collector

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Technologies · 1 identified
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain Submit evidence & help protect others

VirusTotal Analysis

6 / 91 security vendors flagged this domain
View on VT
Last analyzed First positive detection Previous stored snapshot: 6 detections
alphaMountain.ai
CRDF
Fortinet
Gridinsoft
LevelBlue
Webroot
Site Performance Analysis

Google PageSpeed Insights — mobile performance audit of amivogue.shop · checked Oct 1, 2026

57
Needs Work
Performance
FCP
2.88s
First Contentful Paint
LCP
44.05s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
323ms
Total Blocking Time
SI
6.15s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-01 03:01:49 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 23.252.79.208.

Threat Response Pipeline

Discovery
Analysis
Notifications
Monitoring

12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Sent Report Recorded
Stored outgoing record associated with domain registrar, 1 abuse contact
abuse@rashost.com
Oct 1, 2026

Evidence & External Reports

Submitted Evidence Snapshot
Sent: Ledger records: 1 Case ID: PD-20261001-187BC3 Recipient: abuse@rashost.com
Page title stored with report: Boutique Officielle en Ligne | AMI
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 2,018.1 KB
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Deep Analysis

Were You Affected by This Site?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Europol
Find the official reporting channel for your EU country
National police directory
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

97-country directory

Template-based draft · optional AI wording assistance requires separate consent

Template-based draft • optional AI wording assistance requires separate consent · Review and submit it yourself

Check Any Domain

Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence

Scan Now

Report Phishing

Submit suspicious domains to our threat database — protect the community

Report

Live Threat Feed

Recent phishing reports and observed availability changes

Monitor

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive
Live Threat Feed Appeal This Listing
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/amivogue.shop"
  title="PhishDestroy threat report for amivogue.shop"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>