VirusTotal
8 / 89
Report

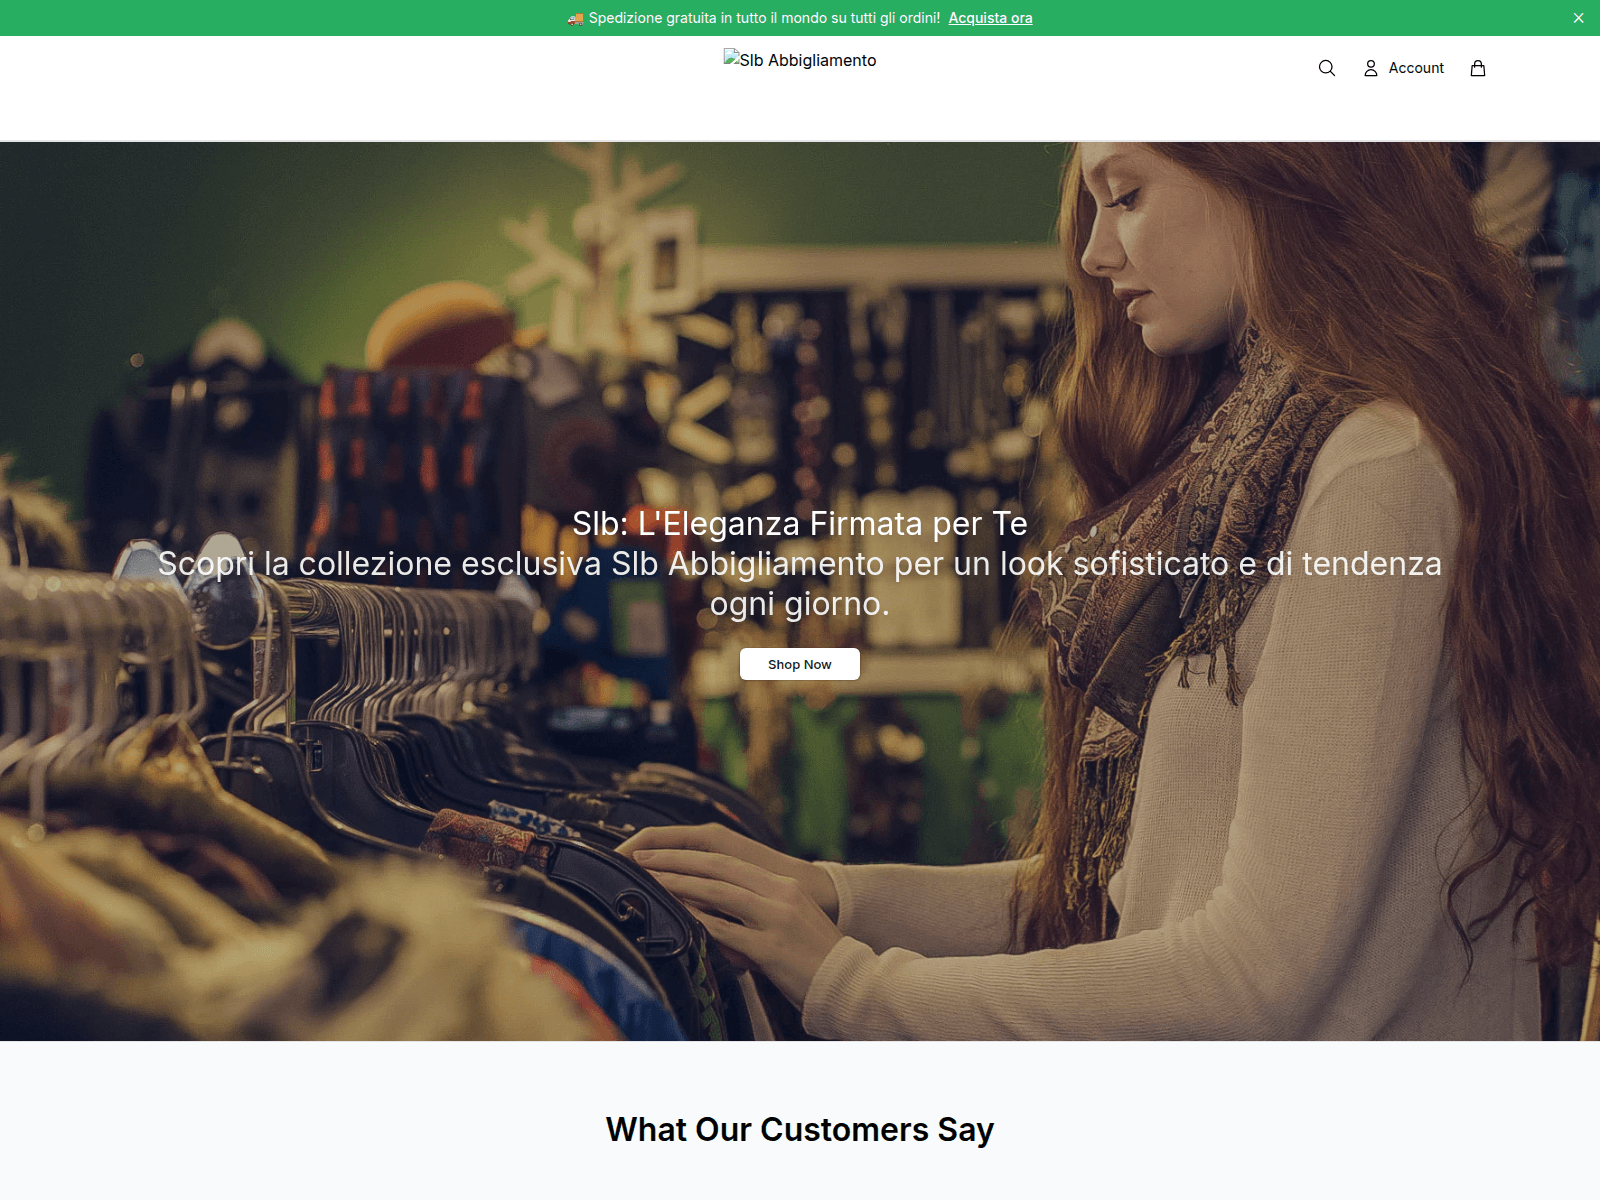
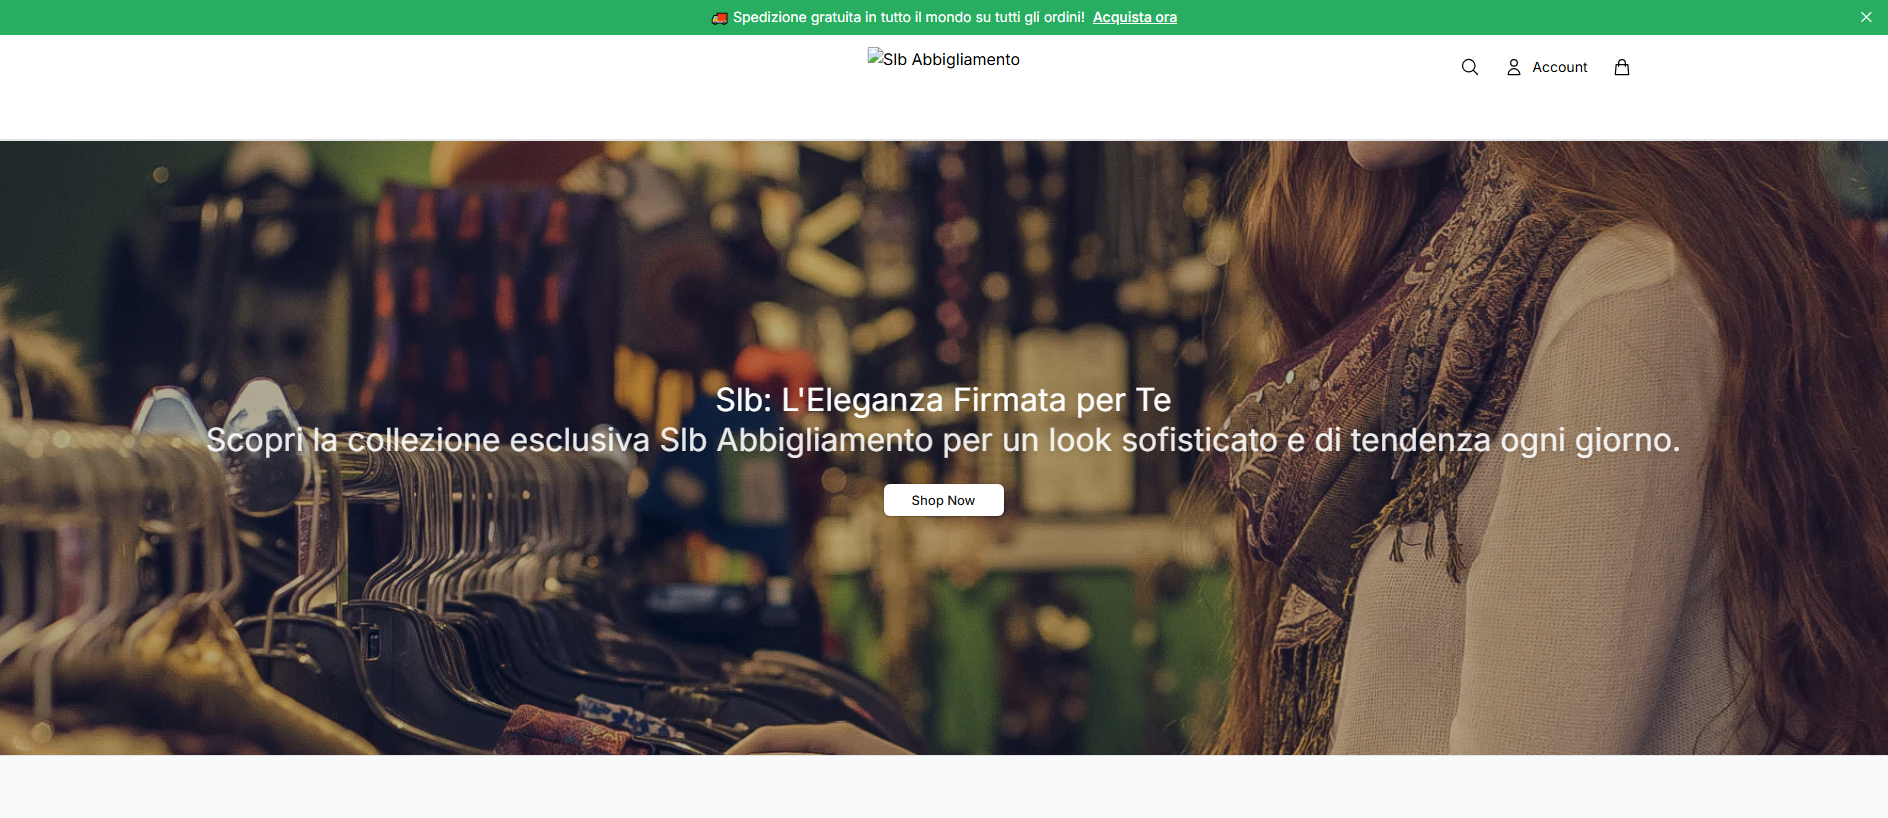
“Abbigliamento Slb | Slb Abbigliamento”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@rashost.com.
The latest stored availability evidence still shows the domain reachable; 23 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| DNS4EU | abbicouture.shop |
malicious | Sinkholed |
On 2026-10-01, abbicouture.shop returned HTTP status 200 in a recorded check, and the domain was first observed on 2026-09-09. A PhishDestroy internal listing also records the domain, while VirusTotal reported 8 detections across 89 scanners on 2026-09-18.
The HTTP check on 2026-10-01 recorded status 200 for abbicouture.shop, and the first observation of the domain is dated 2026-09-09. VirusTotal, checked on 2026-09-18, recorded 8 detections out of 89 scanners. OTX, checked on 2026-09-10, recorded 4 pulses, and the PhishDestroy internal listing records the domain as listed. The SSL scan on 2026-09-09 recorded the issuer as Let's Encrypt / YE2, and the PageSpeed check on the same date recorded a performance score of 69.
The named sources describe separate observations made on their own dates, so the HTTP response, VirusTotal detections, OTX pulses and PhishDestroy listing should be read as distinct records rather than a single combined result. The chronology from first observation to the later checks shows the domain was recorded across multiple dates, but the differing dates alone do not establish a change in behavior. The recorded HTTP status describes only the response captured at that check, not all content served by the domain.
Preserve the HTTP check record for abbicouture.shop and the VirusTotal record as separate source documents for later comparison. Compare the OTX record with the PhishDestroy listing in separate reviews, since each source carries its own observation date. Retain the PageSpeed and SSL scan records alongside the other sources so future checks can be compared against the same set of dated observations.
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
Scanner note: suspended: raw=suspended; http=200; via=https_proxy
aron.ns.cloudflare.comnash.ns.cloudflare.comLocation describes the IP network.
4e4e3cd4d628059d64b39fb733138995240ad30d53cfb47089e47a556674e61bSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of abbicouture.shop · checked Sep 9, 2026
23.252.79.230. 13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
PD-20260909-DB7A2F Recipient: abuse@rashost.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Same favicon hash or the same page title as this host.
These domains also target Linea users. View all Linea threats →
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive