
Search tracked domains and review stored evidence, detections, and the latest observed availability.
223,023
Total Tracked
217,193
VT Detected
93,333
Last Seen Active
129,690
Unavailable at Last Check
1
VT Pending
How This Attack Works
Gambler Scam Panels exploit the allure of gambling to deceive users and extract financial information. Here's a breakdown of how these scams typically unfold:
STEP 1
Enticing Offer
Scammers create convincing gambling websites offering attractive bonuses or winnings.
STEP 2
User Engagement
Victims are drawn in by the promise of easy money and create accounts on these fraudulent platforms.
STEP 3
Data Collection
Scammers collect sensitive personal and financial data under the guise of account verification.
STEP 4
Financial Exploitation
Collected data is used for unauthorized transactions, leading to financial loss for the victim.
Technical Analysis
Gambler Scam Panels often utilize spoofed gambling websites that mimic legitimate platforms. Attackers use phishing kits to create replicas of popular gambling sites, embedding malicious scripts that capture user data. These sites are hosted on domains registered with less-regulated registrars like NICENIC INTERNATIONAL GROUP CO., LIMITED, WEBCC, and Dominet (HK) Limited. Additionally, they may leverage obfuscated JavaScript to hide malicious activities from casual inspection. In some cases, these scams involve fake cryptocurrency gambling, where smart contracts are manipulated to always favor the scammer, utilizing functions that are poorly documented and hard to audit.
Real Cases
SpinWin Scam (2024)
$2 million stolen
Users were lured by promises of high returns on a fake cryptocurrency gambling site, resulting in significant financial losses.
QuickBet Fraud (2023)
$1.5 million stolen
This scam used a well-designed imitation of a major gambling platform to collect user data and funds.
LuckyStrike Hoax (2024)
$3 million stolen
A fake lottery site that promised huge winnings but instead harvested sensitive financial information from users.
How to Detect
Unusually high bonuses or winnings promised
Poor website design with multiple typos
Unsecured website (missing HTTPS)
Unusually urgent demands for personal information
Domain registered recently with a non-reputable registrar
How to Protect Yourself
1
Verify the legitimacy of gambling sites before using them
2
Use secure passwords and two-factor authentication
3
Be wary of sites with unsecured connections
4
Regularly monitor financial statements for unauthorized transactions
5
Report suspicious sites to authorities and platforms like PhishDestroy
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 10,197 domains tracked for this threat type
Gambler Scam Panel 10,197 domains

letorex.com

linegambt.fun
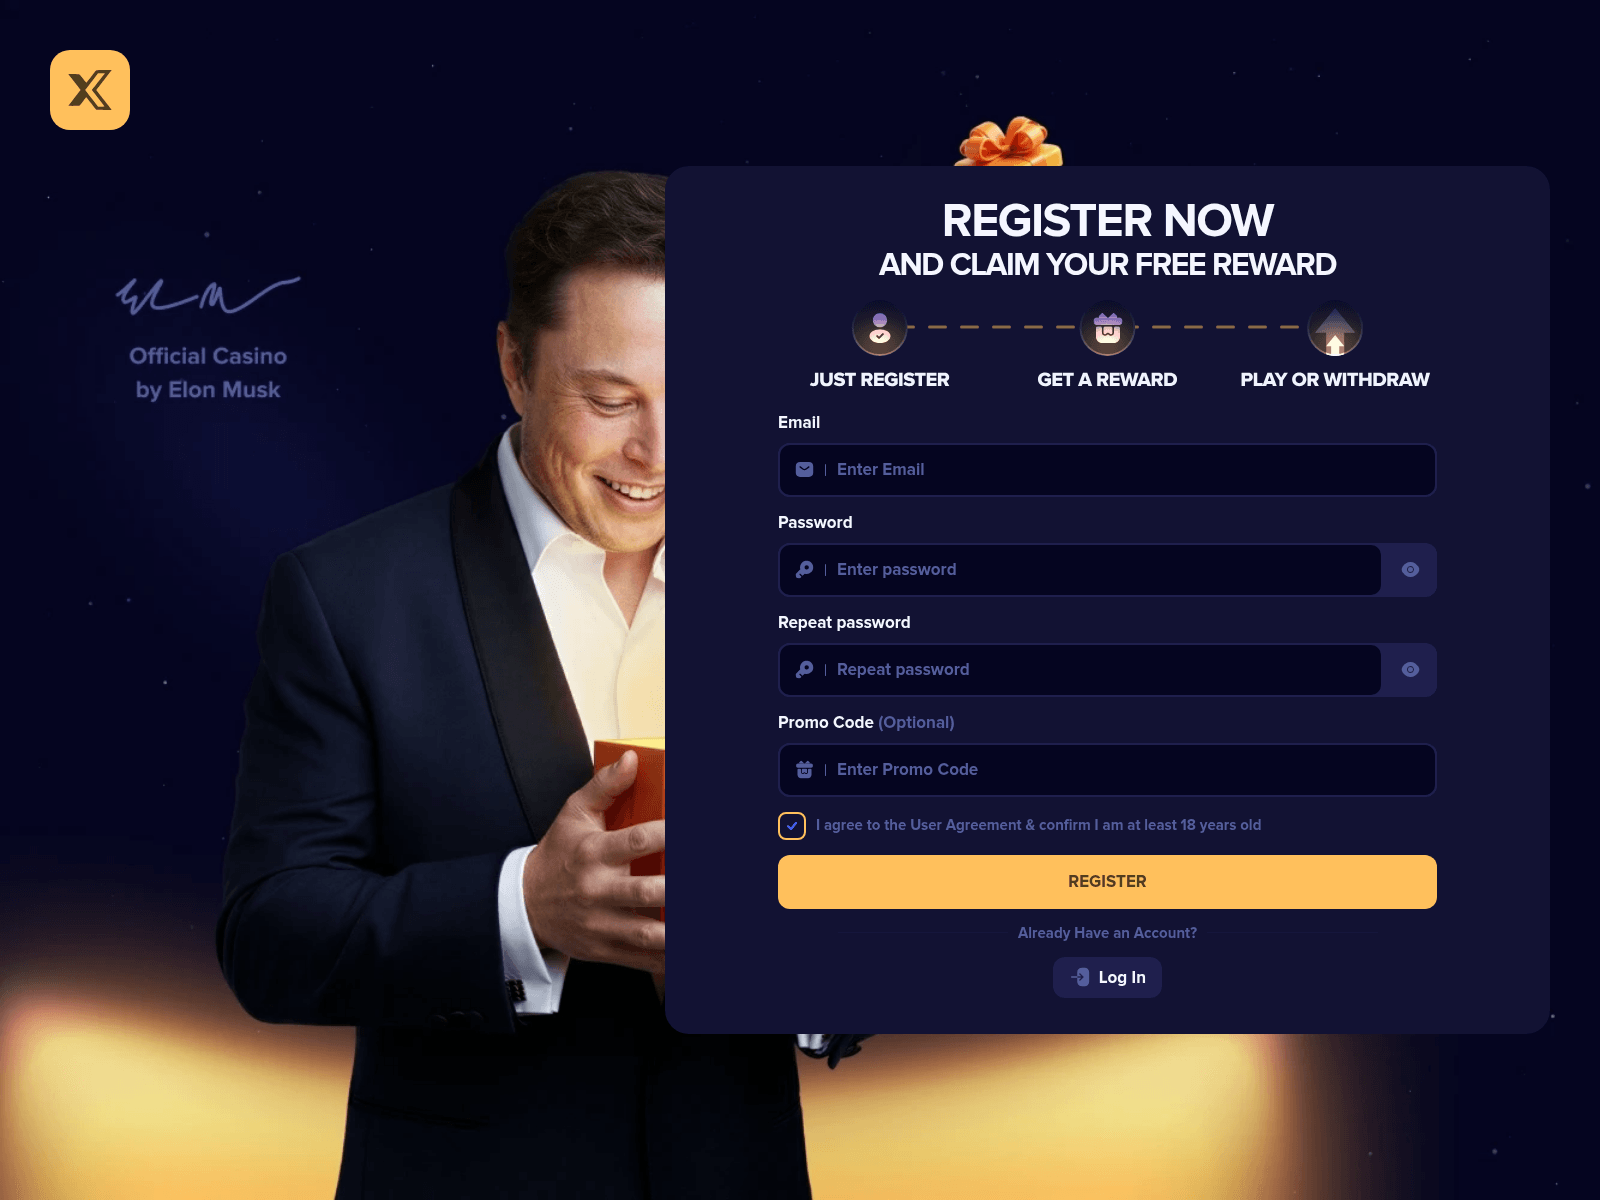
litgert.com

lixfort.com

lixgold.com

lixzeno.com
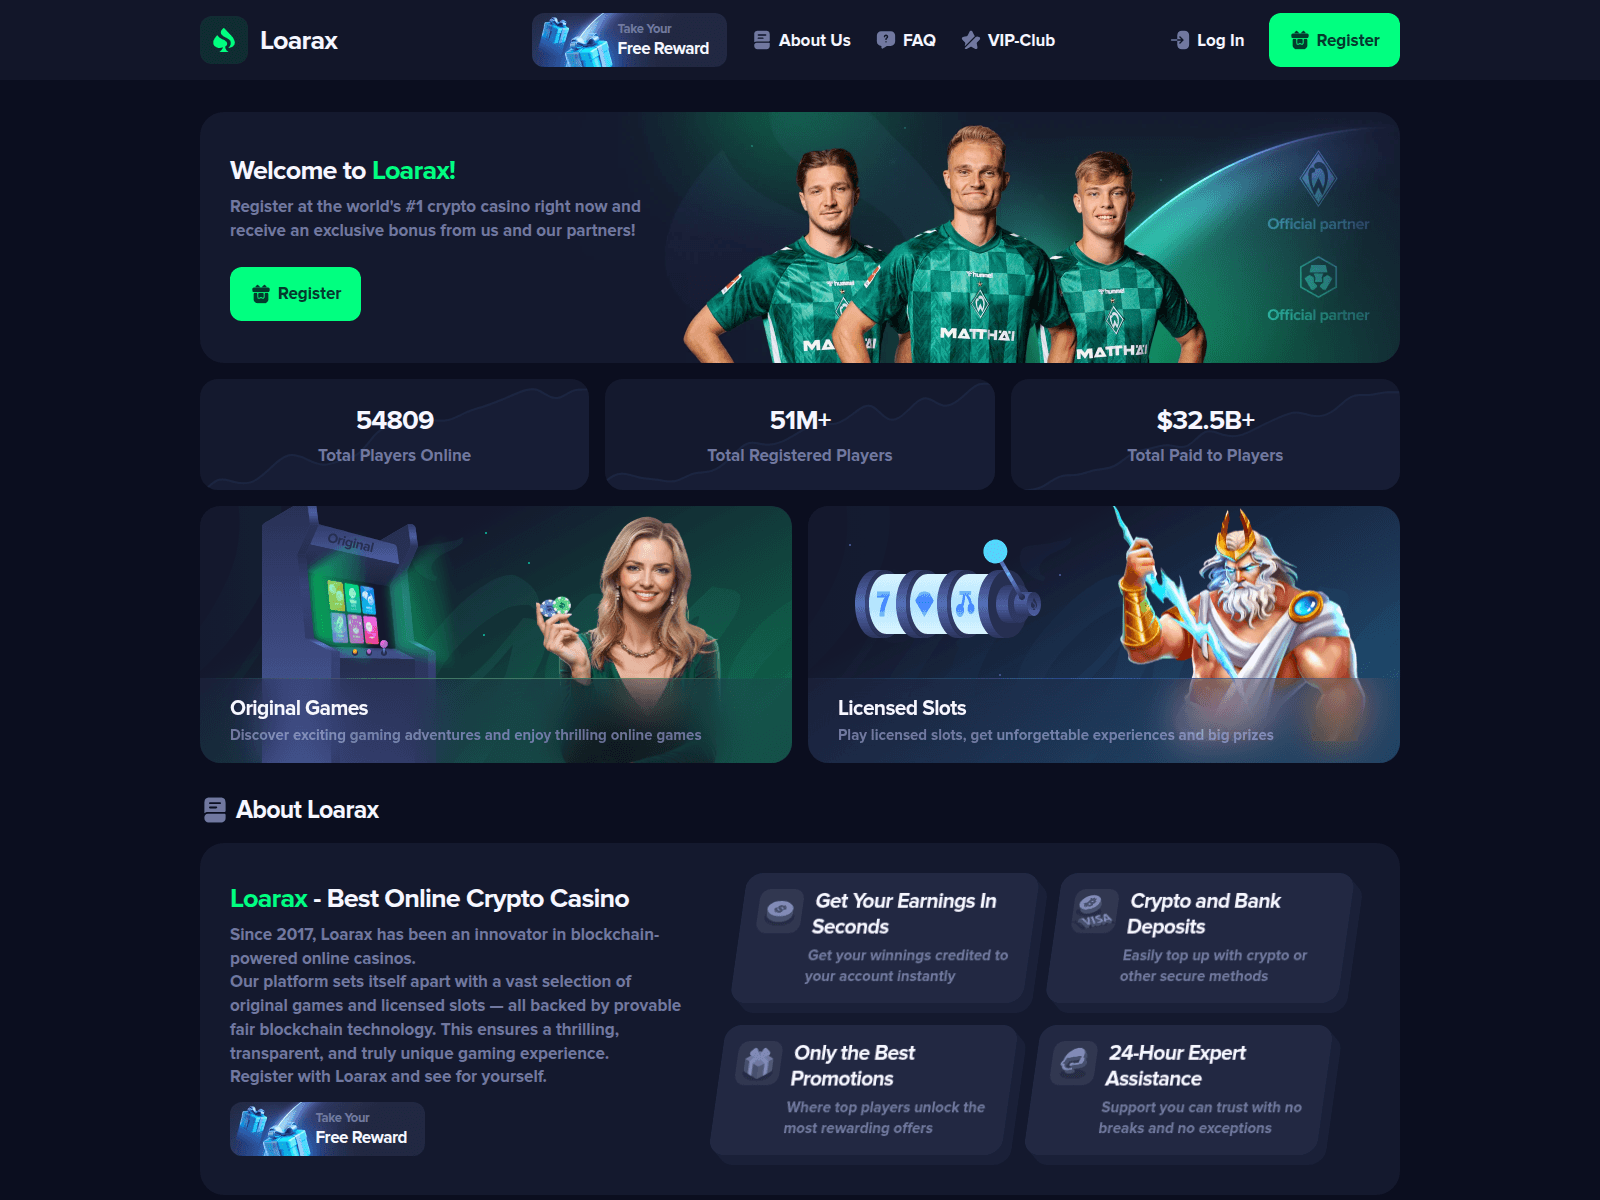
loarax.com
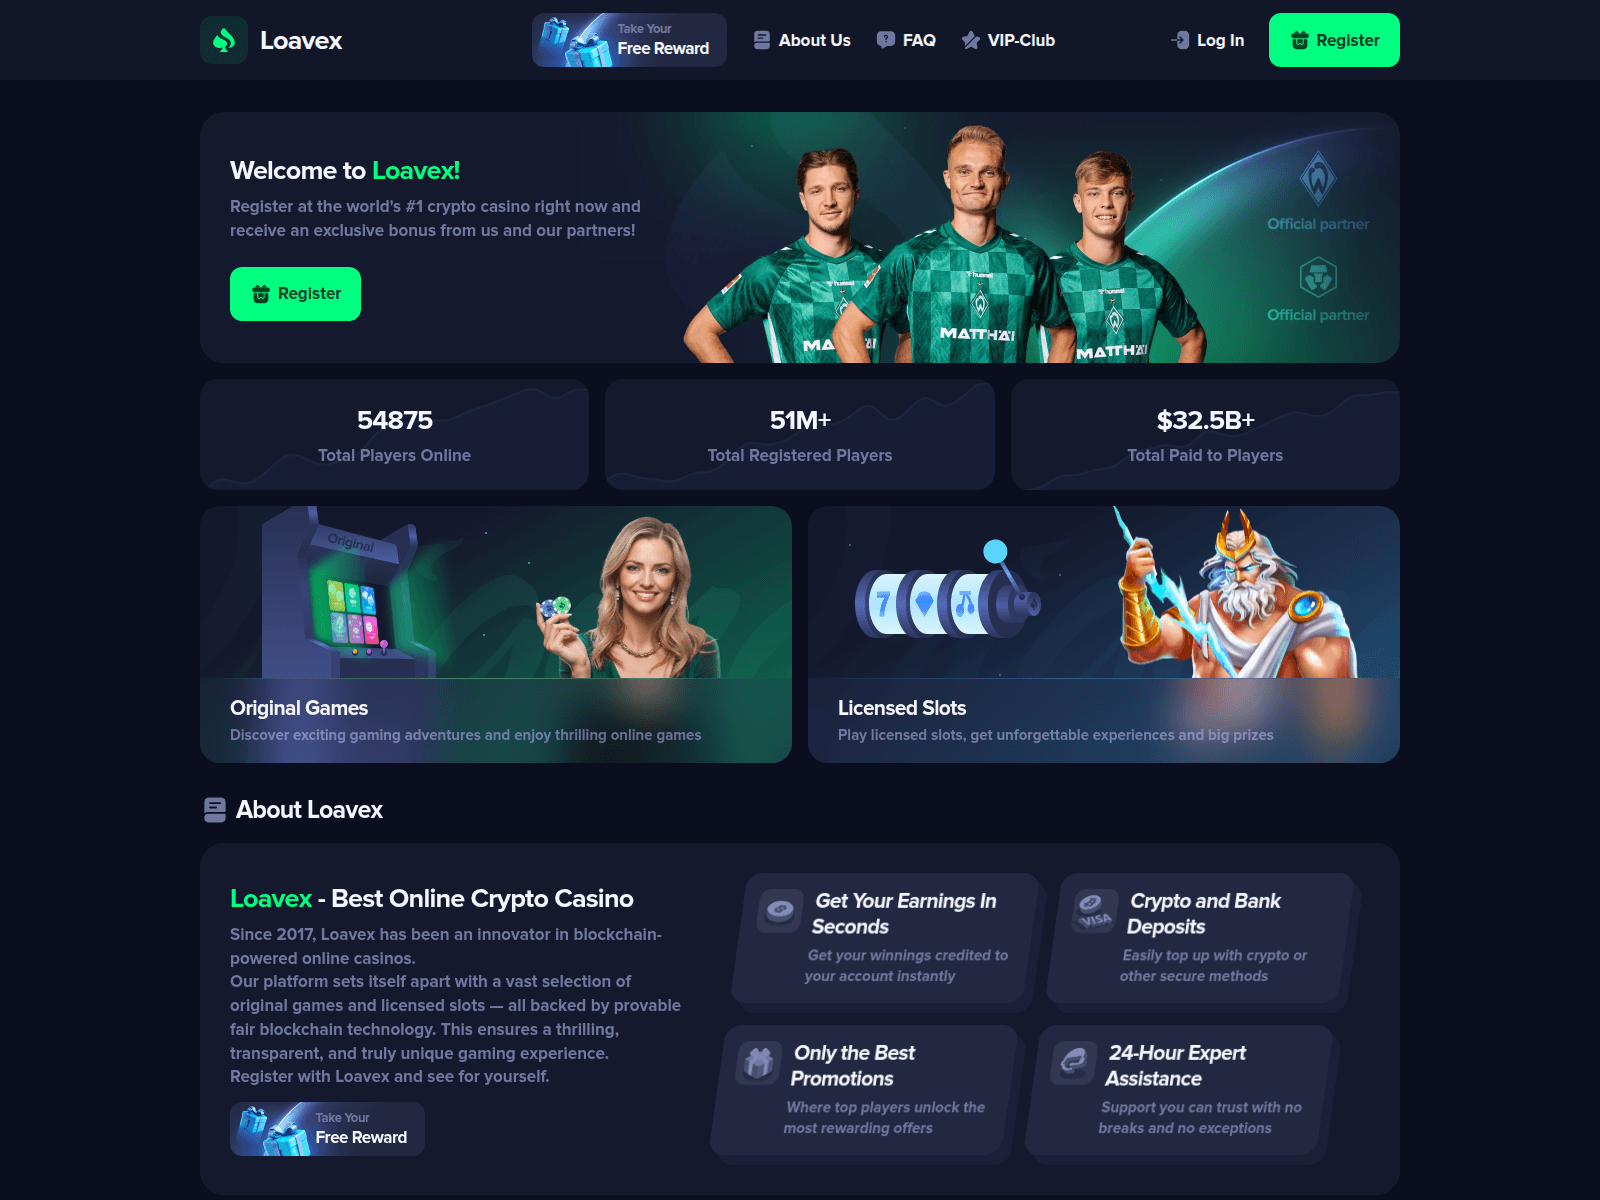
loavex.com

lococas.xyz

loggitex.com

lopugamb.com

losangeleswin.top
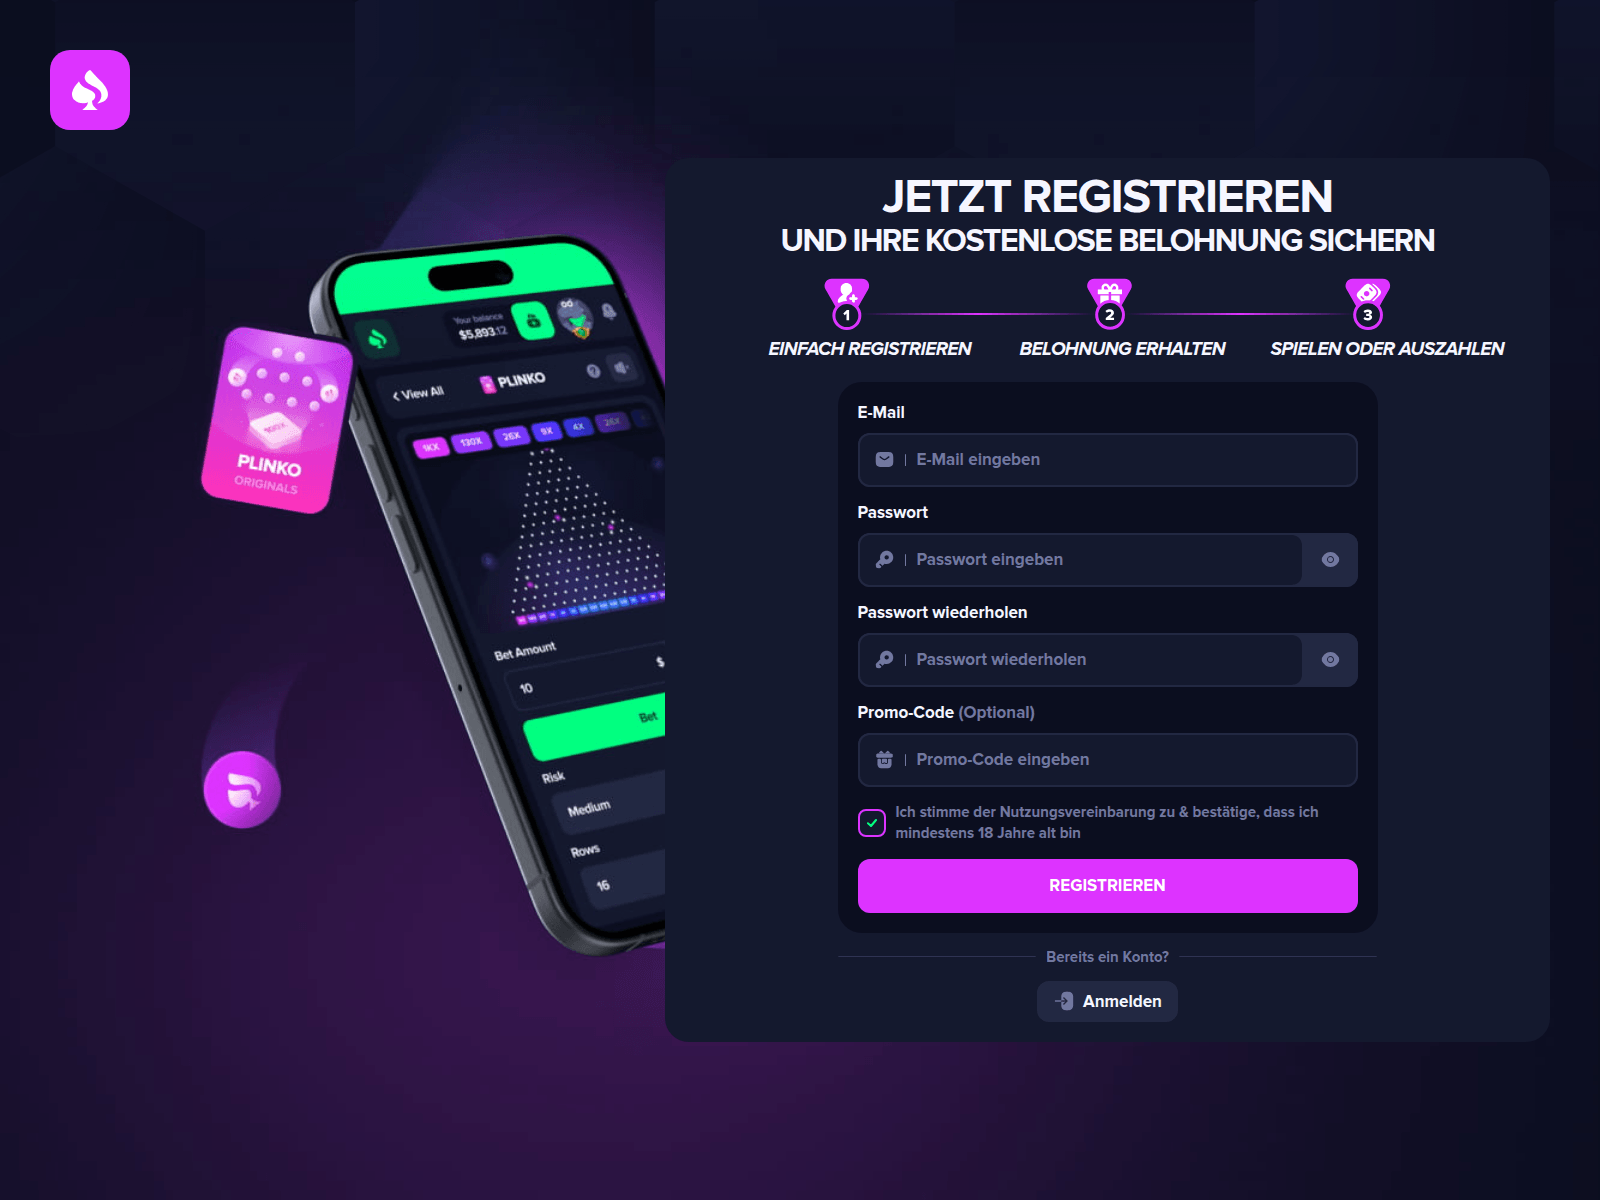
luckstrike.top

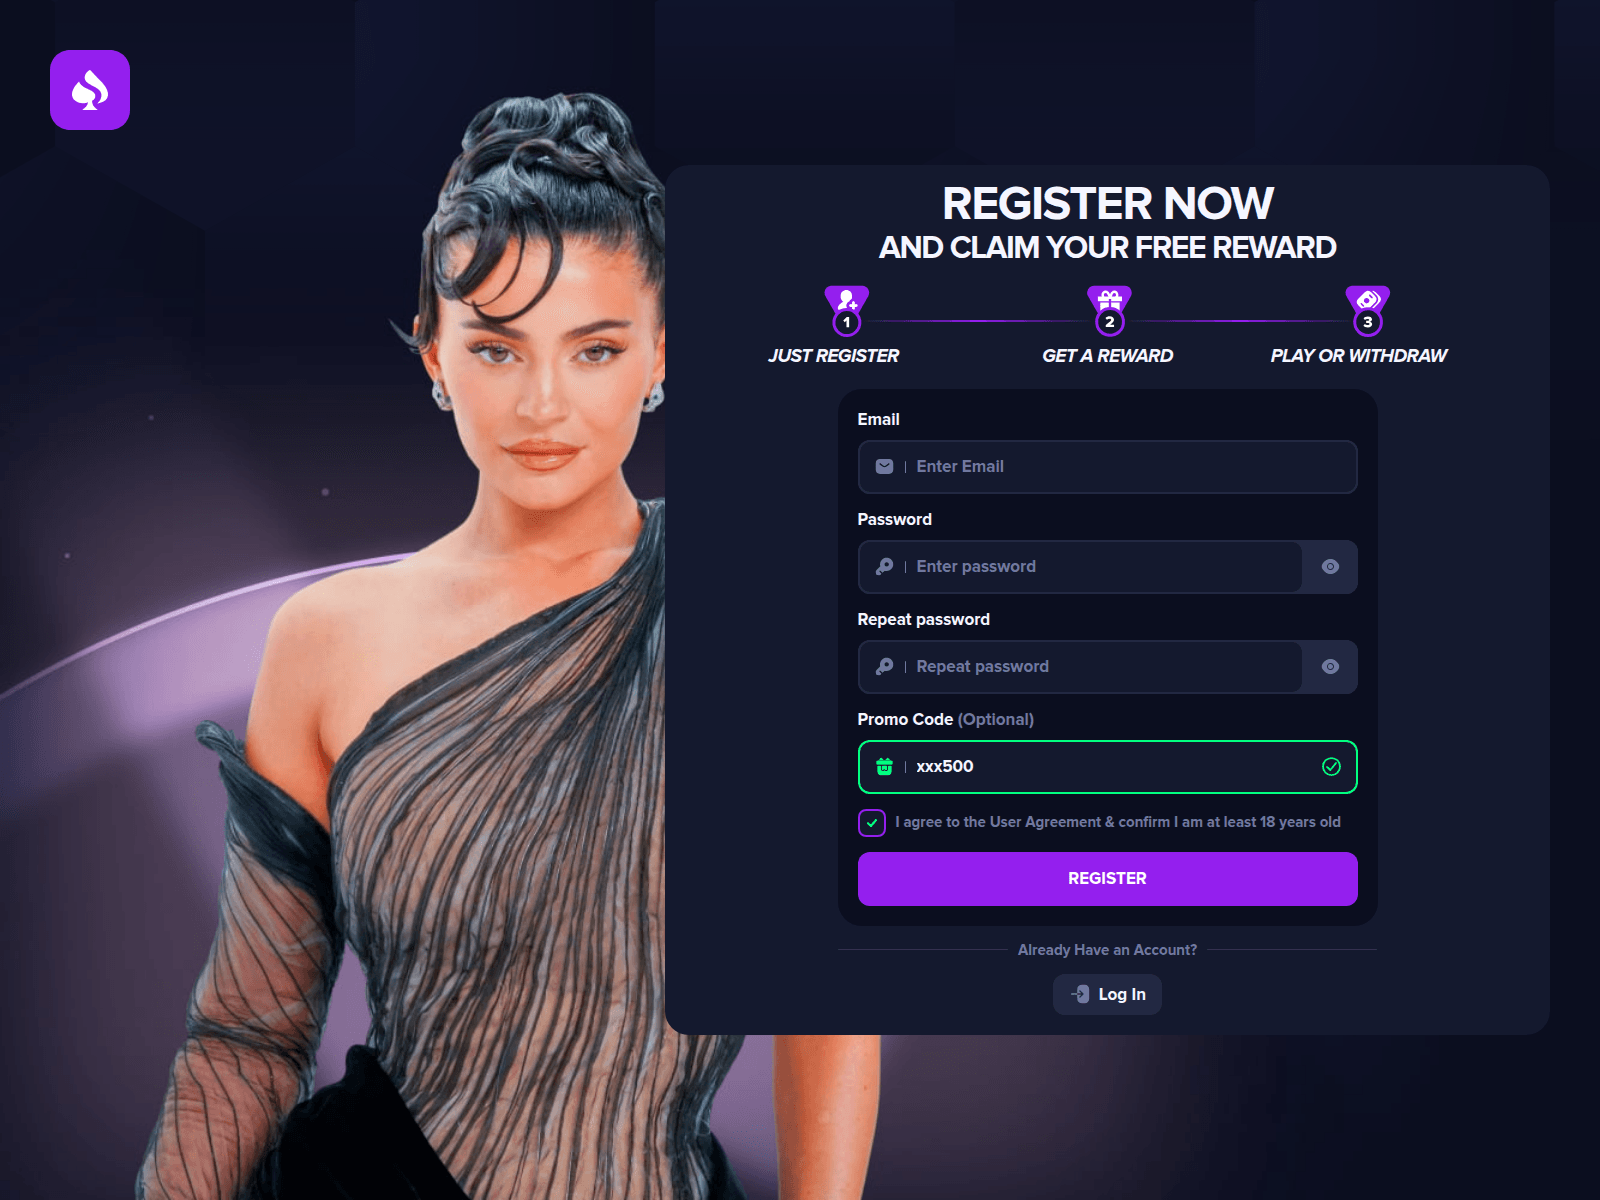
luckybooms.top

luckyclash.online

luckygo.live

luminbet.com

lummicasino.vip
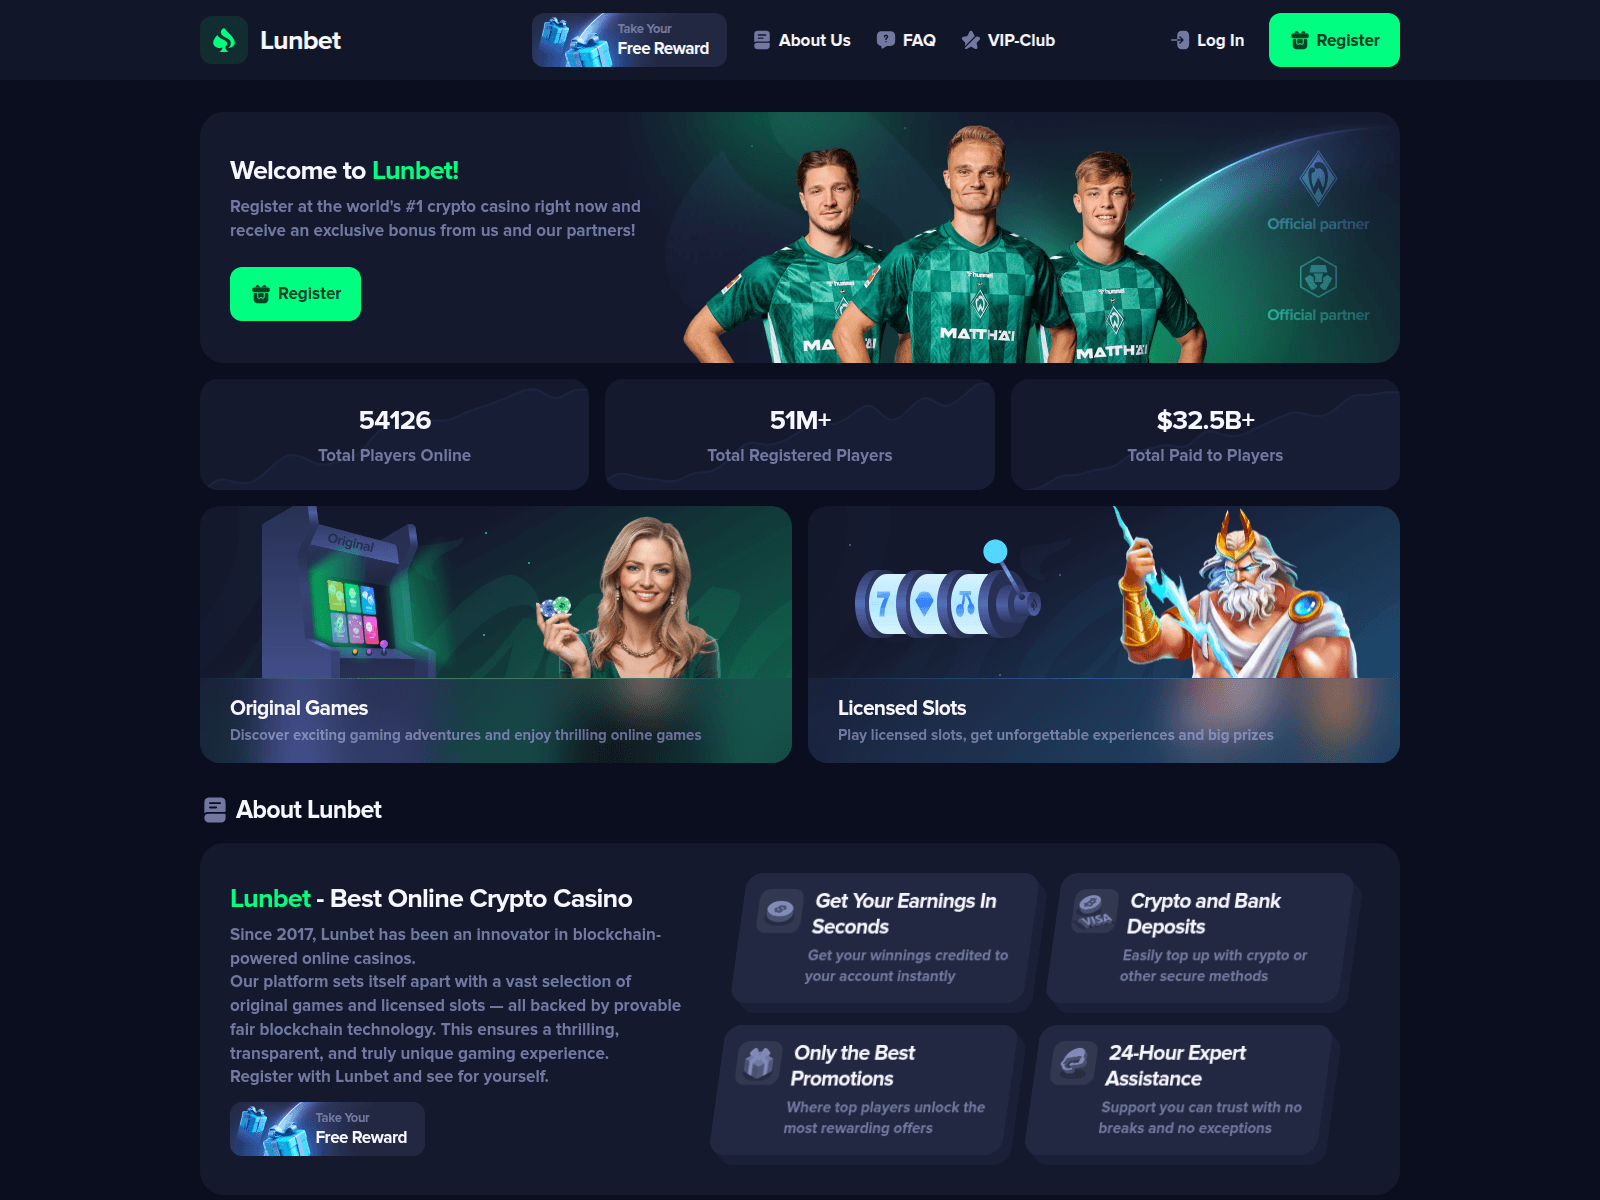
lunbet.cc

luncas.com

lunocas.com
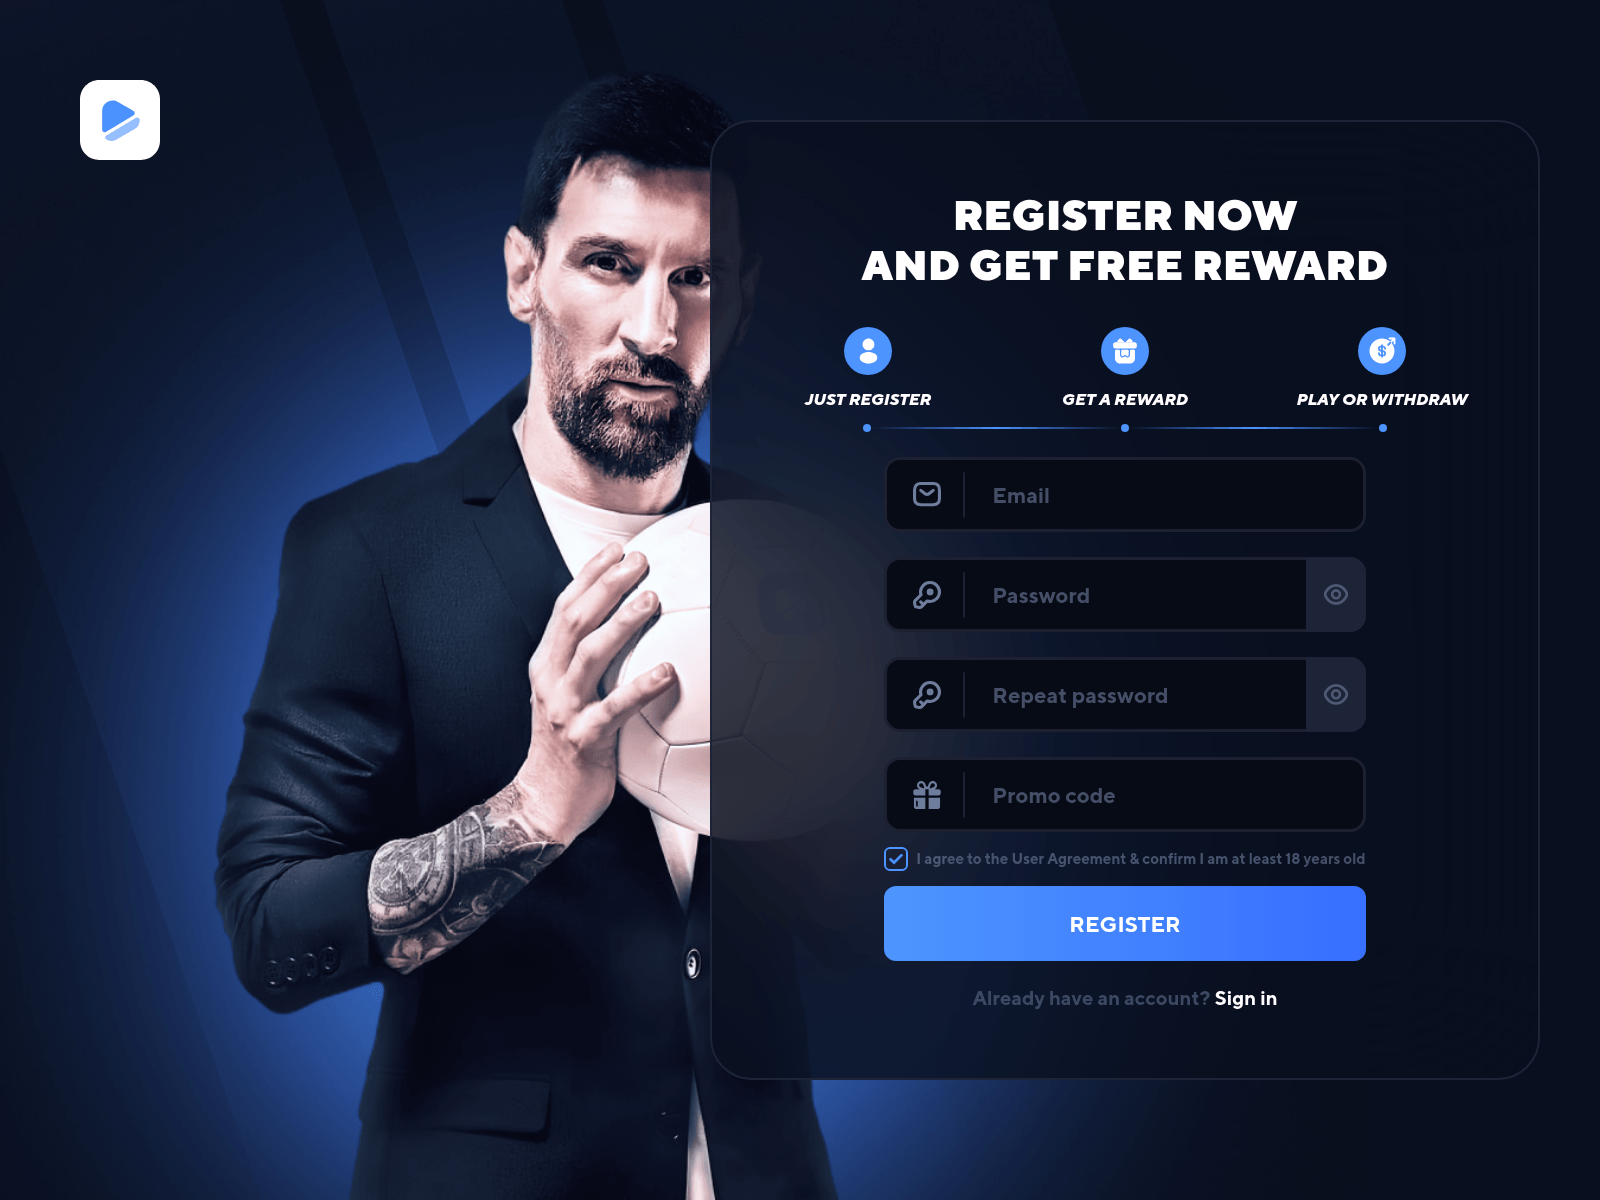
luxurywinclub.live
luxwex.com

mainapi2.vip

majora.top

marginbet.cc
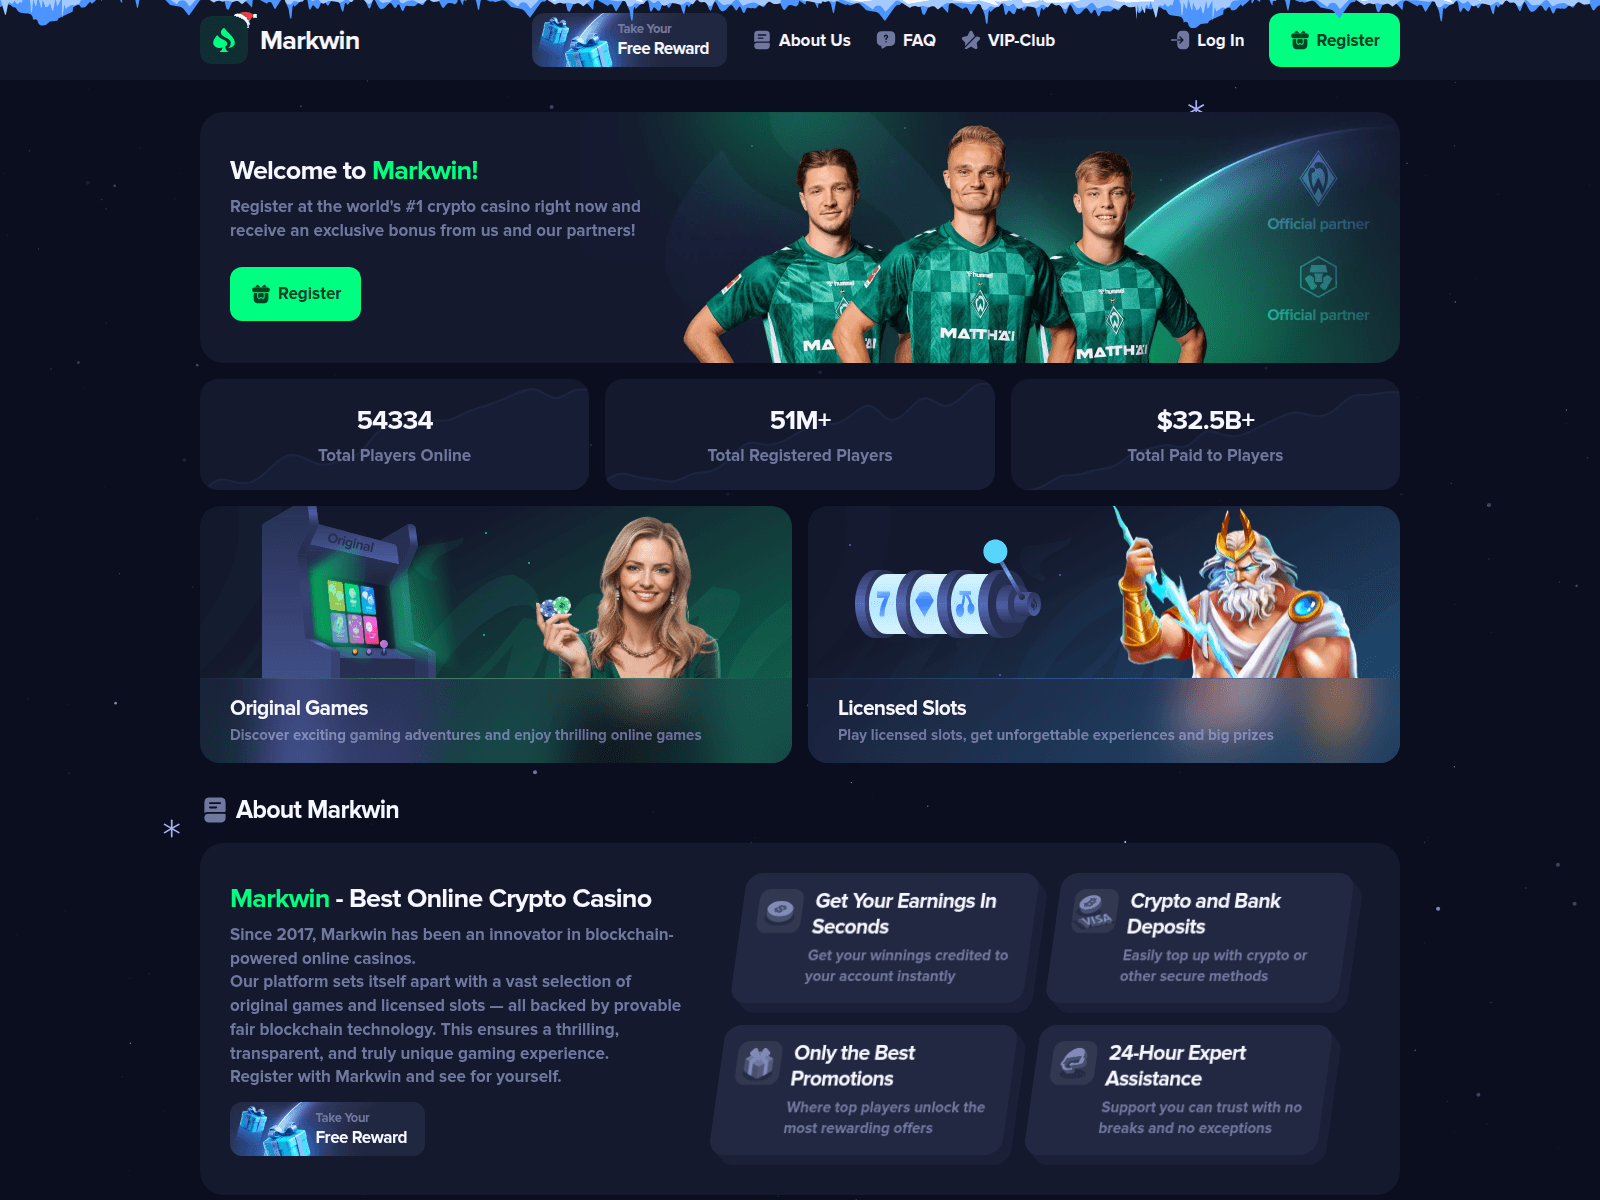
markwin.xyz

master-betting.net

mavinabet.top
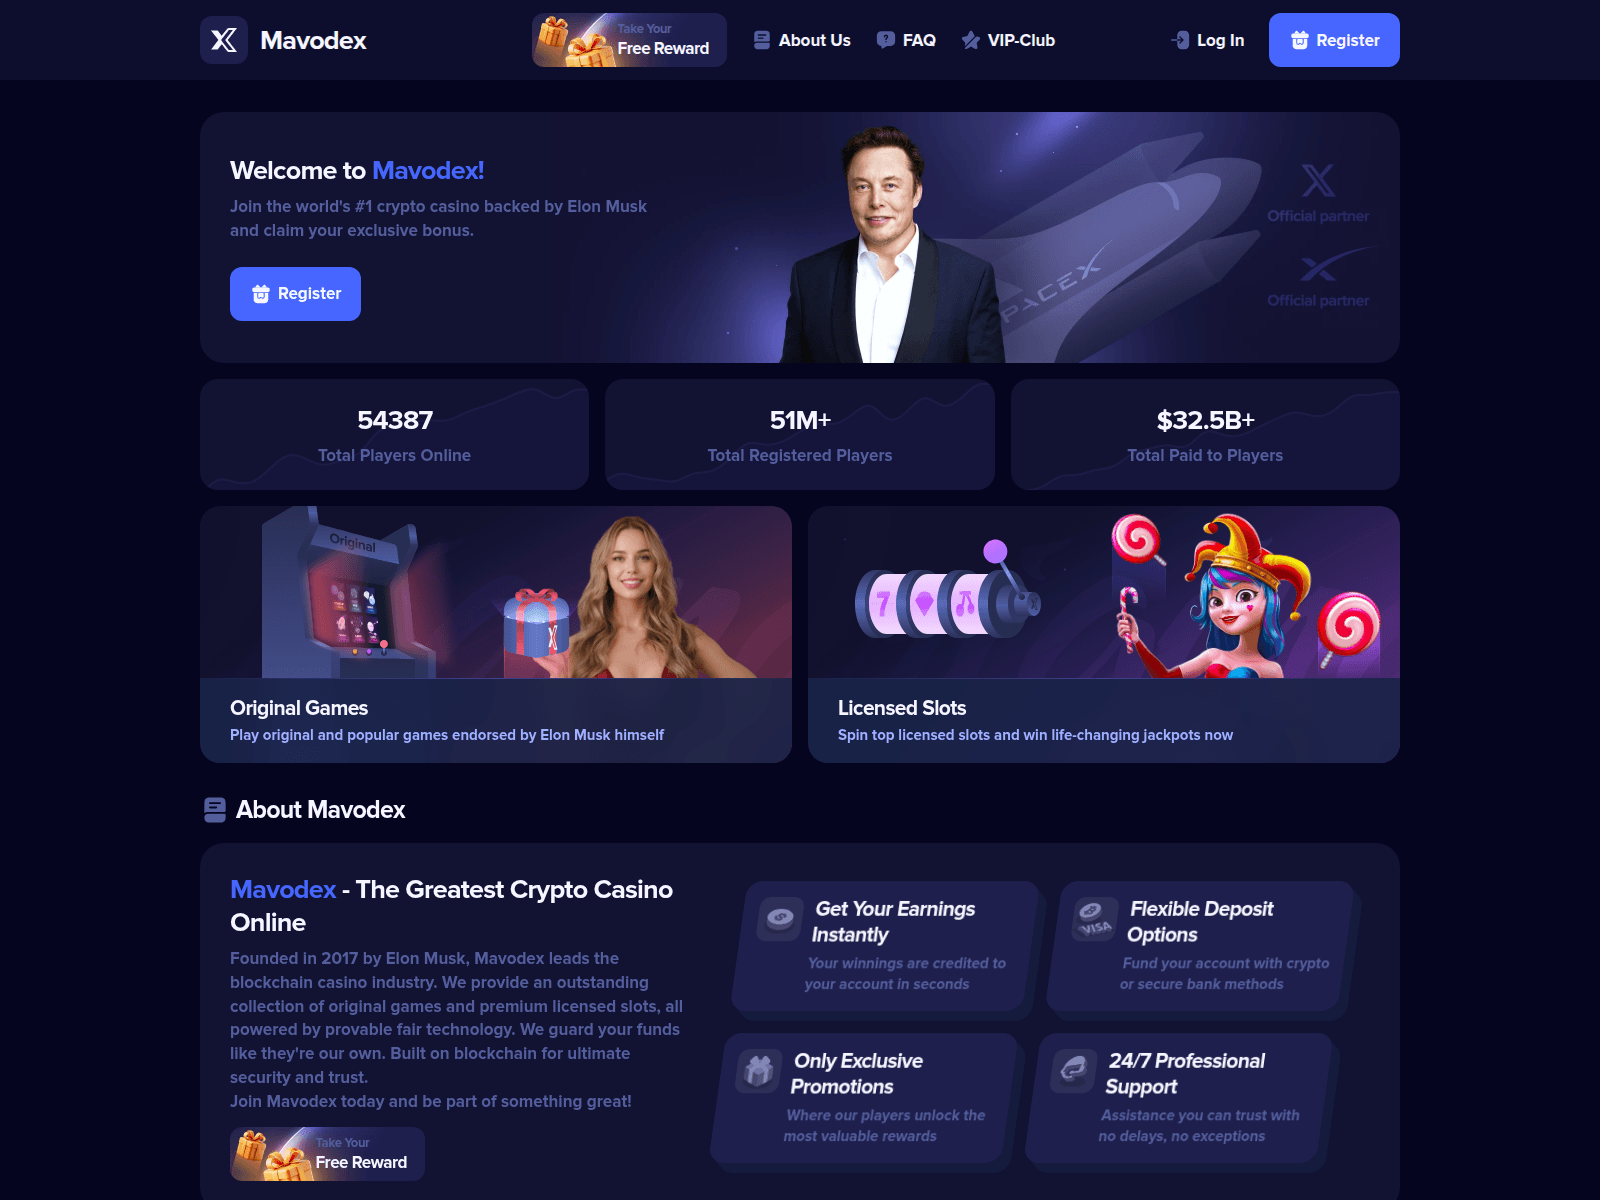
mavodex.com

medogex.com
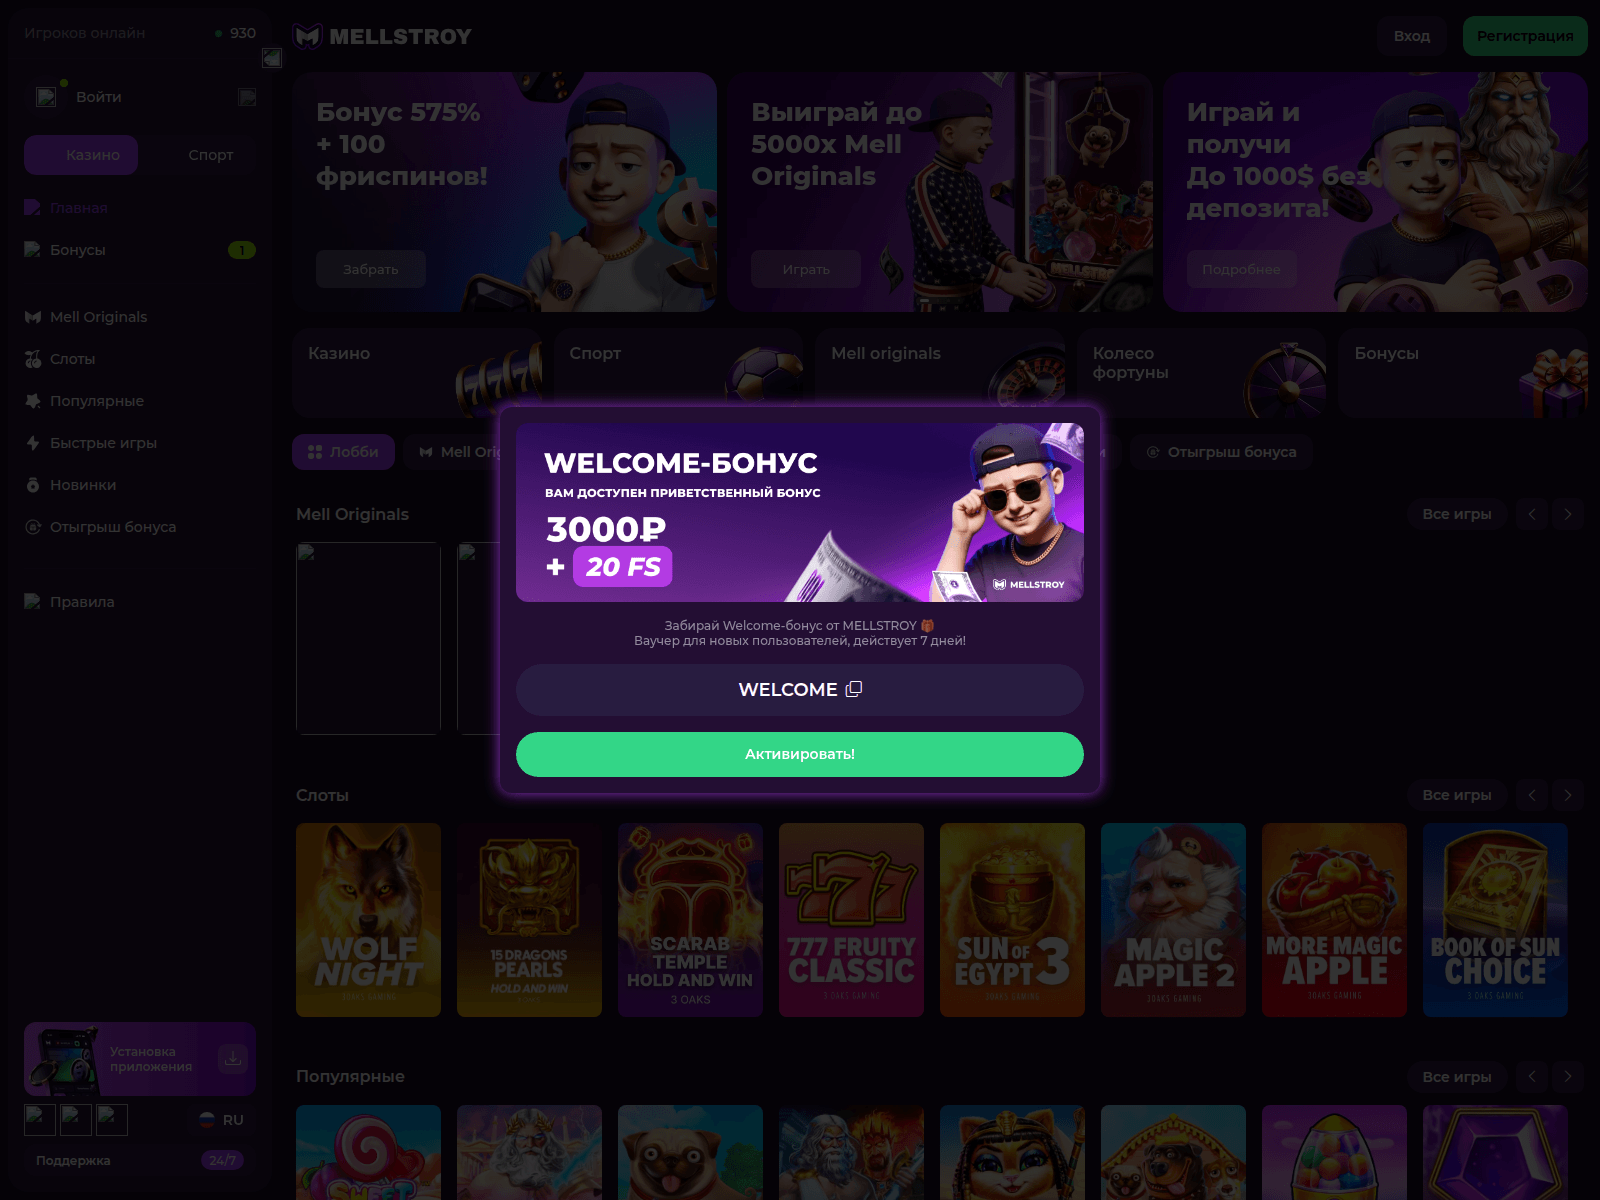
mellwins.games

meotax.com
milbeto.com
miolax.com
miukas.com

molbets.com
moondepo.com

moonrollcasino.com
mopewex.com

moveplays.com

mrtrumpcasino.bet

munovbet.com
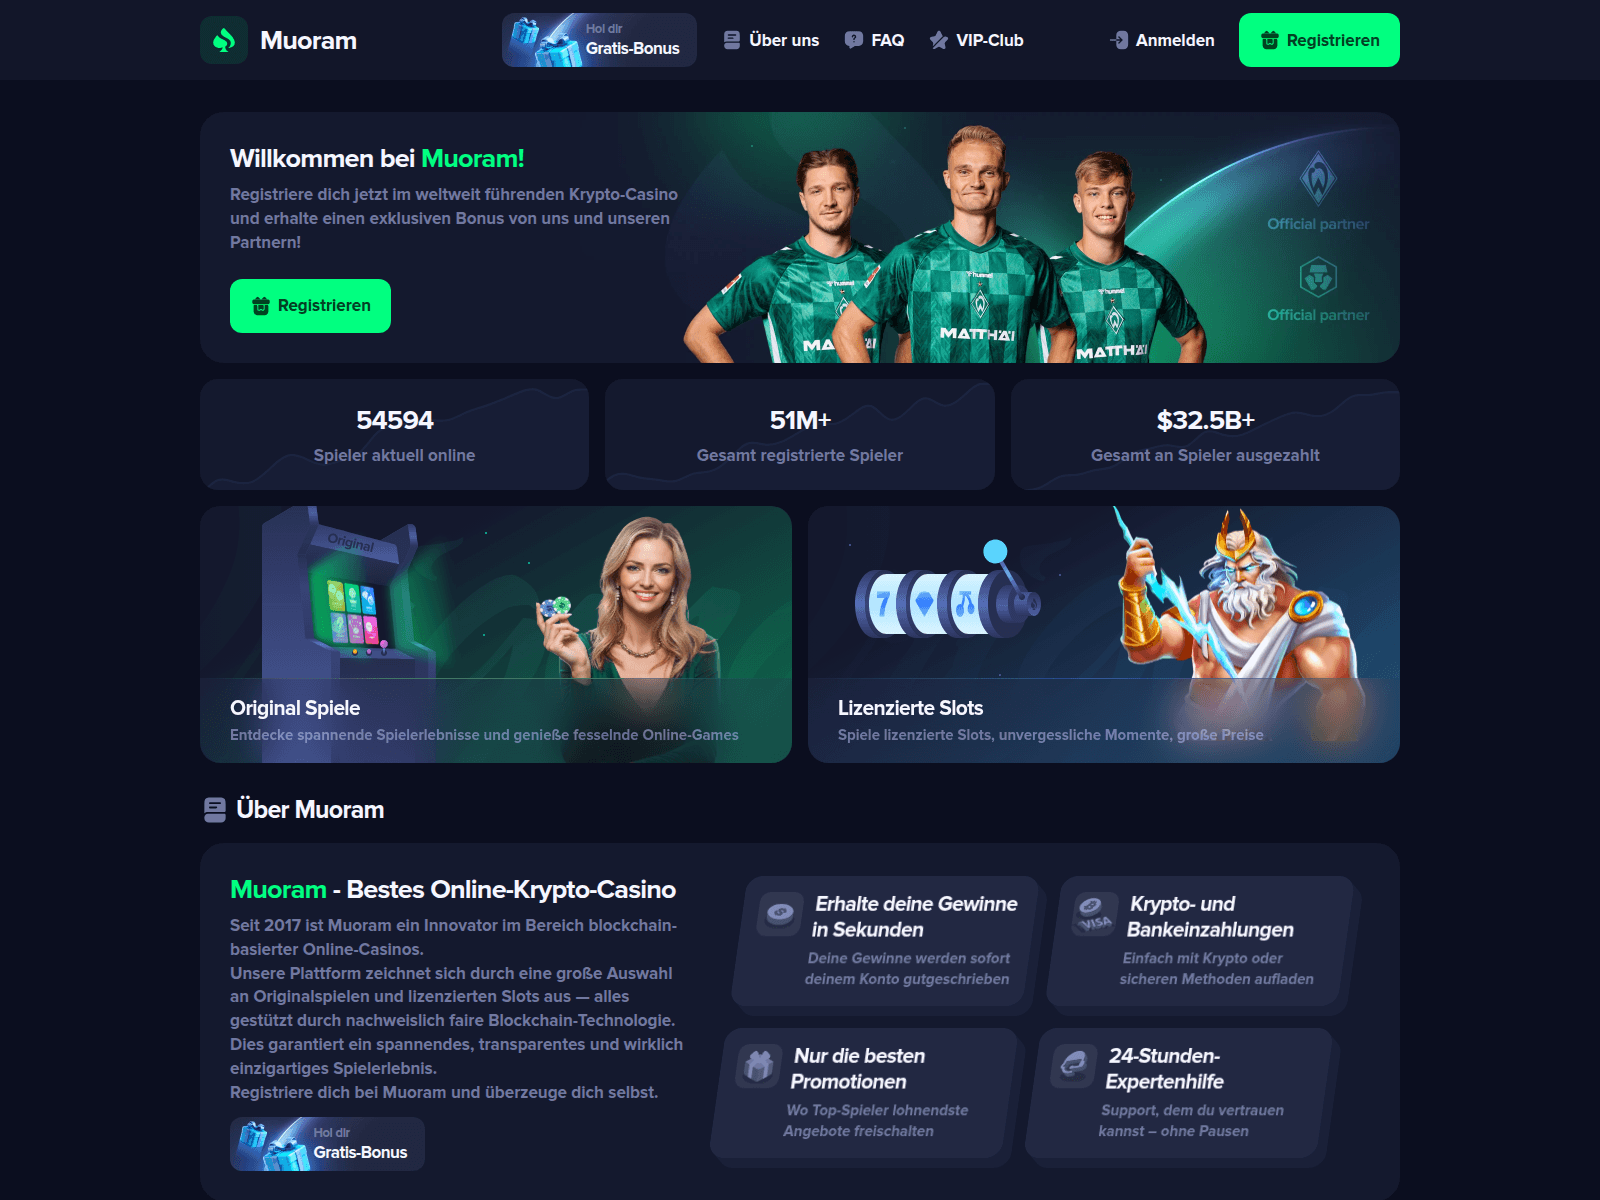
muoram.com

muraze.com

musk-bet.com

muskgamb.com

muskstake.com

musurio.space

mycas.bet

mythblast.com

nedofex.com

nelkas.com

new-shuffle.com

newstakes.vip

nexusbetx.com
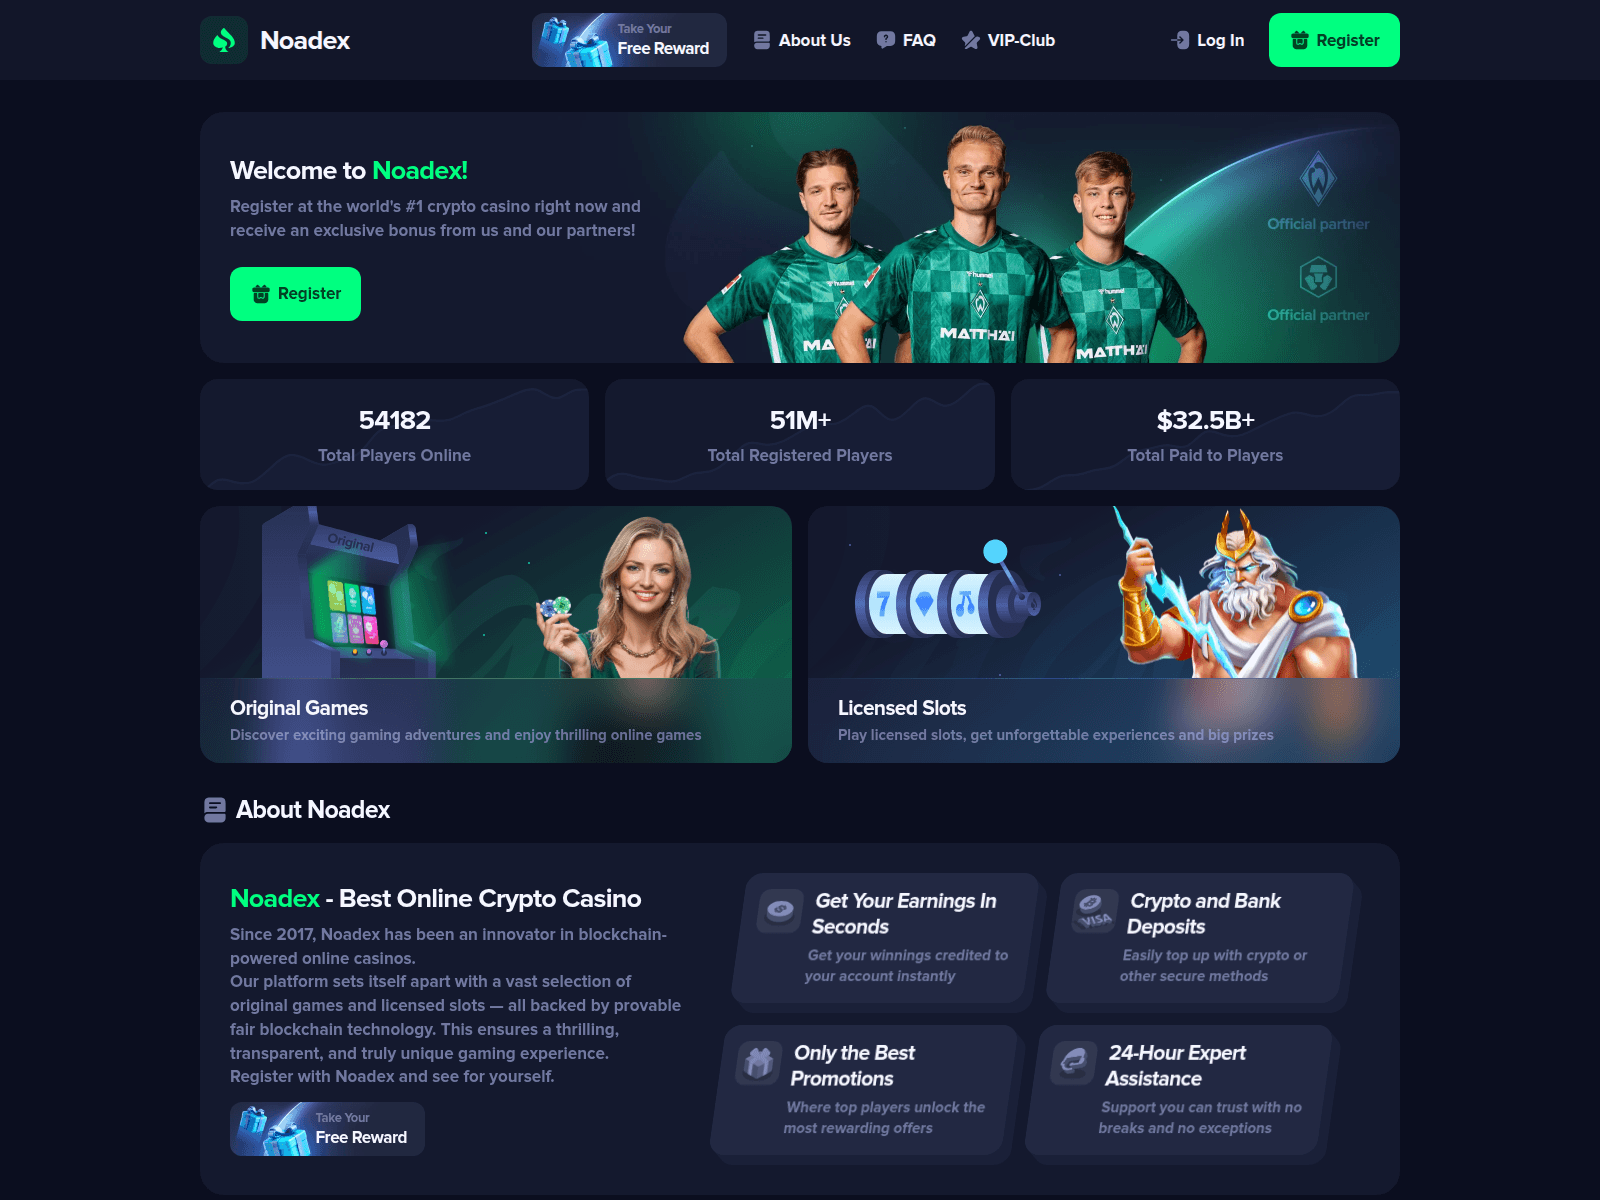
noadex.com

noavax.win

noblecas.com

nodplays.com

nomcase.com

nooxcas.com

nosmex.com

noxfort.com

nozewin.com

nulocas.com

nuzwex.com

olympus369.net
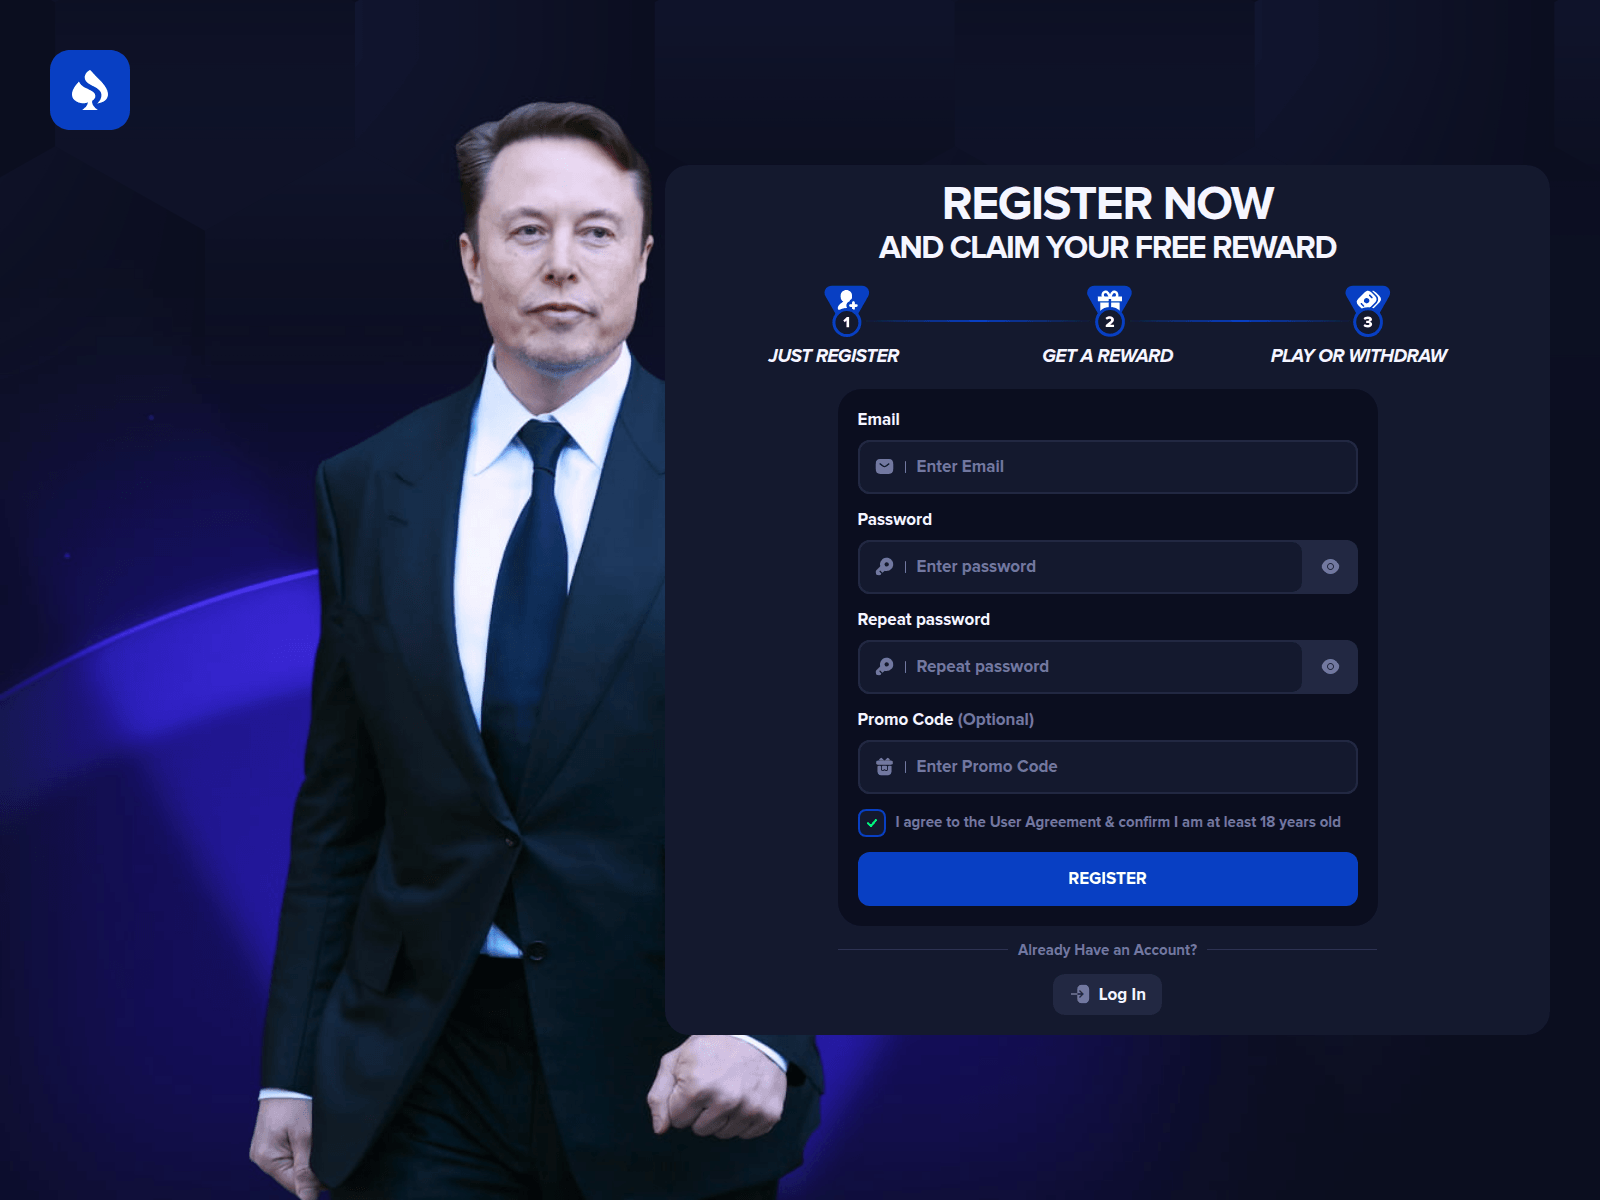
omawon.com

orbiantex.com

osbeto.com

ovoroyal.com

ovowave.com

ovowins.com

oxcas.com

ozalplays.com

page-c0k.pages.dev

palacexbet.com
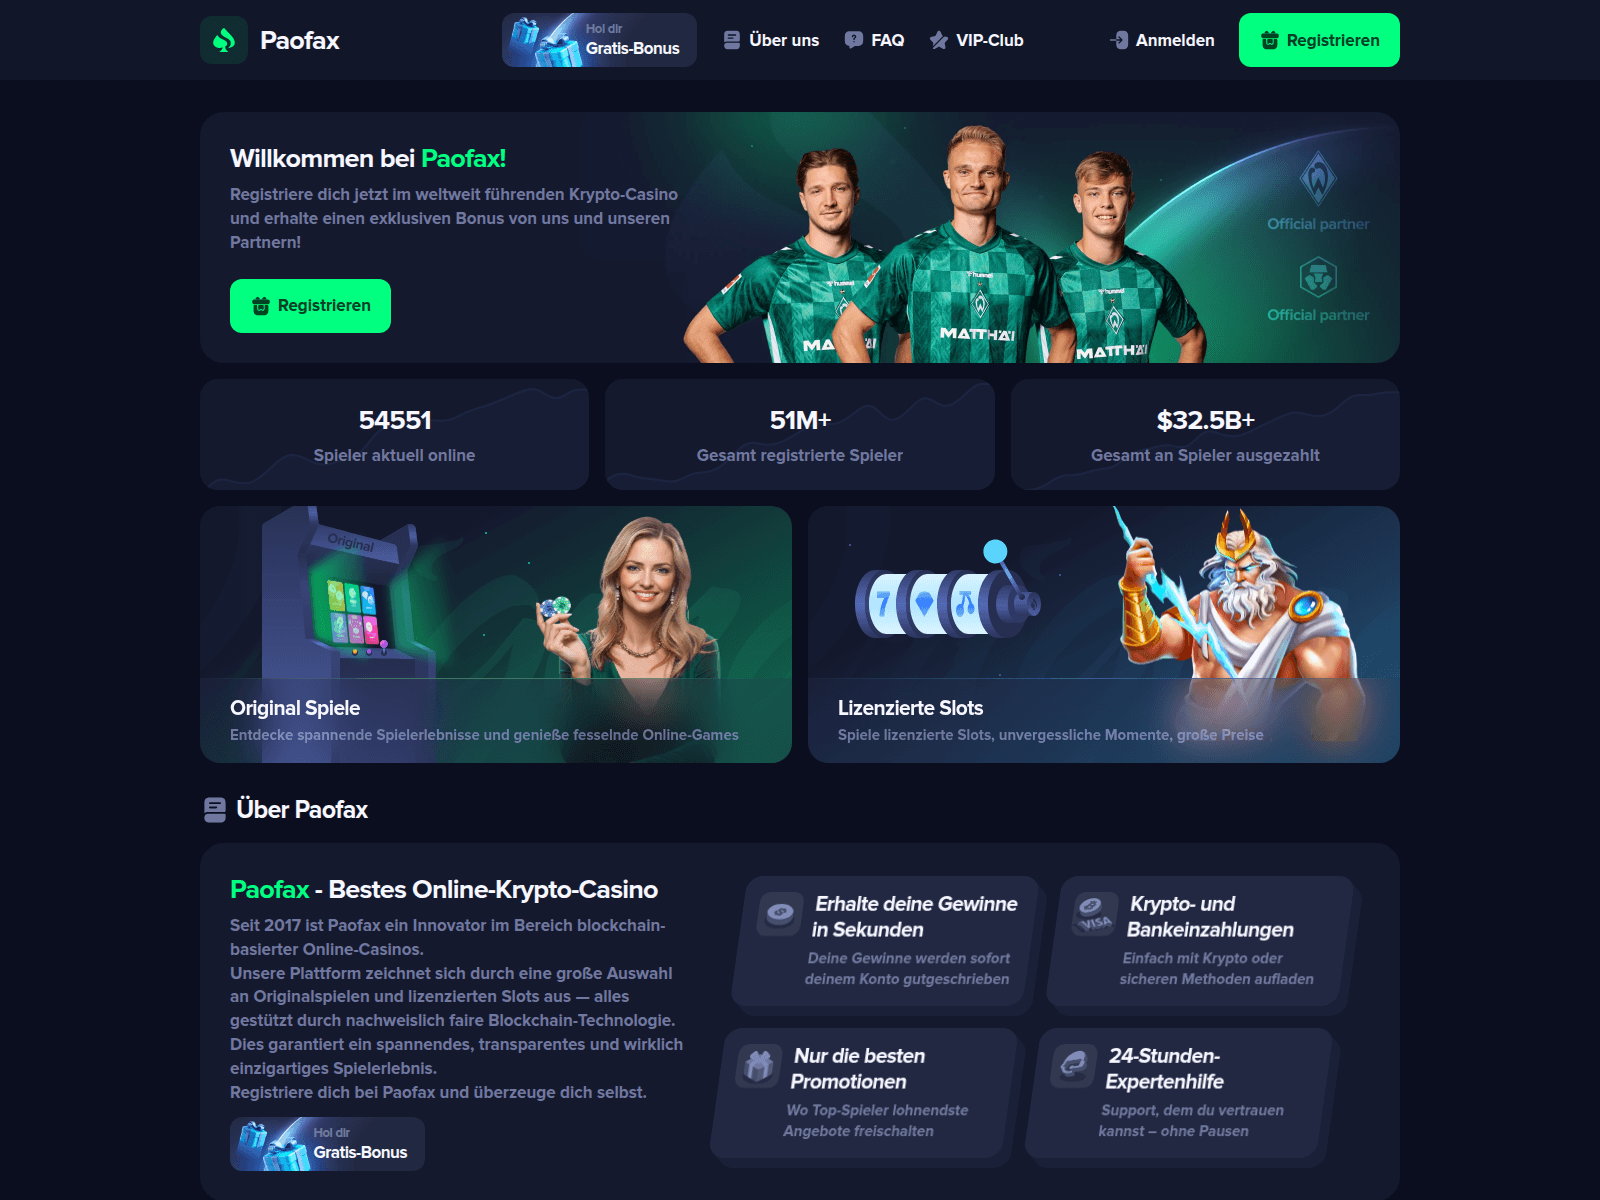
paofax.com
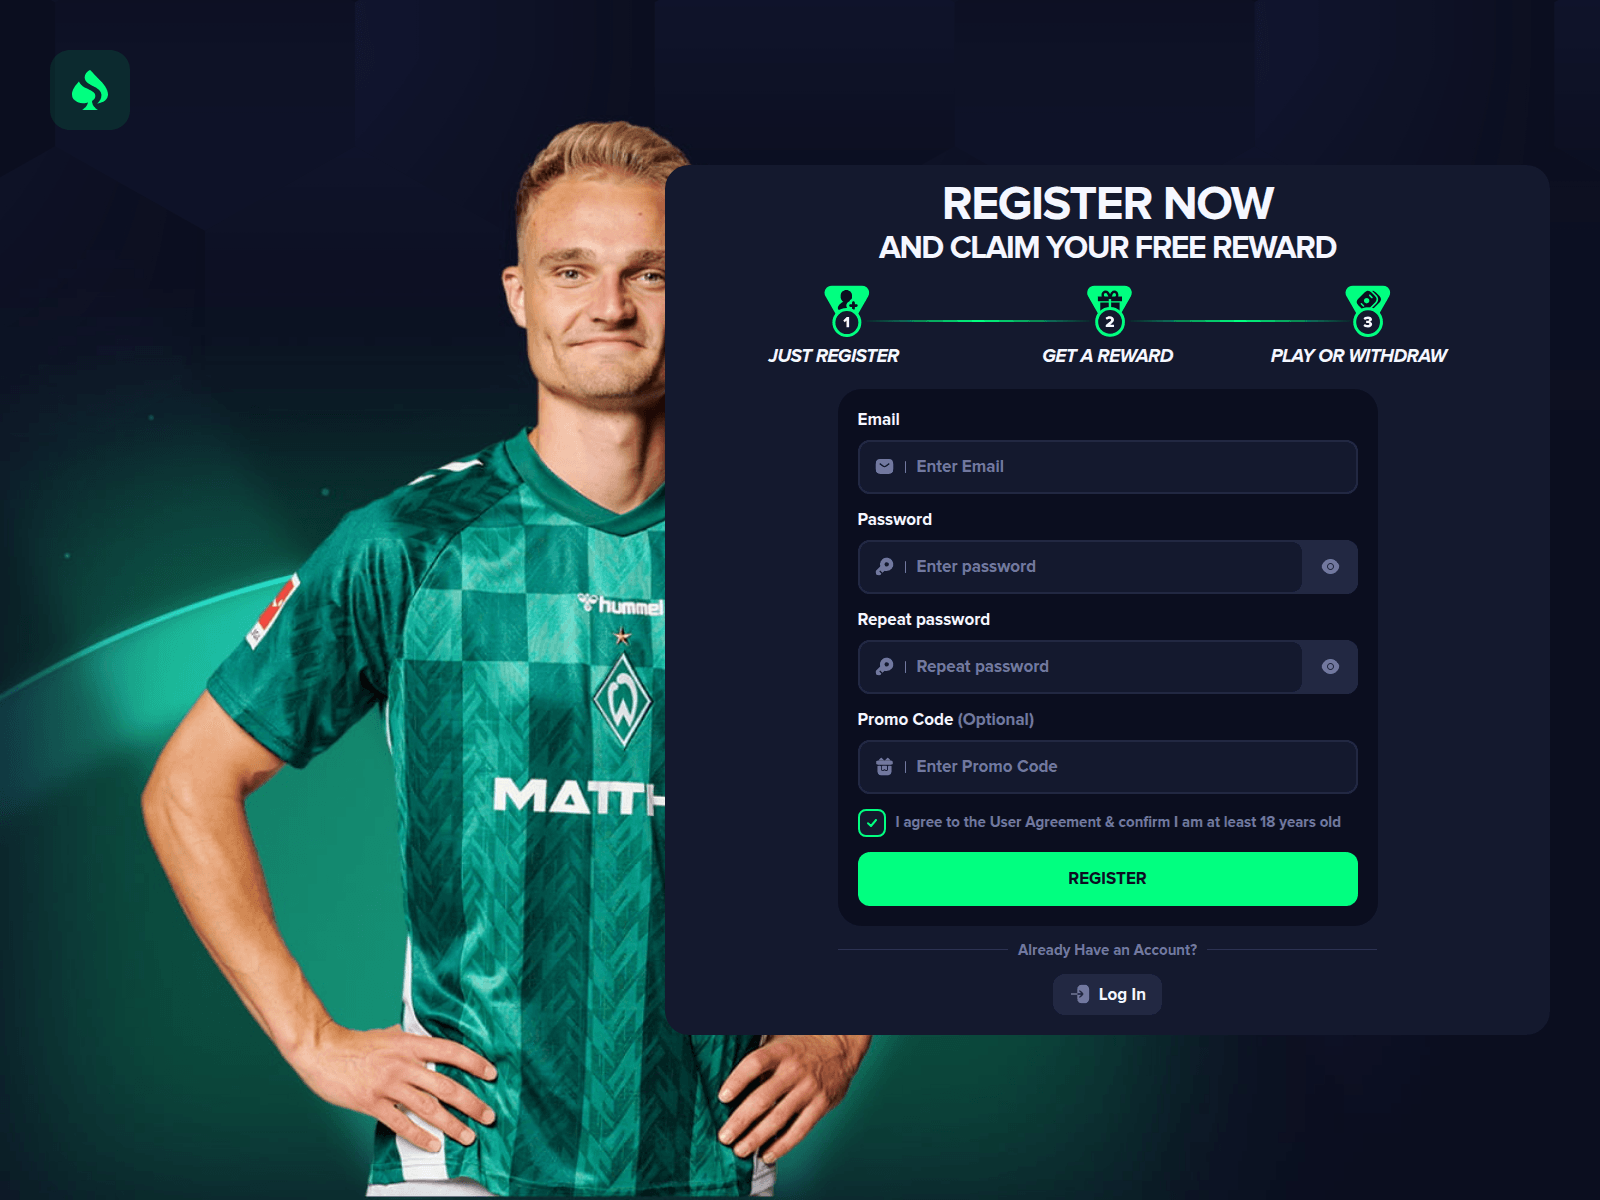
peaksmain.com

pexcas.com

pixgame.org

pizda.bet

playceleb.com
playglobal8.com

playroyalfortune.com

plays-arena.com

playzus.com

plinkodrop.top

ploznex.com
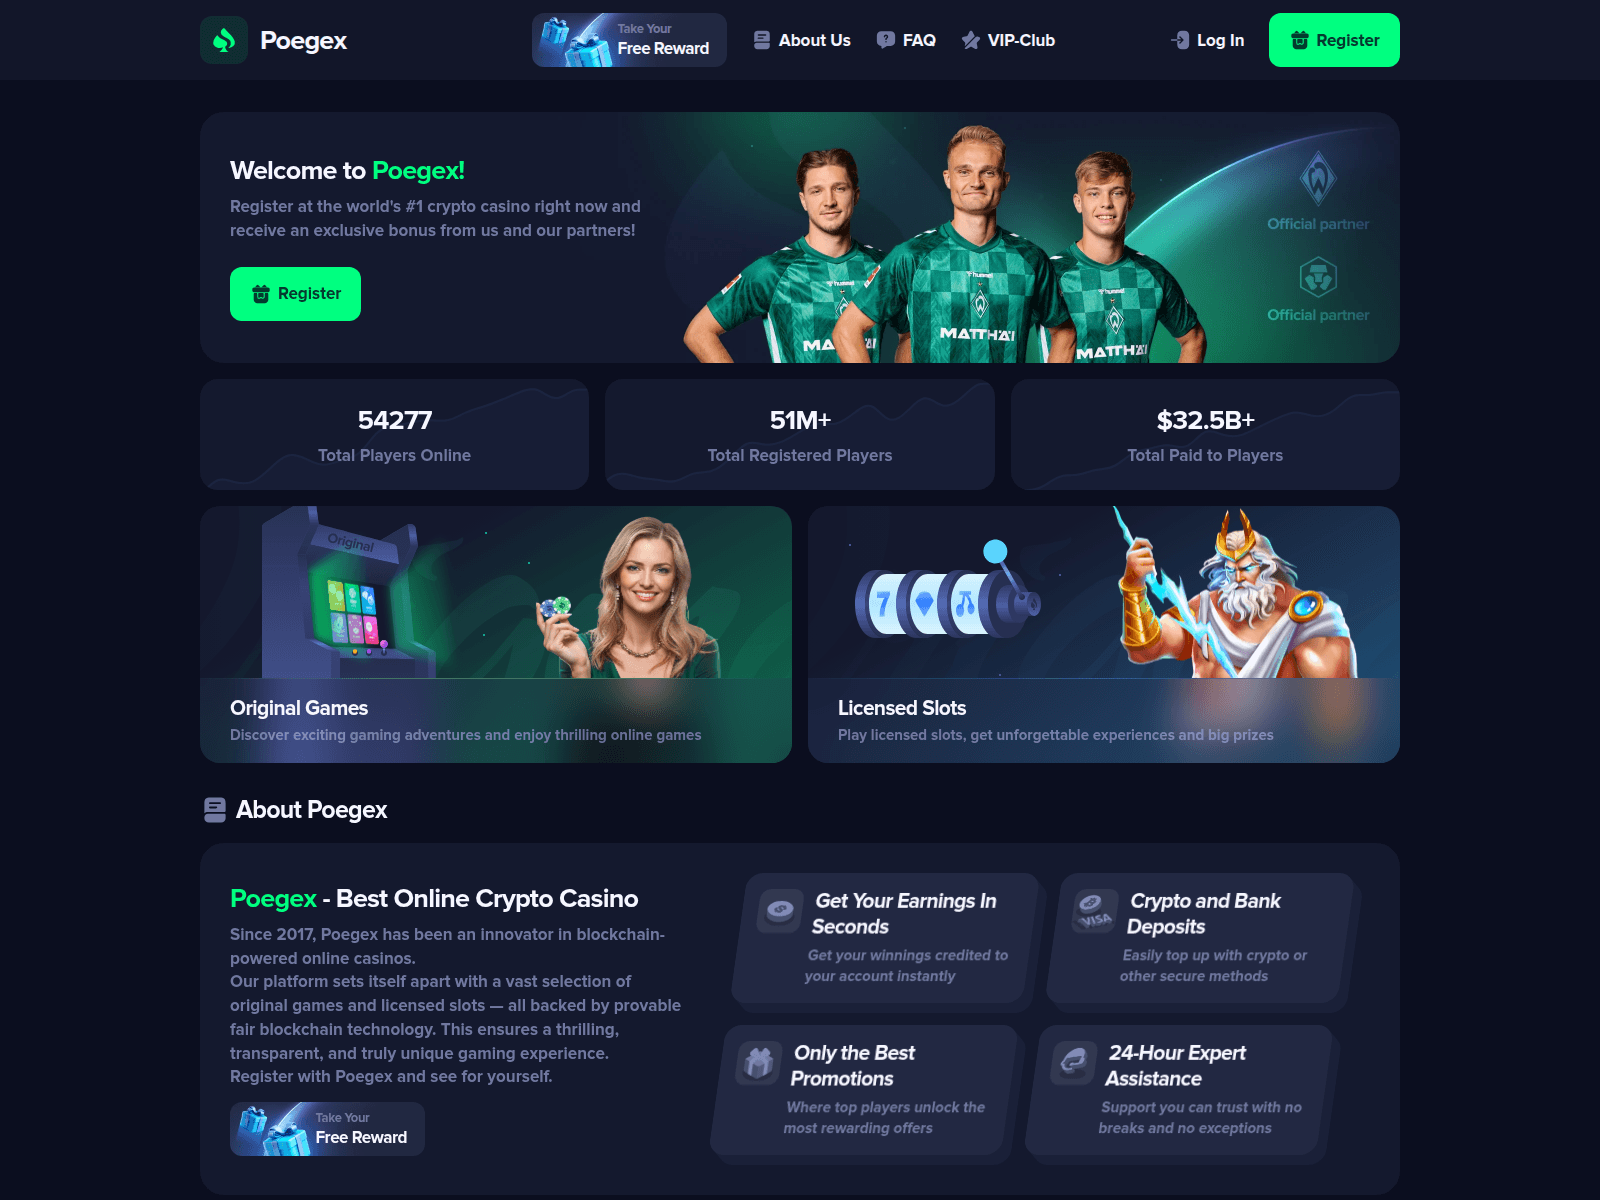
poegex.com
pokoplay.com

portesix.com

prismstake.top

proxycas.com
Threat Response Pipeline
How every domain in this hub is verified and how confirmed threats are neutralized. Full pipeline visualization →
Threat Intelligence Checks— every domain is scanned & cross-checked against:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ReportCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Security FiltersQuad9 · AdGuard · CleanBrowsingWeb-CheckFull surface scan
 crt.sh
Global Vendor Sync— confirmed detections are pushed to 29 partners:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecSiteReviewAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftTakedown APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ReportHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust