
Search tracked domains and review stored evidence, detections, and the latest observed availability.
221,218
Total Tracked
215,444
VT Detected
86,801
Last Seen Active
134,417
Unavailable at Last Check
0
VT Pending
How This Attack Works
Solana Drainer threats exploit vulnerabilities in Solana's crypto ecosystem to steal funds. Understanding their operation is crucial for prevention.
STEP 1
Target Identification
Attackers identify potential victims through phishing emails and fake websites.
STEP 2
Phishing Execution
Victims are lured to malicious sites mimicking legitimate platforms, like phantomairdrop.com.
STEP 3
Credential Harvesting
Once on the fake site, victims input sensitive information, believing it to be secure.
STEP 4
Fund Drainage
Attackers utilize harvested credentials to access wallets and drain funds via illicit transactions.
Technical Analysis
Solana Drainer attacks leverage phishing techniques to exploit the Solana blockchain. Attackers often create copycat websites using top TLDs such as .com, .xyz, and .cc, with domains hosted by registrars like Cloudflare, Inc. and PDR Ltd. These sites employ deceptive JavaScript and HTML code to mimic legitimate interfaces, tricking users into entering their private keys or seed phrases. Once credentials are obtained, attackers interact with the Solana blockchain via RPC calls to execute unauthorized transactions. The usage of smart contract functions like `transfer` and `approve` allows attackers to swiftly move funds out of victims' accounts. The infrastructure often involves a network of proxy servers to obfuscate the origin of the attack and make tracing back to the perpetrators difficult.
Real Cases
Phantom Wallet Breach (2023)
$2 million stolen
Attackers created a fraudulent Phantom wallet site to harvest user credentials, resulting in a $2 million theft.
SolUnion Scam (2024)
$1.5 million stolen
Using the domain phantom.solunion.cc, scammers executed a sophisticated phishing attack, stealing $1.5 million in SOL.
VaultBenefits Exploit (2024)
$3 million stolen
A fake airdrop campaign via vaultbenefits.net led to credential compromise and a subsequent $3 million drain.
How to Detect
Unsolicited emails or messages offering free SOL or airdrops
Websites with slight misspellings of legitimate names
Requests for private keys or seed phrases
Suspicious URL structures or unfamiliar TLDs like .xyz or .cc
Lack of HTTPS security on sites claiming to be secure
How to Protect Yourself
1
Verify URLs carefully before interacting
2
Enable multi-factor authentication on your wallet
3
Never share your private key or seed phrase
4
Regularly check transaction histories for unauthorized activity
5
Use official wallet apps and browser extensions
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 2,752 domains tracked for this threat type
Solana Drainer 2,752 domains
iraninusolana.fun

jaecoinmigration.world


jitoget.com

jitohub.com

jitonow.com

jjup.ng

jo.sol-flow.com
join-kabuto.xyz

jtosol.com
jumper-solana.vercel.app
jup-wet-drop.top

jupiter-solanaa.pages.dev

jupuary.fun

komino.finance

layerbtcai.xyz
lobstar.votecoin-pump.fun
lolcoinbnb.live
mail.bestsolanavolumebot.com

marinade.investments

marketplace.dexscreener.exchange

marlnade-finacne.cfd

masterbot.reallocation.finance
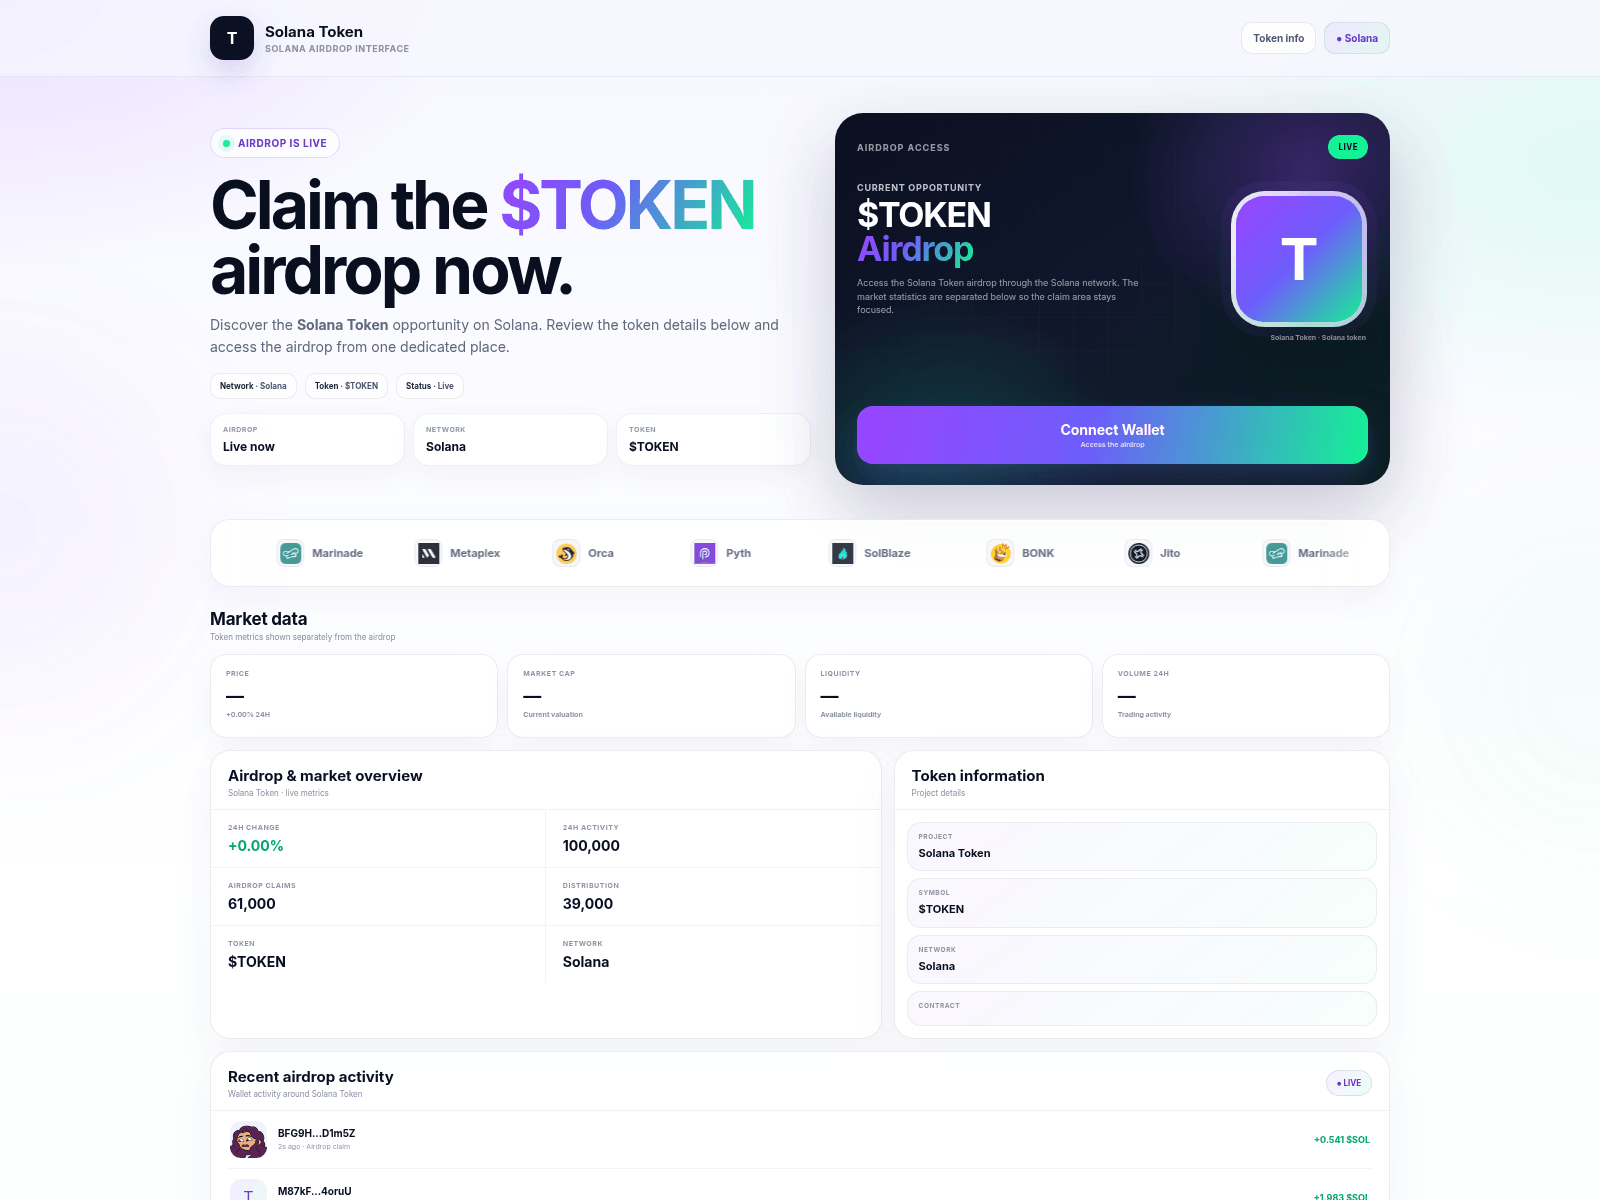
memecoins-onsolana.netlify.app

memescoin.run
memesolana.pages.dev
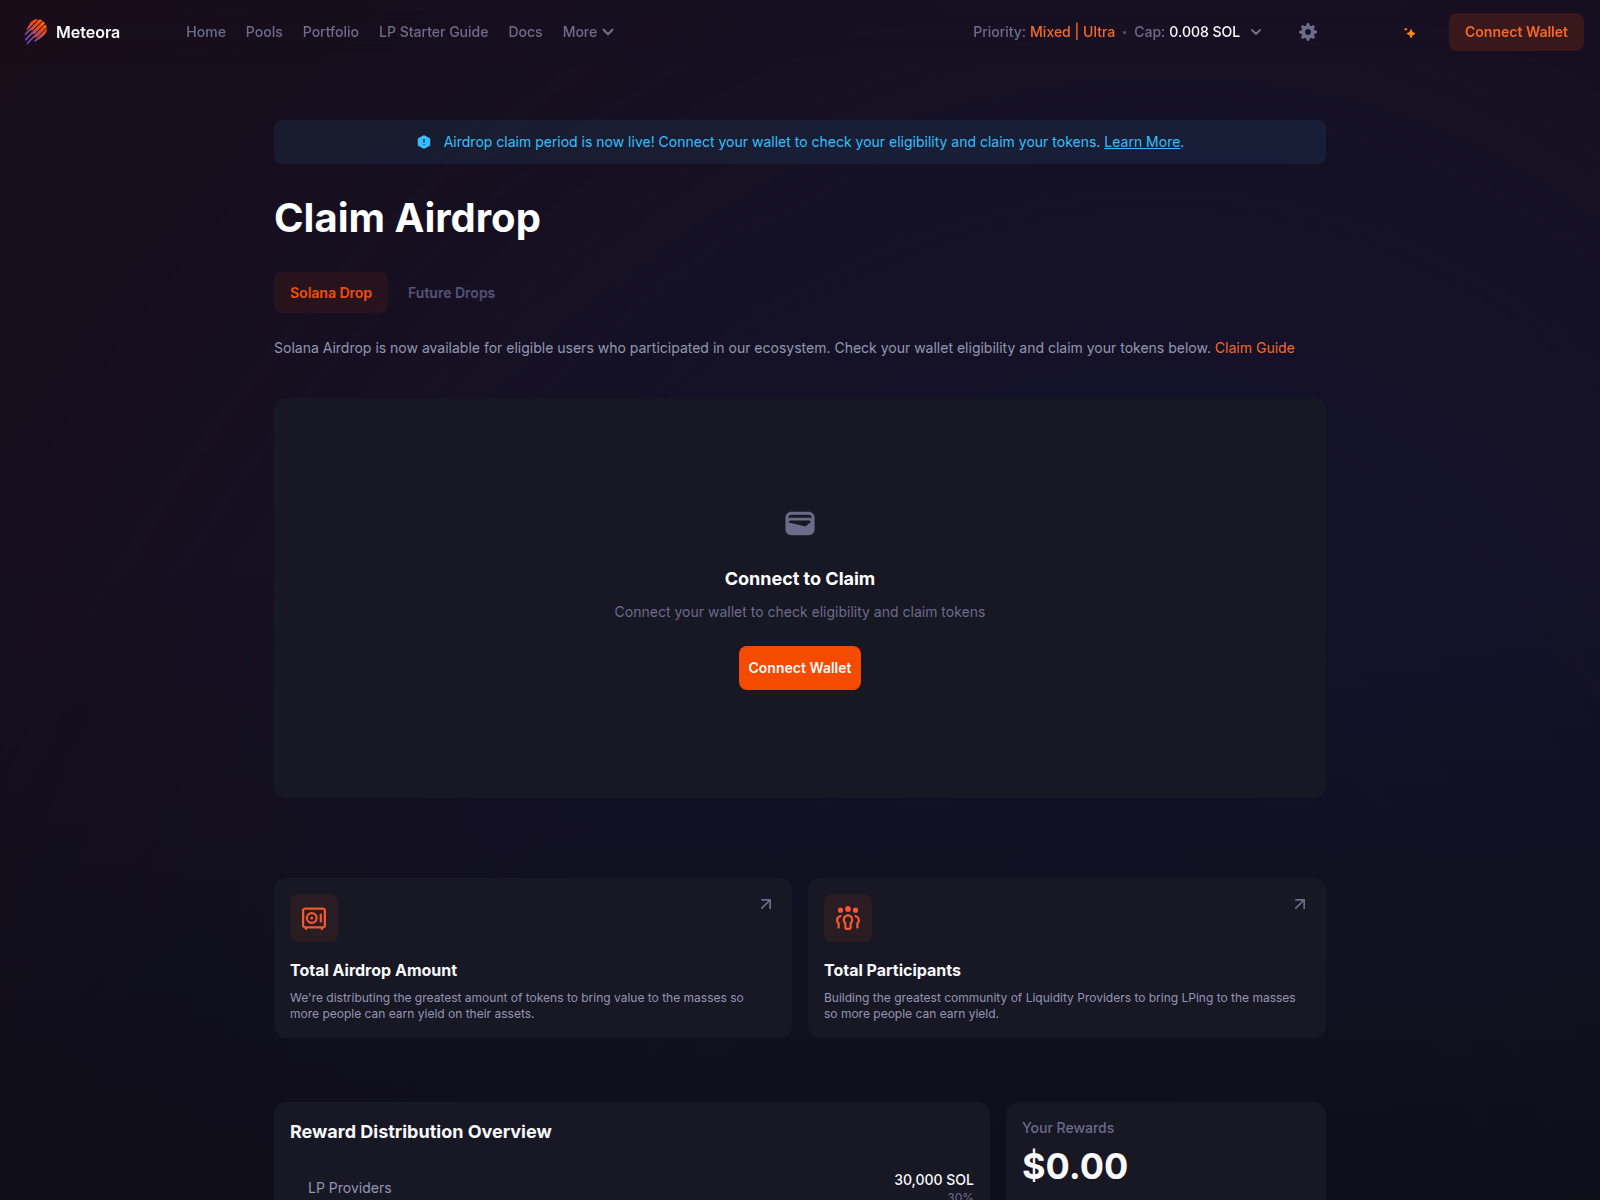
meteoraag.org
mevcrm.com

minio.live

mintmemesol.org

moomshot.org

moonshot.cyou

mountain.xsolana.cc

nanaonsolana.xyz

nickelcoin.fun
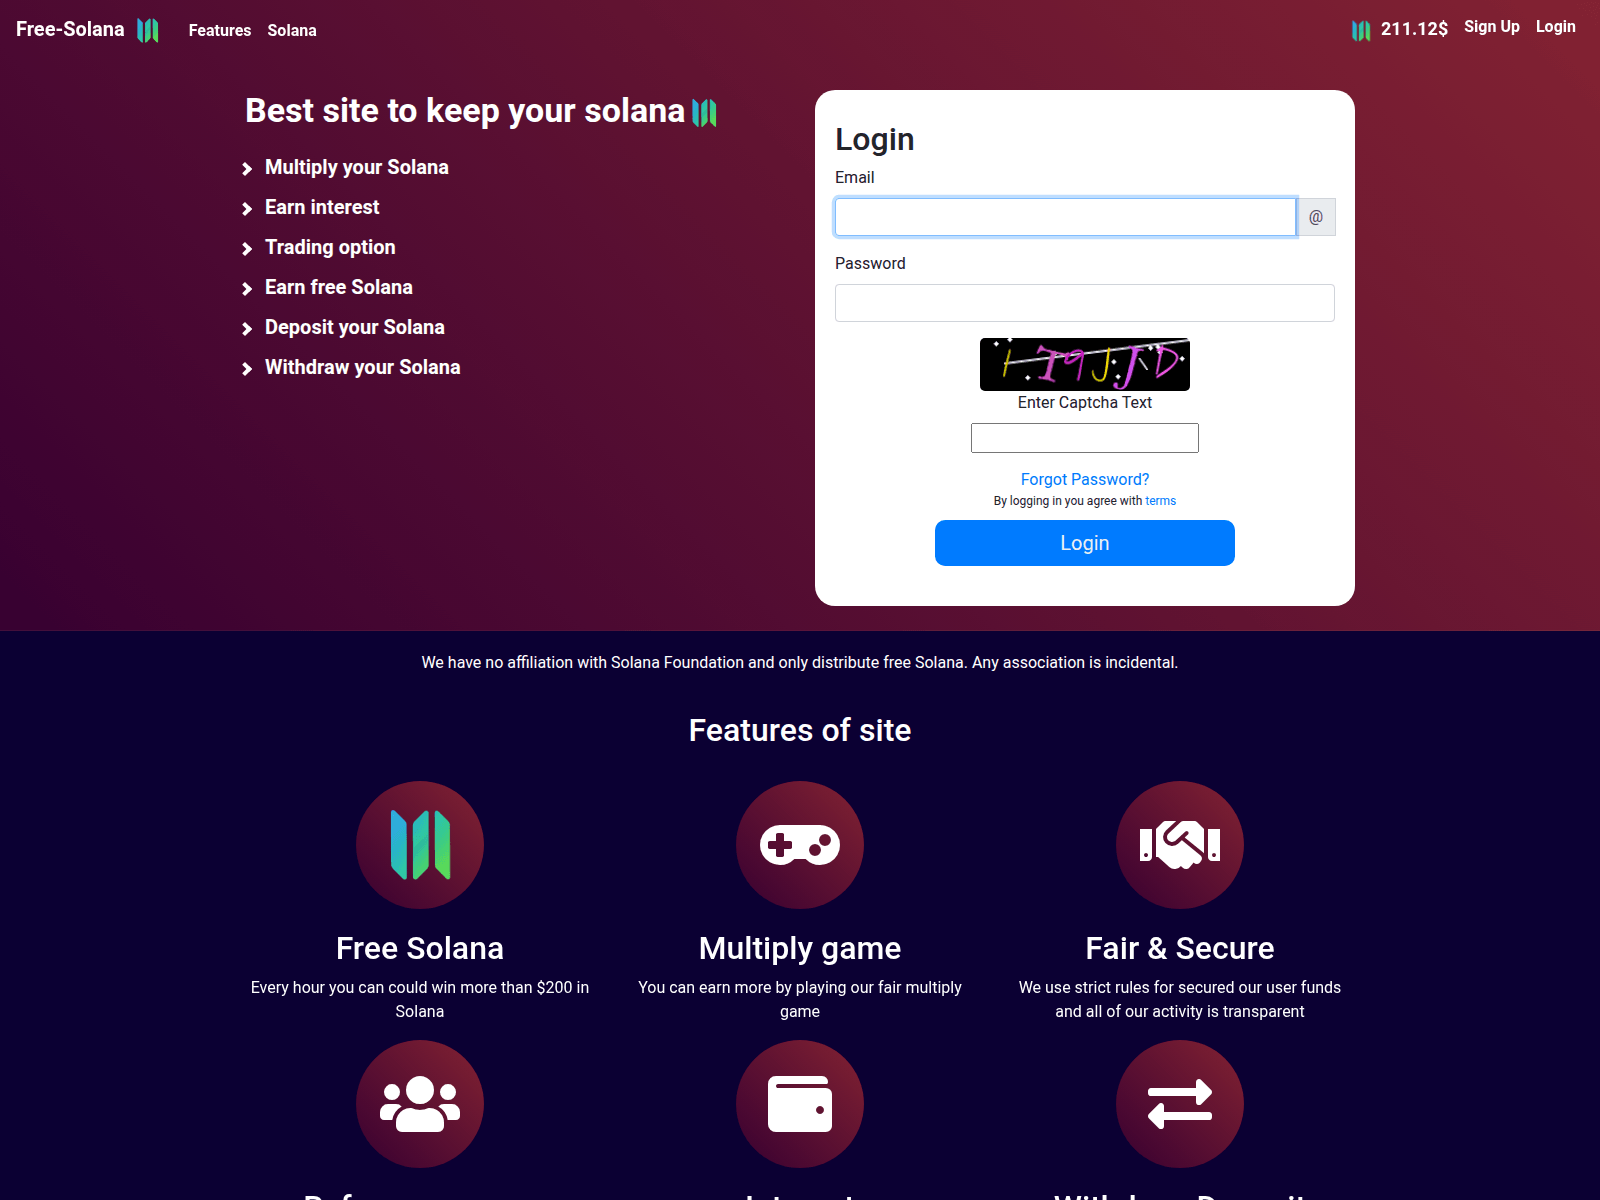
ns2.free-solana.com

onwinlogin.com
orangeerasolana.net

orcacoin.run

pay.in-cryptomus.com

payout-phantom.com
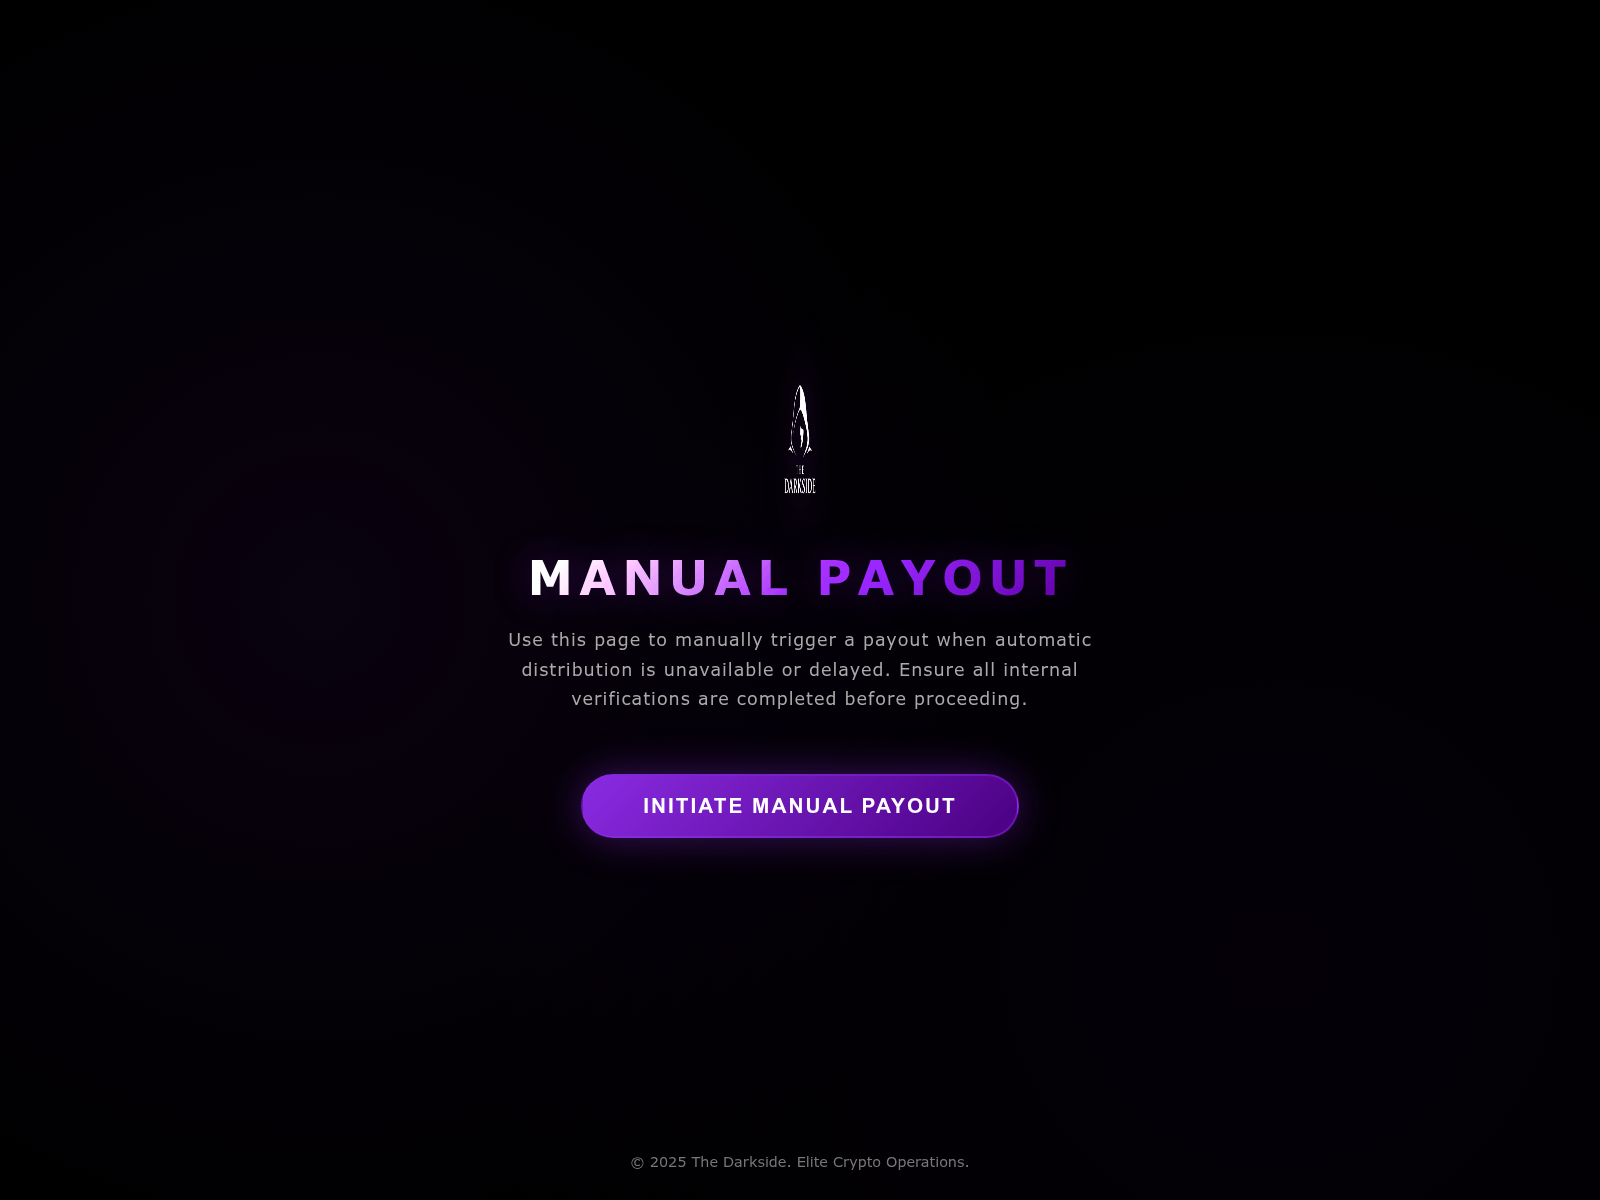
payoutdarkside.pro
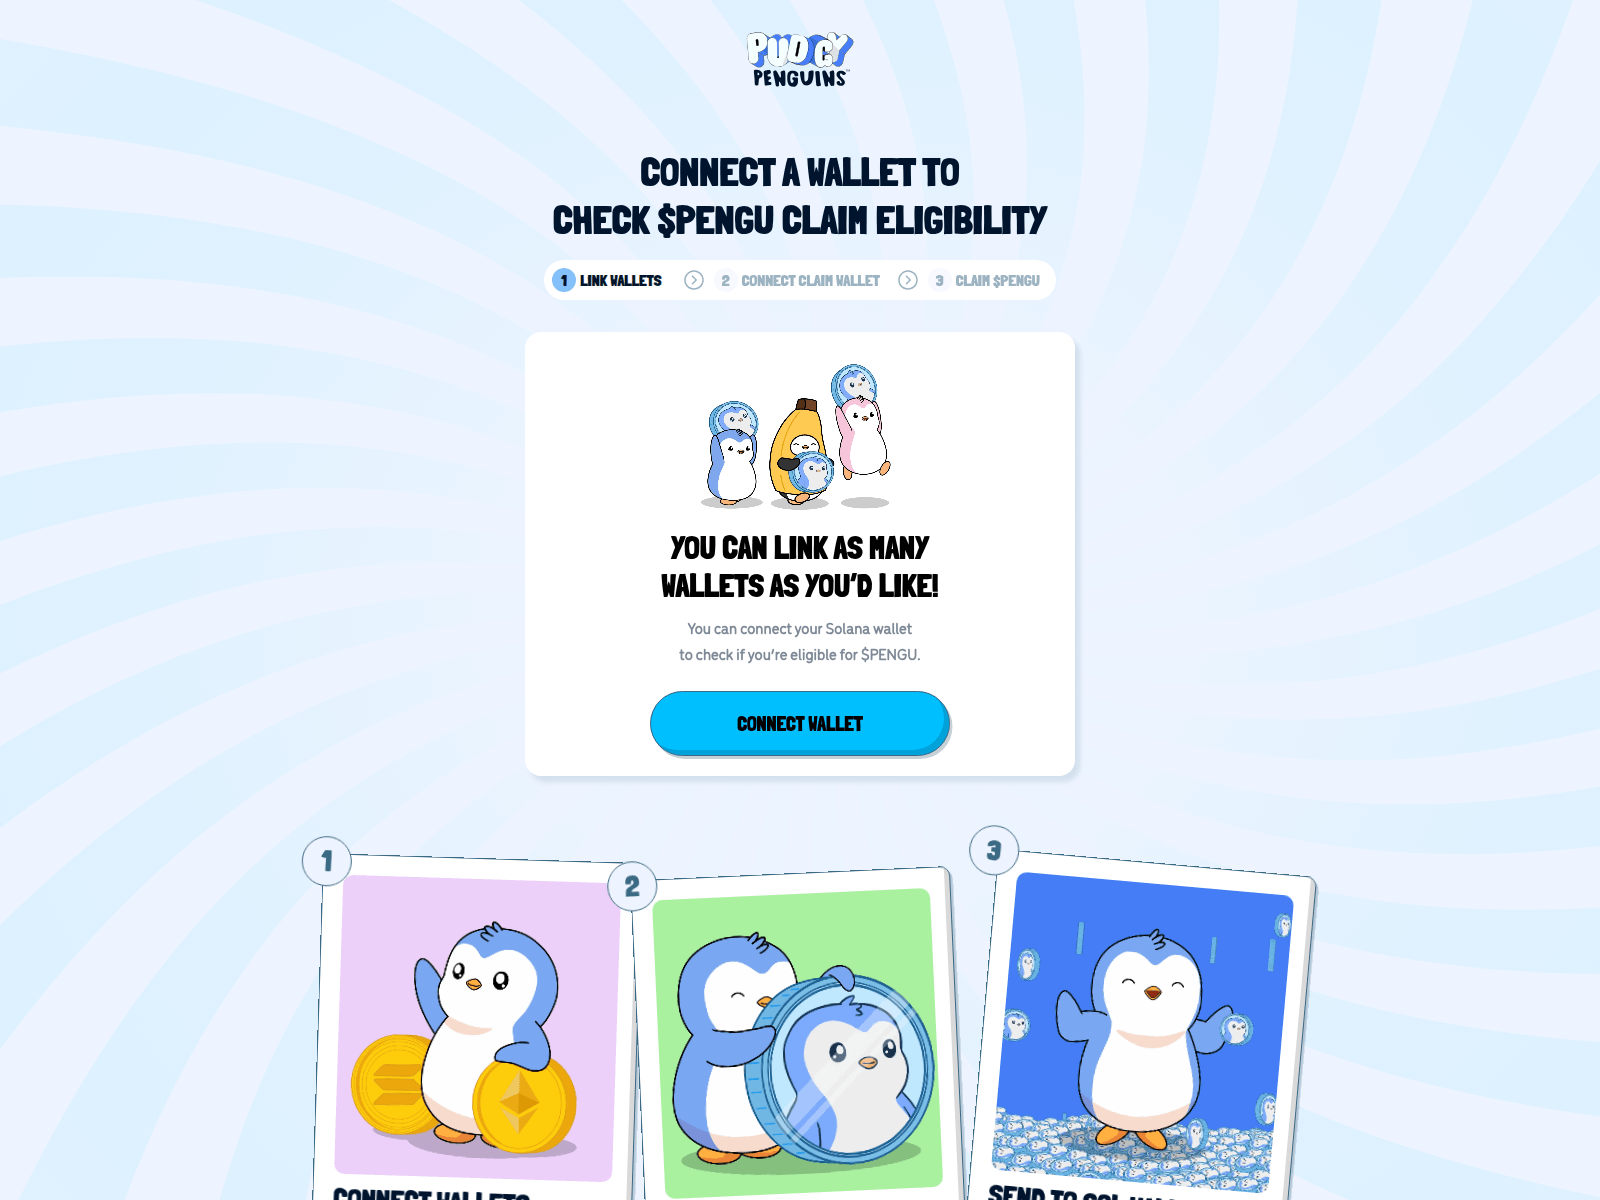
pengu.onsol.pro
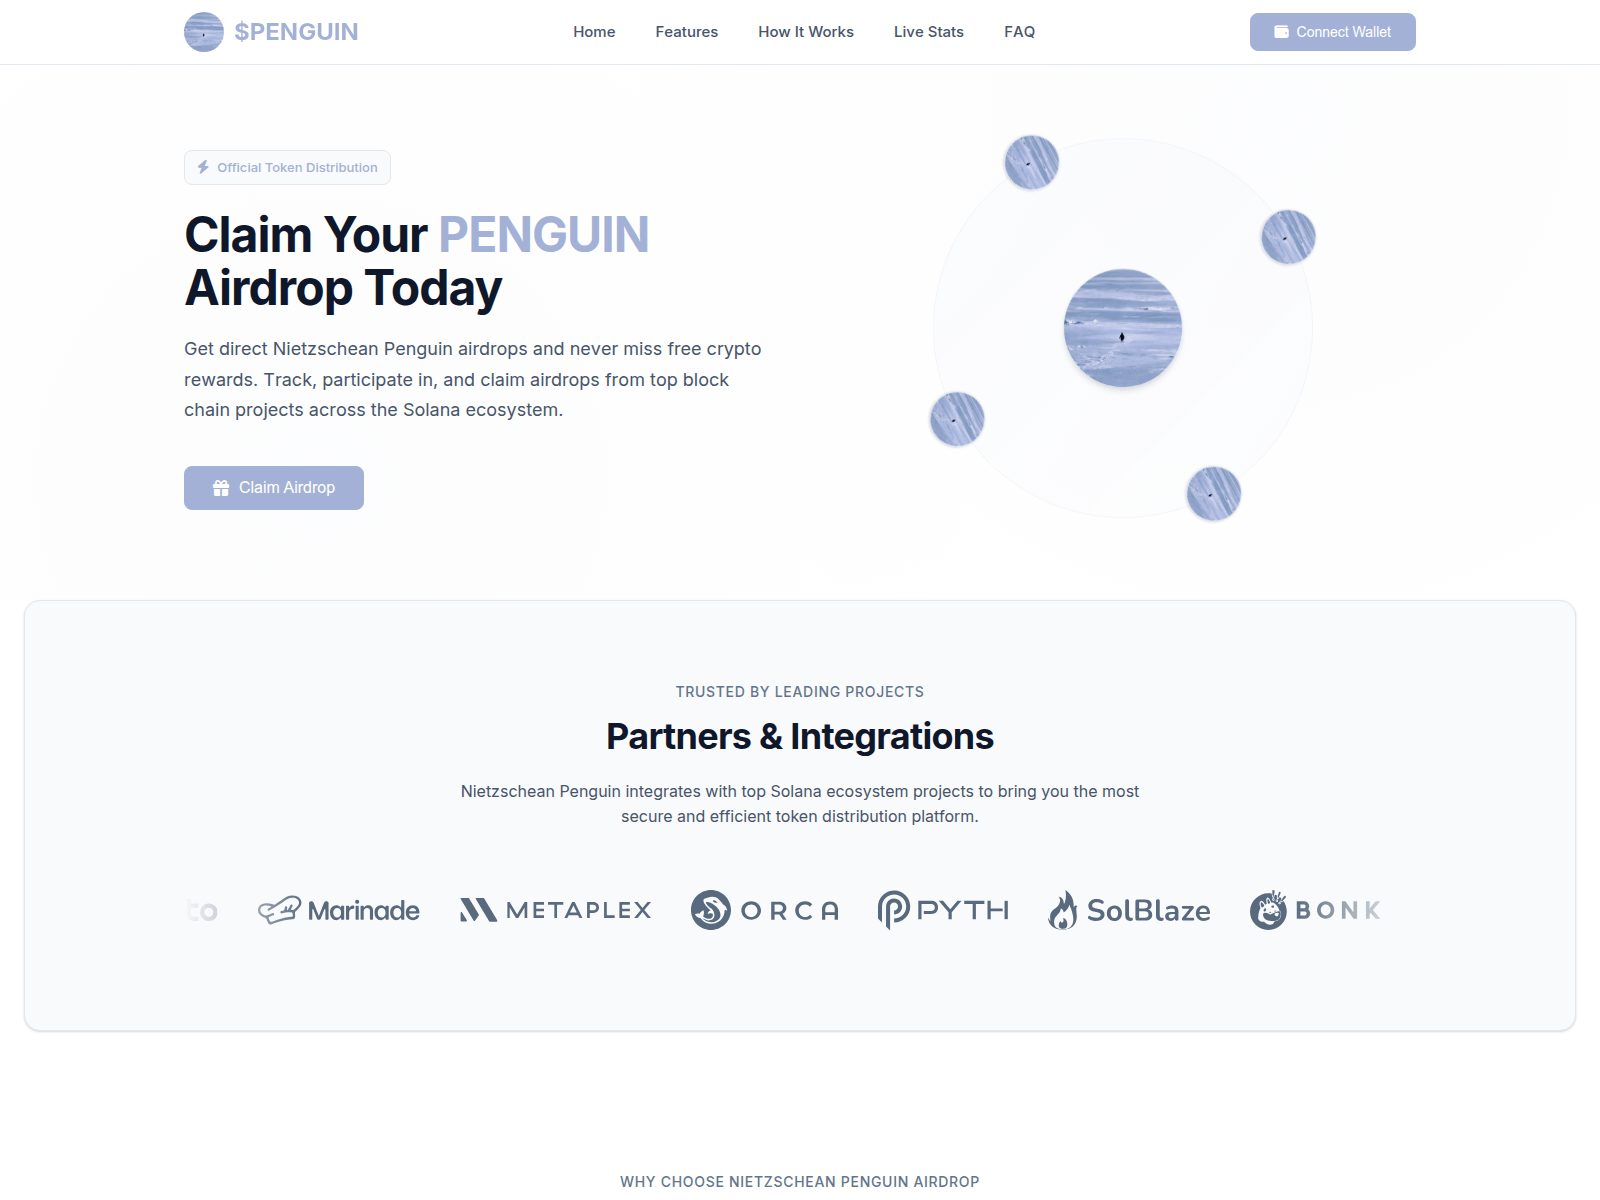
penguin.solgrid.trade

penguinofficial.top
penguinofsolana.com

pengusol-drop.fun
phantom-app-2mt.pages.dev

phantom-coin.xyz
phantom-eng-ui.pages.dev

phantom-project.top
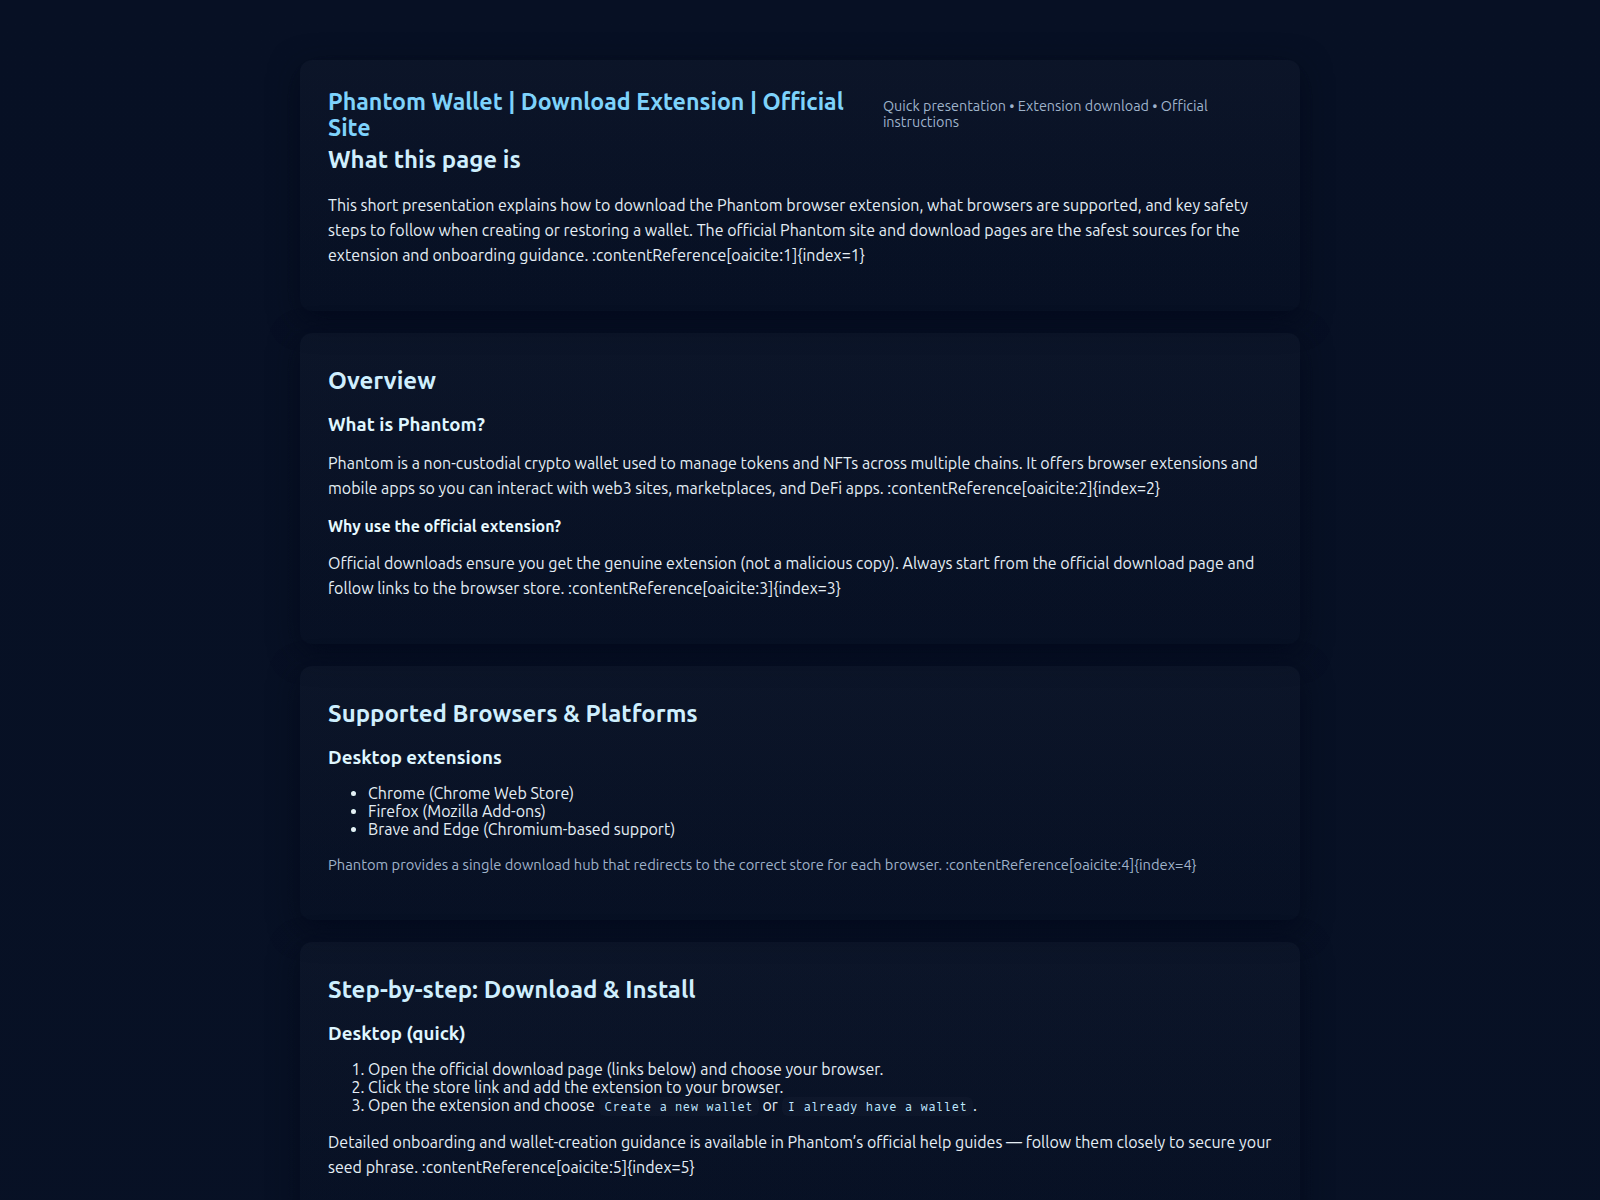
phantom-solana-wallet-te.pages.dev
phantom-ur.pages.dev
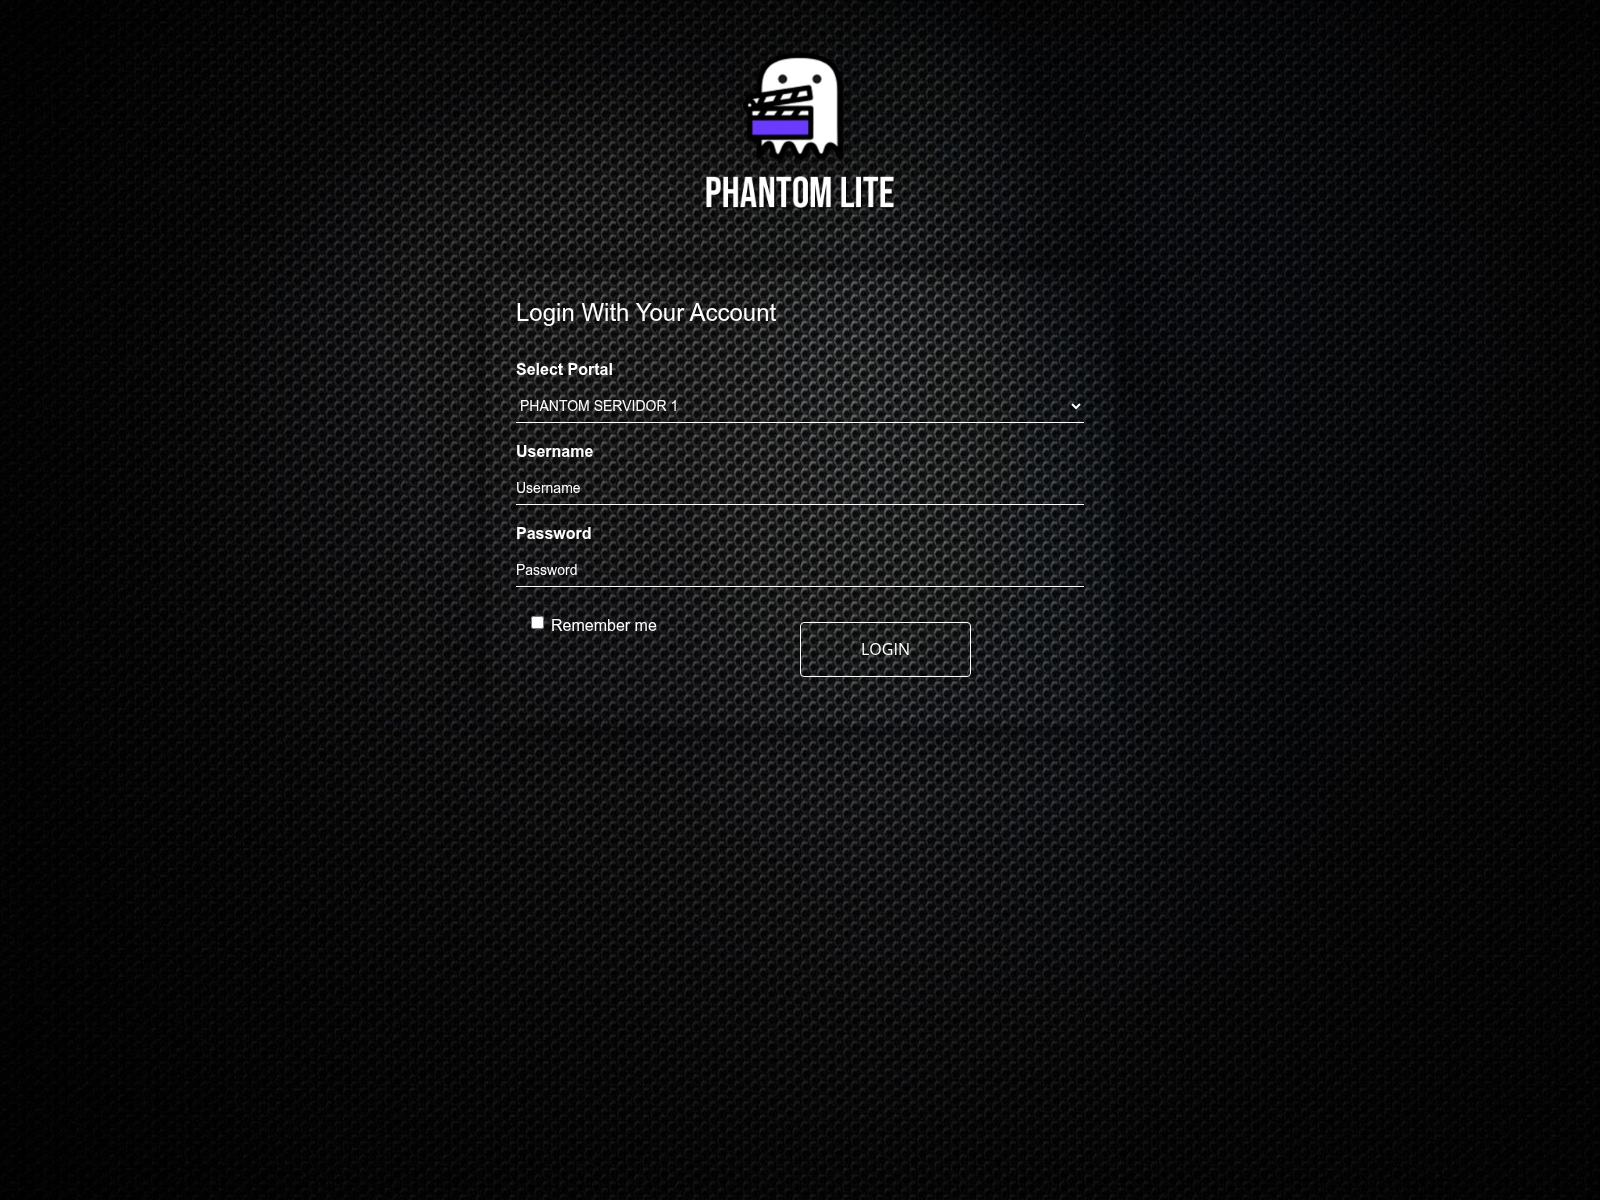
phantom.cbbrst.top
phantom.printopost.com
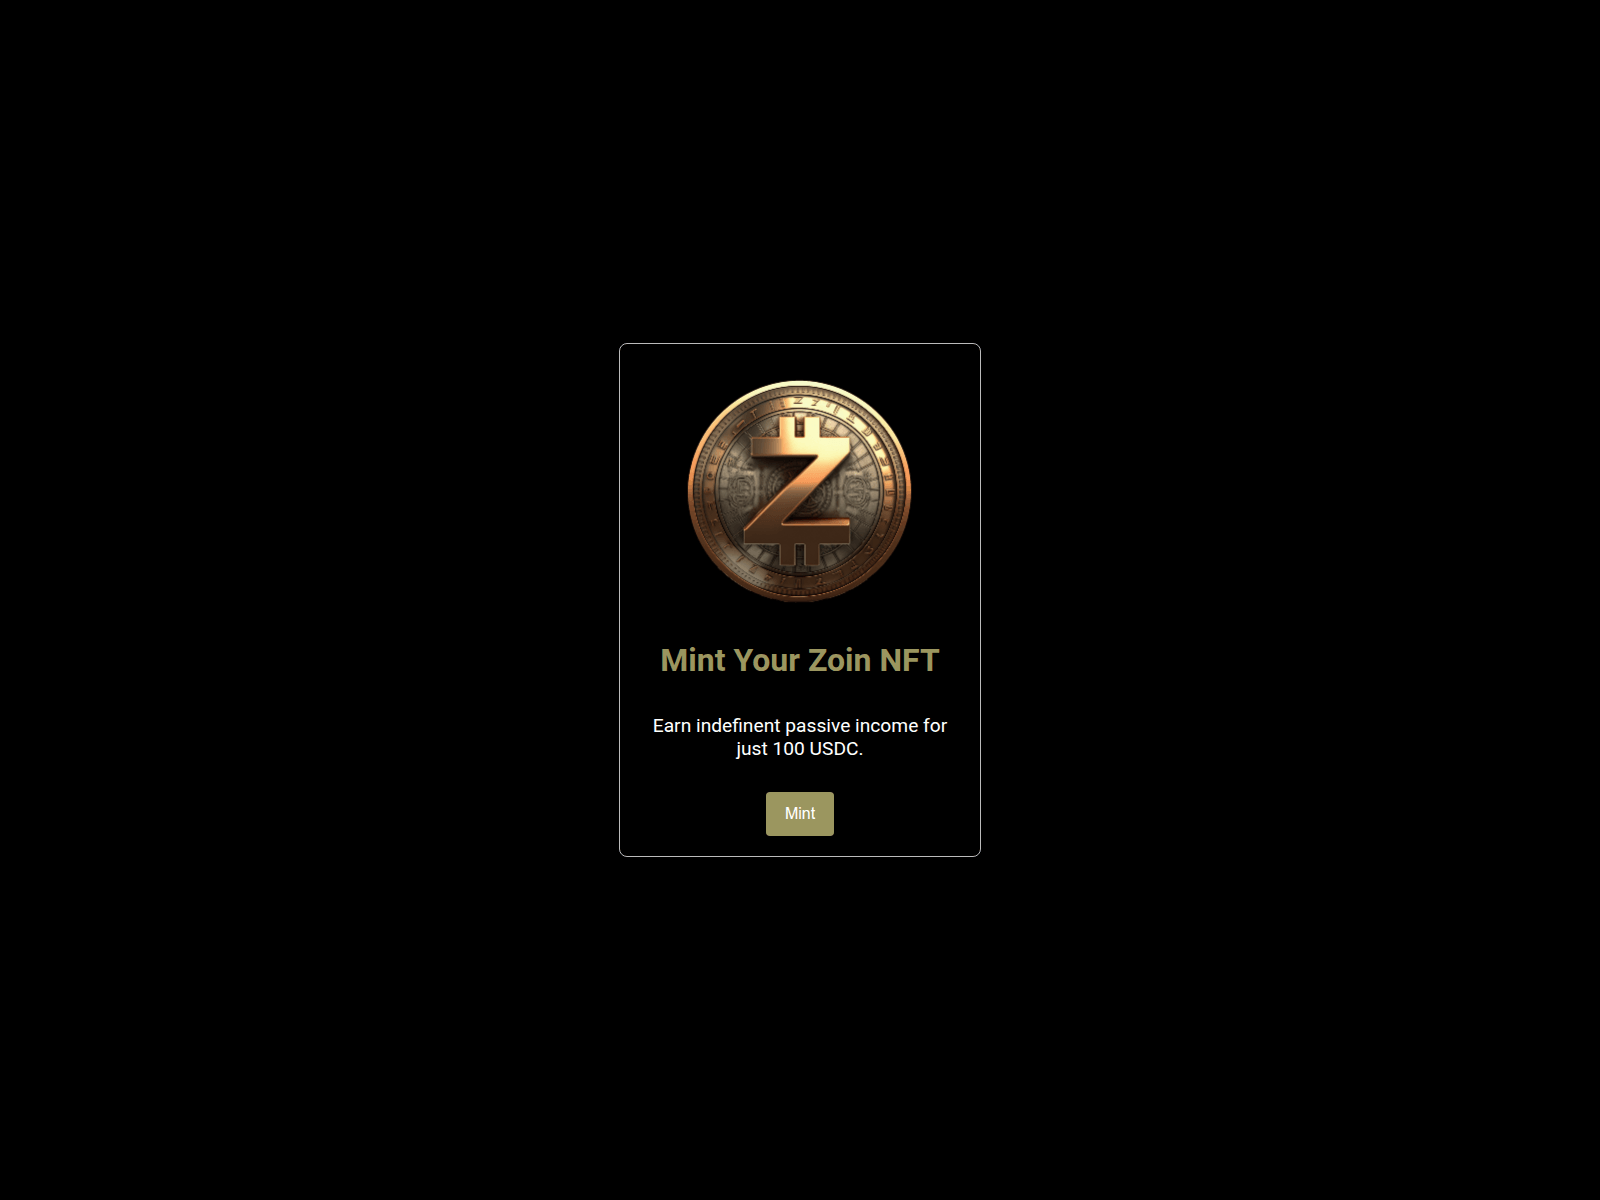
phantomapp.pages.dev
phantomarcade43.top
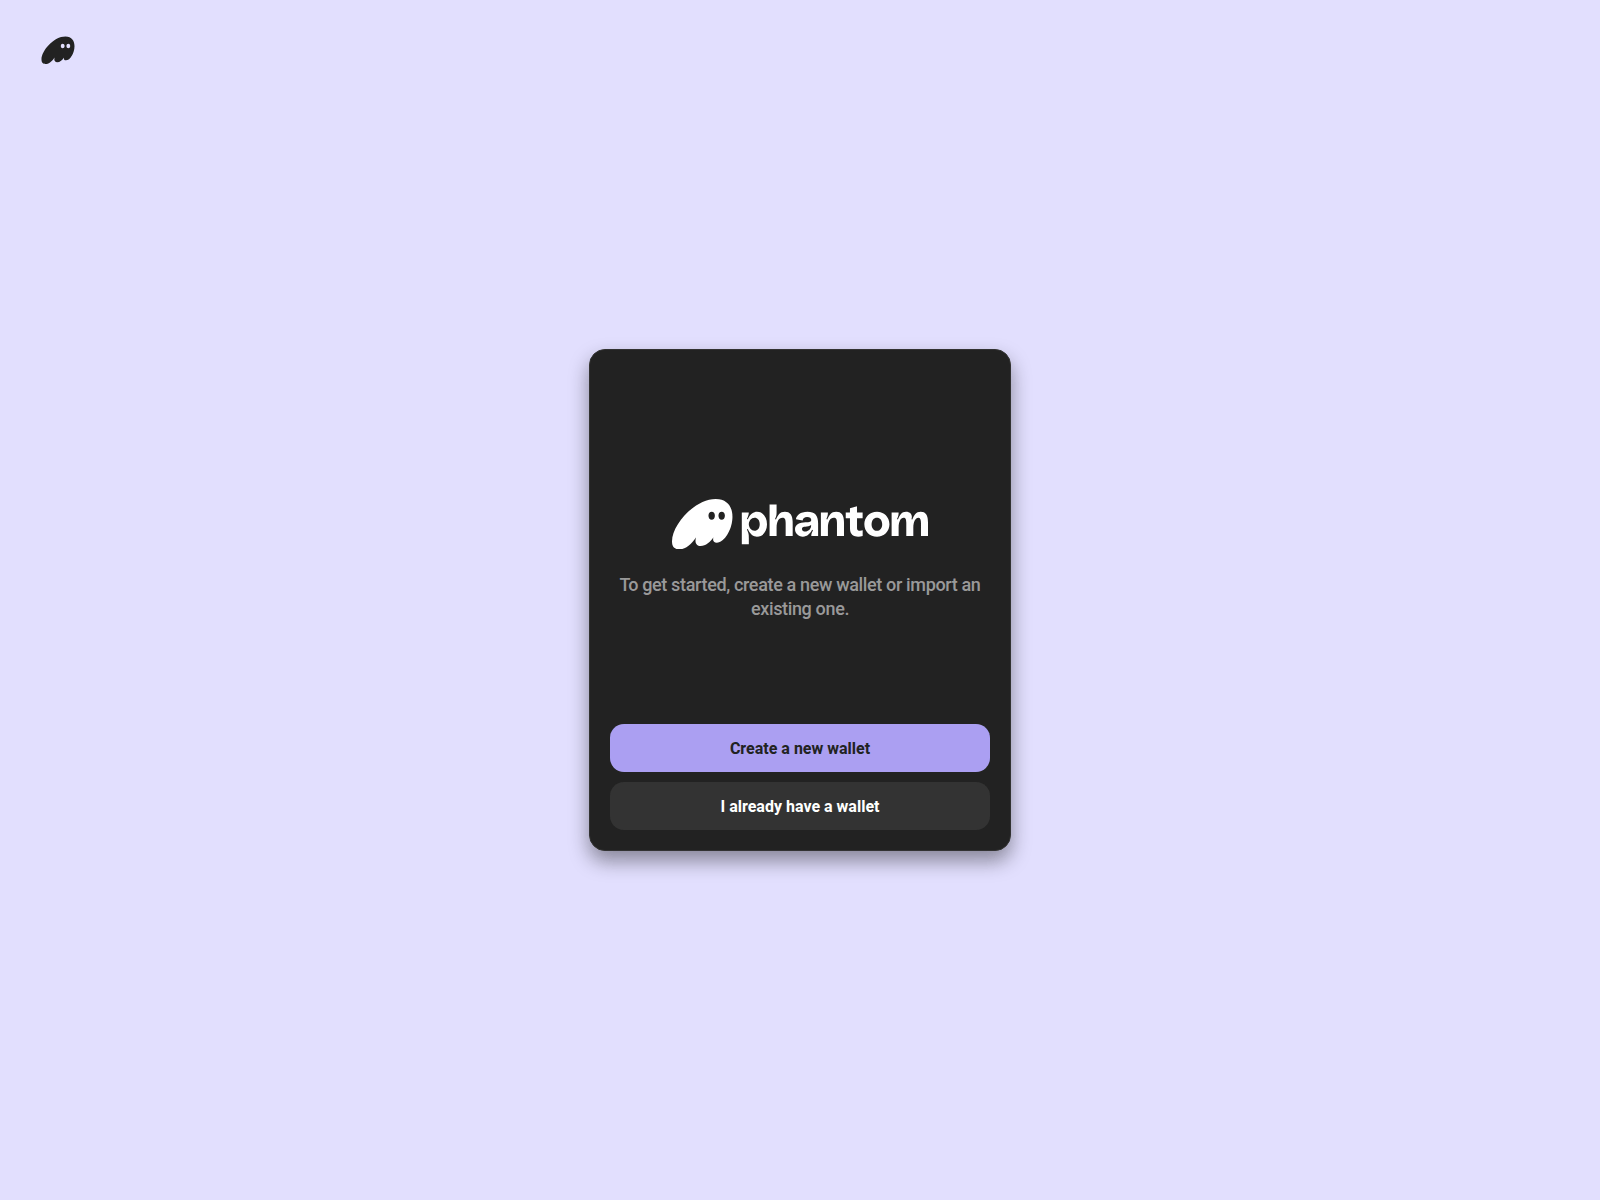
phantombfnaelmomeimhlpmgjnjophhpkkoljpa-google-extensions.pages.dev
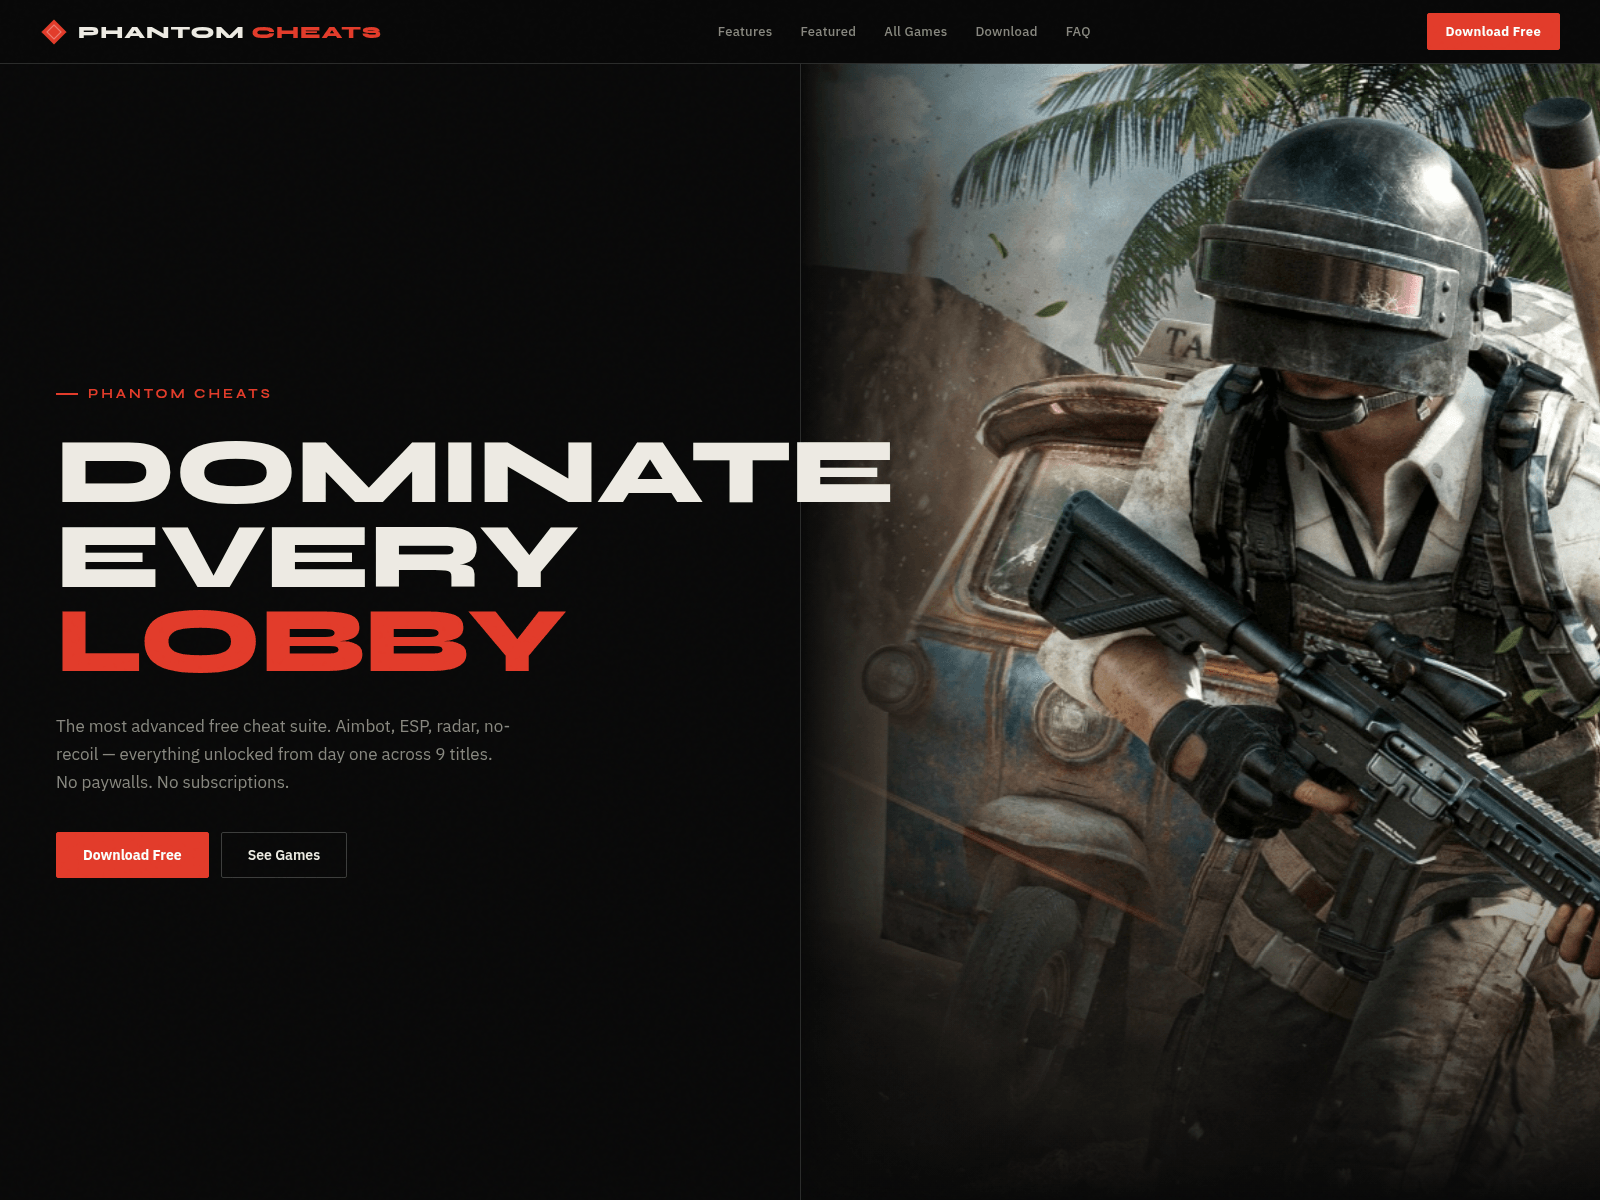
phantomcheats.fun
phantomdrop-app1.pages.dev

phantomlattice.info
phantomminer.cfd
phantommusic.elabbassi.com
phantomvisualstt.com
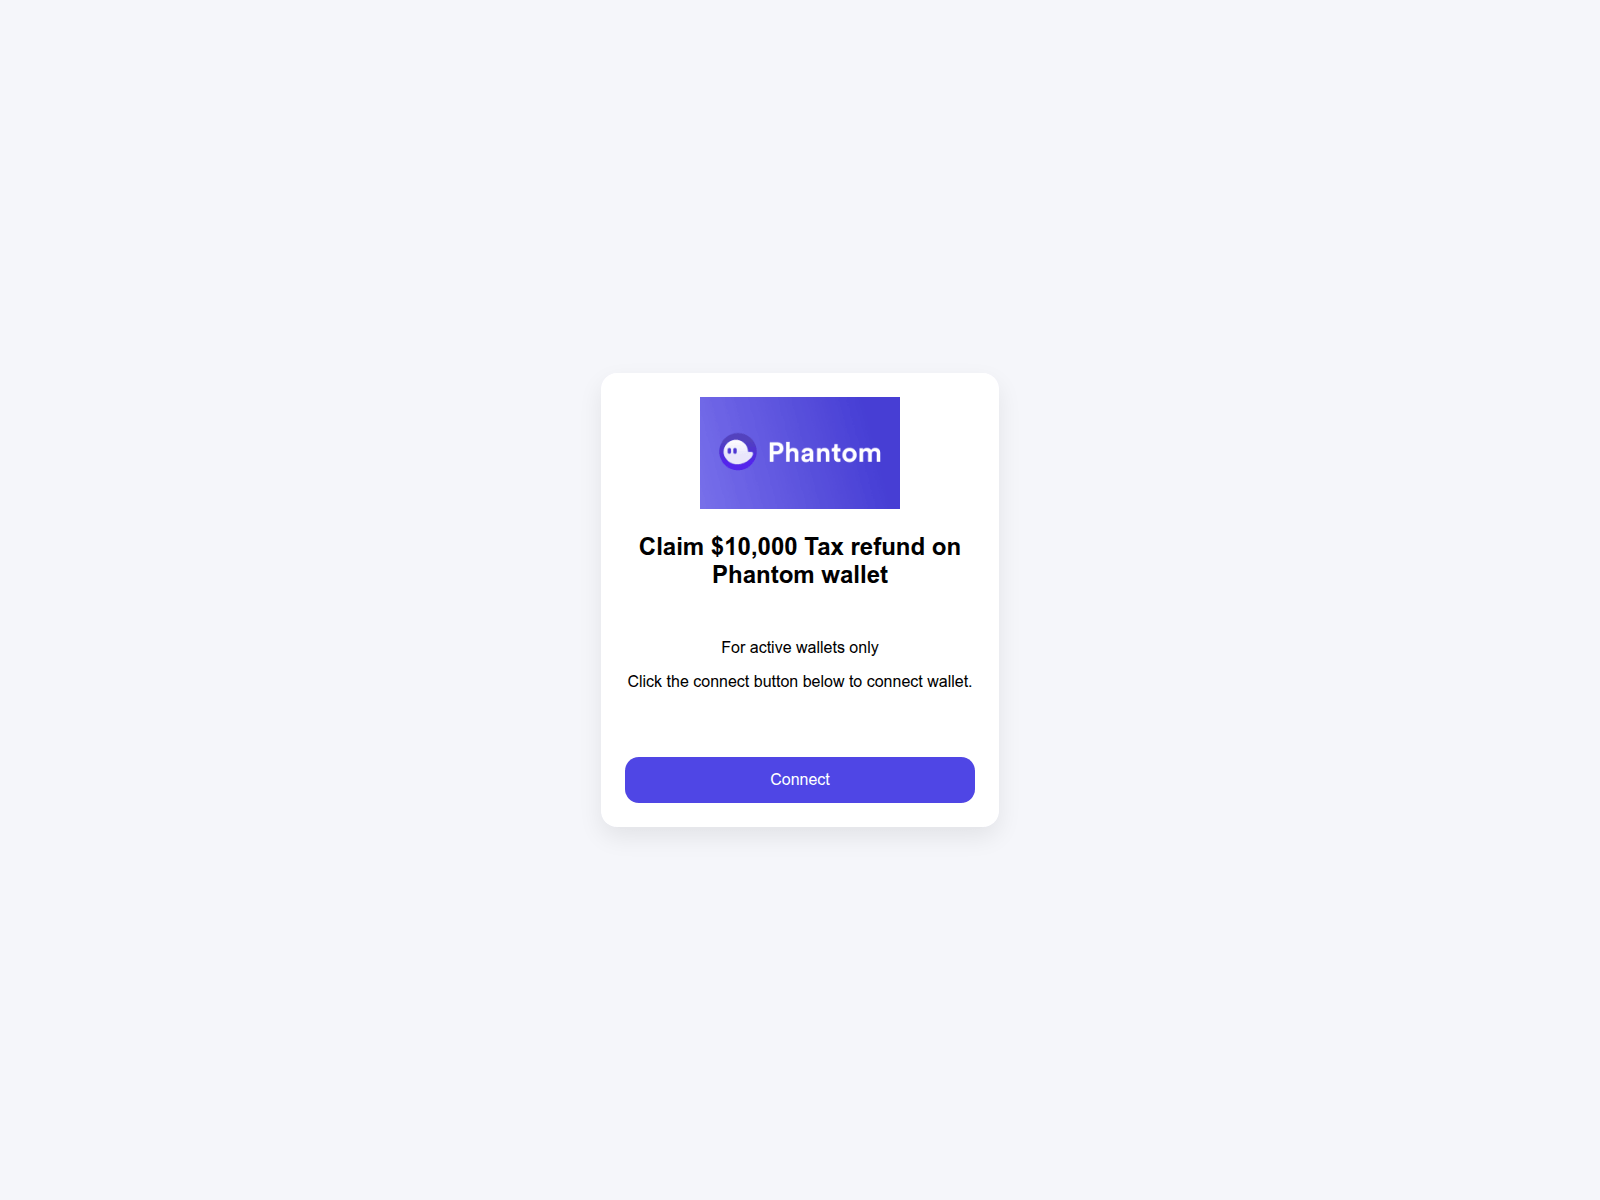
phantomwallet.listing-check.com
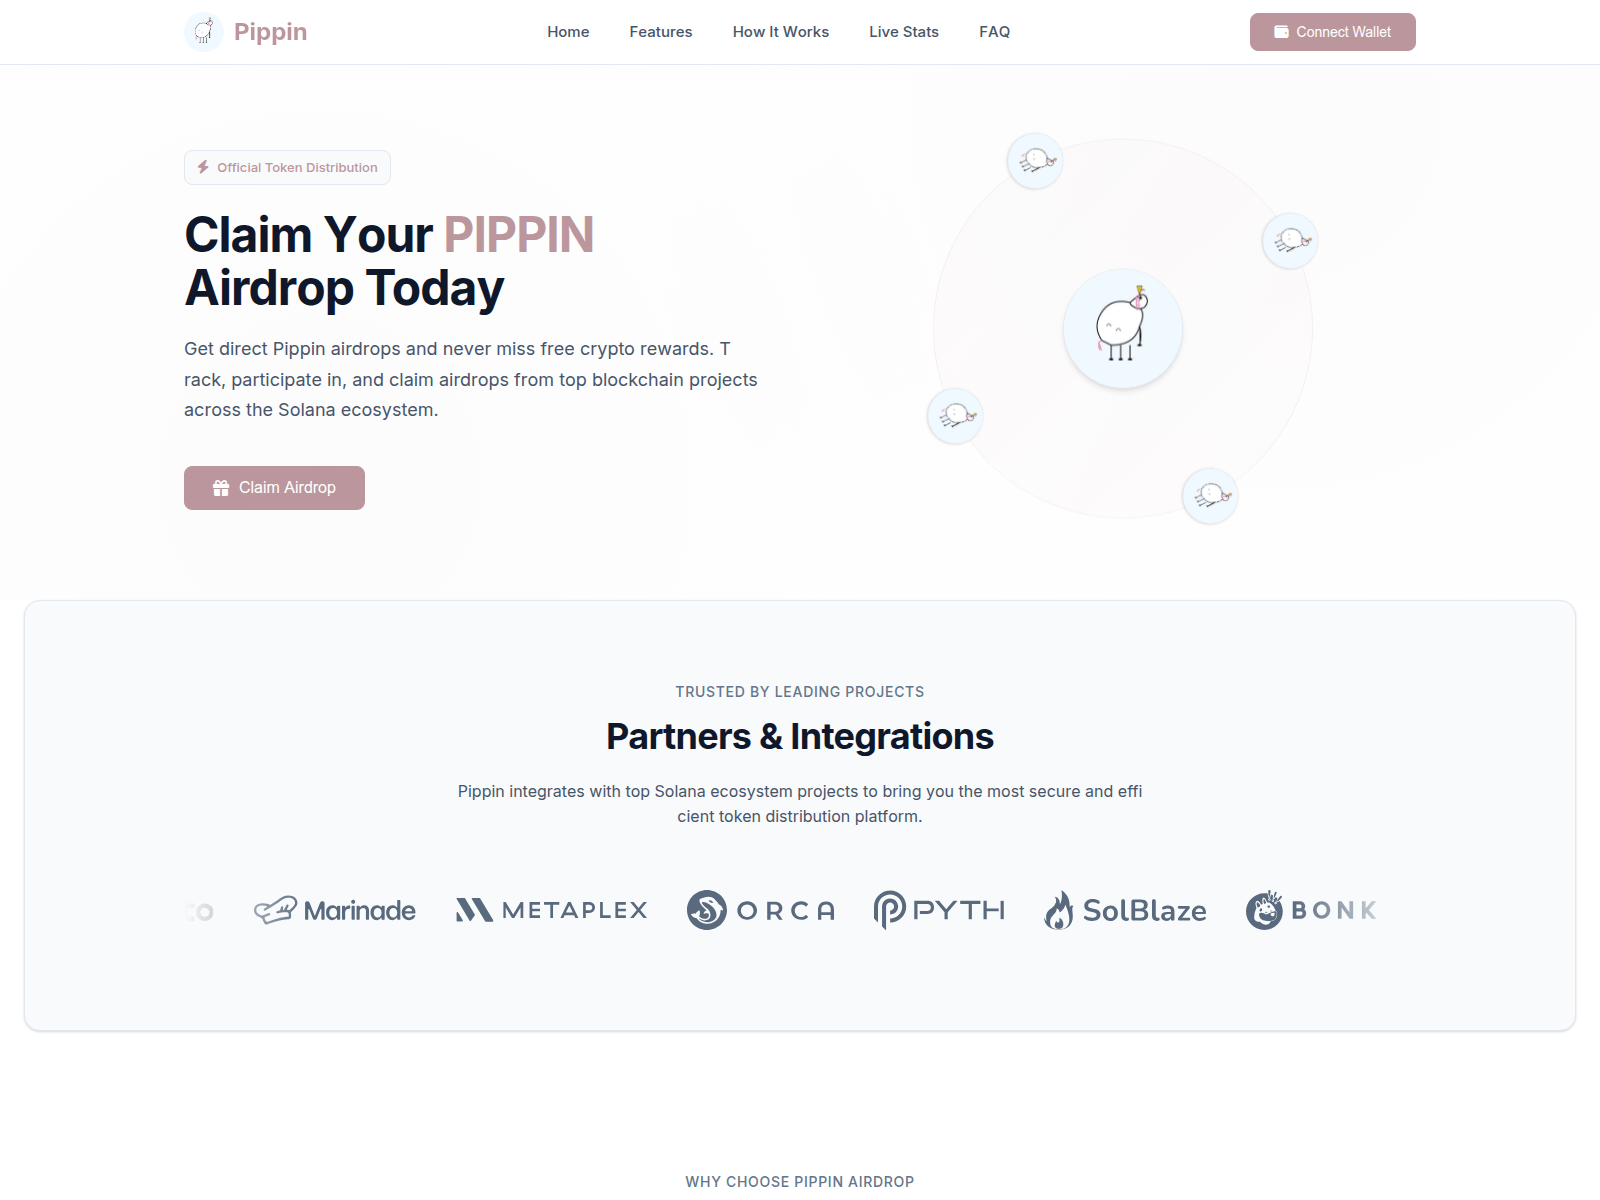
pippincoinsol.com

pippinlove.top

play-to.click
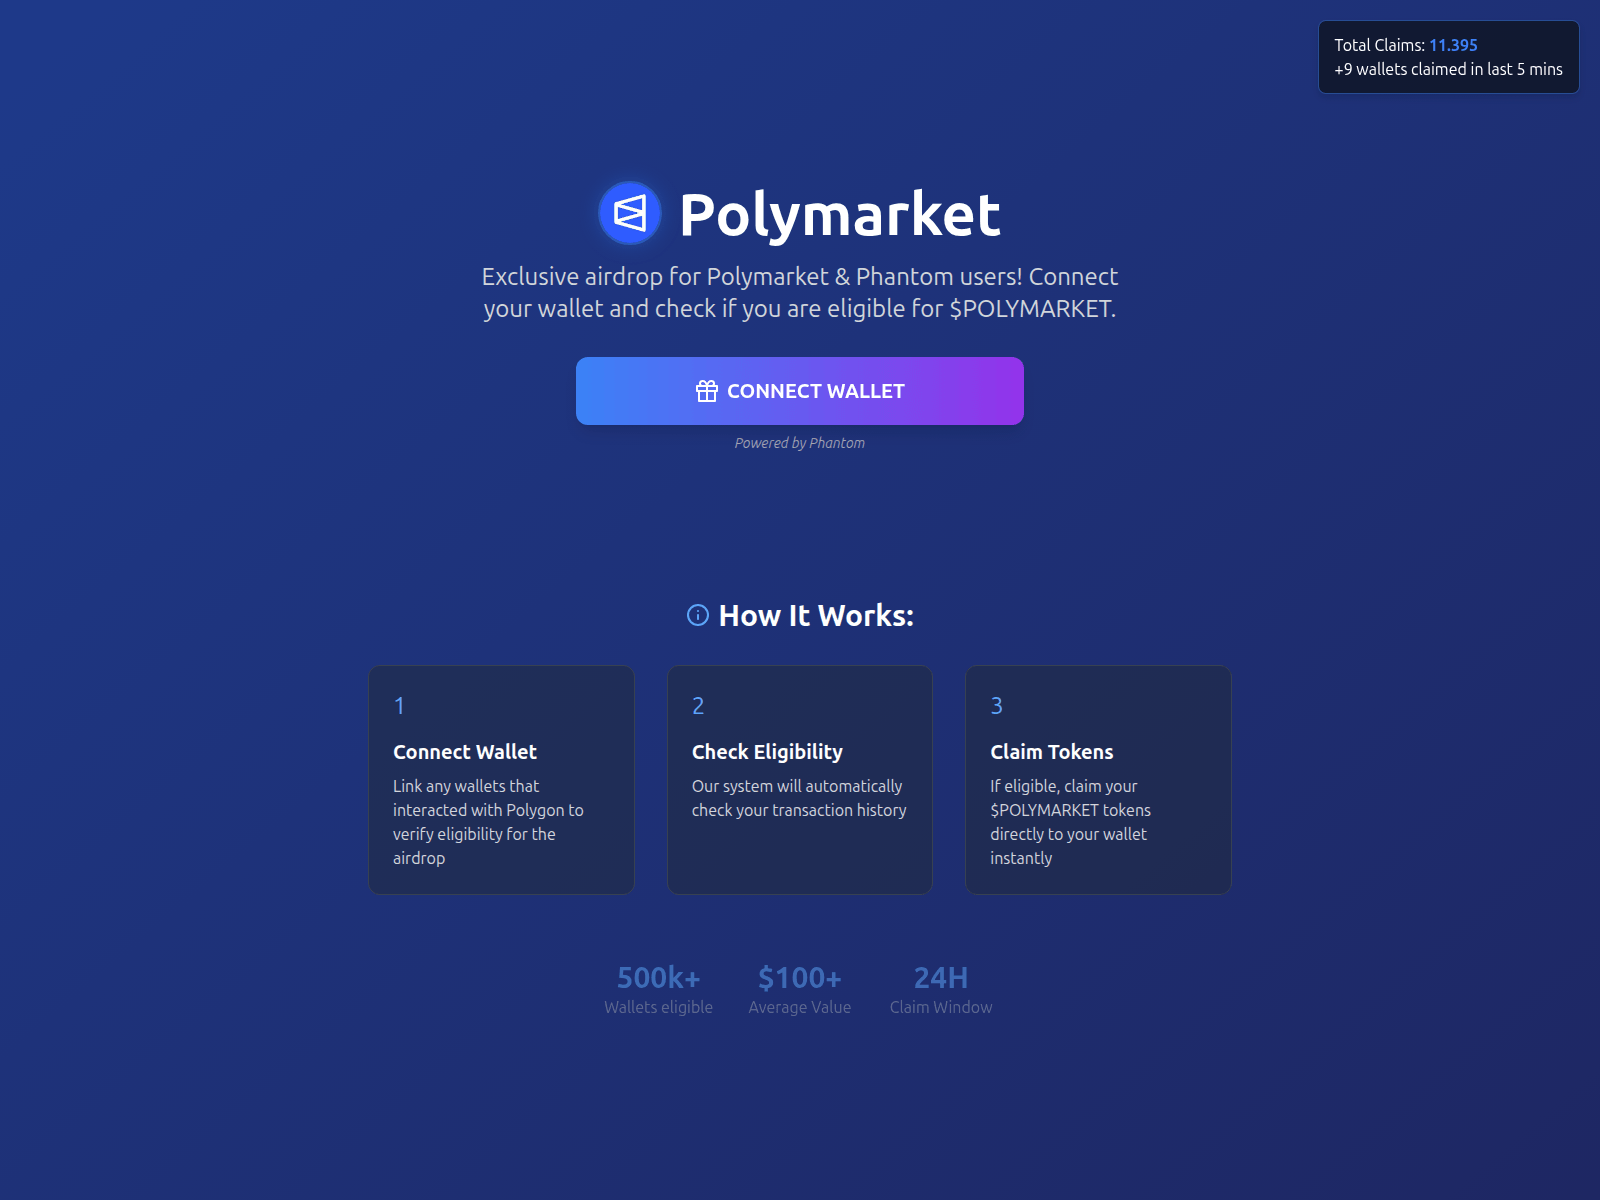
poiymarket.live
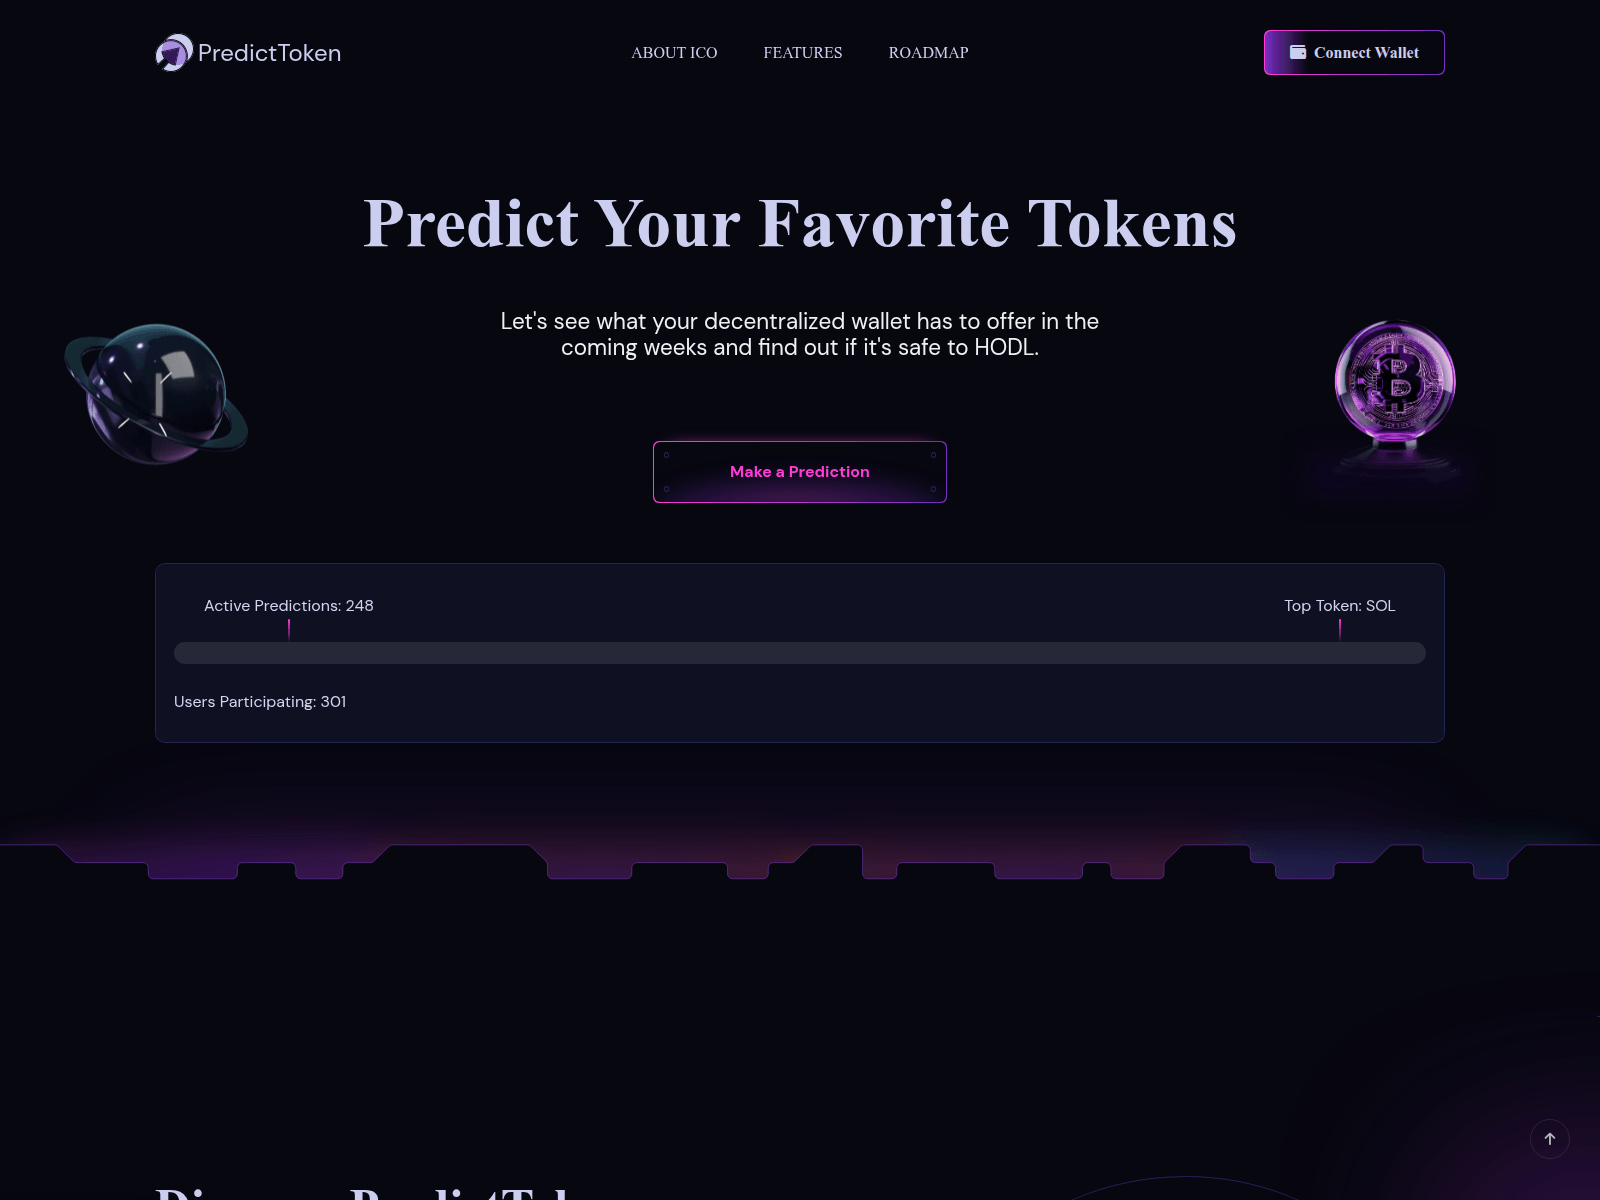
predictmytoken.com

privy-verification.is

protocolnodes.com

pump.solspin.me
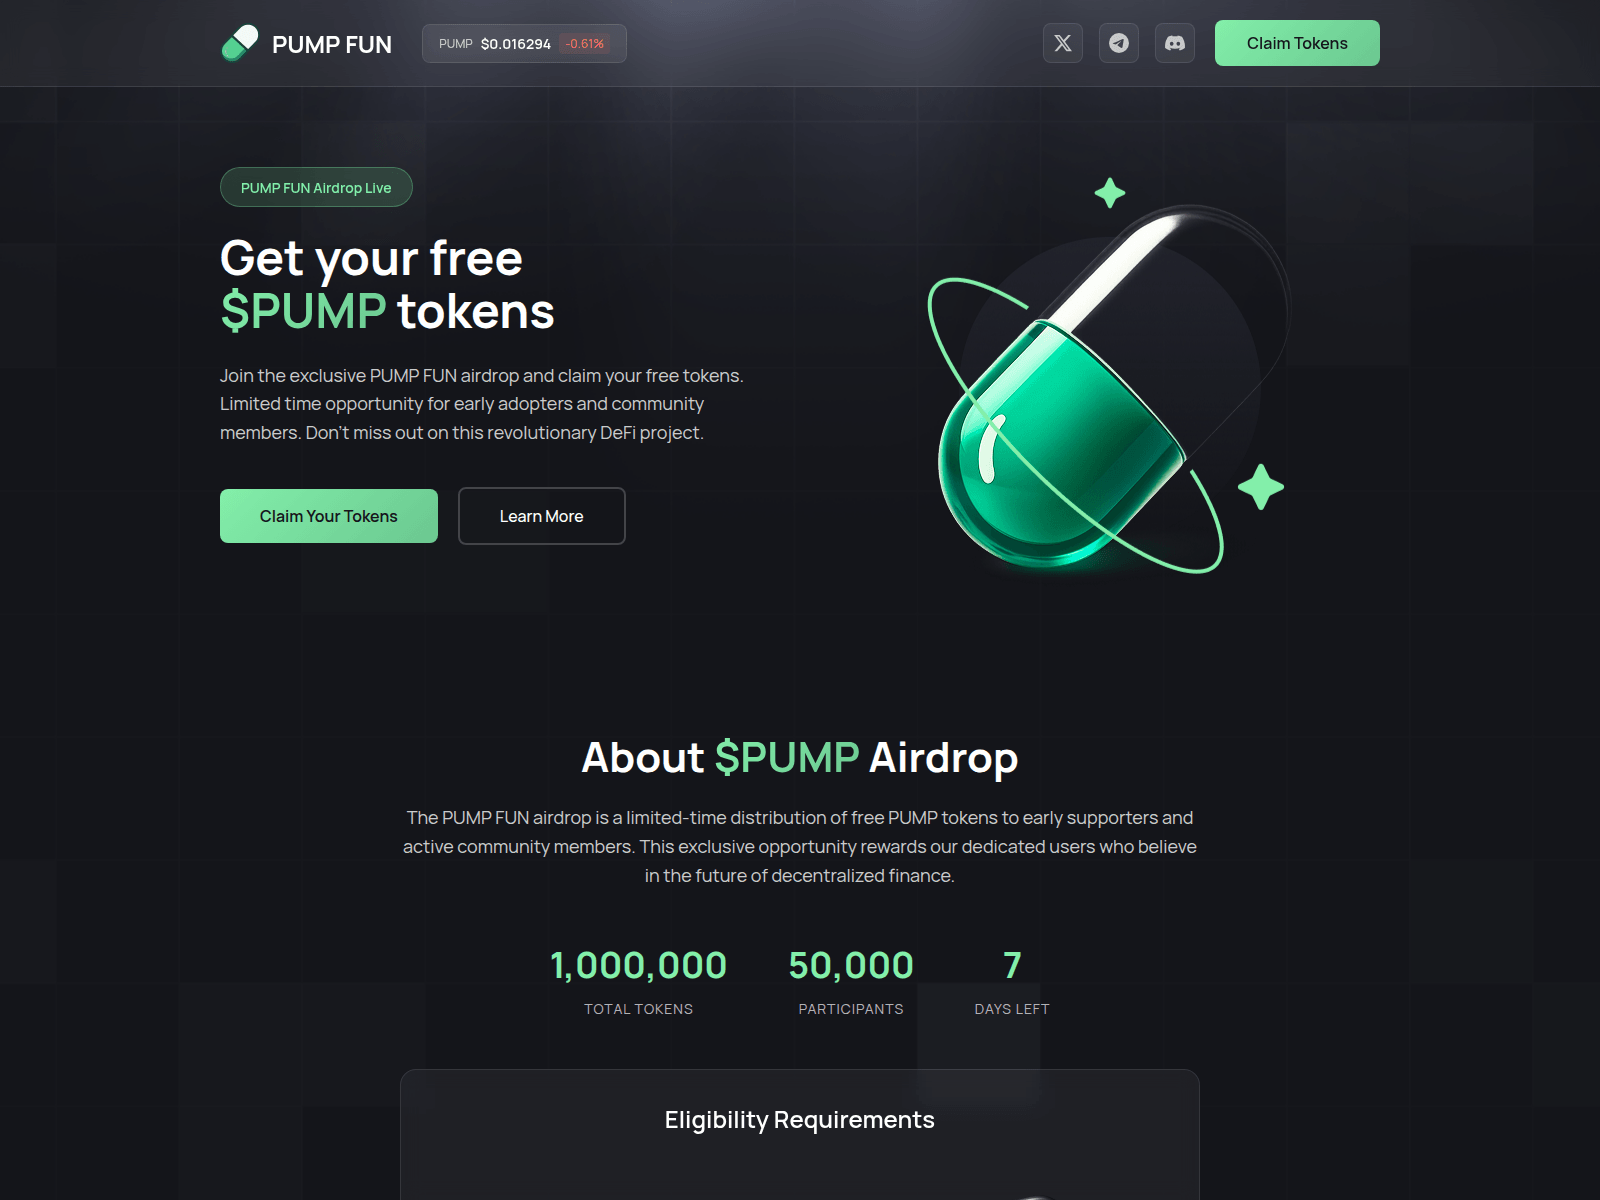
pump.web-hub.cc
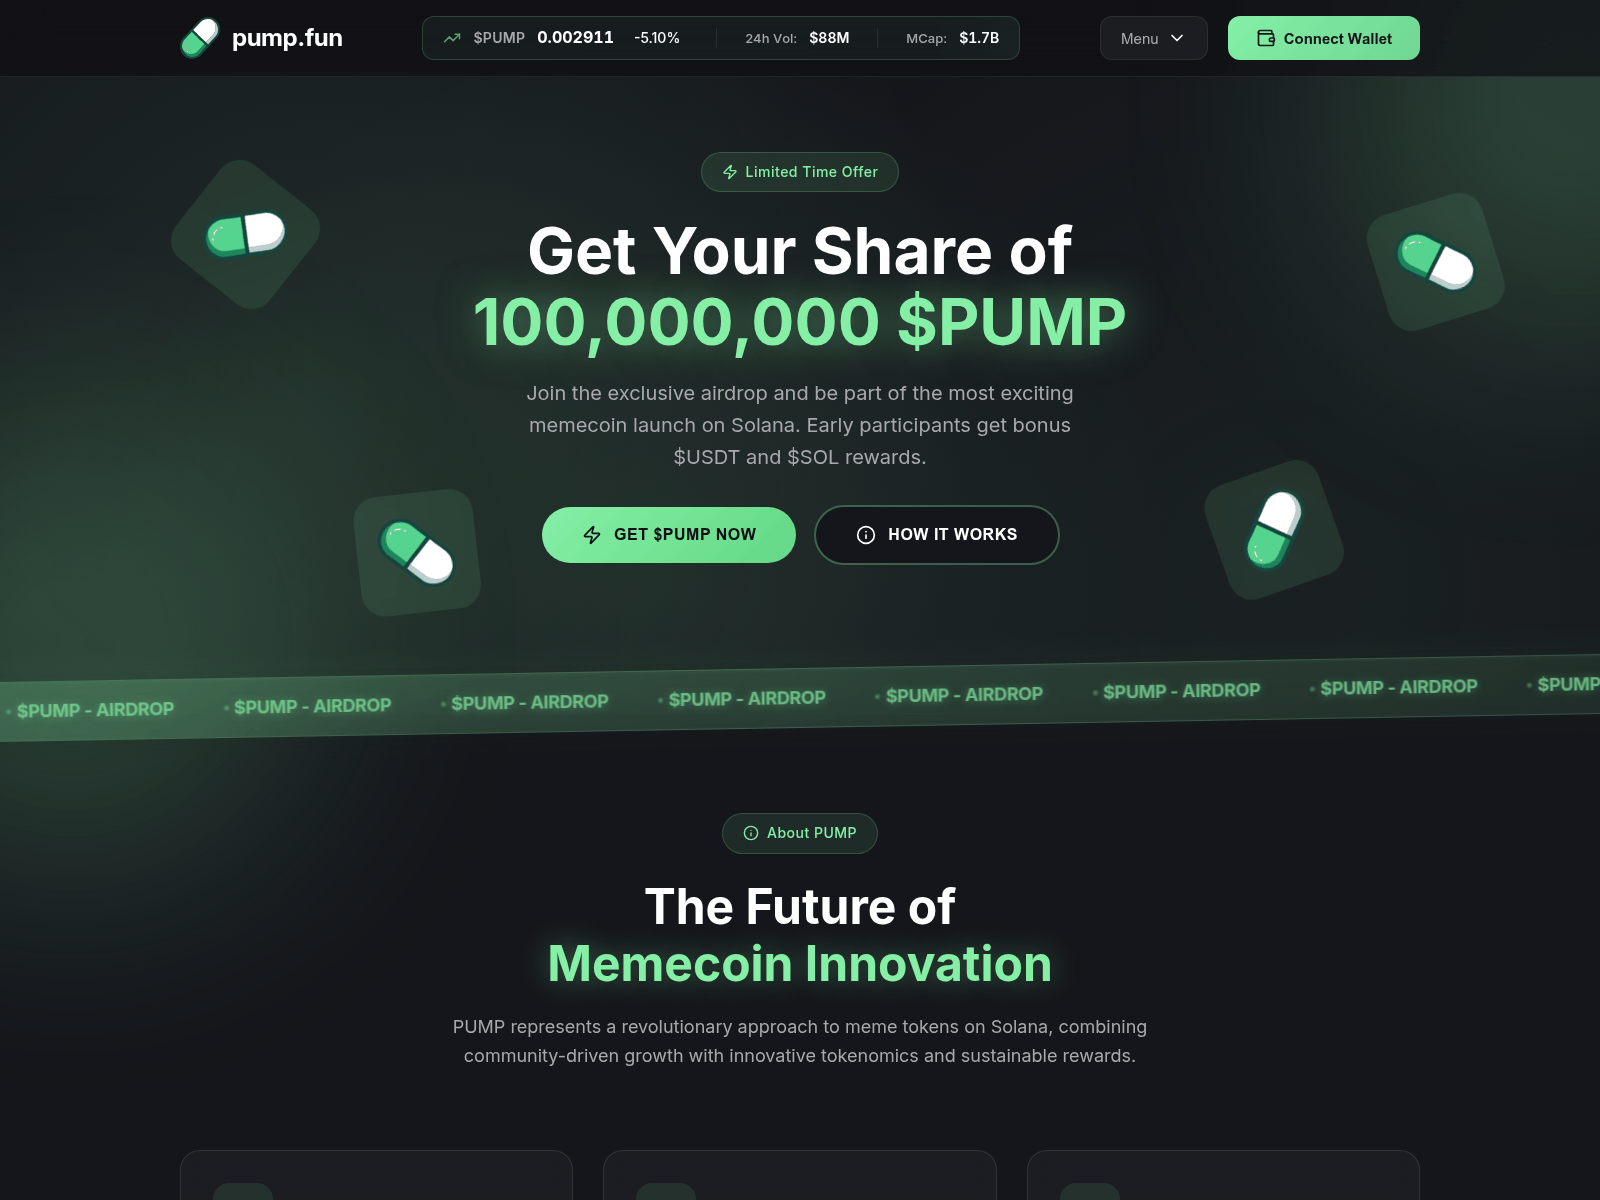
pumpfun-promotion.net
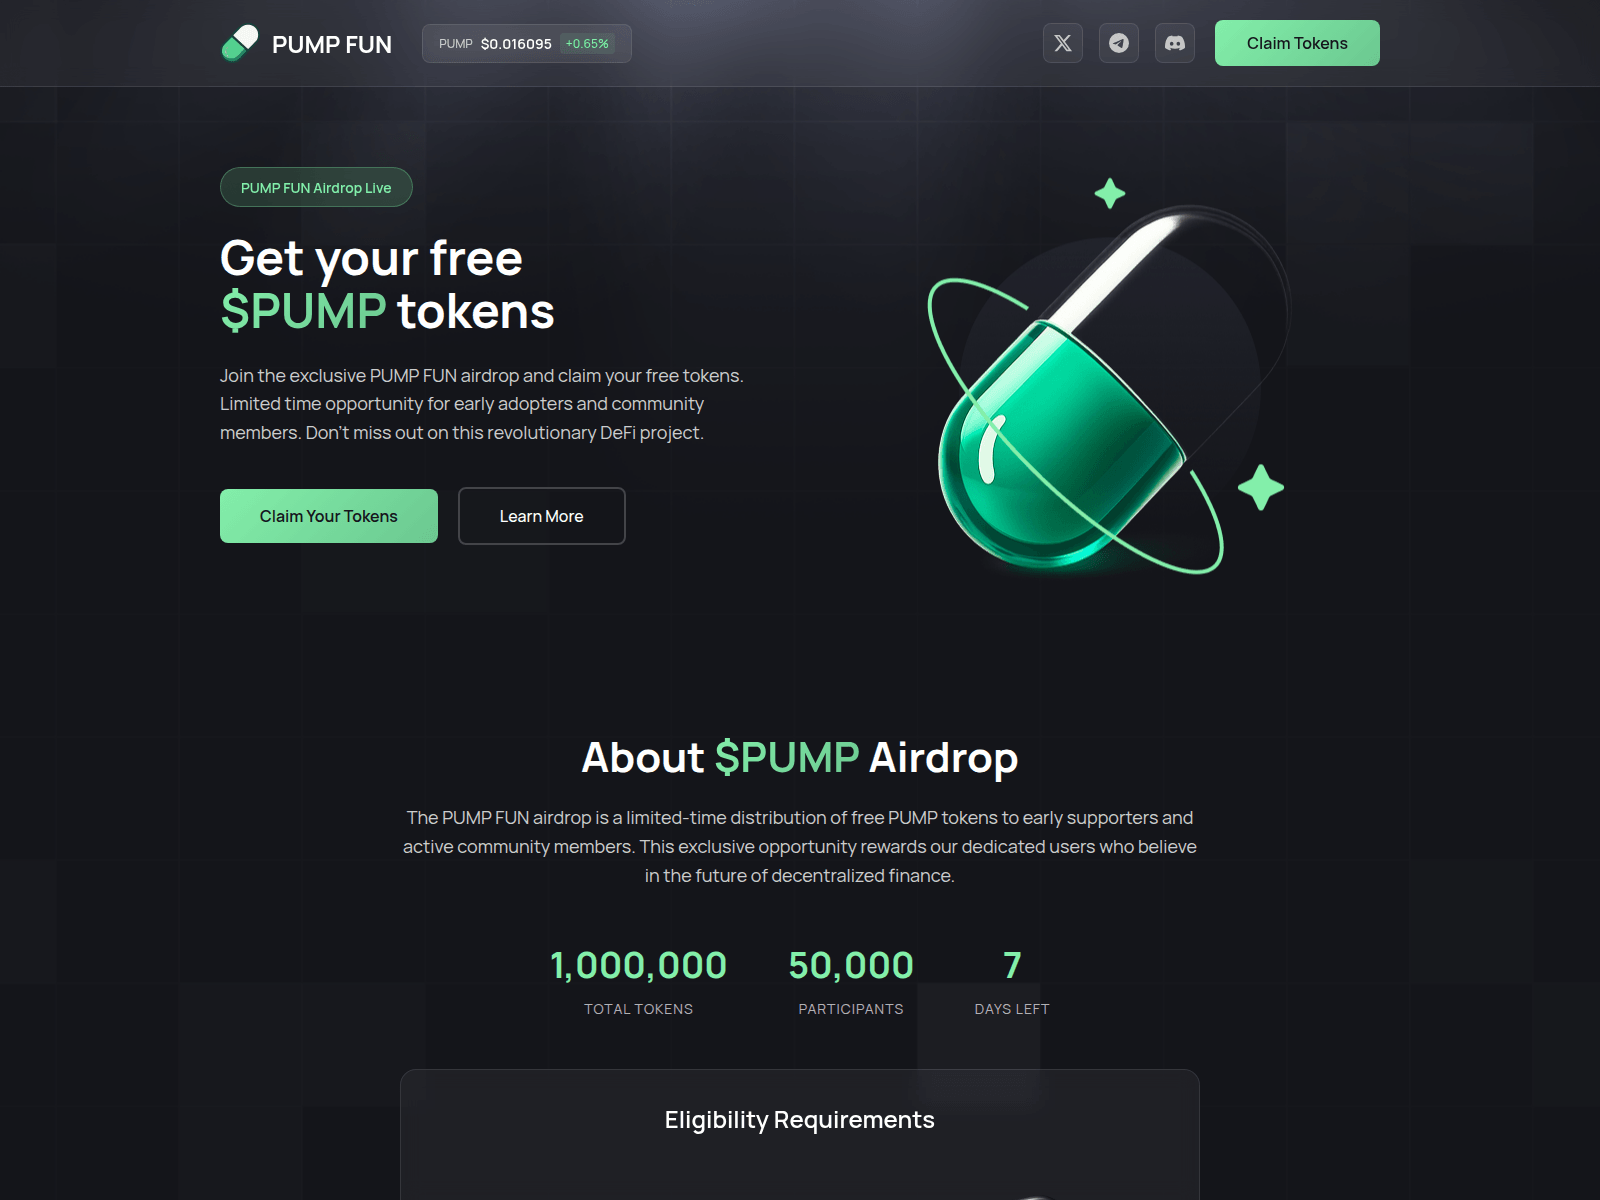
pumpfun2025.com

pumpof.fun

pumpswap.club
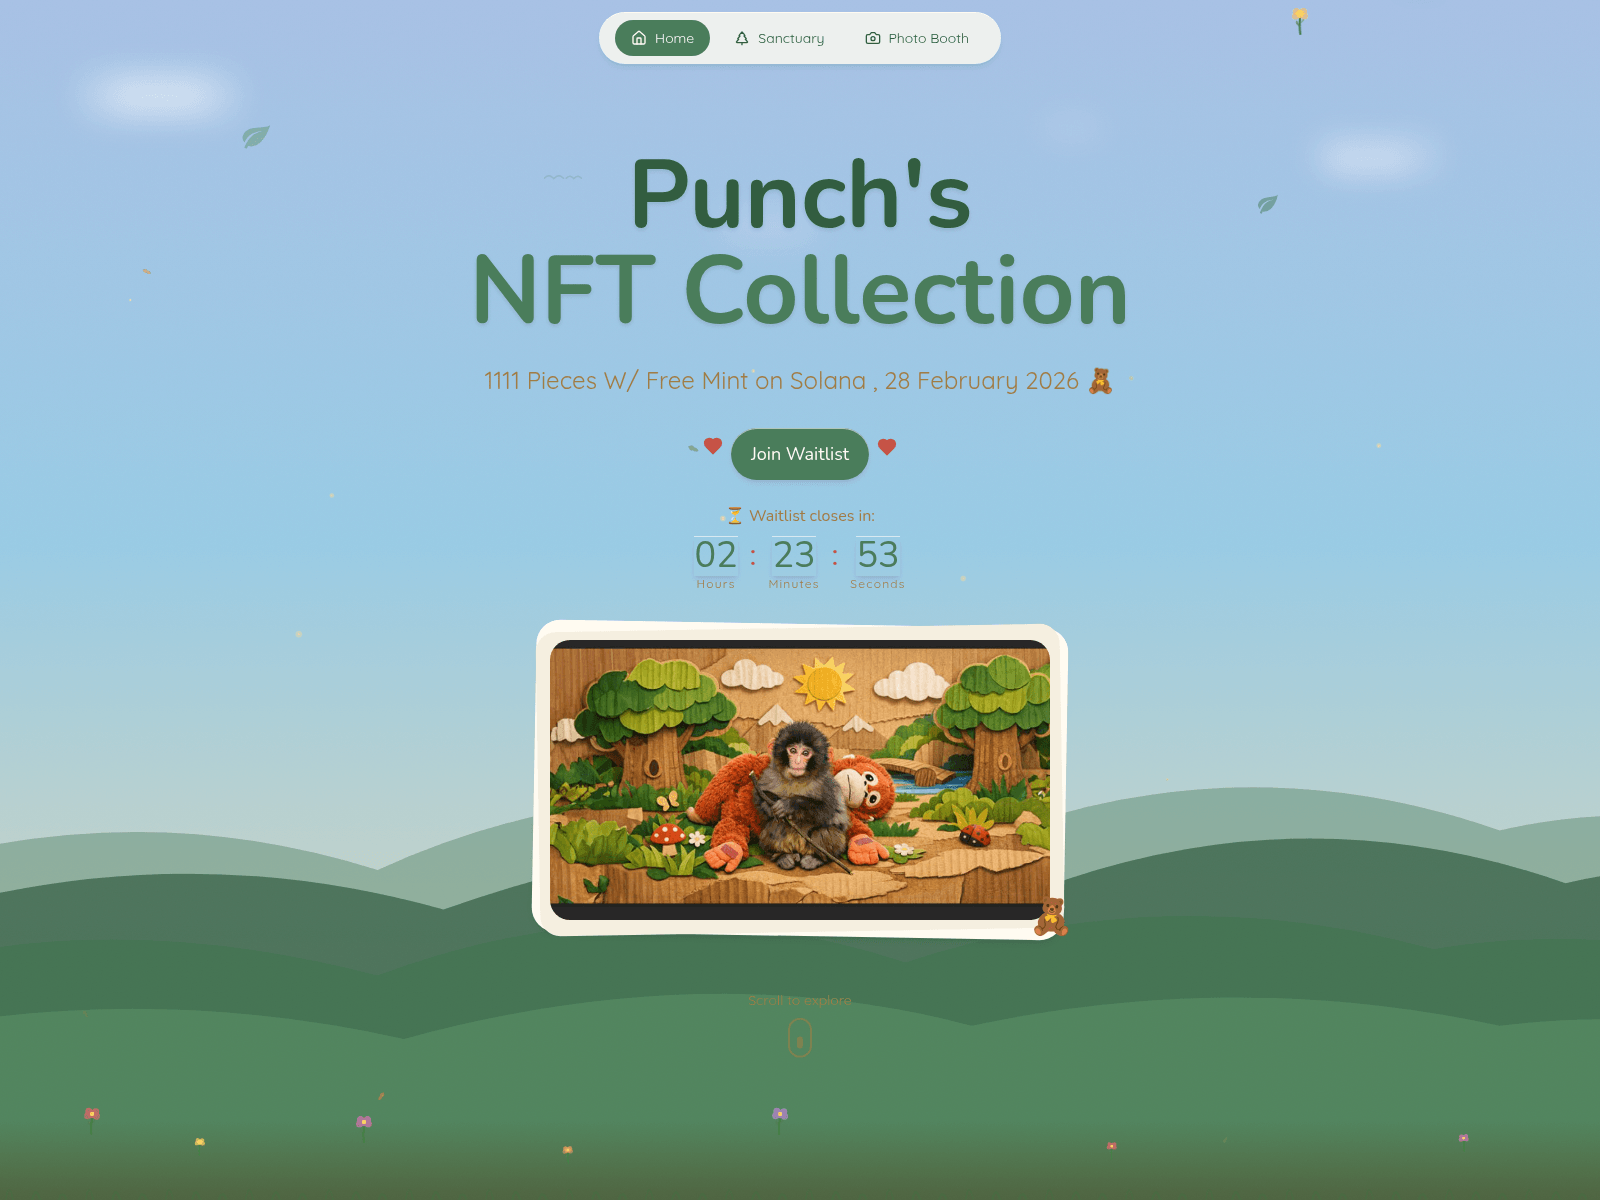
punchinsolana.fun
punchofsol.net
punchonsol.net
punchsolana.app
qpwrz.gdn

ray-claims.website
raydium.io-liquidity-pools.in

raydium.solnode.xyz
raydum-rewardchecker.xyz

register-wankcoin.fun

register-zreal.fun

revshare.live

revshares.xyz

reward-protocol.site

reward-ray.network

reward-saros.xyz

rewards-sachi.xyz

rewards-wojak.xyz
rewards-zeralabs.com

riseupsolana.xyz
Threat Response Pipeline
How every domain in this hub is verified and how confirmed threats are neutralized. Full pipeline visualization →
Threat Intelligence Checks— every domain is scanned & cross-checked against:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ReportCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Security FiltersQuad9 · AdGuard · CleanBrowsingWeb-CheckFull surface scan
 crt.sh
Global Vendor Sync— confirmed detections are pushed to 29 partners:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecSiteReviewAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftTakedown APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ReportHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust