Zum Sicherheitsbericht springen
Domänensicherheit und Bedrohungsinformationen
websxx.com favicon

websxx.com

“WEB3.AI”

Registrar
Cloudflare
Resolved IP
188.114.97.3
Registered
12.09.2026
PhishDestroy assessment Kritisch
Verfügbarkeit Letzter bekanntermaßen aktiv Letzte gespeicherte Erreichbarkeitsbeobachtung Beobachtet · HTTP probe
VirusTotal-Erkennungen: 11/91 Spamhaus DBL: DBL_PHISH Gespeicherte Sperrlistenübereinstimmungen: 2 Betrugstyp: Impersonation
OTX: 4 refs 15.09.2026 CDN
API
Diese Domain wurde als bösartig markiert.
Sicherheits-Engines melden eine Entdeckung: 11. Öffentliche Blocklisten, die eine Übereinstimmung melden: 2. Seien Sie äußerst vorsichtig – Geben Sie keine Anmeldeinformationen oder persönlichen Daten ein.
VirusTotal
engine detections
Google Safe Browsing
OTX
community references
Page captures
open gallery
Domain age
Page analysis & latest checksVirusTotal 0 / 89 · checked 2026-09-15 4 checks

VirusTotal

0 / 89

engines flag the domain

Open

Google Safe Browsing

Gekennzeichnet

Social engineering

Open

AlienVault OTX

0

threat pulses mention the domain

Open

Site status

Online · HTTP 200

Cloudflare · 172.67.184.110 · TLS: Google Trust Services

Reports received
1
First reported
2026-09-15 14:28 UTC
Gelistet
2026-09-15 14:28 UTC
Reported by
PhishDestroy team
Basis for listing
Google Safe Browsing threat flag

Each check shows its own collection time. Zero detections do not guarantee safety.

Berichtsübersicht

Phishing: websxx.com — Letzter bekanntermaßen aktiv (HTTP 200). Zusammenfassung der Beweislage: VirusTotal 11/91 (alphaMountain.ai, BitDefender, CRDF…

Die ausführliche Analyse von PhishDestroy AI bleibt auf Englisch, damit der ursprüngliche forensische Bericht unverändert bleibt.

Source evidenceVirusTotal 11 / 91 · OTX 4 references 6 sources

Spamhaus DBL

DBL_PHISH

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Analysis

Kritisch
VirusTotal
11 / 91
OTX
4 community refs
Page captures
2

PhishDestroy threat report

Overview

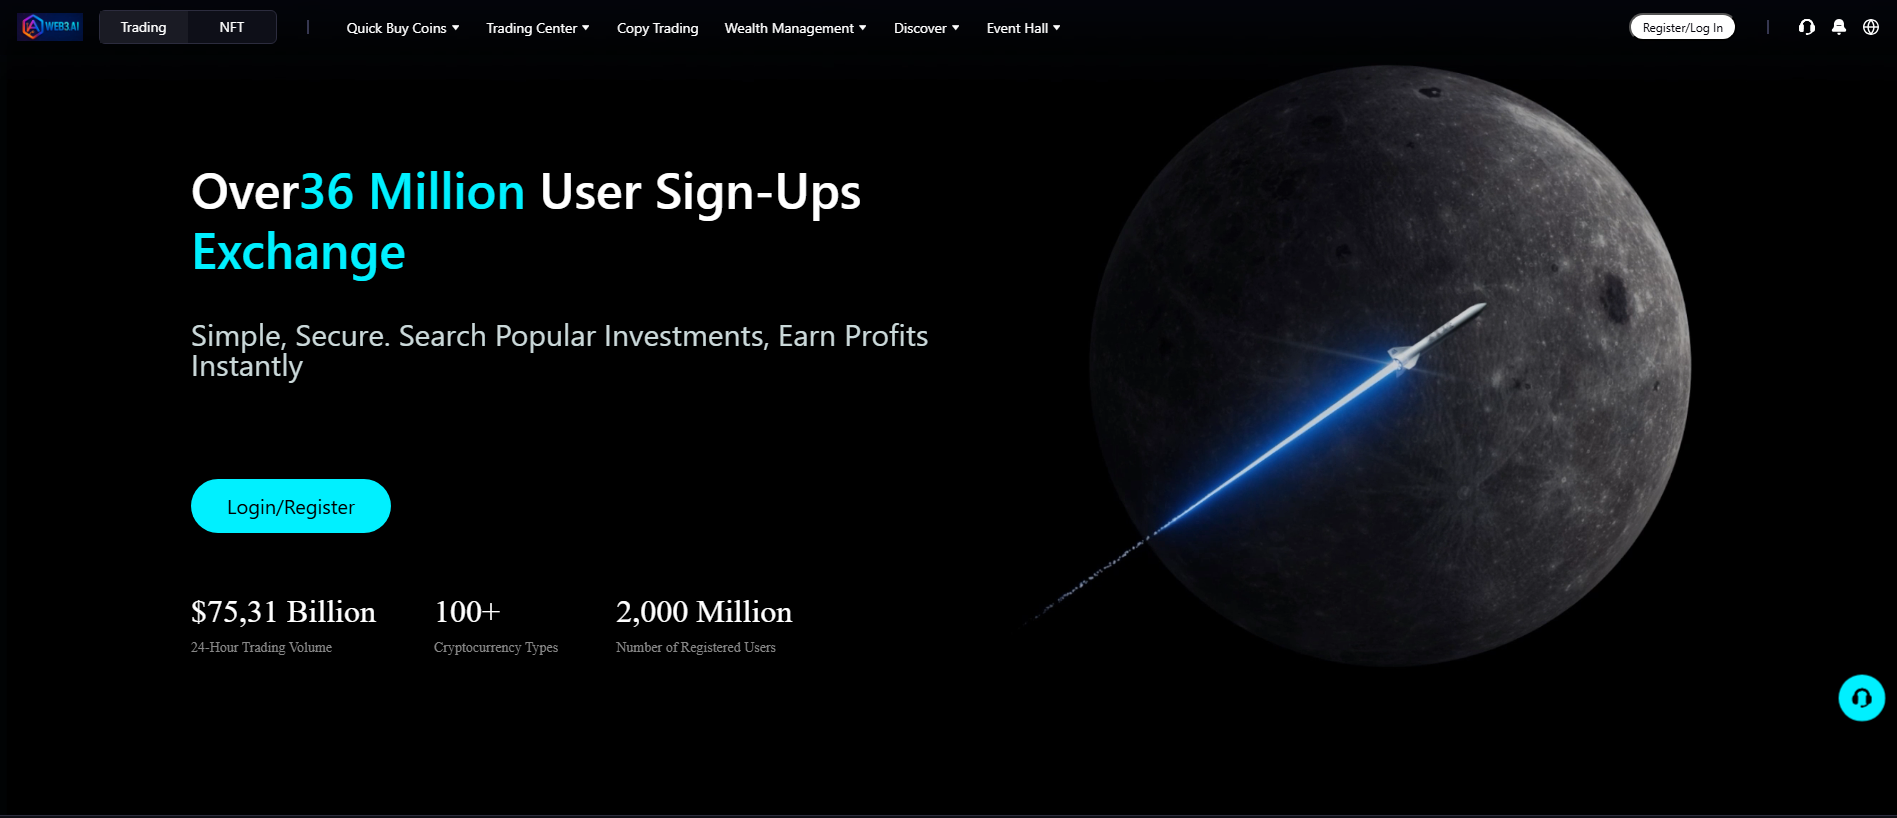
websxx.com is a phishing site that presents itself as WEB3.AI, the name shown in its page title, to lure crypto users into trusting it. PhishDestroy first flagged it on 2026-09-15, only three days after the domain was registered. As of 2026-10-19 the site was still online and serving its content, so it remains a live risk.

How the scam works

Impersonation pages like this copy the name and look of a known crypto brand so visitors believe they are on the official site. The page then pushes the victim toward an action that hands control to the operators, such as connecting a wallet and signing a request, typing in a recovery phrase, or entering account credentials. Whatever is surrendered there gives the attackers direct access to the victim's funds or account, and crypto transfers made this way are rarely recoverable.

Evidence

Eleven of 91 VirusTotal engines flagged the domain as of 2026-09-25, among them BitDefender, Kaspersky, Fortinet, Forcepoint ThreatSeeker, G-Data, Gridinsoft, CRDF and alphaMountain.ai. urlscan.io returned a malicious verdict and tagged the page as a crypto scam. The domain appears on the MetaMask and SEAL blocklists alongside PhishDestroy's own, which means wallet software that relies on those lists can warn users before they interact. Spamhaus lists it in its domain blocklist as phishing, and four AlienVault OTX pulses reference it.

Infrastructure

The domain was registered through Cloudflare, Inc. on 2026-09-12, and PhishDestroy detected it three days later. That short gap is typical of throwaway domains that are set up quickly and put to use right away. The site sits behind Cloudflare's network at 188.114.97.3, geolocated to Canada. That address belongs to Cloudflare's proxy edge rather than to the operators' own server, so it does not reveal where the content is actually hosted.

What to do

If you connected a wallet to this site, review and revoke any token approvals or permissions you granted, and move remaining funds to a new wallet if you signed anything you did not fully understand. If you typed a recovery phrase, treat that wallet as compromised and transfer its assets immediately to a wallet with a freshly generated seed. If you entered a password, change it everywhere you reused it and turn on two-factor authentication. Only reach WEB3.AI through bookmarks or links from its verified channels. Defenders should block the domain at DNS and proxy level and report it to Cloudflare as both registrar and host.

Blocklist matchesMetaMask · PhishDestroy · SEAL 3
MetaMask Gelistet View source
PhishDestroy PhishDestroy list View source
SEAL Gelistet View source

Last checked

Gespeicherte Aufnahme · 2 captures

Domain details

Domain
URLScan verdict Schädlich score 100 Phishing report ↗
IP Context Cloudflare shared edge origin IP hidden Die Edge-IP-Reputation wird dieser Domäne nicht zugeordnet.
OTX tags 2026-09activeall-domainsblocklistcontentcryptoDomainsdrainerfraudlivemonthlyphishdestroyphishingscam
Registrar Cloudflare US(US)
ICANN-RegistrierungsstelleICANN Lookup (RDAP) →
RegistrierungErstellt 12.09.2026 (38d · New) — Expires 12.09.2027
HTTP-Status200
Technische DetailsProvenance & timestamps
Erstmals entdeckt15.09.2026
DOM Analysisanalyzed 15.09.2026score 100/10011 brand signals
Submitted URLhttp://websxx.com/
Favicon Hash
Observed page title
WEB3.AI
Automated brand references
Aave Across Base Coinbase Ethereum Kraken Near Sui +3
TLS-Zertifikat
Ausgestellt von Google Trust Services / WE1 · stored validity ends in 51 days

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
188.114.97.3
Network ASN
AS13335
Organization
CloudFlare, Inc.
Observed location
Toronto, CA
Server header
cloudflare

Die Edge-IP-Reputation wird dieser Domäne nicht zugeordnet.

Nameserver 2

  • betty.ns.cloudflare.com
  • razvan.ns.cloudflare.com

Location describes the IP network.

TLS-Zertifikat

Issuer
Google Trust Services / WE1
Valid from
2026-09-12 06:52:08
Valid until
2026-12-11 07:49:30
Validity
Within stored validity dates
Collection time
2026-10-11 01:03:39 UTC
Collection source
PhishDestroy collector
Certificate fingerprintfb2014c382edf0eb5d99db0c64447aa96c22c1c3a228f559aca5d1f99db3b021

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Latest Classified Outcome 2026-10-19 22:33:20 UTC

Primary outcome Aktive Inhalte reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation Aktive Inhalte Ordinary HTTP content served 90% 2026-10-19 22:33:20 UTC
RDAP registration Unbekannt
Observed timeline last reachable: 2026-10-19 22:35:40 UTC last content: 2026-10-19 22:33:20 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Technologien · 6 identified
Detected via Cloudflare Radar · Wappalyzer engine
Diese Domain melden Reichen Sie Beweismaterial ein und helfen Sie mit, andere zu schützen

VirusTotal-Analyse

11 / 91 Sicherheitsanbieter haben diese Domain markiert
View on VT
Last analyzed First positive detection Previous stored snapshot: 11 detections
alphaMountain.ai
BitDefender
CRDF
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
Lionic
SOCRadar
Sophos

Archivierte Beweise

Wayback Machine Snapshot
Zur Beweisüberprüfung steht ein historischer Schnappschuss zur Verfügung
View Archive
Registration & observation details3

Availability observations

Last reachable observation
Last content observation
Estimate basis
Currently reachable

An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

websxx.com
Gespeichertes Ergebnis
Cloaked / Filtered
Stored observation history21

Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.

  1. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  2. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  3. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  4. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  5. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

Earlier observations 16
  1. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  2. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  3. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  4. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  5. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  6. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  7. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  8. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  9. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  10. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  11. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  12. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  13. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  14. VirusTotal · Detection count

    0→3

  15. Google Safe Browsing · Threat flag

    No flag recorded→Flag recorded

  16. Availability monitor · First collection record

    Erreichbar

Recorded activity

5 entries
  1. AlienVault OTX

    4 community references

    View source
  2. Google Safe Browsing

    No threat flag

    View source
  3. VirusTotal

    11/91 engine detections

    View source
  4. Added to PhishDestroy

    websxx.com

    View source
  5. URLScan

    Page captured

    View source

Ähnliche Domains

516 gespeicherte ähnliche Domains

Alle anzeigen (88)
colnbase.com homoglyph Interner Bericht xn--conbse-sta7g.com homoglyph Interner Bericht coinbasez.com addition Interner Bericht aavef.com addition Interner Bericht xn--ave-ila.com homoglyph Interner Bericht athereum.org bitsquatting dethereum.org insertion e.thereum.org subdomain efhereum.org replacement ehereum.org omission etereum.org omission eth3reum.org replacement ether.eum.org subdomain etheream.org vowel-swap ethereim.org replacement ethereium.org insertion etherem.org omission etheremu.org transposition ethereom.org vowel-swap etheresum.org insertion ethereujm.org insertion ethereum2.org addition ethereum3.org addition ethereum4.org addition ethereumc.org addition ethereumd.org addition ethereumorg.com various ethereumr.org addition ethereums.org addition ethereumx.org addition ethereun.org homoglyph ethereunm.org homoglyph ethereurm.org homoglyph ethereurn.org homoglyph ethereuym.org insertion ethereuzm.org insertion ethereyum.org insertion etherium.org vowel-swap etherrum.org replacement etherteum.org insertion etherum.org omission ethezeum.org bitsquatting ethireum.org vowel-swap ethnereum.org insertion ethreum.org omission ethureum.org bitsquatting etihereum.org homoglyph ithereum.org vowel-swap othereum.org vowel-swap rethereum.org insertion sethereum.org insertion thereum.org omission uthereum.org bitsquatting zethereum.org insertion zthereum.org replacement ikraken.com insertion jkraken.com insertion kaken.com omission karken.com transposition keaken.com replacement kkraken.com repetition kr2aken.com insertion kraaken.com repetition kraekn.com transposition kraen.com omission kraiken.com insertion krak3n.com replacement krake.com omission krakeb.com replacement krakeen.com repetition krakeh.com replacement krakencom.com various krakewn.com insertion krakien.com insertion krakin.com vowel-swap krakjen.com insertion krakken.com repetition krakn.com omission krakne.com transposition krakon.com vowel-swap krakren.com insertion krakrn.com replacement krakwen.com insertion krakwn.com replacement kralen.com replacement kramen.com replacement kreaken.com insertion krkaen.com transposition

100 von 516 angezeigt

Nachweise und externe Berichte

Eingehende Analyse
Help & reporting

Wurden Sie von dieser Website betroffen?

4 evidence signal groups linked 0 stored notification records Letzter bekanntermaßen aktiv

Listed domains receive at least one abuse report; this entry has no retained notification history.

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Wenn Sie Kontoanmeldeinformationen, persönliche oder Zahlungsinformationen eingegeben oder eine Datei von dieser Domain heruntergeladen haben, ergreifen Sie sofort Maßnahmen. Nachfolgend finden Sie Ressourcen, die Ihnen helfen, den Vorfall zu melden und sich zu schützen.

Official reporting routes

Vorsicht vor Betrügern, die mit der Rückforderung von Geldern locken! Kriminelle nehmen unter Umständen erneut Kontakt zu Opfern auf und geben dabei vor, Ermittler, Anwälte oder Beitreibungsbeamte zu sein. Zahlen Sie keine Vorabgebühren und geben Sie keine Anmeldeinformationen weiter. Erfahren Sie mehr über Betrug im Zusammenhang mit Wiederaufbaumaßnahmen →

Melden Sie sich bei Ihren örtlichen Behörden

Wählen Sie Ihr Land aus, um Offizielle Kontakte im Bereich Cyberkriminalität oder einen Beschwerdeentwurf erstellen → zu erhalten.

97-Länder-Verzeichnis

Template-based draft · optional AI wording assistance requires separate consent

KI-gestützter Entwurf – Vorfalldetails werden vom KI-Anbieter verarbeitet · Überprüfen Sie es und reichen Sie es selbst ein
After a phishing incident

Empfehlungen und Ratschläge für Betroffene

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

Was soll ich sofort tun?

Dringend

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • Alle Passwörter ändern — E-Mail, Exchange-Konten, alles, wofür dasselbe Passwort verwendet wird
  • 2FA aktivieren mit einer Authentifizierungs-App (nicht per SMS). Deaktivieren Sie die SMS-basierte Wiederherstellung
  • Karten einfrieren Falls Sie auf der Phishing-Seite Ihre Bankdaten eingegeben haben

Welche Informationen sollte ich für meinen Bericht sammeln?

FBI-Richtlinien

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • Genaue Daten und Uhrzeiten — jeder Transaktion und des ersten Kontakts mit dem Betrüger
  • Screenshots — betrügerische Websites, Chat-Nachrichten, E-Mails, Wallet-Transaktionen, soziale Medien
  • Alle URLs und Domains die der Betrüger verwendet (einschließlich websxx.com)
  • Kommunikation — E-Mails, SMS, Telefonnummern, Benutzernamen, die der Betrüger verwendet hat

Auch wenn dir nicht alle Details bekannt sind — trotzdem Anzeige erstatten. Auch unvollständige Informationen sind für die Ermittlungen hilfreich.

Wo soll ich den Betrugsfall melden?

  • FBI IC3 — Internet Crime Complaint Center (Meldestelle der US-Bundesbehörden)
  • Europol — Meldungen zu Cyberkriminalität in Europa (EU)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • Ortspolizei — sorgt für eine offizielle Dokumentation, auch wenn sie nicht sofort handeln können

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • Gefälschte Websites — pixelgenaue Kopien legitimer Websites mit leicht abgeänderten Domains
  • Schweineschlachtung — über Wochen hinweg über Telegram, WhatsApp und Dating-Apps aufgebautes Vertrauen, dann wurde Geld gestohlen
  • Betrugsmaschen im Zusammenhang mit der Rückforderung von Geldern — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • Durch KI gestützte Betrugsmaschen — Deepfakes, automatisiertes Phishing und KI-generierte Websites, die es erschweren, Betrugsversuche zu erkennen

Wie kann ich mich in Zukunft schützen?

  • Offizielle Websites als Lesezeichen speichern — Klicken Sie niemals auf Links in E-Mails, Direktnachrichten oder Anzeigen
  • Domains überprüfen — nachsehen, ob PhishDestroy Bevor Sie Kontakt aufnehmen: Überprüfen Sie HTTPS, die Rechtschreibung und das Alter der Domain.
  • „Zu schön, um wahr zu sein“ = Betrug — garantierte Renditen, Prominente als Werbeträger, dringende Fristen

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

Bleiben Sie auf dem Laufenden, bleiben Sie sicher

Beobachten Sie aktuelle Bedrohungen oder legen Sie Widerspruch gegen diesen Eintrag ein, wenn Sie der Meinung sind, dass es sich um einen Fehlalarm handelt

About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

Diesen Bericht einbetten

Teilen Sie diese Bedrohungsinformationen auf Ihrer Website oder in Ihrem Blog

embed.html
<iframe
  src="https://phishdestroy.io/de/embed/domain/websxx.com"
  title="PhishDestroy threat report for websxx.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>