Zum Sicherheitsbericht springen
Domänensicherheit und Bedrohungsinformationen
rain-bet.casino favicon

rain-bet.casino

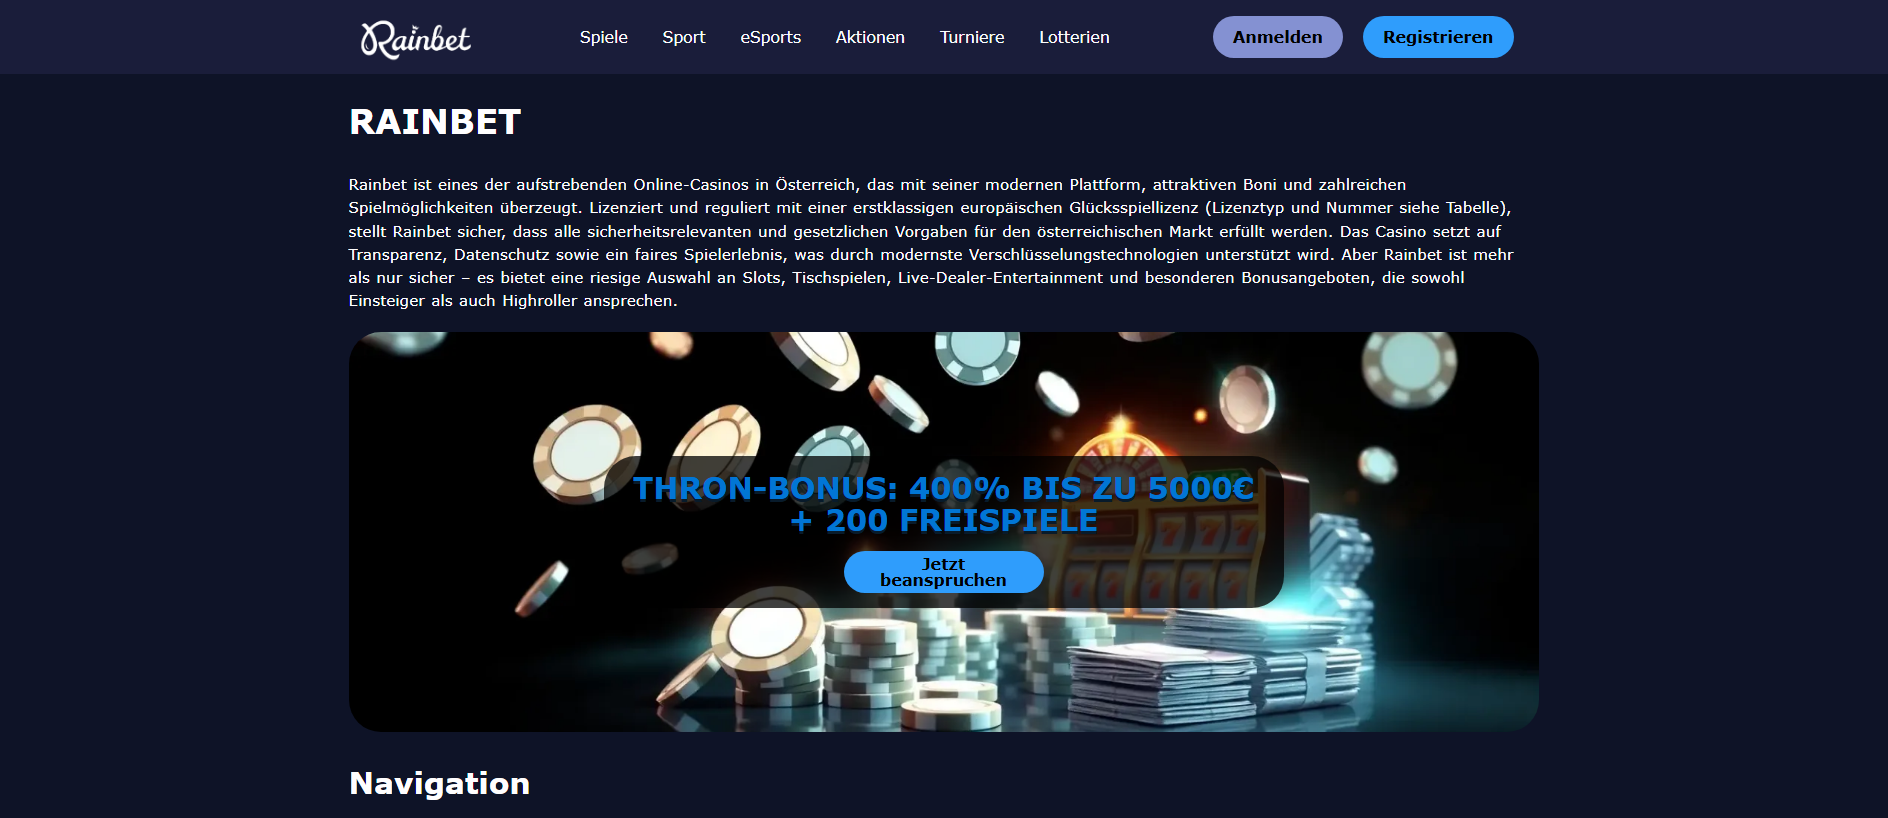
“Rainbet | Anmelden, 400% bis zu 5000€ + 200 Freispiele”

Registrar
Hosting Concepts
Resolved IP
188.114.97.3
Registered
18.06.2025
Drohungsurteil Kritisch
Verfügbarkeit Letzter bekanntermaßen aktiv Letzte gespeicherte Erreichbarkeitsbeobachtung Beobachtet
Source: HTTP probe
VirusTotal-Erkennungen: 10/91 Spamhaus DBL: DBL_PHISH Gespeicherte Sperrlistenübereinstimmungen: 2 Betrugstyp: Gambling
OTX: 4 refs 23.07.2026 1 Report Sent CDN
API
Diese Domain wurde als bösartig markiert.
Sicherheits-Engines melden eine Entdeckung: 10. Öffentliche Blocklisten, die eine Übereinstimmung melden: 2. Seien Sie äußerst vorsichtig – Geben Sie keine Anmeldeinformationen oder persönlichen Daten ein.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@registrar.eu. The latest stored availability evidence still shows the domain reachable; 2 months has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
2 months
Reports sent
1
Latest case ID
PD-20260723-26BF1C
Current status
HTTP 200 at latest stored check
Berichtsübersicht

rain-bet.casino — Letzter bekanntermaßen aktiv (HTTP 200). Betrugstyp: Gambling. Zusammenfassung der Beweislage: VirusTotal 10/91 (ChainPatrol, alphaMountain.ai, BitDefender, Chong Lua Dao, CRDF); Spamhaus DBL_PHISH; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 100/100. Registrar: Hosting Concepts.

Die ausführliche Analyse von PhishDestroy AI bleibt auf Englisch, damit der ursprüngliche forensische Bericht unverändert bleibt.

Spamhaus DBL
DBL_PHISH
VirusTotal
VirusTotal
10 det.
OTX references
URLScan
URLScan
TLS-Zertifikat
Abgelaufen oder nicht verifiziert
Alter
1.3 yr
Beobachteter Status
Letzter bekanntermaßen aktiv 200
PhishDestroy
DestroyList
Gelistet
Reports Sent
1

Source evidence

8 sources

VirusTotal

10 / 91

Melden

Spamhaus DBL

DBL_PHISH

URLQuery

checked — no detections recorded

Melden

OTX

4 community references

Melden

CF-Radar

provider verdict: clean

Melden

URLScan capture

gespeicherter Bericht

Stored URLScan capture preview
Melden

URLScan verdict

Analyse abgeschlossen

Melden

Google Safe Browsing

Checked; no threat flag recorded

Melden

Zusammenfassung der Beweislage

Kritisch
VirusTotal
10/91
OTX
4 community refs
URLScan
Stored capture

Analysis as of July 23, 2026 indicates that the domain rain-bet.casino was registered on June 18, 2025 through Hosting Concepts B.V. d/b/a Registrar.eu. The authoritative name servers are donna.ns.cloudflare.com and wilson.ns.cloudflare.com, both belonging to Cloudflare’s DNS service. DNS resolution points the domain to the IPv4 address 188.114.97.3, a host that appears in Cloudflare’s network and is used by multiple unrelated sites, offering no inherent indication of malicious intent but also providing anonymity for threat actors. The domain has been flagged by the PhishDestroy blocklist and is present on a single external security blocklist, confirming that at least one independent anti‑phishing feed has identified it as suspicious.

A VirusTotal scan was performed by 95 AV engines; none raised a detection. While the lack of detections does not constitute a safety guarantee, it does suggest that the payload or landing page has not yet been associated with known malware signatures. Publicly available intelligence does not include a page title, SSL certificate details, HTTP response codes, Safe Browsing verdicts, or Open Threat Exchange (OTX) tags for rain-bet.casino. Consequently, the exact content and credential‑harvesting techniques employed by the site remain unconfirmed.

The absence of these data points limits the ability to attribute a specific phishing kit or to validate whether the domain is actively serving malicious pages. Defenders should continue to treat rain-bet.casino as a high‑confidence phishing indicator based on its blocklist presence and registrar profile. Recommended actions include adding the domain to network‑level deny lists, configuring email gateways to block URLs that resolve to the associated IP address, and monitoring DNS queries for the Cloudflare name servers.

Analyse von Erkennung und Umgehung

Verdacht auf Cloaking: Scanner- und Besuchertitel weichen voneinander ab

Noch nicht eingescannt Bislang wurde noch kein Unterschied zwischen Crawler und Browser festgestellt.

Gespeicherte Beobachtungen zum Vergleich zwischen Crawler und Browser für diesen Host sowie eine Echtzeit-Fingerabdruckprüfung für Verkehrsverteilungssysteme im Keitaro-Stil.

Gespeichertes Cloaking-Flag
Noch nicht eingescannt
Letzter Tarnungsscan
Vom Scanner erkannter Server-Header
Caddy

Anmerkung des Scanners: alive_content: raw=ok; http=200; via=https_proxy; server=Caddy

Titel, der dem Sicherheitsscanner angezeigt wirdrain-bet.casino
Titel, der einem Browser-Besucher angezeigt wirdRainbet | Anmelden, 400% bis zu 5000€ + 200 Freispiele
Live-TDS-Fingerabdruckprüfung
Sieben Keitaro-Fingerabdrücke sowie ein Vergleich zwischen Crawler und Browser, der vom „PhishDestroy“-Scanner ausgeführt wird, wenn dieses Fenster geöffnet ist.
Warten

Gespeicherte Aufnahme · 3 captures

Seitentitel
Rainbet | Anmelden, 400% bis zu 5000€ + 200 Freispiele
TLS-Zertifikat
Hostname coverage not recorded · Ausgestellt von Google Trust Services · stored validity ends in 52 days

Domain details

Domain
URLScan Verdict Analyse abgeschlossen score 0 report ↗
IP Context Cloudflare shared edge origin IP hidden Die Edge-IP-Reputation wird dieser Domäne nicht zugeordnet.
OTX Tags 2026-07activeall-domainsblocklistcontentcryptoDomainsdrainerfraudlivemonthlyphishdestroyphishingscam
Registrar Hosting Concepts (Unknown)
Abuse-Kontaktabuse@registrar.eu
ICANN-RegistrierungsstelleICANN Lookup (RDAP) →
RegistrierungErstellt 18.06.2025 — Expires 18.06.2027
HTTP-Status200
Technische DetailsProvenance & timestamps
Erstmals entdeckt23.07.2026
DOM Analysisanalyzed 23.07.2026score 100/100
Submitted URLhttp://rain-bet.casino/
Favicon Hash
Fall-ID
ICANN OVERSIGHT

Akkreditierung und RAA-Kontext

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft Nichts wird automatisch gesendet.

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
188.114.97.3
Network ASN
AS13335
Organization
CloudFlare, Inc.
Observed location
Toronto, CA
Server header
cloudflare

Die Edge-IP-Reputation wird dieser Domäne nicht zugeordnet.

Nameserver 2

  • donna.ns.cloudflare.com
  • wilson.ns.cloudflare.com

Location describes the IP network.

TLS-Zertifikat

Issuer
Google Trust Services
Valid from
2026-06-16 01:07:36
Valid until
2026-09-14 02:06:26
Hostname coverage
Hostname coverage not recorded
Validity
Stored certificate expired
Collection time
2026-10-13 19:05:05 UTC
Collection source
PhishDestroy collector
Certificate fingerprint5800c8021e330c7fddaee995fca2bbd5ebffb1a5a305b55aede8d756edbd715f

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 188.114.97.3rapiddns.io

Latest Classified Outcome 2026-10-13 10:37:56 UTC

Primary outcome Unbekannt reason: Probe Inconclusive 20% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unreachable Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Unbekannt Probe Inconclusive 20% 2026-10-13 10:37:56 UTC
RDAP registration Unbekannt
Observed timeline last reachable: 2026-10-13 02:12:27 UTC last content: 2026-10-13 02:12:27 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Casino / Gambling License Verification
Unverified gambling license
This domain markets casino/gambling services. Scam casinos routinely display fake Curaçao, MGA, or Kahnawake license badges that don’t exist in the real registries. Always verify the license number against the official regulator database before depositing. If the site shows a seal but no clickable registry link — or the linked registry page doesn’t exist — treat it as fraudulent.
Curaçao eGaming (official) Malta Gaming Authority UK Gambling Commission PA Gaming Control Kahnawake Gaming Gibraltar Gambling
Technologien · 3 identified
Detected via Cloudflare Radar · Wappalyzer engine
Diese Domain melden Reichen Sie Beweismaterial ein und helfen Sie mit, andere zu schützen

VirusTotal-Analyse

10 / 91 Sicherheitsanbieter haben diese Domain markiert
View on VT
Last analyzed First positive detection Previous stored snapshot: 10 detections
ChainPatrol
alphaMountain.ai
BitDefender
Chong Lua Dao
CRDF
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
SOCRadar

Archivierte Beweise

Wayback Machine Snapshot
Zur Beweisüberprüfung steht ein historischer Schnappschuss zur Verfügung
View Archive
Website-Performanceanalyse

Google PageSpeed Insights — mobile performance audit of rain-bet.casino · checked Jul 23, 2026

100
Good
Performance
FCP
0.9s
First Contentful Paint
LCP
1.37s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
2.47s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Pipeline zur Reaktion auf Sicherheitsbedrohungen

Entdeckung
Analysis
Notifications
Monitoring

12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Bedrohung erkannt
rain-bet.casino erkannt und für eine vollständige Analyse in die Warteschlange gestellt
23.07.2026
Spamhaus DBL
Spamhaus DBL recorded DBL_PHISH
21.09.2026
URLScan.io Capture
Gespeichert URLScan report with capture artifacts
23.07.2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in Wayback Machine — historical evidence archived
23.07.2026
VirusTotal
10/91 recorded on VirusTotal
06.10.2026
Erkennung von Blocklisten
Gefunden in 2 blocklists: MetaMask, SEAL
14.10.2026
OTX Community References
4 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
05.10.2026
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
23.07.2026
Technical Analysis Recorded
Der Bericht enthält gespeicherte Technologie- oder forensische Analyseergebnisse.
14.10.2026
Sent Report Recorded
Stored outgoing record associated with registrar Hosting Concepts B.V. d/b/a Registrar.eu, 1 abuse contact
abuse@registrar.eu
23.07.2026
DestroyList veröffentlicht
23.07.2026
Monitoring Continues
Die Domäne bleibt erreichbar oder zugriffsbeschränkt; Zukünftige Überprüfungen könnten diese Beobachtung aktualisieren.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Status der öffentlichen Sperrliste

Nachweise und externe Berichte

Momentaufnahme der übermittelten Beweise
Sent: Ledger records: 1 Case ID: PD-20260723-26BF1C Recipient: abuse@registrar.eu
Page title stored with report: Rainbet | Anmelden, 400% bis zu 5000€ + 200 Freispiele
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 393.5 KB
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Eingehende Analyse

Wurden Sie von dieser Website betroffen?

6 evidence signal groups linked 1 reports recorded Letzter bekanntermaßen aktiv
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Wenn Sie Kontoanmeldeinformationen, persönliche oder Zahlungsinformationen eingegeben oder eine Datei von dieser Domain heruntergeladen haben, ergreifen Sie sofort Maßnahmen. Nachfolgend finden Sie Ressourcen, die Ihnen helfen, den Vorfall zu melden und sich zu schützen.

Europol
Finden Sie den offiziellen Meldekanal für Ihr EU-Land
National police directory
Vorsicht vor Betrügern, die mit der Rückforderung von Geldern locken! Kriminelle nehmen unter Umständen erneut Kontakt zu Opfern auf und geben dabei vor, Ermittler, Anwälte oder Beitreibungsbeamte zu sein. Zahlen Sie keine Vorabgebühren und geben Sie keine Anmeldeinformationen weiter. Erfahren Sie mehr über Betrug im Zusammenhang mit Wiederaufbaumaßnahmen →

Melden Sie sich bei Ihren örtlichen Behörden

Wählen Sie Ihr Land aus, um Offizielle Kontakte im Bereich Cyberkriminalität oder einen Beschwerdeentwurf erstellen → zu erhalten.

97-Länder-Verzeichnis

Template-based draft · optional AI wording assistance requires separate consent

KI-gestützter Entwurf – Vorfalldetails werden vom KI-Anbieter verarbeitet · Überprüfen Sie es und reichen Sie es selbst ein

Jede beliebige Domain prüfen

Bedrohungsanalyse anhand gespeicherter Blocklisten, WHOIS, DNS und öffentlicher Scan-Beweise

Jetzt scannen

Phishing melden

Melden Sie verdächtige Domains an unsere Bedrohungsdatenbank – schützen Sie die Community

Melden

Echtzeit-Bedrohungsfeed

Aktuelle Phishing-Meldungen und beobachtete Verfügbarkeitsänderungen

Überwachen

Bleiben Sie auf dem Laufenden, bleiben Sie sicher

Beobachten Sie aktuelle Bedrohungen oder legen Sie Widerspruch gegen diesen Eintrag ein, wenn Sie der Meinung sind, dass es sich um einen Fehlalarm handelt

Echtzeit-Bedrohungsfeed Einspruch gegen diesen Eintrag einlegen
HTML · IFRAME

Diesen Bericht einbetten

Teilen Sie diese Bedrohungsinformationen auf Ihrer Website oder in Ihrem Blog

embed.html
<iframe
  src="https://phishdestroy.io/de/embed/domain/rain-bet.casino"
  title="PhishDestroy threat report for rain-bet.casino"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>