VirusTotal
17 / 91
Melden


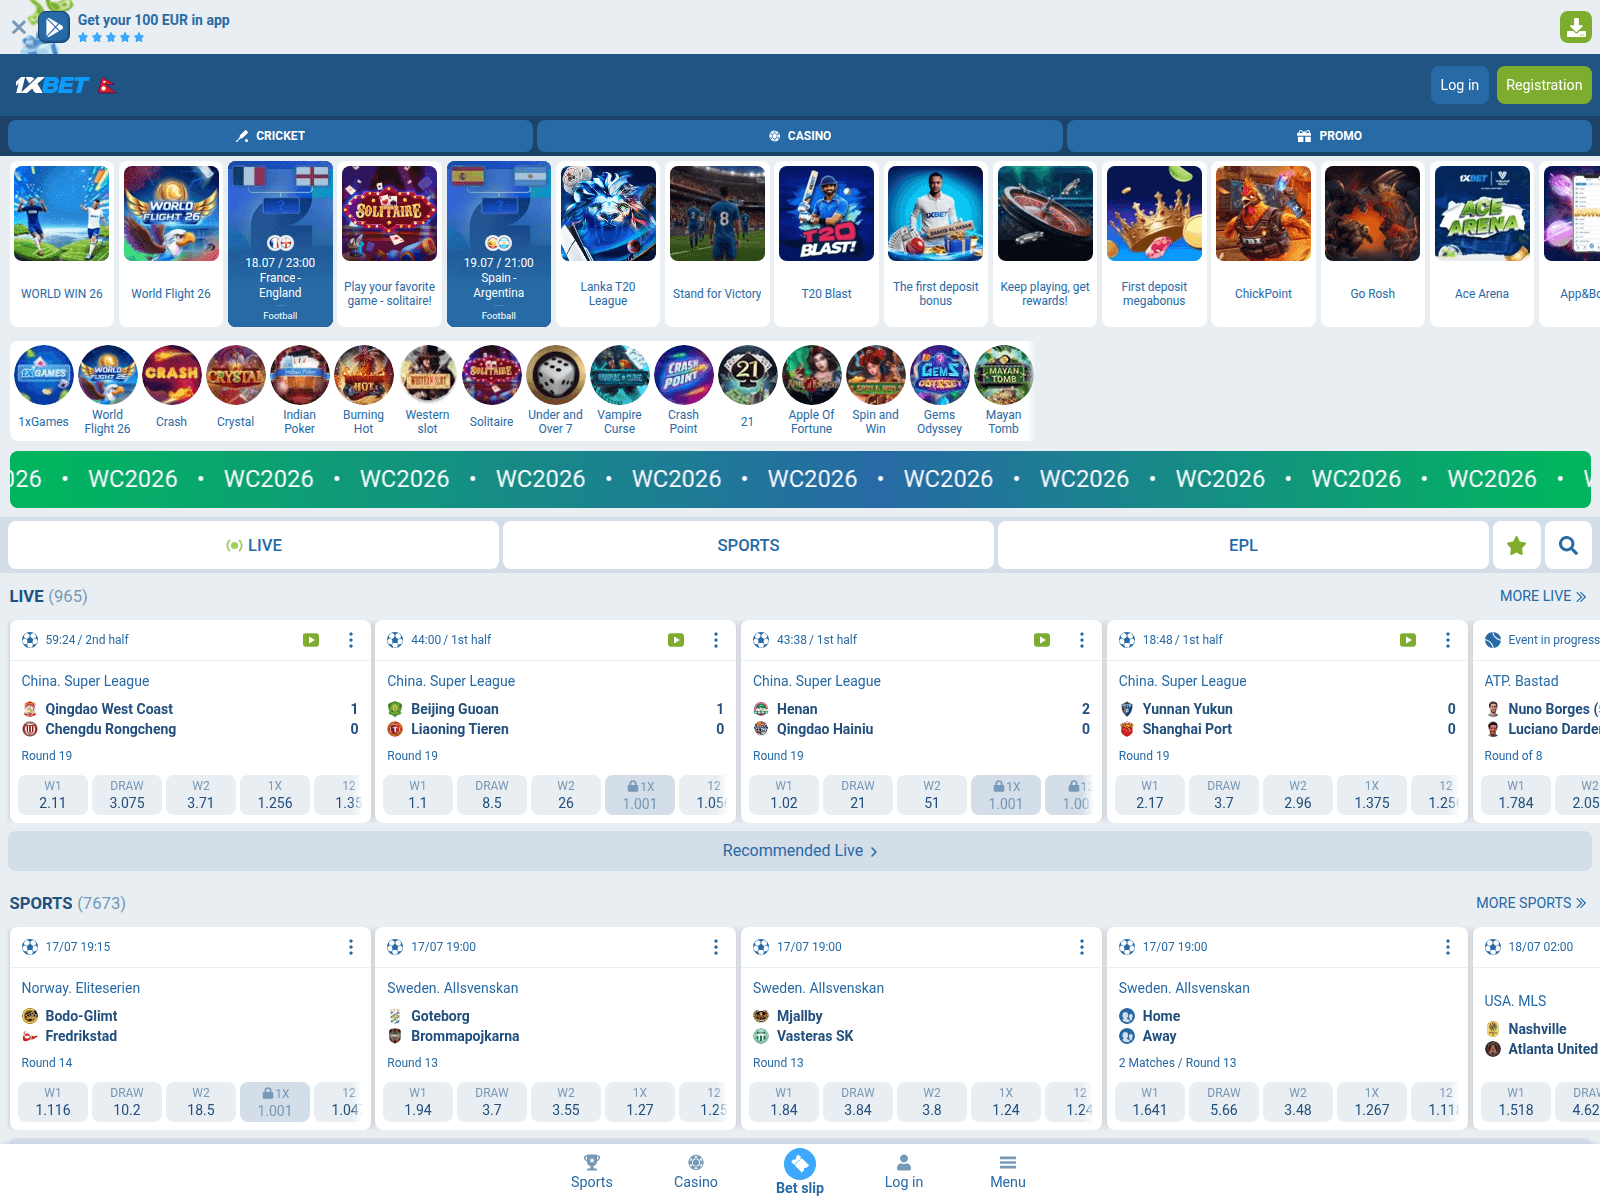
“1xBet Nepal - Online Sports Betting & Casino Site ᐉ nepal1xbet.com”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@safenames.net.
The latest stored availability evidence still shows the domain reachable; 2 months has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
nepal1xbet.com — Letzter bekanntermaßen aktiv (HTTP 301). Betrugstyp: Gambling. Zusammenfassung der Beweislage: VirusTotal 17/91 (alphaMountain.ai, BitDefender, Chong Lua Dao, CyRadar, ESET); URLQuery 5 alerts; PhishDestroy score 100/100. Registrar: SafeNames.
Die ausführliche Analyse von PhishDestroy AI bleibt auf Englisch, damit der ursprüngliche forensische Bericht unverändert bleibt.

17 / 91
5 threat-system alerts
Melden4 community references
Meldengespeicherter Bericht
 Melden
Analyse abgeschlossen
MeldenReport stored; verdict not recorded
MeldenChecked; no threat flag recorded
Melden| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | nepal1xbet.com |
malicious | Sinkholed |
| OpenDNS | nepal1xbet.com |
phishing | Phishing Block |
| Hagezi Threat Feed | nepal1xbet.com |
malicious | Sinkholed |
| DigiCert UltraDNS | nepal1xbet.com |
malicious | Sinkholed |
| DNS4EU | nepal1xbet.com |
malicious | Sinkholed |
This domain, nepal1xbet.com, is actively flagged as a high-risk phishing infrastructure targeting users with fraudulent online gambling services, specifically crypto gambling. Registered on June 12, 2026, through SafeNames Ltd., the domain resolves to IP address 185.174.42.117, hosted by Silverhill Group Holding LTD in Seychelles. Infrastructure analysis reveals the use of CloudNS nameservers (dns51.cloudns.net, dns52.cloudns.net, dns53.cloudns.net, dns54.cloudns.net) and a Let's Encrypt SSL certificate issued under the identifier YE1, which does not inherently indicate malicious activity but is commonly exploited in phishing operations. The domain is currently active, returning an HTTP 302 redirect status, which is often leveraged in phishing campaigns to obscure the final destination or evade detection.
The page title, '1xBet Nepal - Online Sports Betting & Casino Site,' explicitly aligns with the reported scam type of crypto gambling, suggesting an attempt to impersonate or mimic legitimate betting platforms. While the exact content and functionality of the site remain unanalyzed, the combination of the page title, scam classification, and infrastructure details supports the assessment of a targeted phishing operation. Defenders should note that nepal1xbet.com appears on at least one security blocklist and has been included in two AlienVault OTX threat intelligence pulses, indicating prior detection by the security community. Twelve of ninety-one security vendors on VirusTotal flag the domain as malicious, though the absence of detections from other vendors does not imply safety.
The registrar, SafeNames Ltd., is not known for hosting a disproportionate volume of malicious domains, but this does not mitigate the risk posed by the domain itself. Recommended actions include blocking the domain and its associated IP (185.174.42.117) at the network level, monitoring for connections to the CloudNS nameservers, and alerting users to the presence of this threat.
Gespeicherte Beobachtungen zum Vergleich zwischen Crawler und Browser für diesen Host sowie eine Echtzeit-Fingerabdruckprüfung für Verkehrsverteilungssysteme im Keitaro-Stil.
AngieAnmerkung des Scanners: redirect: raw=redirect_301; http=301; via=https_proxy; location=https://nepali.1xbet.com/; server=Angie
dns51.cloudns.netdns52.cloudns.netdns53.cloudns.netdns54.cloudns.netLocation describes the IP network.
d9c42c16bf054d56305cdcda73f3b7043a61278e46fd7526d0d8759684d5ff86Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20260717-EFA5D7 Recipient: abuse@safenames.net Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Wenn Sie Kontoanmeldeinformationen, persönliche oder Zahlungsinformationen eingegeben oder eine Datei von dieser Domain heruntergeladen haben, ergreifen Sie sofort Maßnahmen. Nachfolgend finden Sie Ressourcen, die Ihnen helfen, den Vorfall zu melden und sich zu schützen.


Wählen Sie Ihr Land aus, um Offizielle Kontakte im Bereich Cyberkriminalität oder einen Beschwerdeentwurf erstellen → zu erhalten.
Template-based draft · optional AI wording assistance requires separate consent
Jede Spalte gibt einen Grund an, warum eine Domain mit diesem Host verknüpft ist. Knoten in voller Größe kennzeichnen „VirusTotal“-Erkennungen, gestrichelte Knoten sind bereits offline. Die vollständigen Listen folgen weiter unten.
Teil der Phishing-Kampagne „Unknown“. Alle Kampagnen-Domains anzeigen →
Über denselben Registrar registriert. Ein Registrar betreut Millionen von Kunden, die in keiner Verbindung zueinander stehen; daher werden hier lediglich Berichte zusammengefasst, anstatt eine Verbindung nachzuweisen.
Kürzlich hinzugefügte Berichte aus der PhishDestroy-Datenbank. Diese Discovery-Links implizieren keine gemeinsame Nutzung der Infrastruktur oder des Eigentums.
Bedrohungsanalyse anhand gespeicherter Blocklisten, WHOIS, DNS und öffentlicher Scan-Beweise
Jetzt scannenMelden Sie verdächtige Domains an unsere Bedrohungsdatenbank – schützen Sie die Community
MeldenAktuelle Phishing-Meldungen und beobachtete Verfügbarkeitsänderungen
ÜberwachenBeobachten Sie aktuelle Bedrohungen oder legen Sie Widerspruch gegen diesen Eintrag ein, wenn Sie der Meinung sind, dass es sich um einen Fehlalarm handelt