VirusTotal
6 / 91 engine detections
Bericht öffnen

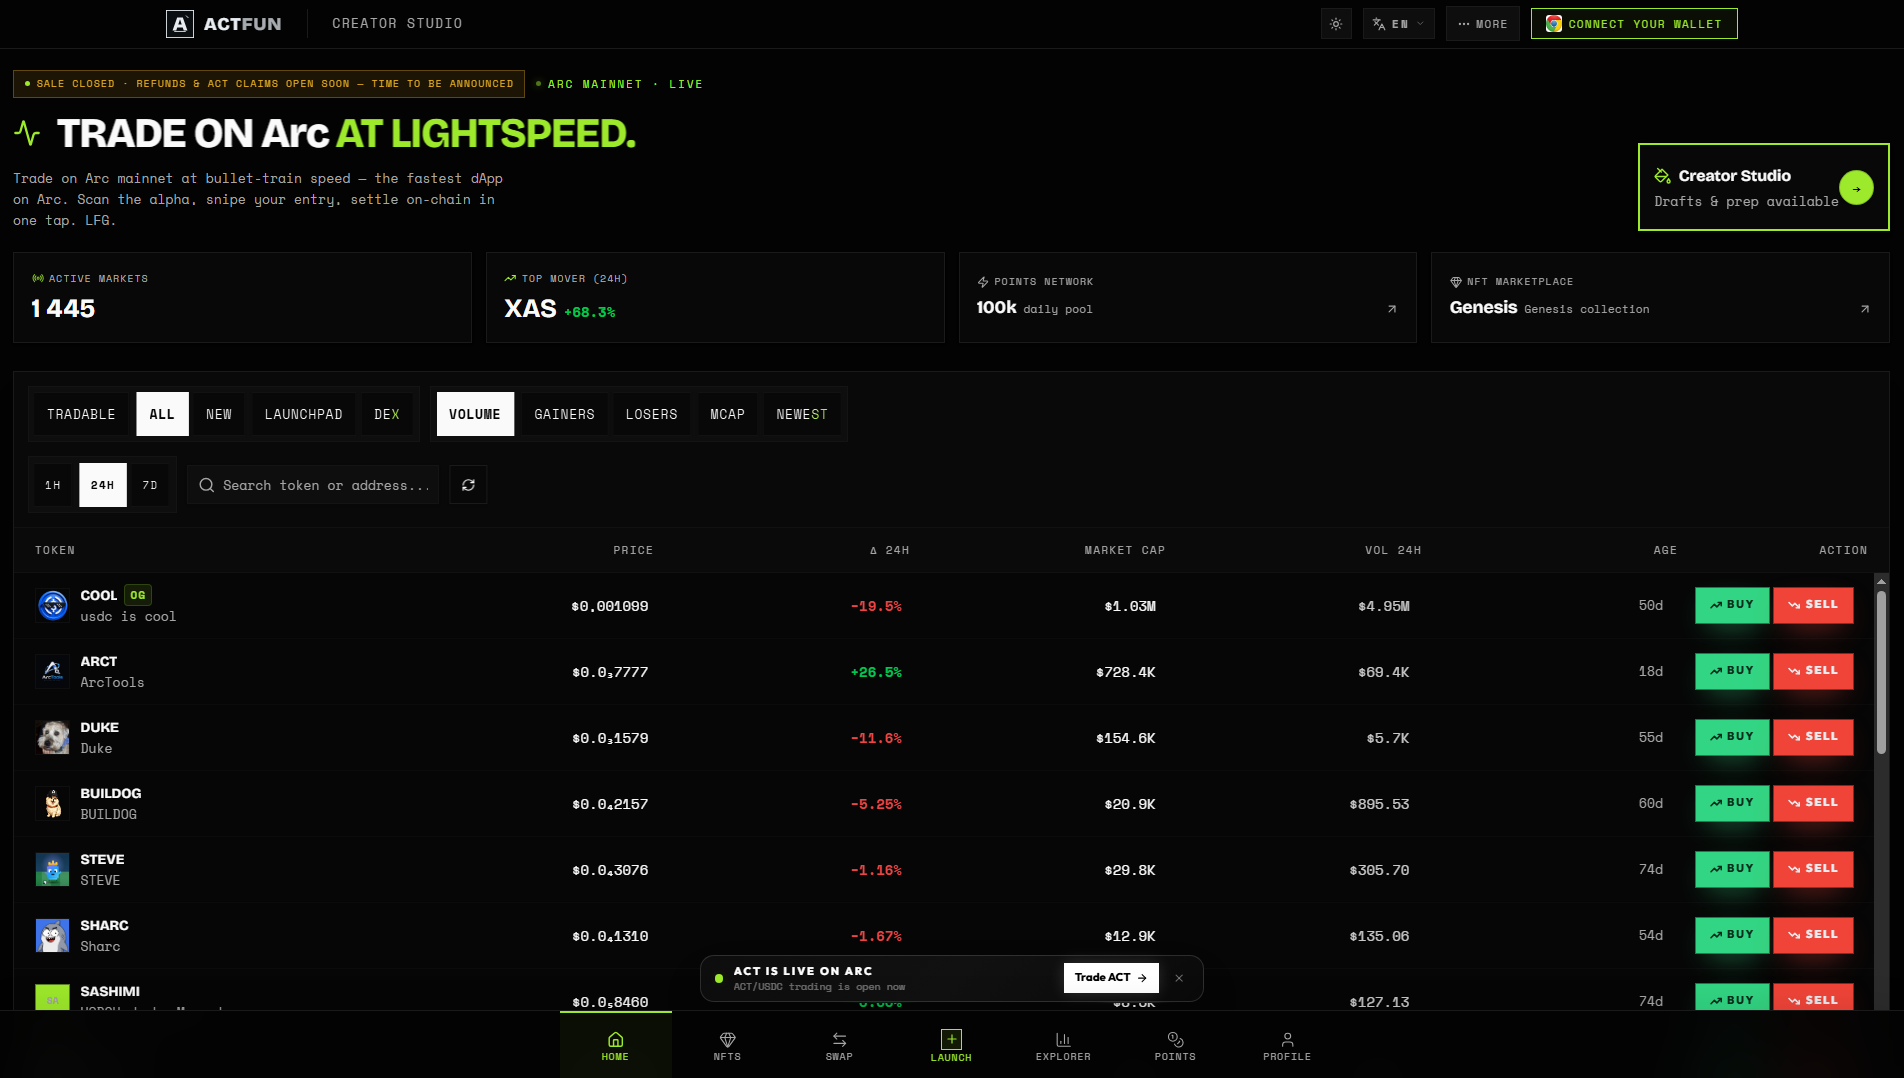
“ACTFUN — Arc Mainnet Token Launchpad”
Phishing: actfun.pro — Inhalt nicht verfügbar. Zusammenfassung der Beweislage: VirusTotal 6/91 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft…
Die ausführliche Analyse von PhishDestroy AI bleibt auf Englisch, damit der ursprüngliche forensische Bericht unverändert bleibt.
6 / 91 engine detections
Bericht öffnenScan report
Bericht öffnen4 community references
Bericht öffnenprovider verdict: clean
Bericht öffnenNo threat flag
Bericht öffnenNo malicious flag
Bericht öffnenResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
actfun.pro presented itself as "ACTFUN — Arc Mainnet Token Launchpad", borrowing the name of a token launch platform to attract people hunting for new tokens on Arc Mainnet. PhishDestroy classifies it as impersonation phishing and first flagged it on 2026-09-28. The site went offline on 2026-10-14 and was still dead when last checked on 2026-10-19.
Fake launchpads exploit the urgency of new token sales. Visitors are told a presale or launch is live and are pushed to connect a wallet and act quickly before they can check that the site is genuine. Because the page copies the ACTFUN branding, a victim believes they are using the real platform. What they actually do is sign transactions, approve token spending or send funds to the operator. A wallet connection or signed approval made on such a page can hand over control of assets, and funds sent for a supposed token purchase are not returned.
Six of 91 VirusTotal engines flagged the domain as of 2026-10-06: alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar and VIPRE. That is a modest share, but six unrelated vendors reaching the same verdict on a brand-new domain is meaningful. The domain also appears in four AlienVault OTX threat pulses, so other researchers were tracking it too, and it is listed on the PhishDestroy blocklist.
The domain was registered through Spaceship, Inc. on 2026-08-09, about seven weeks before PhishDestroy detected it. That gap leaves room for setup and early promotion before the site drew attention. It was hosted on Google LLC cloud infrastructure in the US and used a free Let's Encrypt certificate, so the padlock in the browser said nothing about whether the site was legitimate.
If you connected a wallet to actfun.pro, use a token approval checker to review and revoke any permissions you granted, then move remaining assets to a fresh wallet if you signed anything you did not fully understand. Never share a seed phrase with any launchpad. If you entered one, treat the wallet as compromised and empty it immediately. Before joining a token launch, reach the platform only through its official channels. Security teams should block the domain, search logs for past connections to it, and warn users that a fake ACTFUN launchpad has been circulating.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
0x07704b06981ea962b87296362a1281484d160000Format validated · Domain analysis0x0bffa97f774824e9da843699aedd2835cb1b8022Format validated · Domain analysis0x0c25c9b332d009460ef5d136c3f7988e3cc38b17Format validated · Domain analysis0x0c86ecc7e51998ec611d73fcc041c75c050c6d0fFormat validated · Domain analysis0x1061d7f4934542b654e2a4ef7f04f101b4e8018dFormat validated · Domain analysis0x171a4217b86a807a64eb94757db6849fb4bdbaa0Format validated · Domain analysis0x177b47be2782575284211A000EDA4112807288a5Format validated · Domain analysis0x178b01f61cbea1d2a5581fe1621be607835ec349Format validated · Domain analysis0x1dade69aae616954097747d8e5d218c15c97094cFormat validated · Domain analysis0x1ea1e4f9a9975f1f6e9c0a9f6e8ada7a66e6de52Format validated · Domain analysis0x2164bb17a2d38c1b5170e987b2c0416df1efc752Format validated · Domain analysis0x2ba0f44bdfc17fba30eda9cdbecb908ca45b043bFormat validated · Domain analysis0x38d5bd4737fc40cd4dfd5454c665024ed600c854Format validated · Domain analysis0x3aa37775d9884d42d047c67f6139c4f66c235837Format validated · Domain analysis0x3bad685877990b0cae918f7208da28018fbf3a41Format validated · Domain analysis0x3ead4e80e9e5bc0e01682d7ee74c4881b040d3eaFormat validated · Domain analysis0x4cb8382b9daf7992d3b27d32f7db650c57881daaFormat validated · Domain analysis0x4f7dc89dc44ad08c20d9680d2ee9cfad69bfda55Format validated · Domain analysis0x563eae55f5341a2f08989e5b674ddcfadaccb3d8Format validated · Domain analysis0x5d135c0ed9dec249ff0fdb831c4be1588138d11fFormat validated · Domain analysishttps://t.me/arctrenchesStored page referenceIoC extraction recorded 2026-09-29 04:00:10 UTC
launch1.spaceship.netlaunch2.spaceship.netmx1.spacemail.compriority 0mx2.spacemail.compriority 0Location describes the IP network.
4574cebe39b0bc86ed4c743b5576a459d3fba219496ca5240eb26eeeb8e5b581Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Hostnames retained in the domain record or Certificate Transparency cache. A hostname alone does not establish current availability or malicious activity.
www.actfun.proDomain recordThe original observation time is not recorded for these hostnames.
Google PageSpeed Insights — mobile performance audit of actfun.pro · checked Sep 28, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Erreichbar→Nicht verfügbar
3→4
2→3
0→2
Erreichbar
No threat flag
View source6/91 engine detections
View source4 community references
View sourcePD-20260928-88C60B
actfun.pro
View sourcePage captured
View sourceJede Spalte gibt einen Grund an, warum eine Domain mit diesem Host verknüpft ist. Knoten in voller Größe kennzeichnen „VirusTotal“-Erkennungen, gestrichelte Knoten sind bereits offline. Die vollständigen Listen folgen weiter unten.
Diese Ursprungs-IP hostet mehrere Phishing-Domänen – die Infrastruktur kann kampagnenübergreifend gemeinsam genutzt werden.
Über denselben Registrar registriert. Ein Registrar betreut Millionen von Kunden, die in keiner Verbindung zueinander stehen; daher werden hier lediglich Berichte zusammengefasst, anstatt eine Verbindung nachzuweisen.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
actfun.pro
PD-20260928-88C60B Recipient: abuse@spaceship.com Wenn Sie Kontoanmeldeinformationen, persönliche oder Zahlungsinformationen eingegeben oder eine Datei von dieser Domain heruntergeladen haben, ergreifen Sie sofort Maßnahmen. Nachfolgend finden Sie Ressourcen, die Ihnen helfen, den Vorfall zu melden und sich zu schützen.


Wählen Sie Ihr Land aus, um Offizielle Kontakte im Bereich Cyberkriminalität oder einen Beschwerdeentwurf erstellen → zu erhalten.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
actfun.pro)Auch wenn dir nicht alle Details bekannt sind — trotzdem Anzeige erstatten. Auch unvollständige Informationen sind für die Ermittlungen hilfreich.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Bedrohungsanalyse anhand gespeicherter Blocklisten, WHOIS, DNS und öffentlicher Scan-Beweise
Jetzt scannenMelden Sie verdächtige Domains an unsere Bedrohungsdatenbank – schützen Sie die Community
MeldenAktuelle Phishing-Meldungen und beobachtete Verfügbarkeitsänderungen
ÜberwachenBeobachten Sie aktuelle Bedrohungen oder legen Sie Widerspruch gegen diesen Eintrag ein, wenn Sie der Meinung sind, dass es sich um einen Fehlalarm handelt
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.