
Durchsuchen Sie die erfassten Domains und überprüfen Sie gespeicherte Beweismittel, Erkennungen sowie die aktuell beobachtete Verfügbarkeit.
221,205
Gesamtzahl der erfassten Fälle
215,392
VT erkannt
86,827
Zuletzt aktiv gesehen
134,378
Bei der letzten Überprüfung nicht verfügbar
0
VT Ausstehend

How This Attack Works
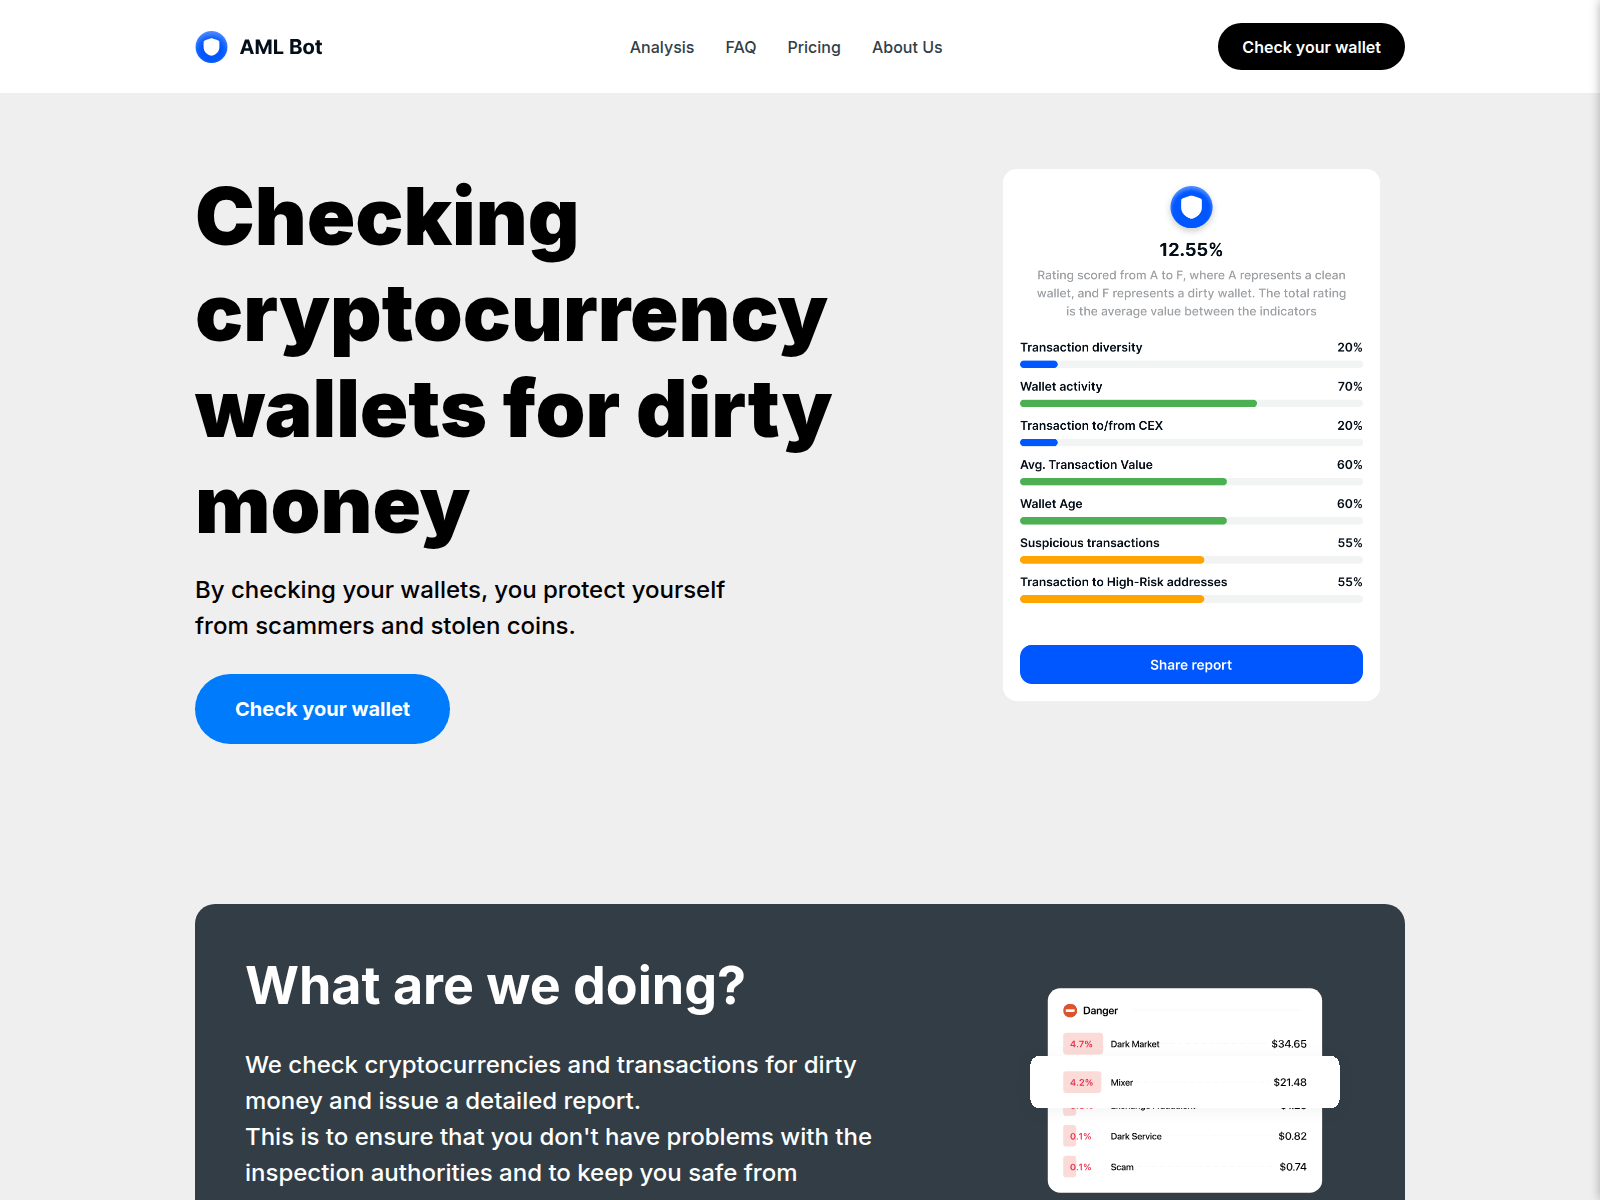
The scam exploits growing awareness of AML/KYC compliance requirements in crypto. Users who want to verify their funds are "clean" land on a convincing clone and unknowingly authorize a wallet drainer.
STEP 1
Lure via Search & Social
Victims encounter fake AML check sites through Google Ads, Telegram DMs, social media posts, or SEO-poisoned search results for queries like "check wallet AML" or "is my crypto clean."
STEP 2
Clone Legitimate UI
The site closely mimics the official AMLBot.com design, branding, and interface. Some clones replicate staff profiles and create fake Telegram accounts impersonating AMLBot team members.
STEP 3
Request Wallet Connection
Unlike the real AMLBot (which only needs a wallet address as text input), the fake site asks users to "connect wallet" via MetaMask or WalletConnect to "generate an AML report."
STEP 4
Drain Assets via Smart Contract
The wallet connection triggers a malicious smart contract (setApprovalForAll or token approval) that scans all tokens/NFTs, prioritizes highest-value assets, and drains everything to attacker-controlled wallets. Transactions are irreversible.
Technical Analysis
The AML scam ecosystem uses sophisticated infrastructure. Domains typically use .com, .org, .app TLDs registered through privacy-friendly registrars (NICENIC, WEBCC account for 163+ domains). Many use Cloudflare CDN for legitimacy.
The drainer mechanism is identical to other wallet-connect phishing: upon connection, the site calls setApprovalForAll() or increaseAllowance() on the victim's token contracts. The drainer scans all assets, estimates value, and prioritizes extraction of highest-value tokens first.
According to AMLBot's 2025 Crypto Crime Bericht, 65% of crypto incidents are driven by social engineering rather than technical exploits, with phishing ranking as the #2 attack type (18% of all incidents).
Key technical indicators: domains containing 'aml', 'amlbot', 'aml-check', 'aml-verify' in the URL; wallet connection prompts (the real AMLBot never requires this); recently registered domains; missing or fake SSL certificates.
Real Cases
AMLBot Clone Wave (2024-2026) (2024-2026)
1,350+ fake domains stolen
AMLBot officially warned about an alarming rise in scammers impersonating AMLBot on various platforms, including fake Telegram bots and clone websites.
amlcheckwallet.cc Drainer (2024)
Wallet drainer active stolen
Registered via Dynadot Inc, resolved to Cloudflare IP 104.21.25.10. Served a fake "AML wallet check" interface with wallet-connect drainer. PhishDestroy report.
PCRisk AML Warning (Jan 2026) (January 2026)
12+ documented domains stolen
PCRisk documented a new wave of fake AMLBot sites including amlbotchecks.com, aml-safety.app, amlrobotsaveru.com, amlpremium.top. FTC reports over 46,000 people lost $1 billion to crypto scams since 2021. PCRisk report.
amlbotchecking.com Campaign (2024)
Multiple victims stolen
Typosquat of AMLBot serving crypto drainer via fake compliance check UI. Documented by Malware Guide and PCRisk.
How to Detect
Site asks to "connect wallet" — the real AMLBot only needs a wallet ADDRESS as text input, never a wallet connection
Domäne contains "aml" variations: amlbot, aml-check, aml-verify, amlcrypto (verify against official amlbot.com)
Recently registered domain (check WHOIS — legitimate AML services have years of history)
Dringend messaging: "Your wallet may be flagged" or "Überprüfen compliance before funds are frozen"
Promoted via Telegram DMs, Google Ads, or unsolicited emails instead of organic search
How to Protect Yourself
1
Bookmark the official AMLBot at amlbot.com — never click links from ads, DMs, or emails
2
Remember: legitimate AML tools only need a wallet address (text), never a wallet connection or private keys
3
Überprüfen any AML domain on PhishDestroy before interacting with it
4
Use a separate "burner" wallet with minimal funds when testing any new DeFi/Web3 service
5
If you connected your wallet to a suspicious site: immediately transfer remaining funds to a NEW wallet and revoke approvals at revoke.cash
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 2,113 domains tracked for this threat type
Fake AML Überprüfen Scam 2,113 domains


Pipeline zur Reaktion auf Sicherheitsbedrohungen
Wie jede Domain in diesem Hub überprüft wird und wie bestätigte Bedrohungen entschärft werden. Vollständige Visualisierung der Pipeline →
Überprüfung der Bedrohungsinformationen— Jede Domäne wird gescannt und anhand folgender Kriterien überprüft:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency BerichtCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Sicherheit FiltersQuad9 · AdGuard · CleanBrowsingWeb-ÜberprüfenFull surface scan
 crt.sh
Globale Anbietersynchronisierung— Bestätigte Nachweise werden an 29 Partner weitergeleitet:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecSiteReviewAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftAbschaltung APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.BerichtHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust