
Durchsuchen Sie die erfassten Domains und überprüfen Sie gespeicherte Beweismittel, Erkennungen sowie die aktuell beobachtete Verfügbarkeit.
221,199
Gesamtzahl der erfassten Fälle
215,387
VT erkannt
93,451
Zuletzt aktiv gesehen
127,748
Bei der letzten Überprüfung nicht verfügbar
0
VT Ausstehend
How This Attack Works
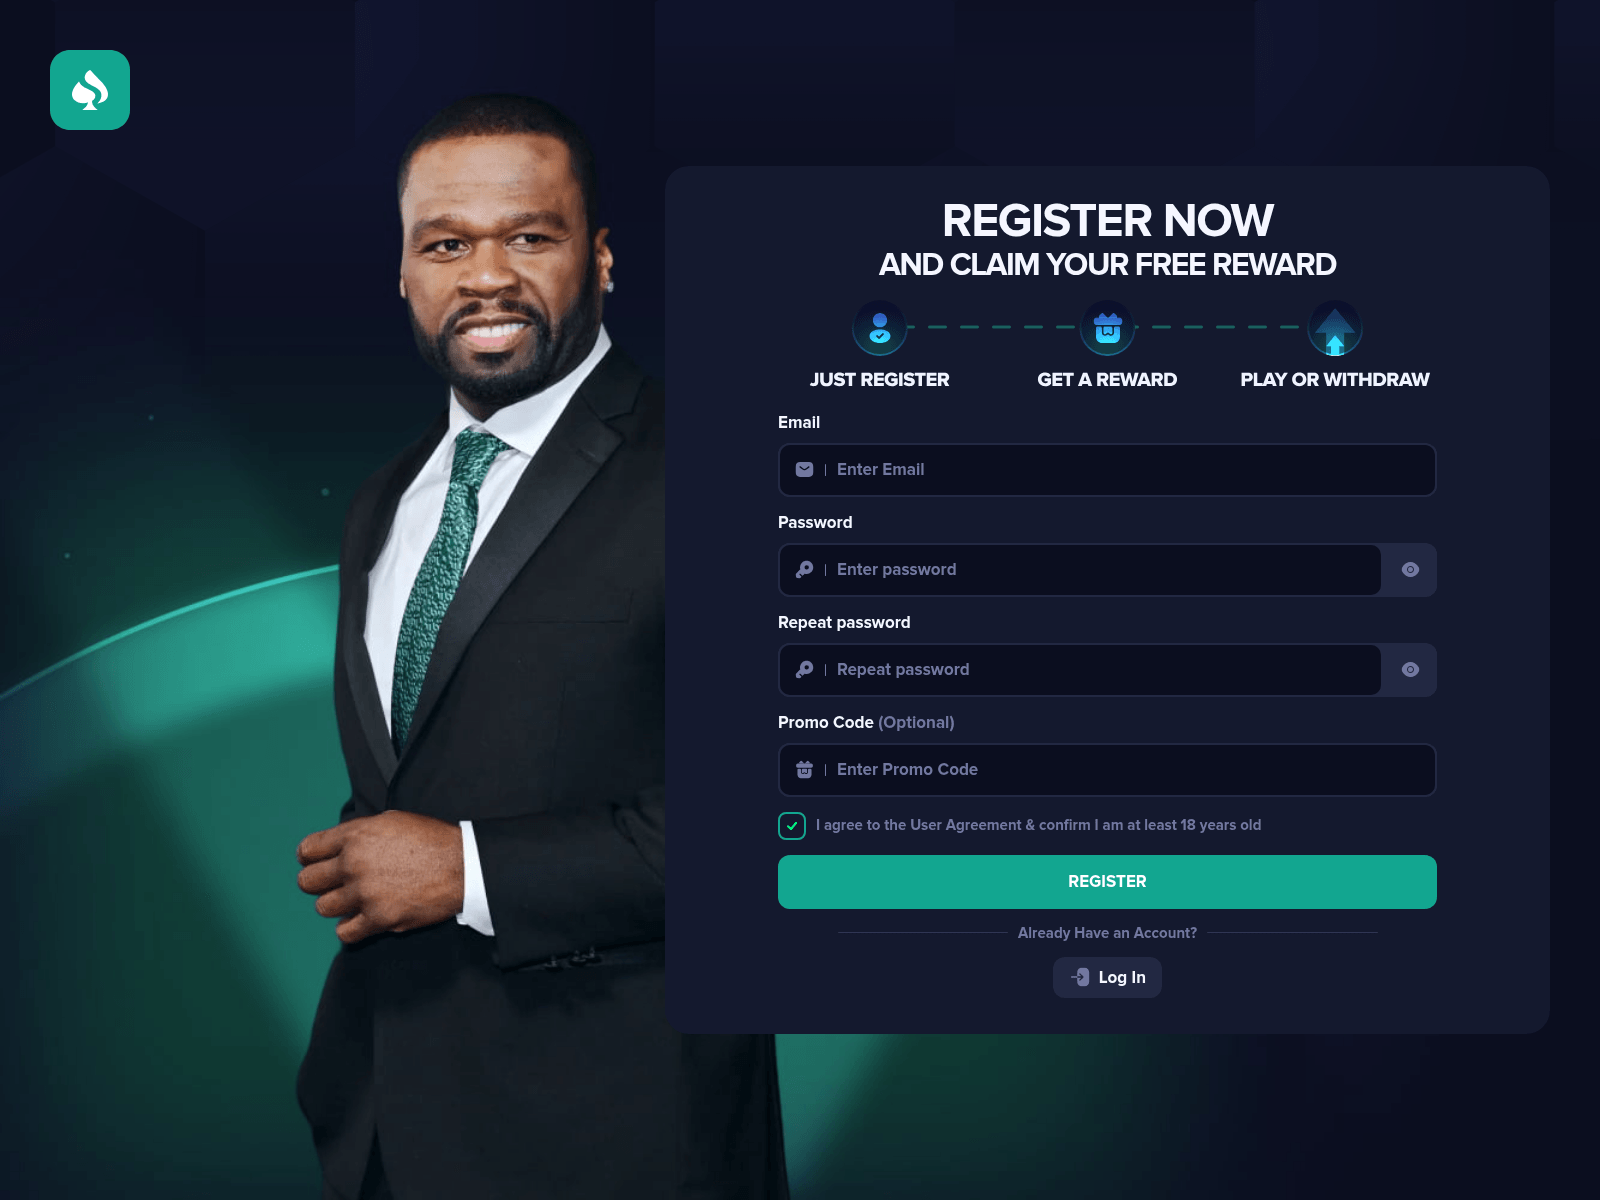
Gambler Scam Panels exploit the allure of gambling to deceive users and extract financial information. Here's a breakdown of how these scams typically unfold:
STEP 1
Enticing Offer
Scammers create convincing gambling websites offering attractive bonuses or winnings.
STEP 2
User Engagement
Victims are drawn in by the promise of easy money and create accounts on these fraudulent platforms.
STEP 3
Data Collection
Scammers collect sensitive personal and financial data under the guise of account verification.
STEP 4
Financial Exploitation
Collected data is used for unauthorized transactions, leading to financial loss for the victim.
Technical Analysis
Gambler Scam Panels often utilize spoofed gambling websites that mimic legitimate platforms. Attackers use phishing kits to create replicas of popular gambling sites, embedding malicious scripts that capture user data. These sites are hosted on domains registered with less-regulated registrars like NICENIC INTERNATIONAL GROUP CO., LIMITED, WEBCC, and Dominet (HK) Limited. Additionally, they may leverage obfuscated JavaScript to hide malicious activities from casual inspection. In some cases, these scams involve fake cryptocurrency gambling, where smart contracts are manipulated to always favor the scammer, utilizing functions that are poorly documented and hard to audit.
Real Cases
SpinWin Scam (2024)
$2 million stolen
Users were lured by promises of high returns on a fake cryptocurrency gambling site, resulting in significant financial losses.
QuickBet Fraud (2023)
$1.5 million stolen
This scam used a well-designed imitation of a major gambling platform to collect user data and funds.
LuckyStrike Hoax (2024)
$3 million stolen
A fake lottery site that promised huge winnings but instead harvested sensitive financial information from users.
How to Detect
Unusually high bonuses or winnings promised
Poor website design with multiple typos
Unsecured website (missing HTTPS)
Unusually urgent demands for personal information
Domäne registered recently with a non-reputable registrar
How to Protect Yourself
1
Verify the legitimacy of gambling sites before using them
2
Use secure passwords and two-factor authentication
3
Be wary of sites with unsecured connections
4
Regularly monitor financial statements for unauthorized transactions
5
Bericht suspicious sites to authorities and platforms like PhishDestroy
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 10,180 domains tracked for this threat type
Gambler Scam Panel 10,180 domains

topcasinoslots.sbs

topgamb.live

torycasino.com

tr.galabetcasino.vip

trcas.us

trionex.cc

trumproll.net

tuzowex.com
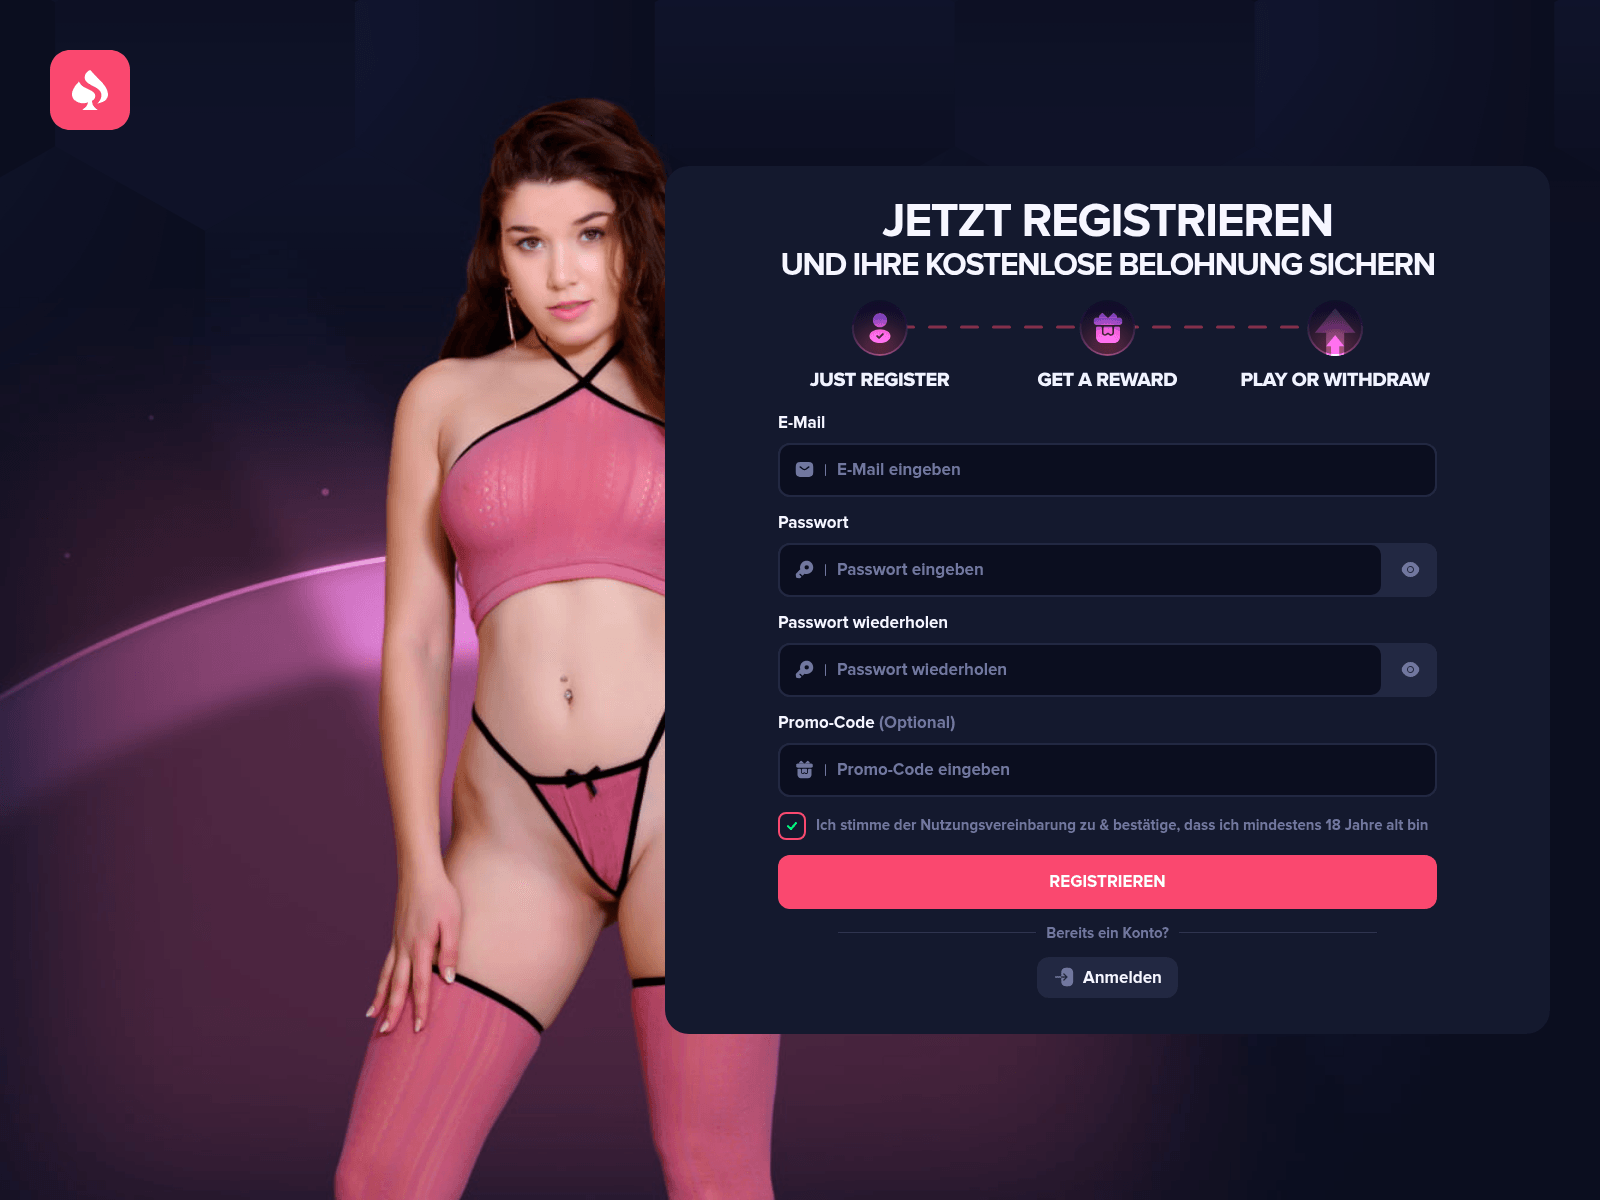
tyraxa.com

ufcslots.net
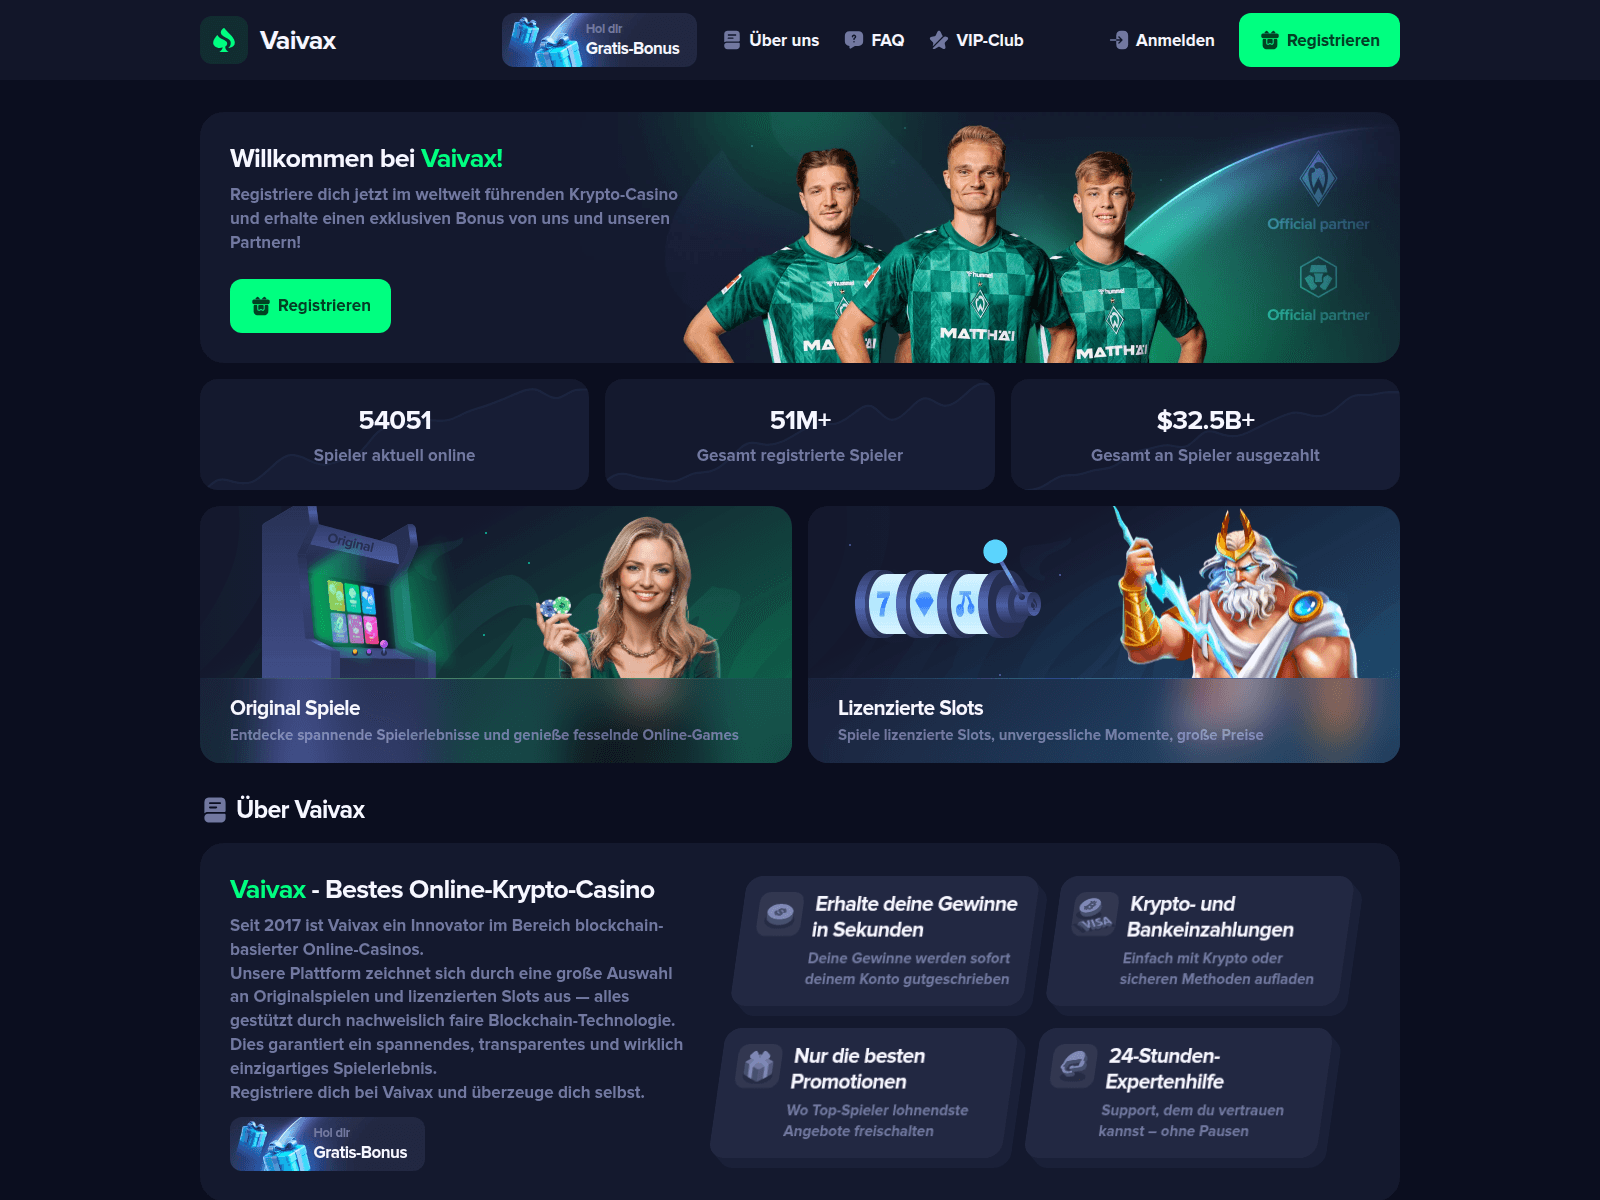
vaivax.com

vaiwax.com

vaorax.com

vaorex.com

varonox.com

vegamb.cc

vegasdiamond.bet
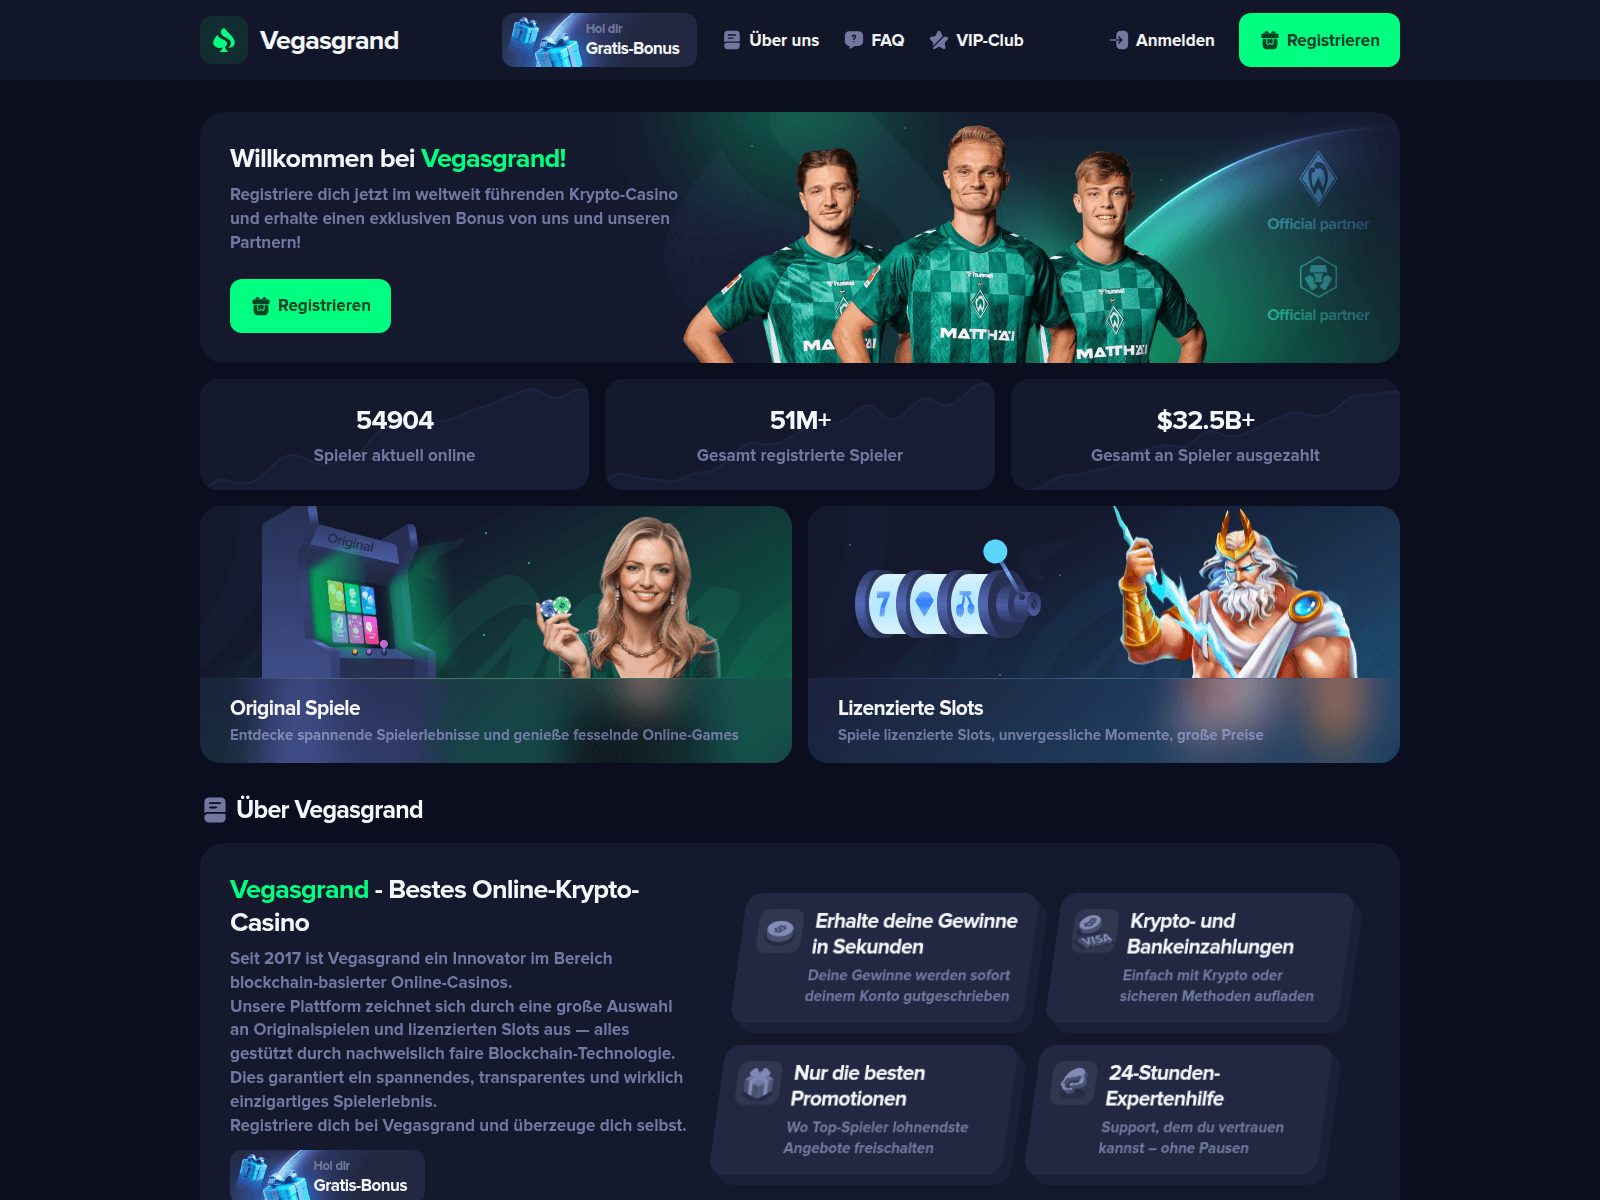
vegasgrand.casino

veirex.com

velarplay.com
veloxowin.com

vemcas.com
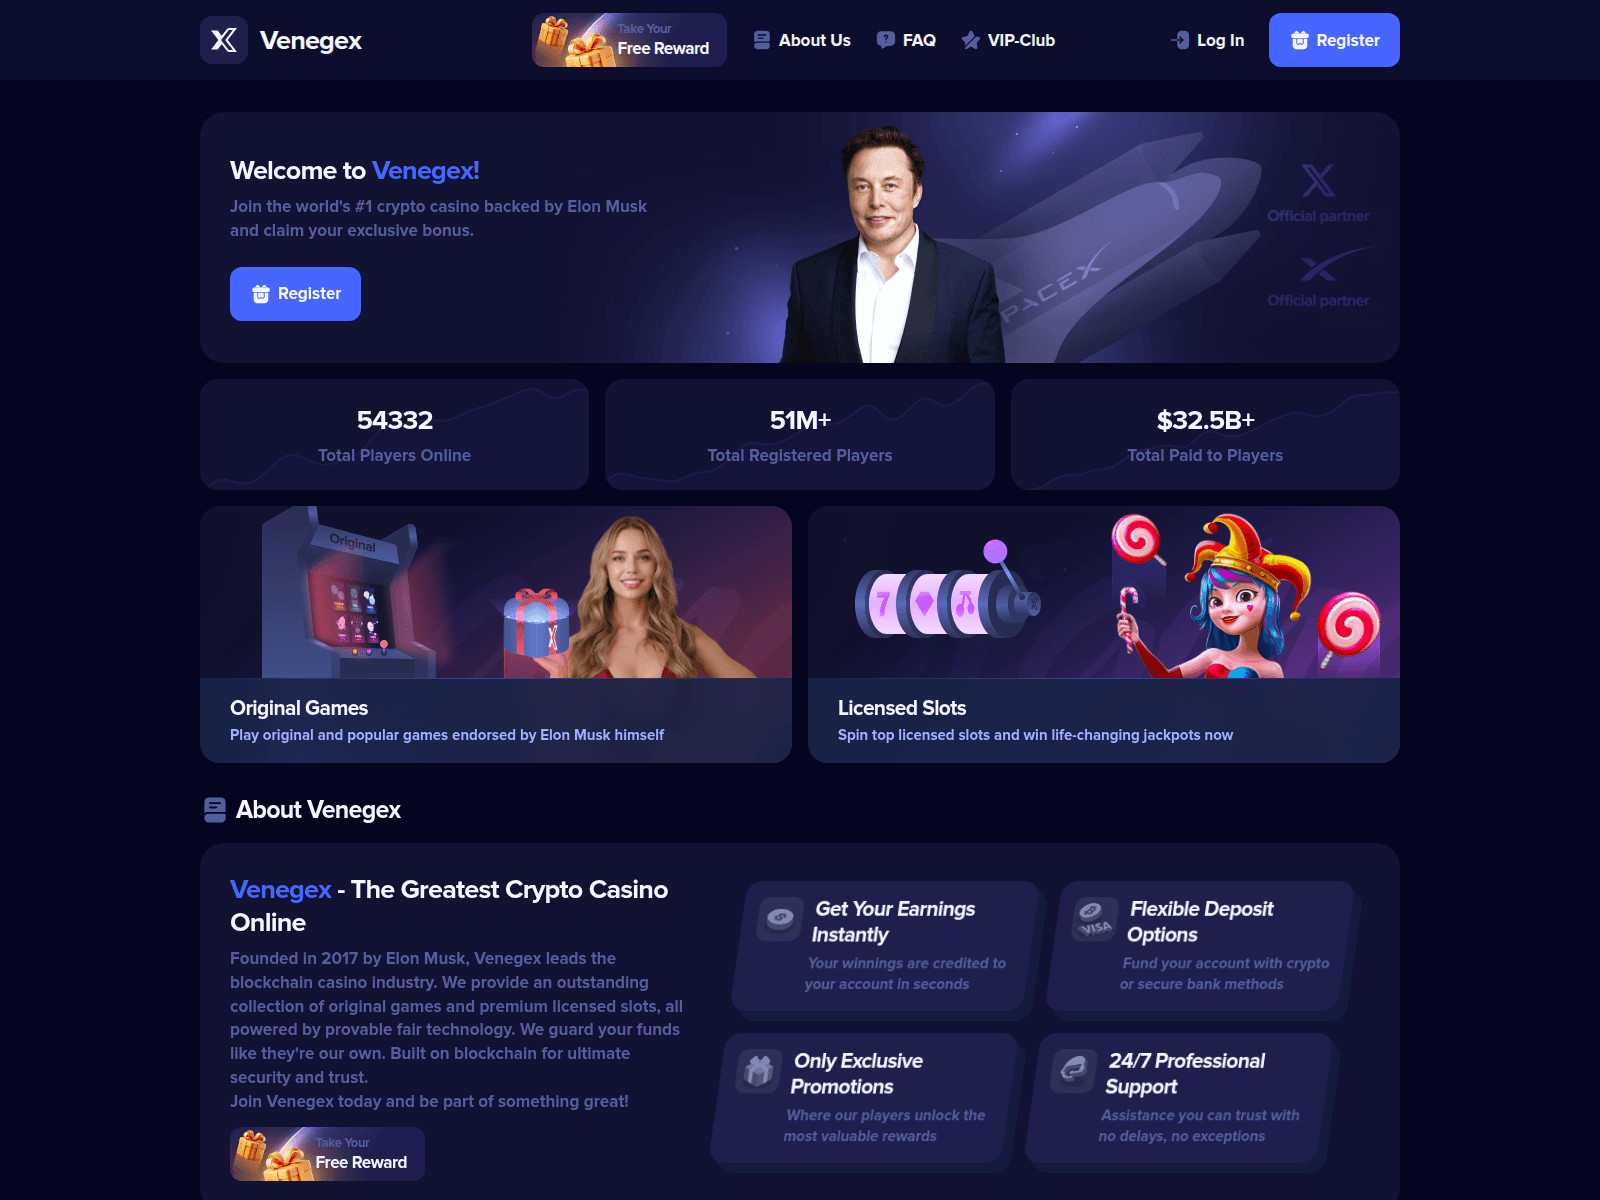
venegex.com

verstap.com

vinewin.com

vip.kaecex.com

vireonroll.com

vitewin.com

voavax.com
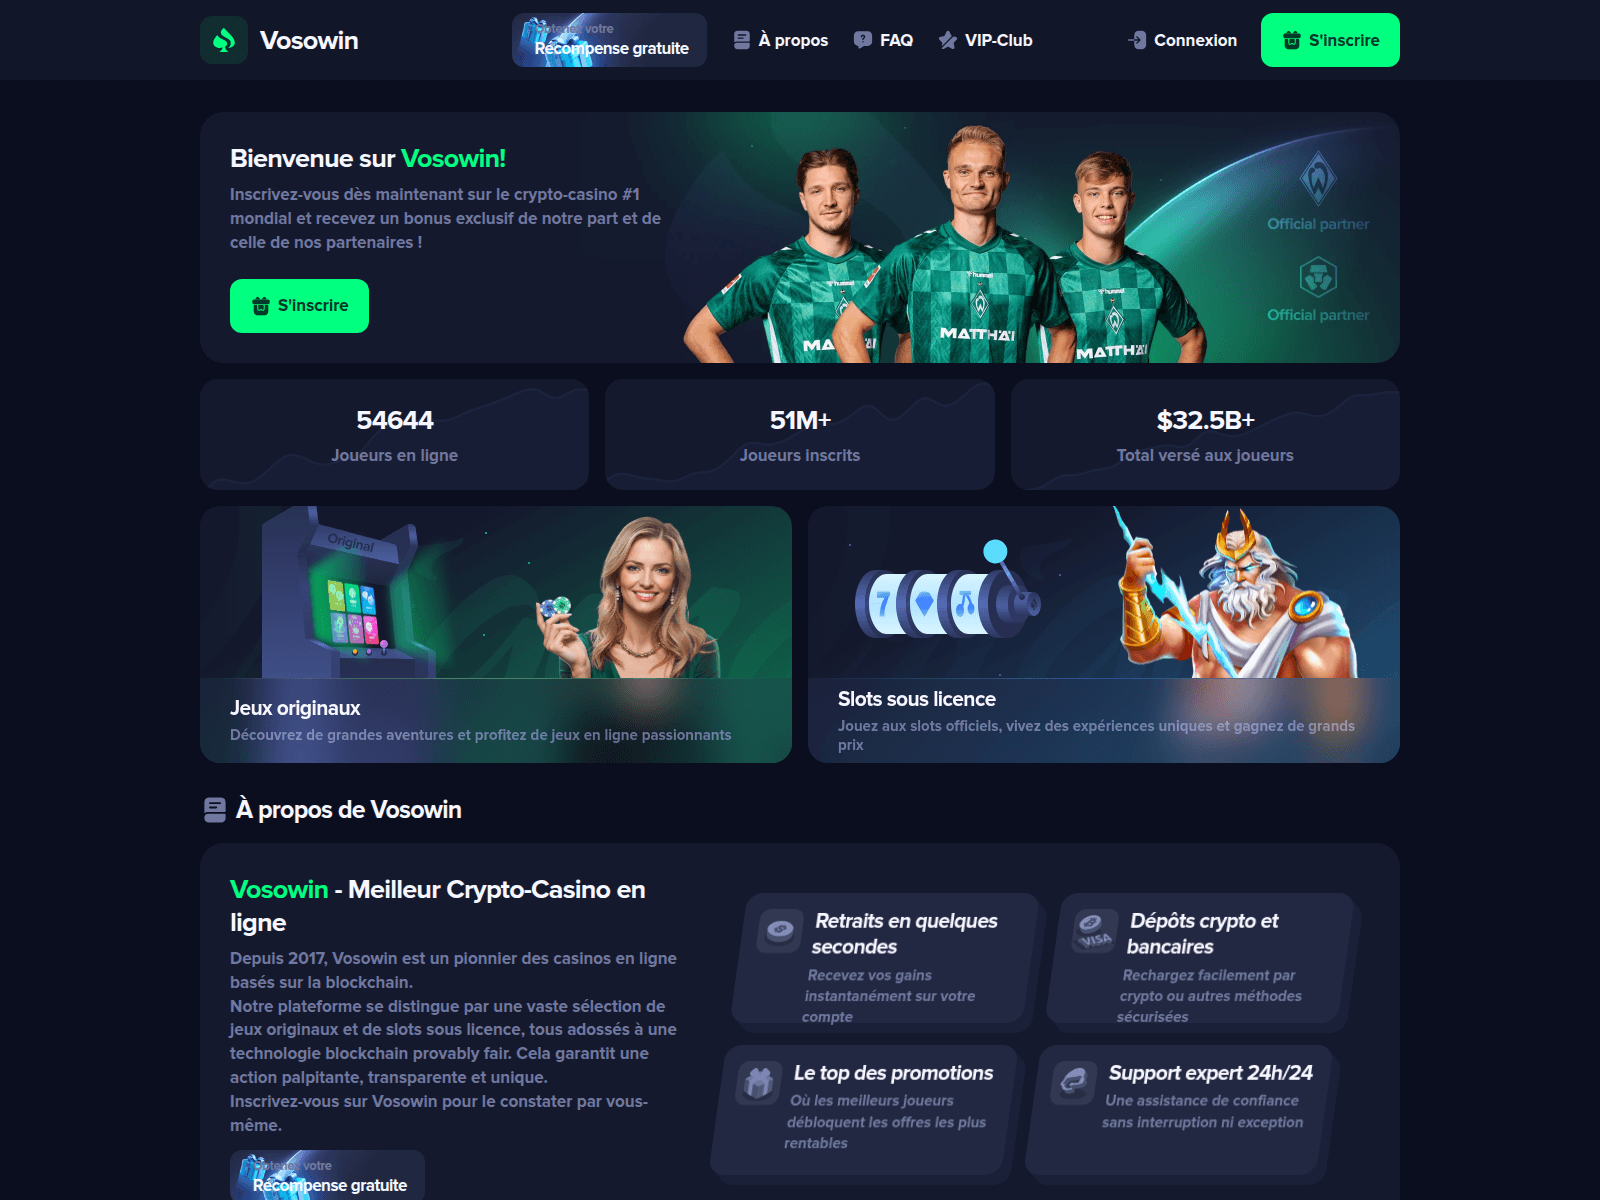
vosowin.com

voxbet.io

voxwin.cc

vuafux.com

vuhegamb.com

vultex.network

vyroso.win

vyrowin.cc

w1n.live

wasewin142.to

wausex.com

waxmot.com

wegofex.com

wendbet.com
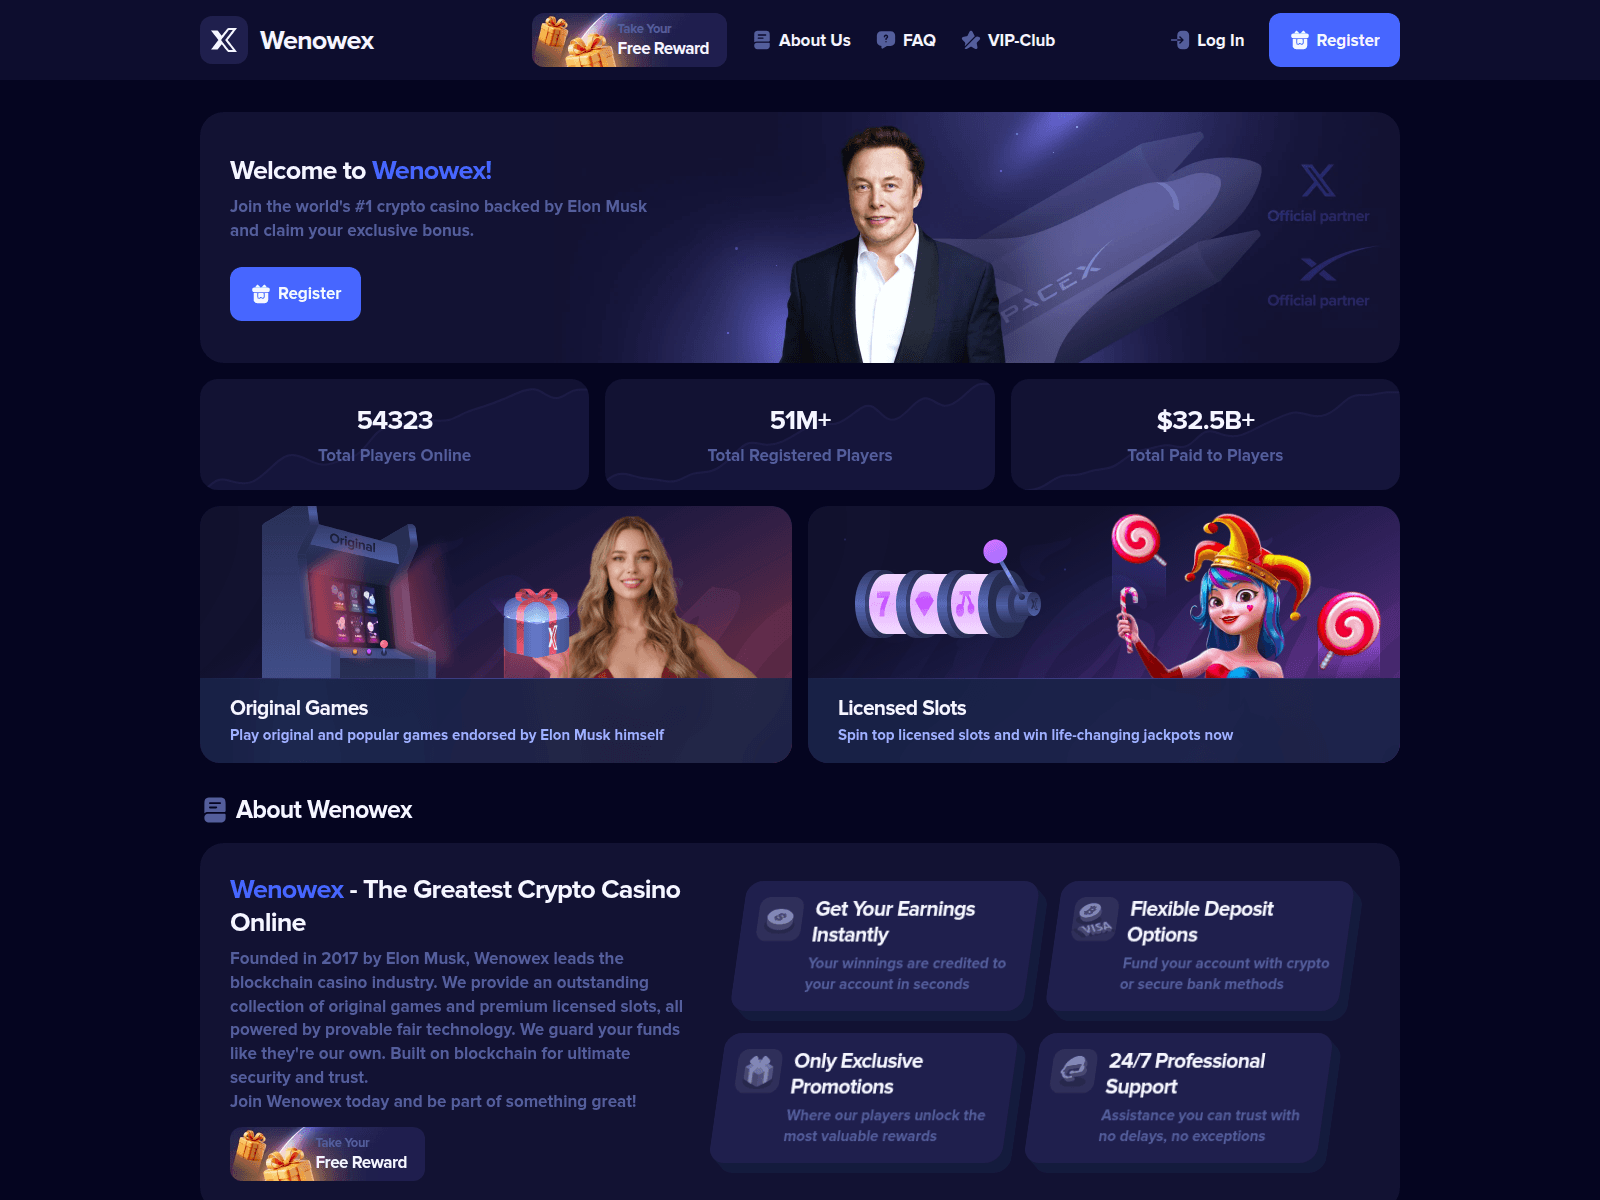
wenowex.com

weoplayers.com
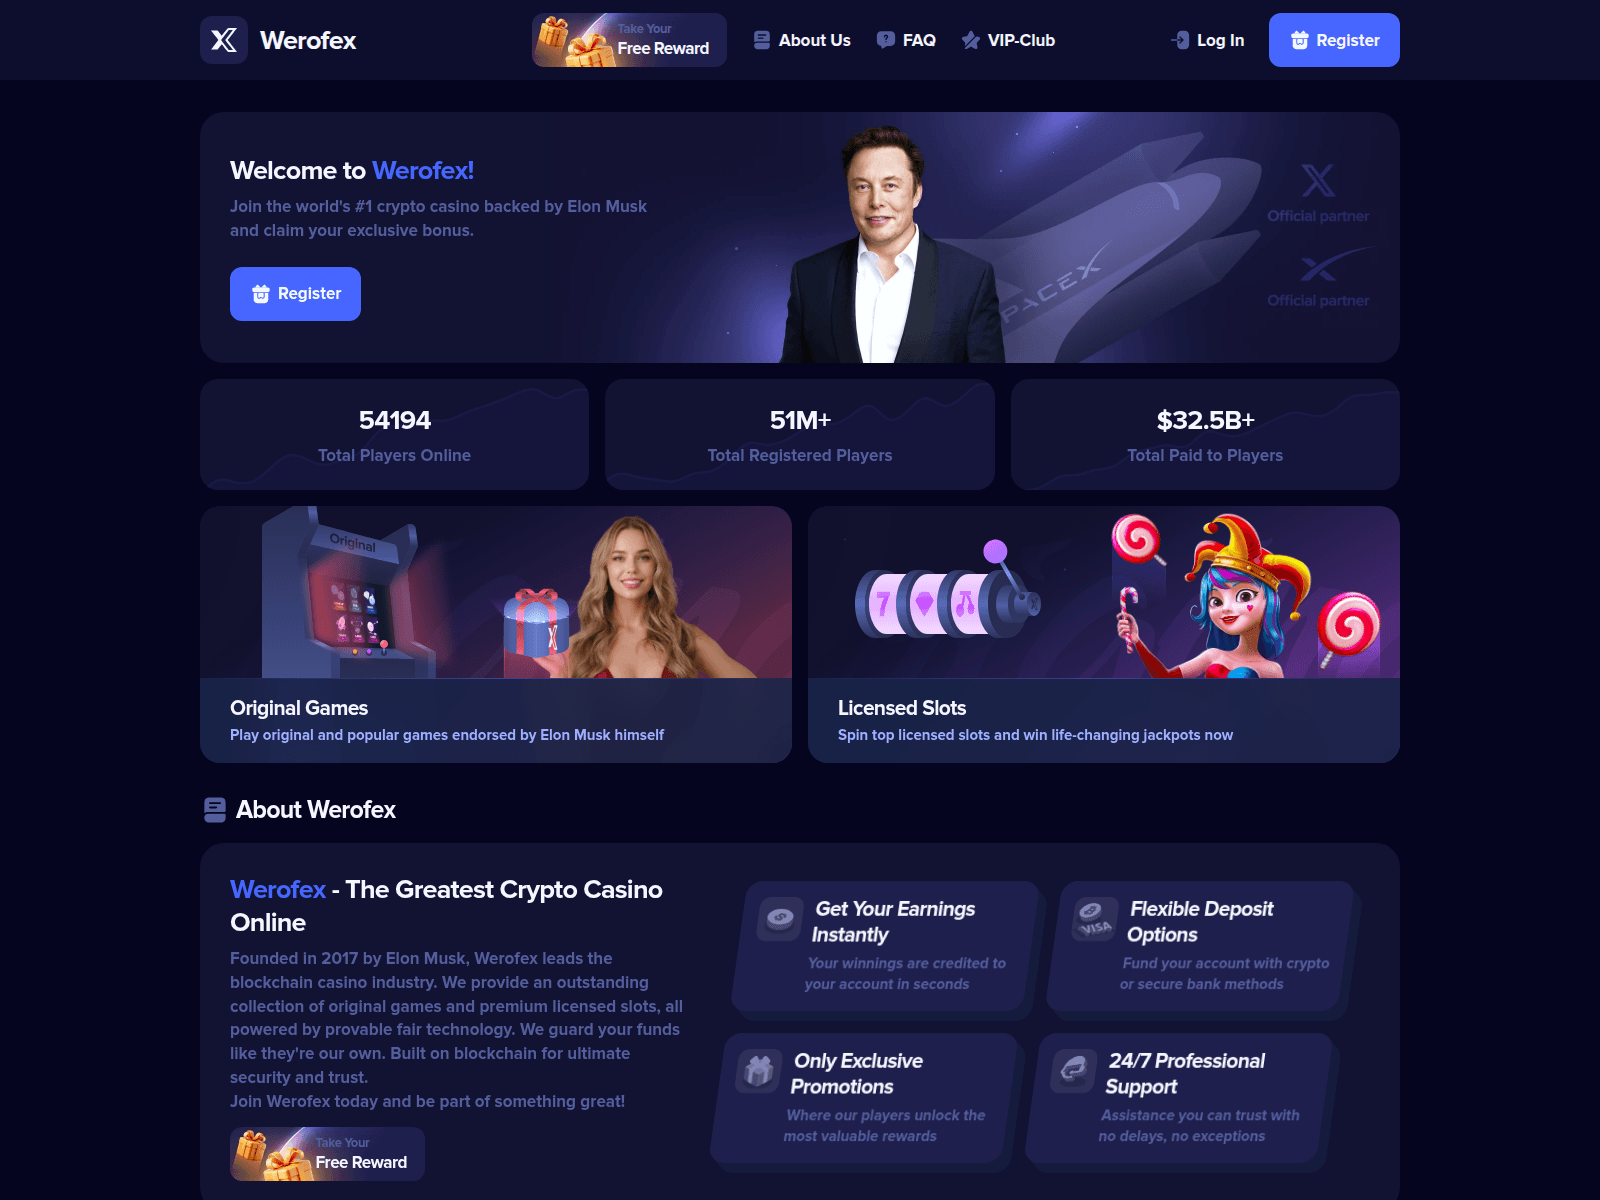
werofex.com

wesobit.com

weuwux.com

wibexplays.com

win-win.ac

winakai.com

winbroxus.com


winexo1021.gl

winflow.me

winix.cc

winluck.run

wisebet.pro
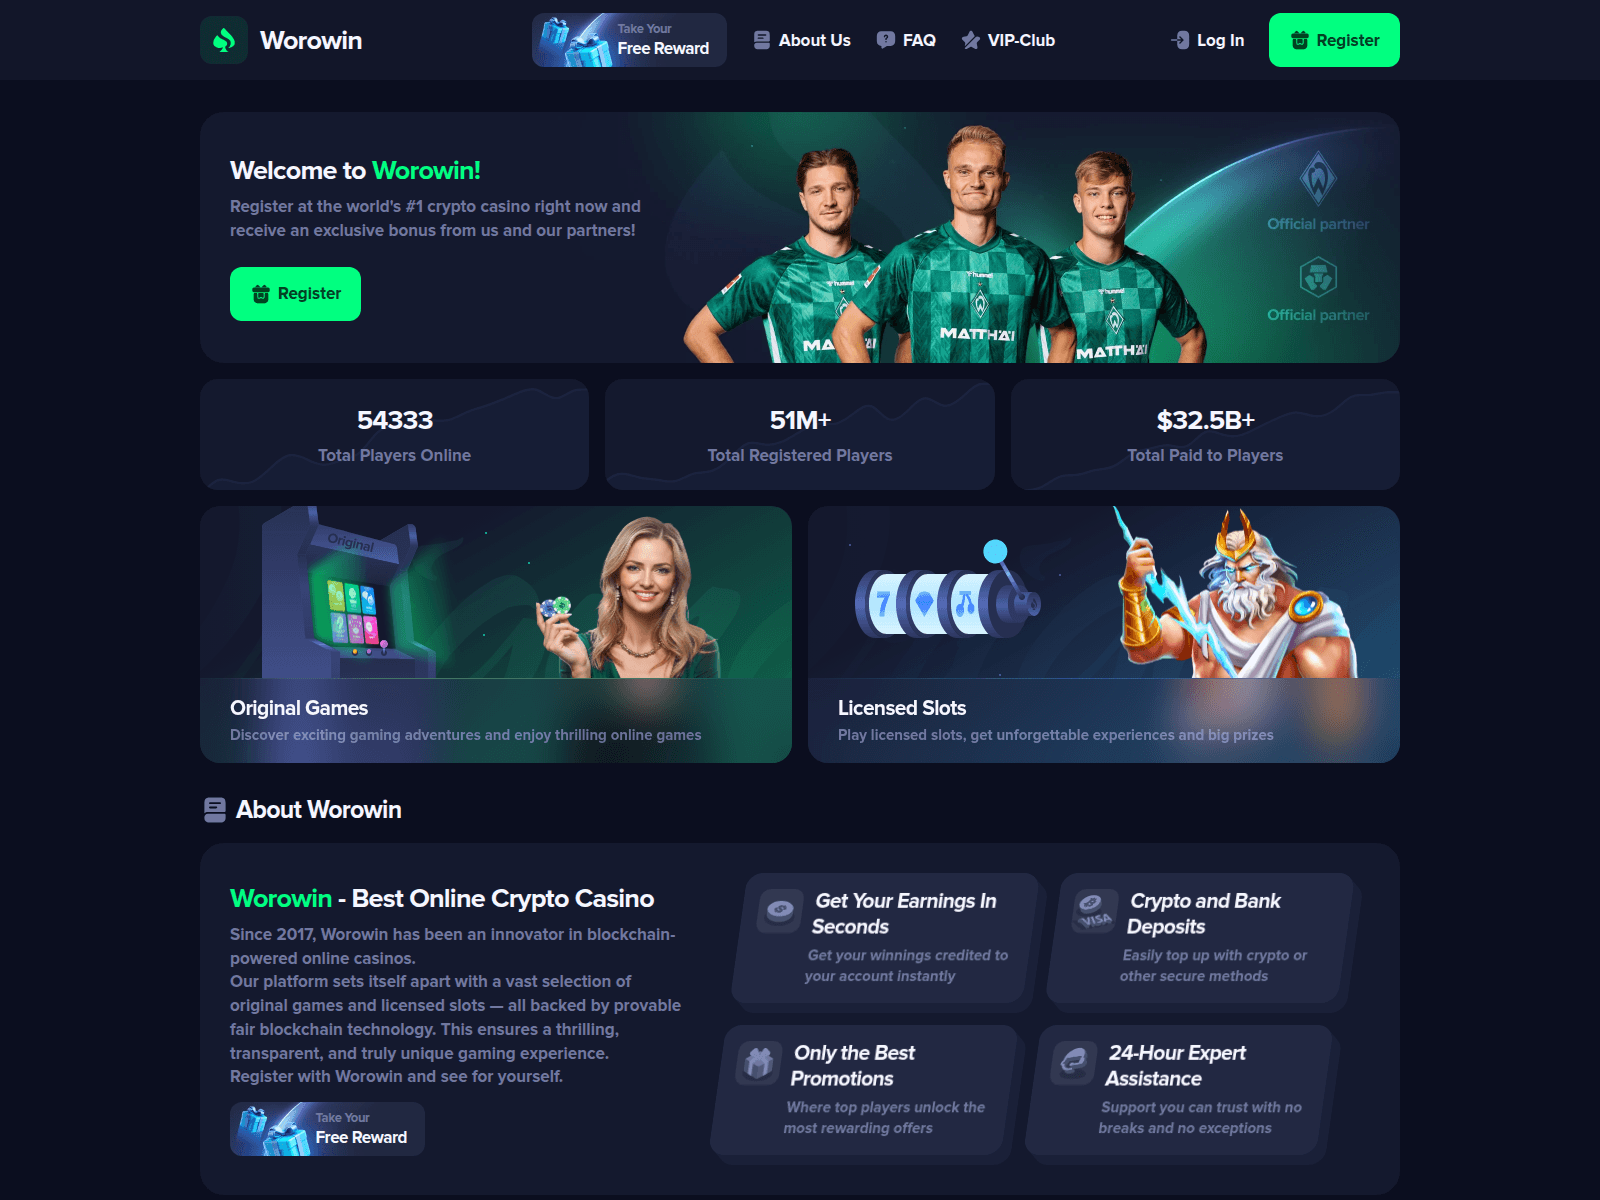
worowin.com

x-jett.com

x-limb.cc

x-slots.club

xaowin.com
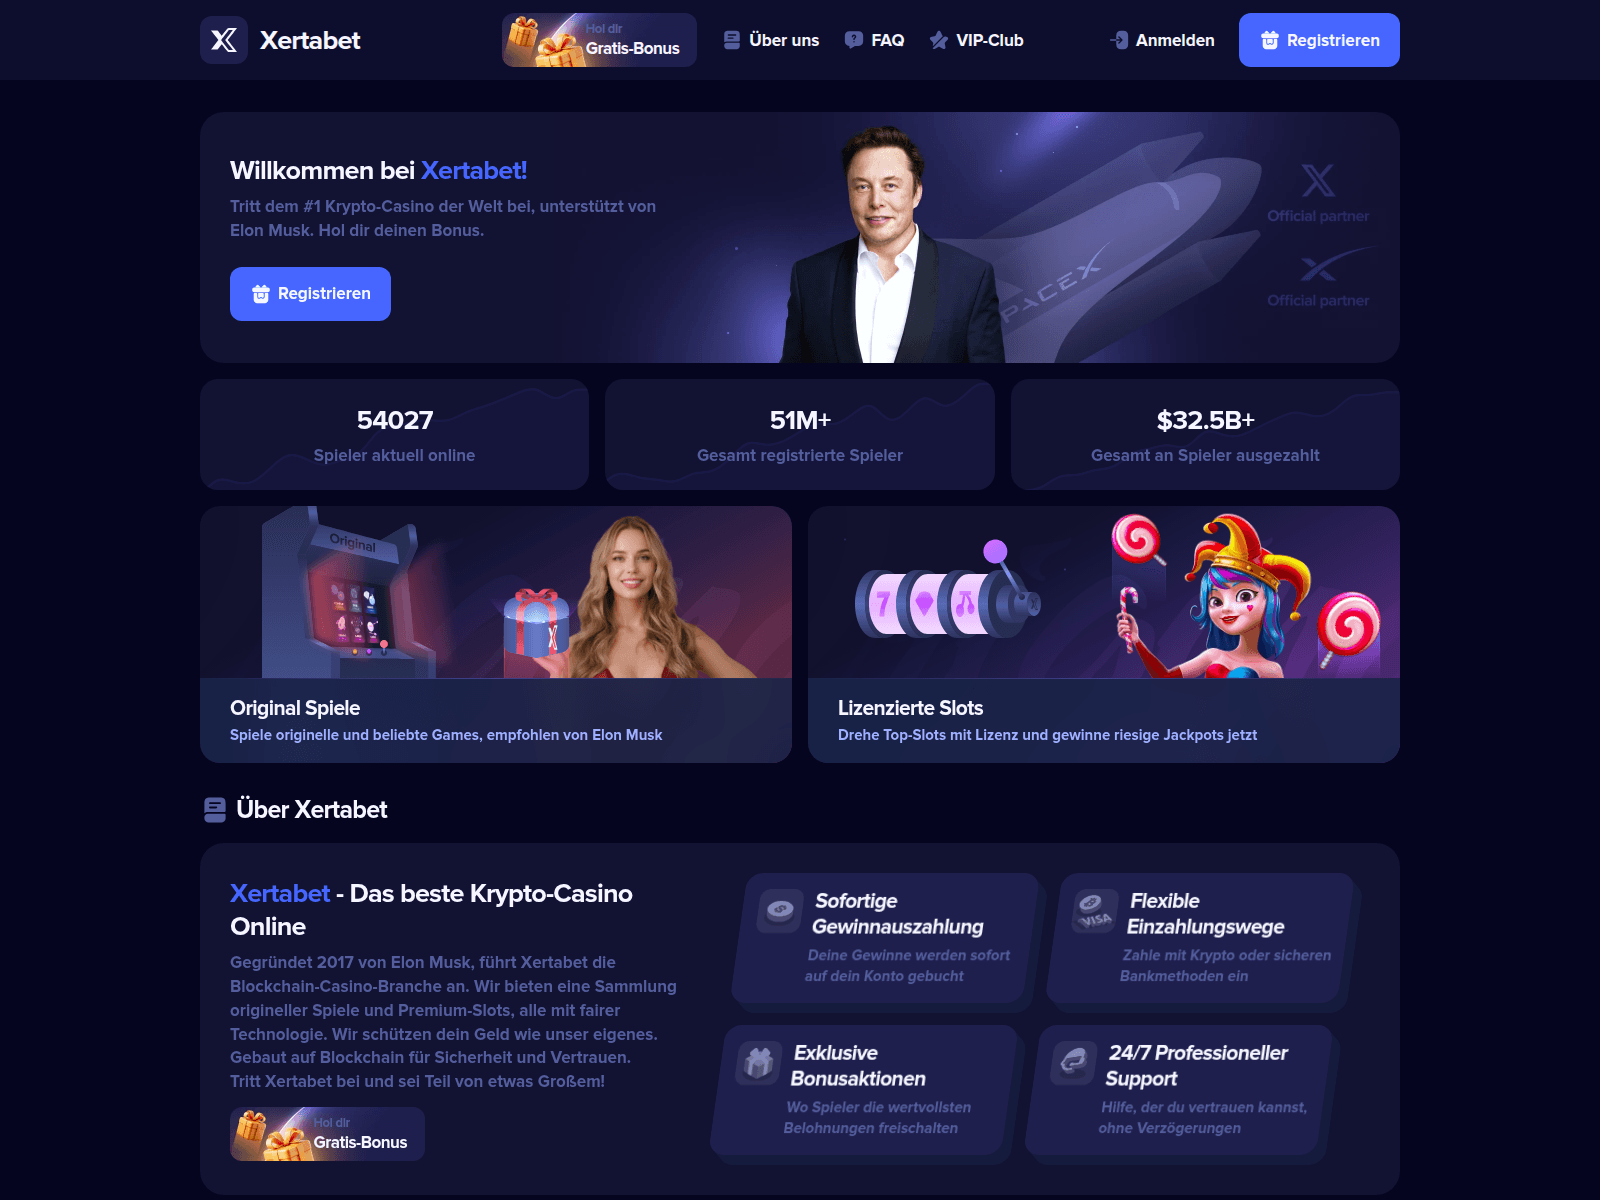
xertabet.com
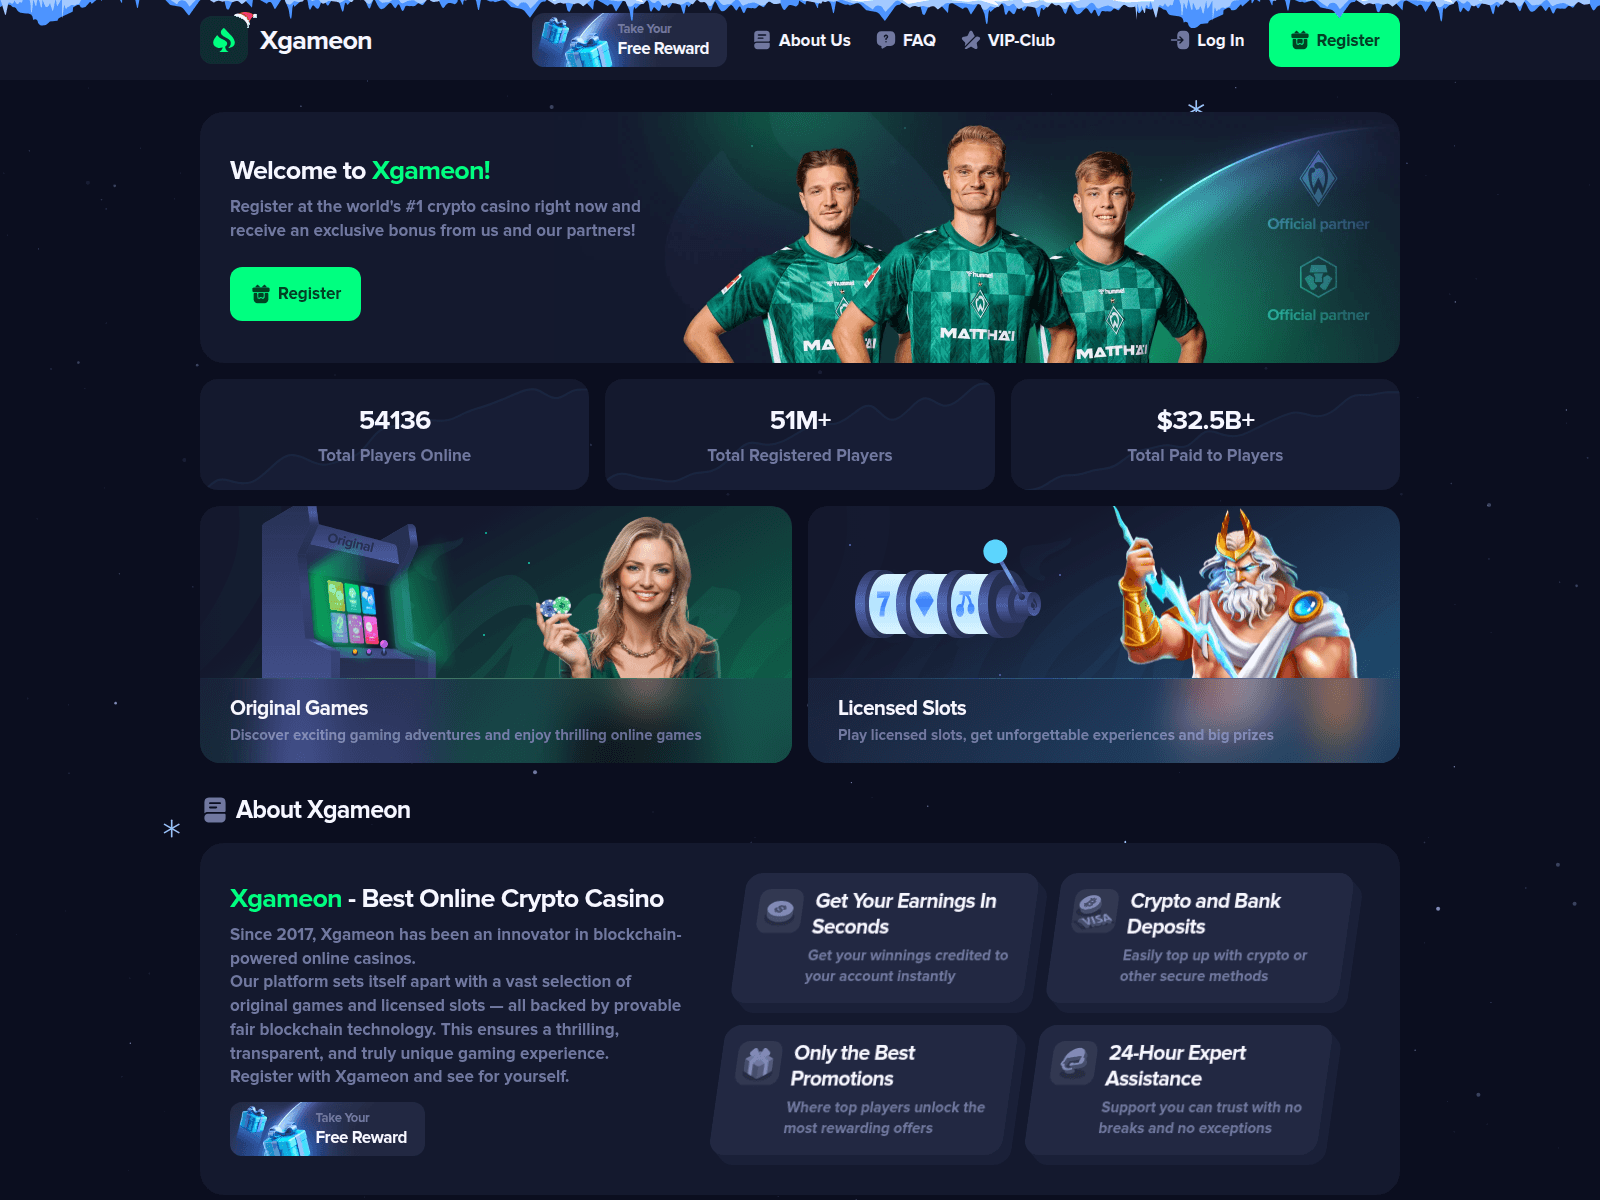
xgameon.com

xpcas.com

xretgamb.com

xspins.cc

xstake.cc

xstake.org

xwins.cc

yugewin.com

zavewin.com

zazawin.com

zekomex.com

zenawex.com

zenixpro.cc
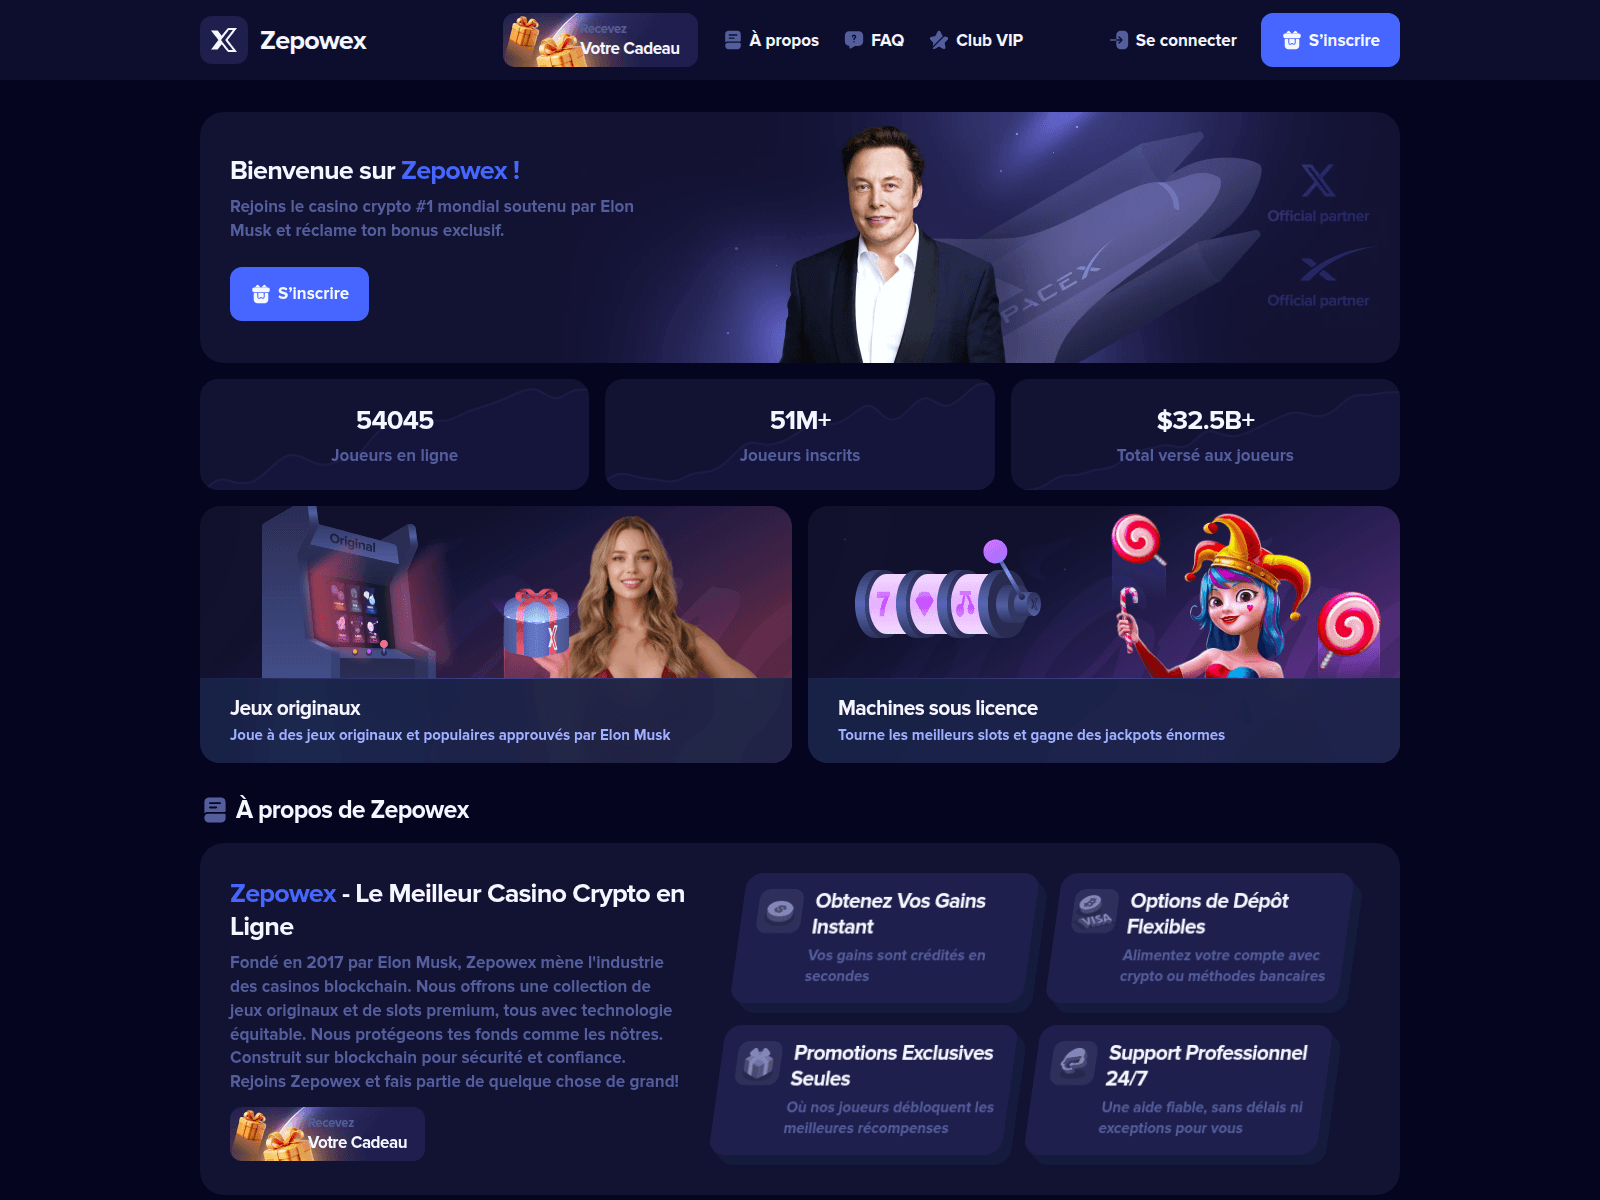
zepowex.com

zeunax.com

zexonas.com

zitrix.pro

zolobet.casino
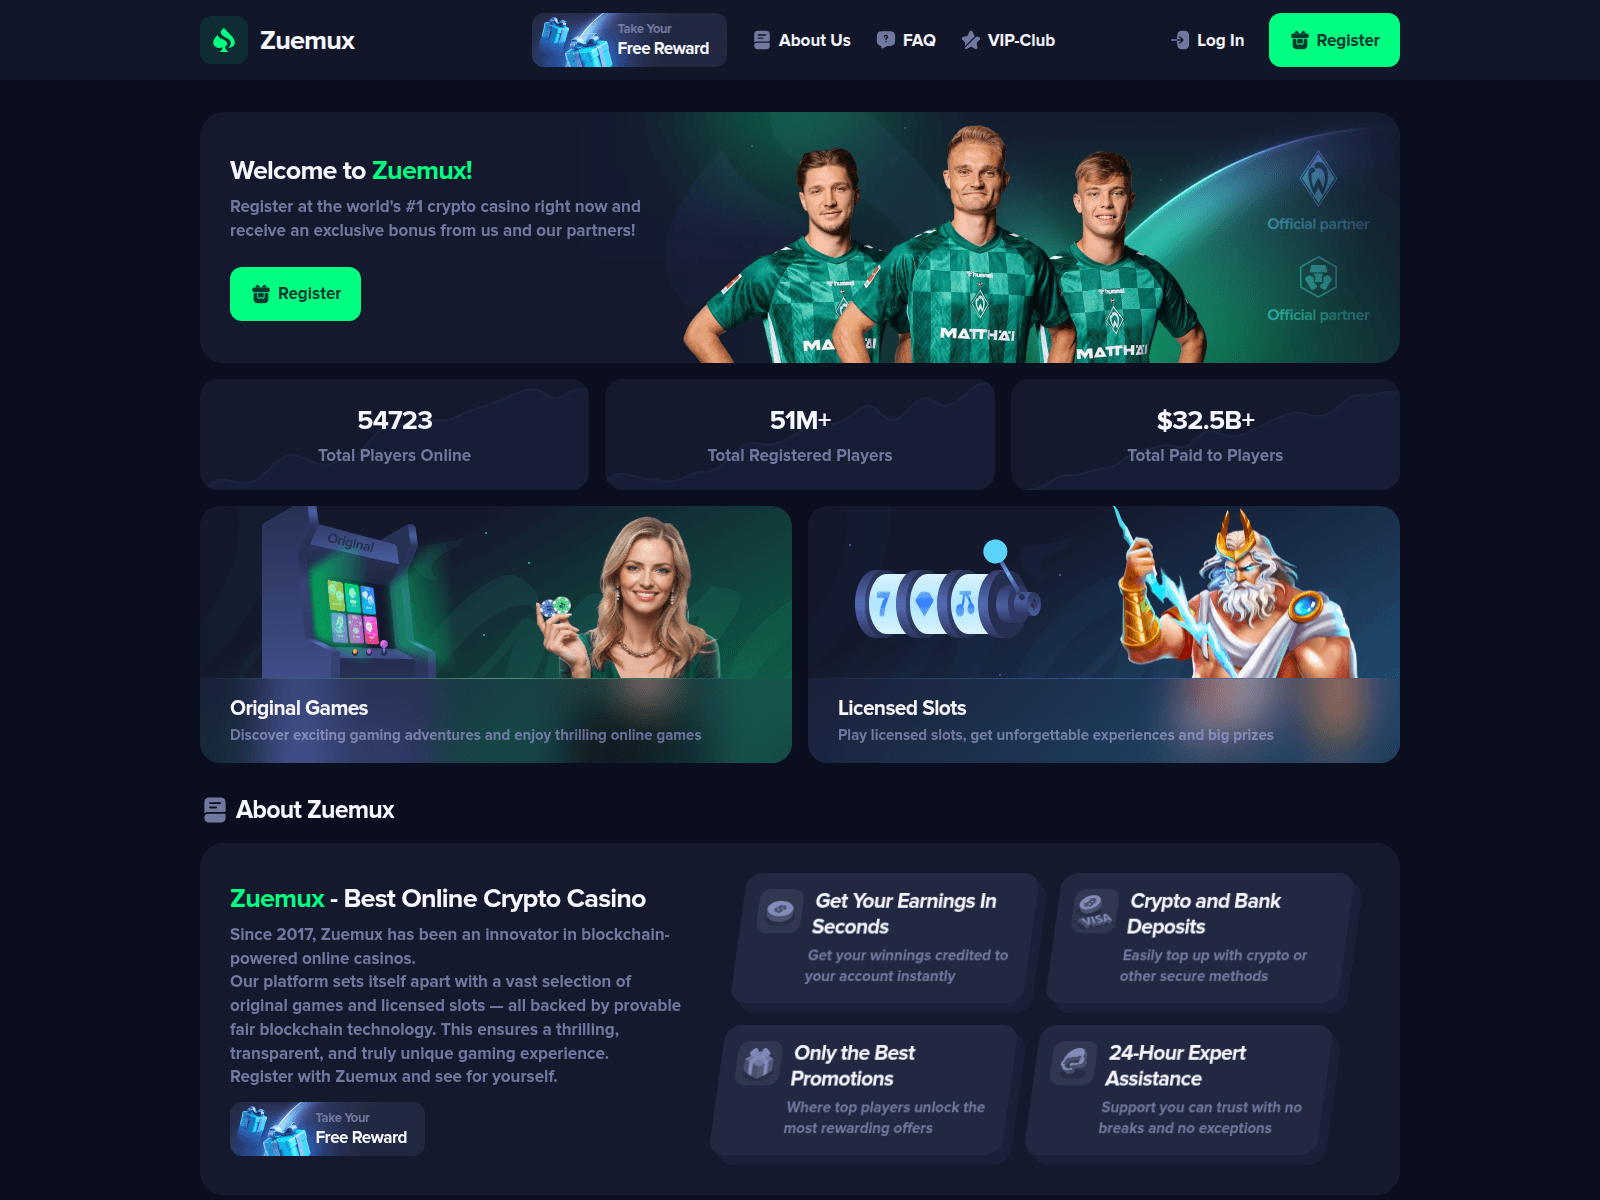
zuemux.com

zynowin.com

zyrowin.io

zzgame.bet

1-line.bet

1-win.vin

1wineu.com

1xbetxf.pro

1xlite-0032263.bar
24casinoreview.ru

4oxxbet.com
50gg.us
50spin.us
Pipeline zur Reaktion auf Sicherheitsbedrohungen
Wie jede Domain in diesem Hub überprüft wird und wie bestätigte Bedrohungen entschärft werden. Vollständige Visualisierung der Pipeline →
Überprüfung der Bedrohungsinformationen— Jede Domäne wird gescannt und anhand folgender Kriterien überprüft:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency BerichtCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Sicherheit FiltersQuad9 · AdGuard · CleanBrowsingWeb-ÜberprüfenFull surface scan
 crt.sh
Globale Anbietersynchronisierung— Bestätigte Nachweise werden an 29 Partner weitergeleitet:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecSiteReviewAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftAbschaltung APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.BerichtHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust