
Durchsuchen Sie die erfassten Domains und überprüfen Sie gespeicherte Beweismittel, Erkennungen sowie die aktuell beobachtete Verfügbarkeit.
221,187
Gesamtzahl der erfassten Fälle
215,381
VT erkannt
93,441
Zuletzt aktiv gesehen
127,746
Bei der letzten Überprüfung nicht verfügbar
0
VT Ausstehend
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake Domains
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Phishing Pages
Phishing pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Malicious Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Analysis
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Infrastructure-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Phishing Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Scam (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Requests for private keys or seed phrases
Unexpected transaction requests
Poor website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1
Always verify domain authenticity
2
Enable two-factor authentication
3
Use hardware wallets for transactions
4
Regularly update security software
5
Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 1,678 domains tracked for this threat type
WalletConnect Abuse 1,678 domains
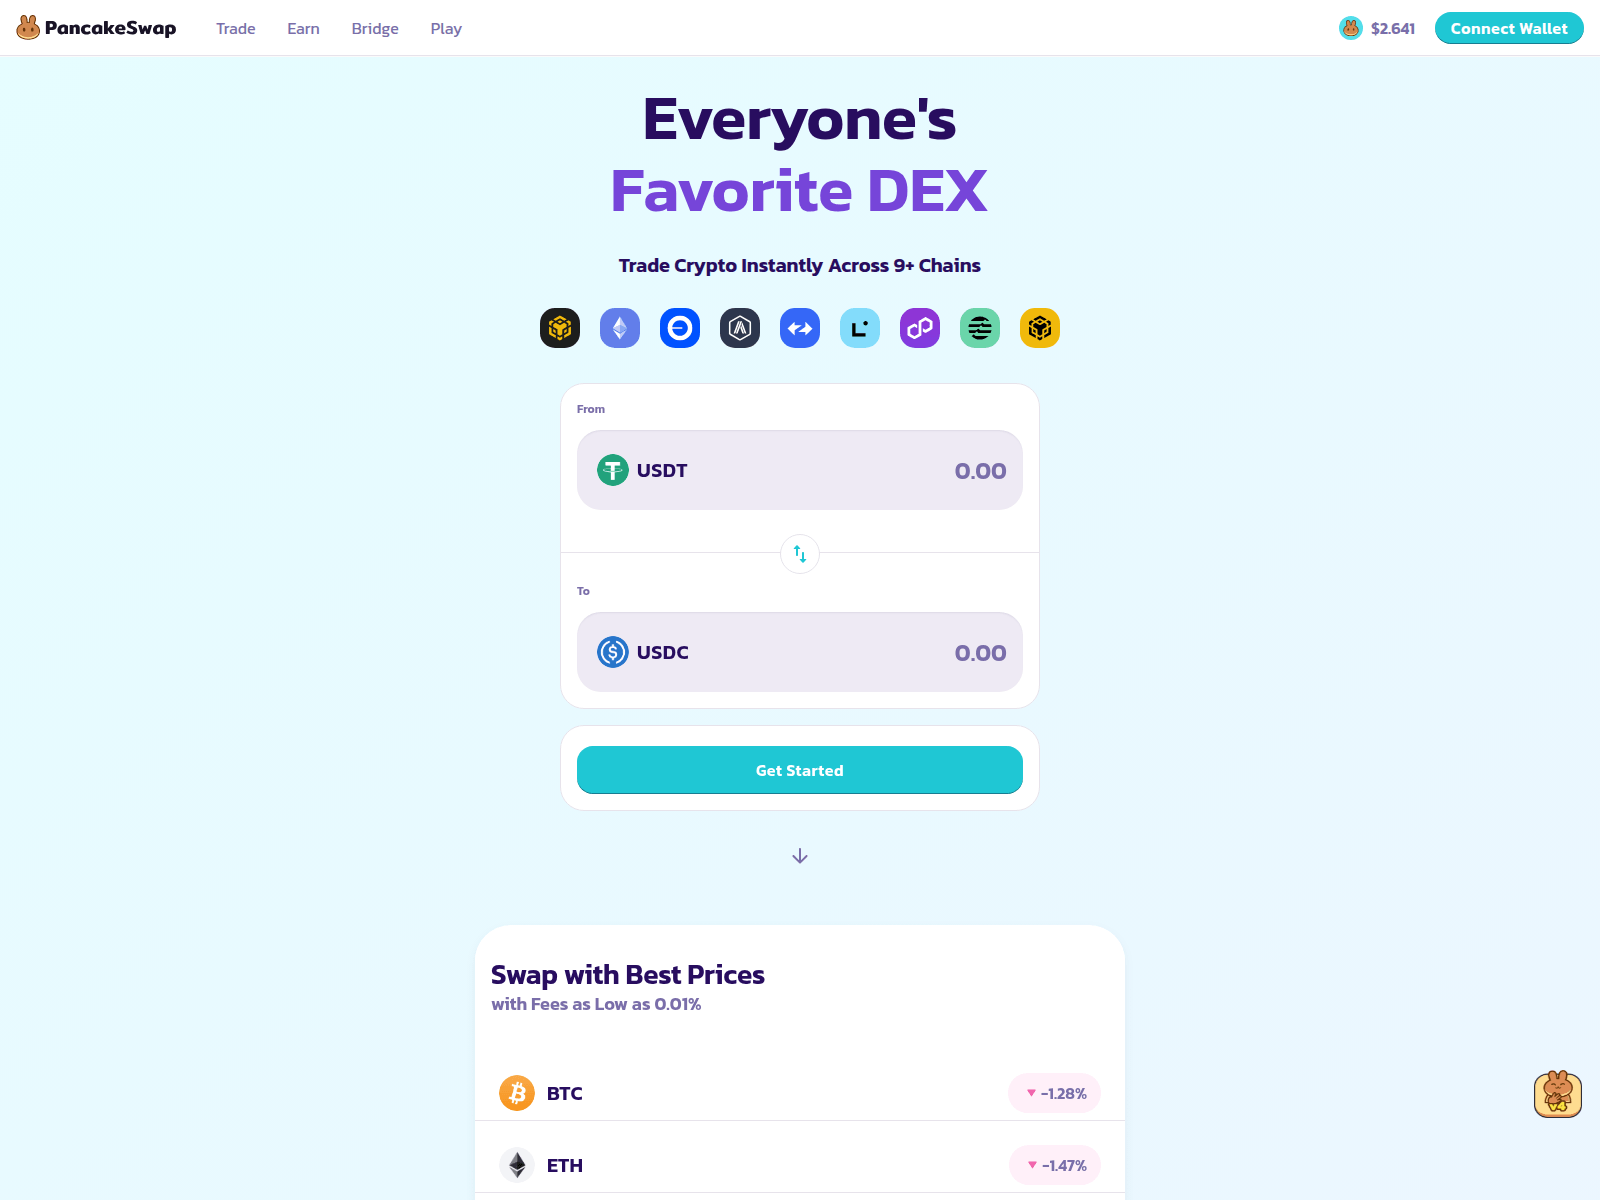
panswap.pro

peth.world

plasmachainlive.com

plasmaoneth.com
polymarket-trade.xyz
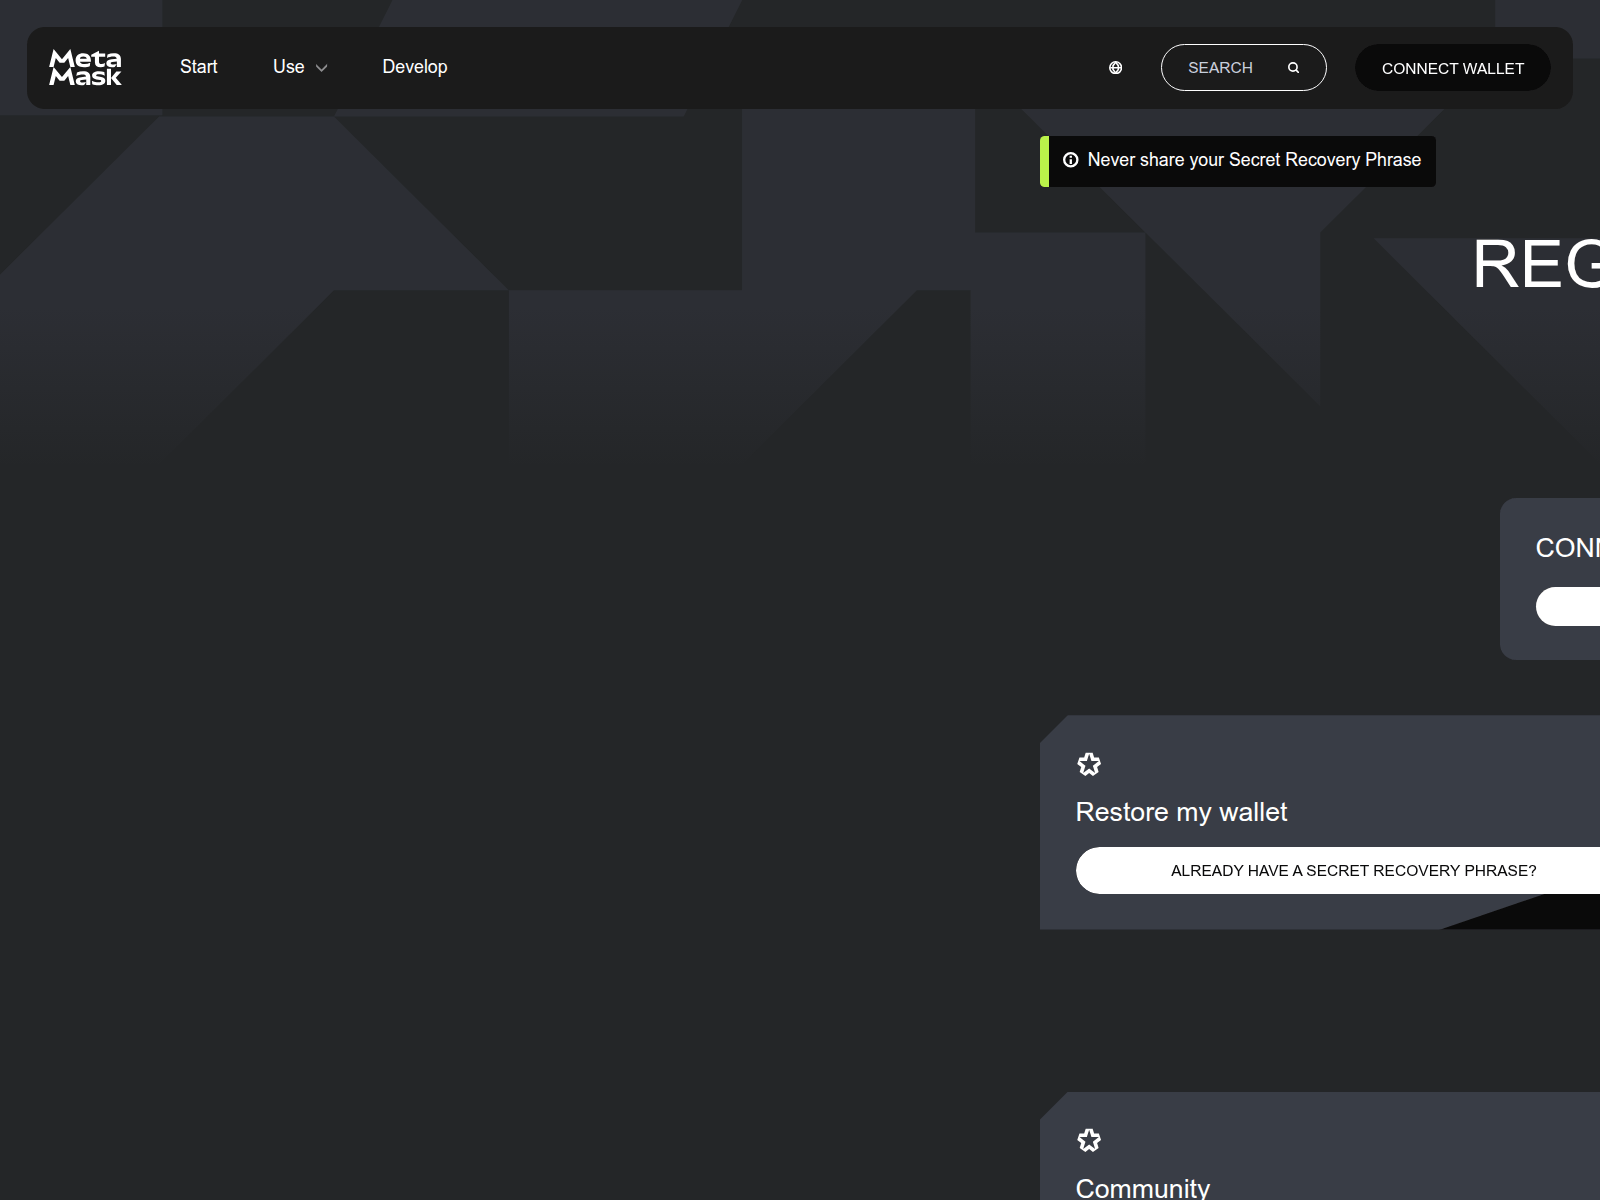
porlfolio-melamask.app

proposal-yieldfi.votings.workers.dev

register-cysicfoundation.org
register-espresso.app
revapay.org

reward-ethena.finance

rewards-yieldusd.com

rubery.fun

secured-file-manager.com

shardssoniclabs.online

shiba-app.org

stage.degengames.fun

stake-lido.vercel.app

stake-nanoeth.net

stlink.pro

stlink.world

tetimons.click

tresure-chests.xyz

unisockshub.com

usdappx.com
usdt-verif.net

virtual-vote.app


web3.pancake.run
xmaquina-verify.com

xplecosystem.xyz

xzxzxz.elysium-drainer.world

xzxzxzxz.elysium-drainer.world

yieldusd-dashboard.net

yieldusd.net

zxzxczcx.elysium-drainer.world

0g-foundiation-claim.netlify.app

0rigiindefi.world

209494.com

3bxnlej.icu

6teen.network

aavdefi.top

airdropmmt.finance

aisdhostingrefund.pages.dev

alloca.org
aml.grentun.icu

aml.riskcheck.info

amlcrypto.help

app-lidopoints.com

app.templefinance.io

app.un.iswap.cam
app.usdclmp.com

app.xn--unswap-4va.org

aster-drops.netlify.app

asterdiex.com
avvvdefi.top

award-yieldusd.org

bakedonape.com
best-wallettoken.com

bitok.run

blaze-giveawaay.net

bob-sepolia-a9kyey7hq-distributed-crafts.vercel.app

buycoin.sbs

centralchain-elitebridge.web.app

chainway.live

check-morpho.app
checker-aml.org

cifr121.com
claim-lighter.com

claim-monad.cyou

claim-perceptron.xyz
claim-ravedao.org

claim-tari.org

claim-turtles.xyz

claim-vooi.org
claim-wet.org
claims-doublezero.app

connectcopy.top

dgdg43.elysium-drainer.world

distribution-etc.com

dlsperese.xyz

dropmonadspro.xyz

duplicate-disabled-1329.invalid

ebemevm.live

esqresso.foundation
ether-fi-verification.com
fcboft.cc
fiwnfa.cc

frrvfe.cc

gain-nanoeth.com

giveaway-blaze.net

grouped-service-display.shmonad-frontend-dapp.pages.dev
hananetwork.app

hyperliquid.com-api-gateway-beta-wallets-v4.pro

hyperliquid.com-service-alpha-auth-app.pro

hyperunit.vc
ink-wrapped.com

jameswins-allocations.xyz

jutroen.app
Pipeline zur Reaktion auf Sicherheitsbedrohungen
Wie jede Domain in diesem Hub überprüft wird und wie bestätigte Bedrohungen entschärft werden. Vollständige Visualisierung der Pipeline →
Überprüfung der Bedrohungsinformationen— Jede Domäne wird gescannt und anhand folgender Kriterien überprüft:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency BerichtCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Sicherheit FiltersQuad9 · AdGuard · CleanBrowsingWeb-ÜberprüfenFull surface scan
 crt.sh
Globale Anbietersynchronisierung— Bestätigte Nachweise werden an 29 Partner weitergeleitet:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecSiteReviewAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftAbschaltung APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.BerichtHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust