
Durchsuchen Sie die erfassten Domains und überprüfen Sie gespeicherte Beweismittel, Erkennungen sowie die aktuell beobachtete Verfügbarkeit.
221,187
Gesamtzahl der erfassten Fälle
215,382
VT erkannt
93,441
Zuletzt aktiv gesehen
127,746
Bei der letzten Überprüfung nicht verfügbar
0
VT Ausstehend
How This Attack Works
Solana Drainer threats exploit vulnerabilities in Solana's crypto ecosystem to steal funds. Understanding their operation is crucial for prevention.
STEP 1
Target Identification
Attackers identify potential victims through phishing emails and fake websites.
STEP 2
Phishing Execution
Victims are lured to malicious sites mimicking legitimate platforms, like phantomairdrop.com.
STEP 3
Credential Harvesting
Once on the fake site, victims input sensitive information, believing it to be secure.
STEP 4
Fund Drainage
Attackers utilize harvested credentials to access wallets and drain funds via illicit transactions.
Technical Analysis
Solana Drainer attacks leverage phishing techniques to exploit the Solana blockchain. Attackers often create copycat websites using top TLDs such as .com, .xyz, and .cc, with domains hosted by registrars like Cloudflare, Inc. and PDR Ltd. These sites employ deceptive JavaScript and HTML code to mimic legitimate interfaces, tricking users into entering their private keys or seed phrases. Once credentials are obtained, attackers interact with the Solana blockchain via RPC calls to execute unauthorized transactions. The usage of smart contract functions like `transfer` and `approve` allows attackers to swiftly move funds out of victims' accounts. The infrastructure often involves a network of proxy servers to obfuscate the origin of the attack and make tracing back to the perpetrators difficult.
Real Cases
Phantom Wallet Breach (2023)
$2 million stolen
Attackers created a fraudulent Phantom wallet site to harvest user credentials, resulting in a $2 million theft.
SolUnion Scam (2024)
$1.5 million stolen
Using the domain phantom.solunion.cc, scammers executed a sophisticated phishing attack, stealing $1.5 million in SOL.
VaultBenefits Exploit (2024)
$3 million stolen
A fake airdrop campaign via vaultbenefits.net led to credential compromise and a subsequent $3 million drain.
How to Detect
Unsolicited emails or messages offering free SOL or airdrops
Websites with slight misspellings of legitimate names
Requests for private keys or seed phrases
Suspicious URL structures or unfamiliar TLDs like .xyz or .cc
Lack of HTTPS security on sites claiming to be secure
How to Protect Yourself
1
Verify URLs carefully before interacting
2
Enable multi-factor authentication on your wallet
3
Never share your private key or seed phrase
4
Regularly check transaction histories for unauthorized activity
5
Use official wallet apps and browser extensions
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 2,752 domains tracked for this threat type
Solana Drainer 2,752 domains
solanavolumeboost.com

soldappsauth.xyz

solfalre.github.io
solflare-wal.com

solmoons.xyz

solprismdapp.xyz

spin.solhq.cc

ssolscan.com

sulf.live
test.phantomwallet.at
tokenpredict.app

troll-live.xyz
trump.solhq.cc

us-phantom-wallet.pages.dev
uscr.lat

usi-phantom.pages.dev

usorcoin.top

uss--phantom.pages.dev
utility.soldex.trade

vkfcz.my

wallet-phantom-eng.pages.dev

wlfi-drop.com

www-vote.usor-events.com

12502.cc
49853.my
74801.academy

air.solgalaxy.cc
app.meteora.bz

app.rneteora.org

app.sol-hyperliquid.live

backpacks.live

bdccoinsolana.lol

bifrostgov.web.app

bullish.lat

bullx-trading.com
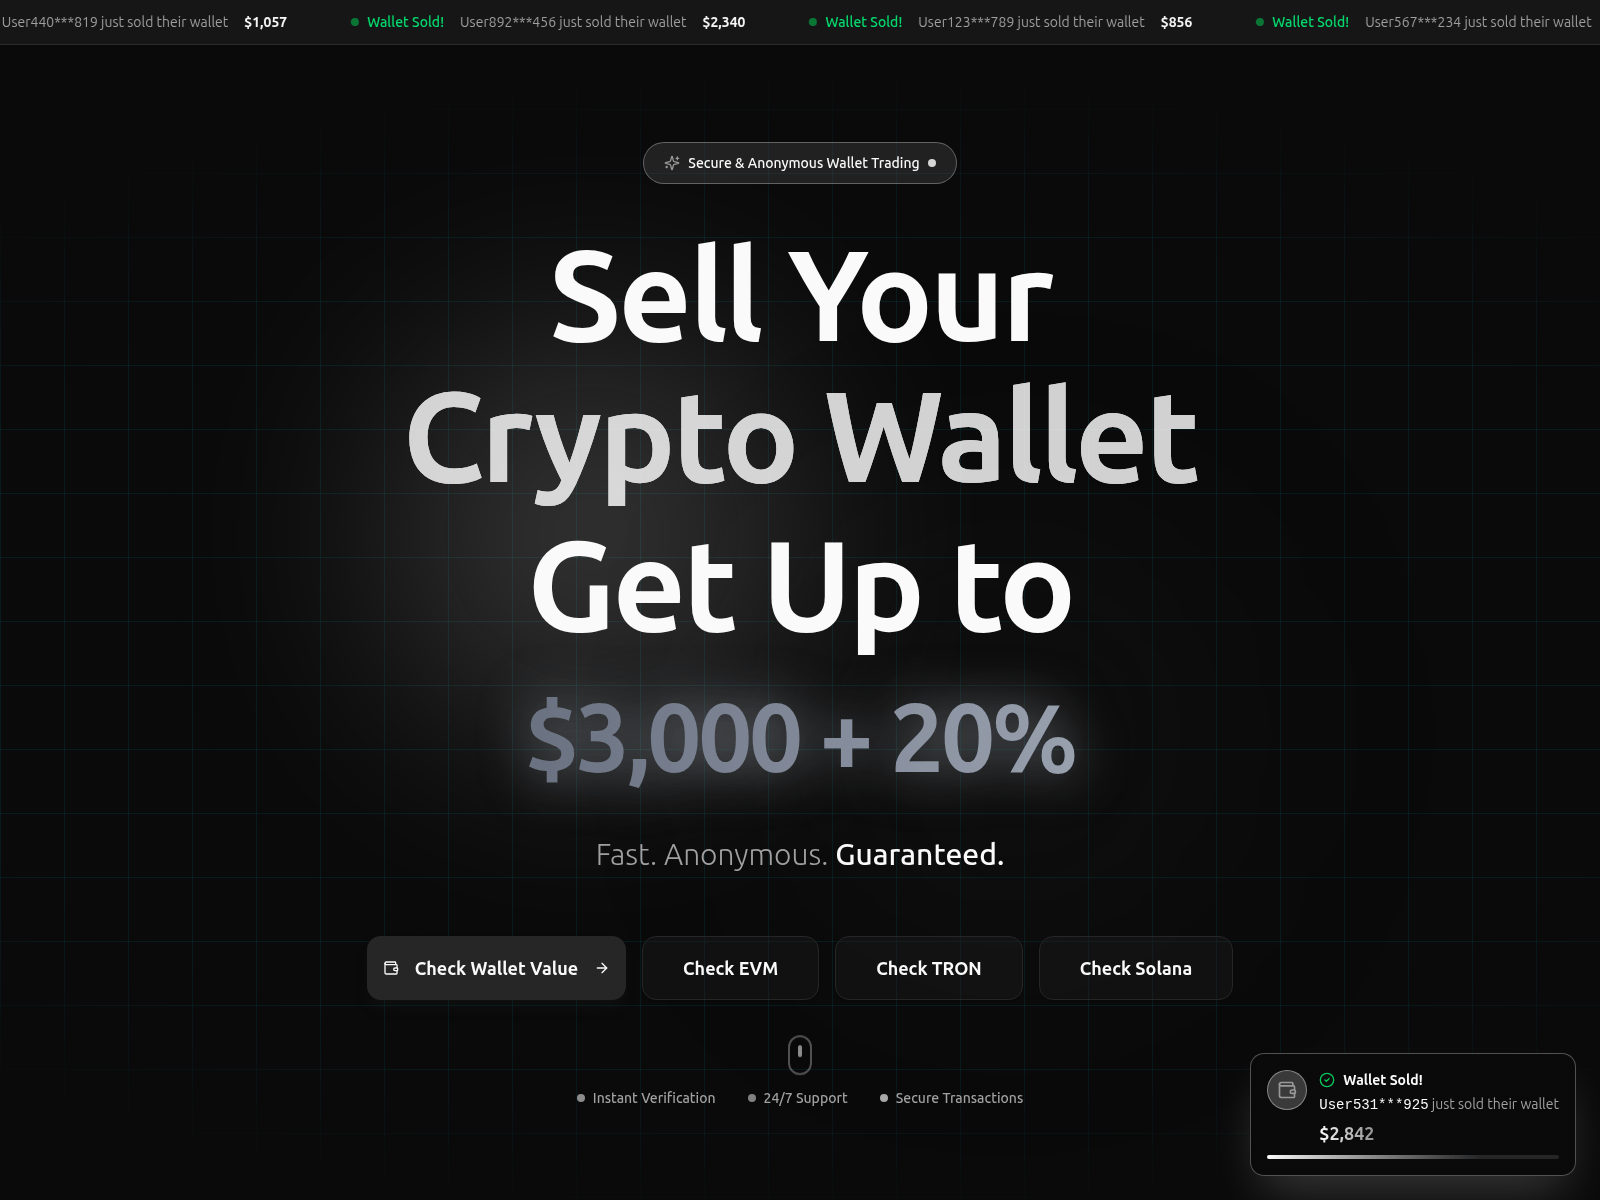
buy-wallet.today
chronostake.com
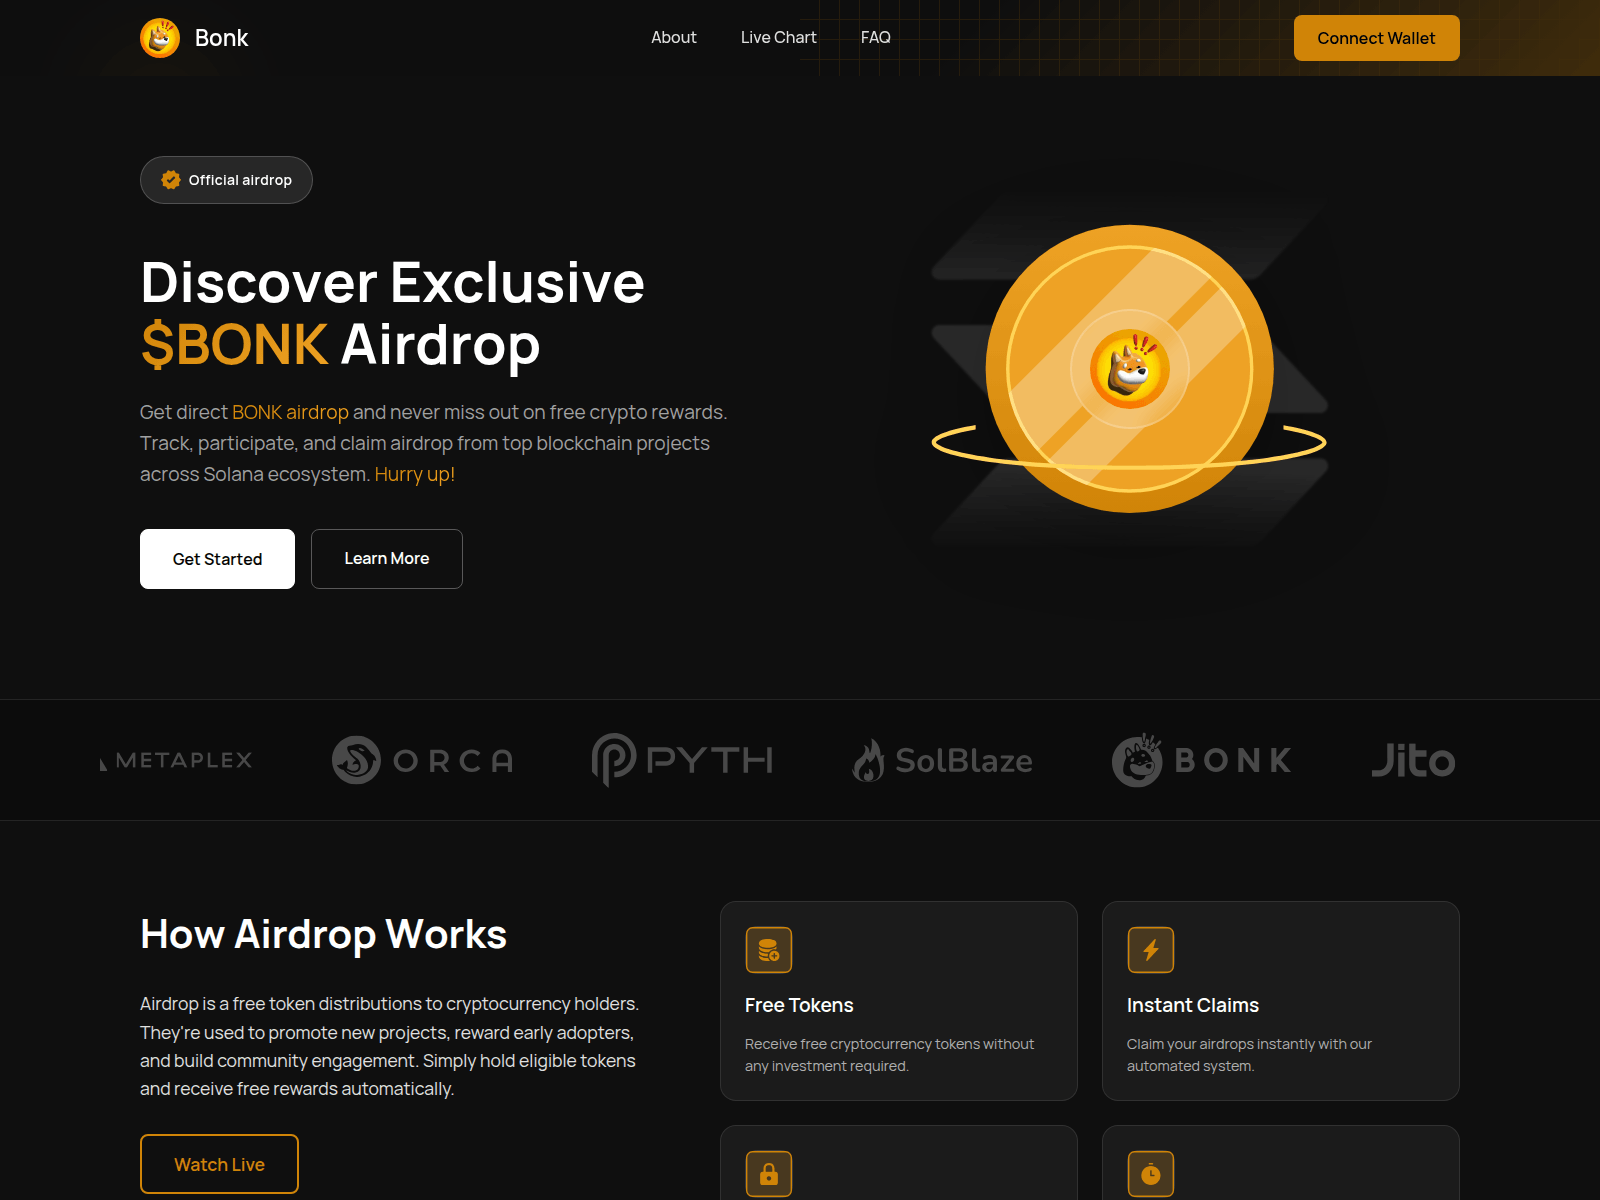
claim.bonkcoin.info
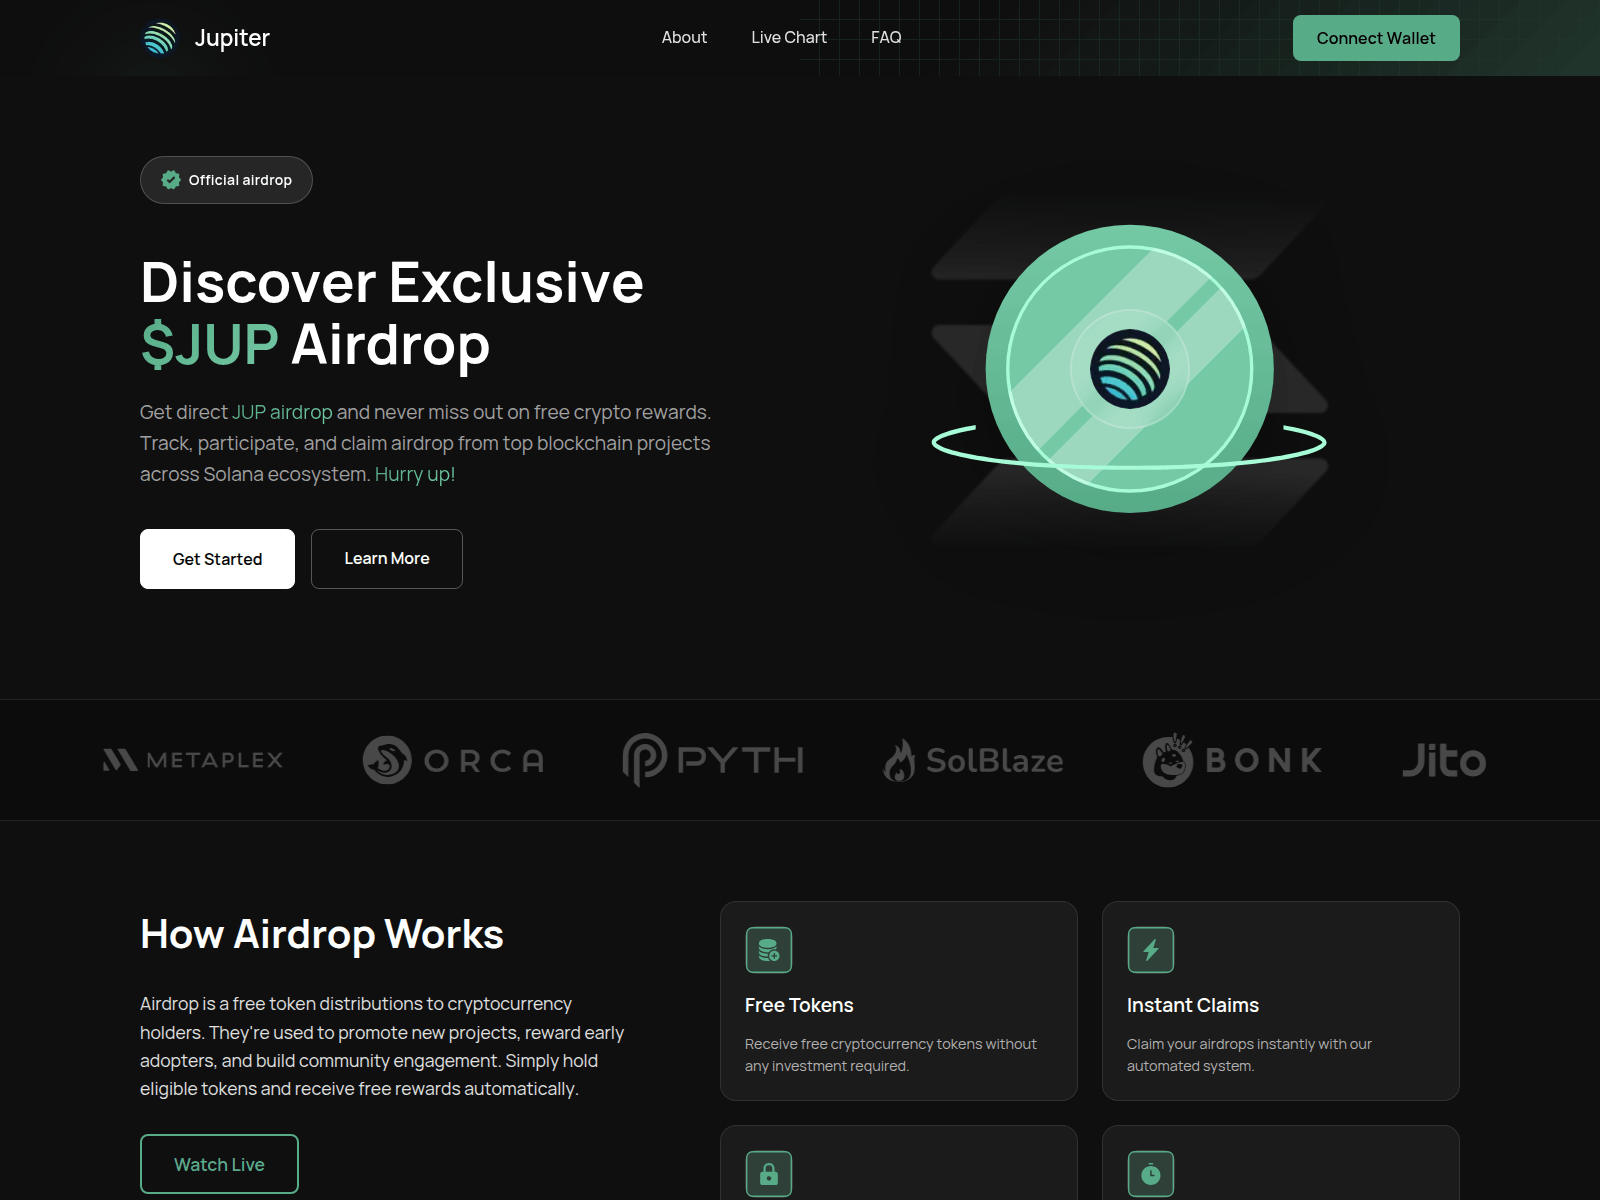
claim.juplter.app

claim.recali.life
claim.usd-solana.com
coin.solgalaxy.cc
coin.solhq.cc

cpnfc.my

cryptorecoverysystem.com

d.upln.app

dale.coincap.click

dexoracle.com

docs-phantom-io.pages.dev

dropgate.fun

en-phantomus-guide.pages.dev

ephantom.pages.dev

events-fogswap.xyz

events-kaio.xyz
geraslot.world

jffgagamdf.top

jitogo.xyz

join-55onsol.xyz
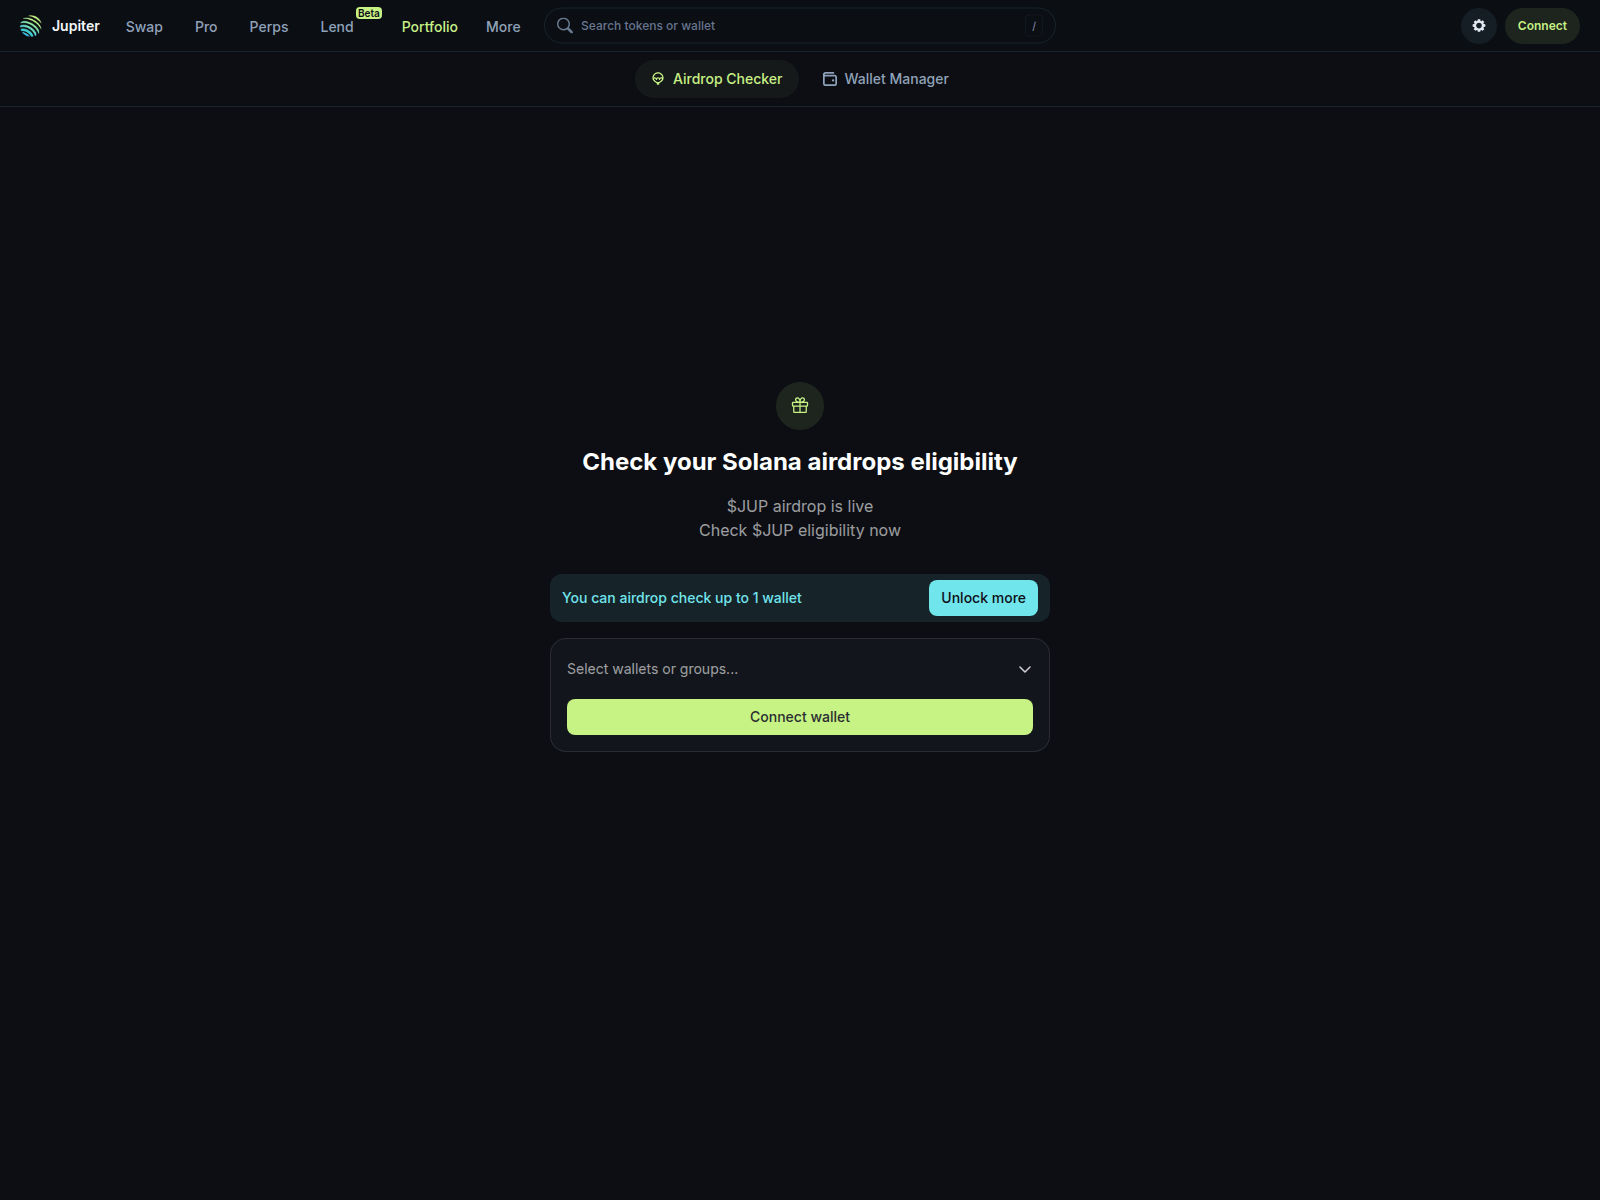
jup-checker.xyz

jupiter-dapp.pro

jupiterdapp.click

jupsolana.com

jupswap.net
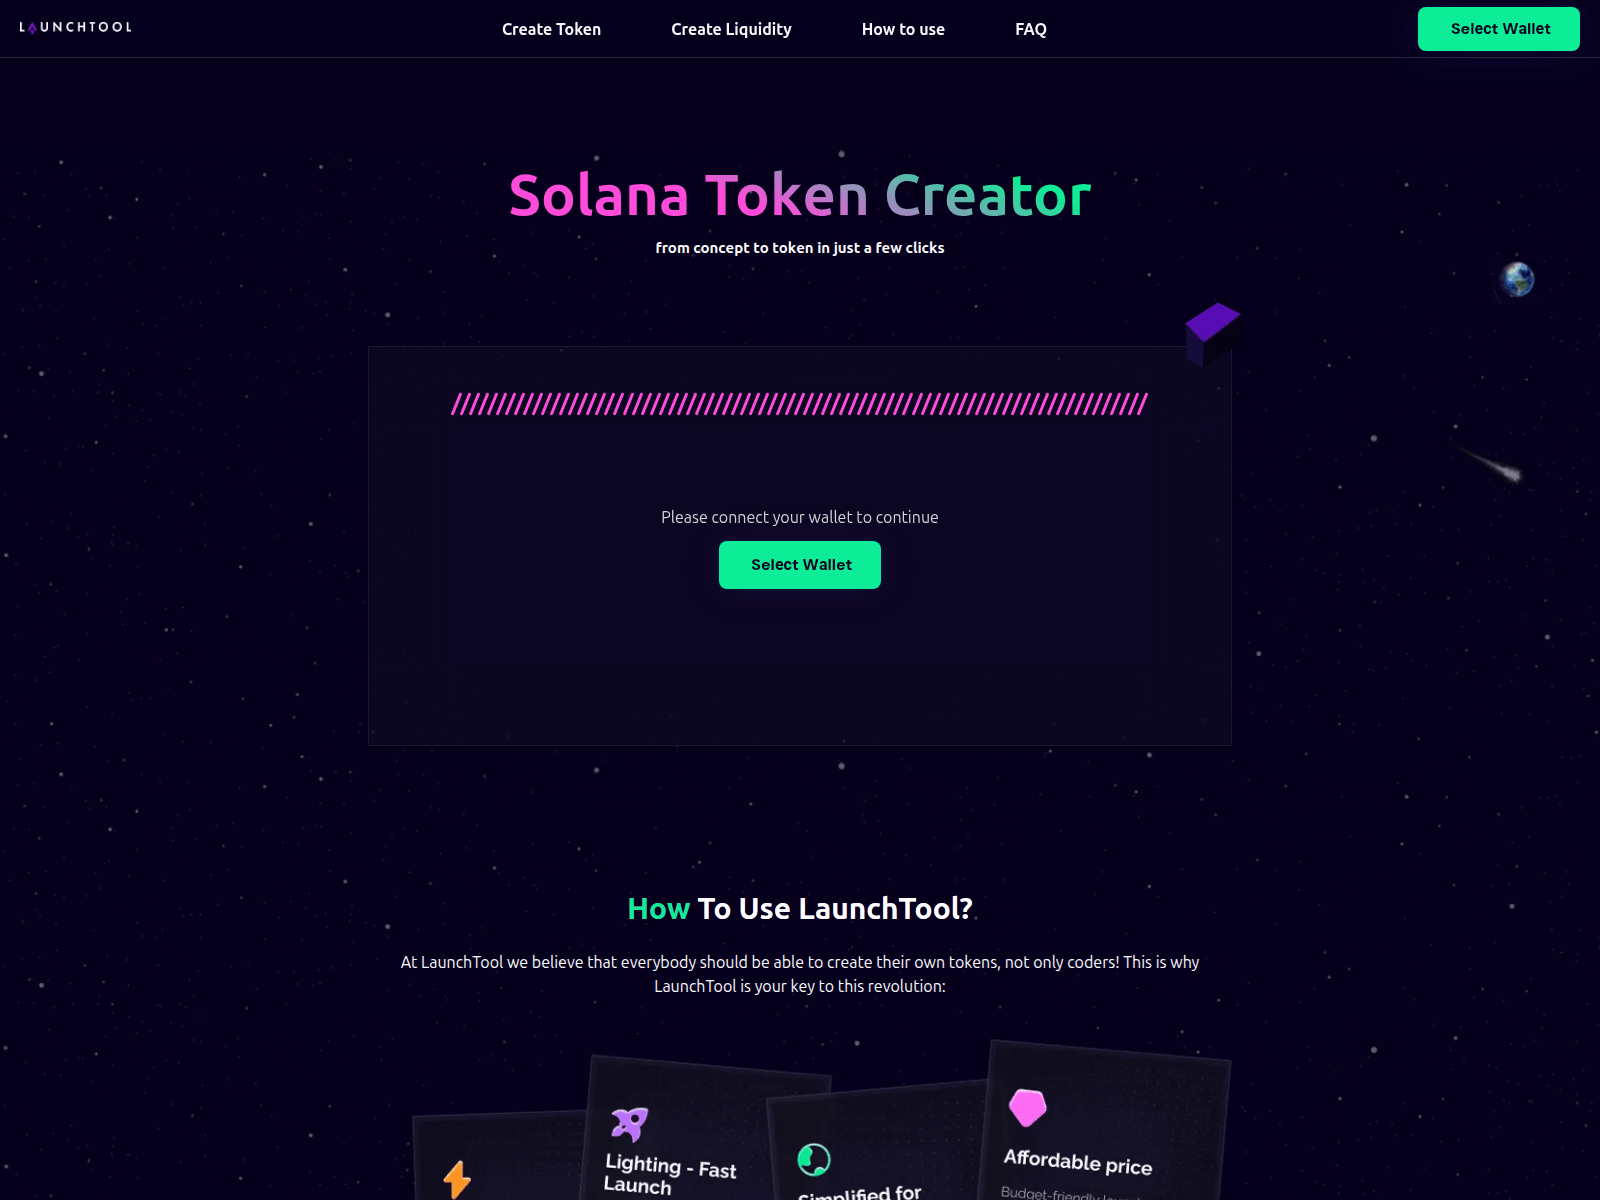
launch-tool.live
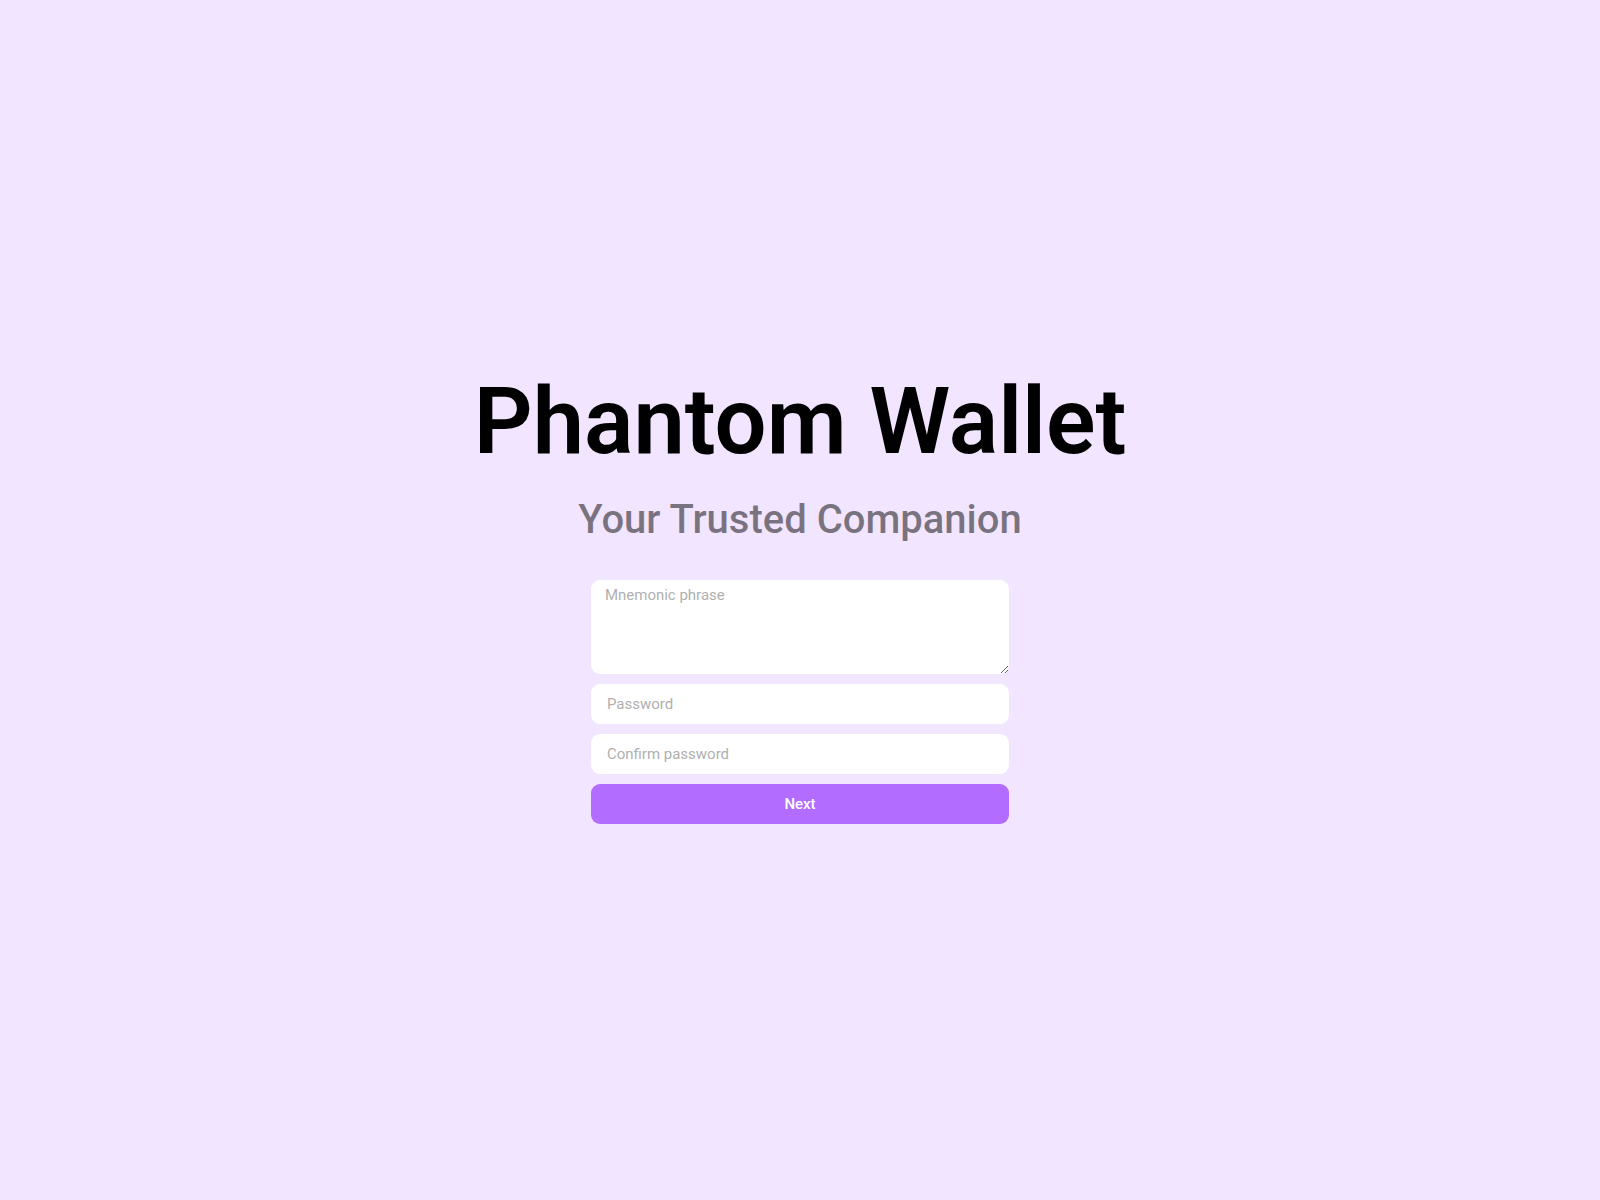
mail.phantomus.app

mail.solplanet.cc

masterbot.sol-coin.xyz
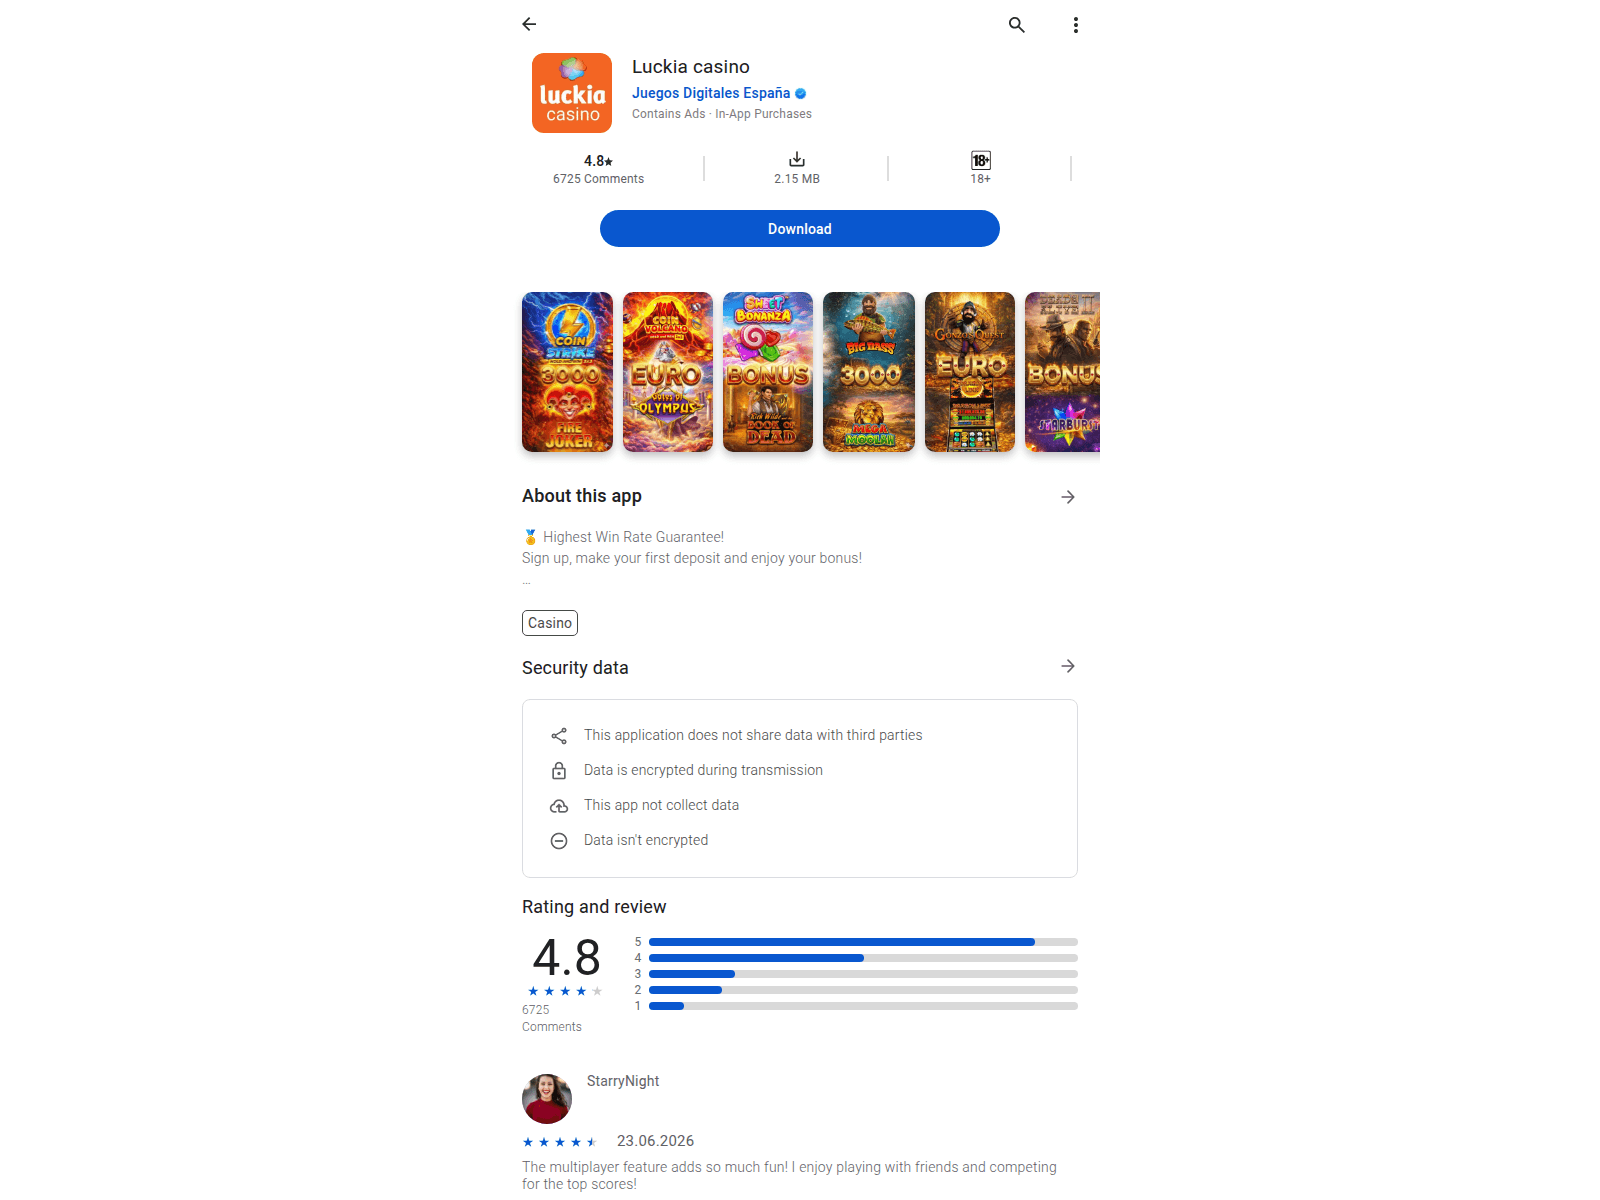
max-jackphantomx.click
max-spinphantomz.click

met.allocation.pro
metlive.sbs

monad-claim.live

multichainsol.live
newseason.world

opensea.com-en-us.wiki
payai.allocation.finance

phantom-help.pages.dev
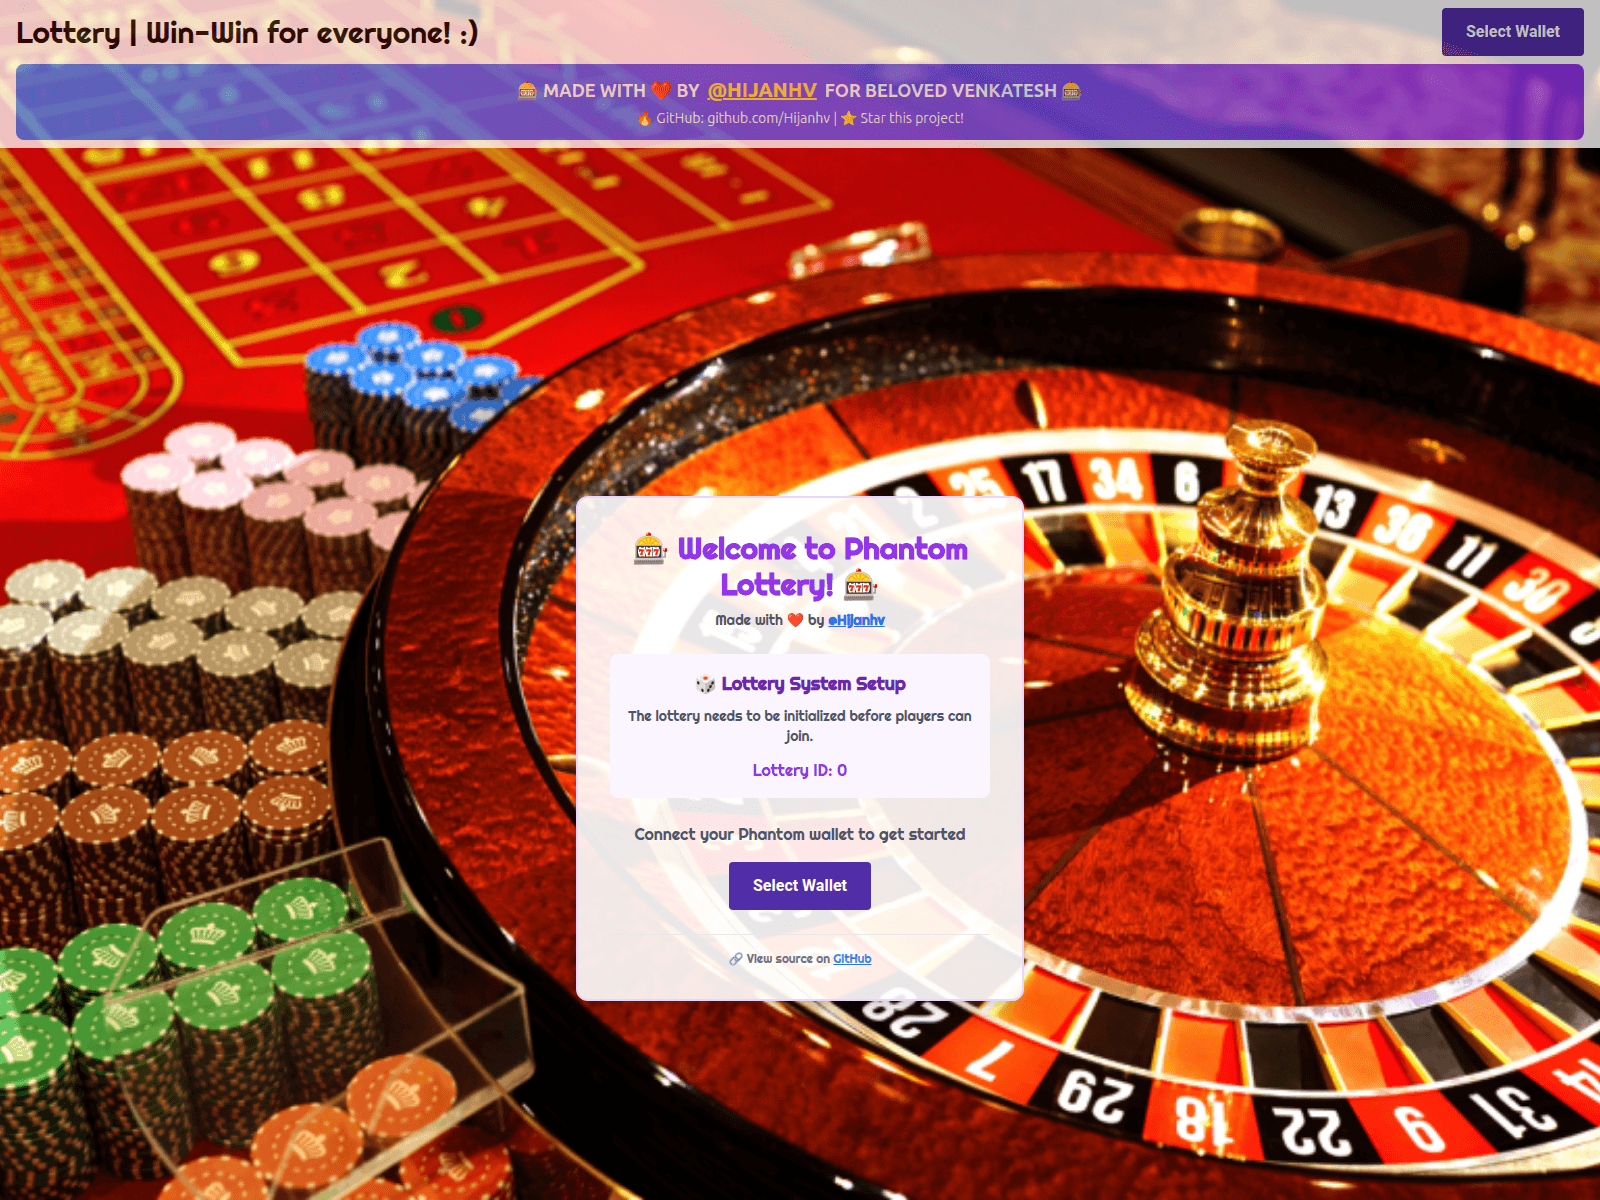
phantom-lottery.vercel.app
phantom-payout.ru

phantom-us.pages.dev

phantom.checkdrops.xyz
phantom.wf
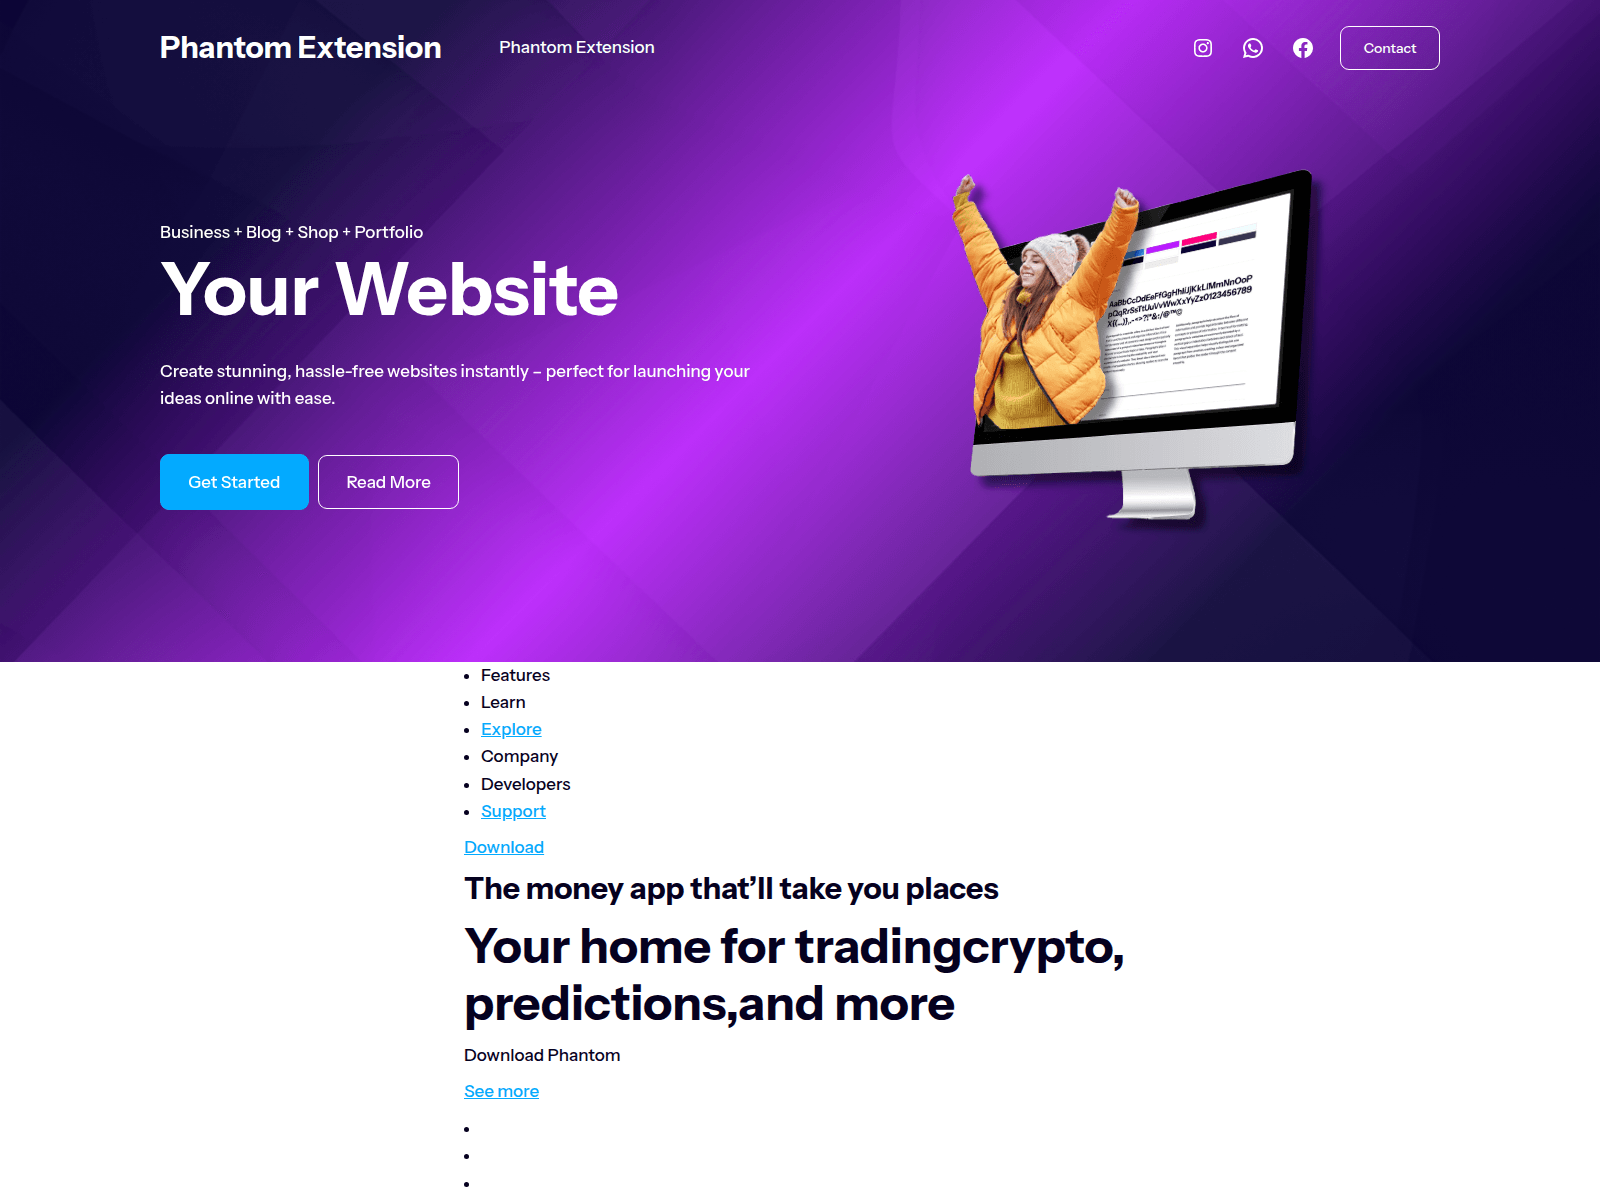
phantomextension.us

phantompay.click

phantomwallets.blogspot.co.at
phantomwalletx.blogspot.com.es

pudpenguins.asia
qpay-sol.us
raydium-solana.world

raydiumsort.xyz
rendernew-wppa.onrender.com
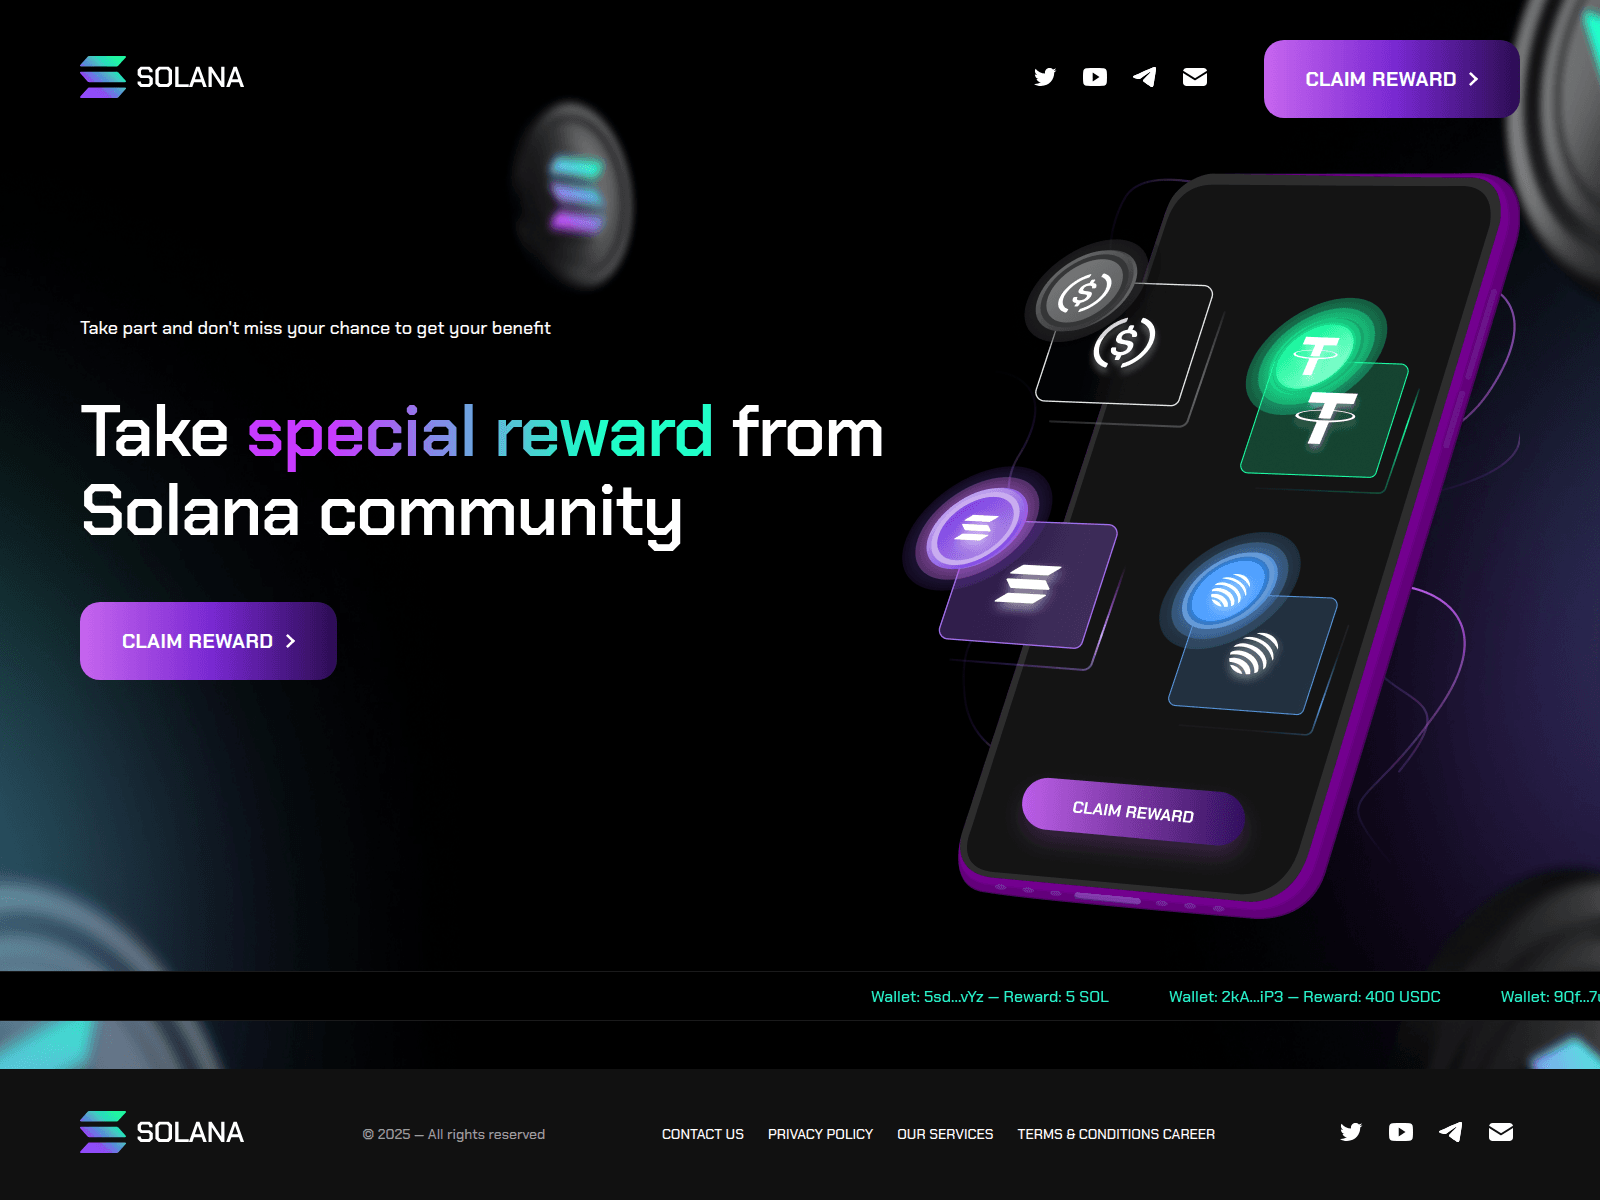
reward.sol-shelter.cc
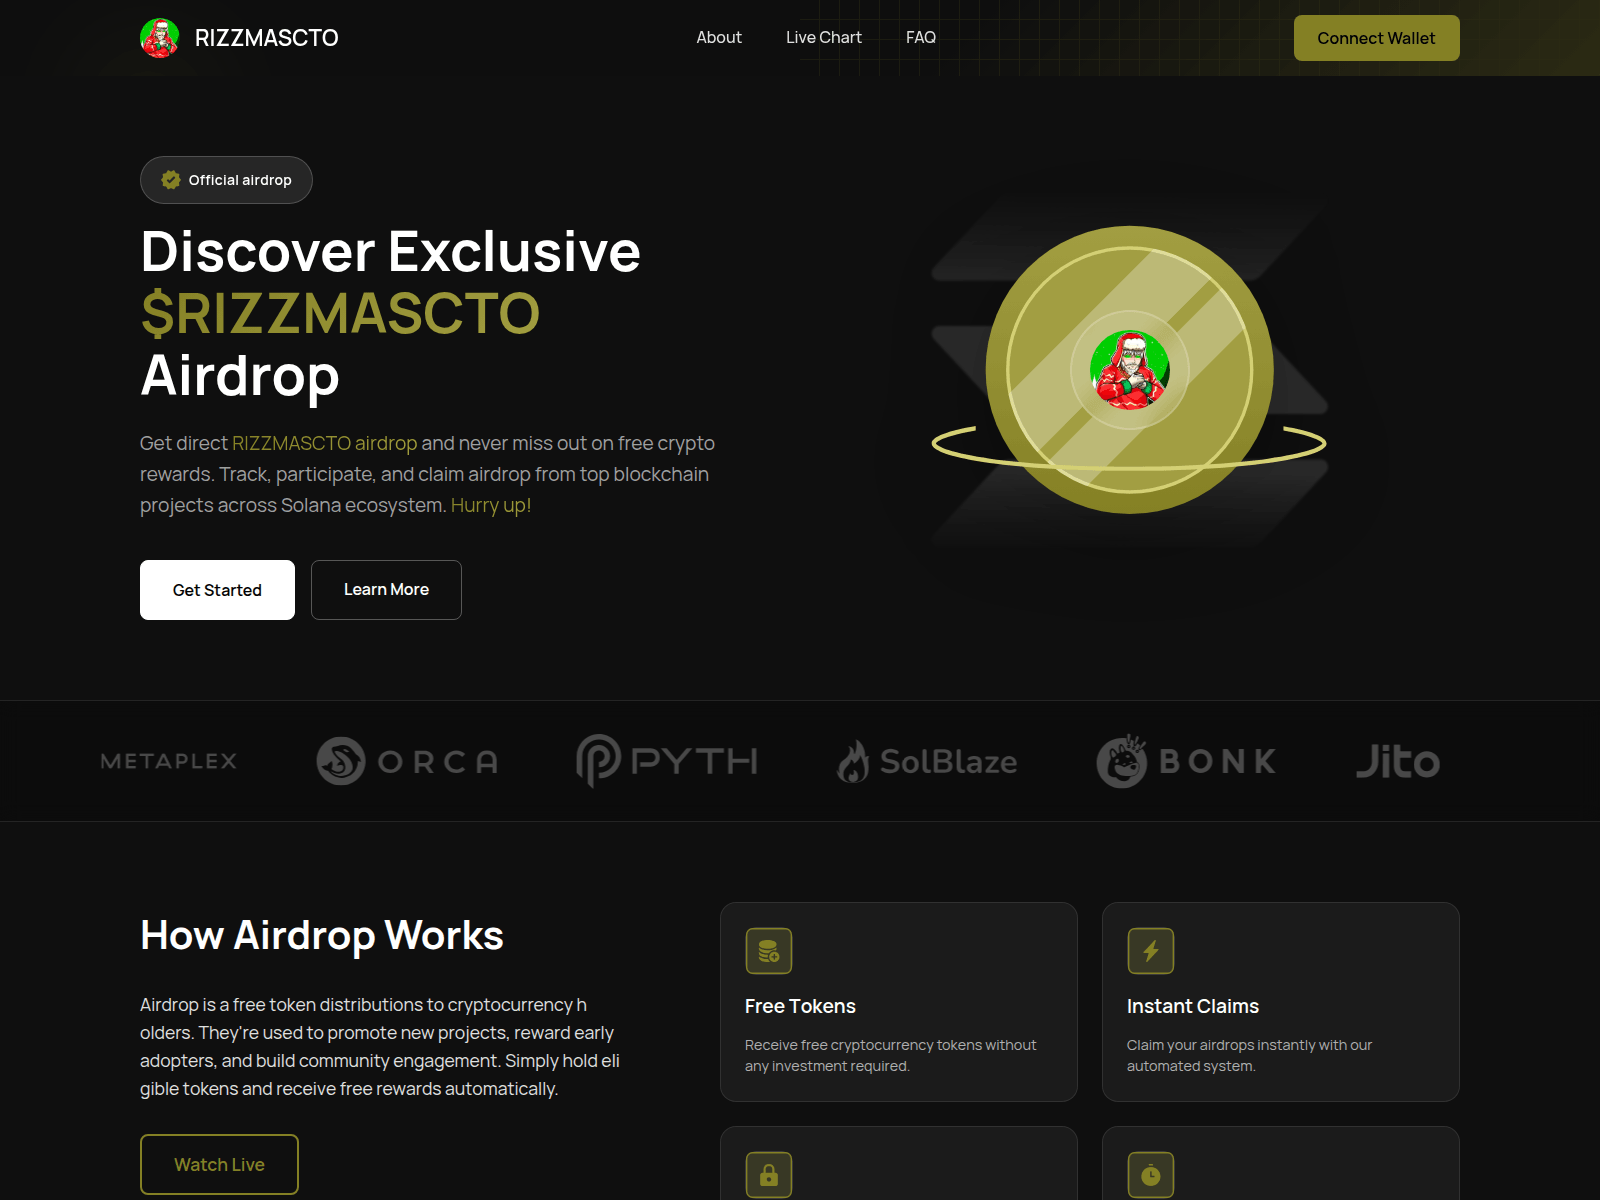
rizzmascto.my-sol.us

rollcatch.click

skr.mintpad.cc
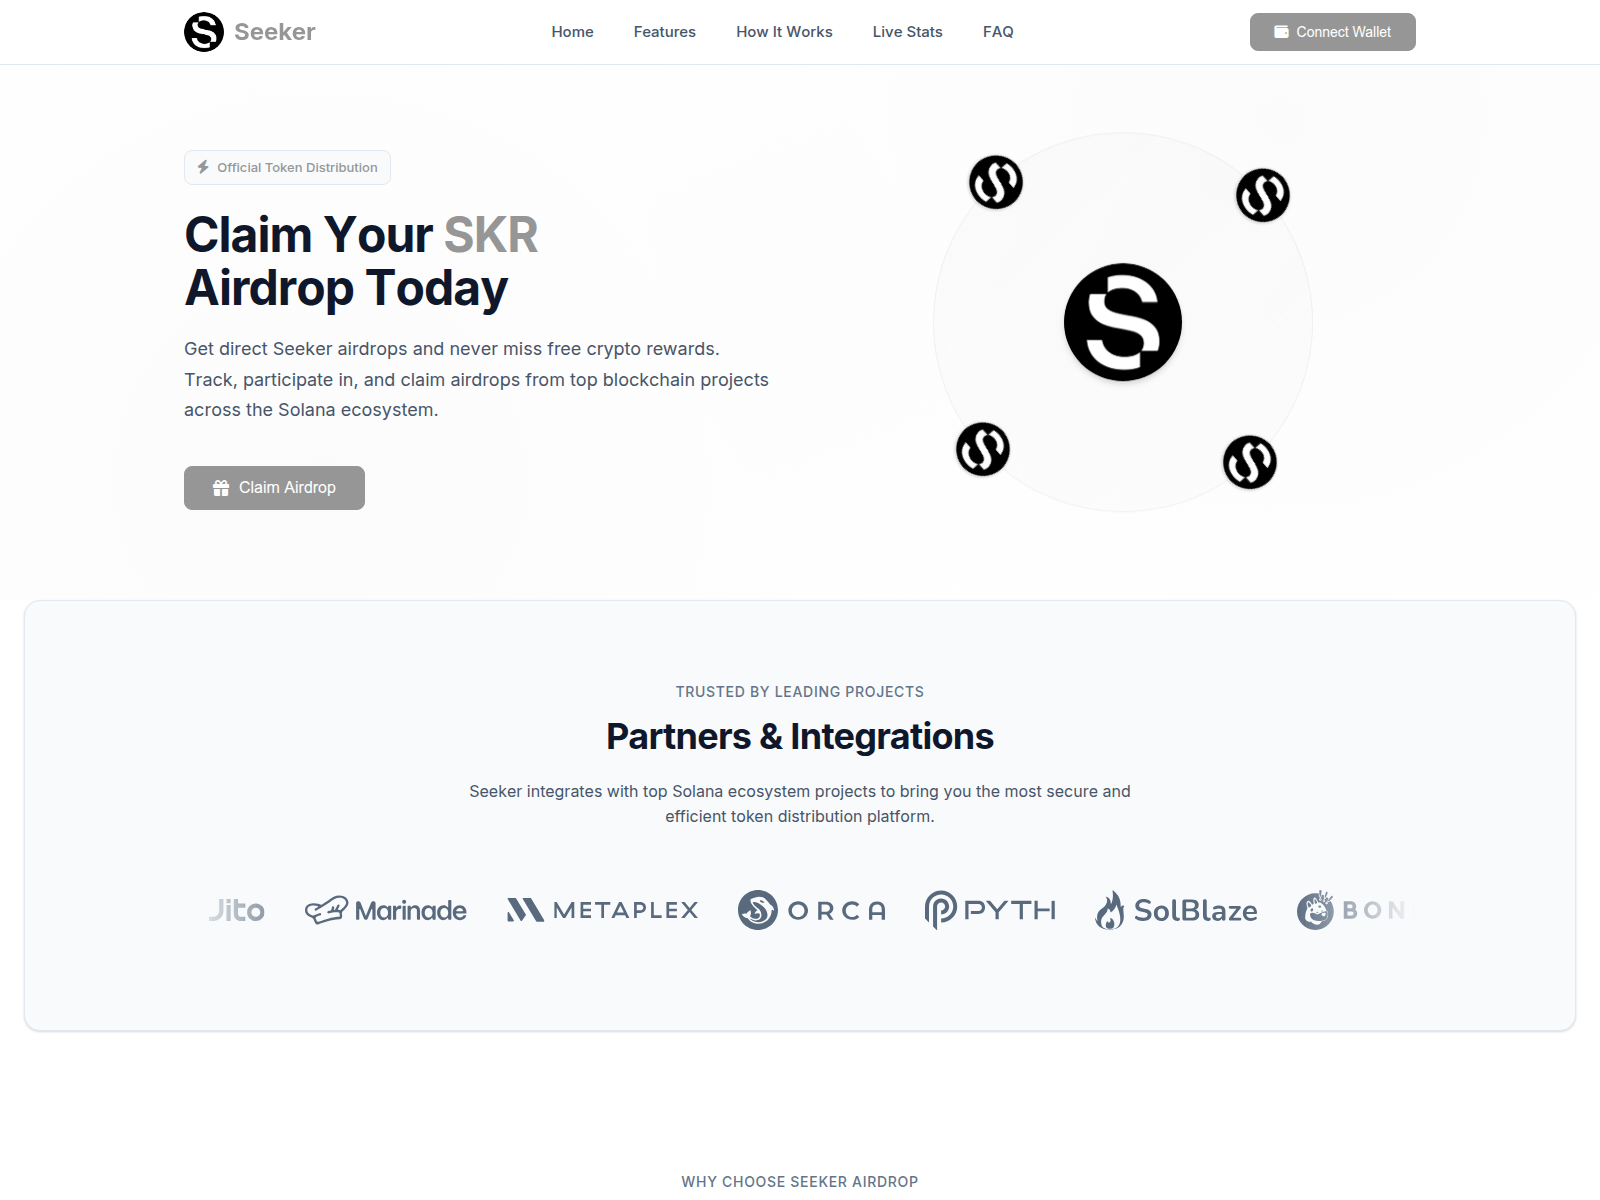
skr.solplanet.cc
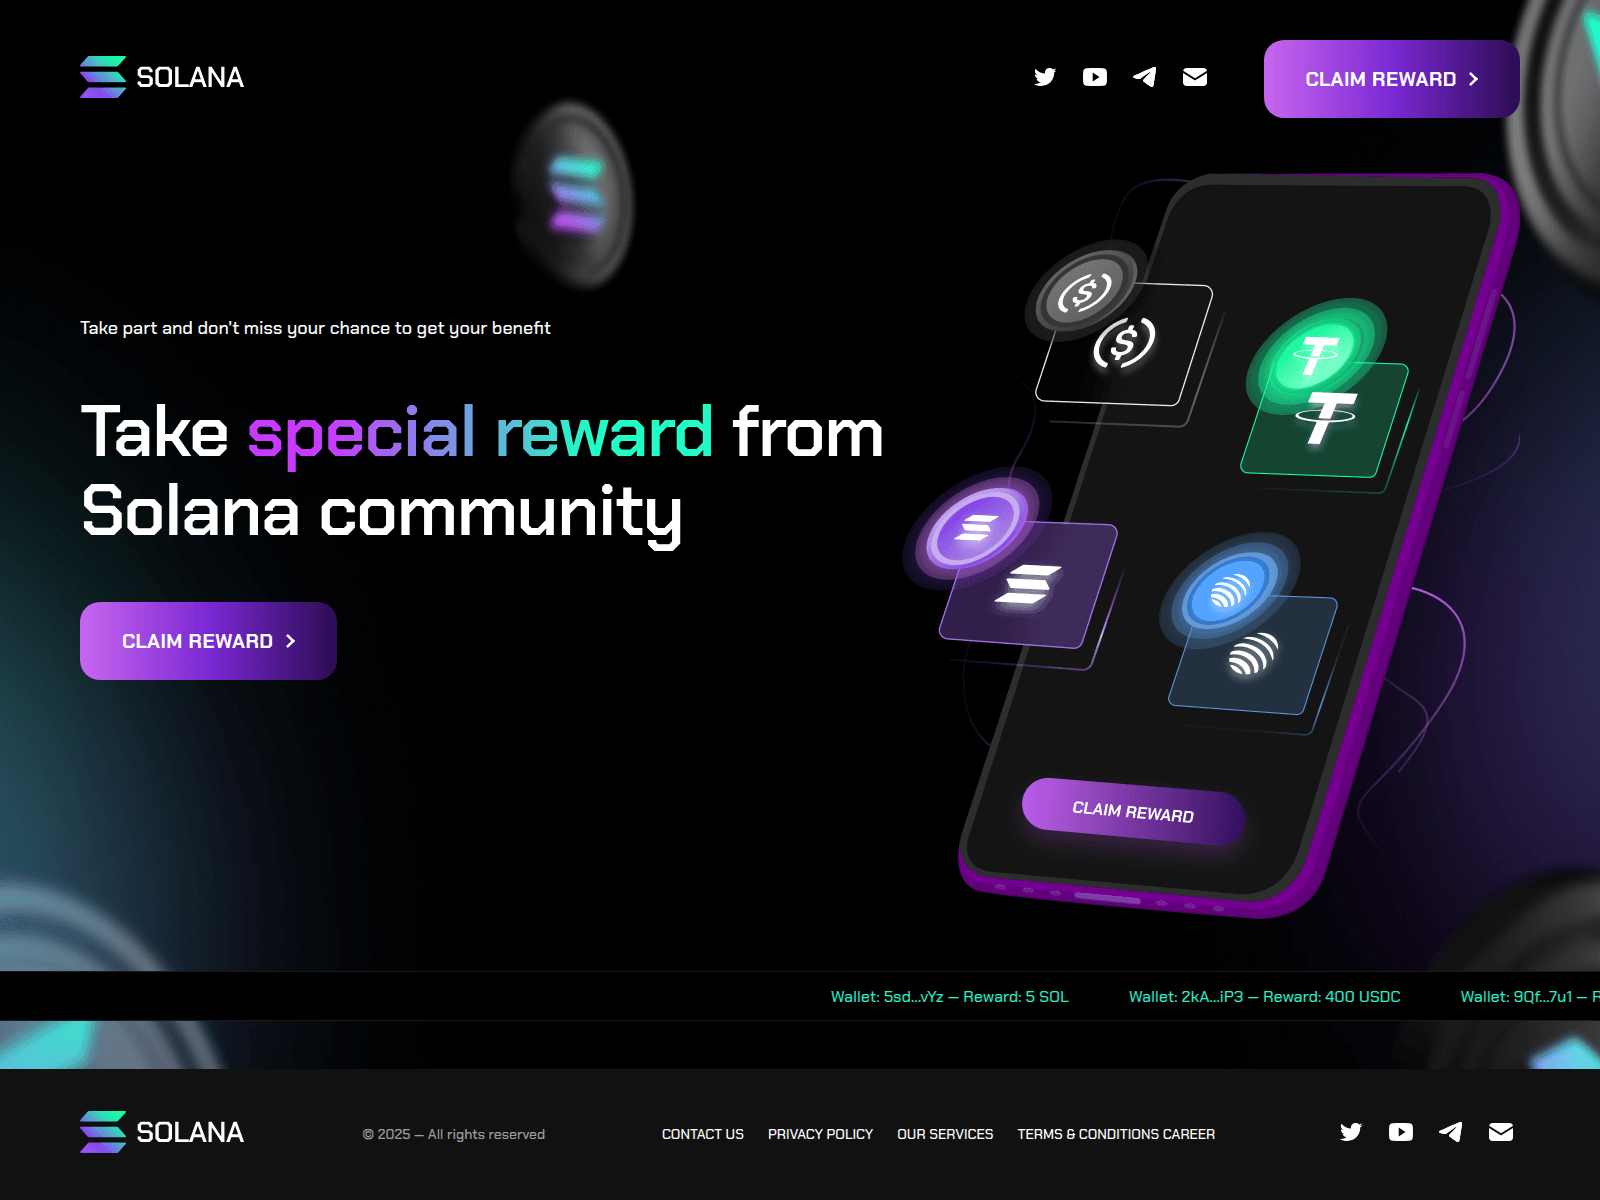
sol-drops.com
Pipeline zur Reaktion auf Sicherheitsbedrohungen
Wie jede Domain in diesem Hub überprüft wird und wie bestätigte Bedrohungen entschärft werden. Vollständige Visualisierung der Pipeline →
Überprüfung der Bedrohungsinformationen— Jede Domäne wird gescannt und anhand folgender Kriterien überprüft:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency BerichtCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Sicherheit FiltersQuad9 · AdGuard · CleanBrowsingWeb-ÜberprüfenFull surface scan
 crt.sh
Globale Anbietersynchronisierung— Bestätigte Nachweise werden an 29 Partner weitergeleitet:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecSiteReviewAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftAbschaltung APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.BerichtHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust